COBIT 2019
Explore articles in the COBIT 2019 category
113 articles
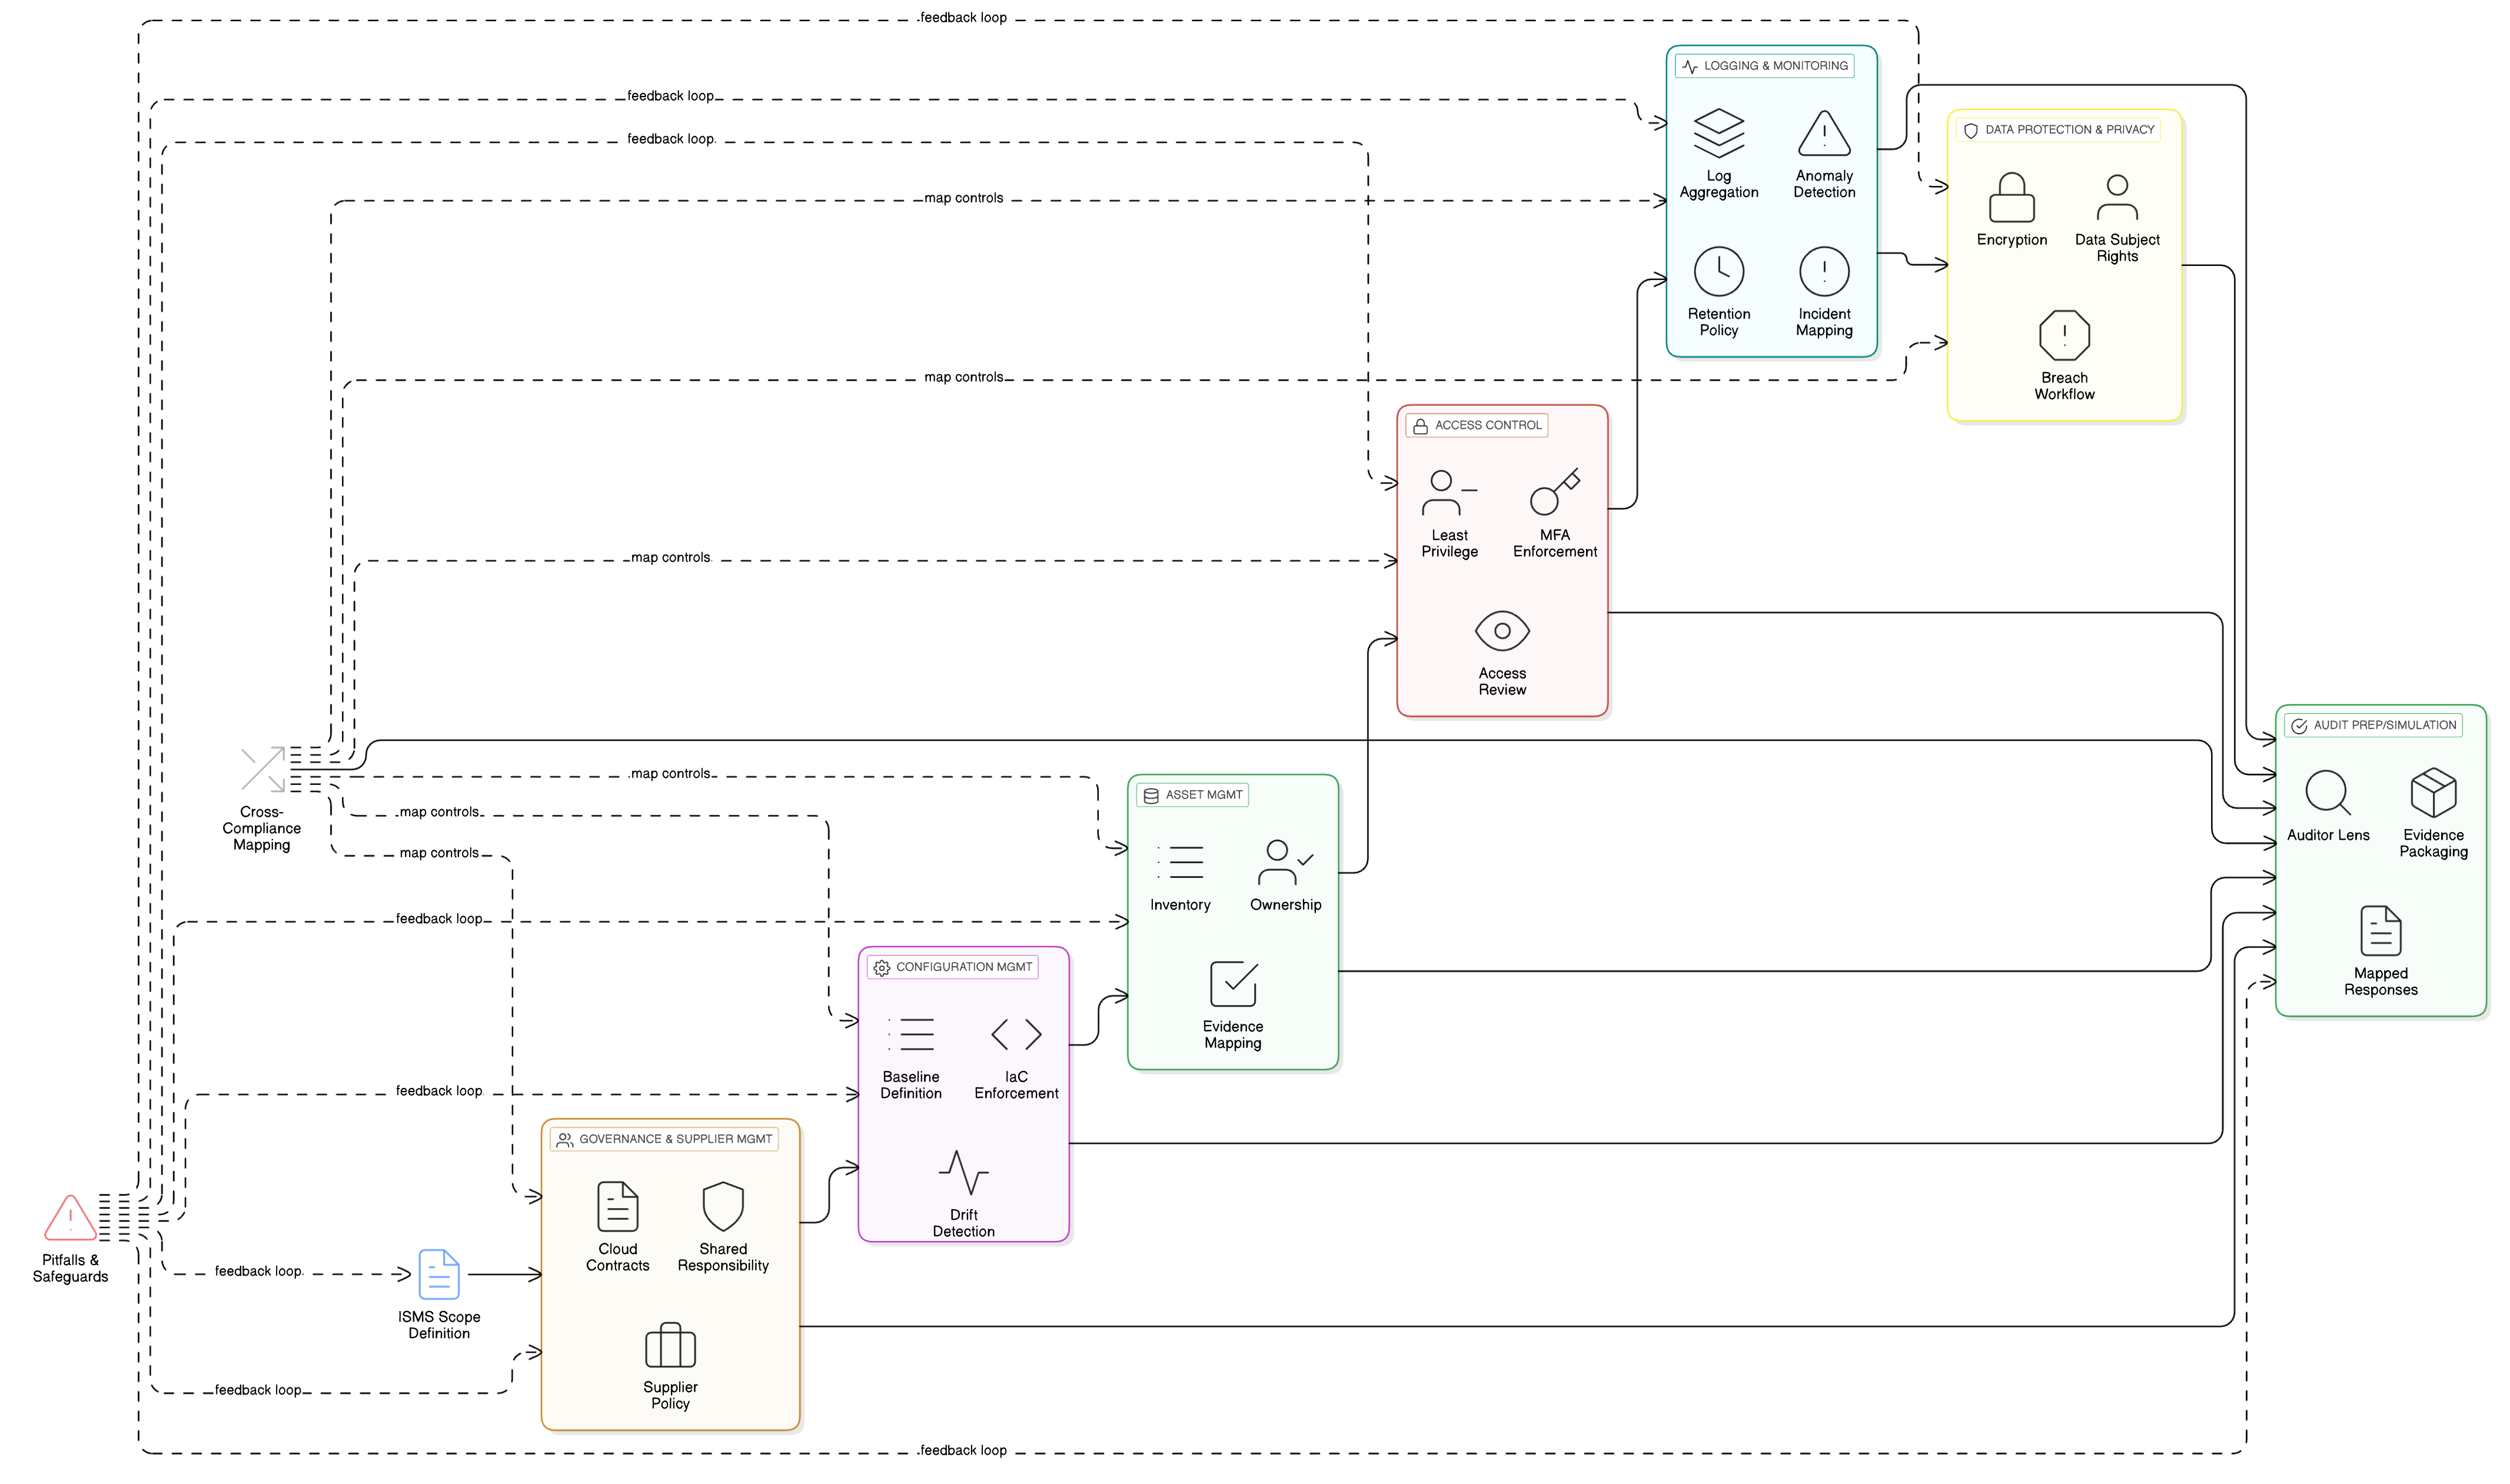
CISOs, compliance managers, and cloud architects: discover how to operationalize ISO 27001:2022 cloud controls for perpetual compliance. Real-world stories, technical mapping tables, and actionable blueprints from Clarysec unite security, governance, and audit-readiness across frameworks.
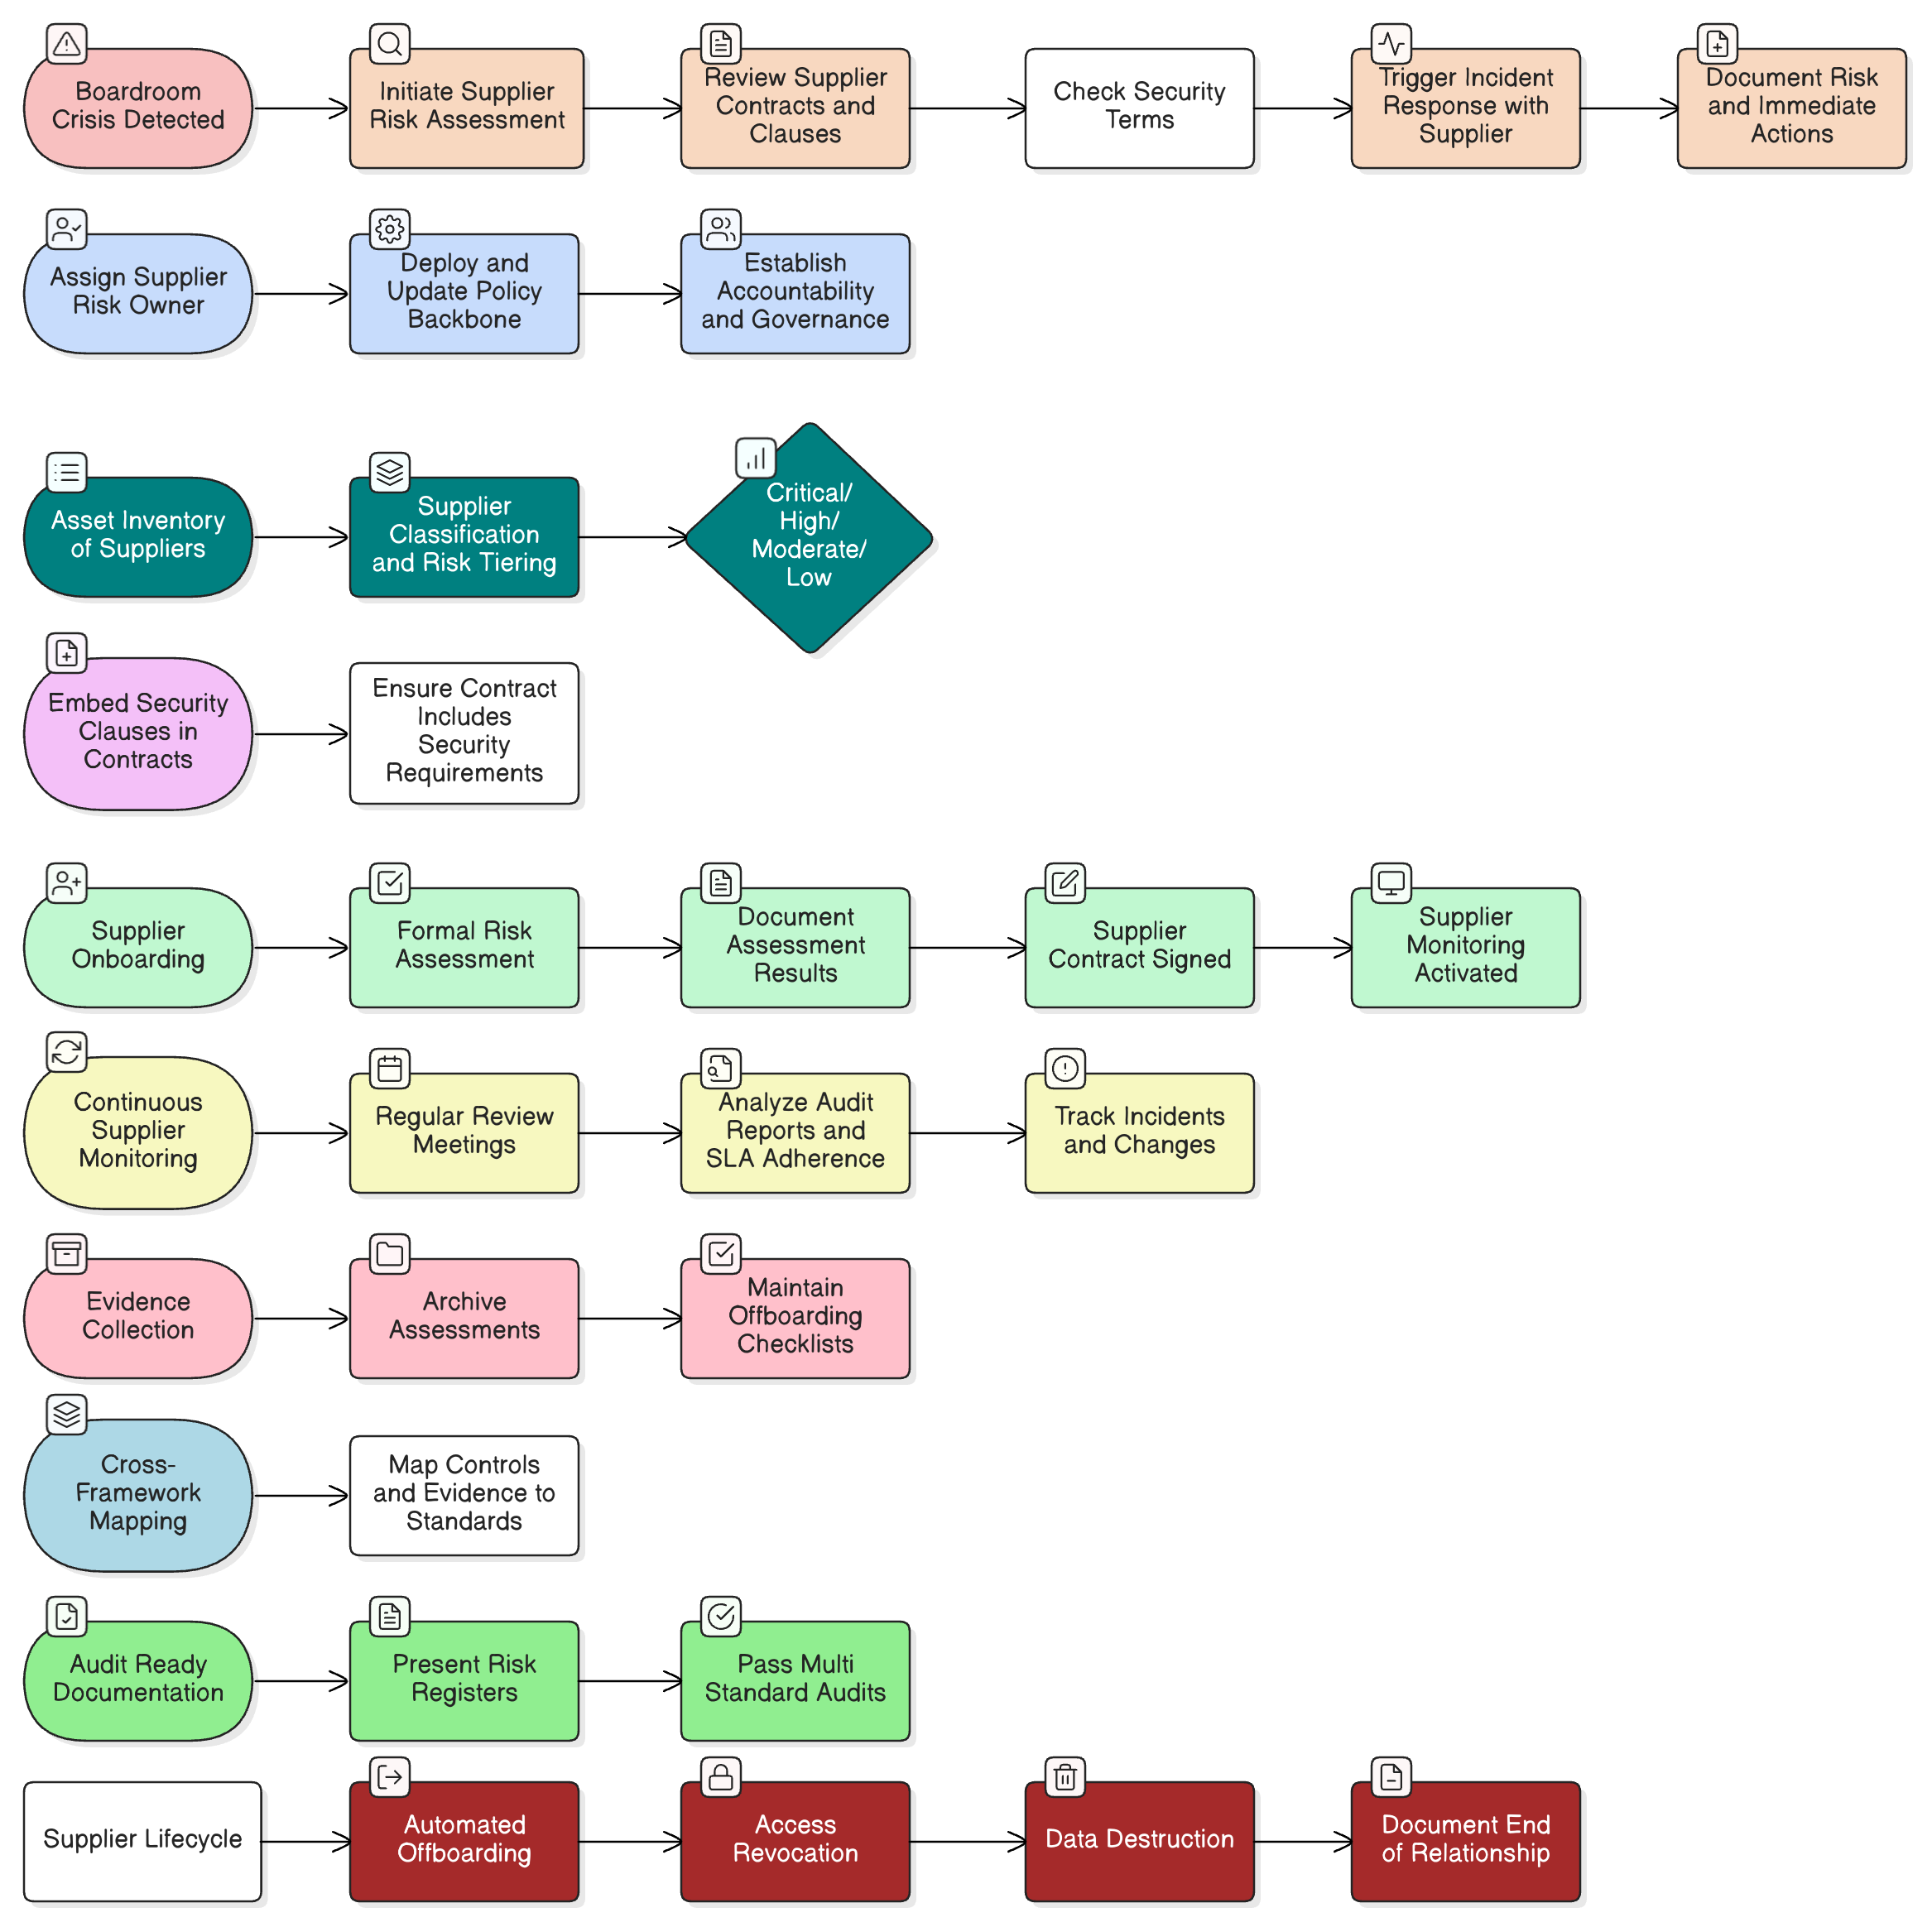
A comprehensive guide to operationalizing supplier risk management, from boardroom crises to cross-framework audit triumphs, using real-world scenarios, Clarysec’s Zenith toolkits, and actionable blueprints that secure the supply chain throughout its entire lifecycle.
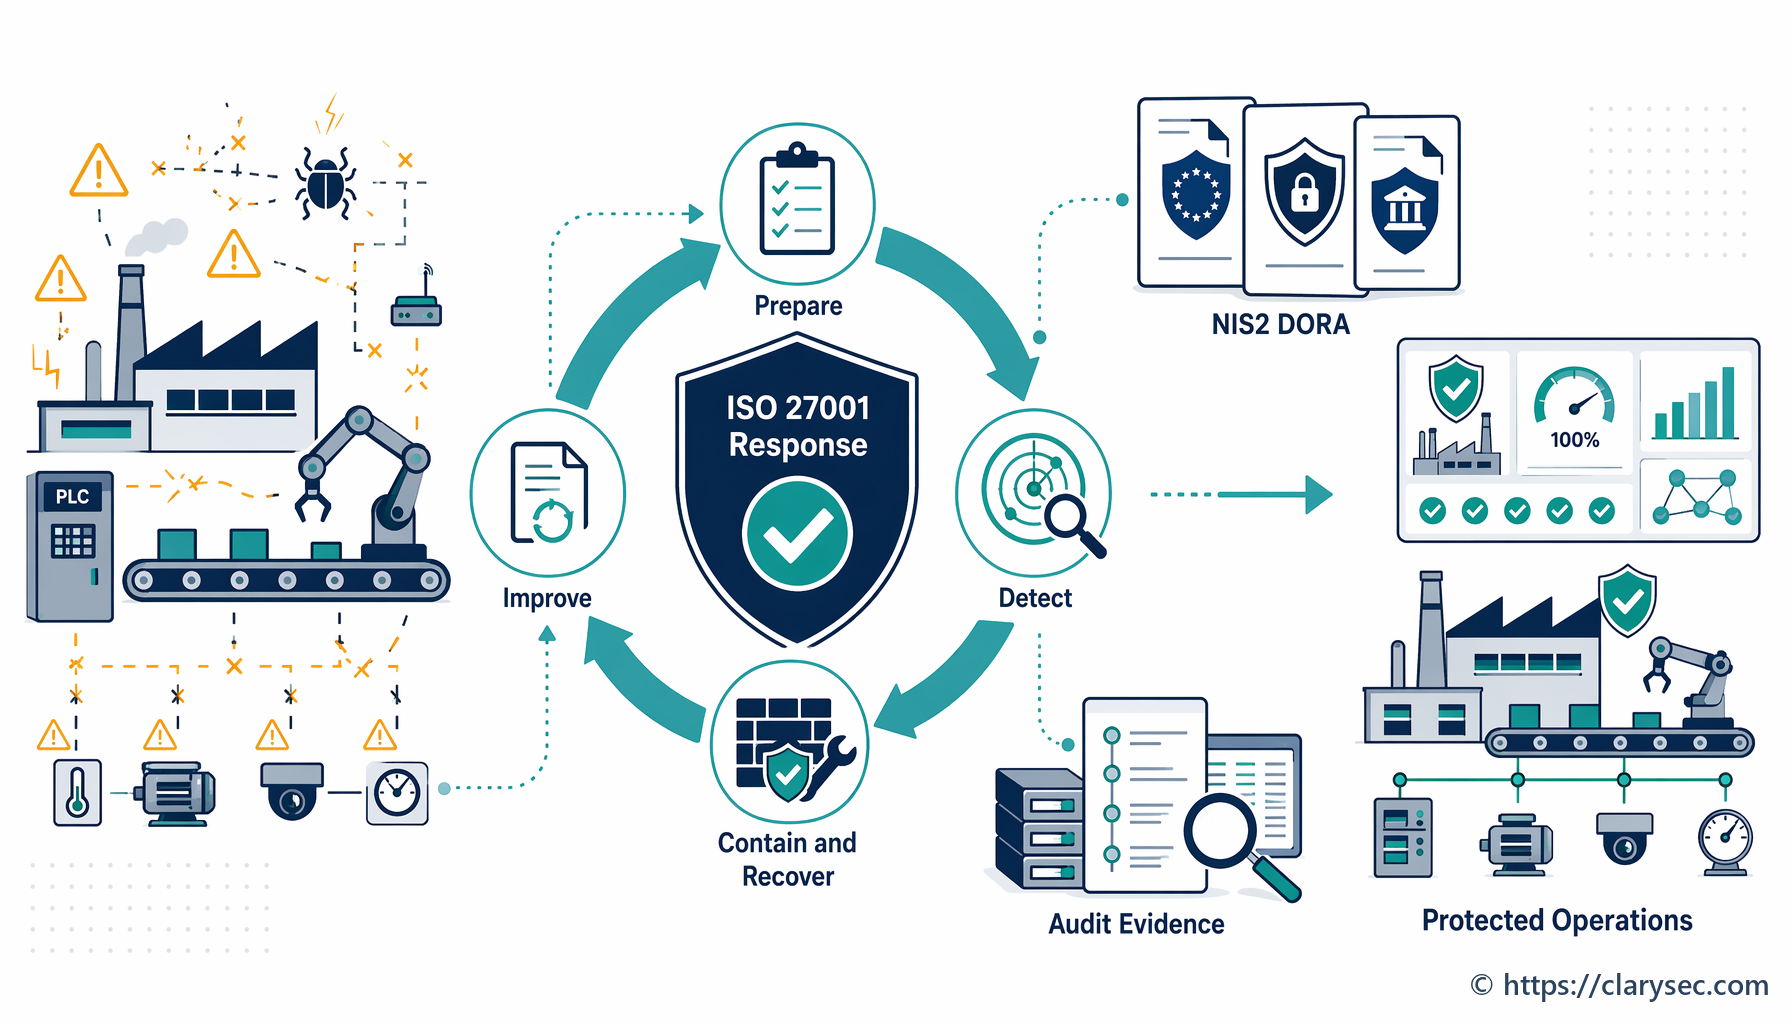
A guide for manufacturers on building a robust, ISO 27001-aligned incident response plan to protect operations and ensure compliance.
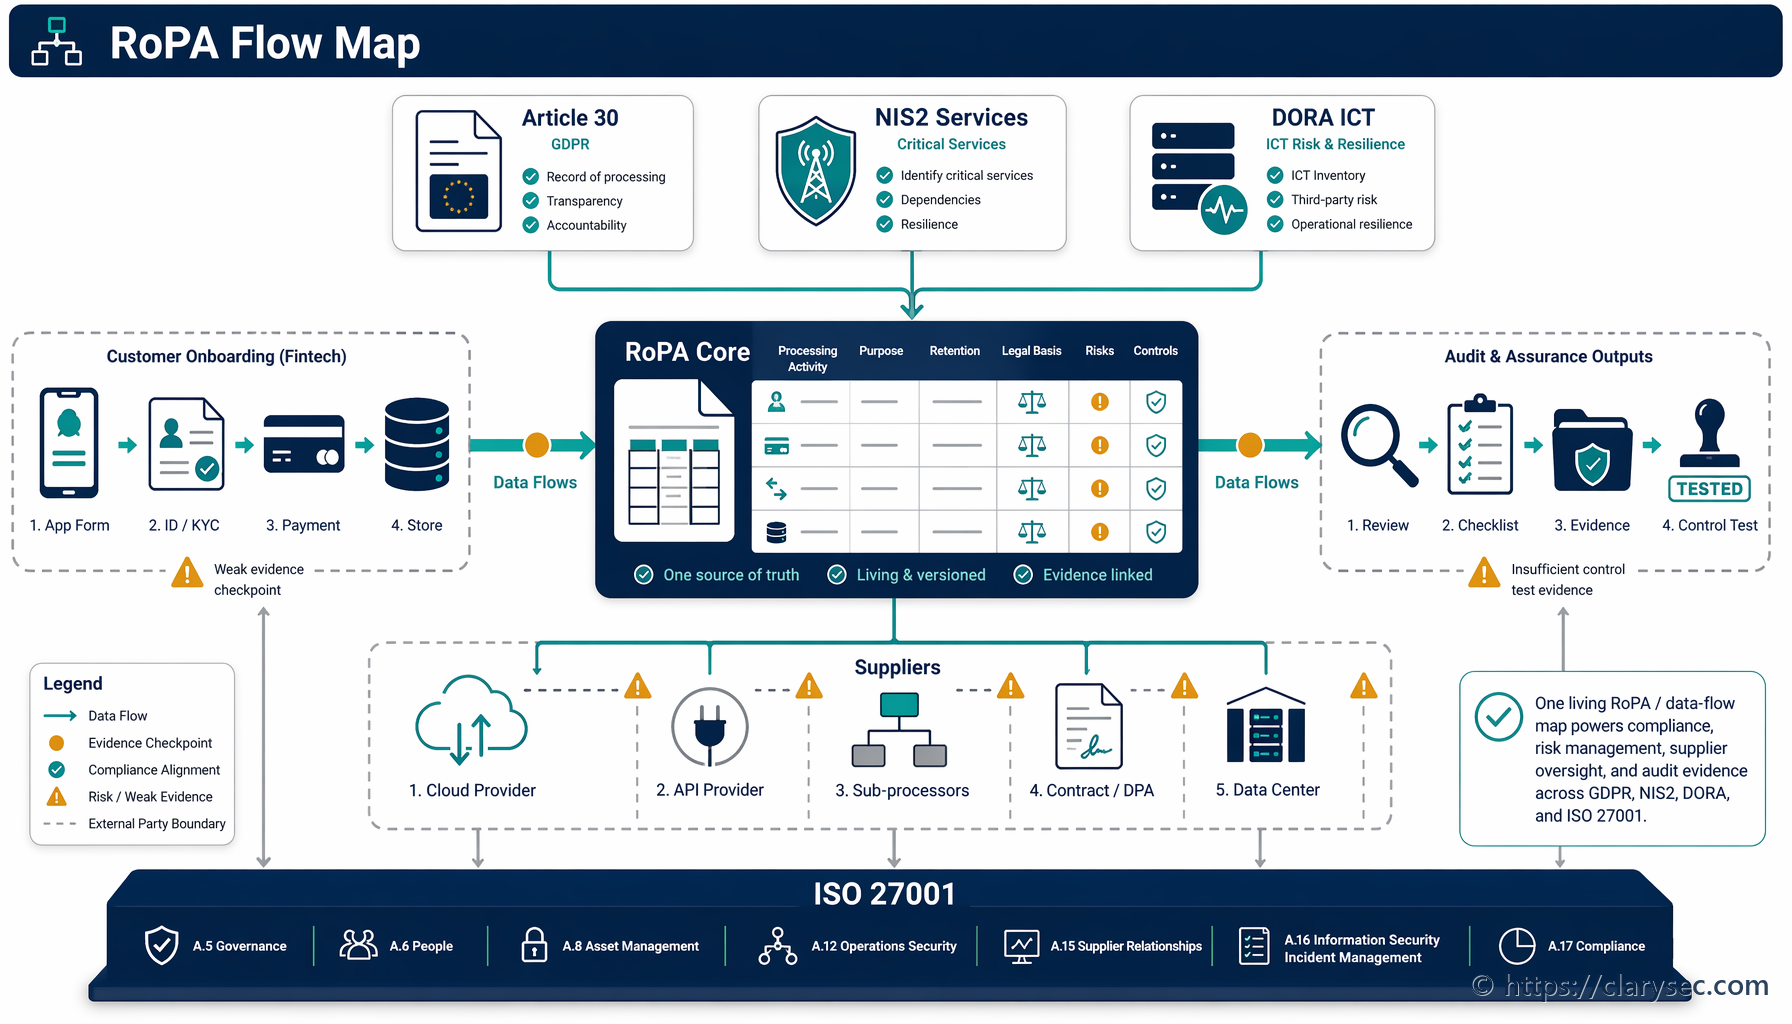
A practical 2026 guide for turning RoPA and data flow mapping into a unified evidence layer for GDPR Article 30, NIS2 critical services, DORA ICT dependencies and ISO/IEC 27001:2022 audits.
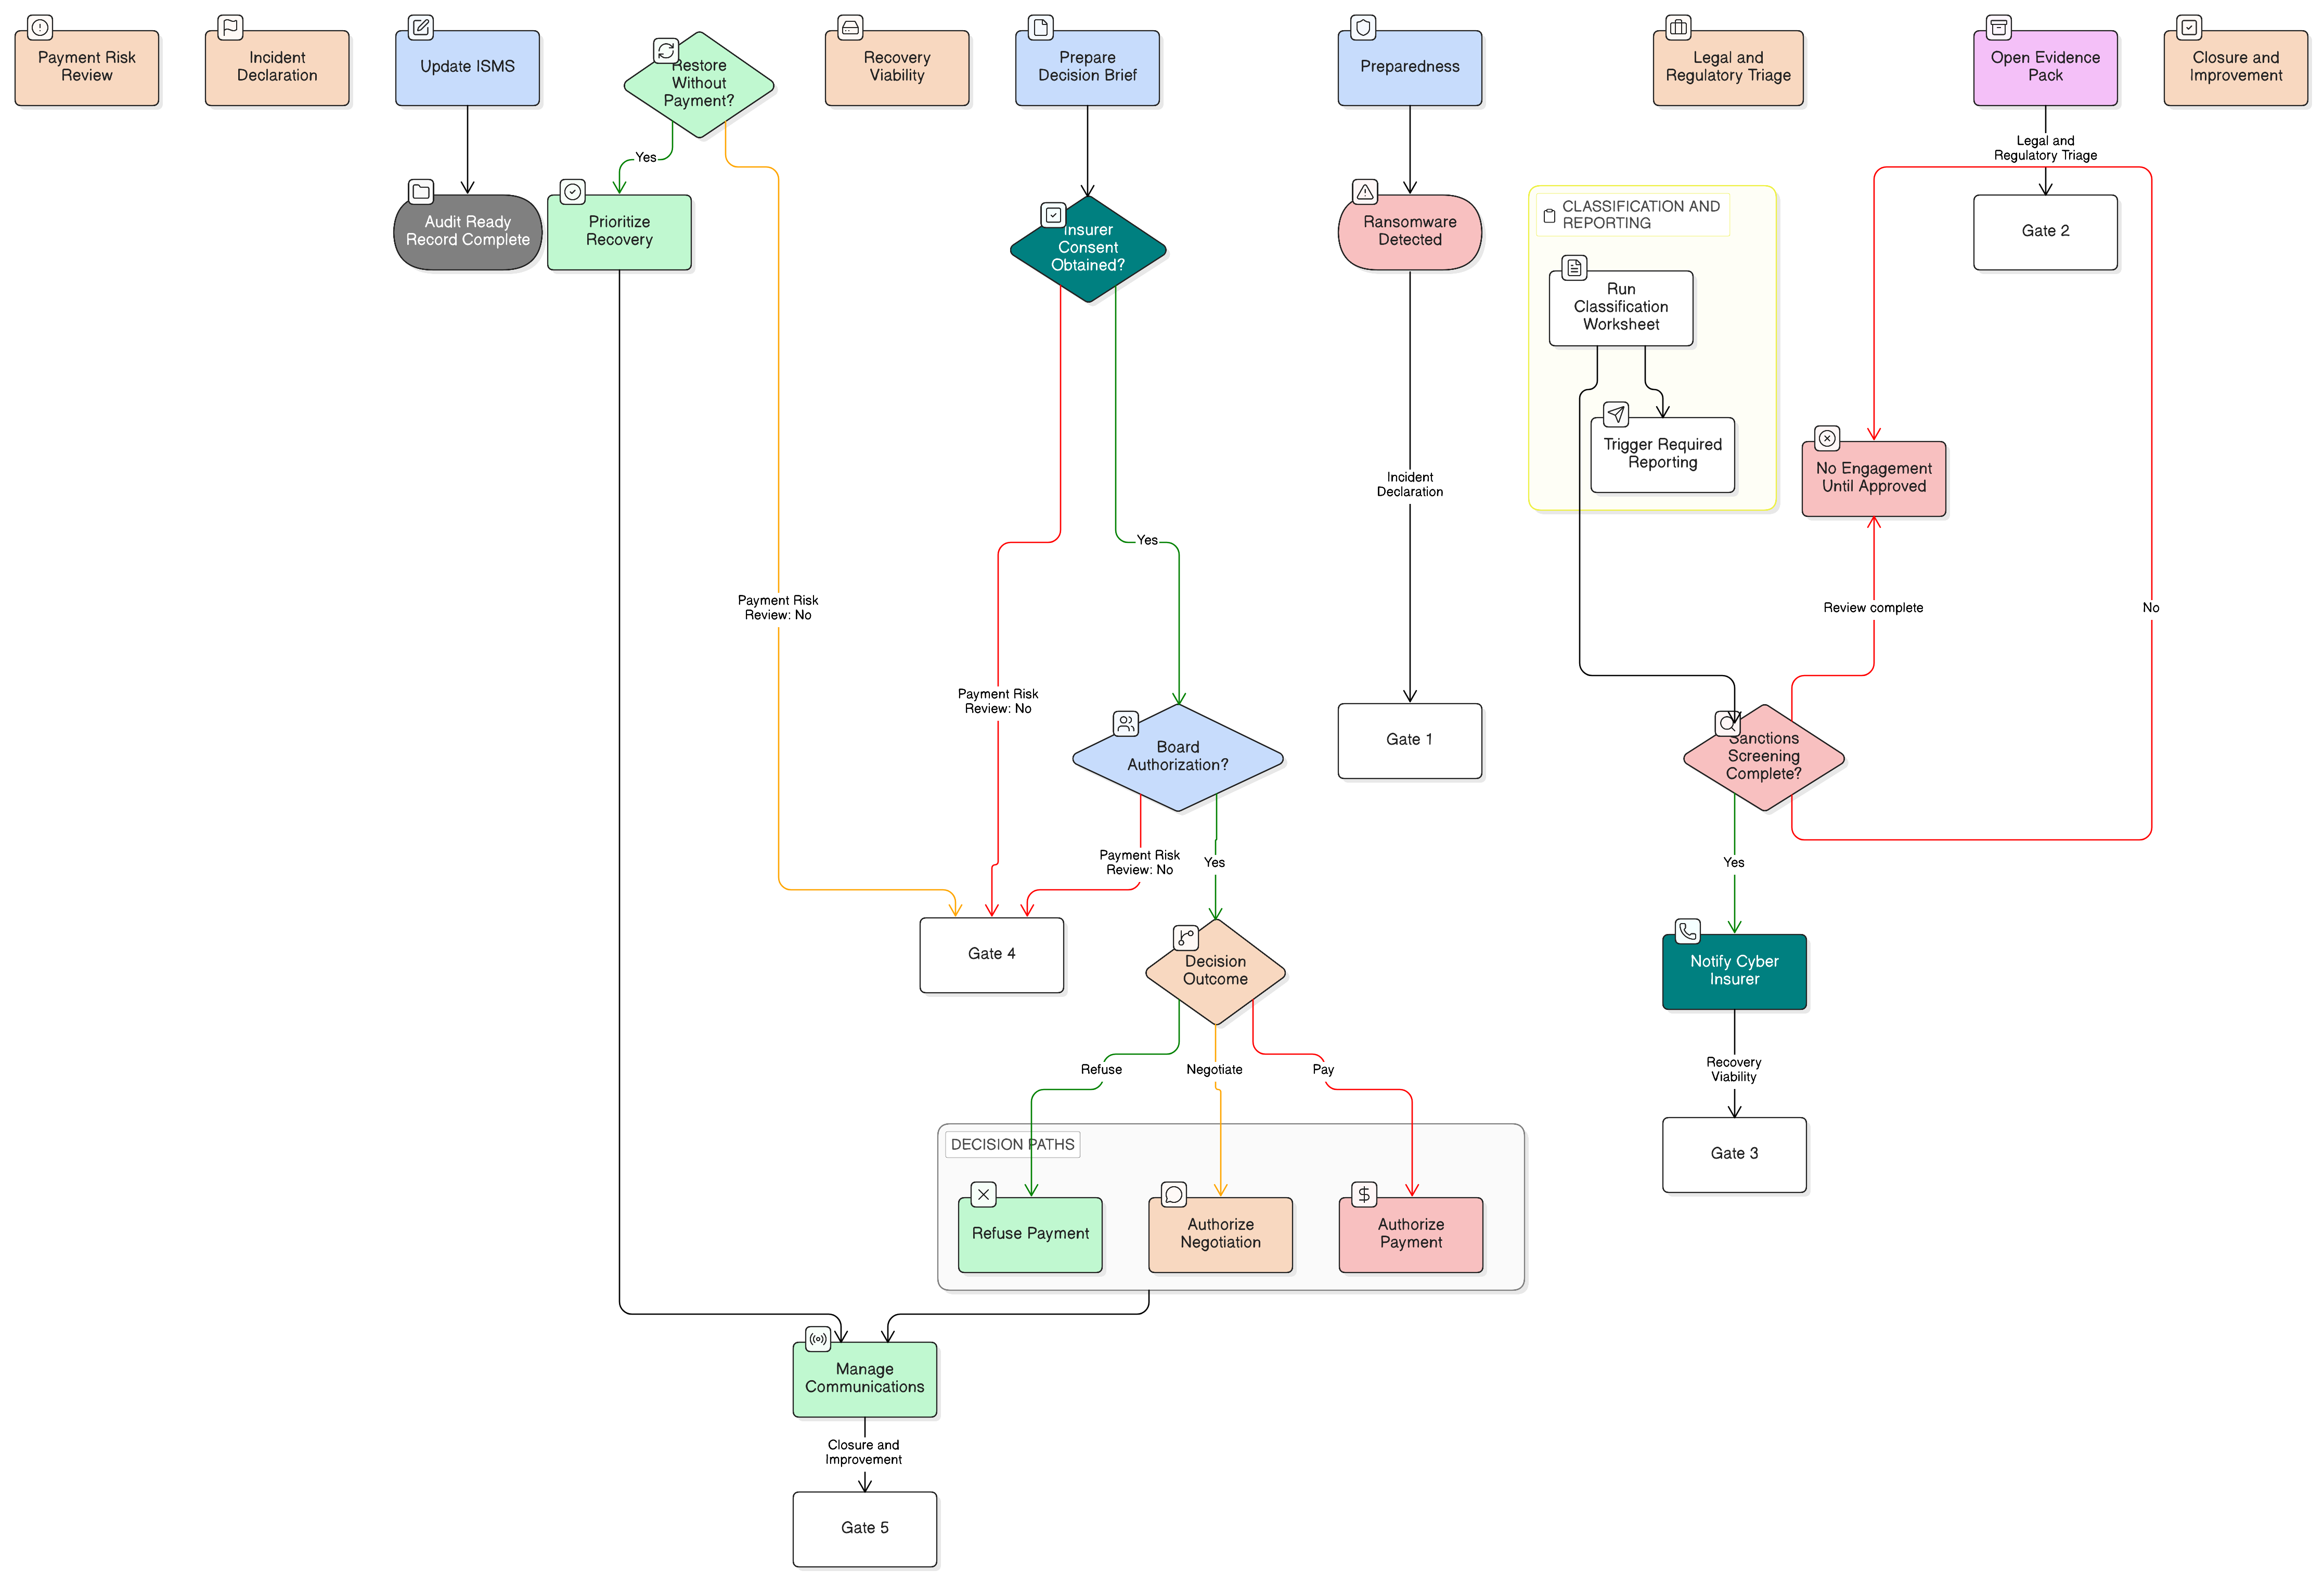
A practical ISO 27001:2022-aligned framework for governing ransomware payment decisions, sanctions checks, evidence preservation, insurance approval, NIS2, DORA and GDPR reporting.