COBIT 2019
Explore articles in the COBIT 2019 category
96 articles
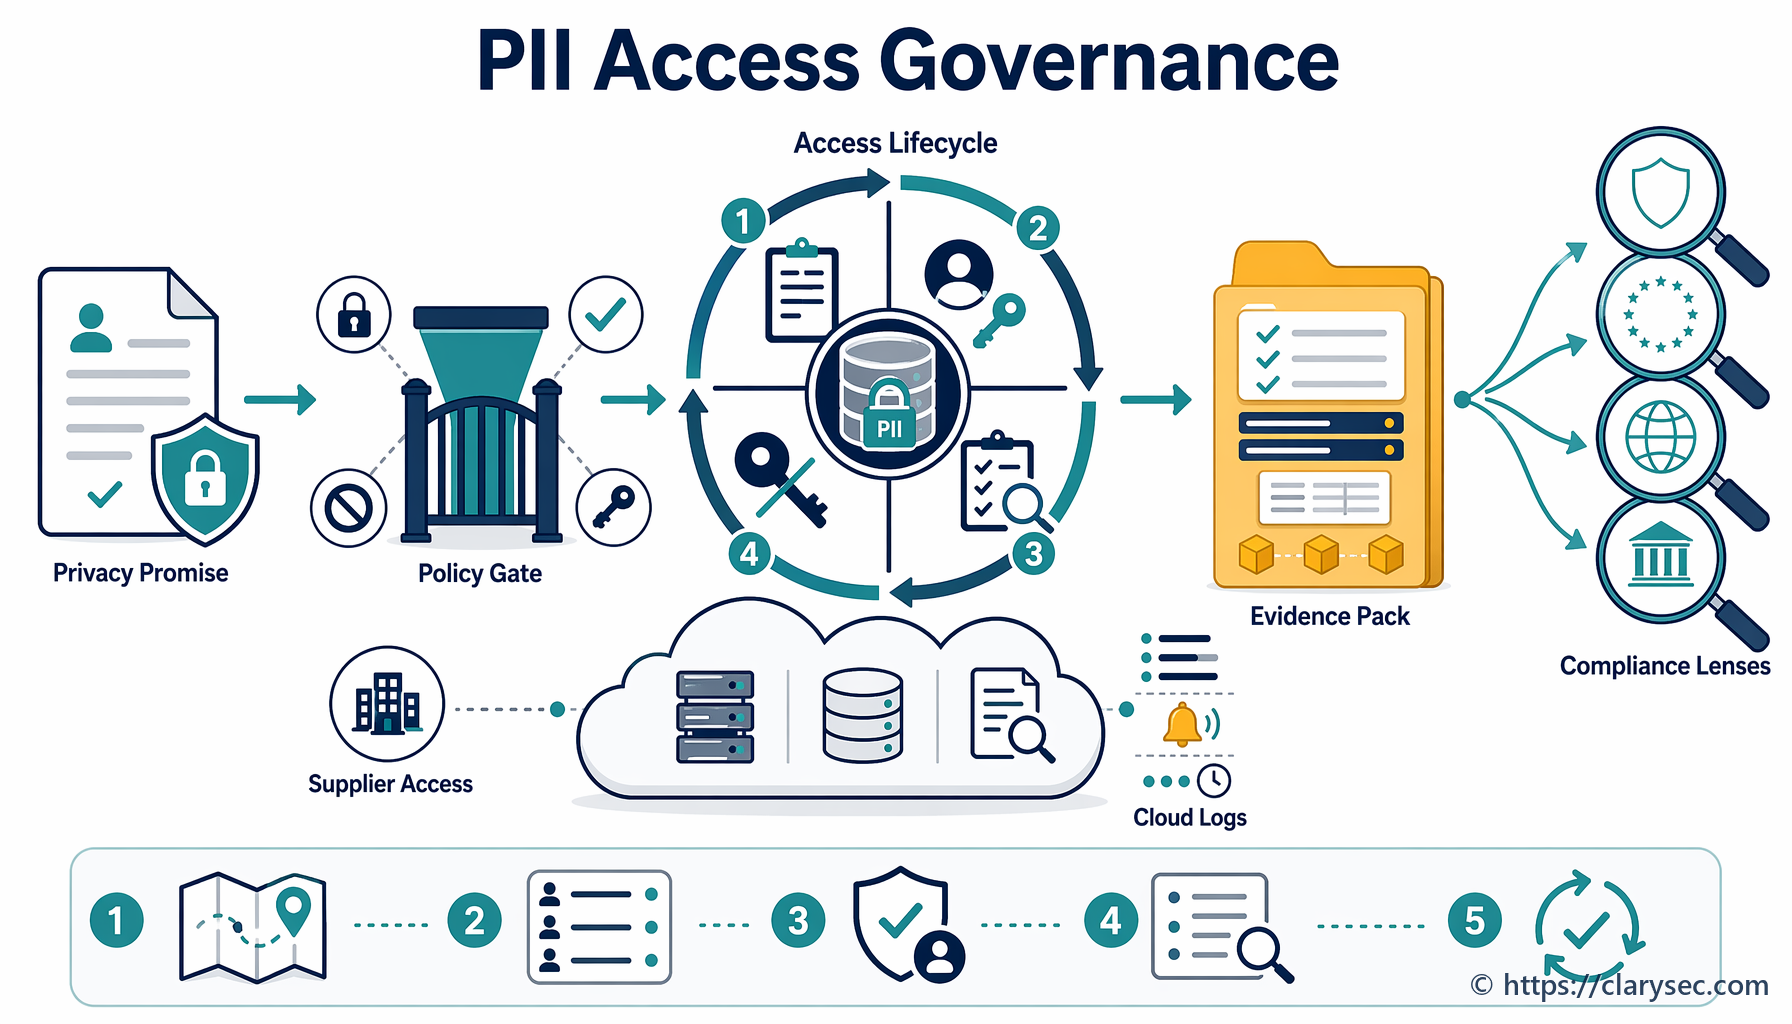
A scenario-driven guide to building audit-ready PII access governance across ISO/IEC 27701:2025, GDPR, ISO/IEC 27001:2022, NIS2, DORA, NIST CSF 2.0, and COBIT 2019 using Clarysec policies, registers, mapping tables, and practical review workflows.
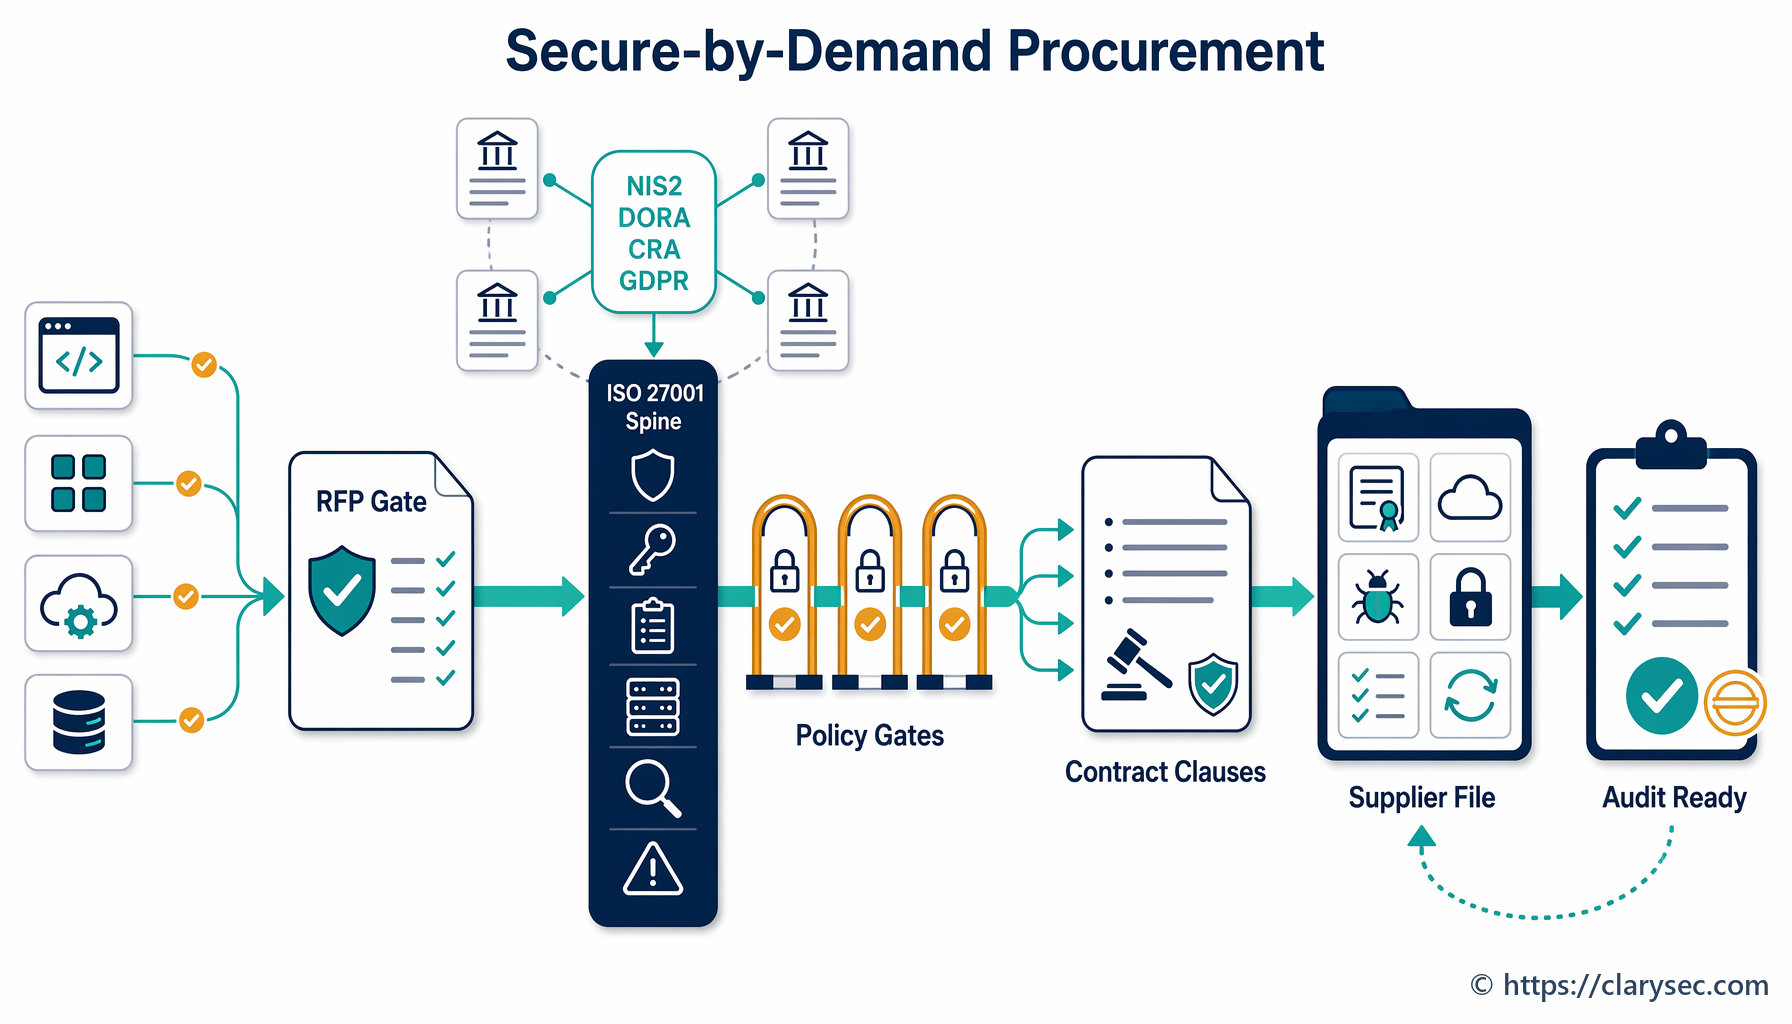
Secure-by-demand procurement moves supplier security, privacy, resilience and product assurance into the buying decision. This flagship guide shows how Clarysec maps ISO/IEC 27001:2022 supplier controls to NIS2, DORA, GDPR, CRA expectations, NIST CSF 2.0 and COBIT-oriented audit evidence before contracts are signed.
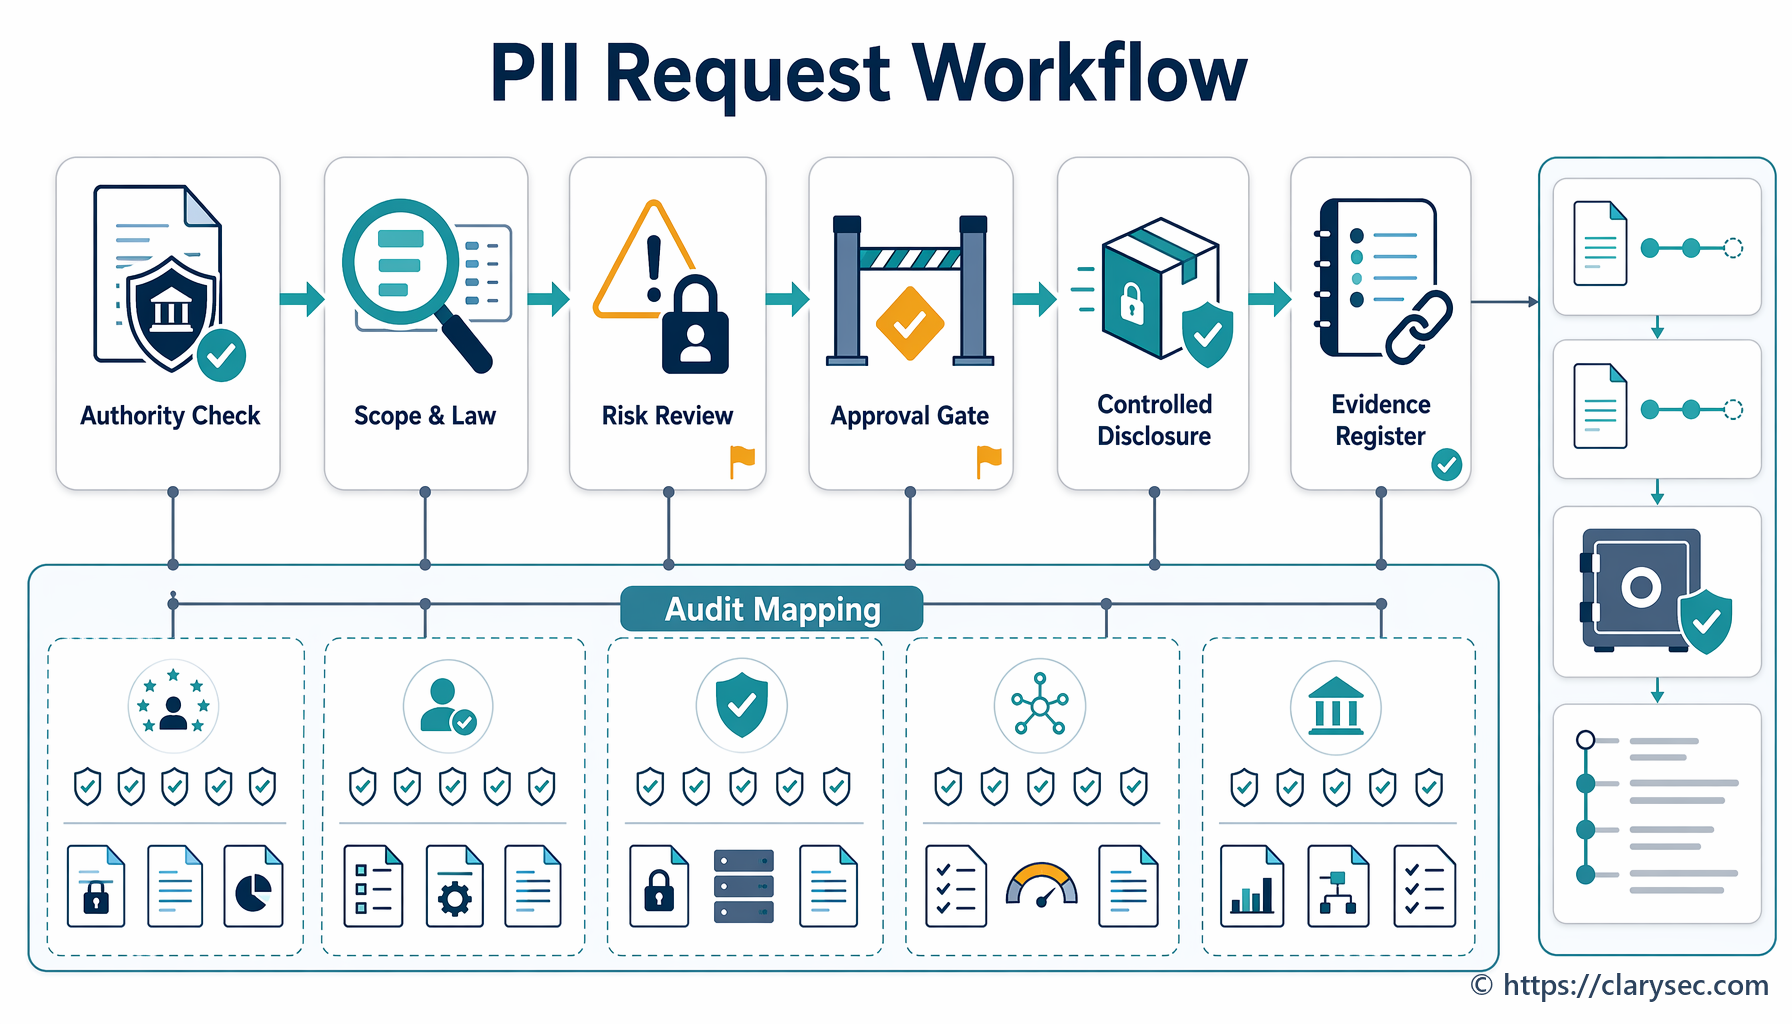
A practical governance model for validating, approving, minimizing, securely disclosing, recording, and evidencing law enforcement and regulator PII disclosure requests under GDPR, ISO 27701:2025, ISO/IEC 27001:2022, NIS2, DORA, NIST, COBIT 2019, and Clarysec policy toolkits.
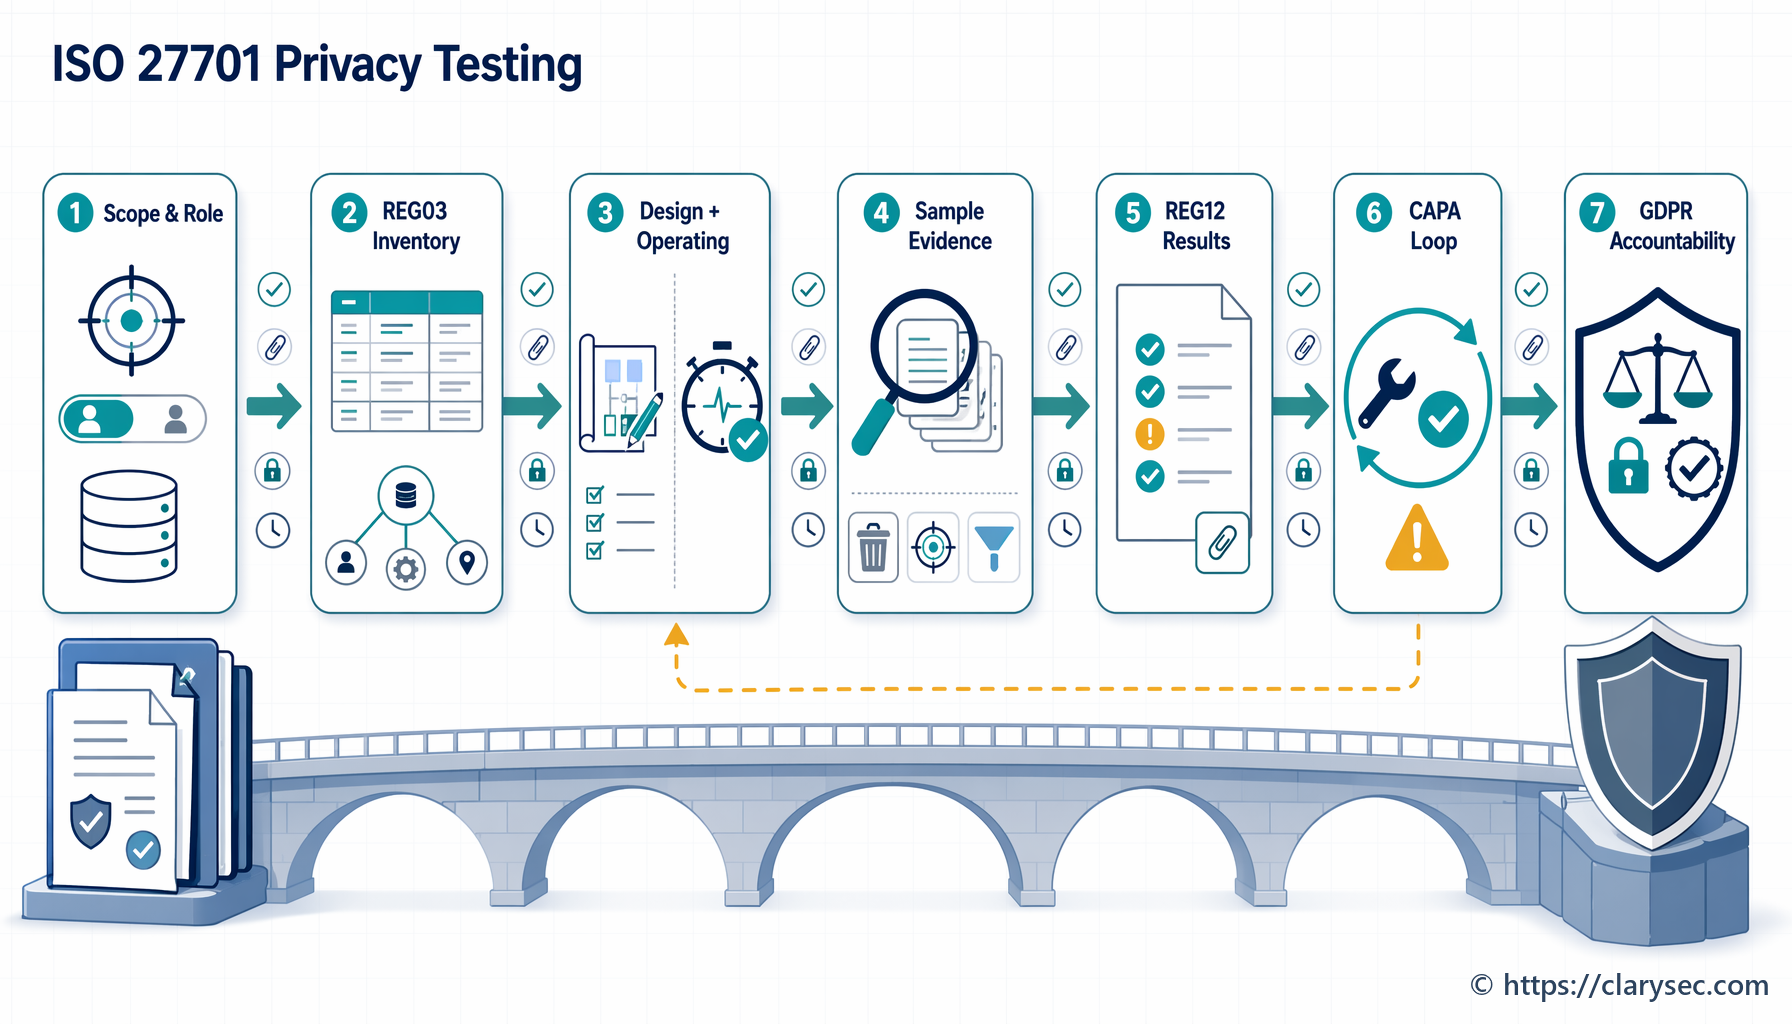
A practical Clarysec guide for CISOs, DPOs, auditors, and compliance teams that need to test ISO 27701:2025 PIMS controls, prove GDPR accountability, and prepare evidence for customers, regulators, and certification audits.
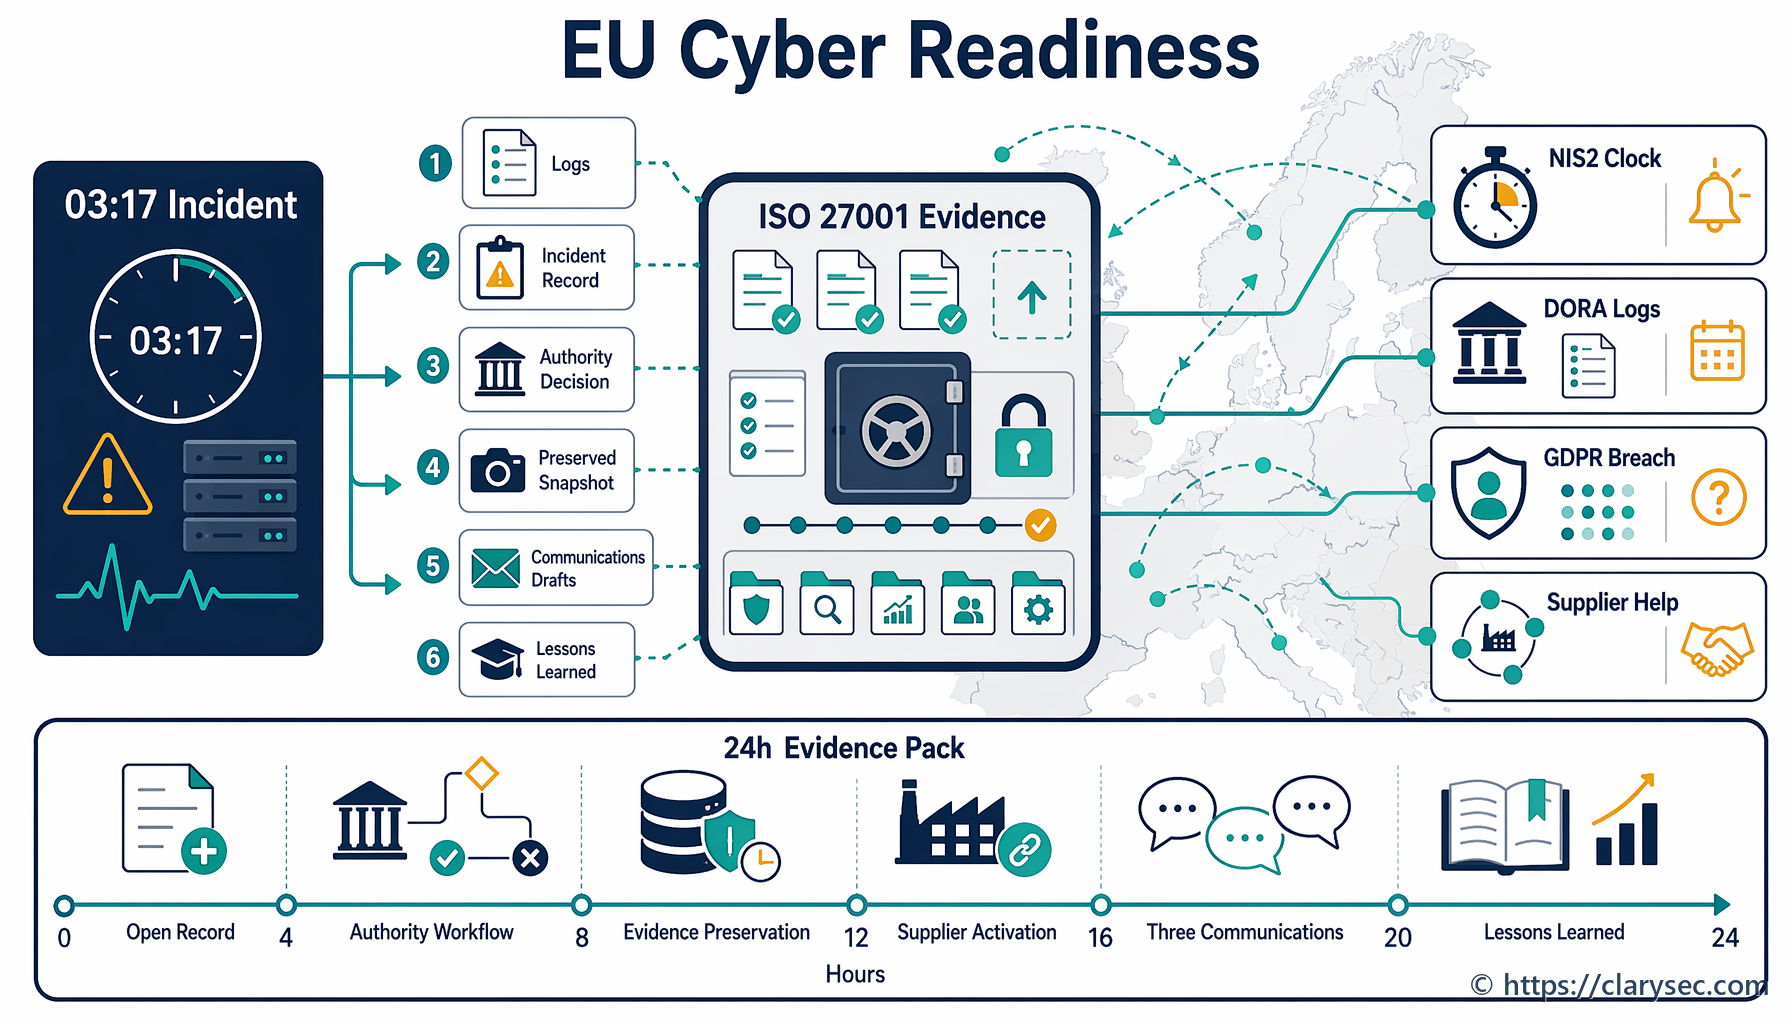
A practical guide to preparing for the EU Cyber Solidarity Act using ISO/IEC 27001:2022 evidence, Clarysec policies, supplier governance, incident response, logging, continuity and cross-compliance mapping for NIS2, DORA, GDPR, NIST CSF 2.0 and COBIT 2019.
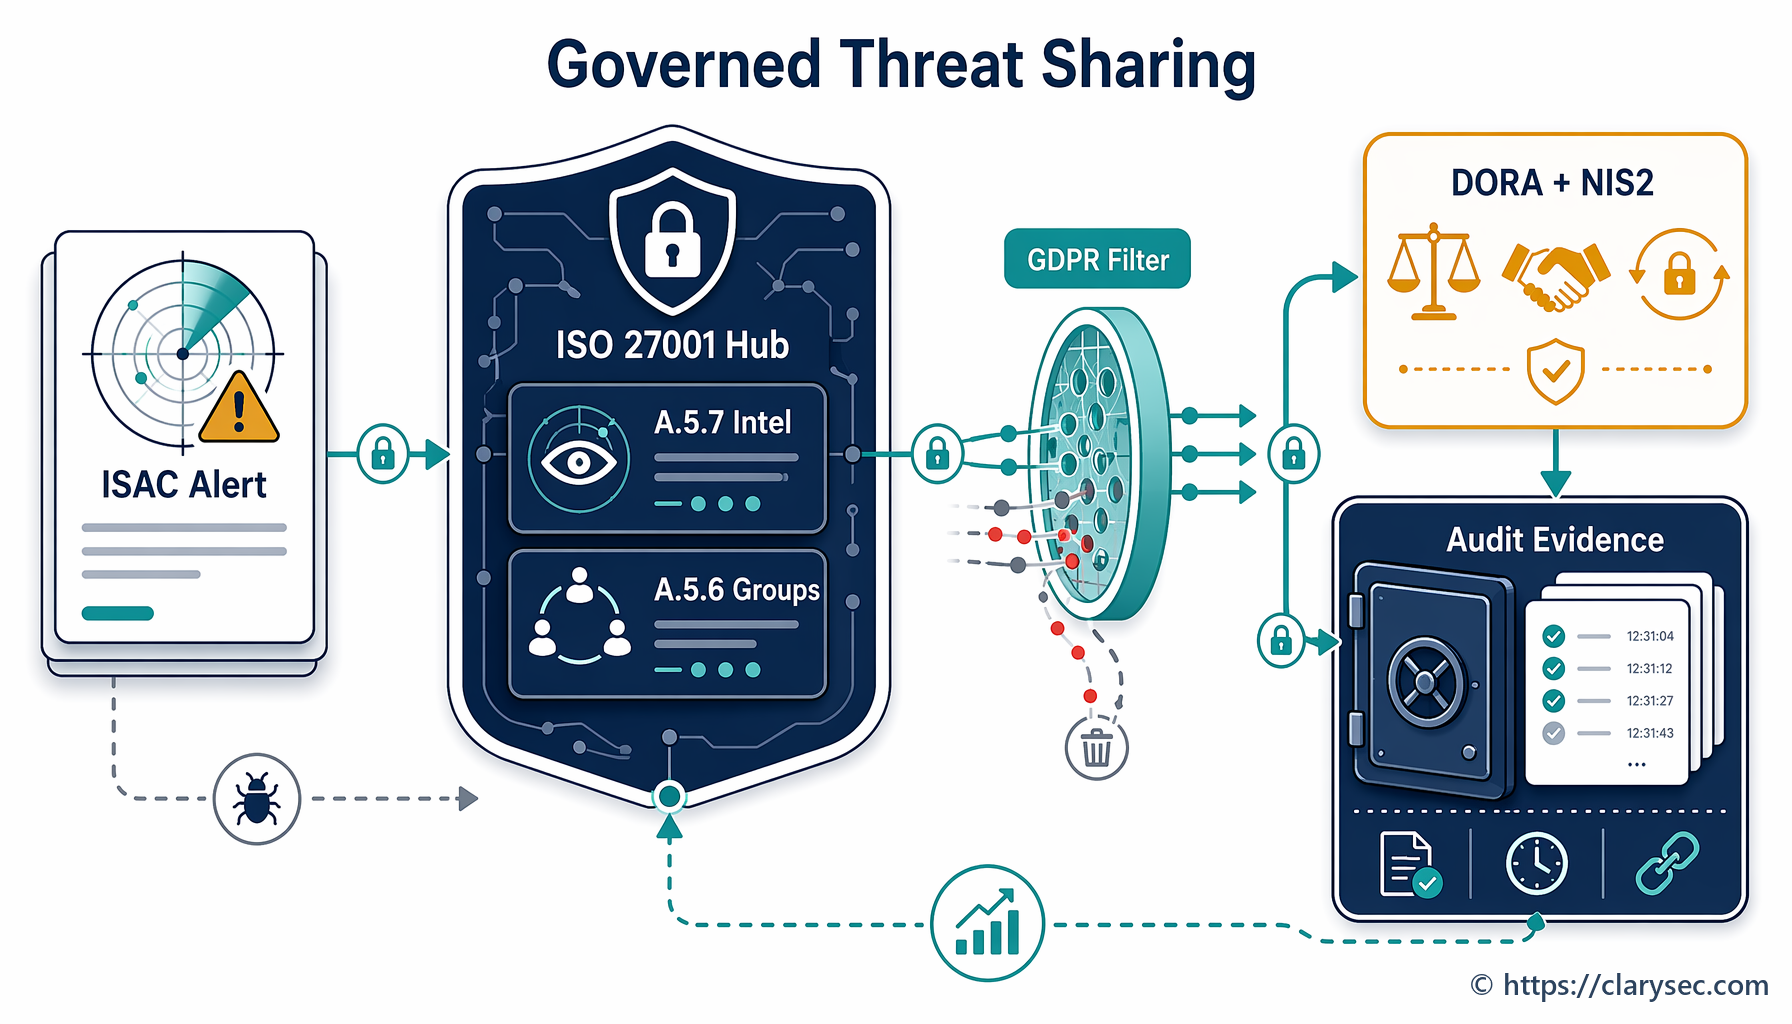
A practical Clarysec guide for building ISO 27001-governed cyber threat intelligence sharing that supports DORA Article 45, NIS2 cooperation, GDPR-safe disclosure, ISAC participation, and audit-ready evidence in 2026.
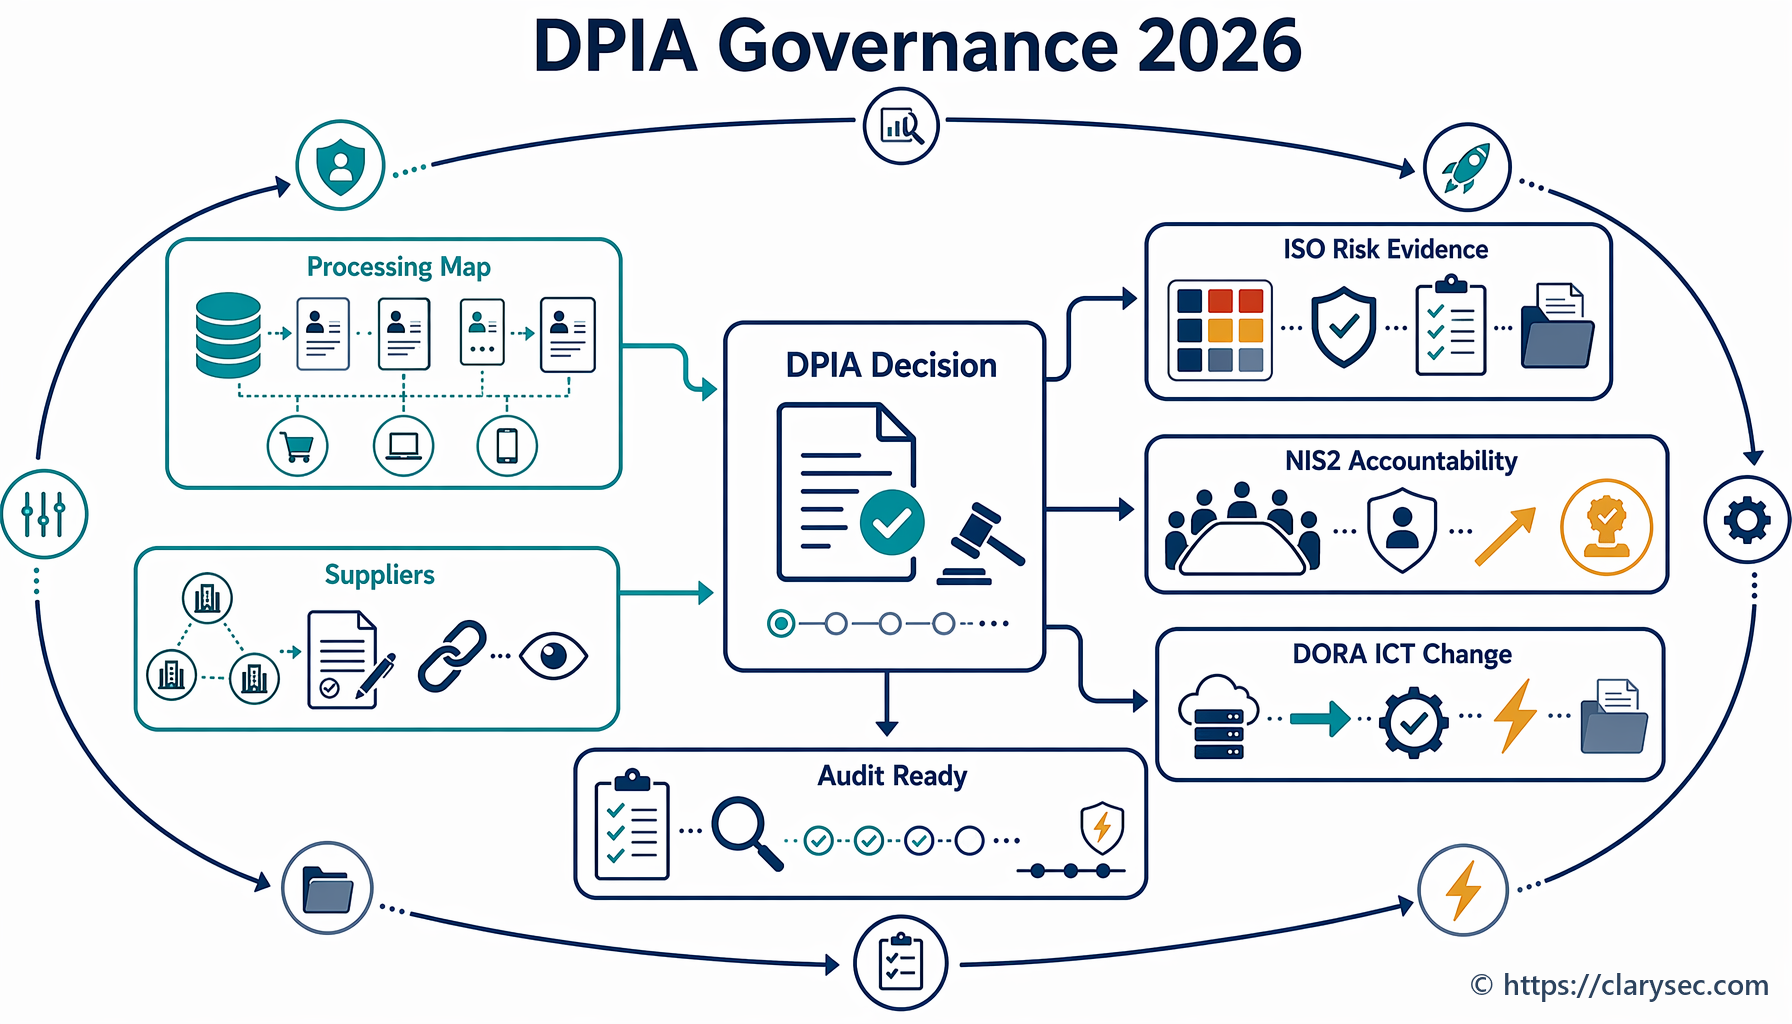
A unified 2026 guide for turning DPIAs into audit-ready governance evidence across GDPR accountability, ISO/IEC 27001:2022, NIS2 cybersecurity measures, DORA ICT change and supplier risk.
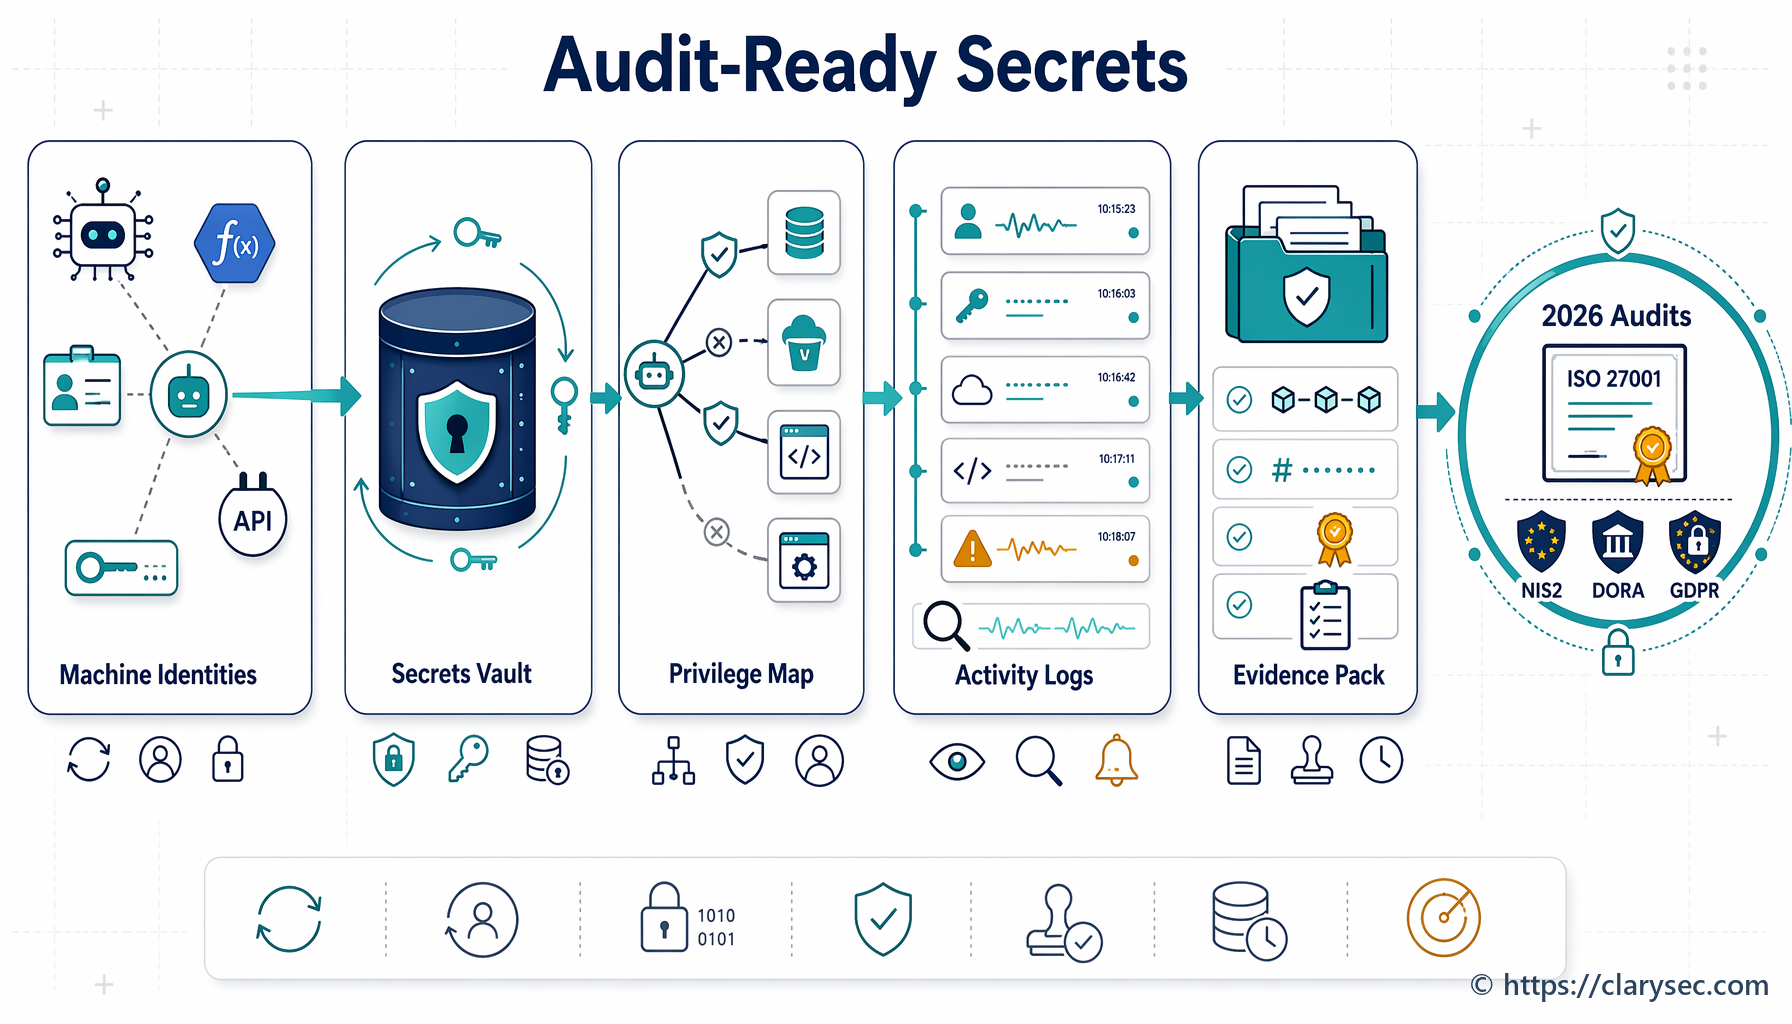
A practical, audit-ready guide to governing non-human identities, API keys, service accounts, CI/CD secrets, certificates and supplier credentials using ISO/IEC 27001:2022 evidence for NIS2, DORA and GDPR.
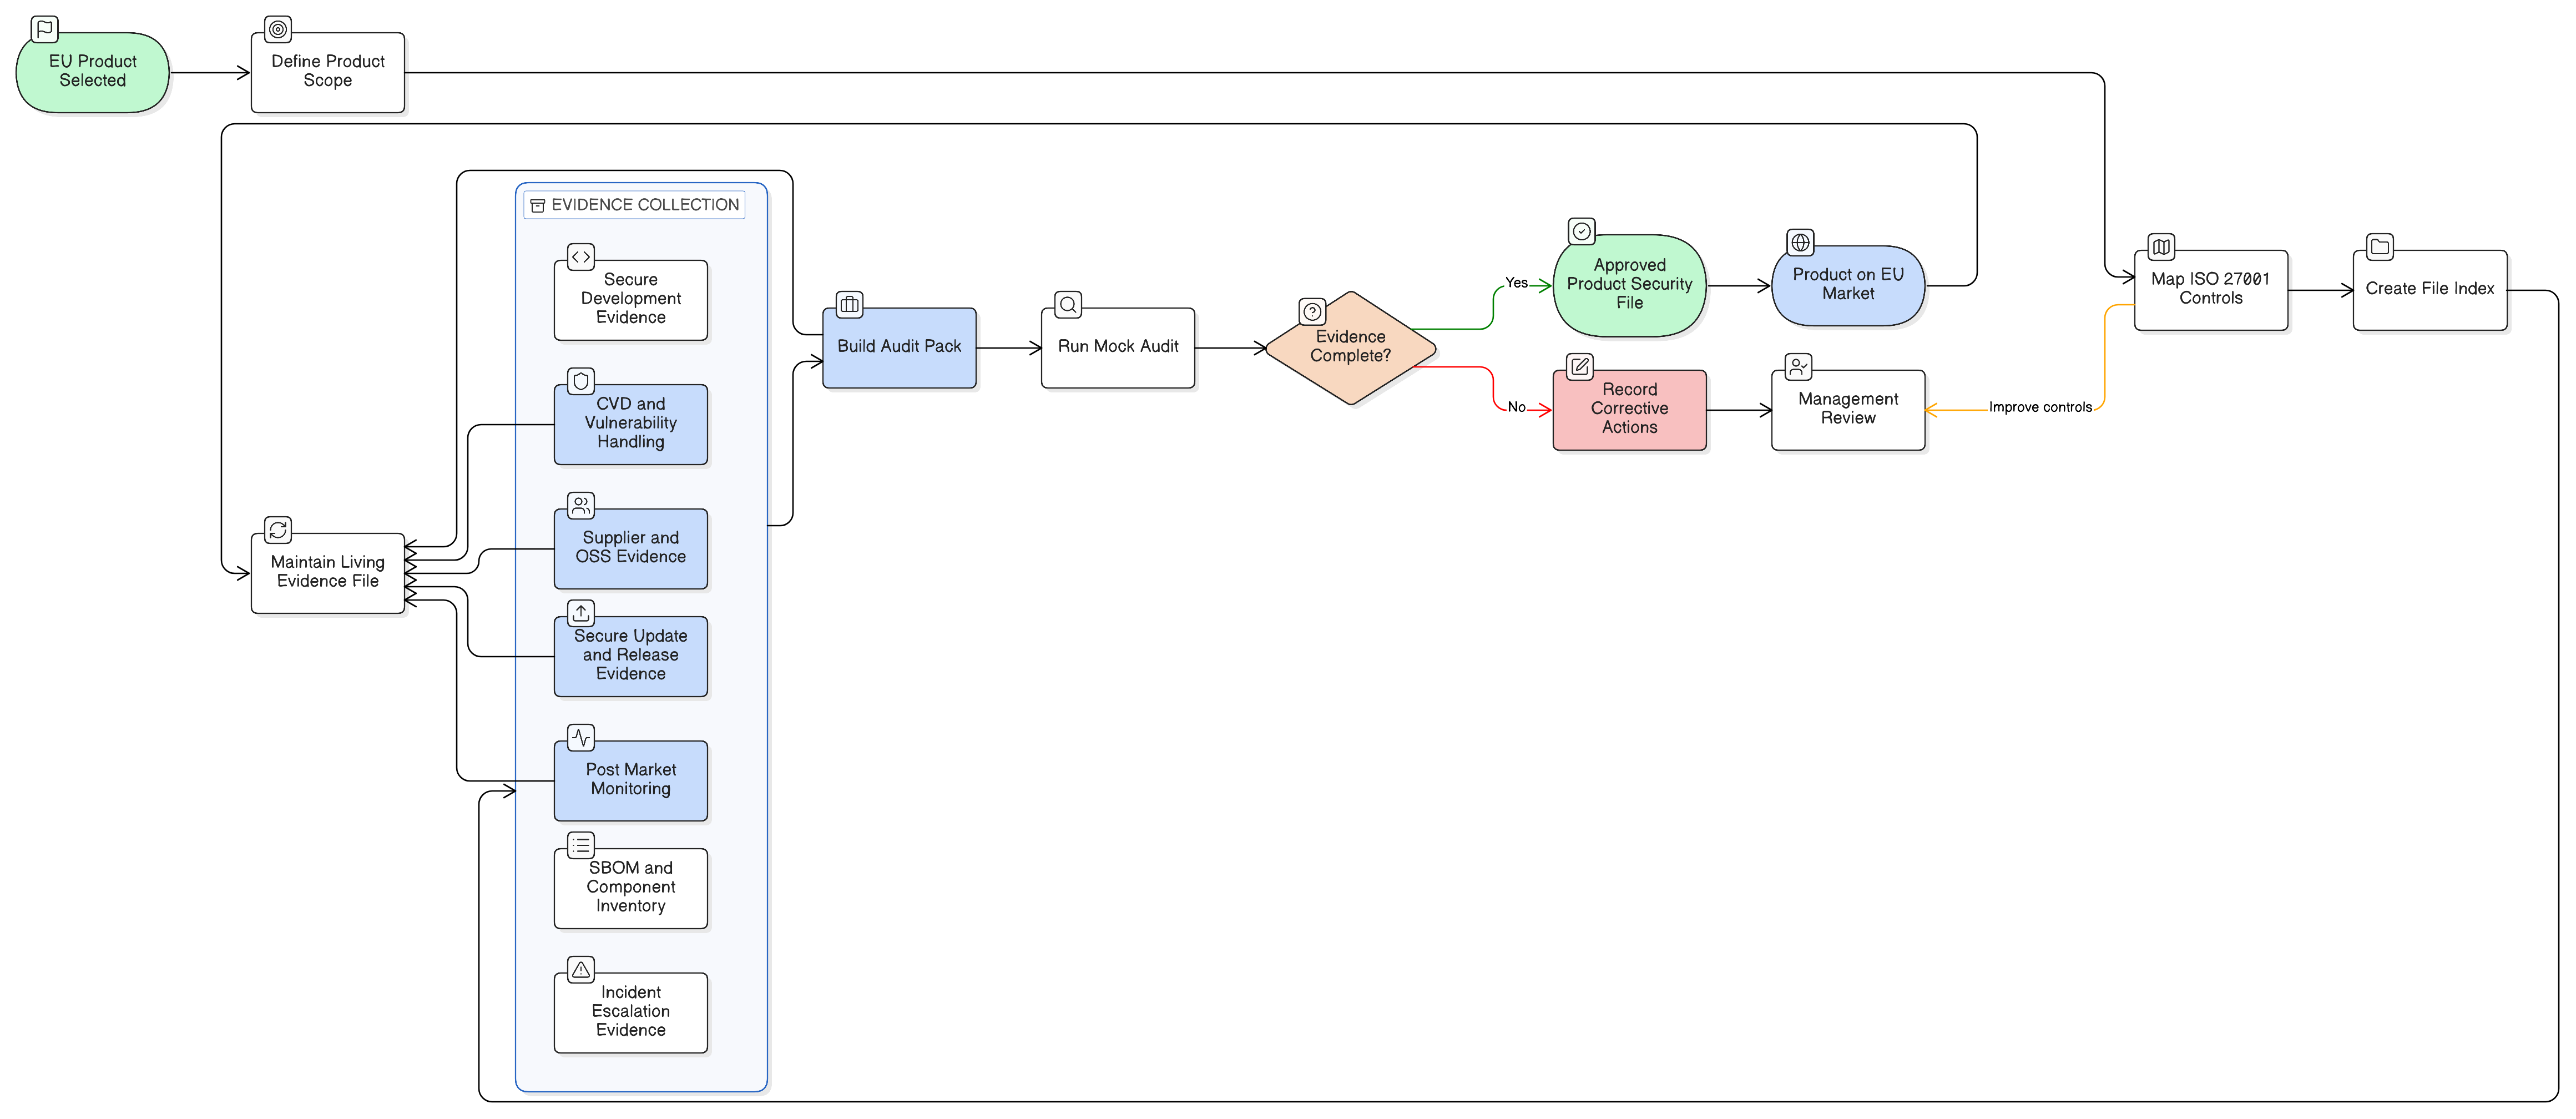
A practical roadmap for building a CRA Product Security File using ISO/IEC 27001:2022, SBOM governance, coordinated vulnerability disclosure, supplier evidence and post-market monitoring.