COBIT 2019
Explore articles in the COBIT 2019 category
96 articles
Turn cryptographic control exceptions from audit risk into proof of ISMS maturity. This flagship guide unites narrative and technical detail, with policy clauses, control mappings, and actionable evidence checklists.
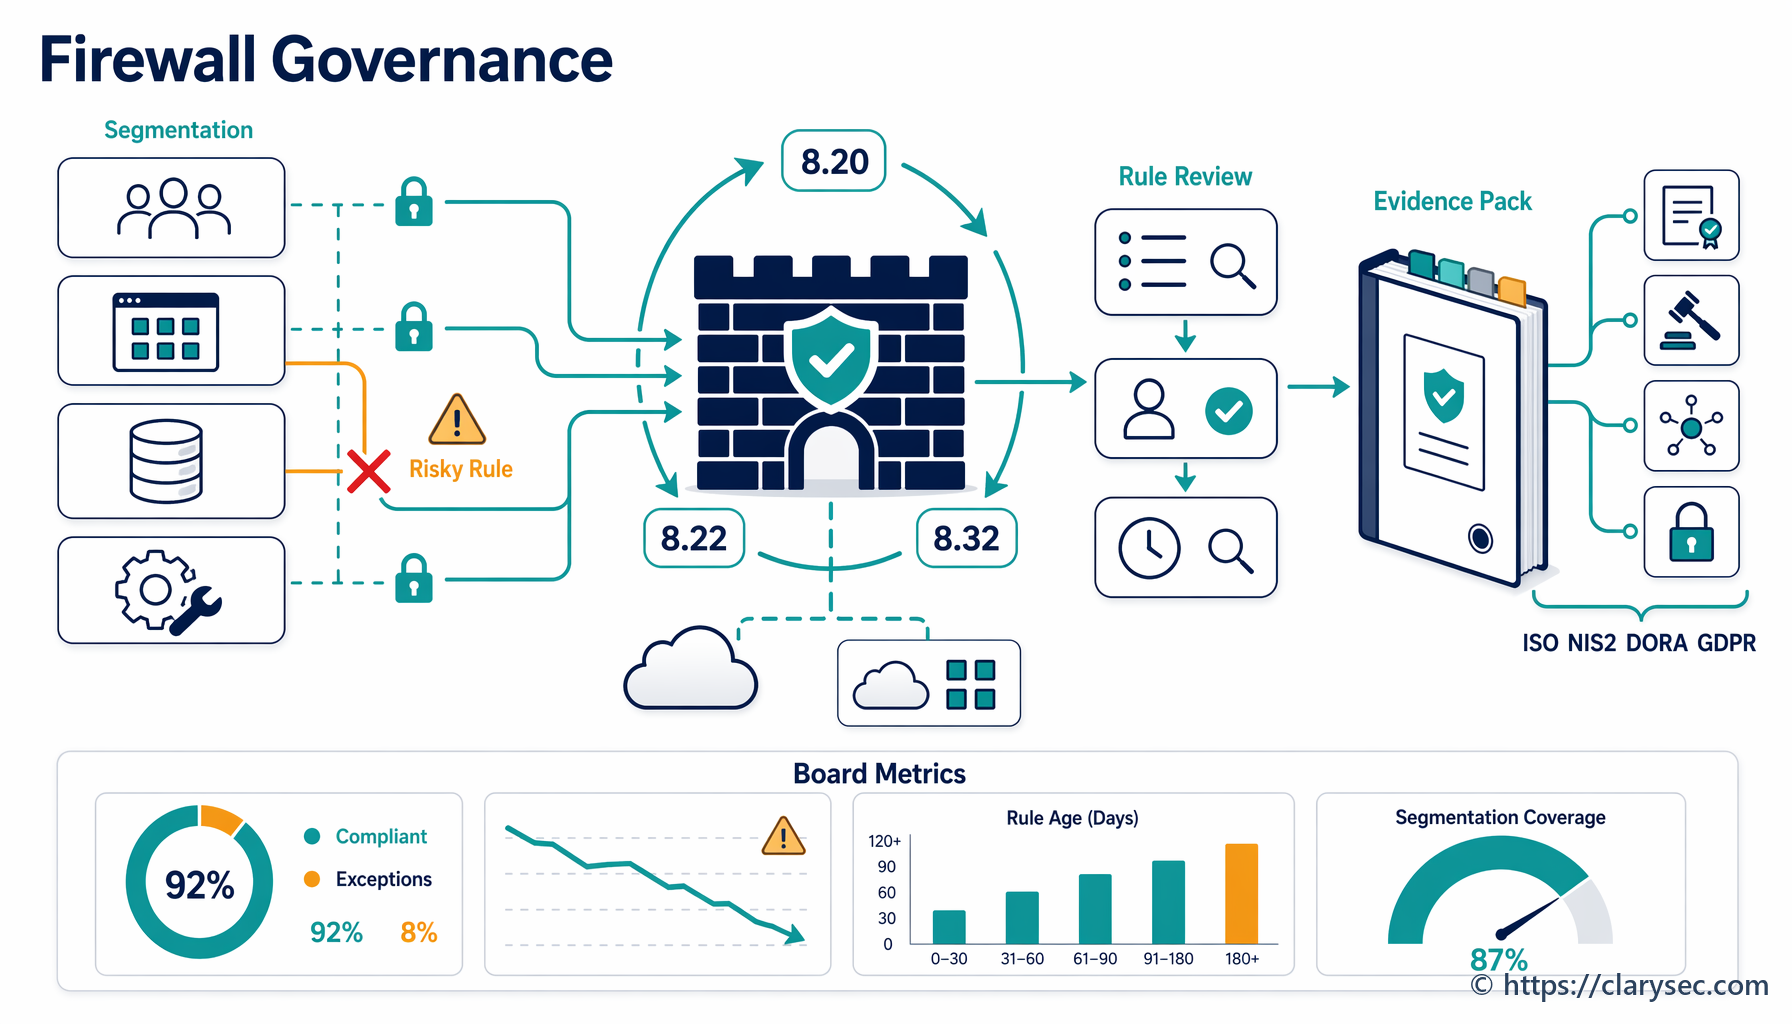
A practical guide to governing network segmentation and firewall rule reviews as ISO/IEC 27001:2022 evidence for NIS2 cyber hygiene, DORA ICT risk management and GDPR Article 32.
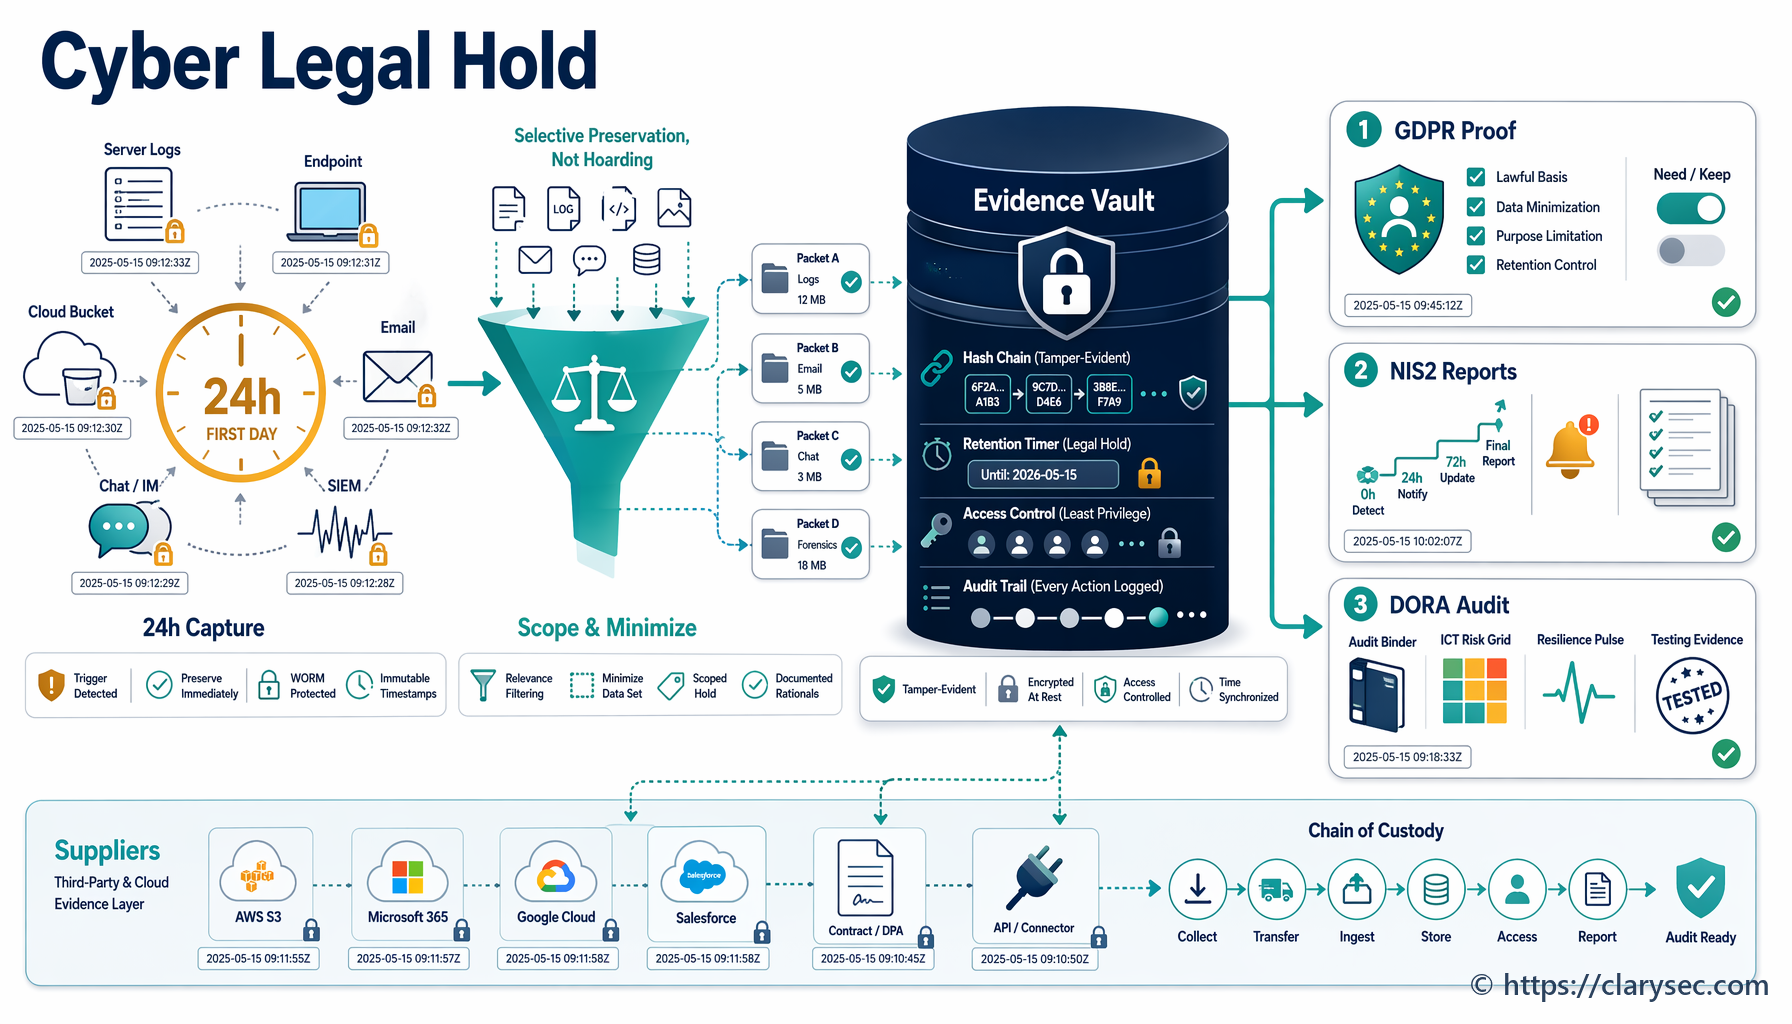
A practical CISO guide to cyber incident legal hold and evidence retention, mapped to ISO/IEC 27001:2022, GDPR, NIS2, DORA, NIST CSF 2.0 and COBIT 2019.
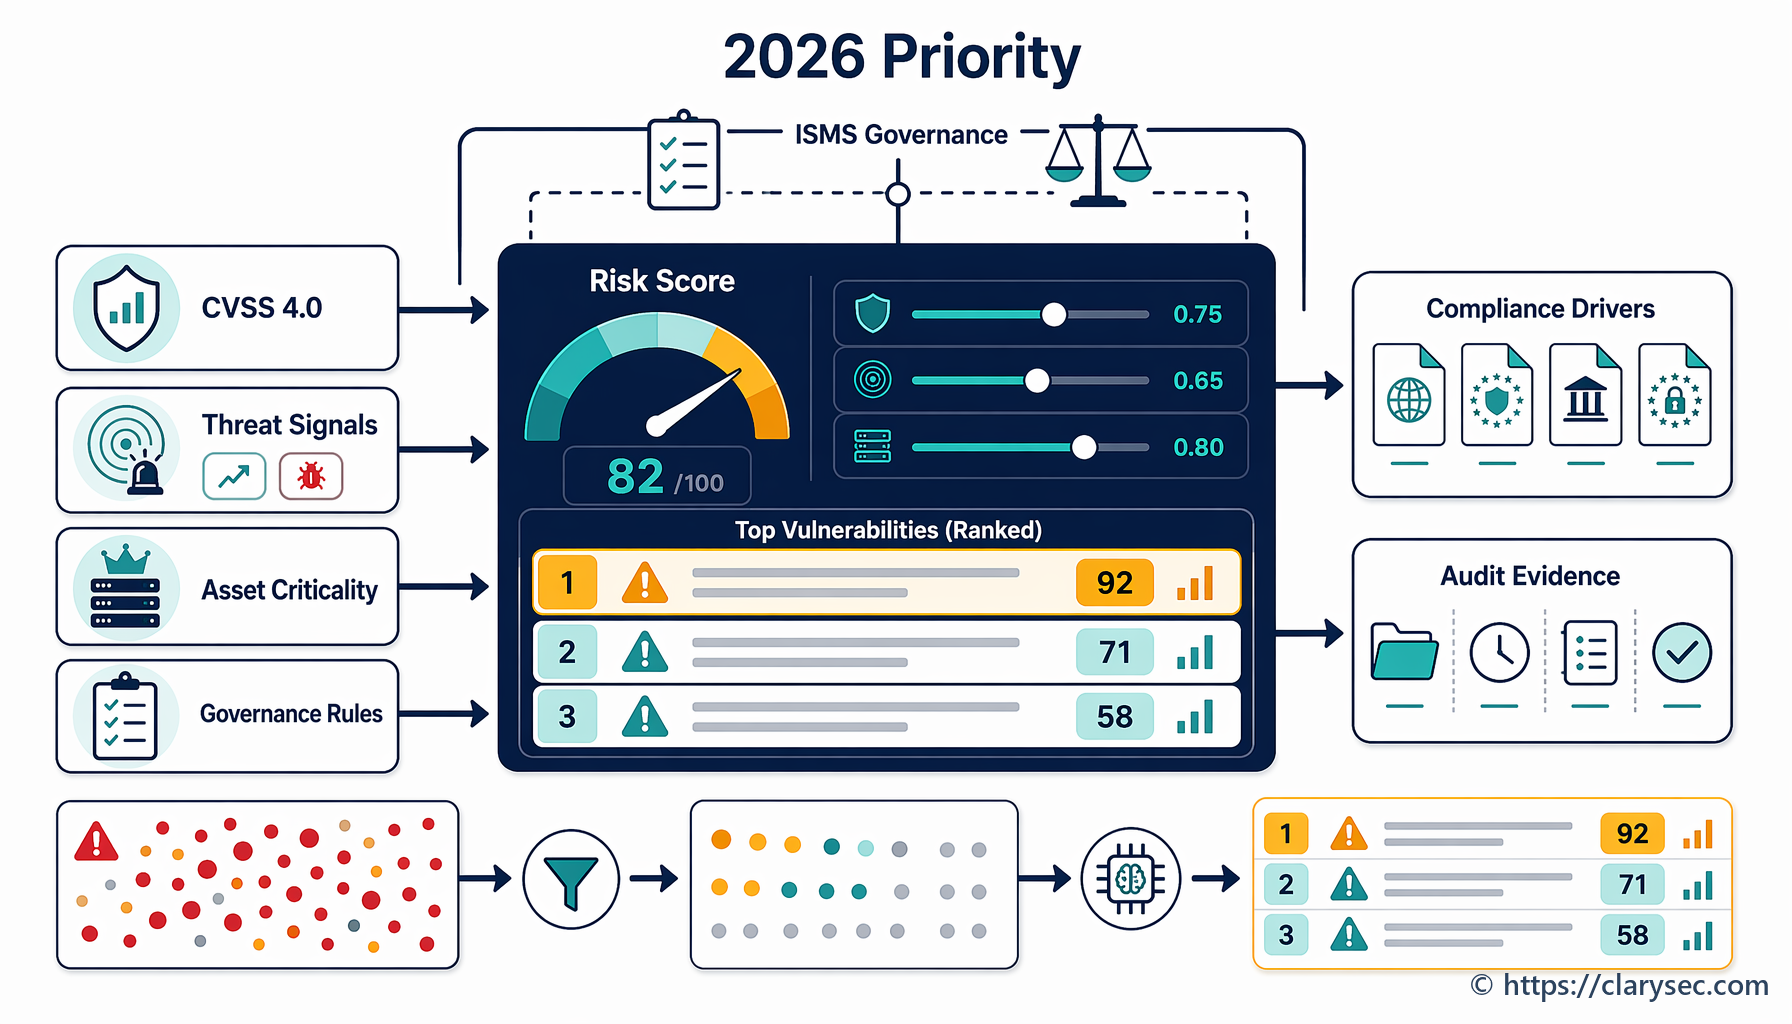
A practical CISO guide to audit-ready, risk-based vulnerability prioritization using CVSS 4.0, EPSS, KEV, EUVD, asset criticality, ISO 27001, NIS2, DORA, GDPR, NIST and COBIT.
A unified NIS2 Implementing Regulation 2024/2690 to ISO/IEC 27001:2022 control mapping for cloud, MSP, MSSP and data centre providers. Includes Clarysec policy clauses, audit evidence, DORA and GDPR alignment, and a practical implementation roadmap.
Outsourcing MDR does not outsource accountability. This flagship guide shows how to govern MDR providers with ISO/IEC 27001:2022 evidence mapped to NIS2, DORA, GDPR, NIST CSF 2.0 and COBIT 2019.
Non-production environments are now a serious audit target. This guide shows how to protect test data, staging systems and QA workflows with ISO/IEC 27001:2022 evidence mapped to GDPR, NIS2, DORA, NIST and COBIT.
A flagship guide for CISOs, compliance managers and business leaders who need to turn NIS2 Article 21 technical measures into ISO 27001:2022 controls, policies, owners, records and defensible evidence.
A practical CISO guide for building a quantum-ready cryptography migration plan using ISO/IEC 27001:2022, ISO/IEC 27002:2022, NIST PQC standards, and Clarysec’s audit-ready toolkits.