COBIT 2019
Explore articles in the COBIT 2019 category
96 articles
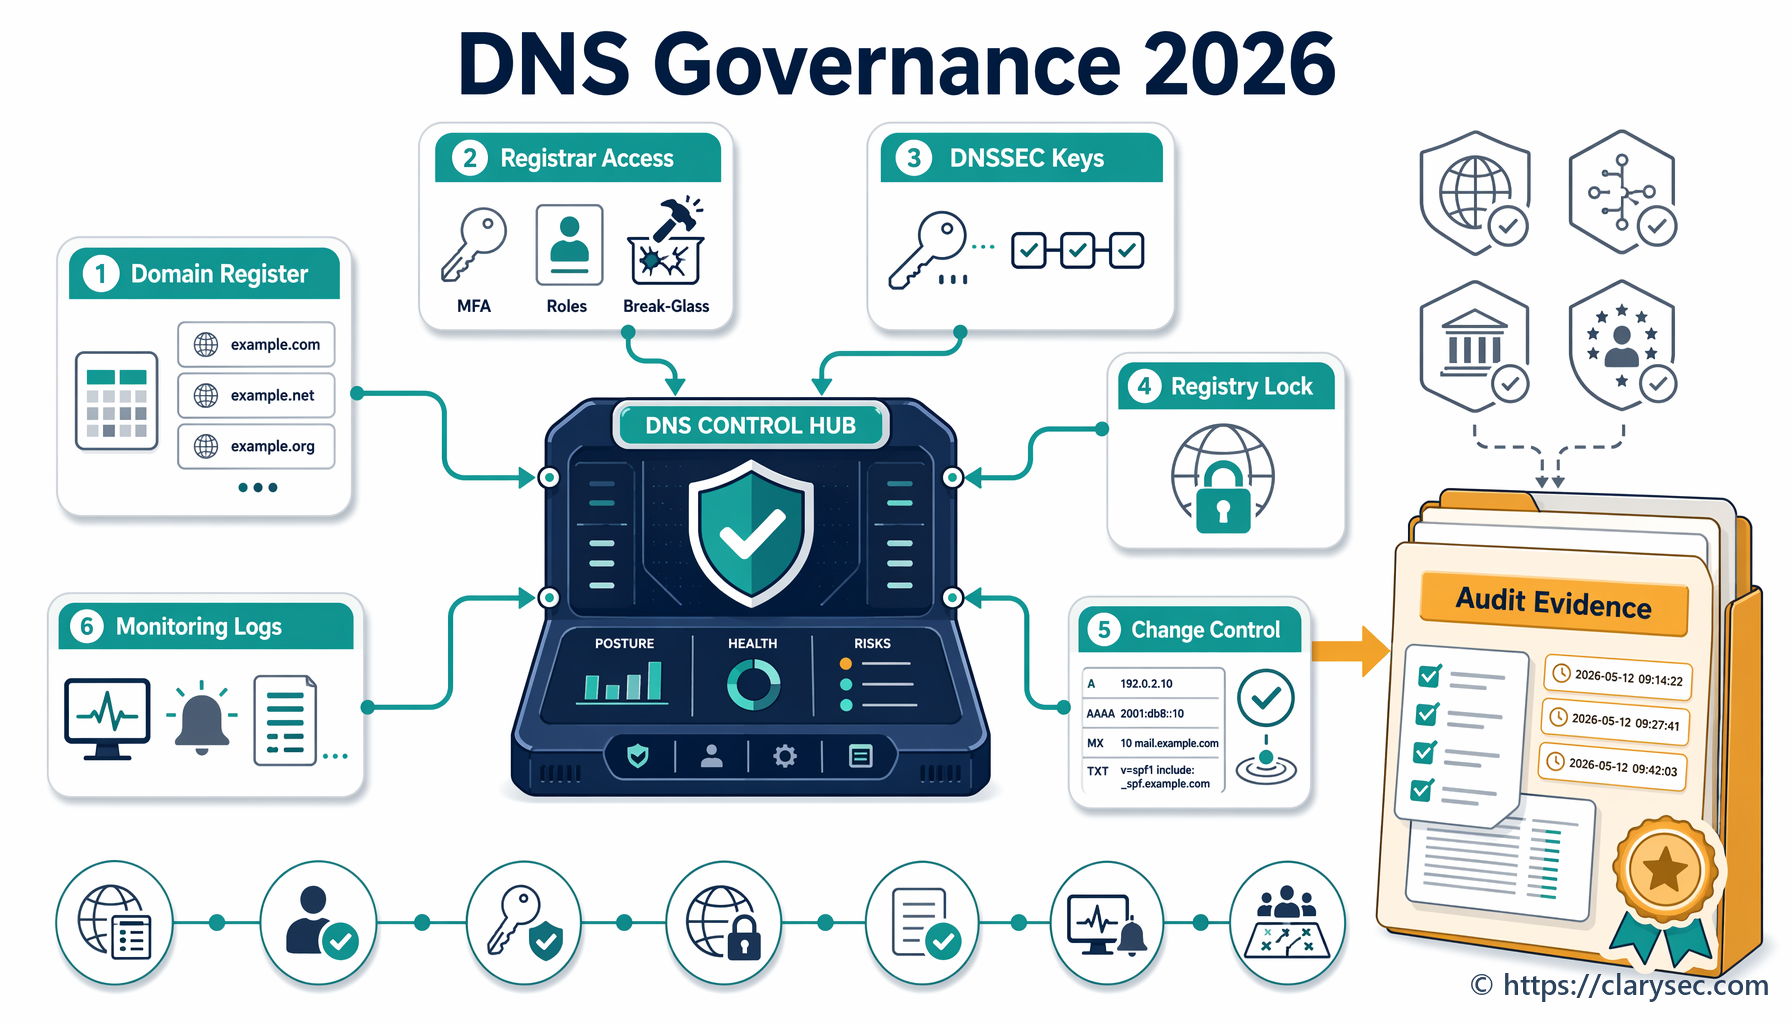
DNS and domain registrar governance is now a board-level resilience issue. This guide shows how to turn DNSSEC, registry lock, registrar access, zone changes and monitoring into defensible compliance evidence.
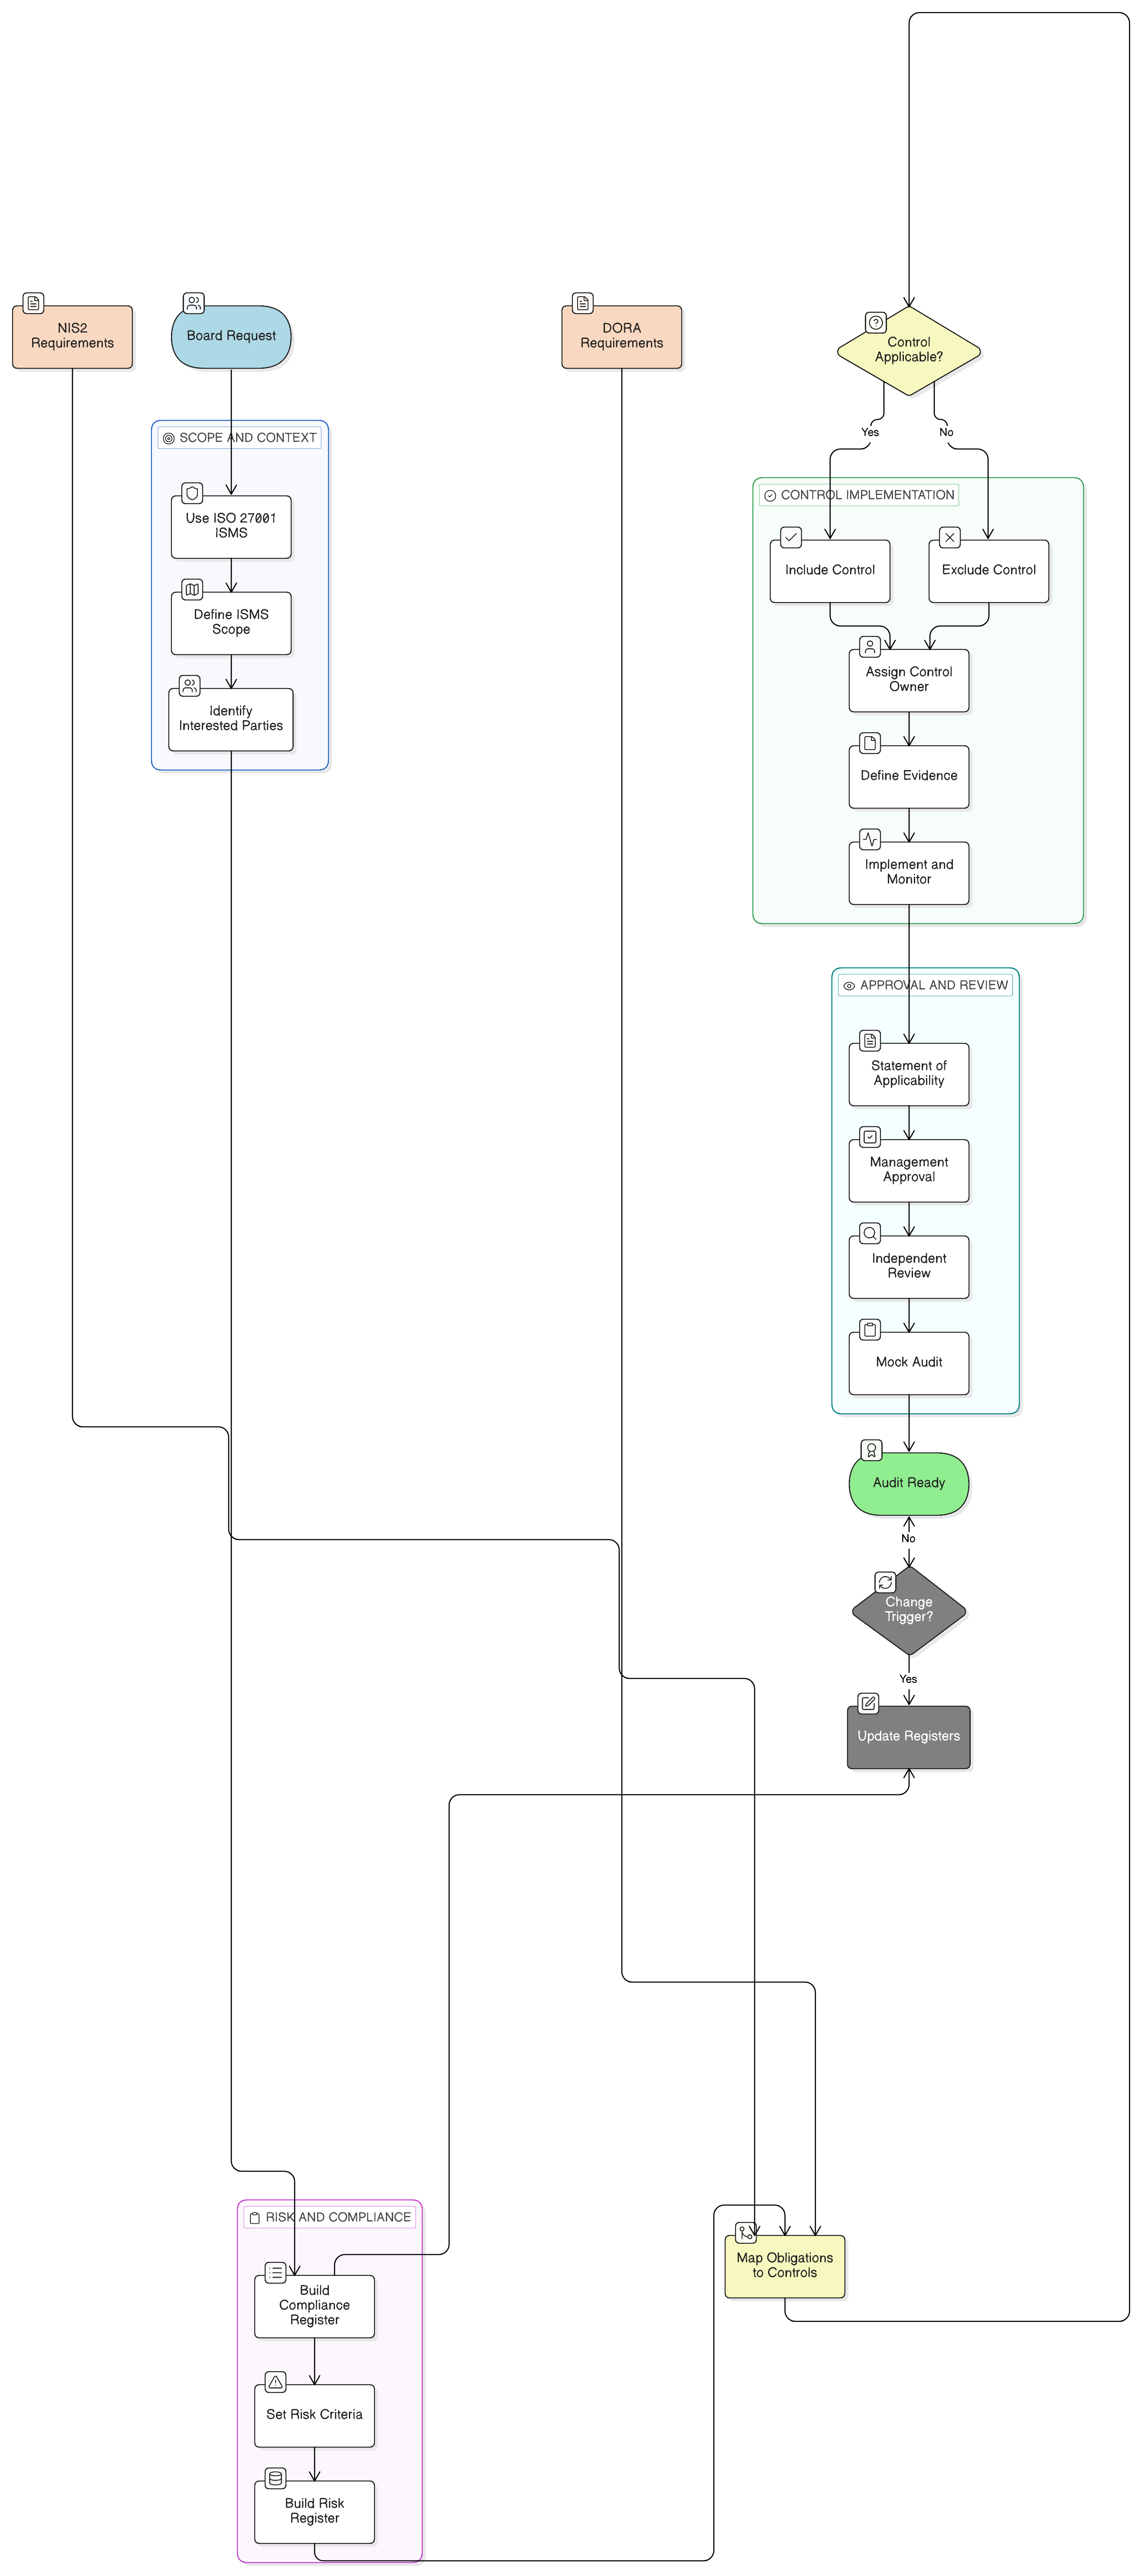
Learn how to use the ISO 27001 Statement of Applicability as an audit-ready bridge between NIS2, DORA, GDPR, risk treatment, suppliers, incident response, and evidence.
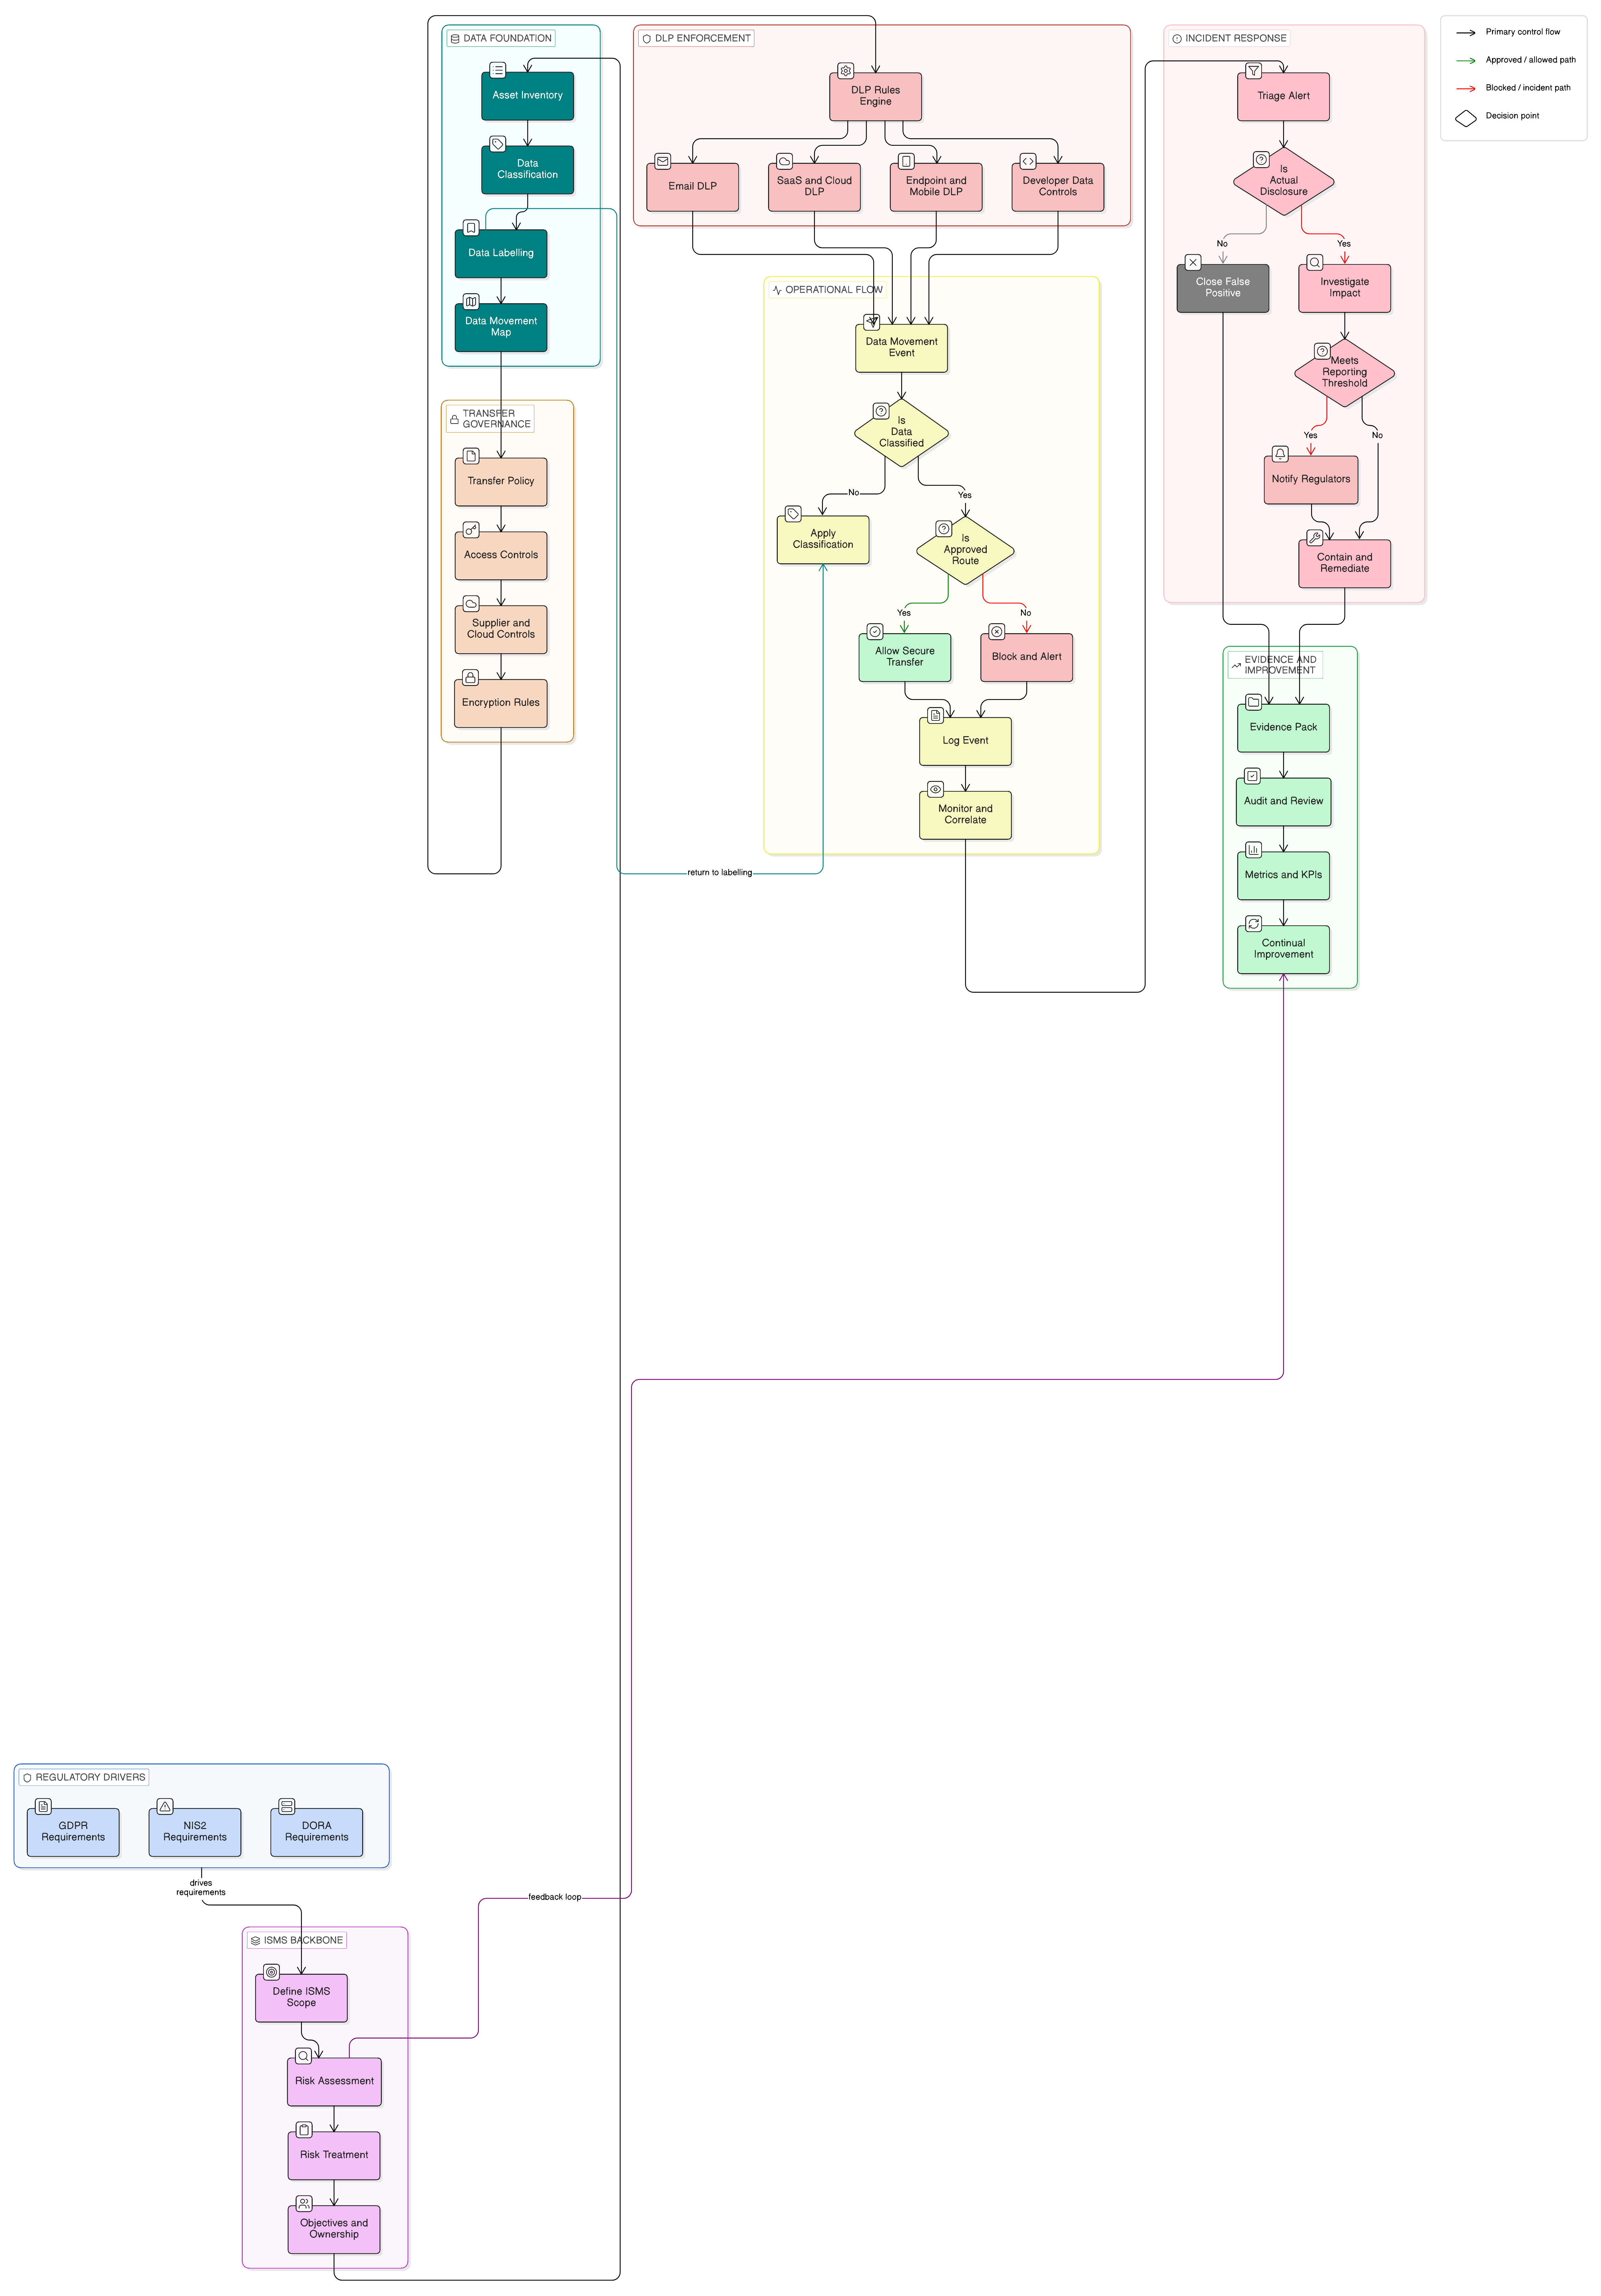
Data Loss Prevention is no longer a standalone tool configuration. In 2026, CISOs need a policy-led, evidence-backed DLP program that connects data classification, secure transfer, logging, incident response, supplier governance and ISO/IEC 27001:2022 controls to GDPR Article 32, NIS2 and DORA.
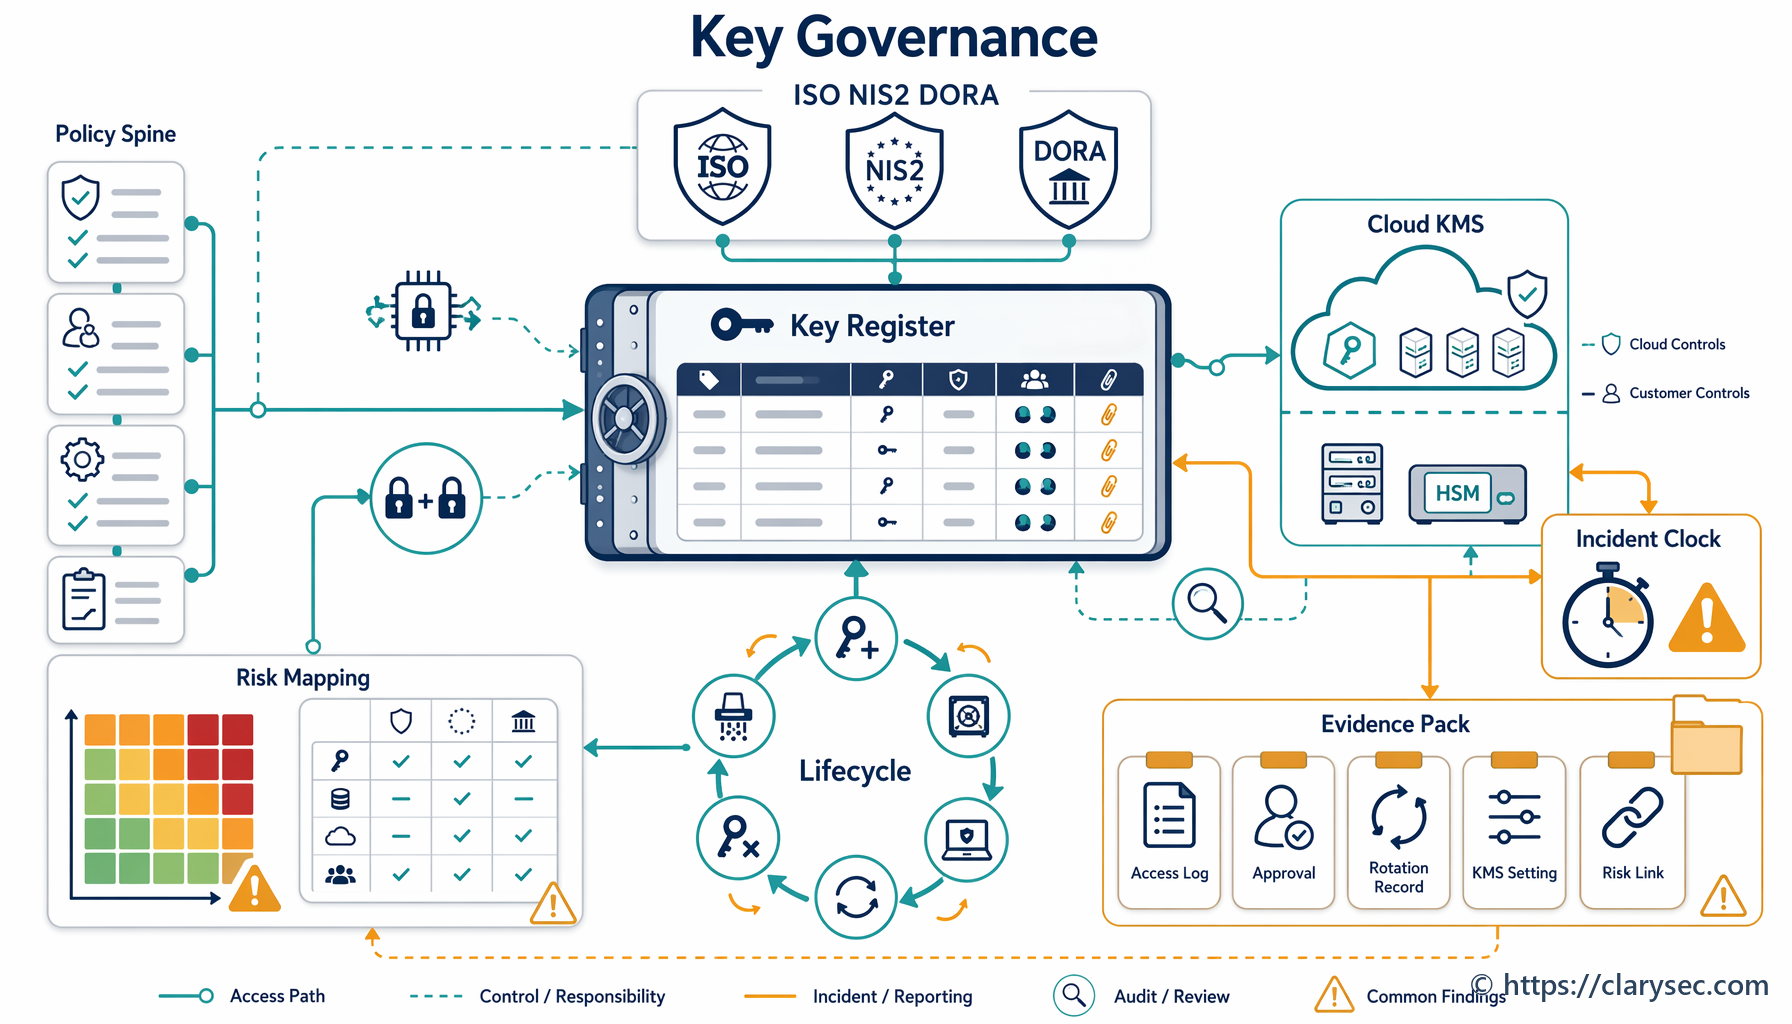
A practical guide to governing cryptographic keys, cloud KMS, HSMs, rotation, recovery and audit evidence through ISO/IEC 27001:2022, NIS2, DORA and GDPR Article 32.
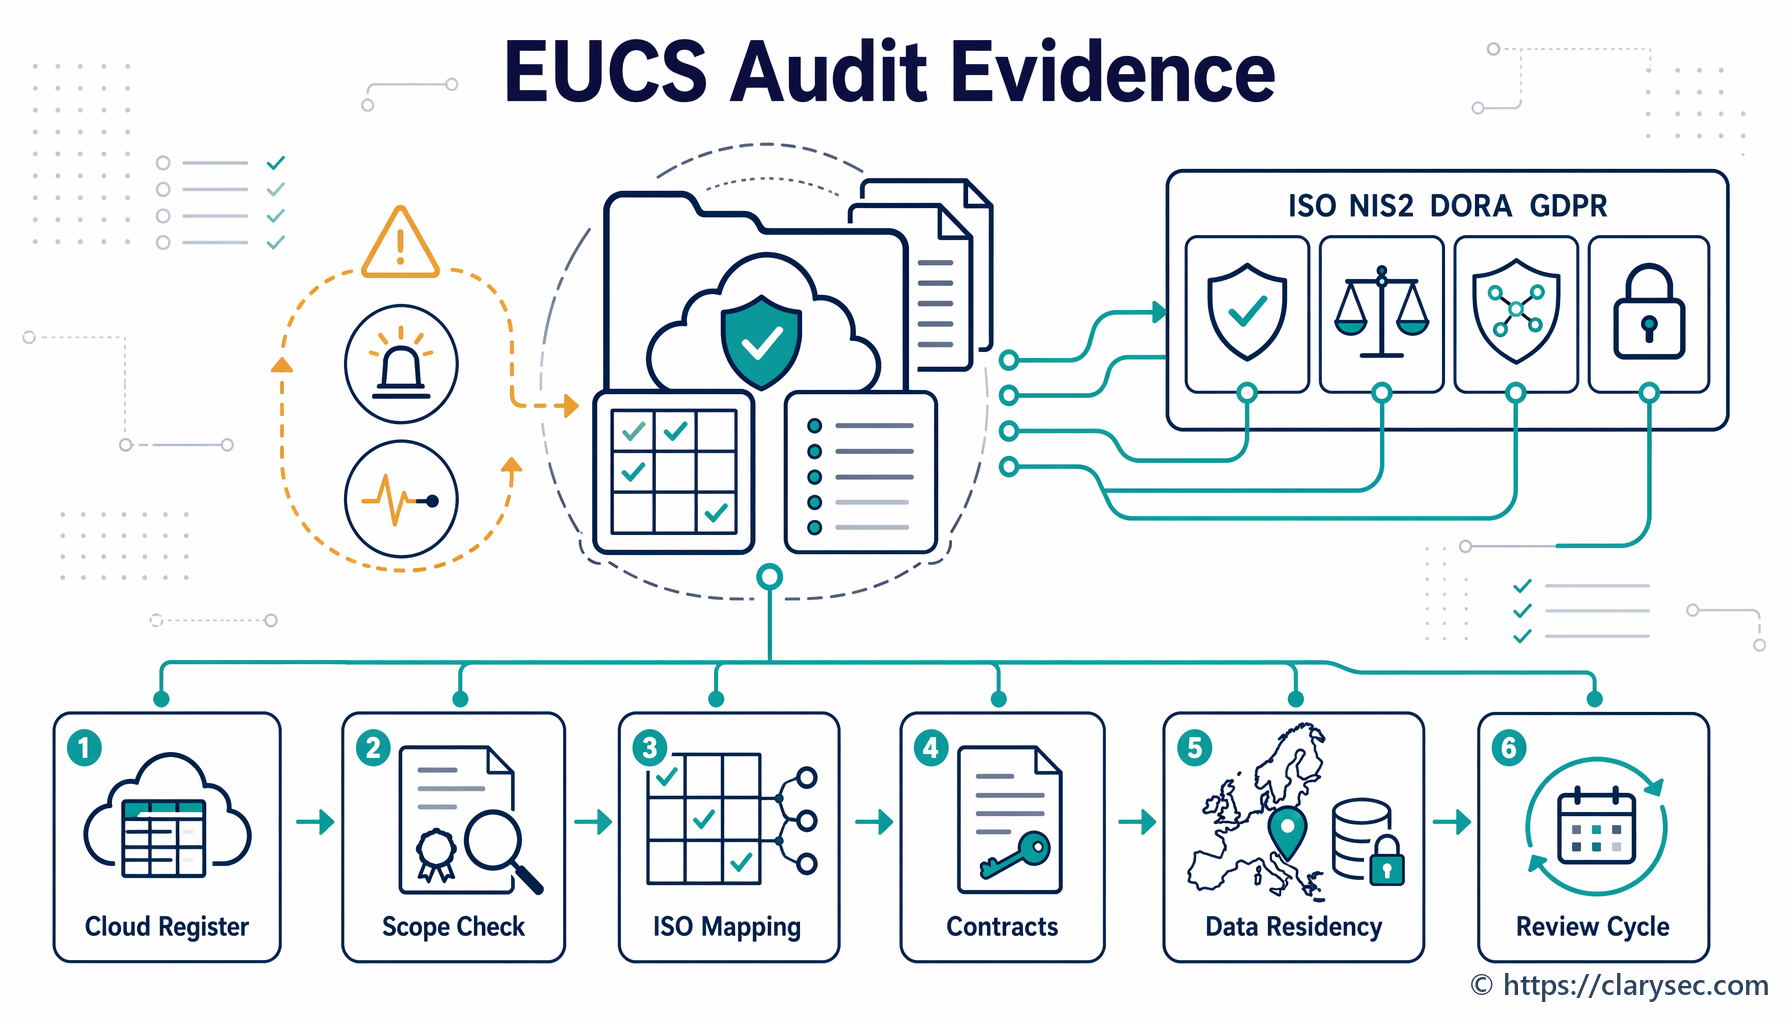
EUCS cloud certification can strengthen cloud provider assurance in 2026, but it must be mapped into your ISO 27001 ISMS, supplier risk process, contracts, incident playbooks and GDPR accountability evidence.
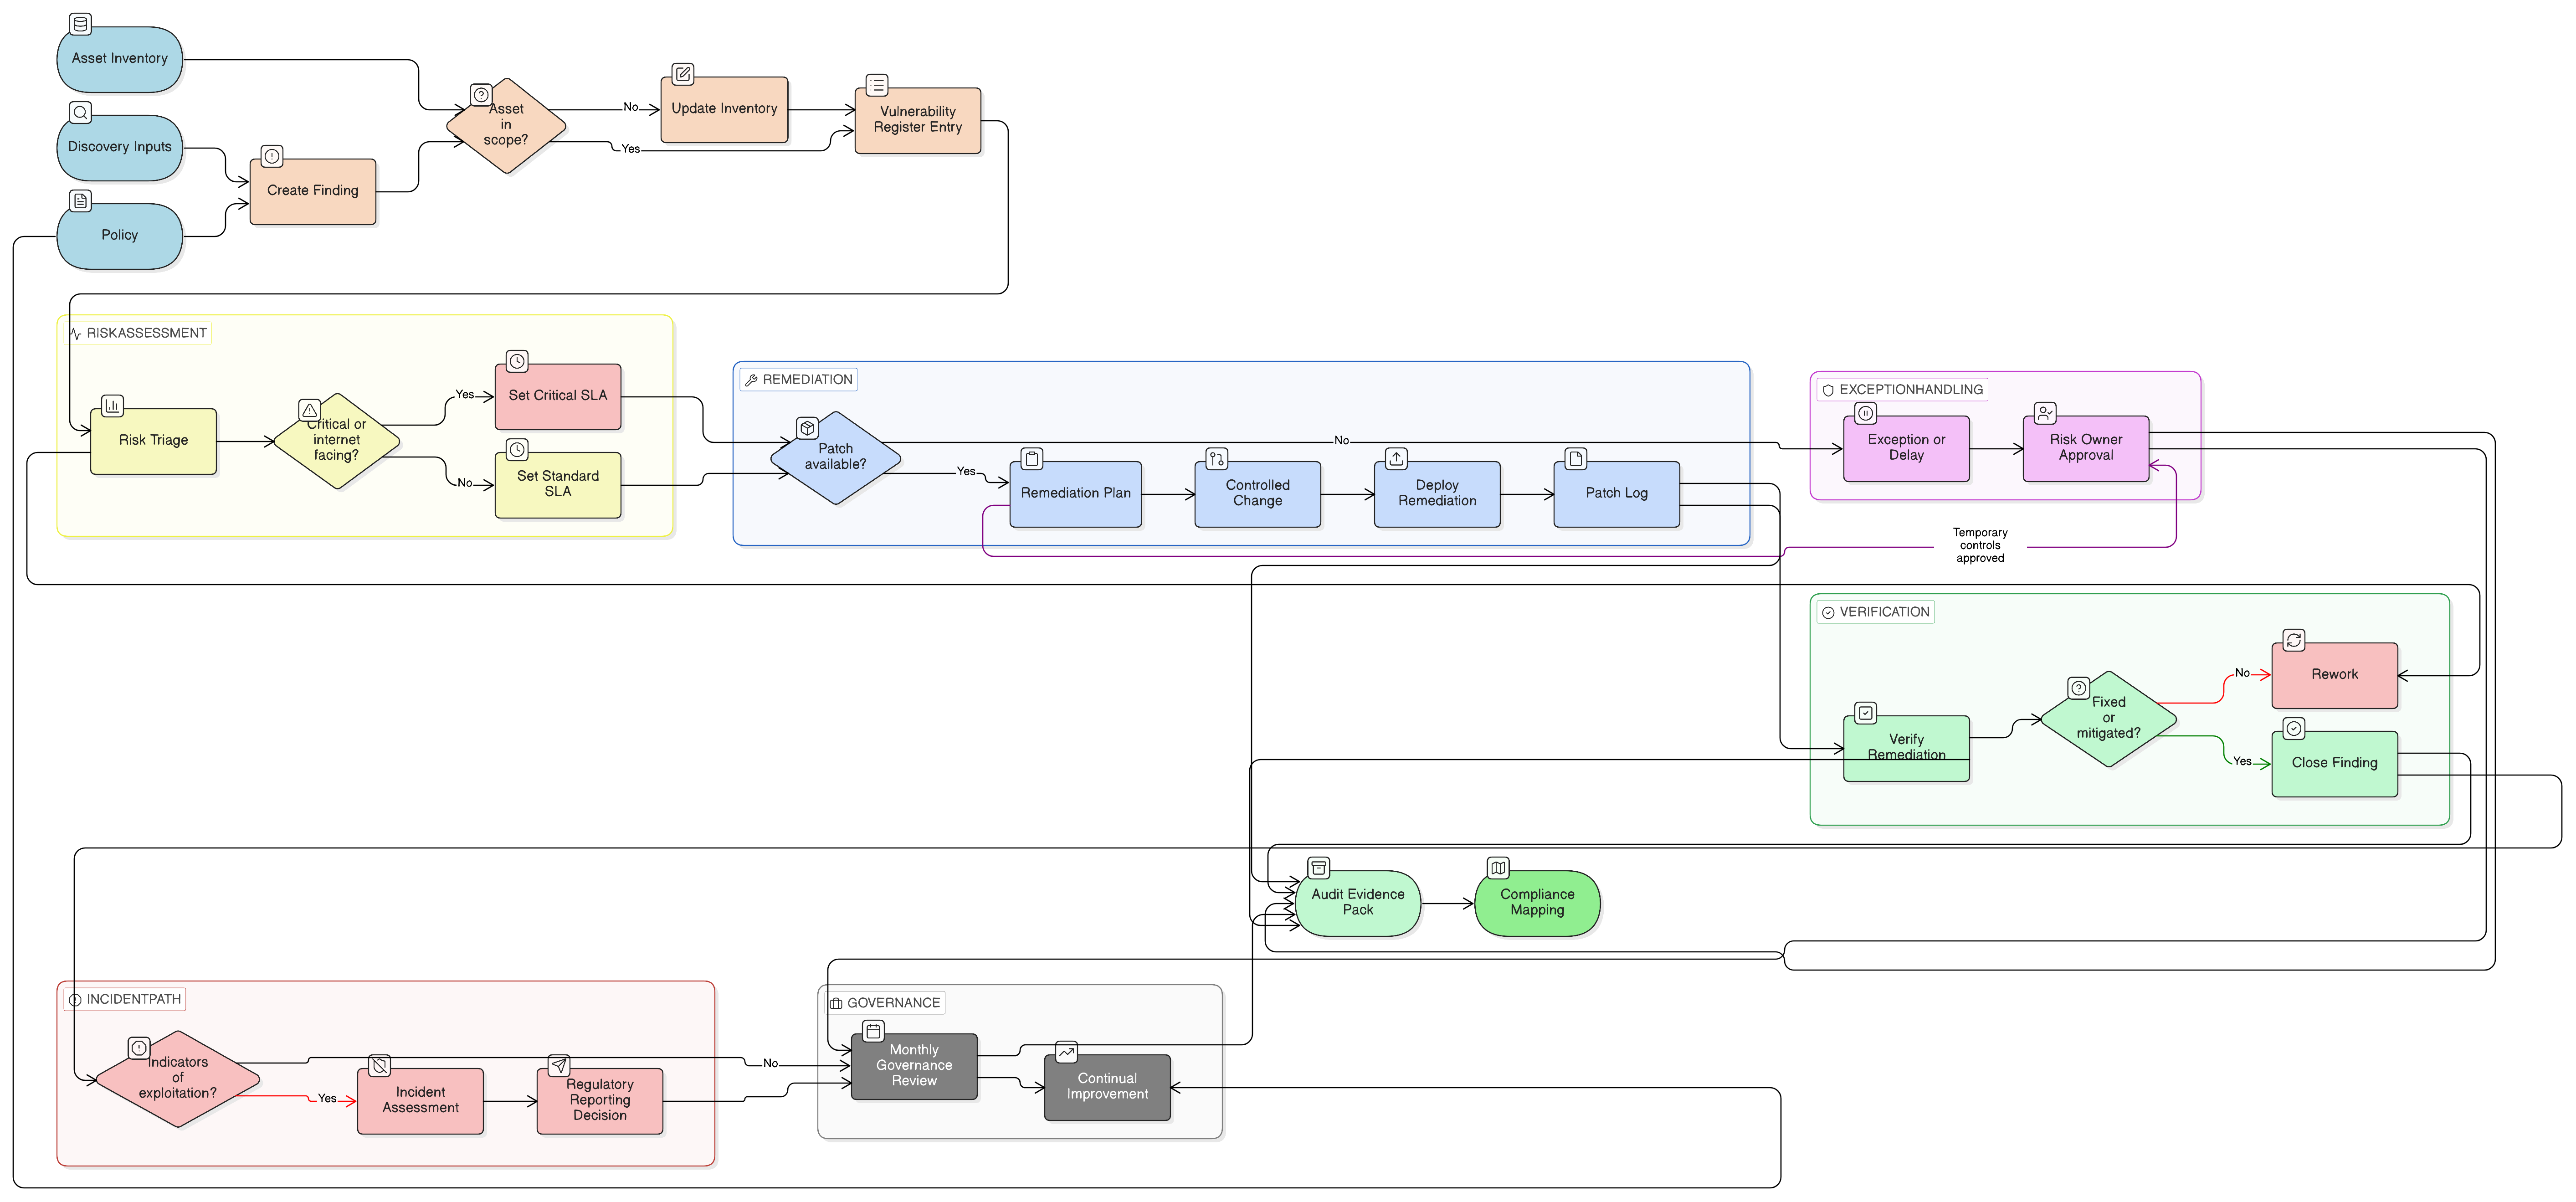
A practical CISO guide to converting vulnerability scans, patch logs, risk decisions and exceptions into audit-ready evidence for ISO 27001:2022, NIS2, DORA, GDPR and COBIT 2019.
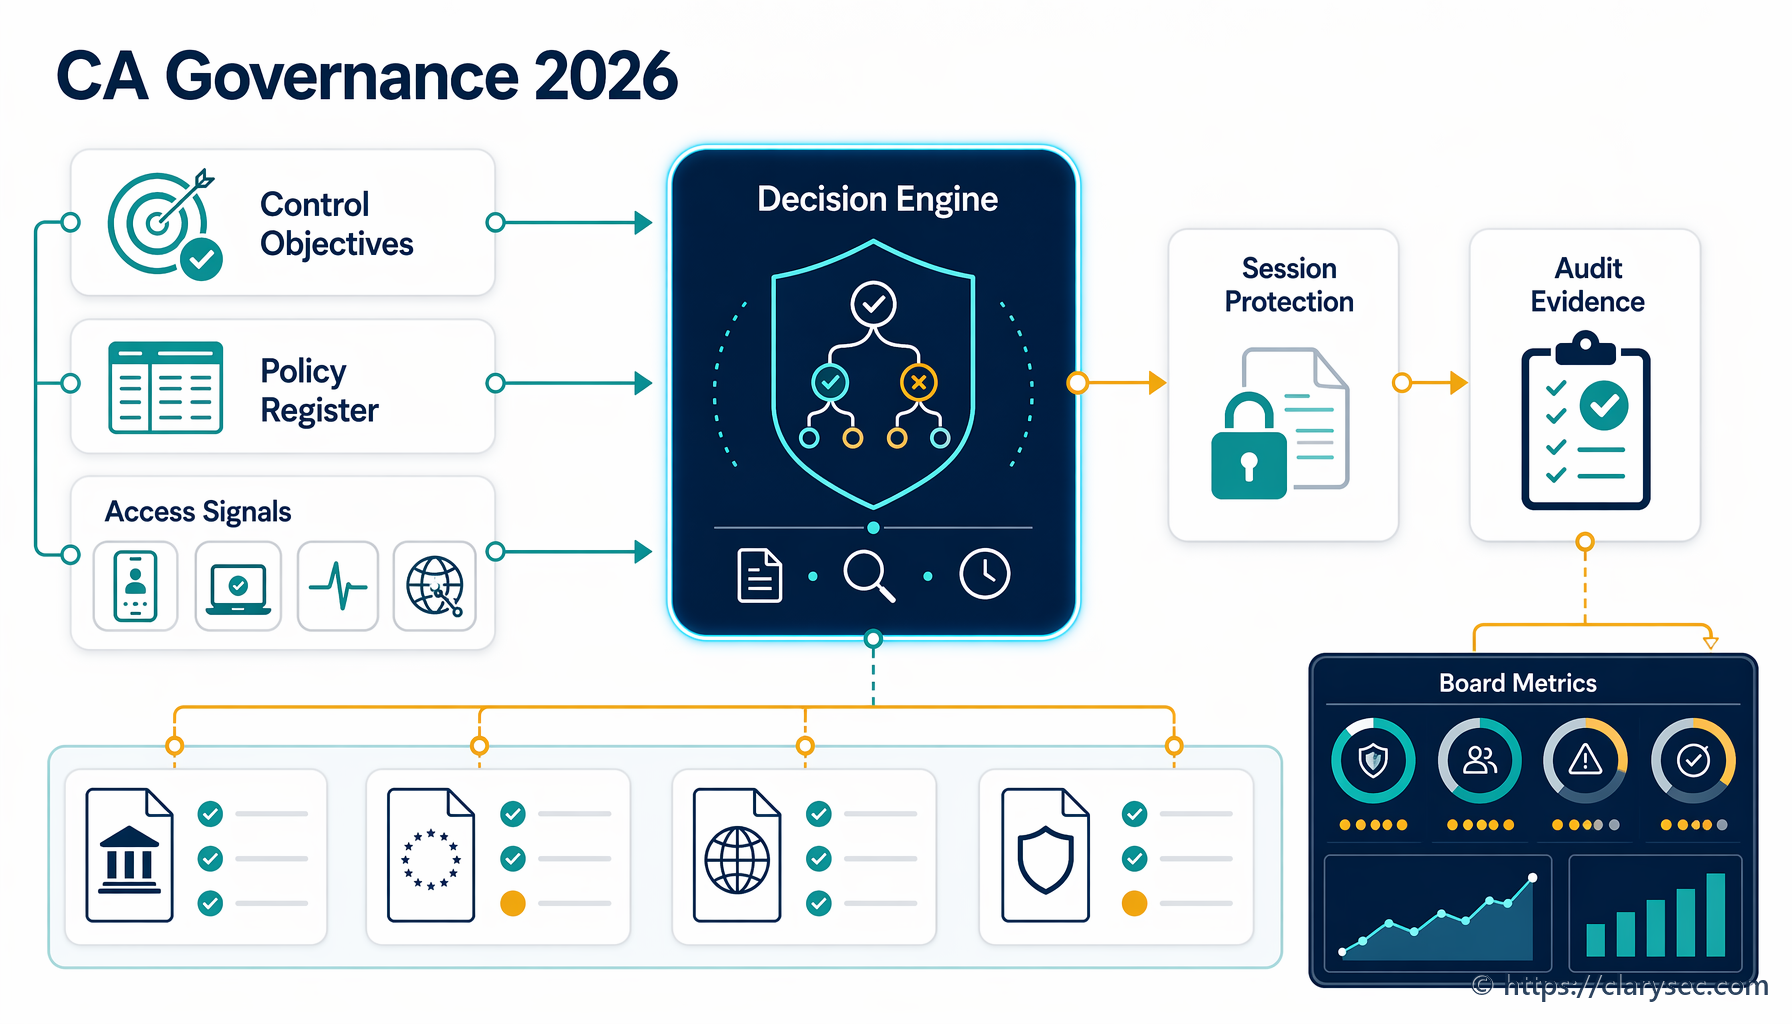
A practical guide for governing Microsoft Entra Conditional Access as an auditable control system, with ISO/IEC 27001:2022, NIS2, DORA, GDPR, NIST and COBIT evidence mapping.
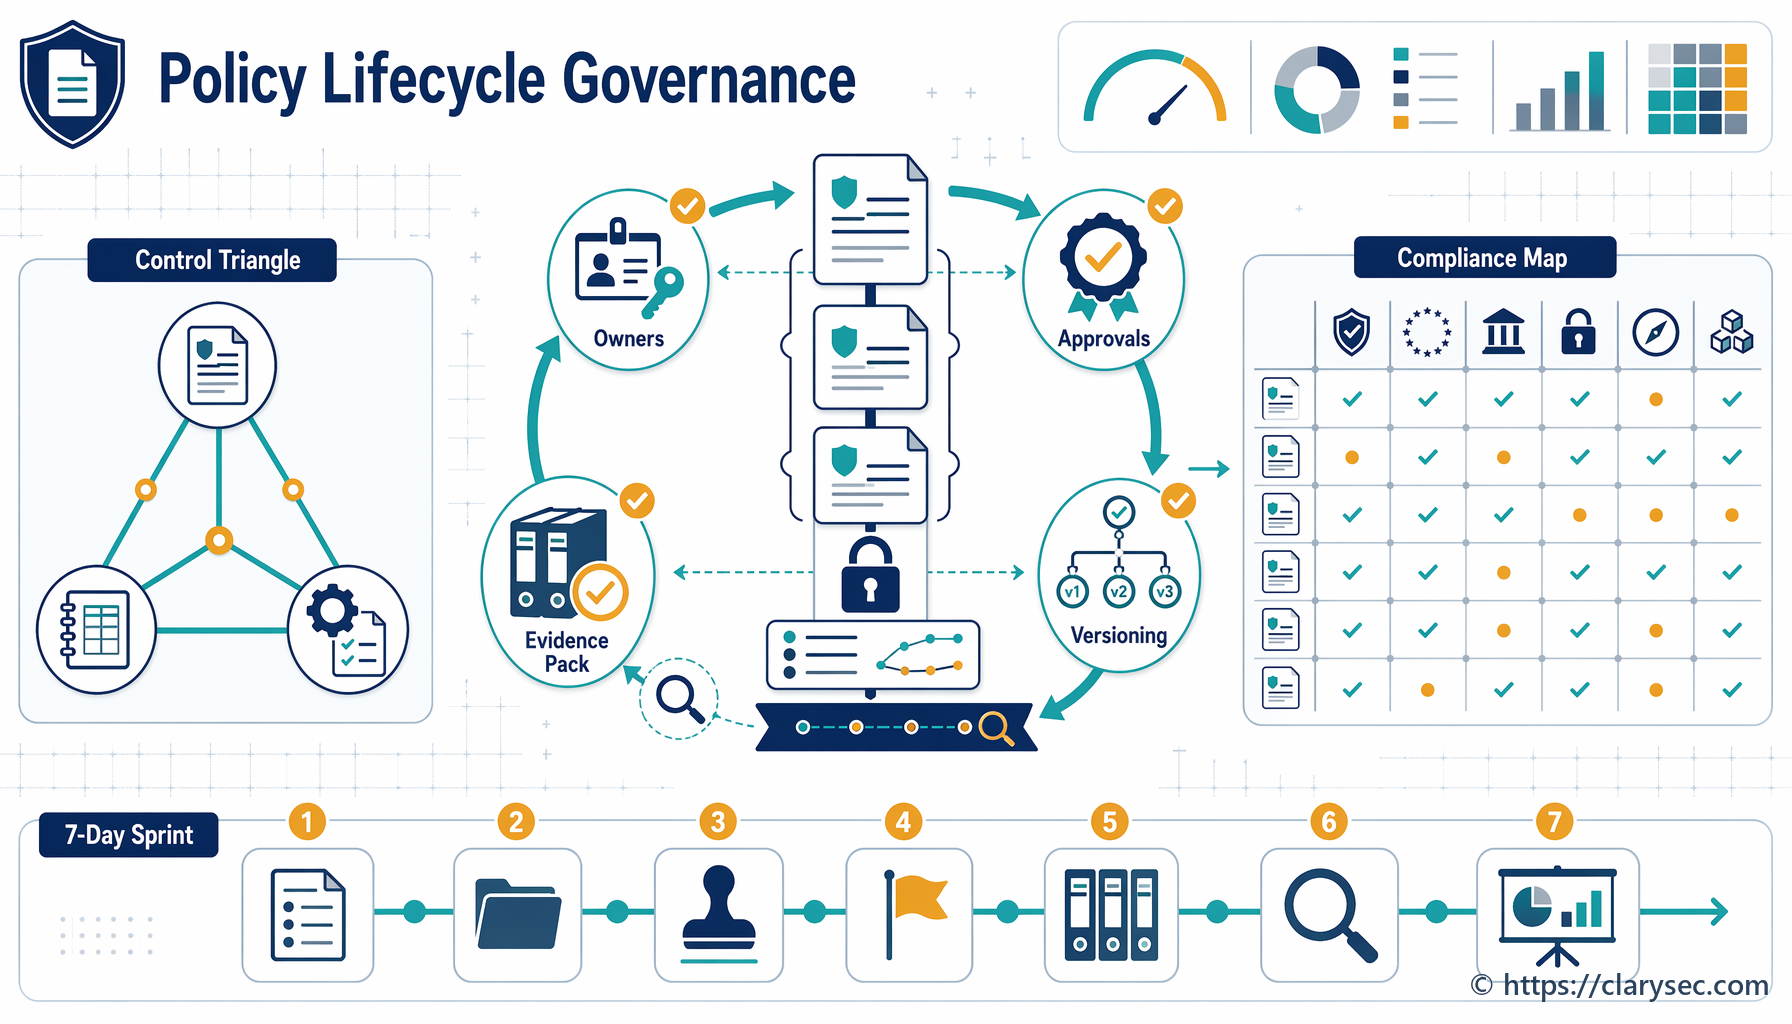
Policy governance is now evidence governance. Learn how to control ISO/IEC 27001:2022 documented information and build audit-ready evidence for NIS2, DORA and GDPR.
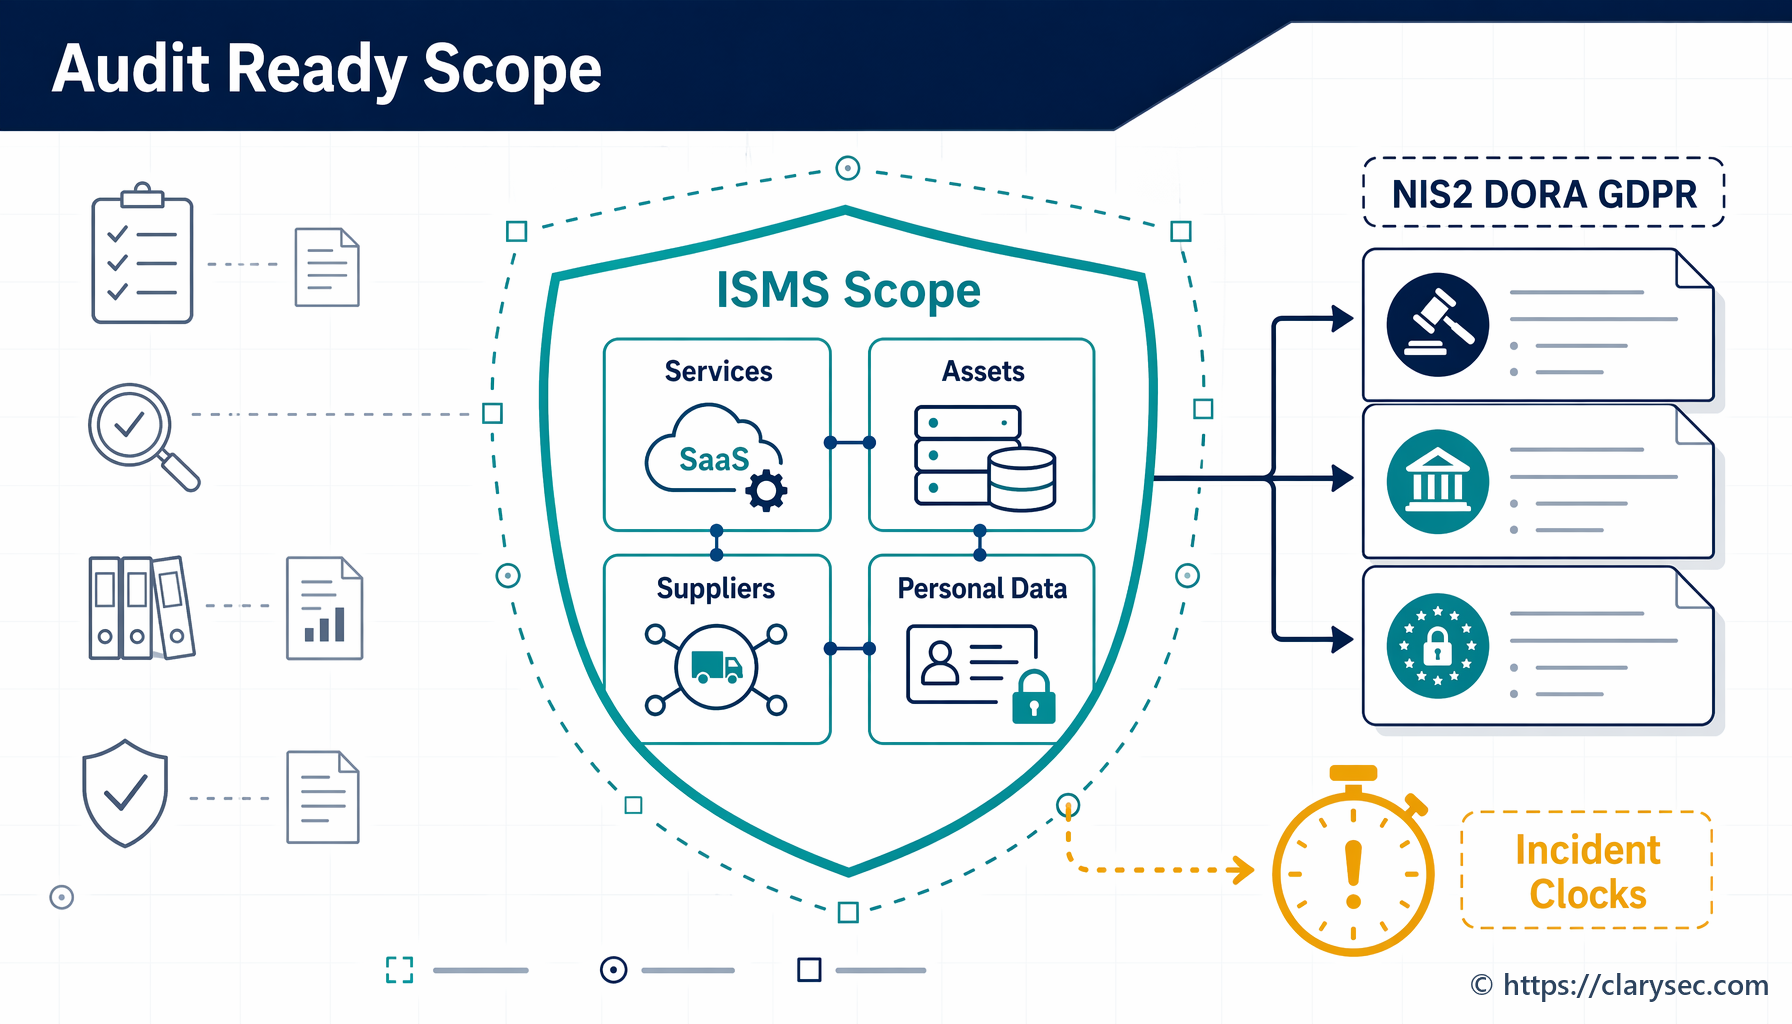
A practical CISO guide to defining ISO 27001 ISMS scope across NIS2 essential services, DORA critical or important functions, GDPR processing, assets, suppliers and audit evidence.