NIST
Explore articles in the NIST category
126 articles
A practical CISO playbook for governing biometric authentication, onboarding, workplace access and fraud controls through GDPR accountability, ISO/IEC 27701:2025 PIMS evidence, ISO/IEC 27001:2022 controls and Clarysec cross-compliance mapping.
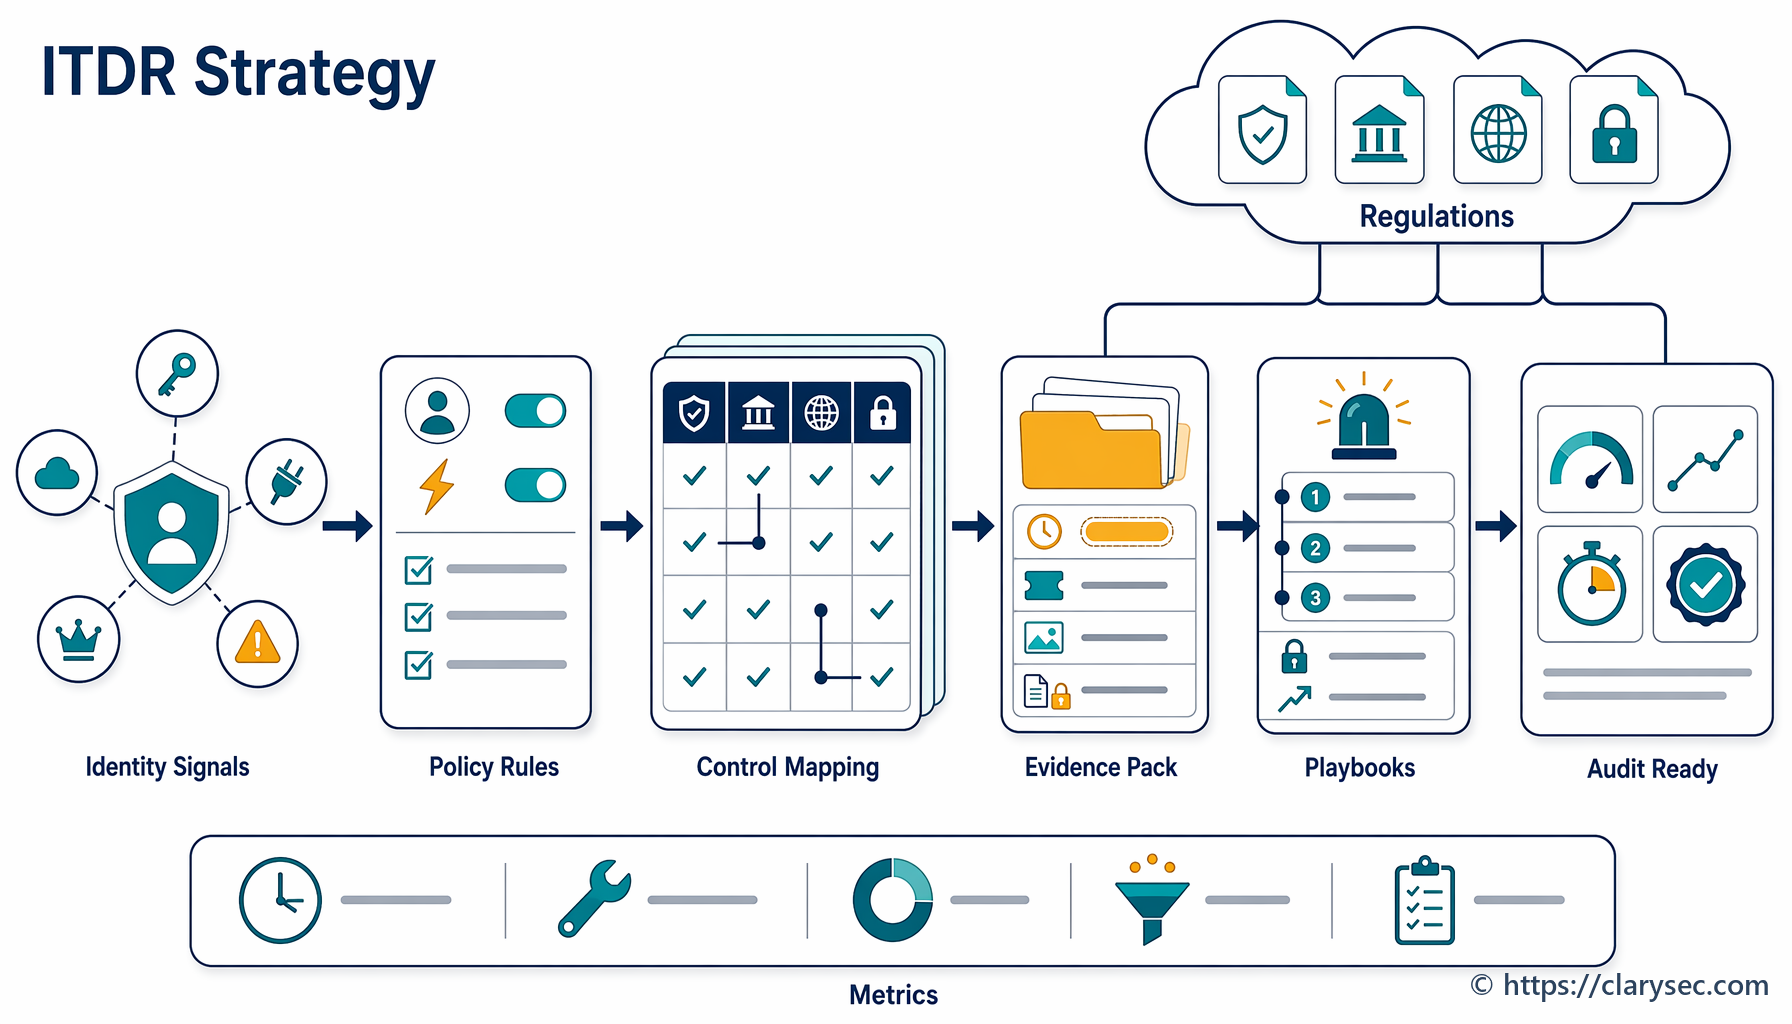
Identity attacks now create regulatory exposure across ISO 27001, NIS2, DORA and GDPR. This guide shows how to build a unified ITDR program with Clarysec policies, Zenith Blueprint and Zenith Controls.
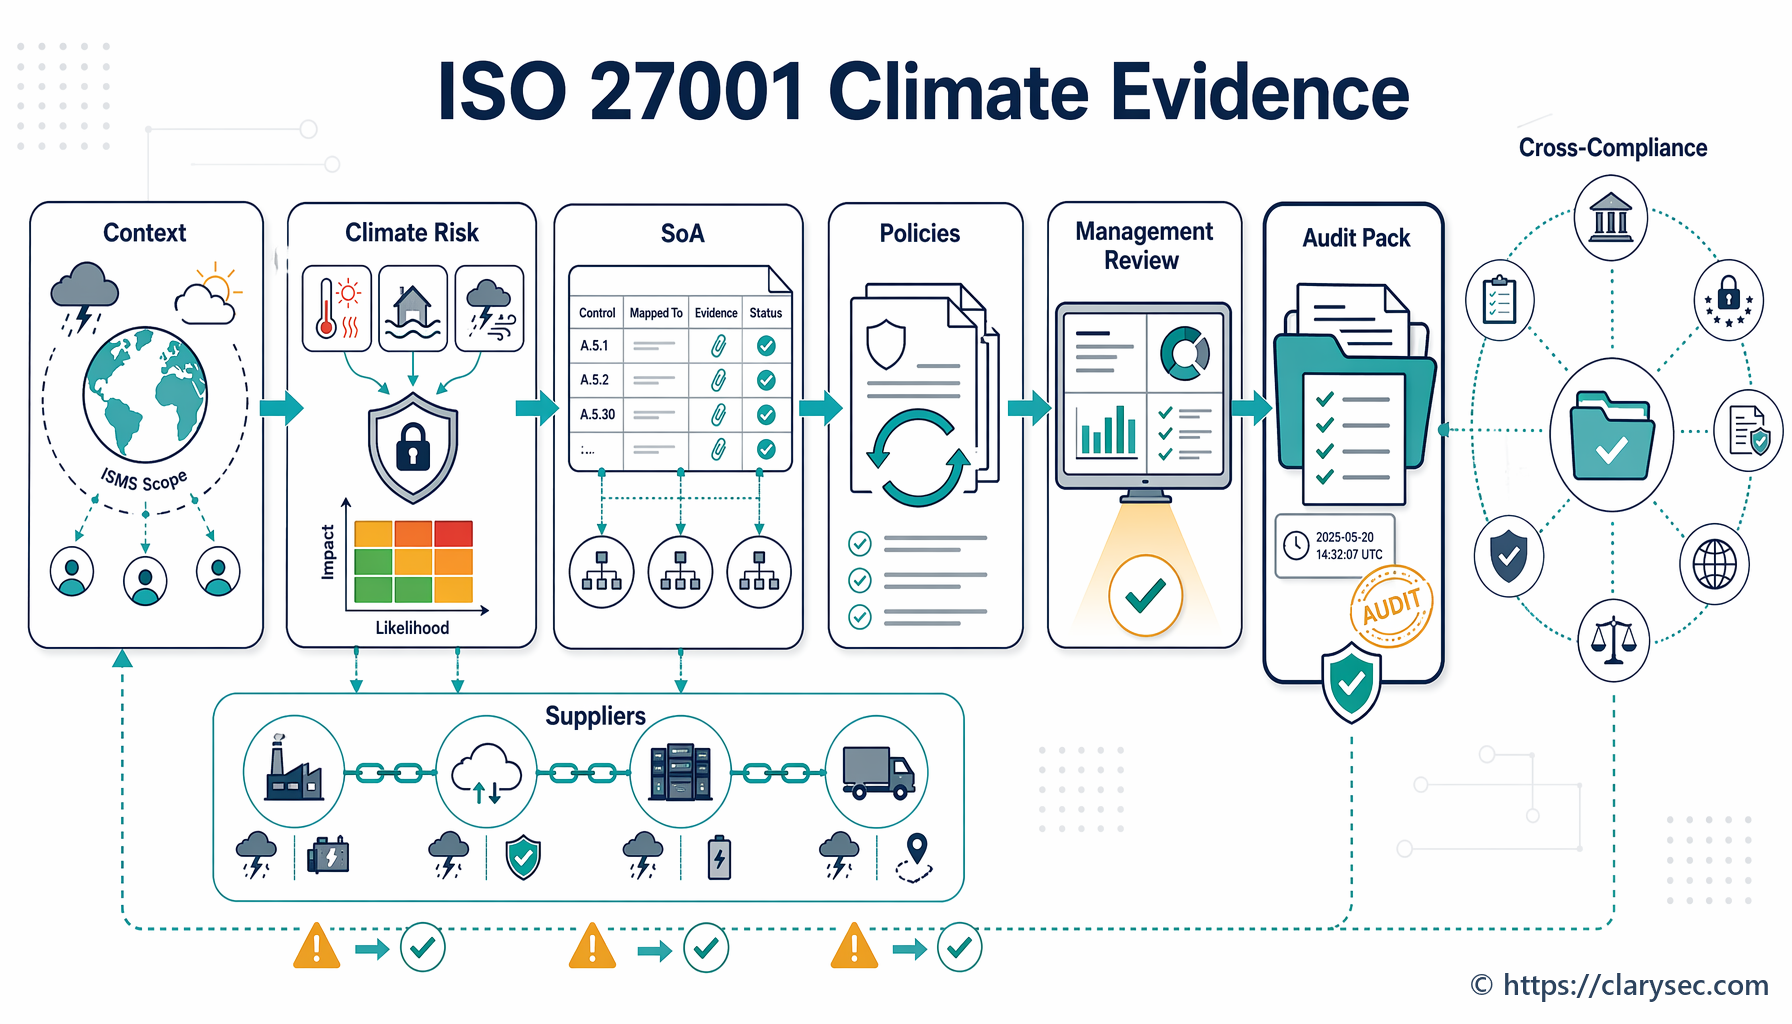
A practical guide for proving ISO 27001 climate change amendment readiness through ISMS context, interested parties, risk assessment, SoA rationale, business continuity, supplier assurance, and management review evidence.
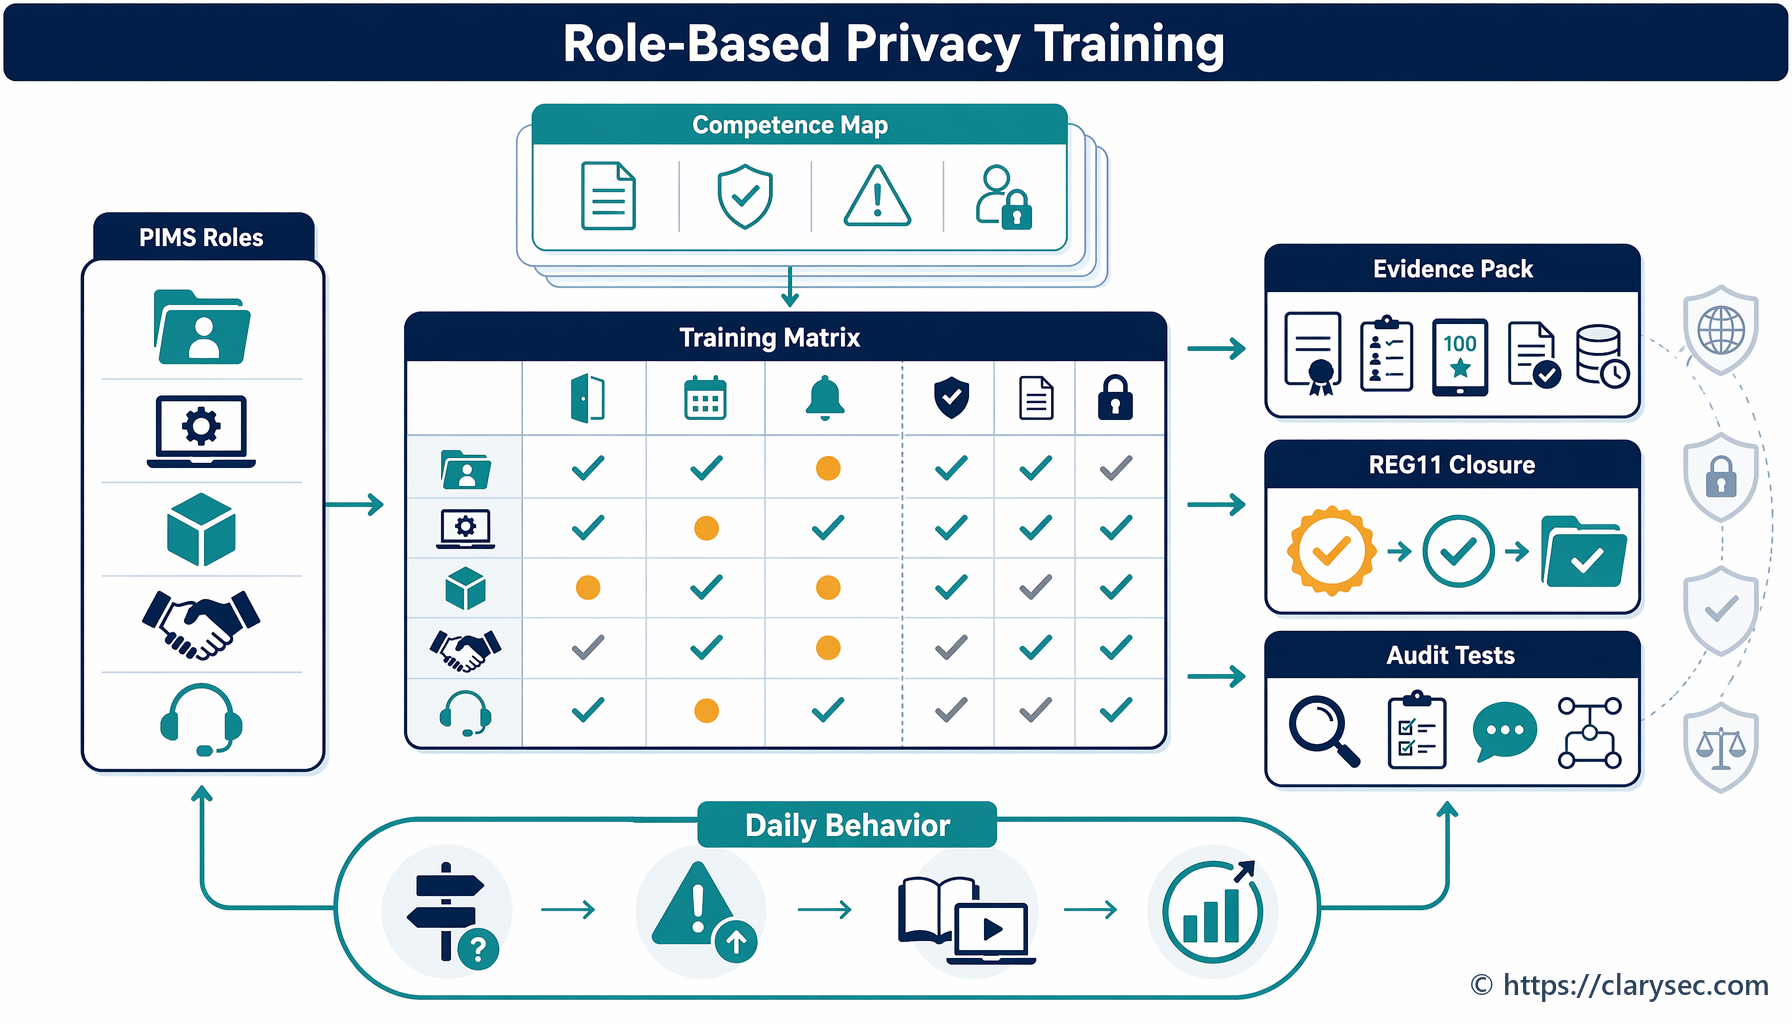
A practical guide to building defensible, role-based privacy awareness training for ISO/IEC 27701:2025, GDPR accountability, NIS2, DORA, NIST, and COBIT.
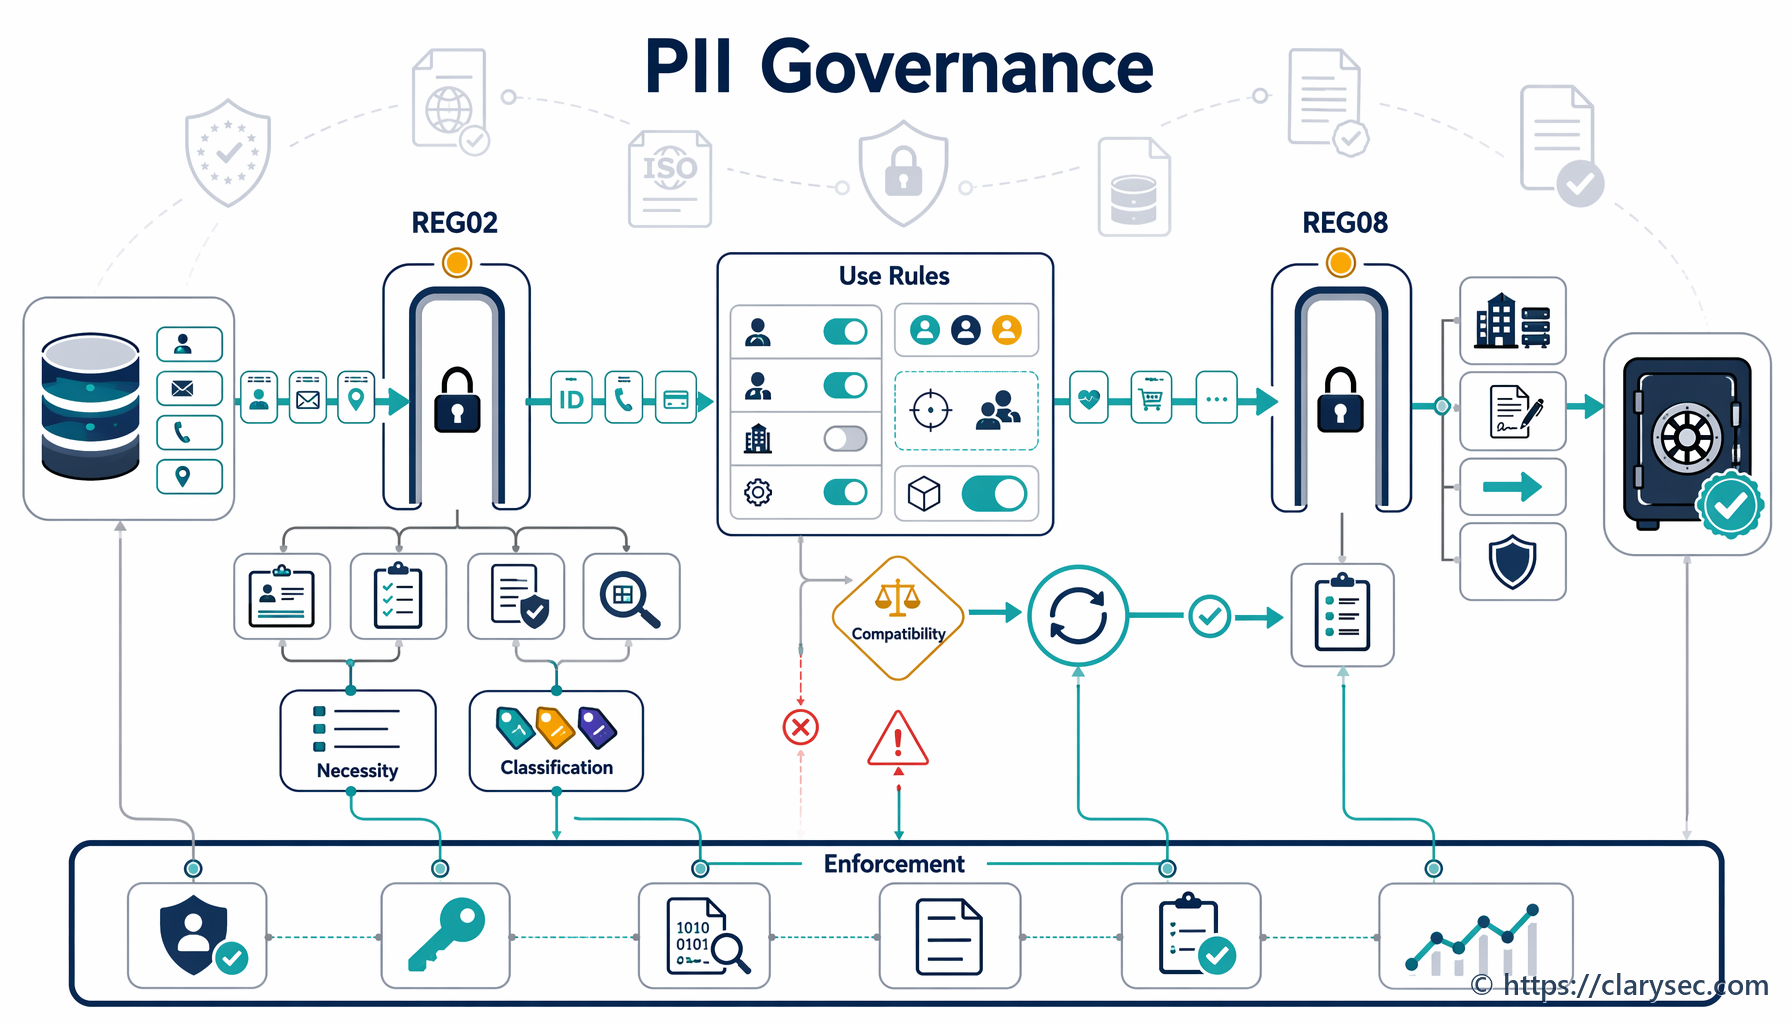
A practical CISO and privacy leader guide to governing PII collection, internal use, secondary use and external disclosure under ISO/IEC 27701:2025, GDPR and Clarysec PIMS toolkits.
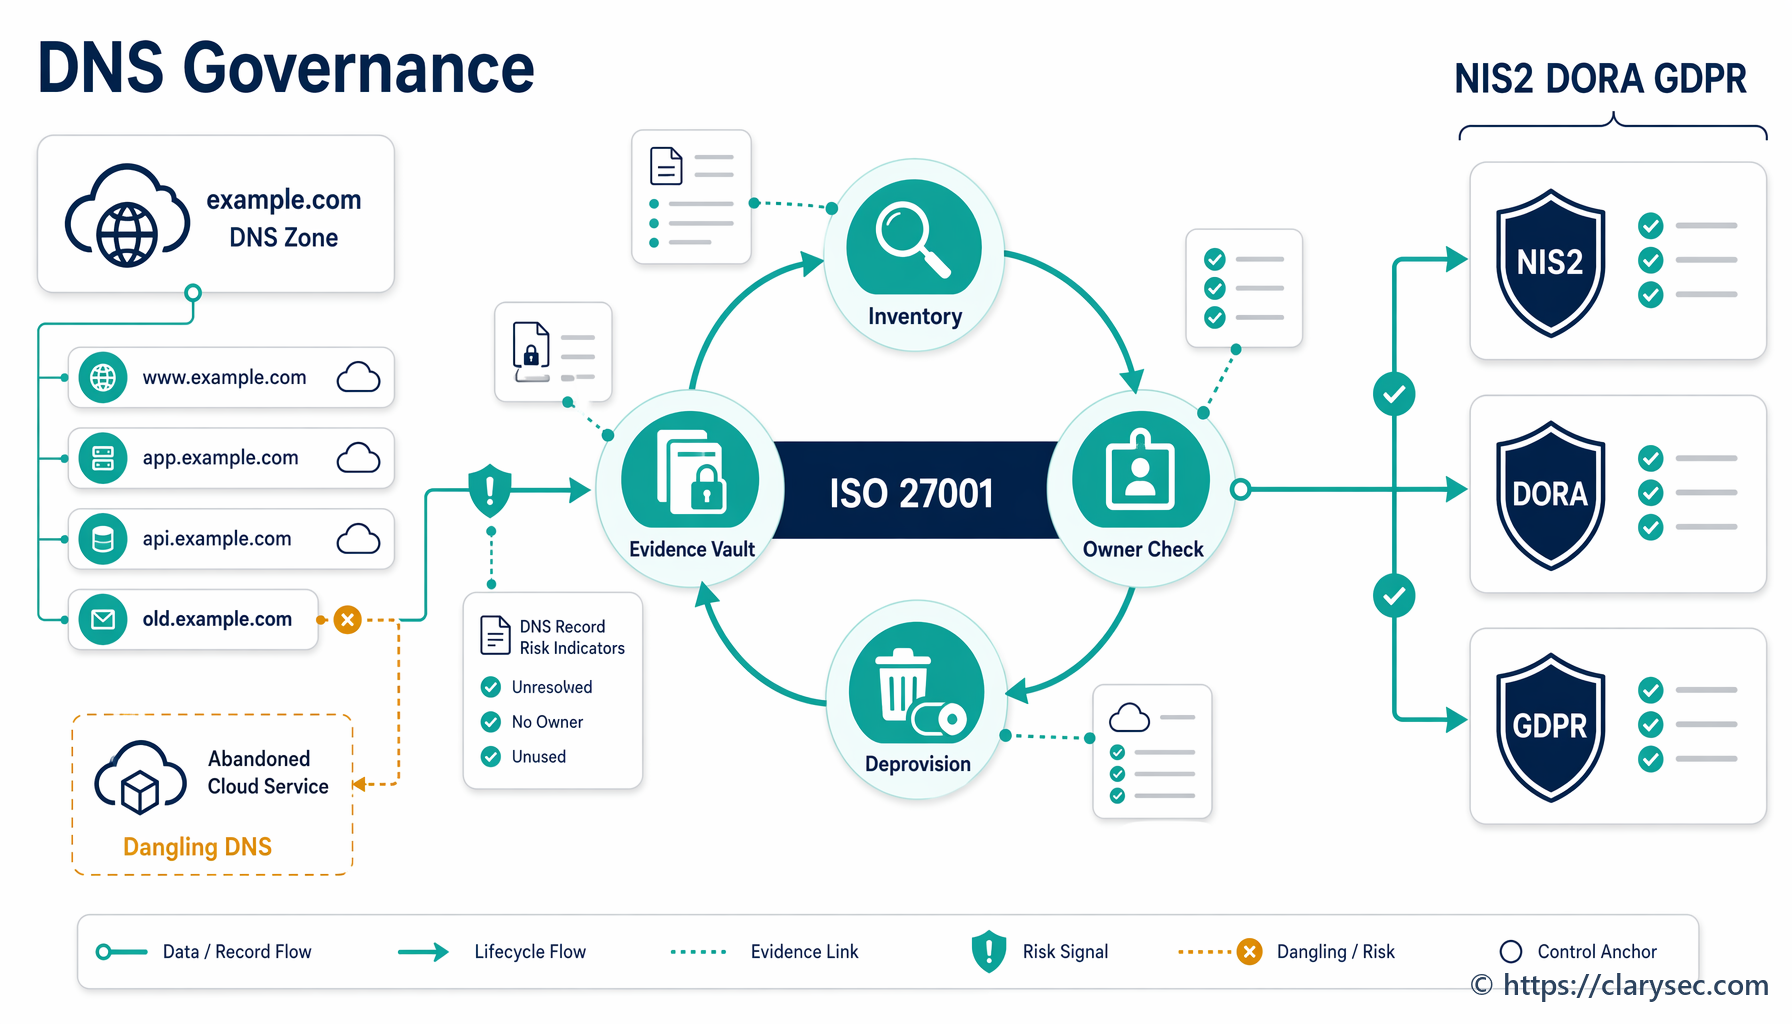
Dangling DNS is not only a cloud hygiene issue. It is evidence of whether asset ownership, change control, vulnerability management, supplier governance and incident response actually work.
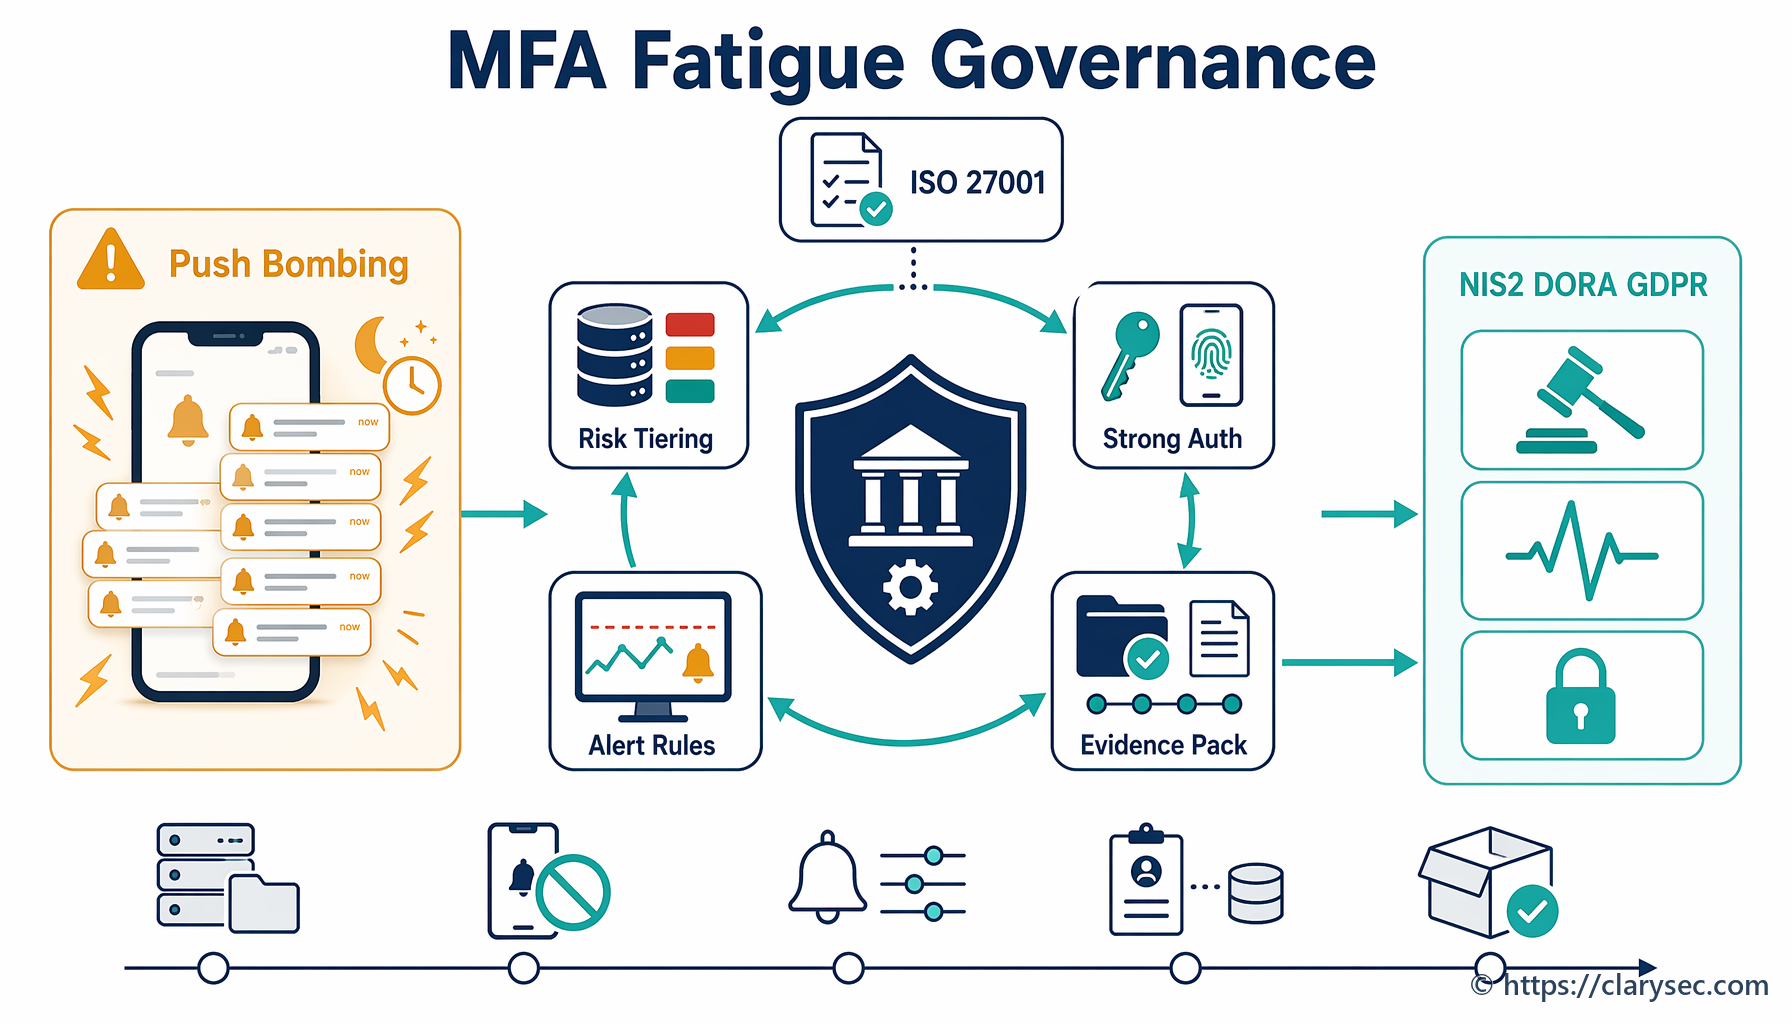
MFA fatigue is not a user problem or a single identity provider setting. It is an access governance, monitoring, training, incident response and evidence challenge that must stand up to ISO 27001:2022, NIS2, DORA and GDPR scrutiny.
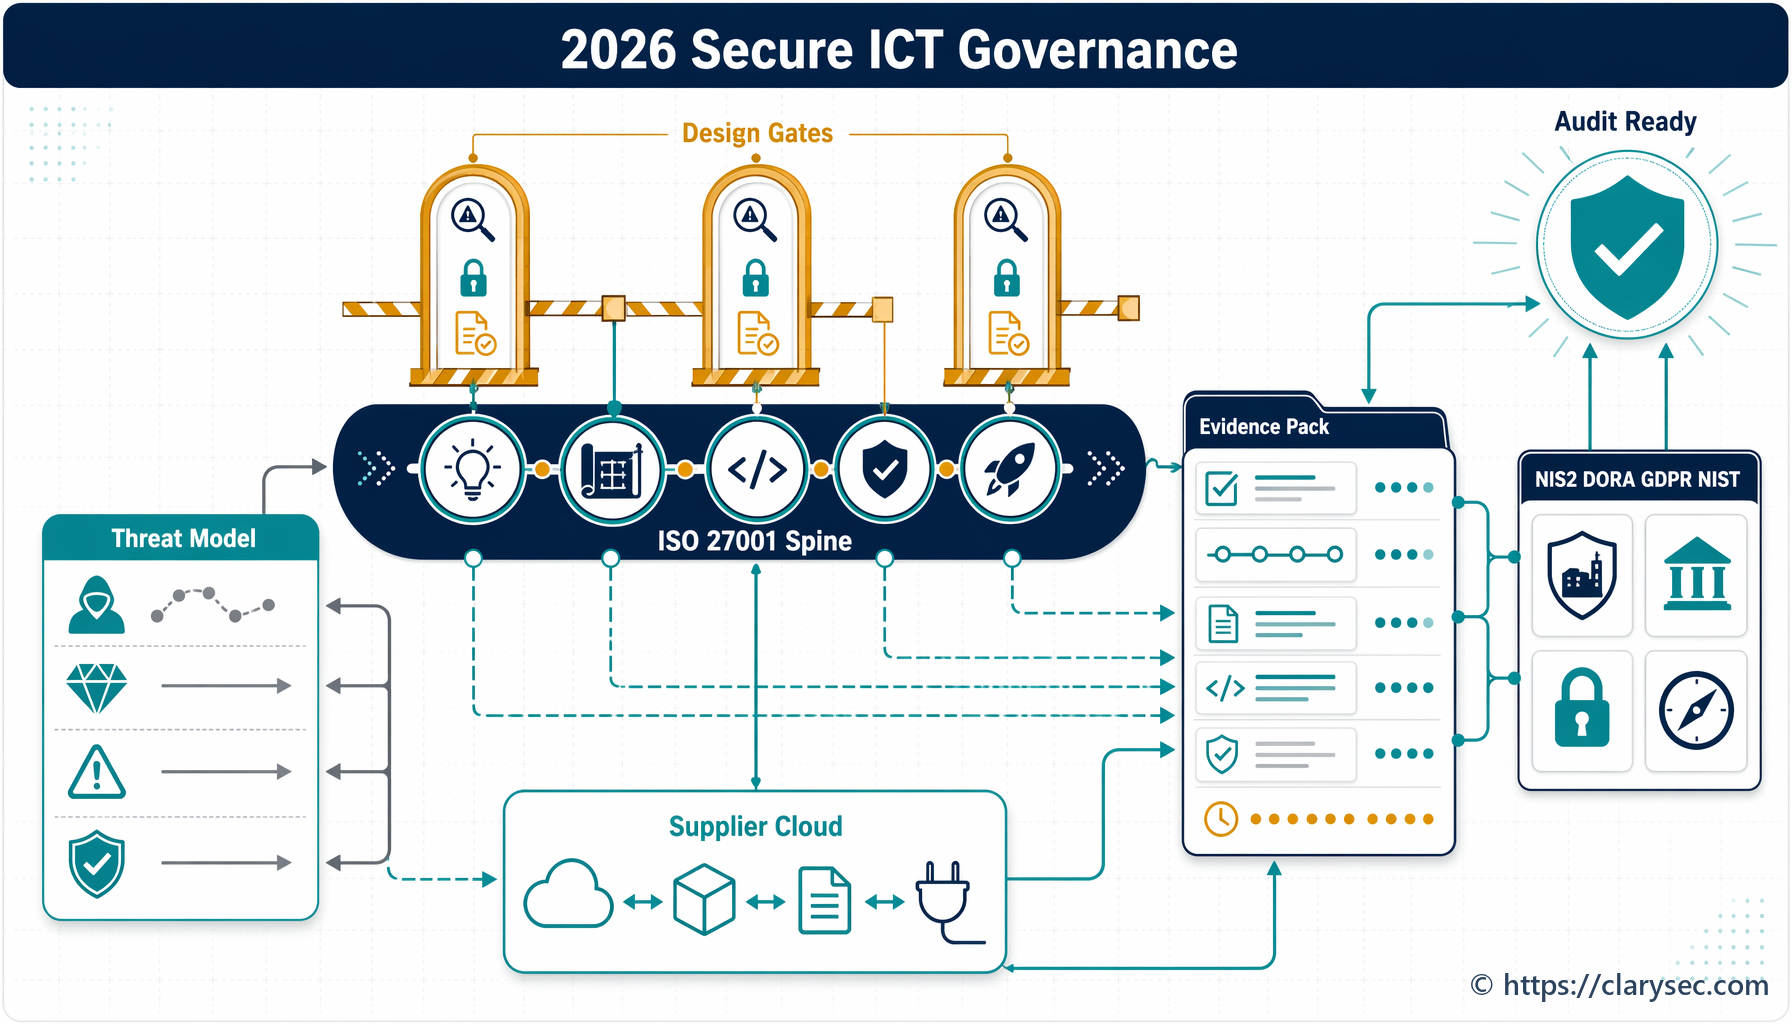
Learn how to embed security-by-design into ICT project governance using ISO/IEC 27001:2022, Clarysec policies, and reusable evidence mapped to NIS2, DORA, GDPR, and NIST CSF 2.0.
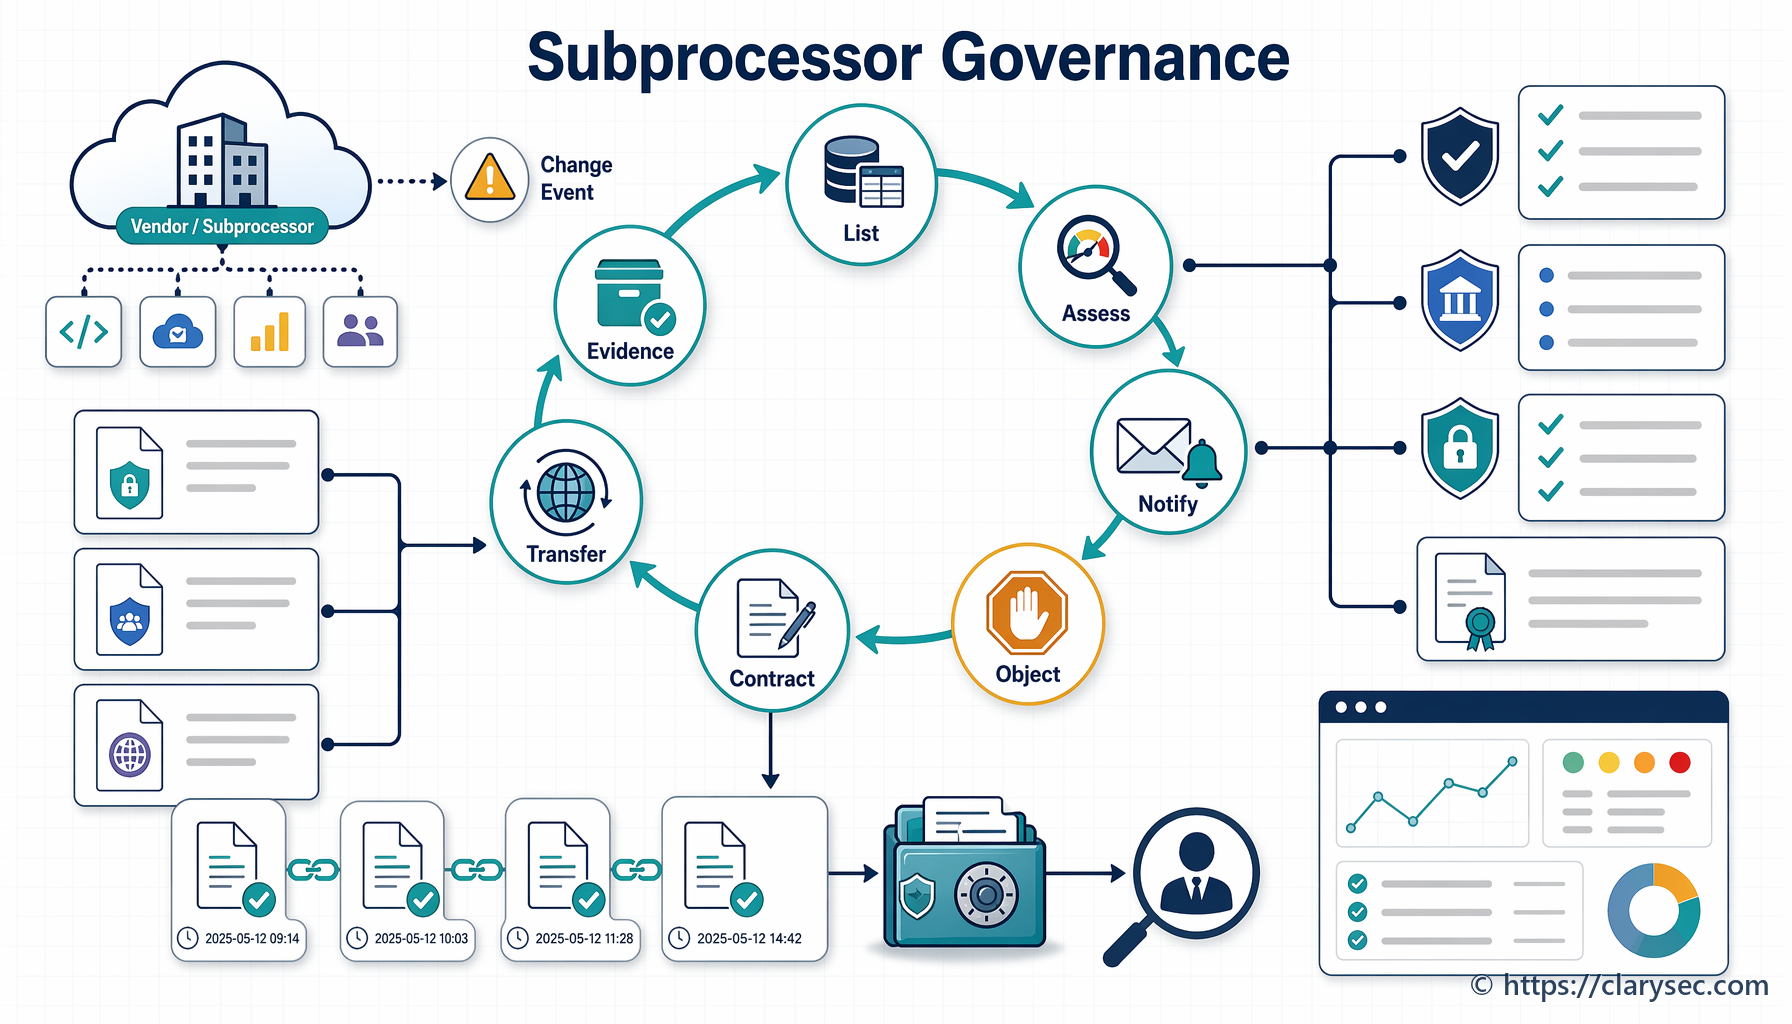
A practical, audit-ready governance model for subprocessor change notifications, customer objections, DPA updates, transfer evidence, and supplier risk controls.