NIS2 Supplier Contracts with ISO 27001 Evidence

It is 07:40 on a Monday. The CISO of a cloud-enabled logistics platform opens an email from a managed detection and response supplier. The message is short, cautious, and uncomfortable: the supplier has detected suspicious access to a support environment used by several customers. Details are limited. The supplier promises an update “as soon as practical.”
By 08:15, the compliance manager is asking whether this could trigger NIS2 reporting. By 08:40, procurement is searching for the contract. By 09:10, the board secretary wants a briefing on management accountability. By 10:00, legal asks whether the contract includes 24-hour notification, audit rights, subcontractor controls, evidence access, business continuity obligations, data return, and deletion provisions.
No one wants to discover during a live incident that a critical supplier agreement only says “reasonable security measures.”
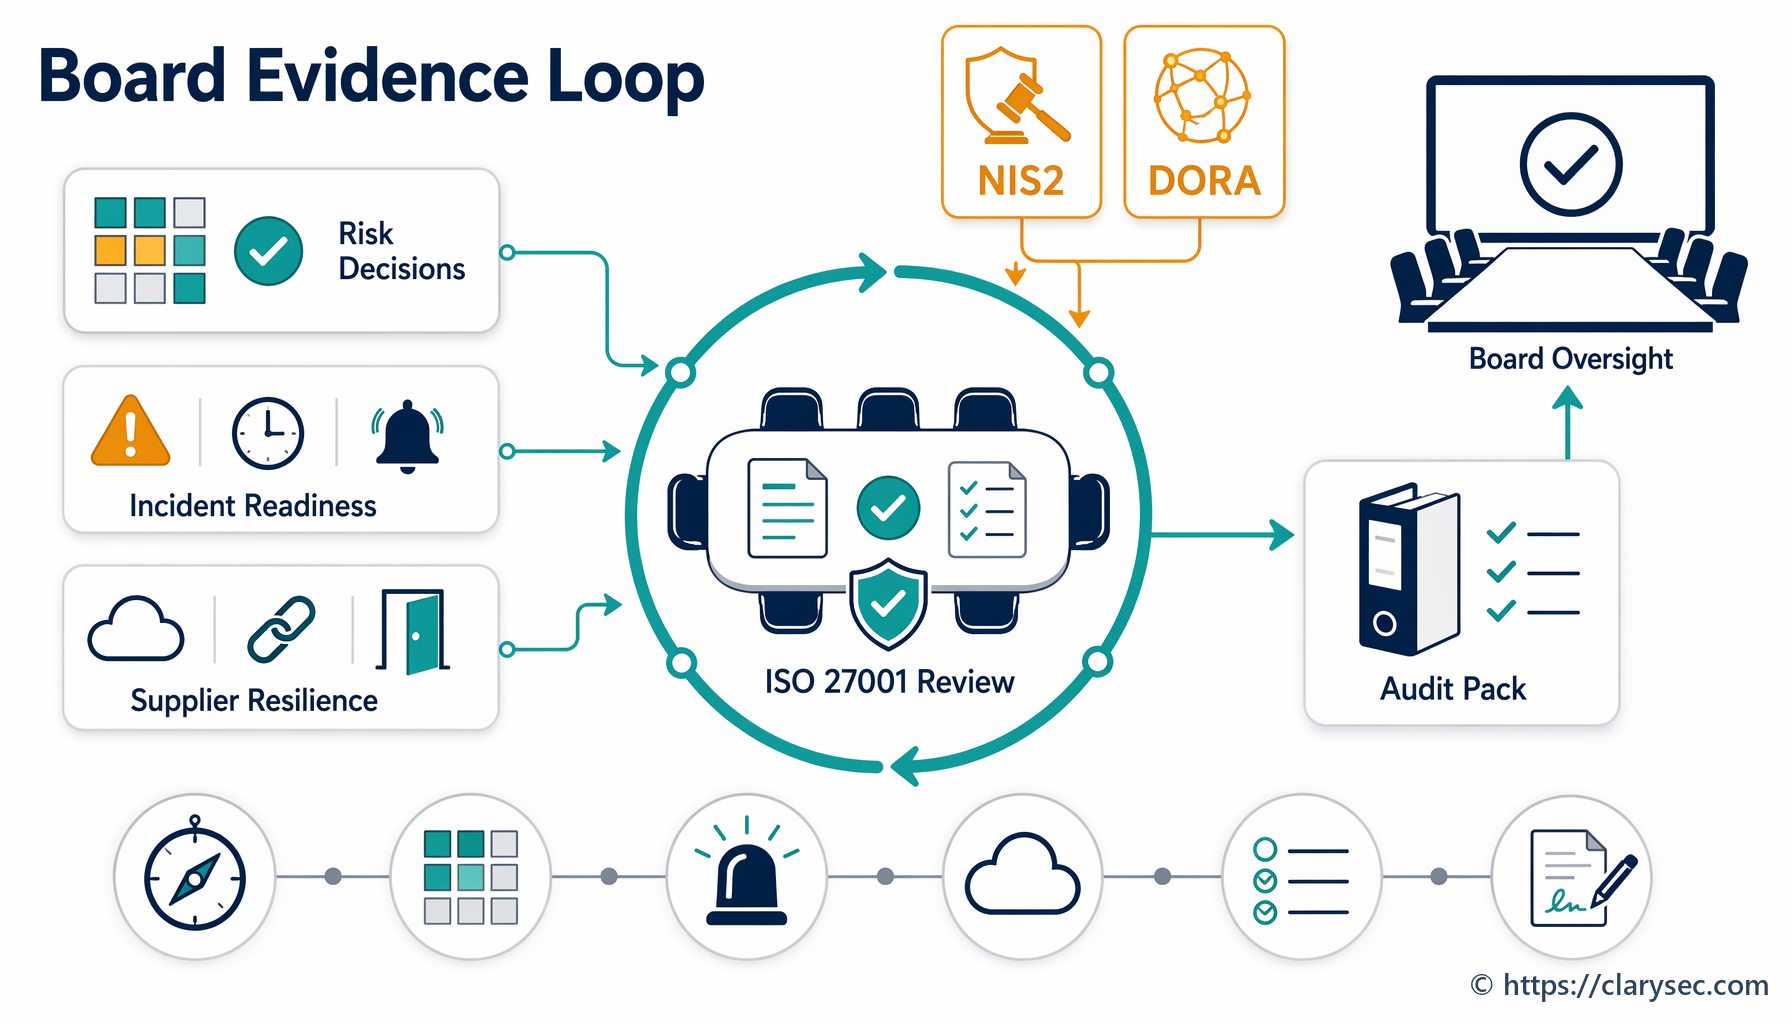
This is where NIS2 supplier contract clauses stop being legal boilerplate and become operational controls. For essential and important entities, supplier governance is now part of board accountability, supervisory evidence, incident readiness, customer assurance, privacy compliance, and resilience planning. A signed contract is not enough. The organization must prove that supplier risks are identified, approved, treated, monitored, and evidenced.
Clarysec’s approach starts from a simple principle: if the supplier clause cannot be monitored, evidenced, and tested, it is not a control.
The Zenith Blueprint: An Auditor’s 30-Step Roadmap places supplier relationships in the Controls in Action phase, Step 23, where agreements, monitoring, onboarding, reassessment, and audit evidence are translated into practical ISMS work. The Zenith Controls: The Cross-Compliance Guide then maps ISO/IEC 27002:2022 supplier controls to NIS2, DORA, GDPR, NIST, COBIT 2019, supporting ISO standards, and audit methodologies.
The result is a supplier governance model that procurement, legal, security, privacy, and the board can all use.
Why NIS2 turns supplier contracts into evidence records
NIS2 Article 20 requires management bodies of essential and important entities to approve cybersecurity risk management measures, oversee their implementation, and be accountable for infringements. Article 21 requires appropriate and proportionate technical, operational, and organizational measures, including risk analysis, incident handling, business continuity, supply chain security, secure acquisition and maintenance, effectiveness assessment, cyber hygiene, cryptography, HR security, access control, asset management, and MFA where appropriate.
Article 21(3) makes supplier due diligence explicit. Organizations must consider vulnerabilities specific to direct suppliers and service providers, the overall quality of products and cybersecurity practices, and secure development procedures.
That language creates a practical obligation: supplier relationships must be risk-based, contractually enforceable, and reviewable. A vendor questionnaire stored in a folder is not enough. A generic contract with no incident timeline, no evidence rights, and no subcontractor visibility is not enough. A supplier certification that no one reviewed is not enough.
ISO/IEC 27001:2022 provides the operating model. Clauses 4.1 to 4.4 require the organization to understand context, interested parties, legal and contractual obligations, ISMS scope, and dependencies. Clauses 5.1 to 5.3 require leadership, policy, roles, and reporting. Clauses 6.1.1 to 6.1.3 require risk assessment, risk treatment, and the Statement of Applicability. Clauses 8.1 to 8.3 require operational control, repeat risk assessments, and documented results.
For supplier governance, the most important ISO/IEC 27002:2022 Annex A controls include:
- A.5.19 Information security in supplier relationships
- A.5.20 Addressing information security within supplier agreements
- A.5.21 Managing information security in the ICT supply chain
- A.5.22 Monitoring, review and change management of supplier services
- A.5.24 Incident management planning and preparation
- A.5.25 Assessment and decision on information security events
- A.5.26 Response to information security incidents
- A.5.27 Learning from information security incidents
- A.5.28 Collection of evidence
- A.5.29 Information security during disruption
- A.5.30 ICT readiness for business continuity
- A.5.31 Legal, statutory, regulatory and contractual requirements
- A.5.34 Privacy and protection of PII
- A.8.8 Management of technical vulnerabilities
- A.8.13 Information backup
- A.8.15 Logging
- A.8.16 Monitoring activities
- A.8.24 Use of cryptography
- A.8.32 Change management
The key is ownership. A clause has little value unless someone owns the risk, someone reviews the evidence, someone tracks exceptions, and someone escalates non-compliance.
The Enterprise Third party and supplier security policy makes this explicit:
“Rights to audit, inspect, and request security evidence”
From section “Governance Requirements”, policy clause 5.3.4.
For SMEs, the Third-Party and Supplier Security Policy-sme sets the same practical expectation:
“Audit rights or the availability of compliance evidence”
From section “Governance Requirements”, policy clause 5.3.4.
This distinction matters. A smaller organization may not be able to audit every major cloud provider on site, but it can require access to assurance evidence, such as ISO/IEC 27001:2022 certification scope, SOC reports, penetration test summaries, vulnerability remediation attestations, incident summaries, business continuity test reports, and data deletion confirmations.
The three-control spine of NIS2 supplier assurance
In Clarysec’s cross-compliance model, three ISO/IEC 27002:2022 controls form the spine of NIS2 supplier governance: 5.19, 5.20, and 5.22.
A.5.19 identifies the supplier risk
Control A.5.19, Information security in supplier relationships, is the foundation. It requires organizations to protect information and assets accessed, processed, stored, or managed by suppliers.
Zenith Controls categorizes this as a preventive control covering confidentiality, integrity, and availability, with the cybersecurity concept “Identify” and the operational capability “Supplier Relationships Security.” It connects A.5.19 to A.5.20, A.5.21, A.5.14, A.5.36, and A.5.10. In practical terms, the organization identifies supplier risk, defines security expectations, controls ICT supply chain exposure, protects information transfer, monitors compliance, and extends acceptable use obligations to external parties.
For NIS2, this maps directly to Article 21(2)(d) supply chain security and Article 21(3) supplier due diligence. For GDPR, it supports the requirement to use processors that provide sufficient guarantees. For DORA, it supports ICT third-party risk management, pre-contract due diligence, criticality review, concentration risk, and lifecycle oversight.
A.5.20 makes the requirement enforceable
Control A.5.20, Addressing information security within supplier agreements, turns security expectations into contractual obligations. Zenith Controls explains the relationship between A.5.19 and A.5.20 clearly:
“5.20 serves as the contractual formalization of the security needs and risks identified under 5.19. While 5.19 involves assessing third-party risks and defining security expectations, 5.20 ensures these expectations are legally binding through contracts or service level agreements (SLAs). Without 5.20, the security measures identified in 5.19 would lack enforceability.”
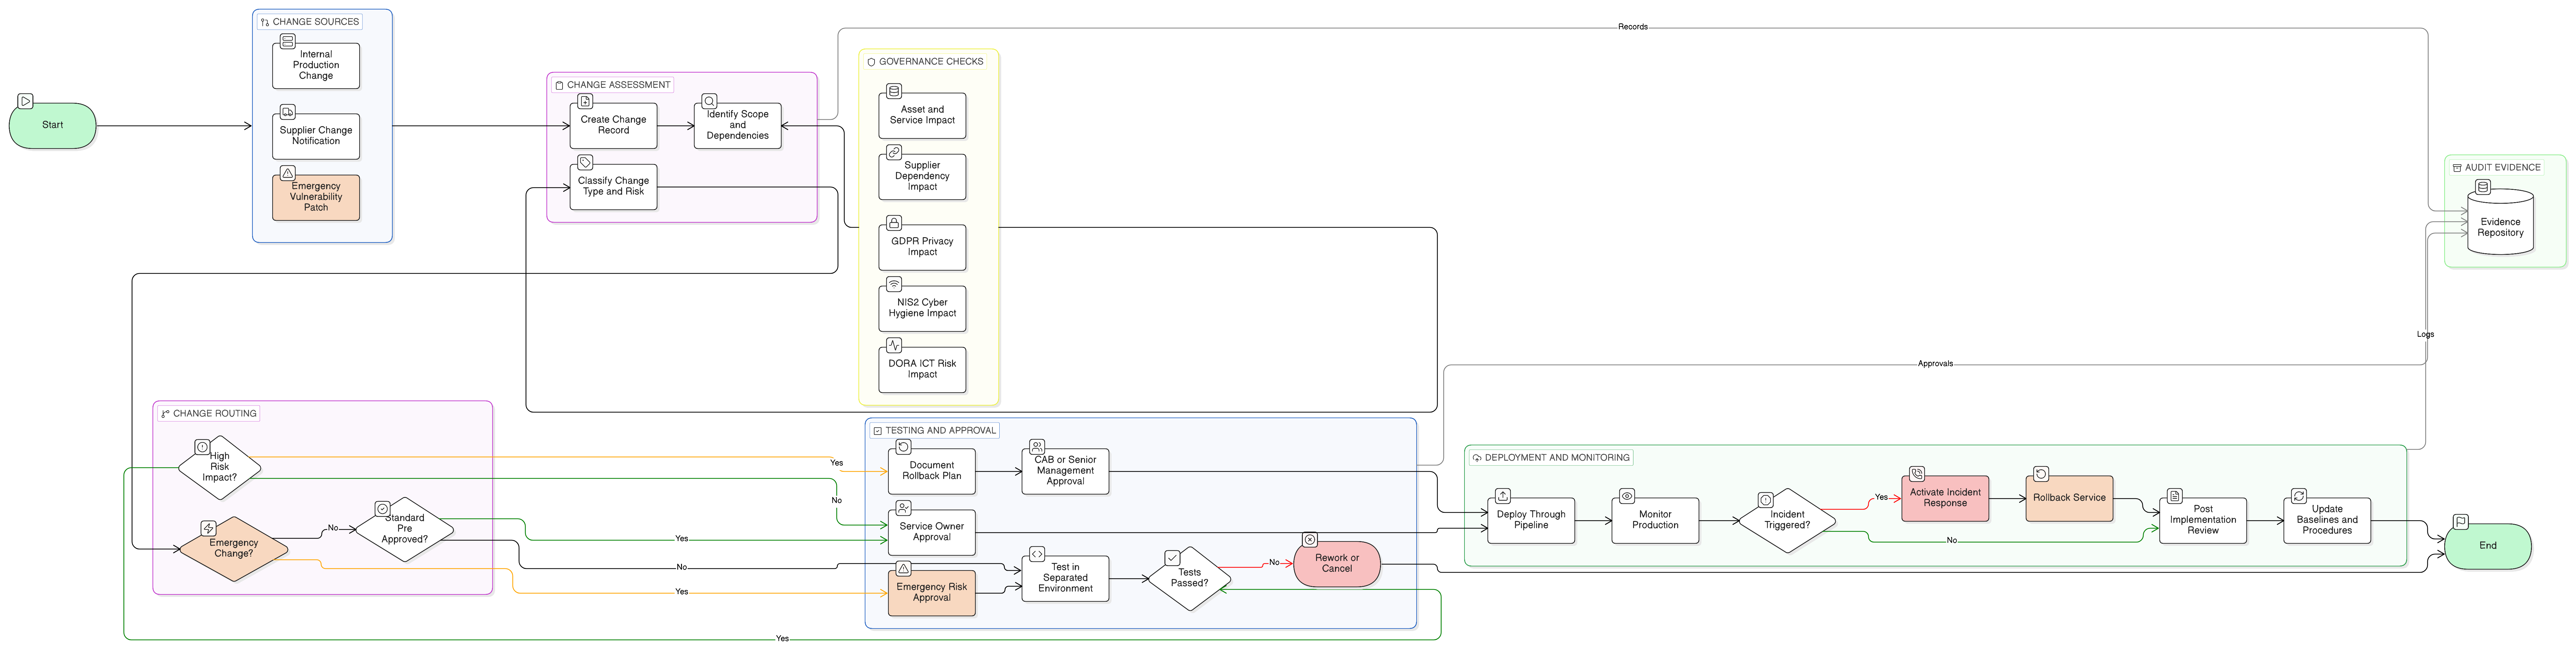
This is where NIS2 risk decisions become clauses: breach notification, audit and evidence rights, encryption, access control, vulnerability management, subcontractor approval, secure transfer, continuity, regulatory cooperation, exit support, and data deletion.
A.5.22 proves the contract is alive
Control A.5.22, Monitoring, review and change management of supplier services, prevents supplier assurance from becoming a one-time onboarding exercise. Zenith Controls ties A.5.22 to A.5.19 and A.5.20, but also to A.5.29 information security during disruption, A.8.8 management of technical vulnerabilities, A.5.36 compliance with policies, rules and standards for information security, A.5.15 access control, and A.8.27 secure system architecture and engineering principles.
That matters because supplier services change. Data locations change. Subprocessors change. Vulnerabilities appear. Certifications expire. Incident patterns emerge. A supplier that was acceptable last year may be too risky today.
What NIS2 supplier contract clauses should include
The Zenith Blueprint, Controls in Action phase, Step 23, gives a practical set of supplier agreement areas:
“Key areas typically addressed in supplier agreements include:
✓ Confidentiality obligations , including scope, duration, and third-party disclosure restrictions; ✓ Access control responsibilities , such as who can access your data, how credentials are managed, and what monitoring is in place; ✓ Technical and organizational measures for data protection, encryption, secure transmission, backup, and availability commitments; ✓ Incident reporting timelines and protocols , often with defined timeframes (e.g., “notify within 24 hours”); ✓ Right to audit , including frequency, scope, and access to relevant evidence (e.g., pen test reports, SoA, certifications); ✓ Subcontractor controls , requiring your supplier to pass on equivalent security obligations to their downstream partners; ✓ End-of-contract provisions , such as data return or destruction, asset recovery, and account deactivation.”
From the Controls in Action phase, Step 23: Organizational controls.
A strong NIS2 supplier clause is specific enough to test. “Supplier shall maintain appropriate security” is weak. “Supplier shall notify the customer security contact within 24 hours of confirmed or suspected incidents affecting customer systems, customer data, service availability, or regulatory reporting obligations” is auditable.
| Clause area | NIS2 purpose | ISO/IEC 27001:2022 and ISO/IEC 27002:2022 anchor | Assurance evidence |
|---|---|---|---|
| Supplier security baseline | Demonstrate appropriate cybersecurity practices before onboarding | Clauses 6.1.2, 6.1.3, 8.1, Annex A 5.19 and 5.20 | Supplier risk assessment, security questionnaire, certification scope, control attestation, remediation plan |
| Incident notification | Support early warning, notification, impact assessment, and final reporting | Annex A 5.24, 5.25, 5.26, 5.27, 5.28 and 5.20 | Incident clause, escalation matrix, sample incident report, notification test record |
| Audit and evidence rights | Enable supervisory, internal audit, customer, and certification evidence requests | Annex A 5.20, 5.22, 5.36 | Right-to-audit clause, SOC report, ISO/IEC 27001:2022 certificate scope, penetration test summary, issue tracker |
| Subcontractor flow-down | Address fourth-party risk and supplier dependency chains | Annex A 5.19, 5.20, 5.21, 5.22 | Subprocessor list, subcontractor approval process, flow-down clause, change notification evidence |
| Access control and MFA | Control supplier access to systems, support portals, APIs, and data | Annex A 5.15, 5.16, 5.17, 5.18, 8.5 | Supplier account inventory, access review, MFA evidence, privileged access logs, termination checklist |
| Vulnerability and patch cooperation | Support vulnerability handling, secure maintenance, and coordinated remediation | Annex A 8.8, 8.9, 8.25, 8.28, 8.29, 5.22 | Vulnerability SLA, patch reports, security advisories, exception approvals, remediation evidence |
| Continuity and recovery | Reduce operational disruption and supplier dependency risk | Annex A 5.29, 5.30, 8.13 | BCP summary, DR test report, RTO and RPO commitments, backup test evidence |
| Data protection and secure transfer | Protect confidentiality, integrity, availability, and privacy in supplier processing | Annex A 5.14, 5.31, 5.34, 8.24 | DPA, transfer records, encryption standards, data flow map |
| Exit and data return | Avoid lock-in, residual access, and orphaned data after termination | Annex A 5.11, 5.20, 5.22 | Exit plan, data deletion certificate, asset return record, access revocation evidence |
Incident clauses must match the NIS2 reporting clock
NIS2 Article 23 creates a staged reporting model for significant incidents: an early warning within 24 hours of becoming aware, an incident notification within 72 hours, intermediate reports where requested, and a final report within one month of the incident notification. A significant incident is one that has caused or is capable of causing severe operational disruption, financial loss, or considerable material or non-material damage to others.
Supplier contracts must support that timeline. If a critical managed service provider takes four days to confirm whether customer environments were affected, the customer may miss its own regulatory window.
The Enterprise Third party and supplier security policy requires:
“Breach notification timeframes (e.g., within 24 or 72 hours, depending on criticality and regulatory requirements)”
From section “Governance Requirements”, policy clause 5.3.3.
The SME Third-Party and Supplier Security Policy-sme also requires defined breach notification timelines from section “Governance Requirements”, policy clause 5.3.3.
For PII incidents, the Enterprise PII Incident and Breach Management Policy connects cybersecurity, financial-sector, customer, and service-recipient reporting:
“[Conditional] The Privacy Lead / PIMS Manager MUST coordinate any required sectoral, cybersecurity, financial-sector, customer, or service-recipient incident reporting when a high-impact PII incident meets an applicable reporting threshold, and MUST record the authority, recipient, timeline, submission, and acknowledgement evidence in REG01 and REG10.”
From section “Notification and communications”, policy clause 4.4.6.
This is mature NIS2 evidence: not just a notification email, but a record of the authority, recipient, timeline, submission, acknowledgement, impact, root cause, and follow-up actions.
Privacy and DORA alignment without duplicate supplier programs
Many NIS2 suppliers also process personal data. GDPR Article 28 requires controllers to use processors that provide sufficient guarantees and to define processor obligations in a written contract. GDPR Article 5 requires accountability for secure and lawful processing. GDPR breach obligations also require rapid cooperation when supplier incidents affect personal data.
The Enterprise Processor, Subprocessor and Third-Party Privacy Management Policy sets the approval gate:
“[Both] The Vendor / Procurement Owner MUST ensure that processor and subprocessor contracts include privacy assistance, security assurance, incident interface through PII15, return or deletion through PII10, transfer linkage through PII13, and audit or assurance cooperation before approval.”
From section “Contract and documented instruction controls”, policy clause 4.3.6.
It also requires evidence review before approval:
“[All] The Information Security Lead MUST review security assurance evidence for each processor, subprocessor, or third-party relationship with PII access or hosting before approval, and MUST record the outcome in REG08 or REG12.”
From section “Due diligence and risk assessment”, policy clause 4.2.2.
DORA adds another layer when the supplier serves a financial entity. DORA Articles 28 to 30 require ICT third-party governance, registers of ICT service contracts, risk-based due diligence, criticality assessment, concentration risk analysis, audit and inspection rights, termination rights, exit strategies, and mandatory contractual provisions. Article 30 is especially relevant because it requires contract content covering service descriptions, locations, data protection, access and recovery, service levels, incident assistance, cooperation with authorities, audit rights, subcontracting, contingency measures, and transition support.
The practical answer is not three separate supplier programs for NIS2, GDPR, and DORA. It is one harmonized supplier evidence model, mapped across frameworks.
| Compliance lens | What the supplier program must prove | Clarysec and ISO/IEC 27001:2022 implementation |
|---|---|---|
| NIS2 | Management-approved cyber risk measures, supply chain security, supplier due diligence, incident handling, continuity, access control, effectiveness assessment | ISMS context, risk treatment, SoA, A.5.19, A.5.20, A.5.21, A.5.22, A.5.24 to A.5.30 |
| GDPR | Processors provide sufficient guarantees, contracts define obligations, security and breach support are demonstrable | DPA, processor evidence review, PII register, A.5.31, A.5.34, A.8.24, privacy policies |
| DORA | ICT third-party risk is governed, registered, monitored, contractually controlled, auditable, and exit-ready | Criticality assessment, ICT contract register, audit rights, exit plan, BCP evidence, A.5.20 and A.5.22 |
| NIST CSF 2.0 | Supplier requirements are governed, prioritized, in contracts, monitored, and included in incident response and recovery | GV.SC-01 to GV.SC-10 mapped to supplier lifecycle, evidence register, response playbooks |
| COBIT 2019 | Supplier agreements, performance, risks, incidents, and corrective actions are managed and reviewed | APO10 supplier agreements and monitoring, DSS supplier risk and service oversight, issue tracking |
NIST CSF 2.0 is useful because its GOVERN function requires understanding dependencies, legal obligations, contractual obligations, risk appetite, policies, accountability, and oversight. Its supply chain category GV.SC covers supplier roles, criticality, contract requirements, due diligence, monitoring, incident inclusion, lifecycle monitoring, and end-of-relationship provisions.
A Clarysec workflow for onboarding a critical supplier
Assume you are onboarding a managed security service provider that will monitor endpoint telemetry, receive alerts containing user identifiers, and support incident triage for a NIS2 in-scope organization.
Step 1: classify the supplier
Record the supplier in your supplier register with the service description, systems and data accessed, PII involvement, support for essential or important services, privileged access, countries of service delivery, subcontractors, fourth-party dependencies, criticality rating, risk owner, procurement owner, and information security reviewer.
This implements ISO/IEC 27001:2022 Clauses 4.2, 4.3, 6.1.2, and 8.1 by connecting interested-party requirements, dependencies, risk ownership, and operational control.
Step 2: map the risk to the SoA
In the Zenith Blueprint, Risk Management phase, Step 13, Clarysec recommends cross-referencing regulations in the risk register or SoA:
“Cross-reference regulations: If certain controls are implemented specifically to comply with GDPR, NIS2, or DORA, you can note that in either the Risk Register (as part of risk impact justification) or in the SoA notes.”
From the Risk Management phase, Step 13: Risk Treatment Planning and Statement of Applicability.
For the MSSP, include at least A.5.19, A.5.20, A.5.21, A.5.22, A.5.24 to A.5.28, A.5.29, A.5.30, A.5.31, A.5.34, A.8.8, A.8.15, A.8.16, and A.8.24.
Step 3: require enforceable clauses
Use a supplier security addendum requiring 24-hour initial incident notification, a 72-hour detailed update, final incident reporting, MFA for privileged access, named user accounts, subcontractor controls, secure transfer, encryption, assurance evidence, regulatory cooperation, BCP and DR evidence, exit support, data return or deletion, and access revocation.
The Enterprise Supplier Dependency Risk Management Policy provides the continuity requirement:
“Where applicable, a requirement for the supplier to maintain its own Business Continuity Plans (BCP/DRP) and incident management plans, to test them, and to provide summaries or test reports to us upon request.”
From section “Implementation Requirements”, policy clause 6.8.4.
Step 4: build the assurance evidence pack
Before approval, request the signed agreement, SLA, security addendum, ISO/IEC 27001:2022 certification scope or equivalent assurance, SOC report where available, penetration test executive summary, vulnerability management summary, incident response procedure summary, BCP or DR test summary, access control and MFA attestation, subcontractor list, data deletion and exit procedure, and DPA where PII is processed.
The SME Third-Party and Supplier Security Policy-sme makes basic contractual evidence measurable:
“Signed agreements and SLAs”
From section “Enforcement and Compliance”, policy clause 8.3.2.1.
It also identifies recurring supplier evidence:
“Valid security certifications or updated control evidence”
From section “Policy Implementation Requirements”, policy clause 6.3.1.2.
For broader vendor due diligence, the Audit and Compliance Monitoring Policy states:
“Vendor due diligence shall include review of certifications (e.g., ISO 27001, SOC 2), security questionnaires, and incident records.”
Step 5: monitor based on criticality
The Enterprise Processor, Subprocessor and Third-Party Privacy Management Policy requires quarterly monitoring for high-risk PII relationships:
“[All] The Vendor / Procurement Owner MUST monitor active high-risk processor and subprocessor relationships quarterly and other active PII processor and subprocessor relationships annually against due diligence conditions, contract status, assurance status, open issues, and review dates in REG08.”
From section “Ongoing monitoring, assistance, disclosure interface, and exit”, policy clause 4.5.1.
This is how A.5.22 becomes real. The review should determine whether the supplier remains within risk appetite, whether evidence is current, whether open issues exist, whether incidents occurred, and whether service changes require reassessment.
How auditors will test NIS2 supplier clauses
Auditors rarely start by reading your policy in isolation. They sample suppliers and follow the evidence trail.
An ISO/IEC 27001:2022 auditor will ask for the supplier inventory, risk classification, supplier criteria, due diligence records, contracts, evidence, SoA mapping, and monitoring history. For Annex A 5.20, the auditor will inspect whether the sampled contracts contain enforceable clauses. For Annex A 5.22, the auditor will test whether reports were reviewed, exceptions were logged, and actions were followed up.
A NIS2 competent authority may focus on whether supplier cybersecurity practices and secure development procedures were assessed under Article 21(3). A DORA-oriented reviewer may ask for ICT contract register entries, exit strategies, concentration risk analysis, and mandatory Article 30 provisions. A privacy auditor may test processor contracts, subprocessor flow-down, breach interfaces, and evidence of sufficient guarantees.
| Audit perspective | Likely audit test | Common finding |
|---|---|---|
| ISO/IEC 27001:2022 auditor | Sample high-risk suppliers and compare risk assessment, contract clauses, SoA applicability, and monitoring records | Supplier controls included in SoA but not evidenced in contracts or reviews |
| ISO/IEC 27007-style ISMS audit | Interview procurement, legal, IT, and service owners to verify workflow operation | Security review bypassed for urgent supplier onboarding |
| COBIT 2019 auditor | Test supplier agreement management, performance monitoring, and corrective action governance | Contract requires quarterly reports, but no one reviews or escalates them |
| ISACA ITAF auditor | Inspect evidence quality, account controls, and termination records | Supplier accounts remain active after contract end |
| NIST assessor | Check external system service controls, supplier assessment evidence, and continuous monitoring | Supplier risk was assessed once and never updated after service change |
| Privacy auditor | Review processor contracts, subprocessor flow-down, breach interface, and evidence of sufficient guarantees | DPA exists but security assurance evidence was not reviewed |
The Enterprise PII Security and Access Control Policy shows how access control, vulnerability, configuration, monitoring, and cryptography link back to ISO/IEC 27001:2022:
“ISO/IEC 27001:2022 — Clause 6.1.3; Clause 8.1; Annex A controls 8.1, 8.2, 8.3, 8.5, 8.8, 8.9, 8.15, 8.16, 8.20, 8.24. Addressed by clauses [4.1.1; 4.1.2; 4.2.1; 4.2.3; 4.3.2; 4.4.1; 4.4.2; 4.5.1; 4.5.2; 4.6.1; 4.6.3; 4.7.1; 4.7.4; 4.7.5; 4.8.1; 4.8.2; 7.1.1; 7.1.2].”
From section “Reference Standards and Frameworks”, policy clause 13.9.
When a supplier has access to PII, privileged systems, or monitoring data, access control evidence is not separate from supplier assurance. It is part of the same audit trail.
The procurement trap: signed contracts without assurance operations
The most common NIS2 supplier governance failure is not the absence of contracts. It is the gap between contract language and day-to-day operation.
A contract may require annual penetration test summaries, but no owner requests them. It may require 24-hour incident notification, but the supplier only has a generic support address. It may require subcontractor approval, but procurement never receives change notices. It may include audit rights, but the organization has no process to evaluate SOC report exceptions. It may require data deletion on exit, but IT never validates account deactivation.
The Zenith Blueprint, Controls in Action phase, Step 23, explains how supplier controls come to life:
“In practice, this control comes to life through:
✓ Supplier risk assessments, ✓ Pre-engagement due diligence questionnaires, ✓ Contract templates with embedded security terms, ✓ Supplier onboarding checklists that include access provisioning and monitoring setup, ✓ Ongoing reassessments, especially when supplier scope changes, incidents occur, or renewals come due.
And this control doesn’t stop at tier one suppliers. Your vendor may outsource to their own providers, and you may still bear the risk.”
That is the board-level NIS2 message: outsourcing service delivery does not outsource accountability.
NIS2 supplier contract remediation checklist
Start with your top 20 suppliers by criticality and run a focused remediation exercise:
- Identify suppliers supporting essential or important services.
- Confirm whether each supplier processes PII, supports regulated services, or has privileged access.
- Assign a business owner, procurement owner, and security reviewer.
- Verify that the supplier risk assessment is current and aligned with the actual service scope.
- Confirm the contract includes security baseline, incident notification, audit or evidence rights, subcontractor controls, continuity, secure transfer, access control, vulnerability cooperation, and exit clauses.
- Confirm breach timelines support 24-hour and 72-hour escalation needs where relevant.
- Request updated assurance evidence, including certifications, SOC reports, penetration test summaries, BCP or DR tests, and incident history.
- Review evidence, do not just store it.
- Log exceptions and assign remediation owners.
- Update the SoA and risk register where supplier controls support NIS2, GDPR, DORA, or customer commitments.
- Schedule monitoring frequency based on supplier criticality.
- Test one supplier incident escalation path.
- Test one supplier termination path, including data return, deletion, asset recovery, and access revocation.
If you cannot prove these points for a critical supplier, the contract is not yet audit-ready.
Turn supplier clauses into supervisory evidence
NIS2 supplier governance is now a live operational discipline. Supervisory authorities, customers, certification auditors, privacy teams, financial-sector partners, and boards will not only ask whether supplier clauses exist. They will ask whether the clauses are risk-based, enforceable, monitored, evidenced, and connected to incident reporting, continuity, access control, vulnerability management, subcontractor flow-down, and exit.
Clarysec helps organizations close that gap with the Zenith Blueprint for turning supplier controls into ISMS phases, risk treatment, SoA entries, onboarding routines, and audit evidence. Zenith Controls maps ISO/IEC 27002:2022 supplier controls A.5.19, A.5.20, and A.5.22 to NIS2, DORA, GDPR, NIST, COBIT 2019, supporting ISO standards, and audit methodologies. Clarysec supplier and privacy policies provide the clause structure, evidence expectations, and monitoring routines that make supplier assurance defensible.
Your next action is simple: select five critical suppliers, sample their contracts, map each clause to ISO/IEC 27001:2022 risk treatment and Annex A controls, request fresh assurance evidence, and run a 24-hour incident notification tabletop. If the evidence trail breaks, Clarysec’s toolkits give you the structure to repair it before an incident, customer review, or supervisory request does it for you.
Frequently Asked Questions
About the Author

Igor Petreski
Compliance Systems Architect, Clarysec LLC
Igor Petreski is a cybersecurity leader with over 30 years of experience in information technology and a dedicated decade specializing in global Governance, Risk, and Compliance (GRC).Core Credentials & Qualifications:• MSc in Cyber Security from Royal Holloway, University of London• PECB-Certified ISO/IEC 27001 Lead Auditor & Trainer• Certified Information Systems Auditor (CISA) from ISACA• Certified Information Security Manager (CISM) from ISACA • Certified Ethical Hacker from EC-Council