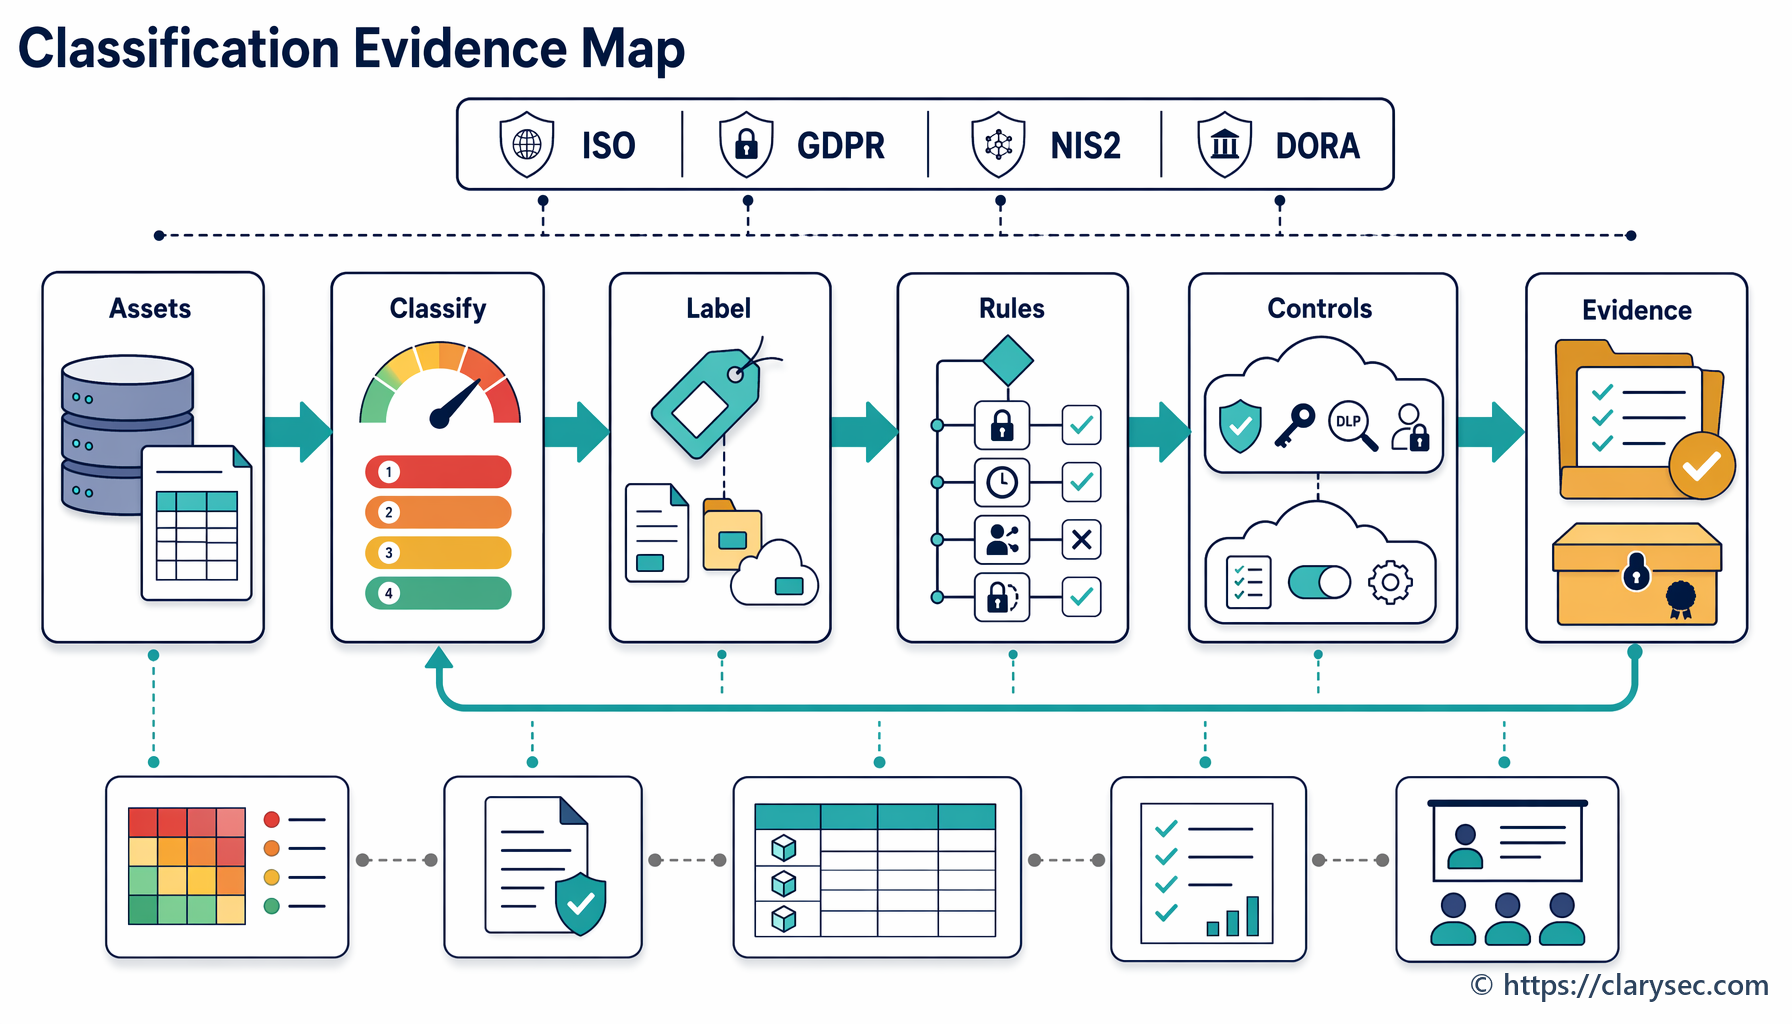
Data Classification for ISO 27001, GDPR, NIS2 and DORA
A practical CISO guide to using data classification and information labelling as the evidence layer for ISO/IEC 27001:2022, GDPR Article 32, NIS2 Article 21 and DORA ICT risk management.
Articles tagged with "Access Control"
A practical CISO guide to using data classification and information labelling as the evidence layer for ISO/IEC 27001:2022, GDPR Article 32, NIS2 Article 21 and DORA ICT risk management.
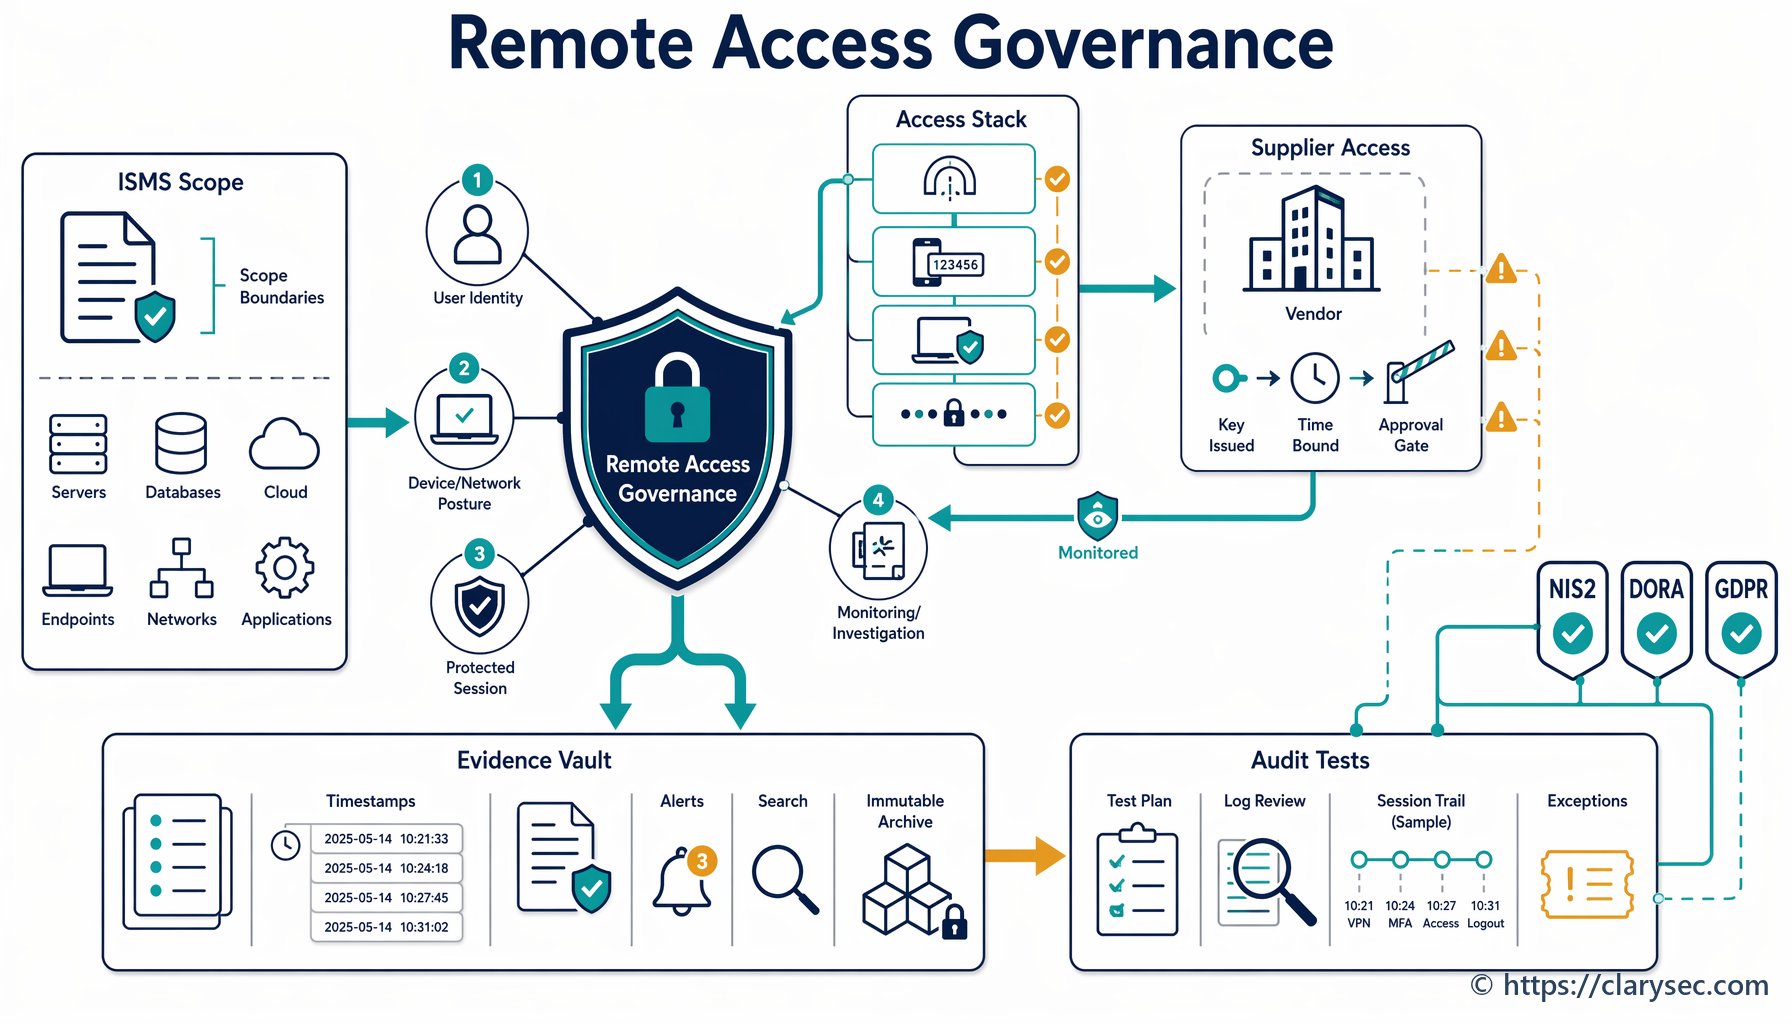
Remote access is no longer a narrow IT topic. In 2026, VPN, MFA, supplier access, endpoint posture, logging and patch evidence must satisfy ISO 27001 auditors, NIS2 management accountability, DORA ICT risk rules and GDPR Article 32 security obligations.
A practical guide for building audit-ready GDPR Article 32 technical and organisational measures using ISO 27001:2022, ISO 27005, NIS2, DORA and Clarysec toolkits.
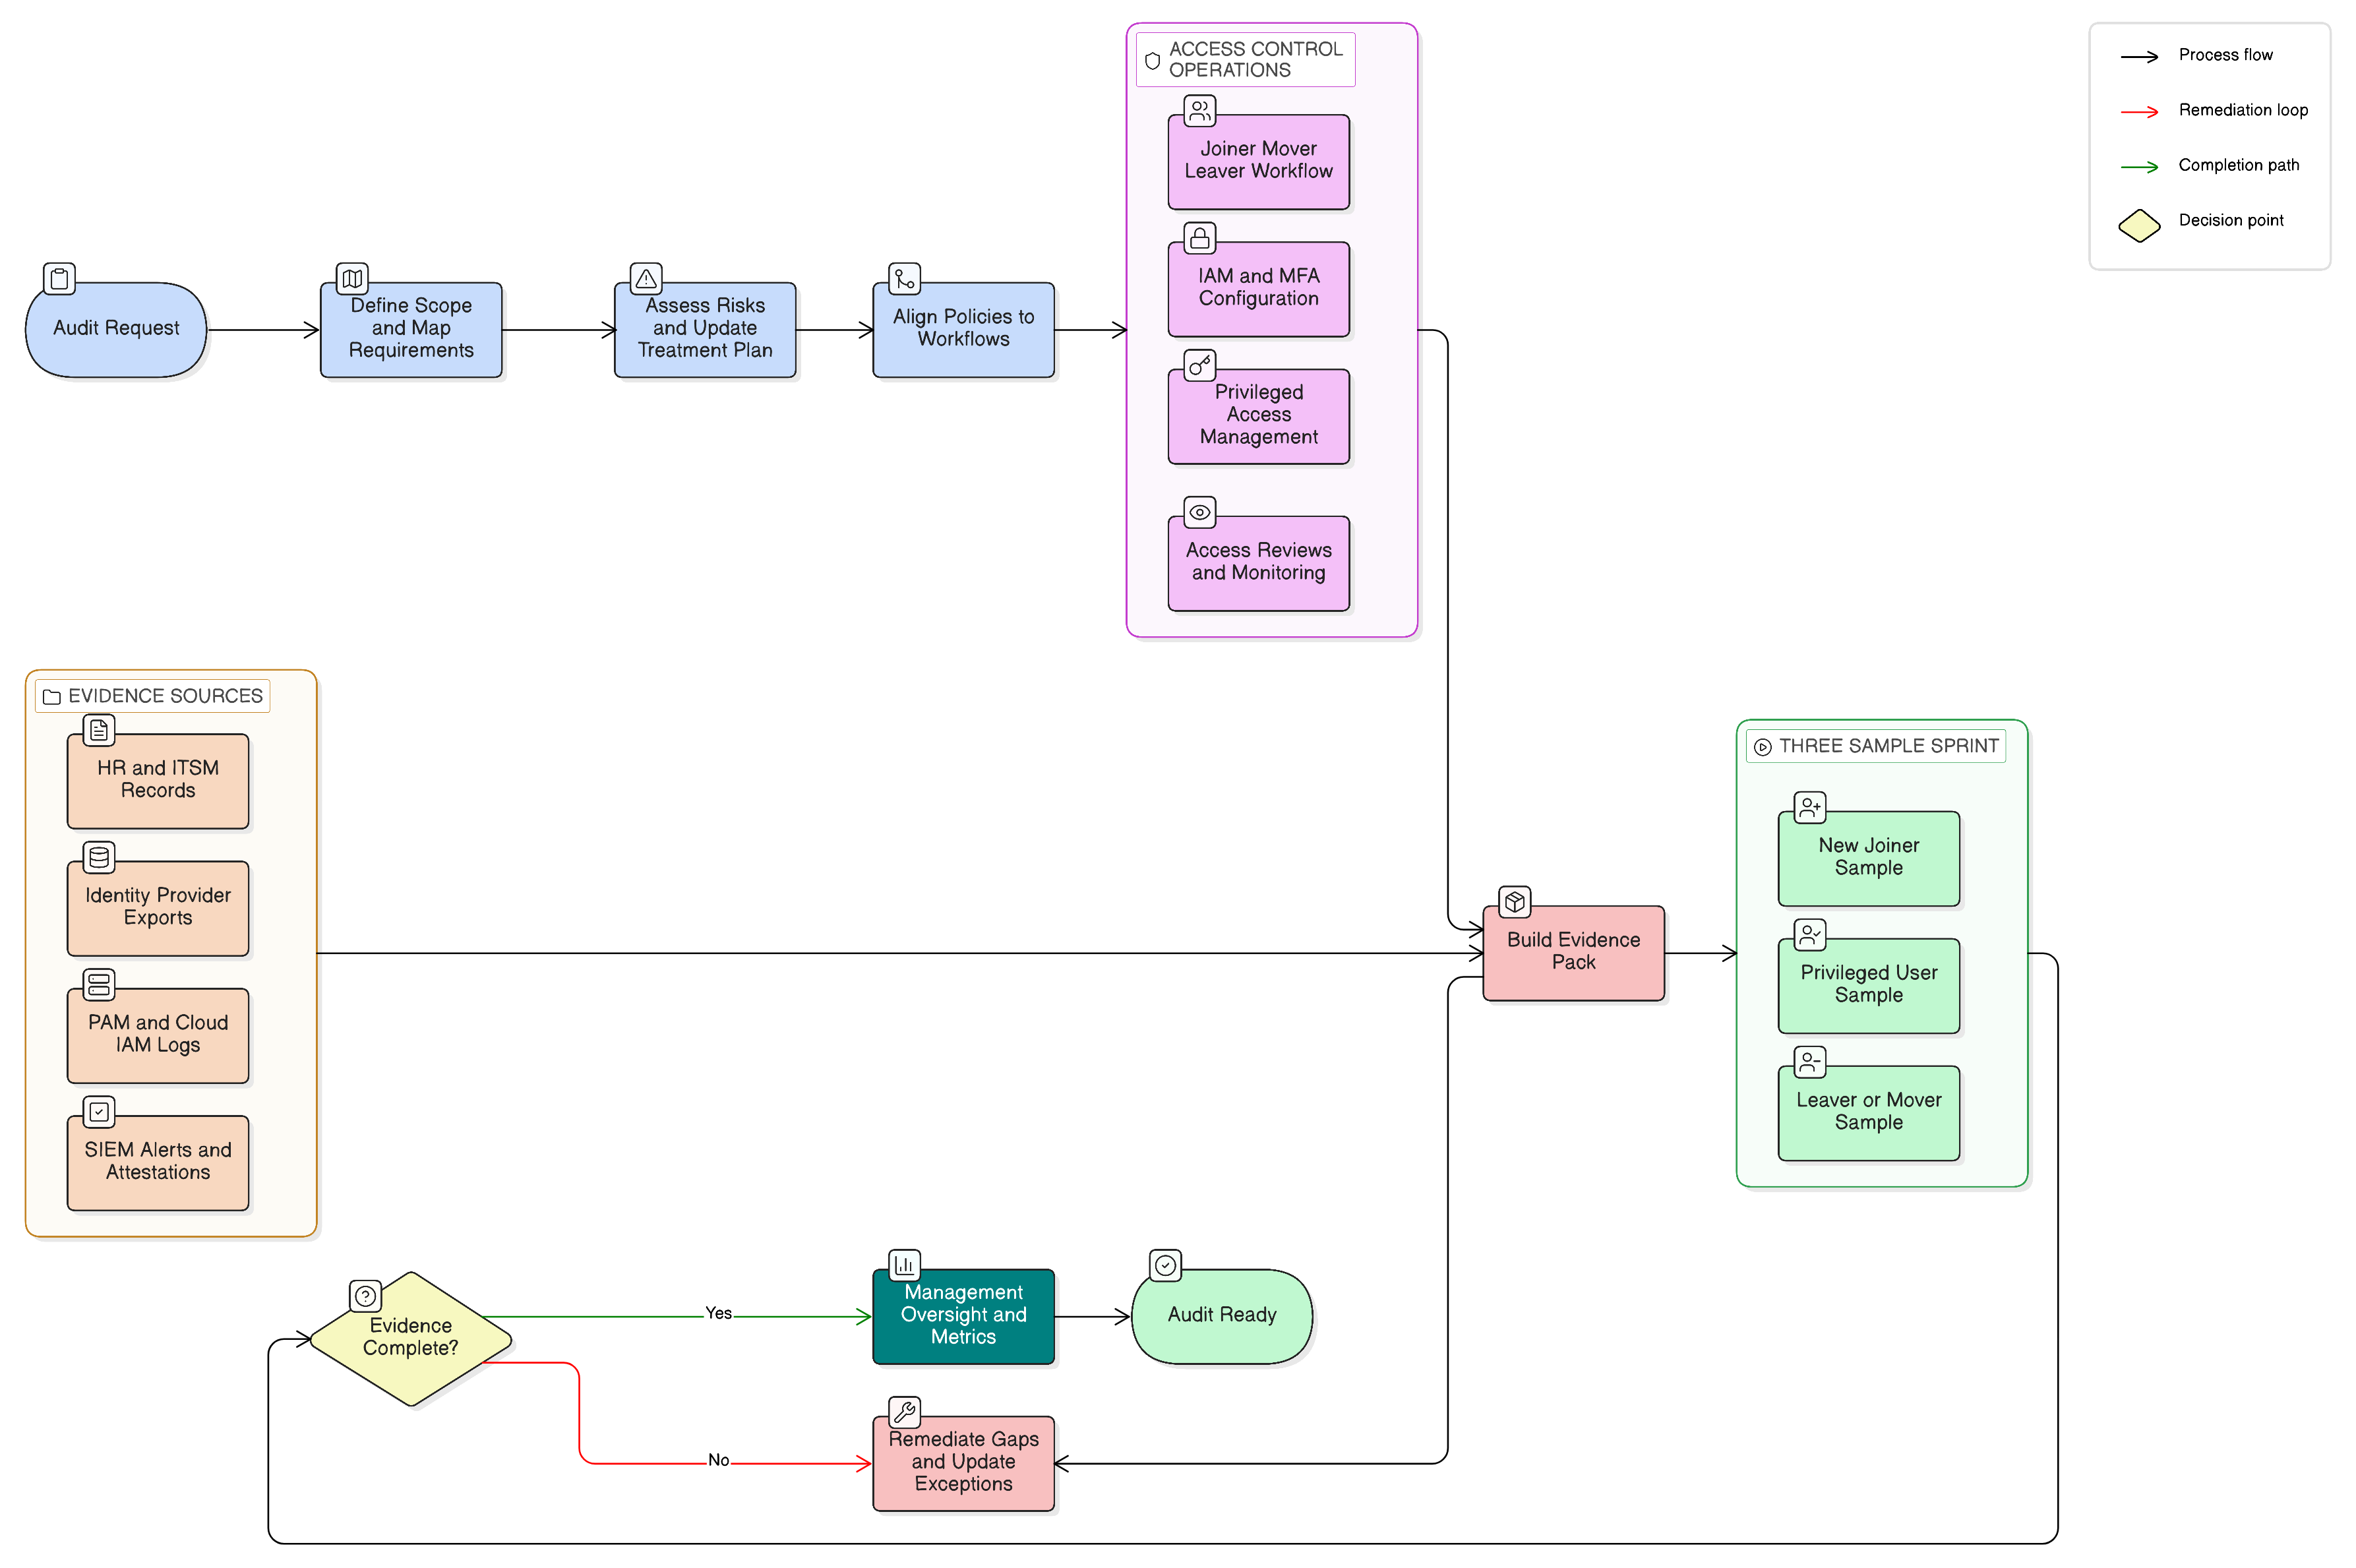
A practical CISO guide to building one access control evidence model for ISO/IEC 27001:2022, NIS2, DORA, GDPR, NIST and COBIT.
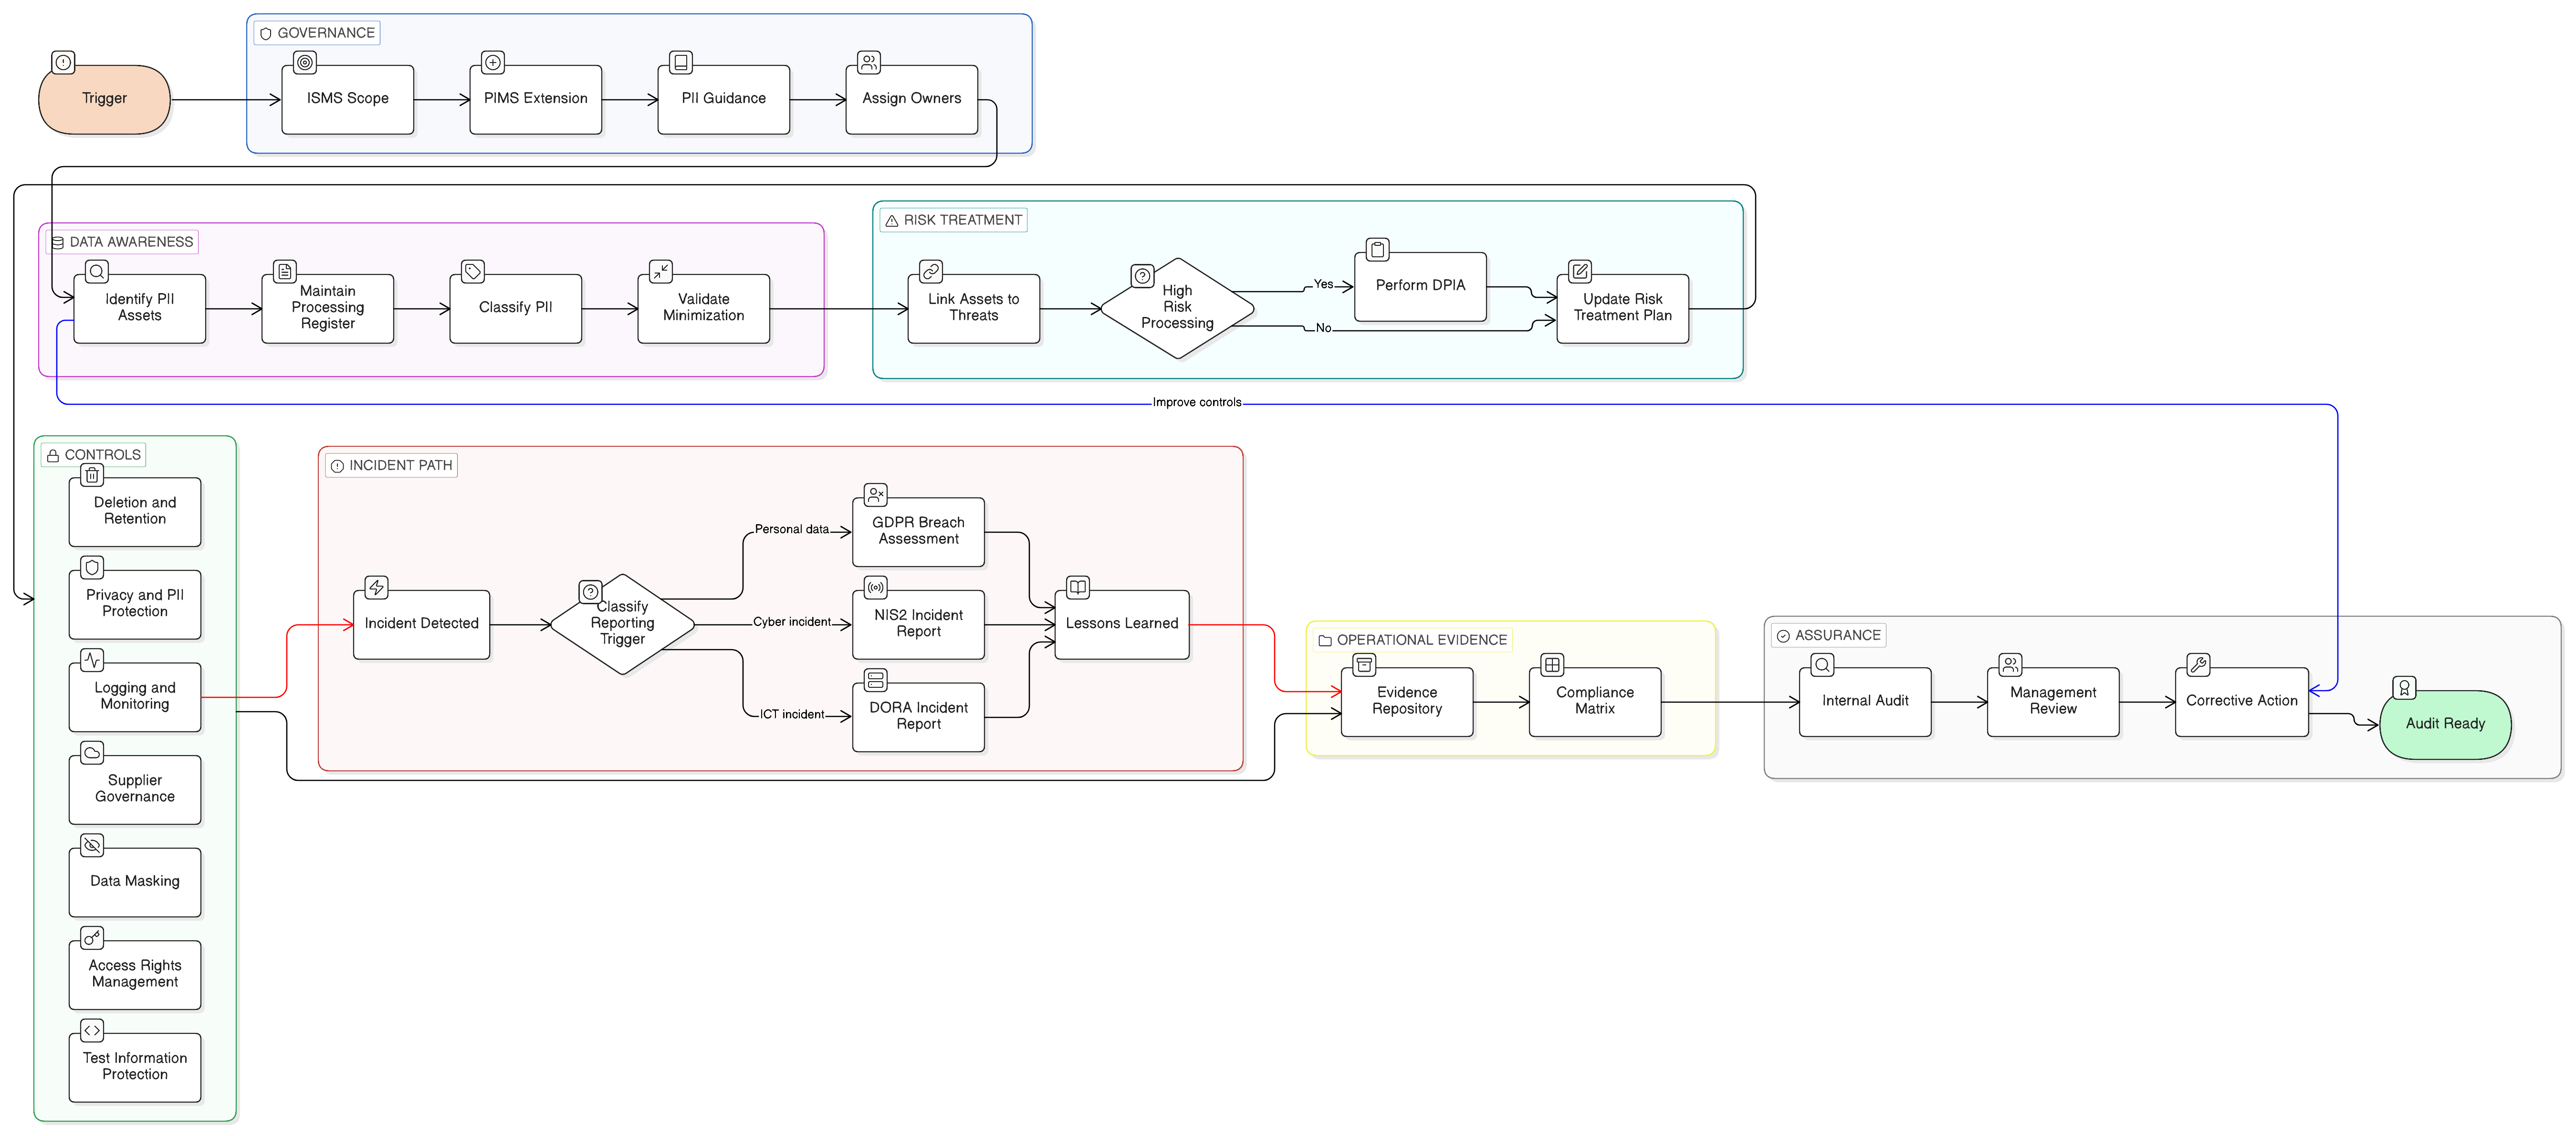
Learn how to build audit-ready PII protection controls by extending ISO/IEC 27001:2022 with ISO/IEC 27701:2025 and ISO/IEC 29151:2022, mapped to GDPR, NIS2, DORA, NIST-style assurance, and COBIT 2019 governance expectations.
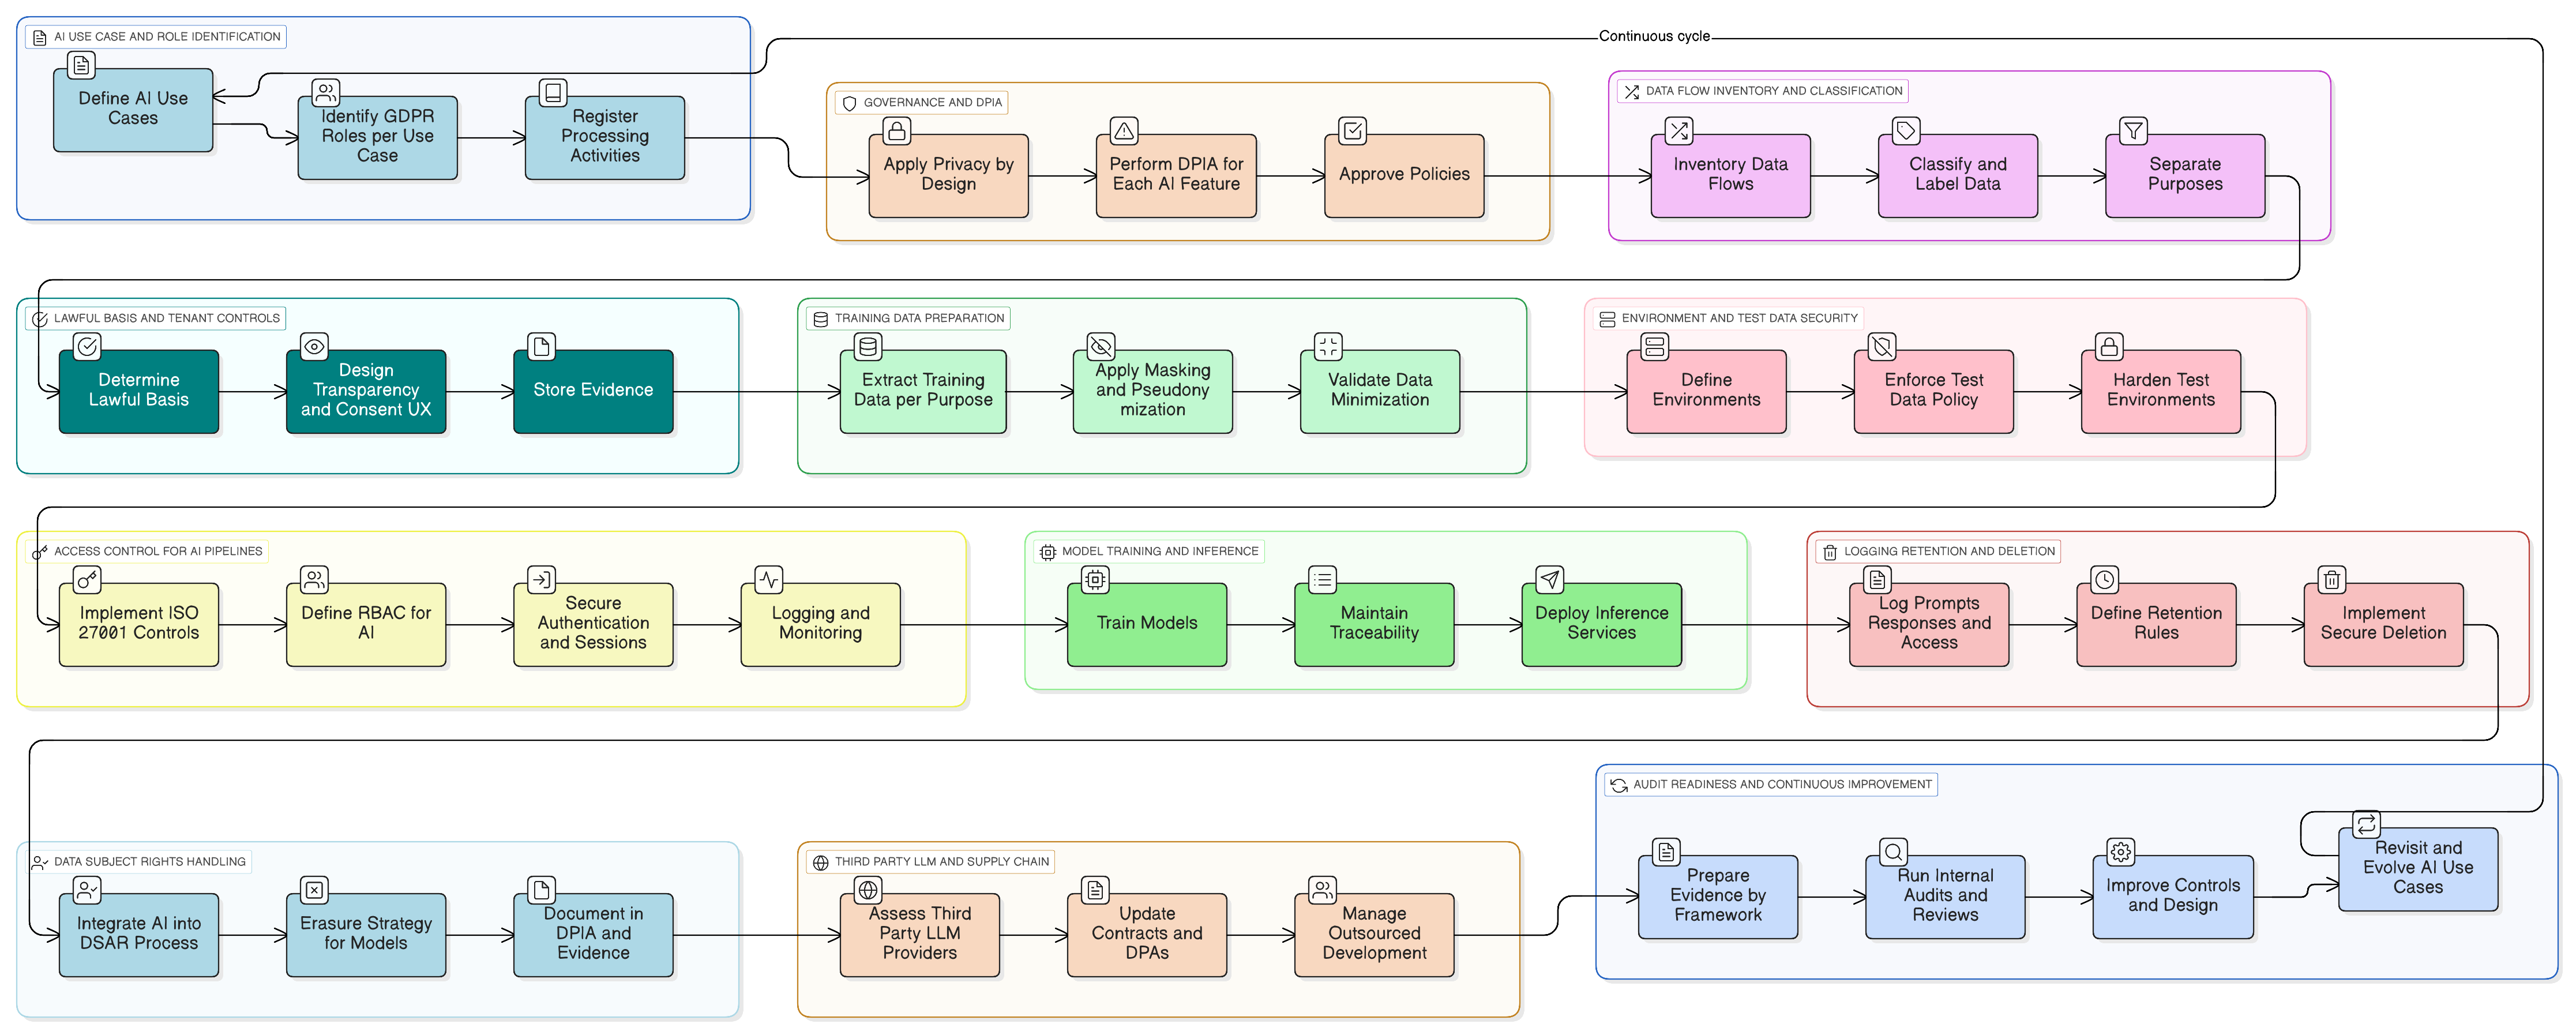
This article provides a practical playbook for CISOs to navigate the complex intersection of GDPR and AI. We offer a scenario-driven walkthrough for making SaaS products with LLMs compliant, focusing on training data, access controls, data subject rights, and multi-framework audit readiness.
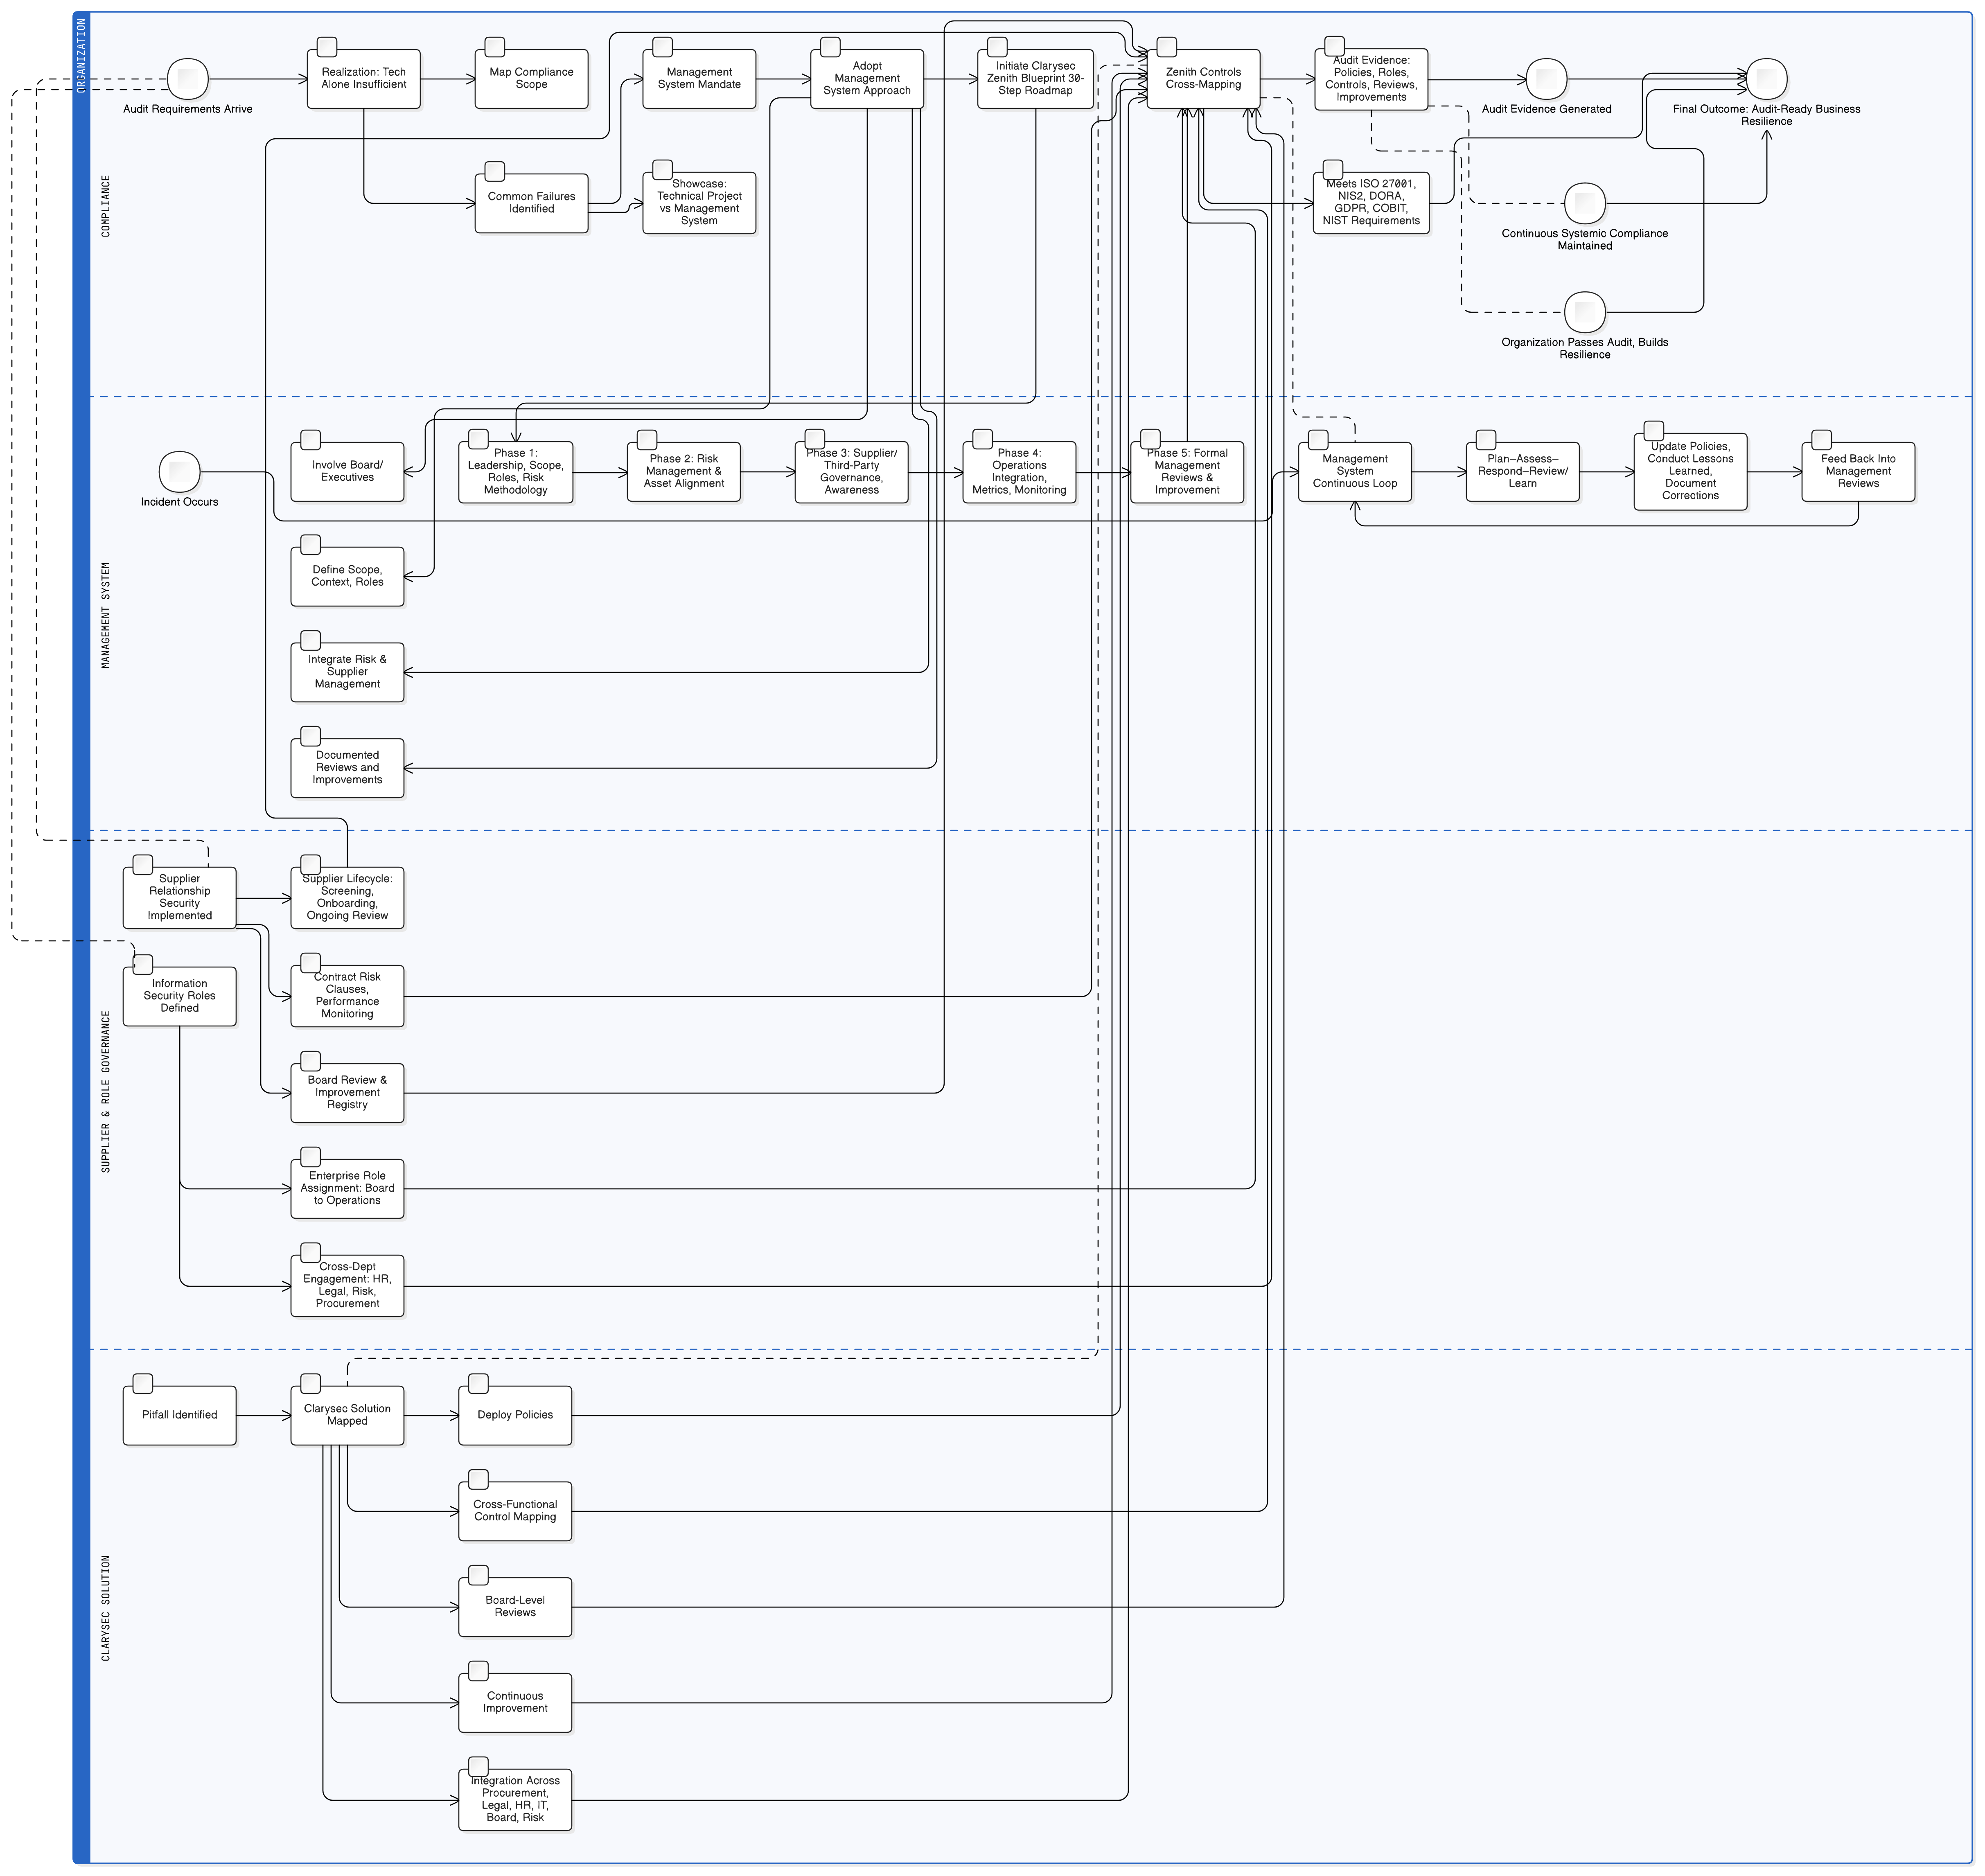
Audit disasters aren’t caused by weak firewalls, they’re the result of treating compliance as a tech checklist. Discover Clarysec’s management system strategies, mapped controls, and practical policies for seamless ISO 27001, NIS2, and DORA compliance.
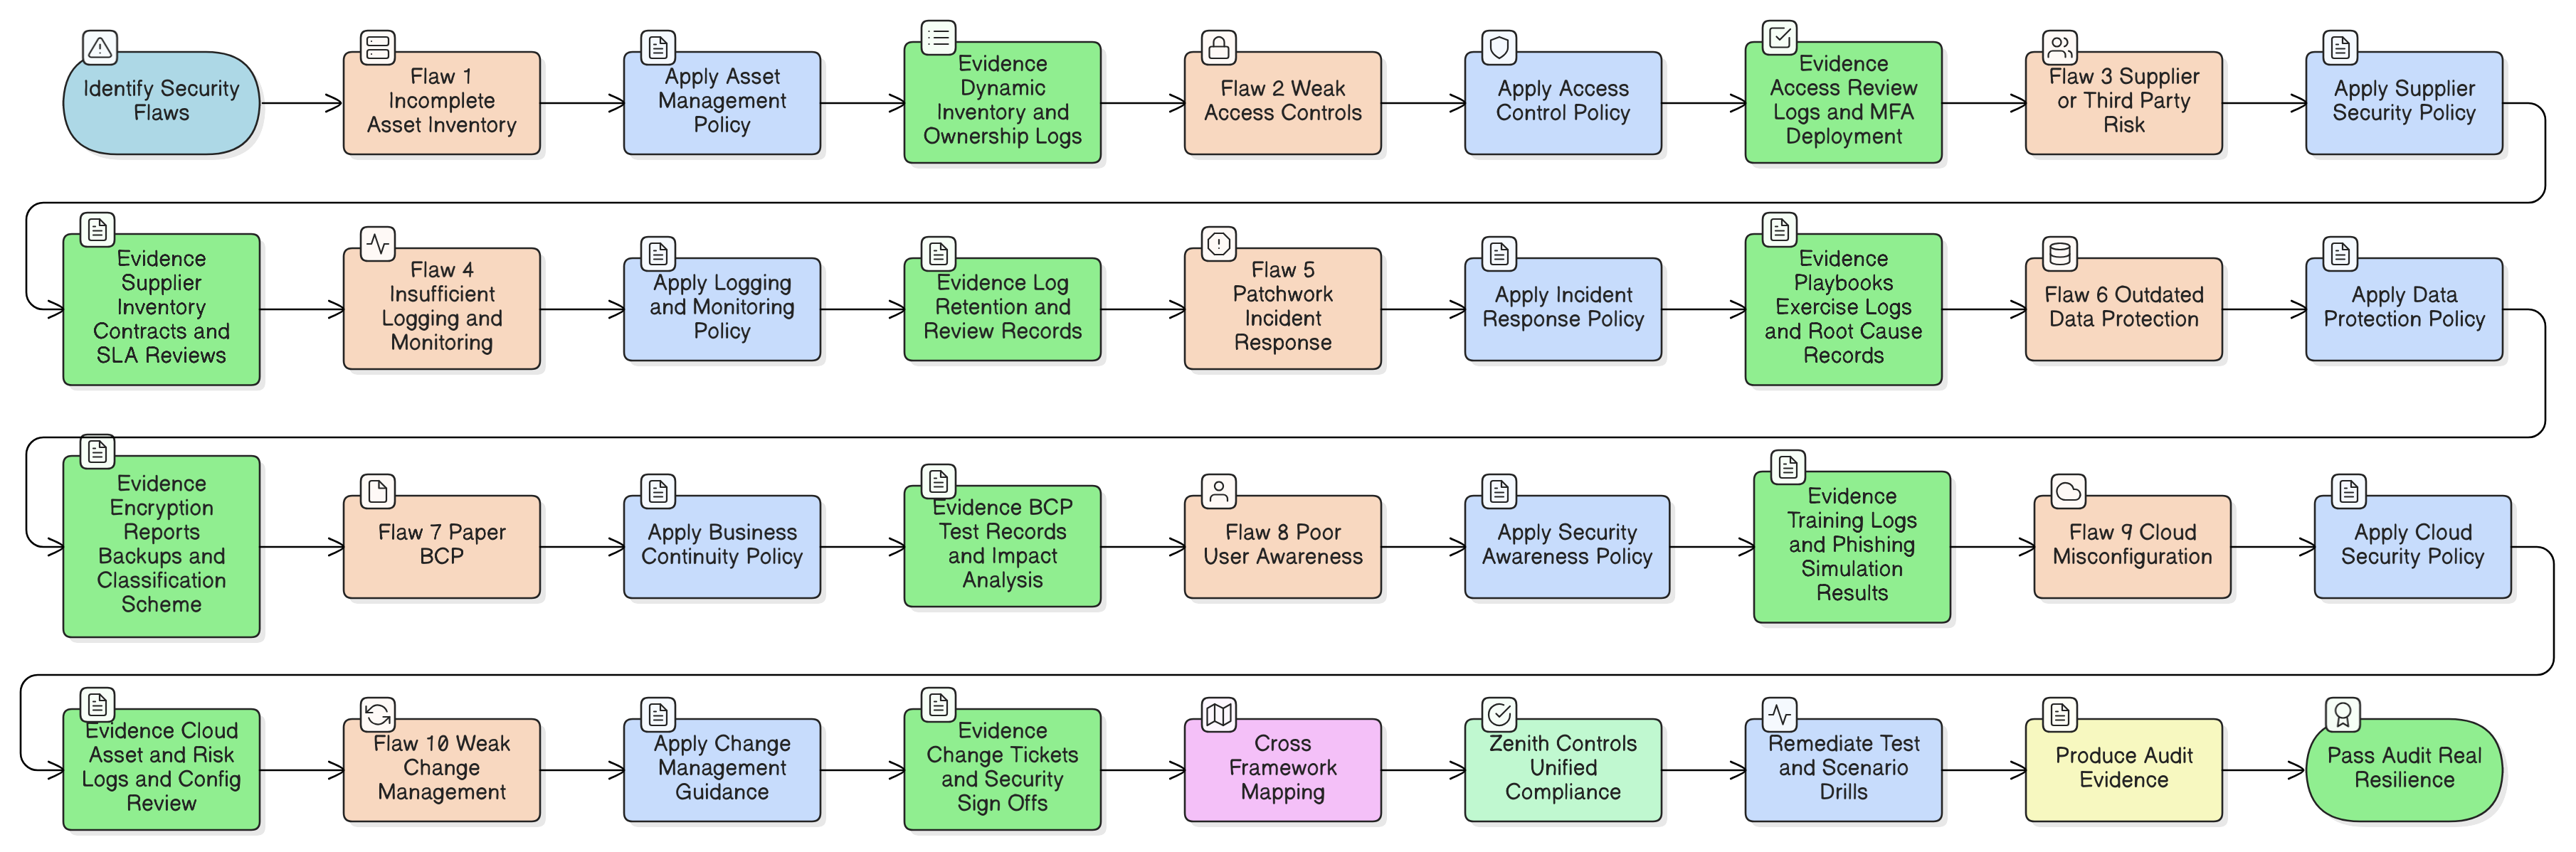
It was 2:00 PM on a Tuesday when Alex, the CISO at a fast-growing FinTech firm, was forced to stop their ransomware simulation. Sparks were flying on Slack, the board watched with growing alarm, and the DORA compliance deadline hovered menacingly. The simulation, intended to be routine, had snowballed into a showcase of vulnerabilities: entry points went undetected, critical assets weren’t prioritized, the communication plan failed, and supplier risk was murky at best.
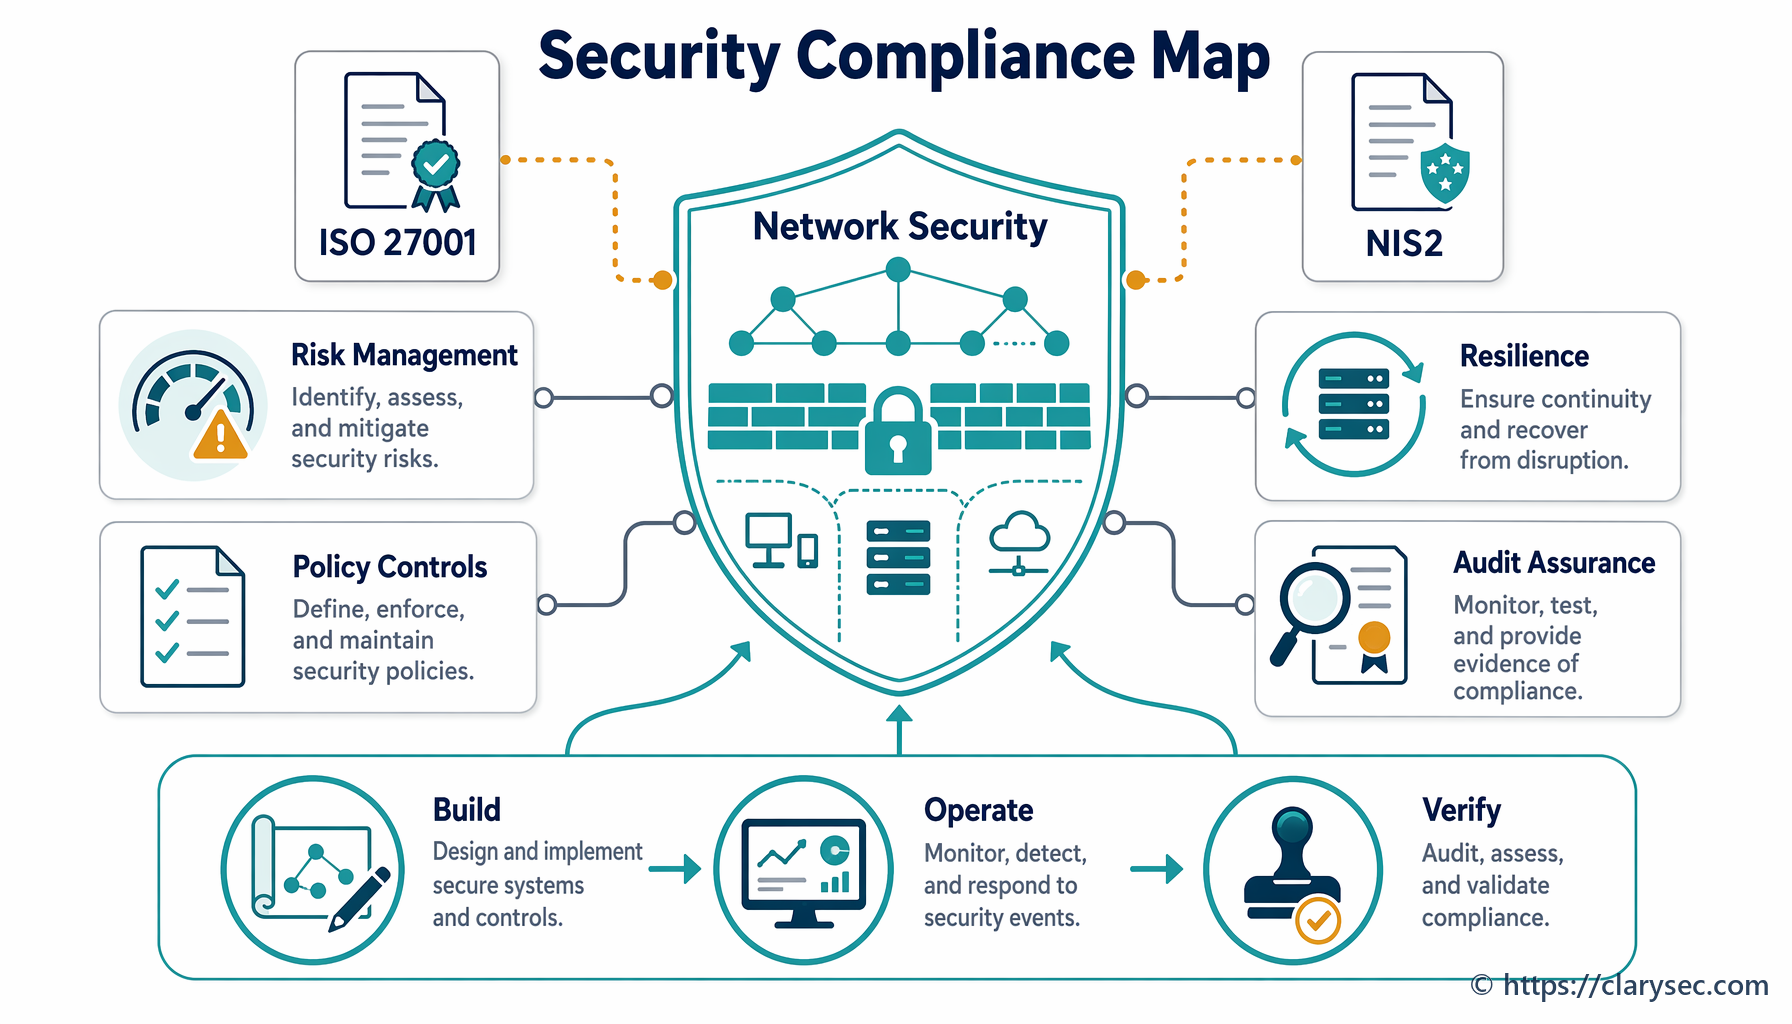
Network security is essential for ISO 27001 and NIS2 compliance, underpinning risk management, resilience, and regulatory assurance for modern organisations.