#Audit
Articles tagged with "Audit"
93 articles
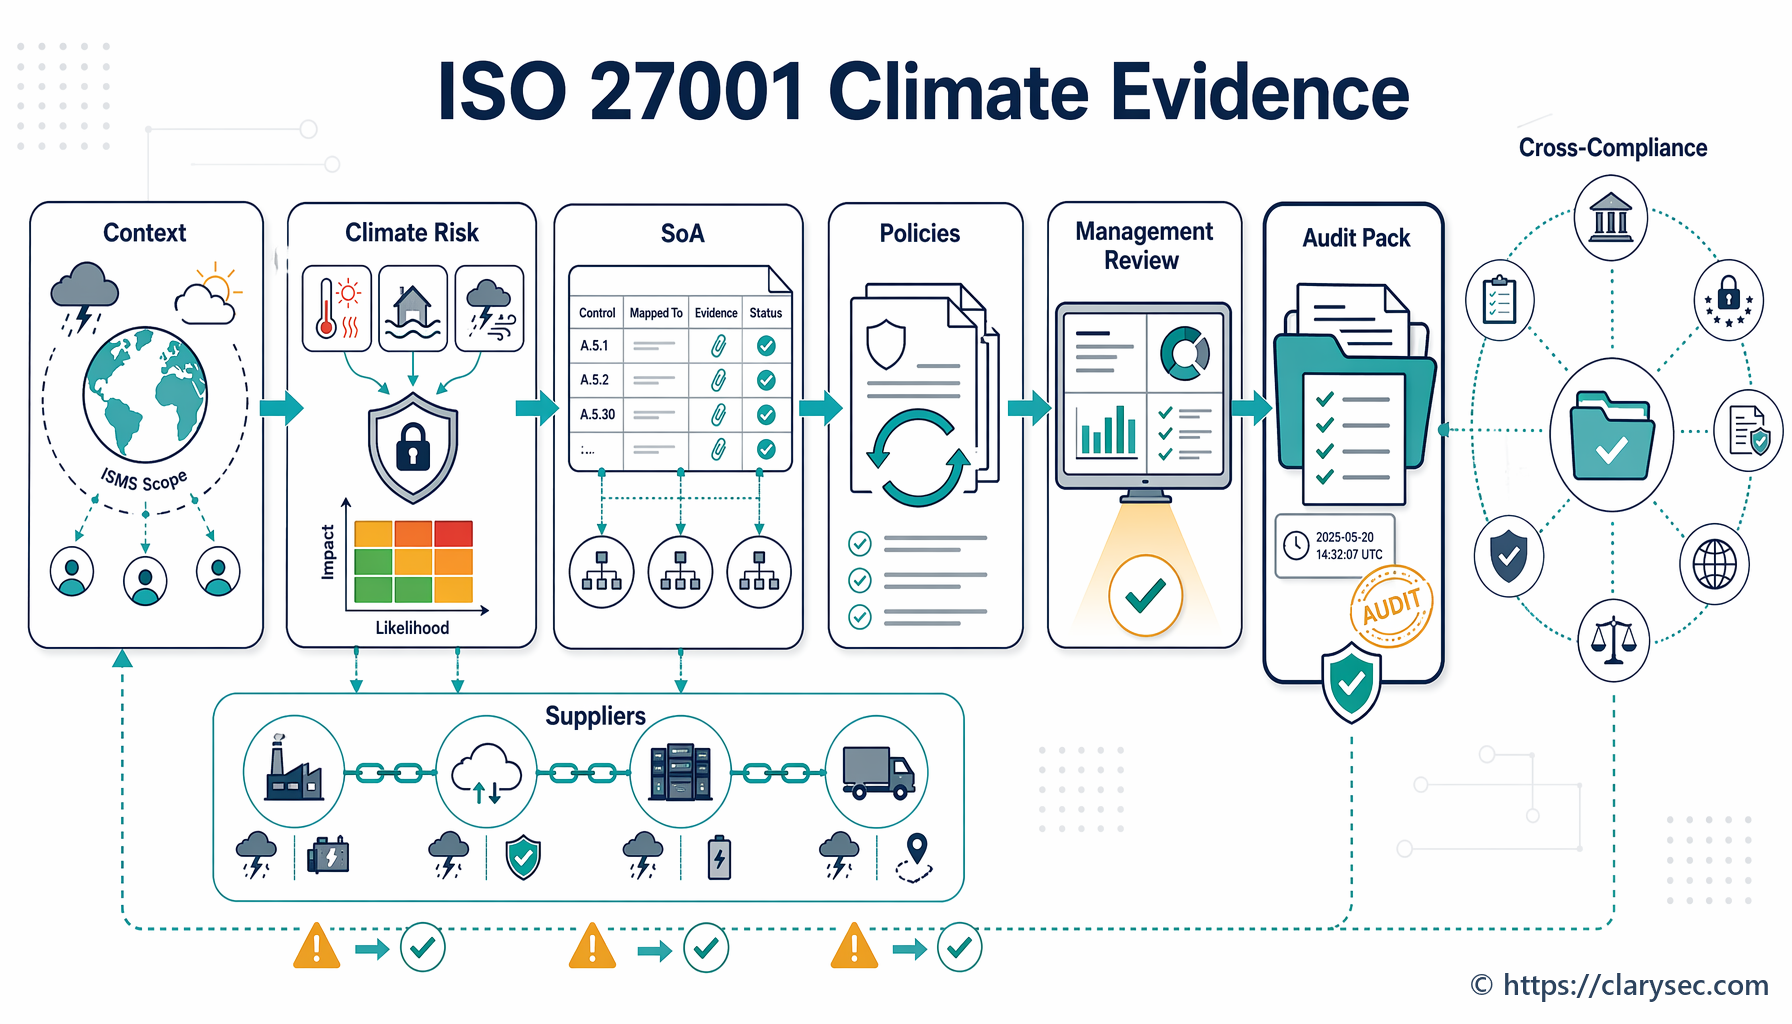
A practical guide for proving ISO 27001 climate change amendment readiness through ISMS context, interested parties, risk assessment, SoA rationale, business continuity, supplier assurance, and management review evidence.
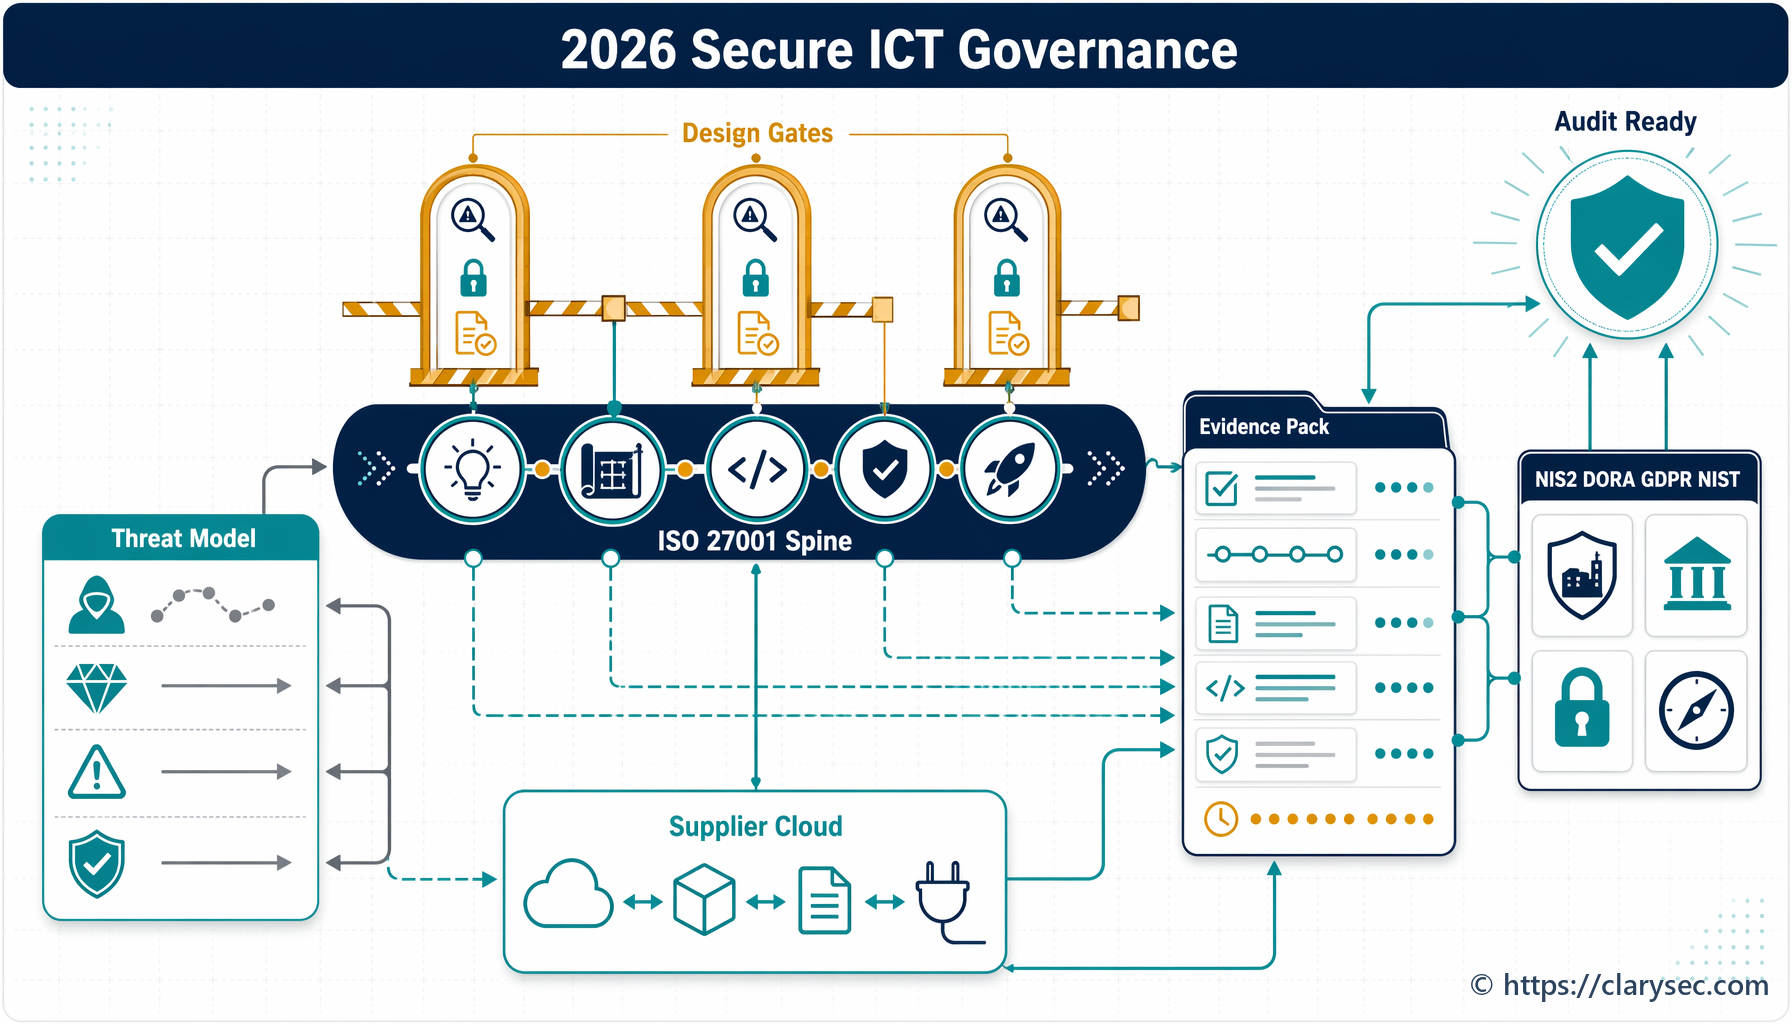
Learn how to embed security-by-design into ICT project governance using ISO/IEC 27001:2022, Clarysec policies, and reusable evidence mapped to NIS2, DORA, GDPR, and NIST CSF 2.0.
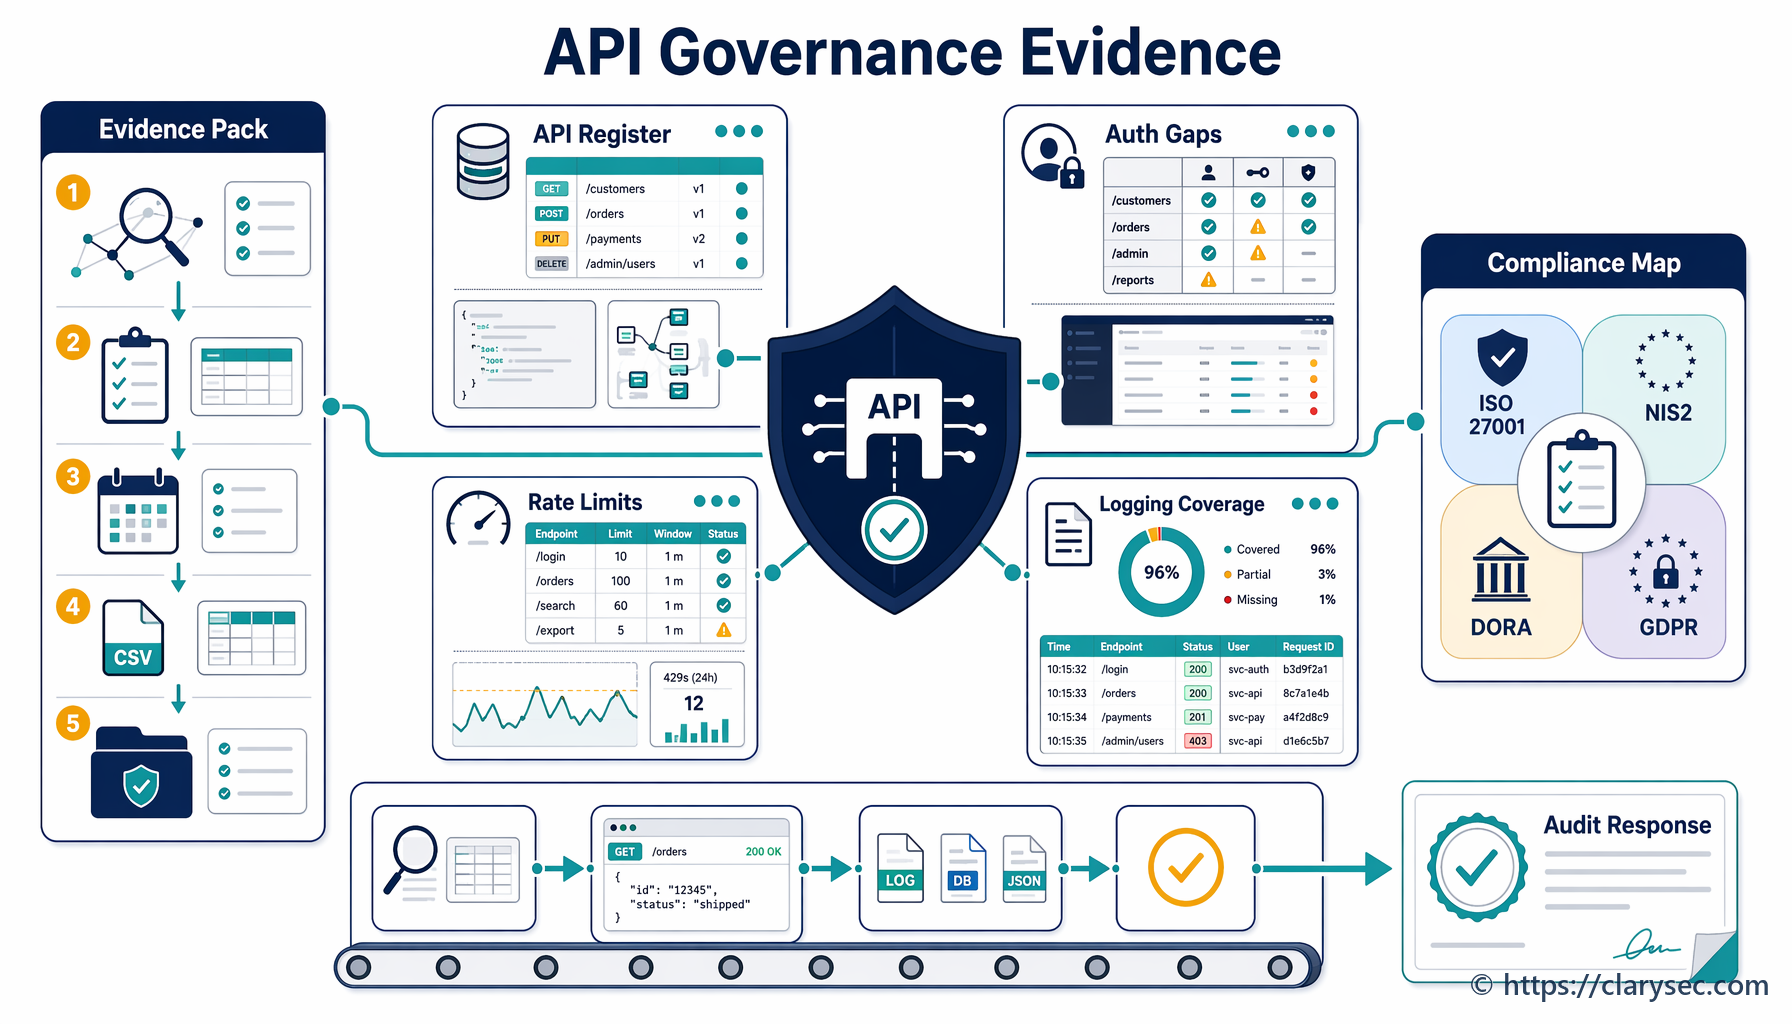
Shadow APIs, weak tokens, missing rate limits and inconsistent logs are now governance failures. This flagship guide shows CISOs how to build API security evidence for ISO/IEC 27001:2022, NIS2, DORA, GDPR, NIST CSF 2.0 and COBIT-aligned audits.
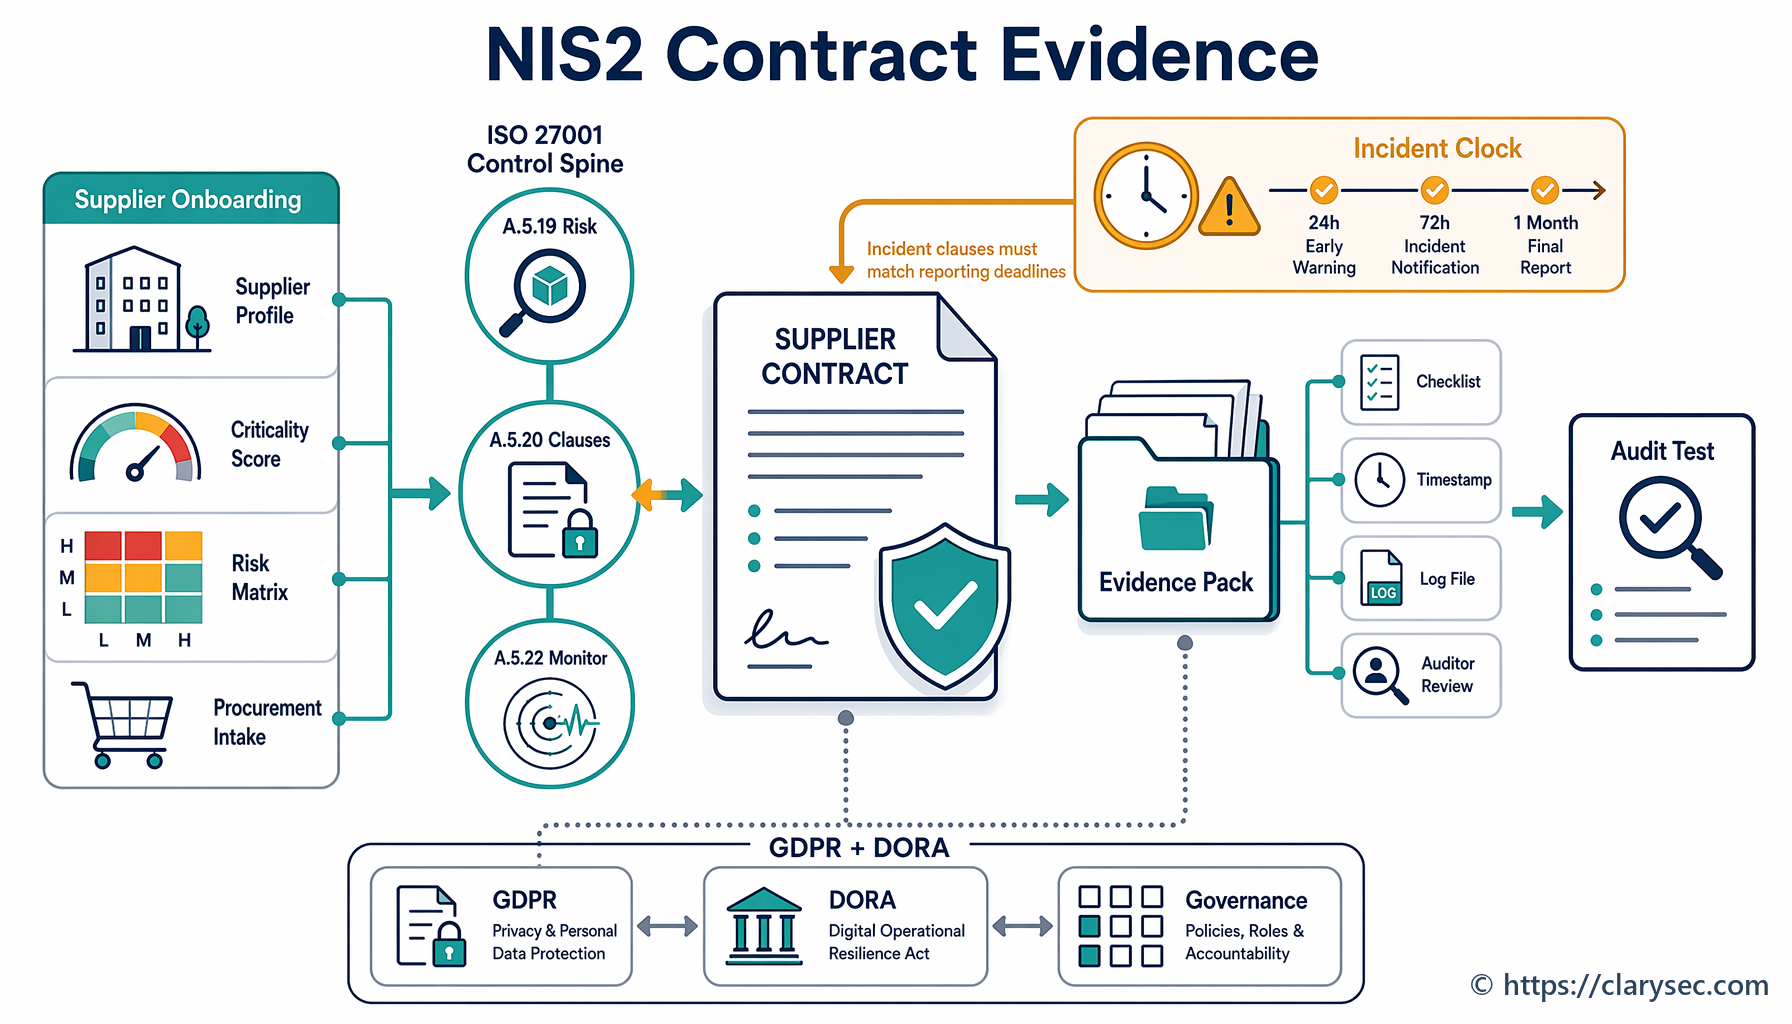
A practical Clarysec guide for turning NIS2 supplier contract clauses into audit-ready ISO/IEC 27001:2022 assurance evidence, GDPR accountability, DORA alignment, and board-level supplier governance.
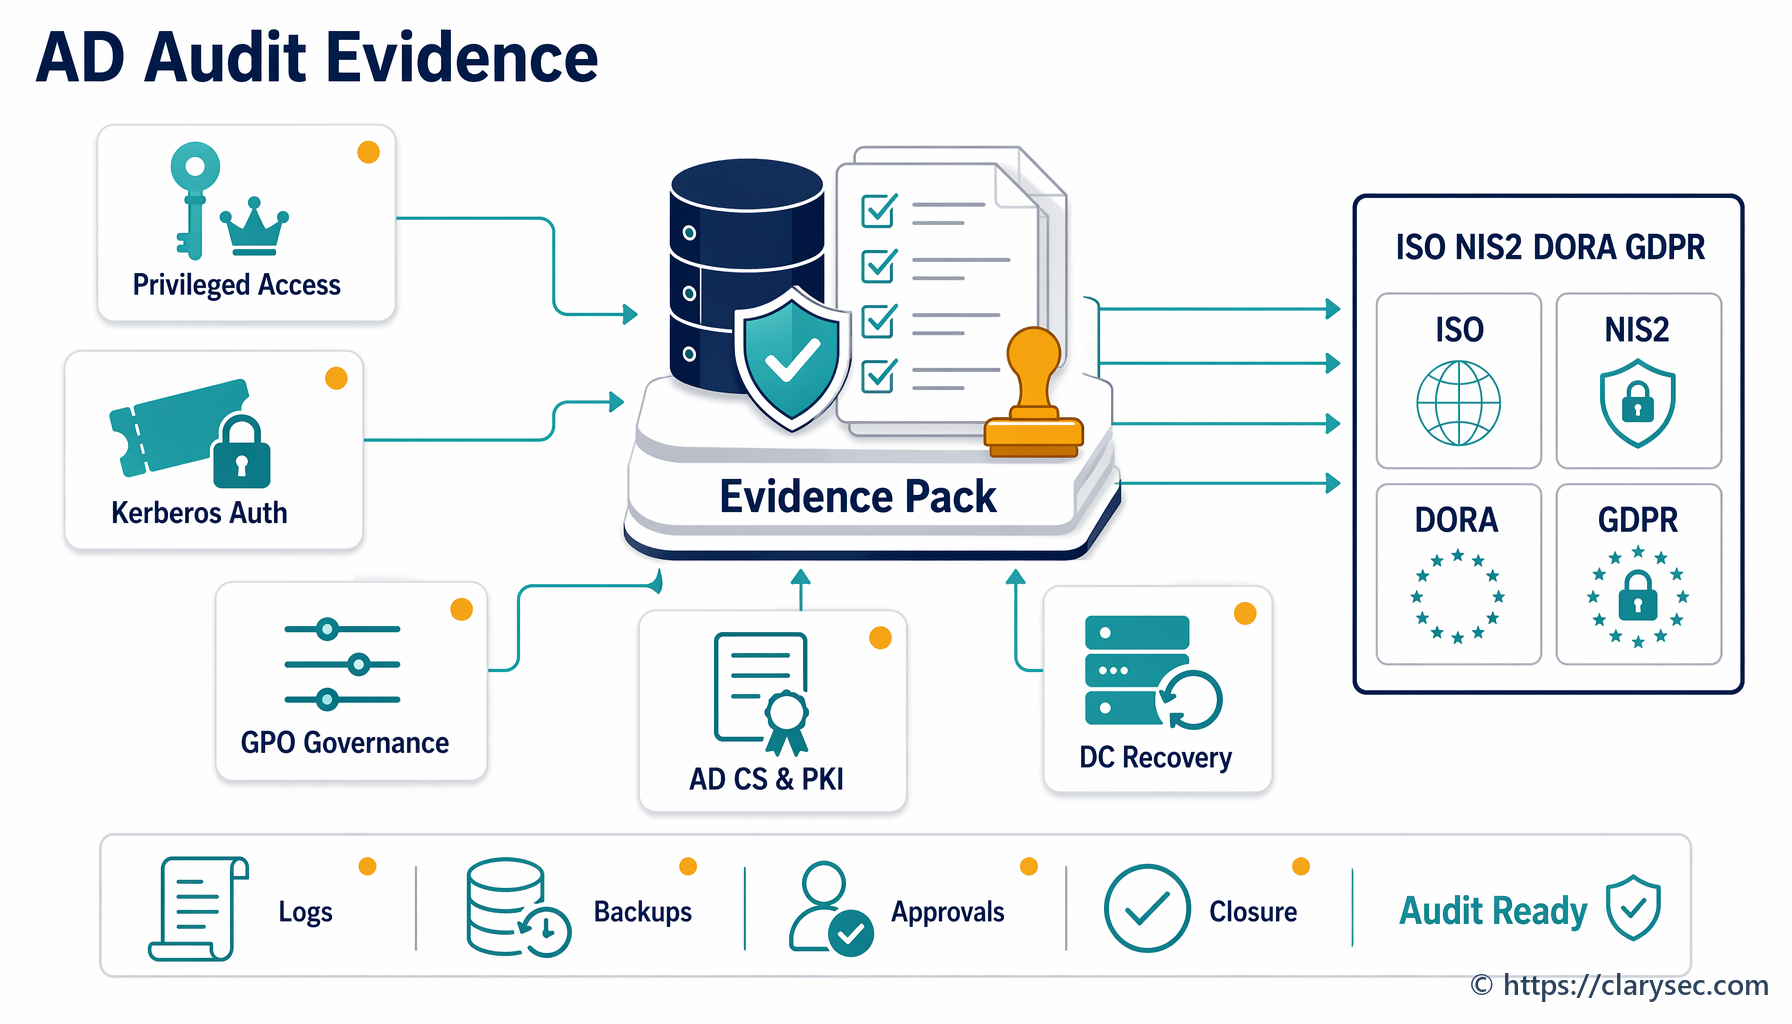
A scenario-driven CISO guide to turning Active Directory hardening into audit-ready evidence for ISO/IEC 27001:2022, NIS2, DORA, GDPR, NIST CSF 2.0 and governance reviews.
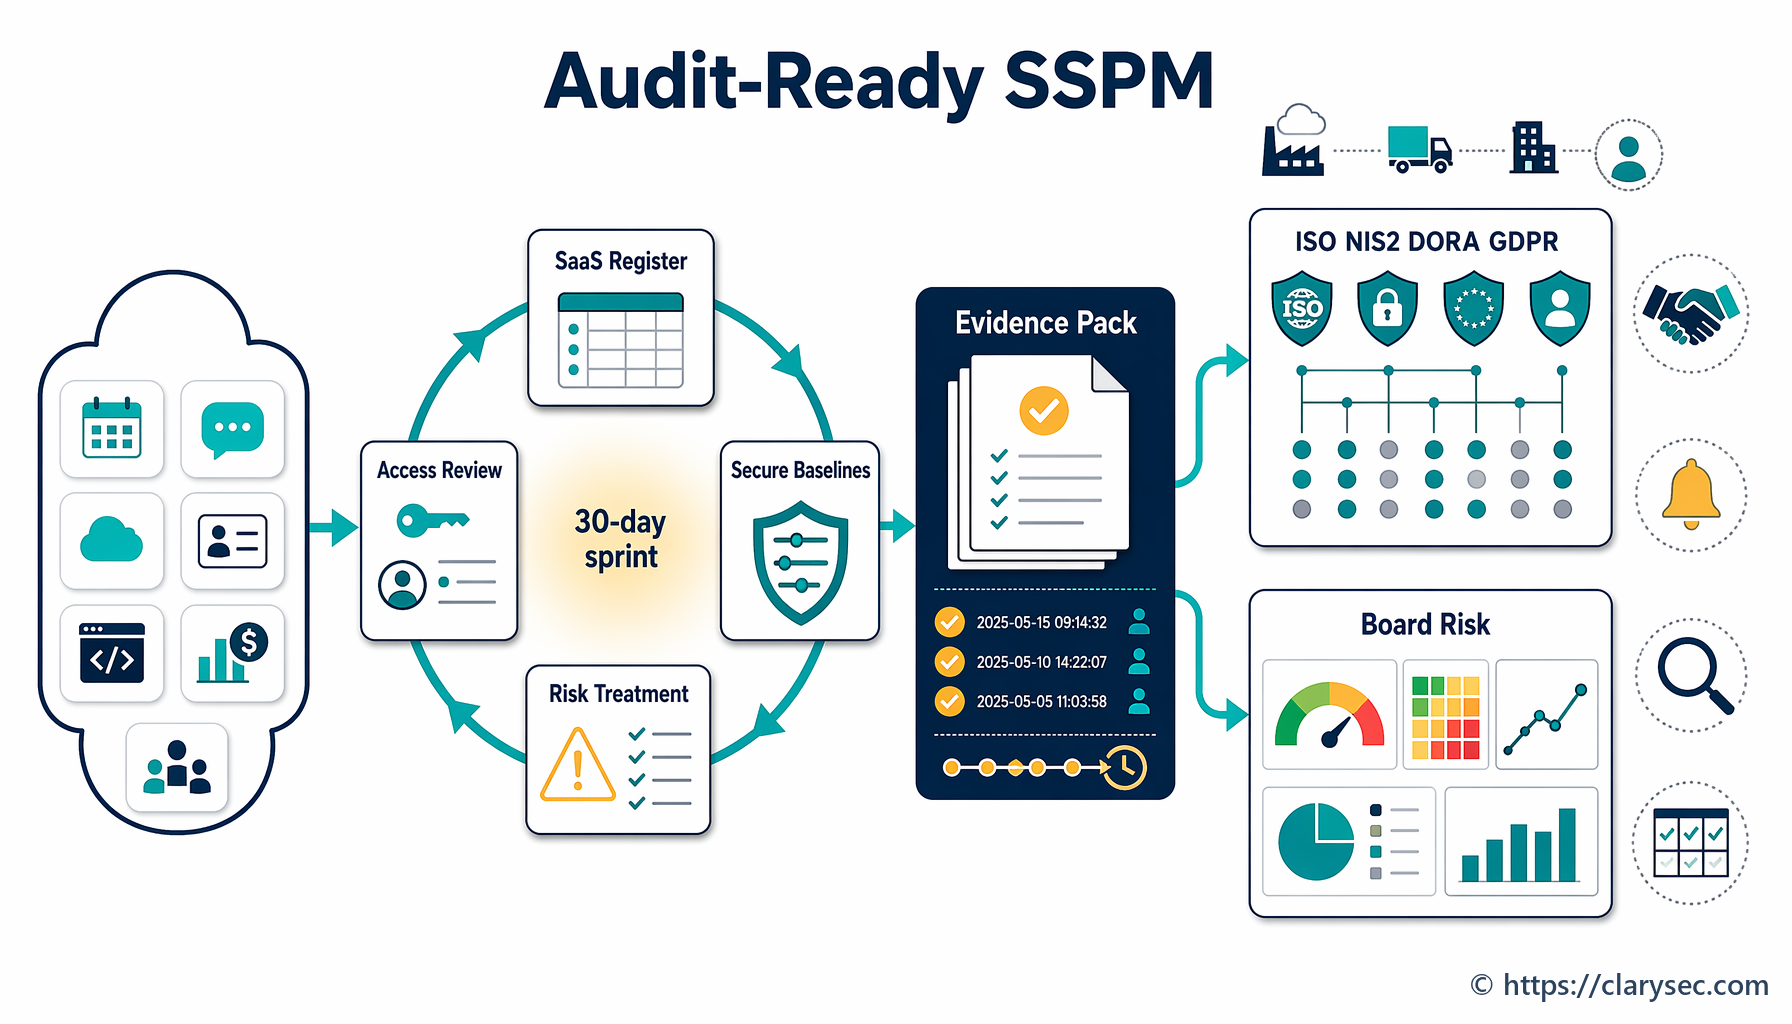
A practical CISO guide to using ISO/IEC 27001:2022 and Clarysec policy evidence to govern SaaS inventory, access, configuration, logging and suppliers for NIS2, DORA and GDPR.
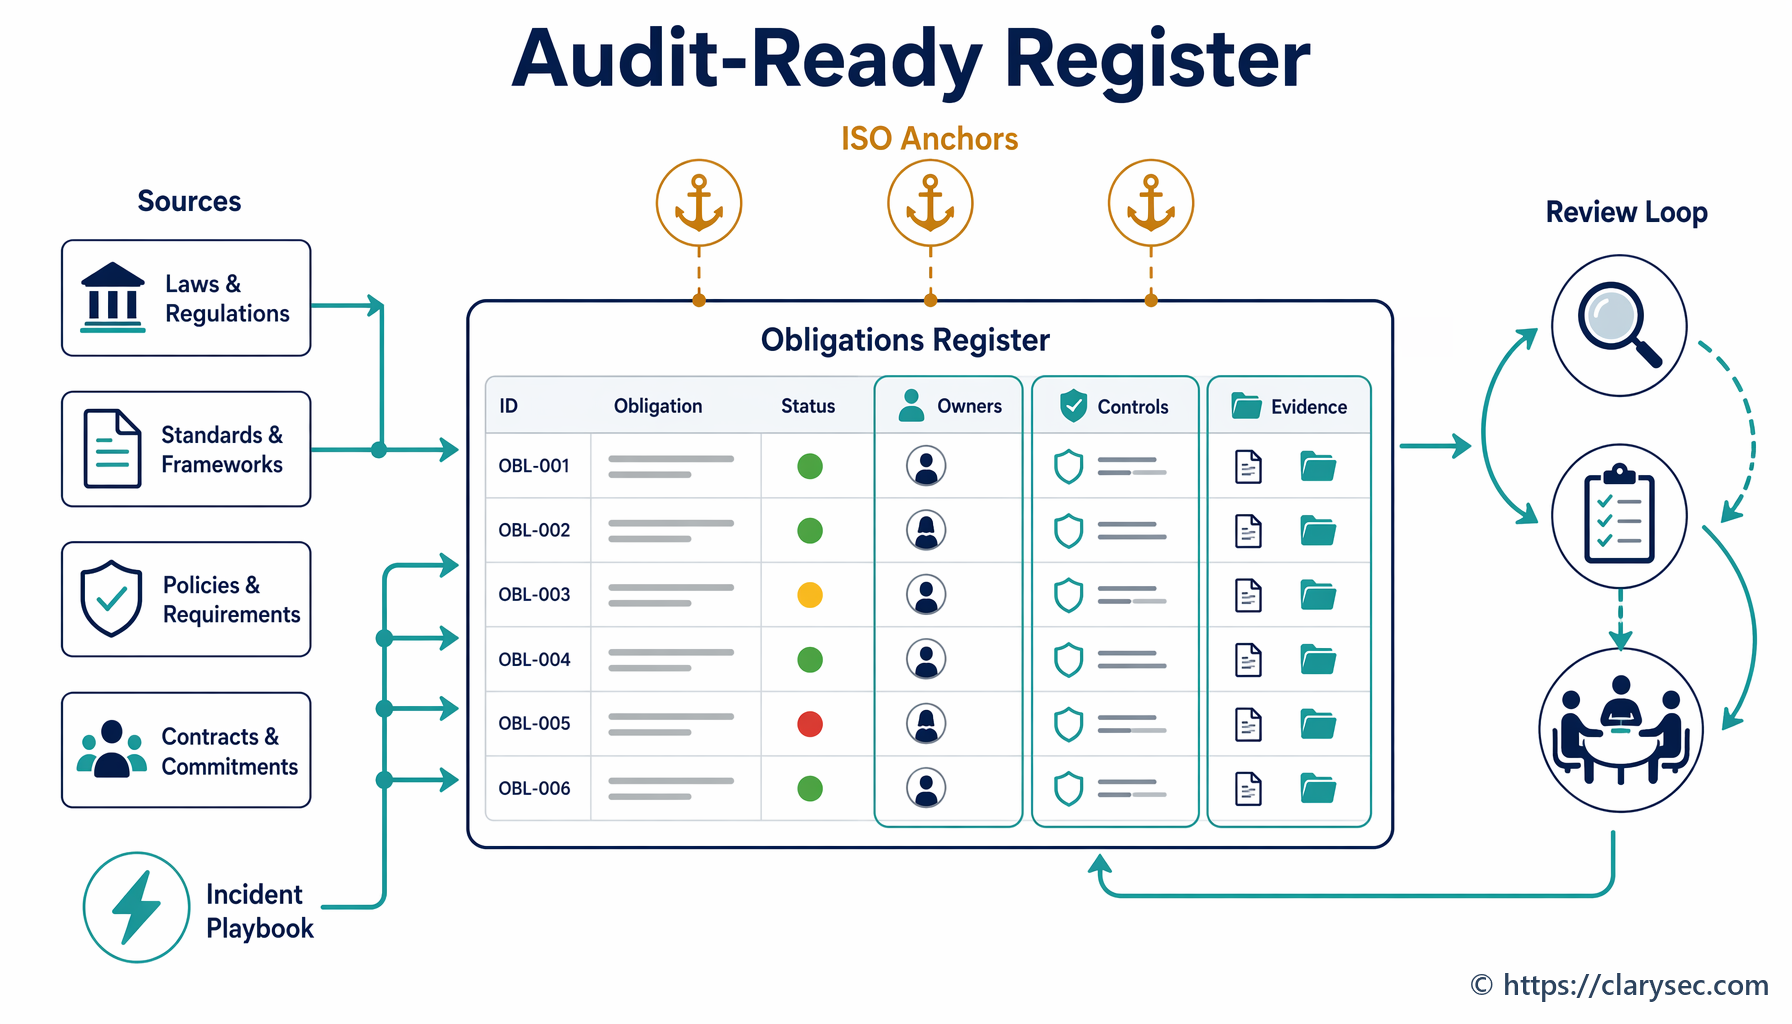
A practical guide to building a 2026 cybersecurity compliance obligations register that maps NIS2, DORA, GDPR, ISO/IEC 27001:2022 and customer contracts to owners, controls, evidence, audits and management review.
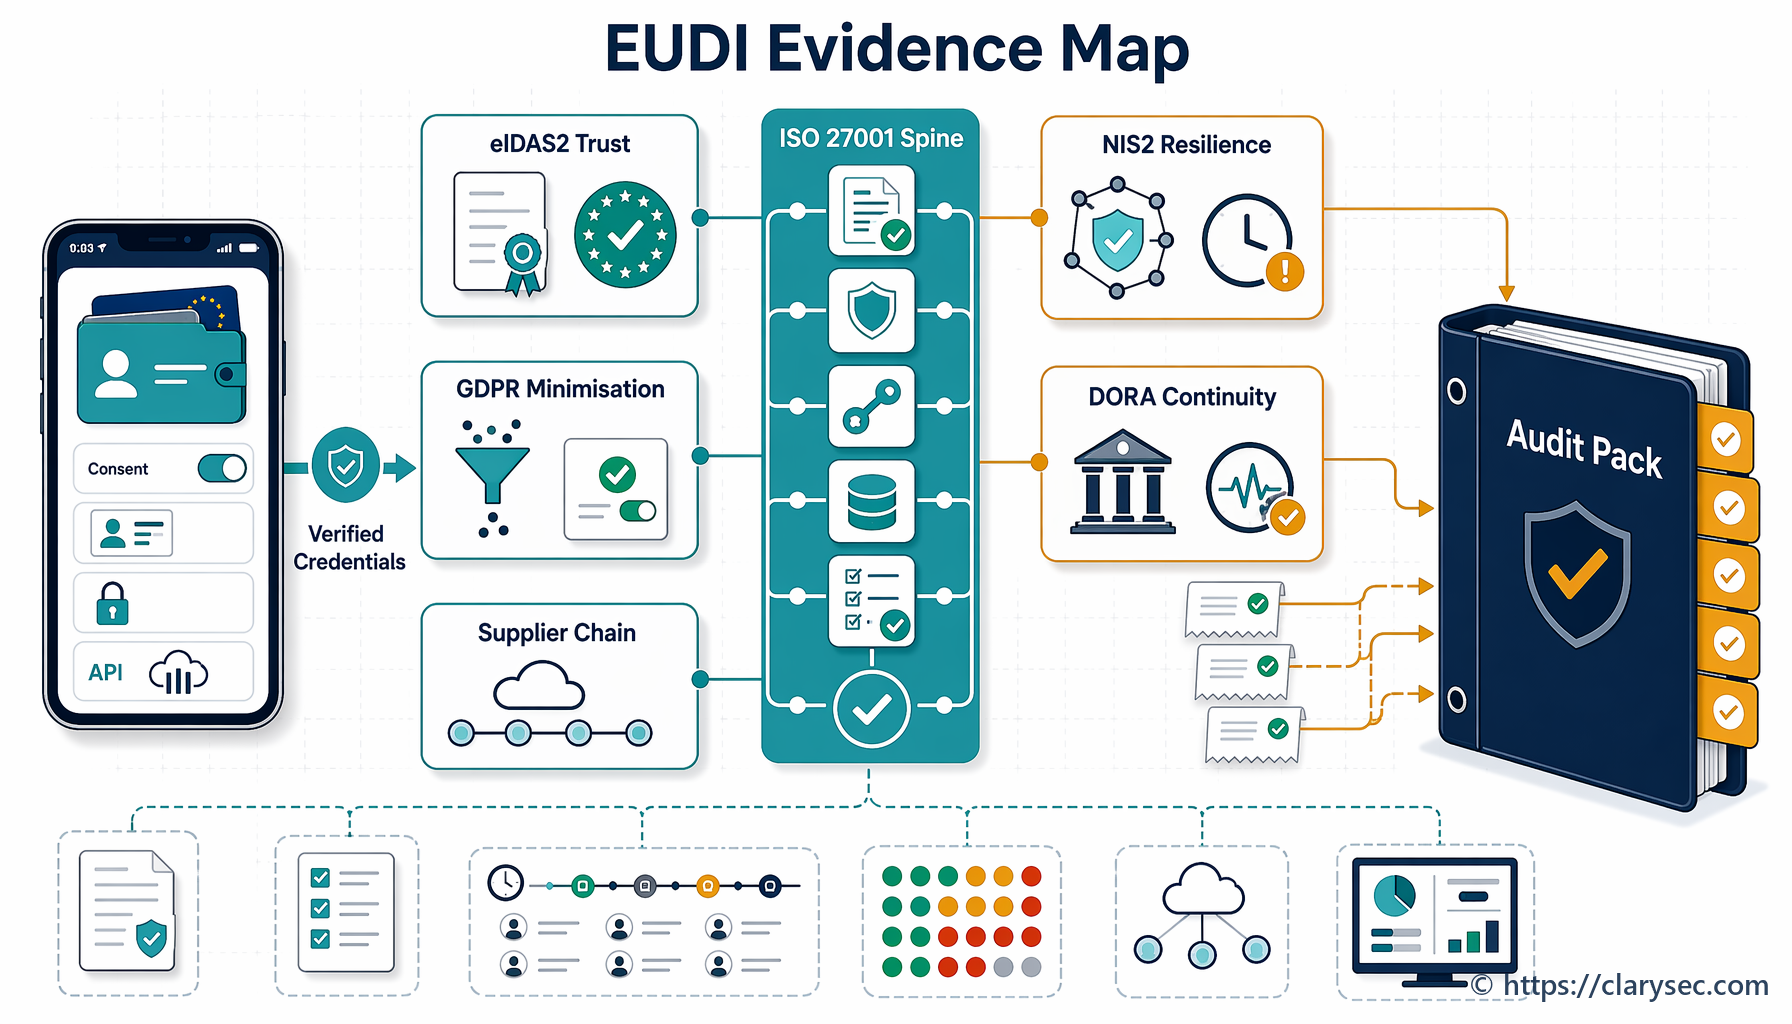
A practical CISO guide for mapping EU Digital Identity Wallet relying-party evidence into ISO/IEC 27001:2022, GDPR, NIS2, DORA, NIST CSF 2.0 and COBIT 2019 using Clarysec policies and toolkits.
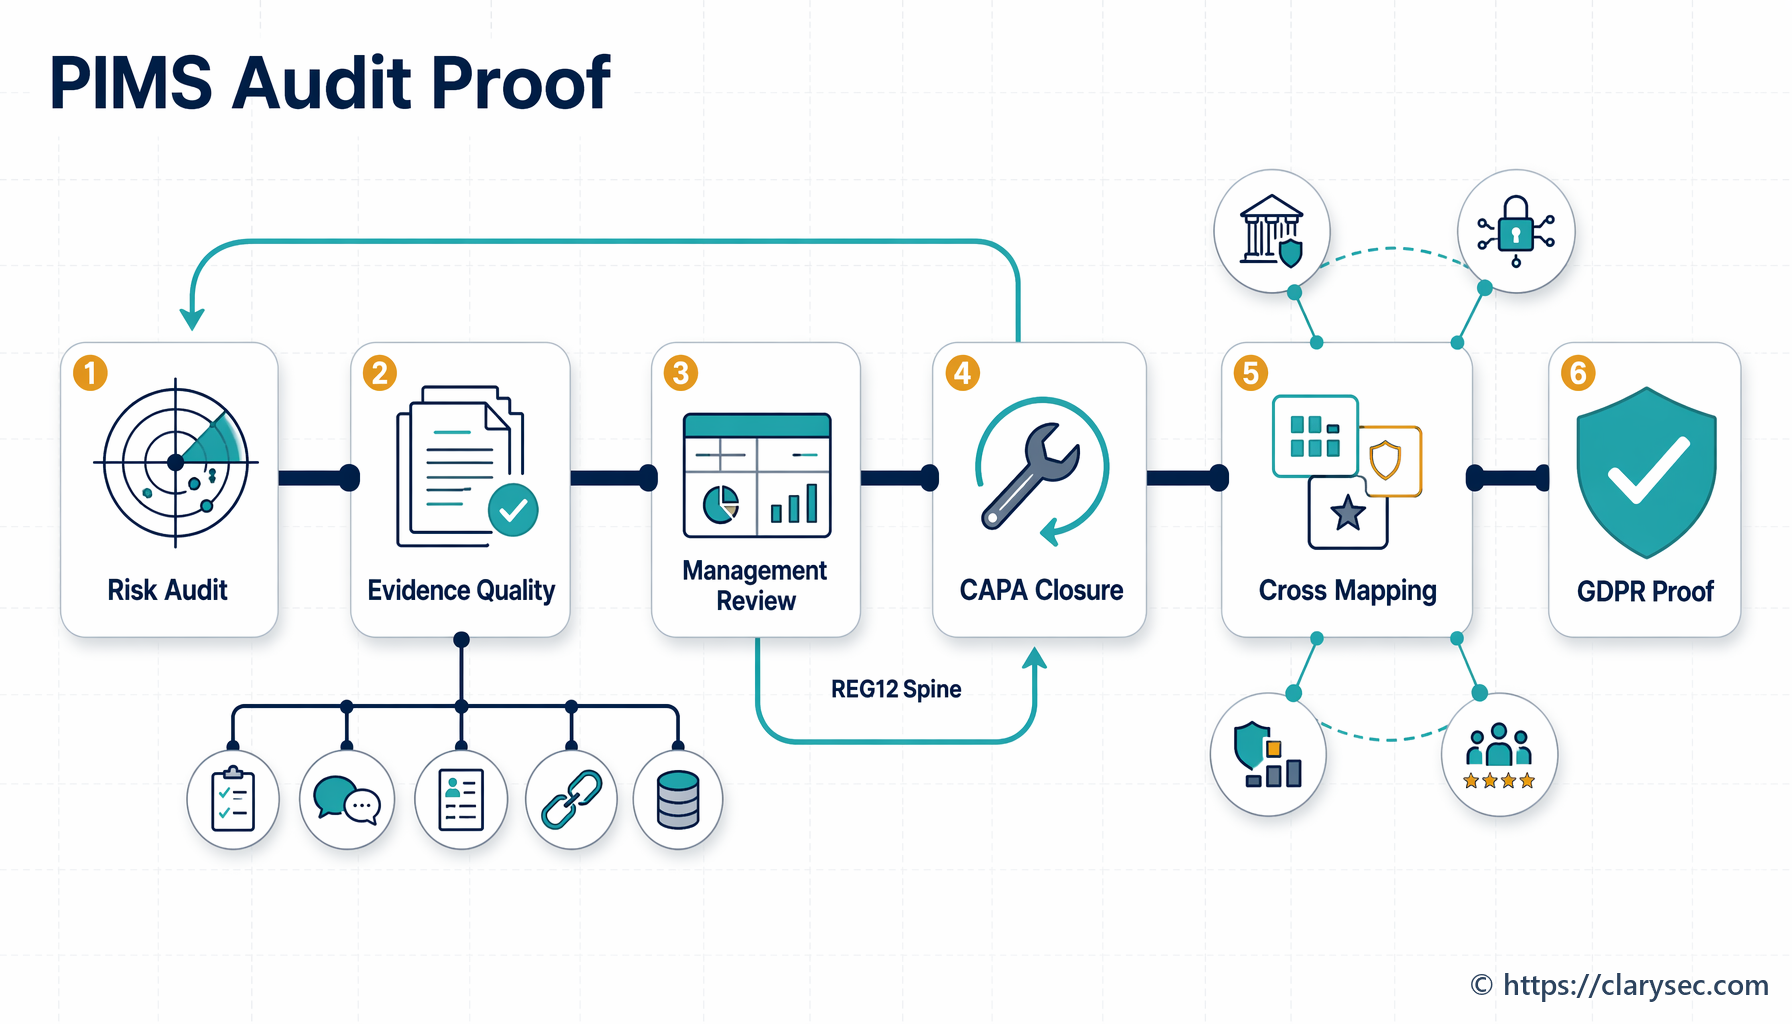
Learn how to build an ISO 27701:2025 PIMS audit and management review cycle that proves GDPR accountability with evidence, CAPA, leadership decisions and cross-compliance mapping.