#Business Continuity
Articles tagged with "Business Continuity"
27 articles
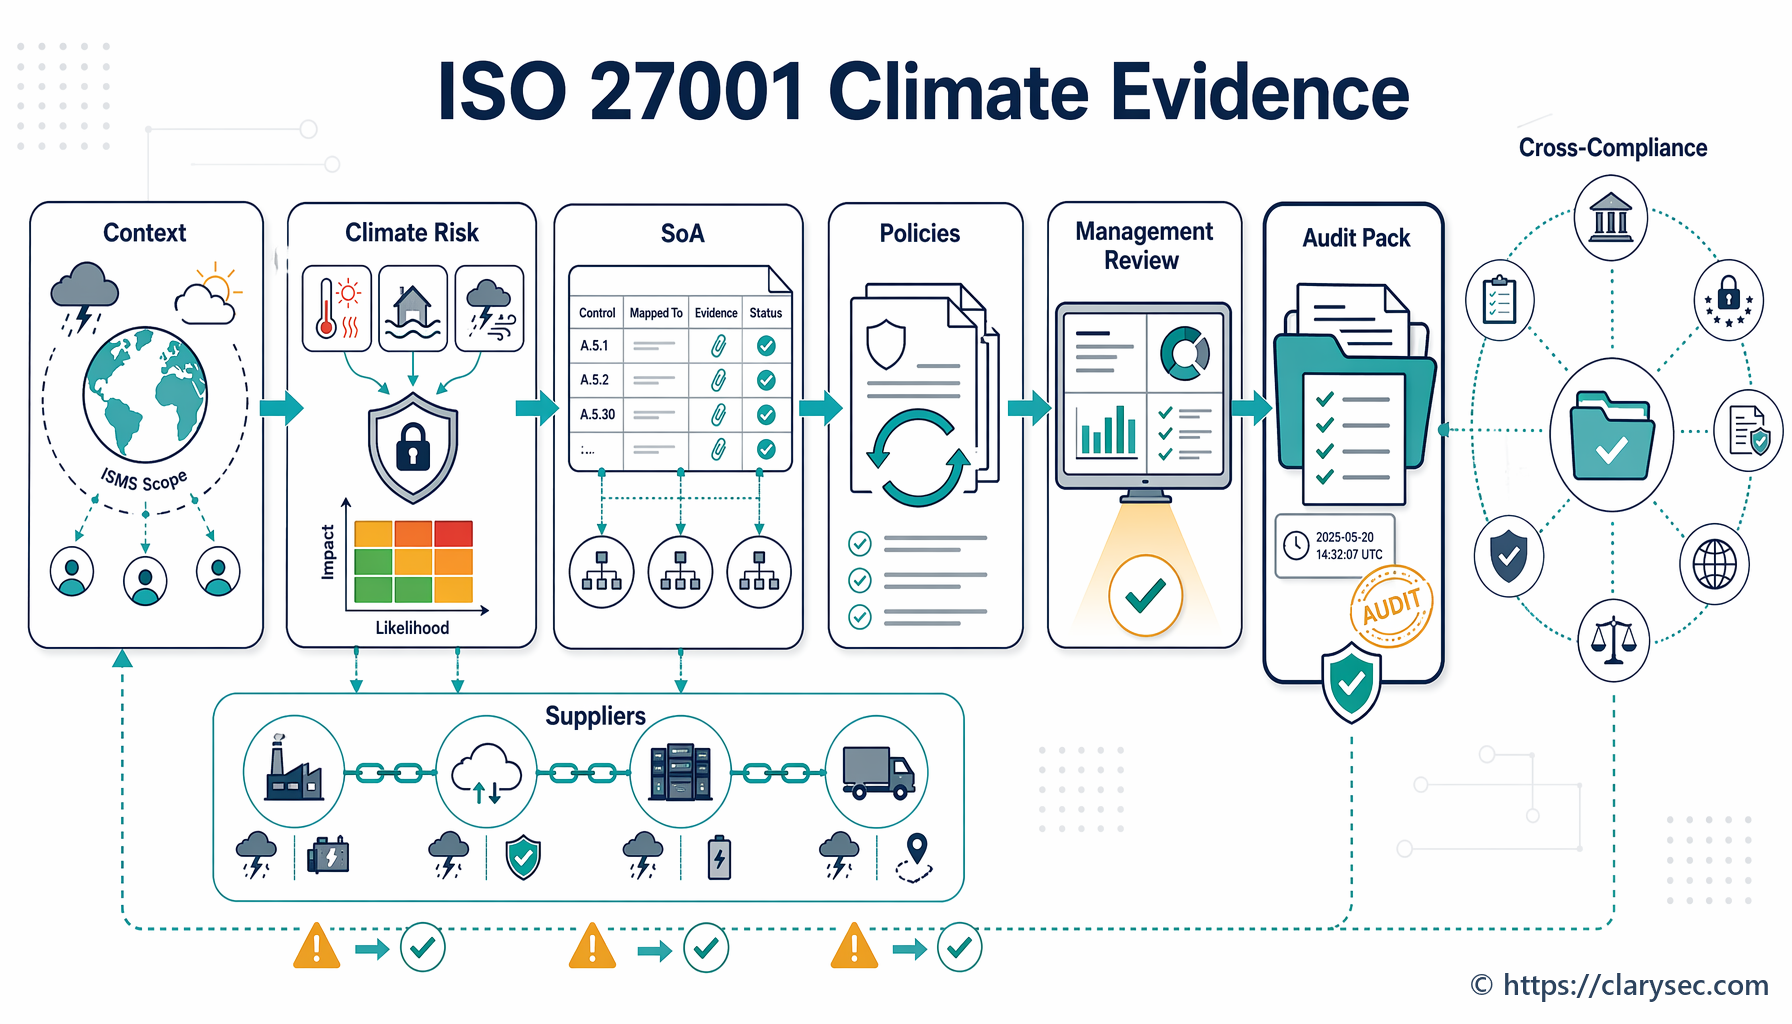
A practical guide for proving ISO 27001 climate change amendment readiness through ISMS context, interested parties, risk assessment, SoA rationale, business continuity, supplier assurance, and management review evidence.
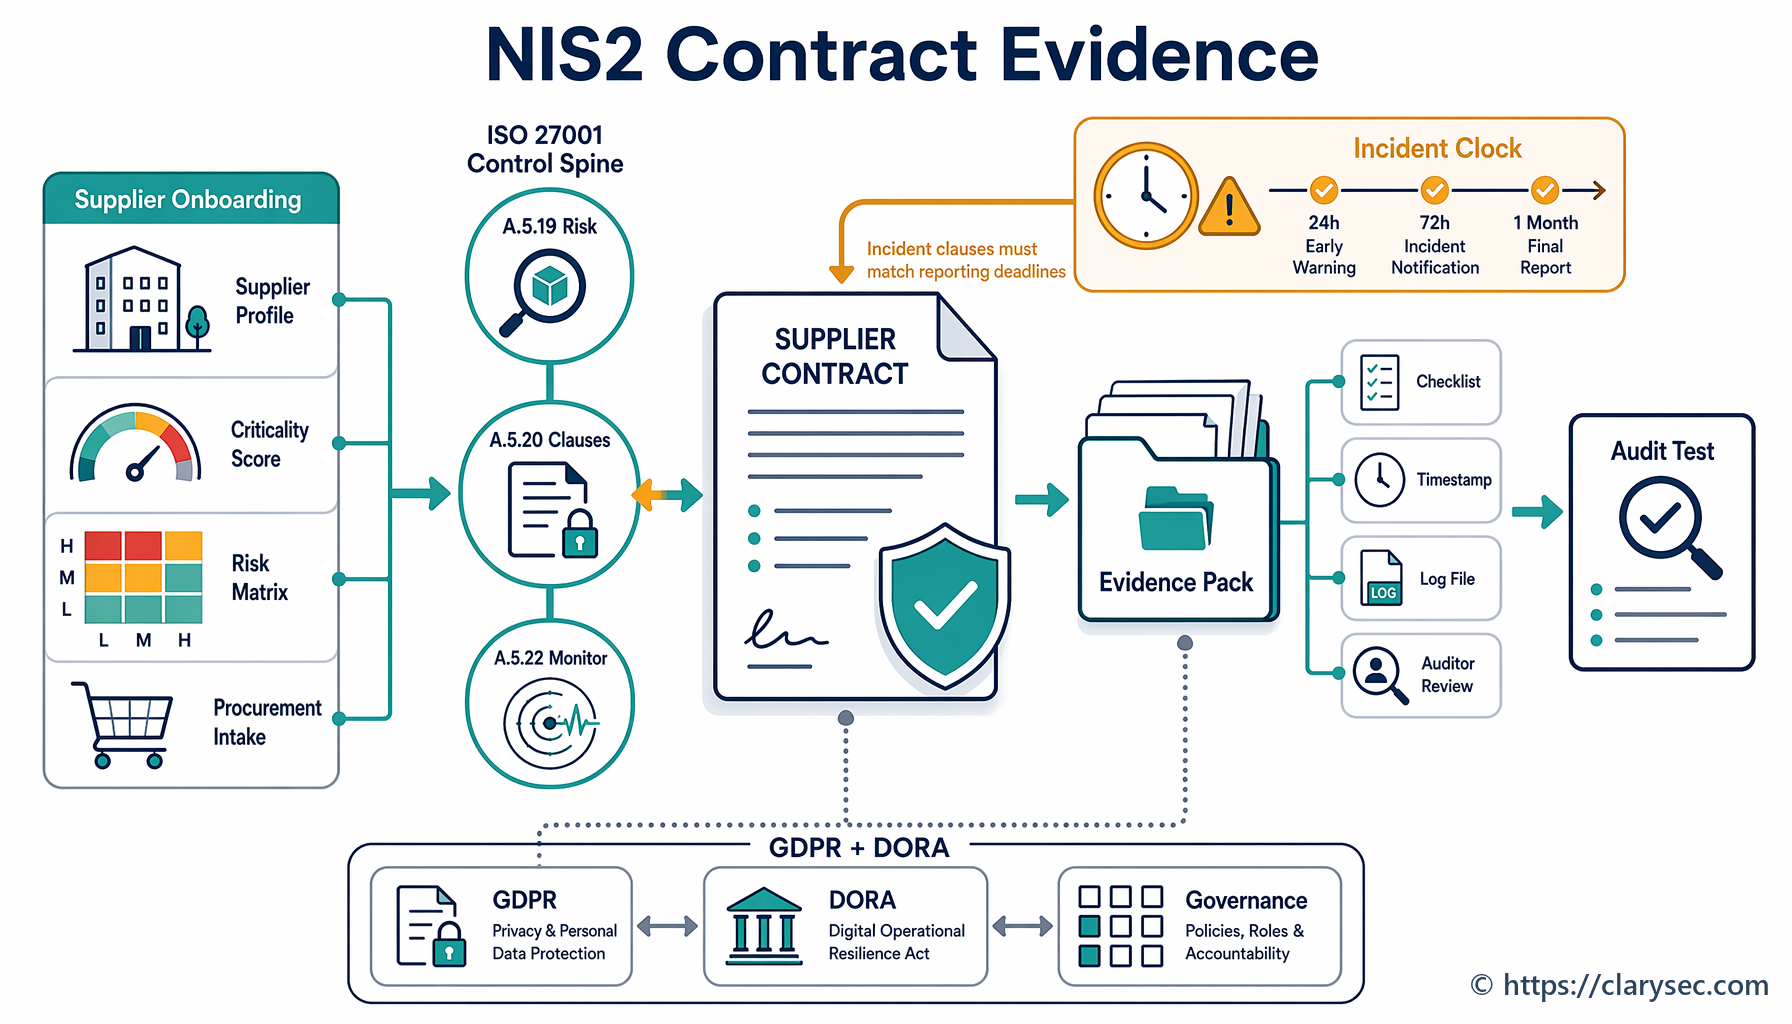
A practical Clarysec guide for turning NIS2 supplier contract clauses into audit-ready ISO/IEC 27001:2022 assurance evidence, GDPR accountability, DORA alignment, and board-level supplier governance.
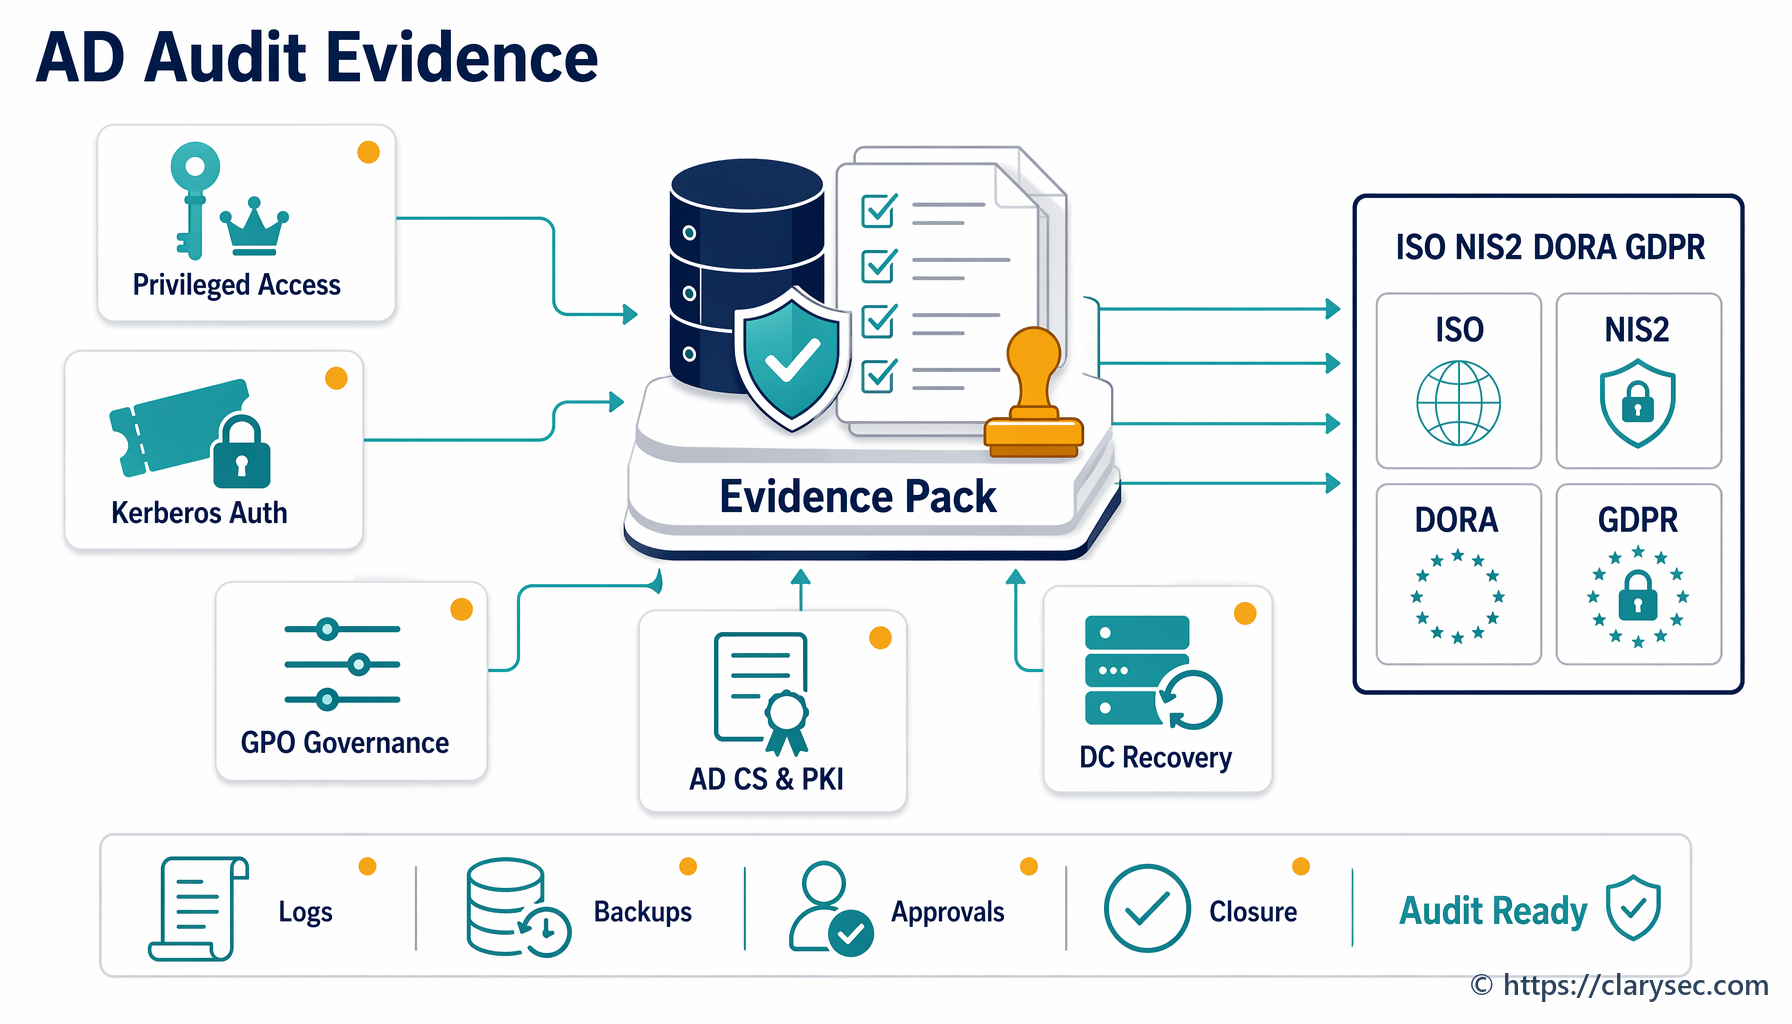
A scenario-driven CISO guide to turning Active Directory hardening into audit-ready evidence for ISO/IEC 27001:2022, NIS2, DORA, GDPR, NIST CSF 2.0 and governance reviews.
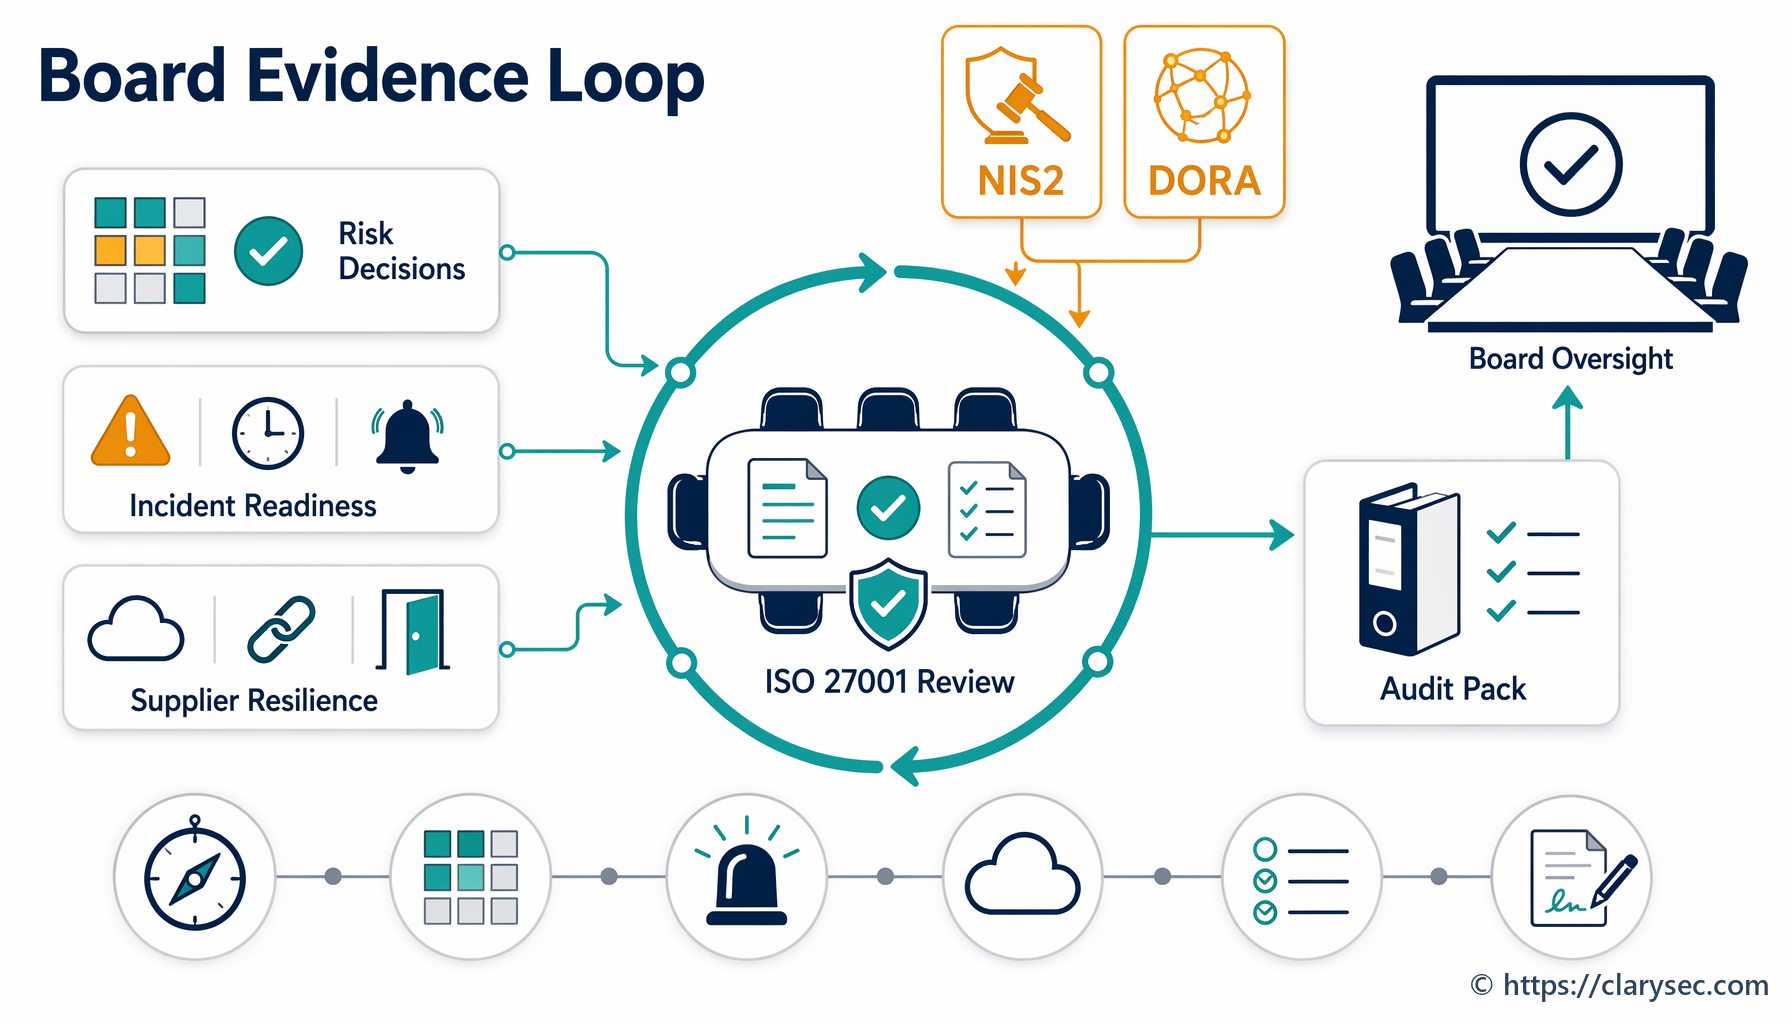
ISO/IEC 27001:2022 Clause 9.3 management review is becoming the practical board evidence mechanism for proving cybersecurity oversight under NIS2 and DORA. This guide shows how CISOs, compliance managers, auditors, and owners can turn review minutes, KPIs, incidents, risks, and corrective actions into defensible governance evidence.
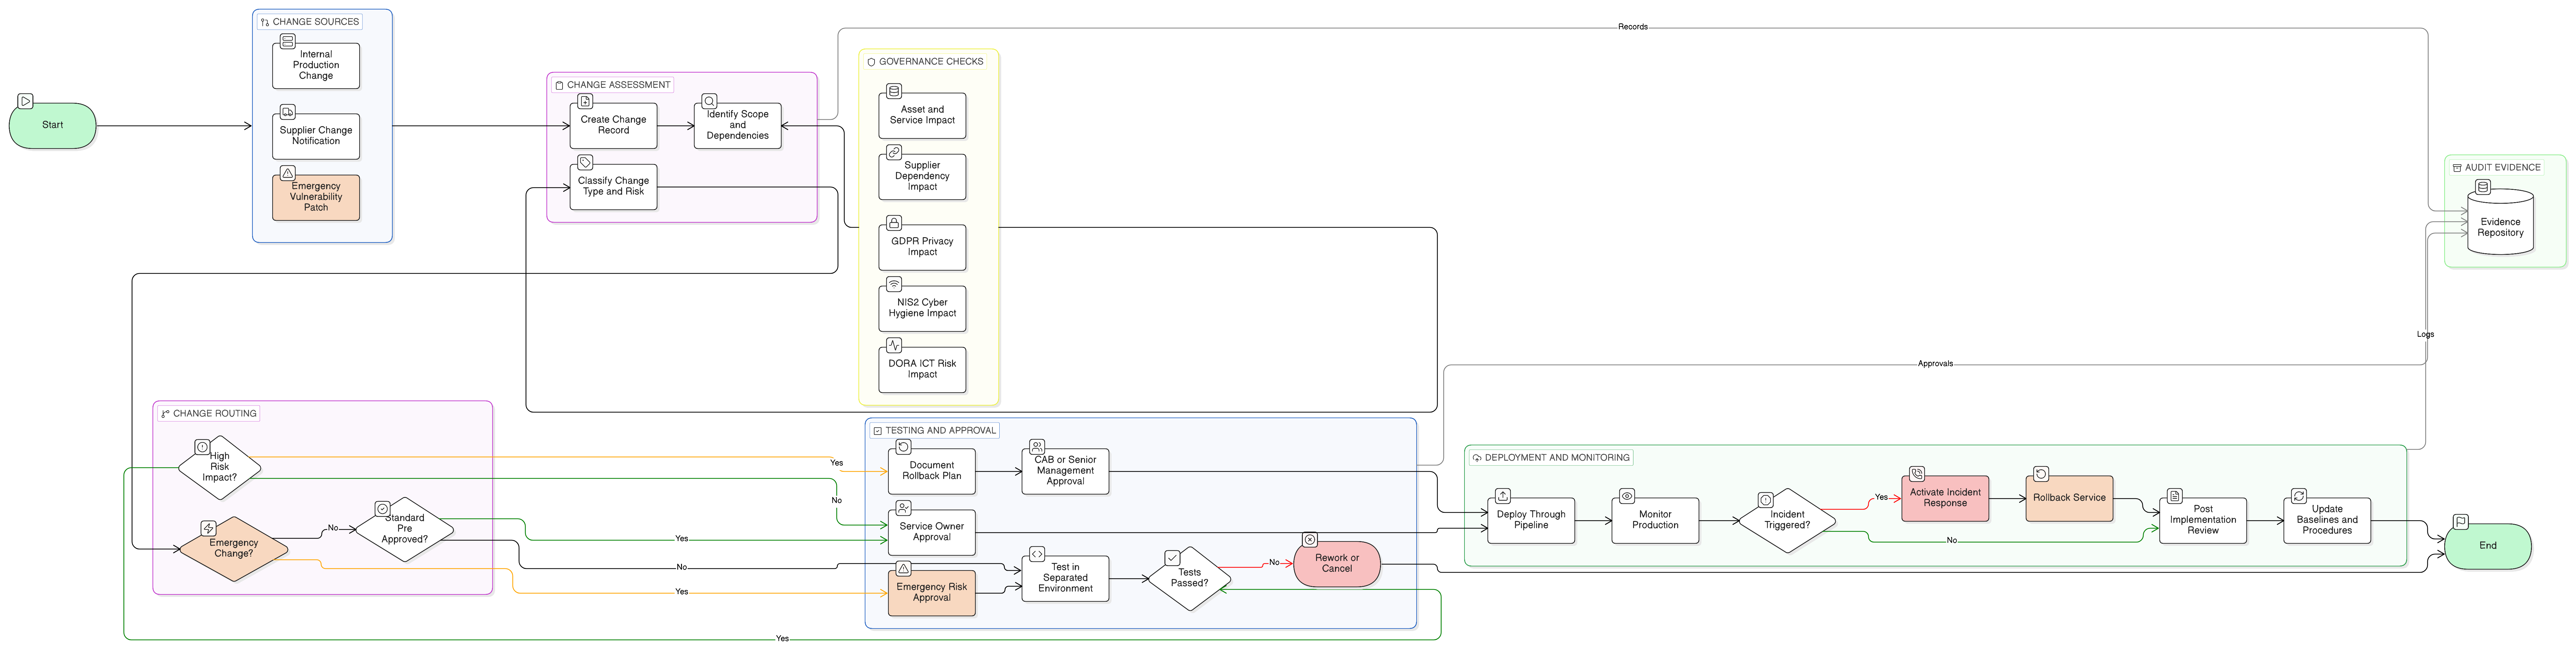
A practical, scenario-driven guide to secure change management using ISO/IEC 27001:2022, Clarysec policies, Zenith Blueprint, and Zenith Controls to support NIS2, DORA, GDPR, NIST CSF 2.0, and audit evidence in 2026.
A practical flagship guide for CISOs, compliance managers and auditors building a unified ISO 27001:2022 internal audit programme that supports NIS2, DORA, GDPR, NIST CSF and COBIT assurance. Includes scope design, sampling, findings, corrective action, cross-compliance mapping and a 2026 evidence calendar.
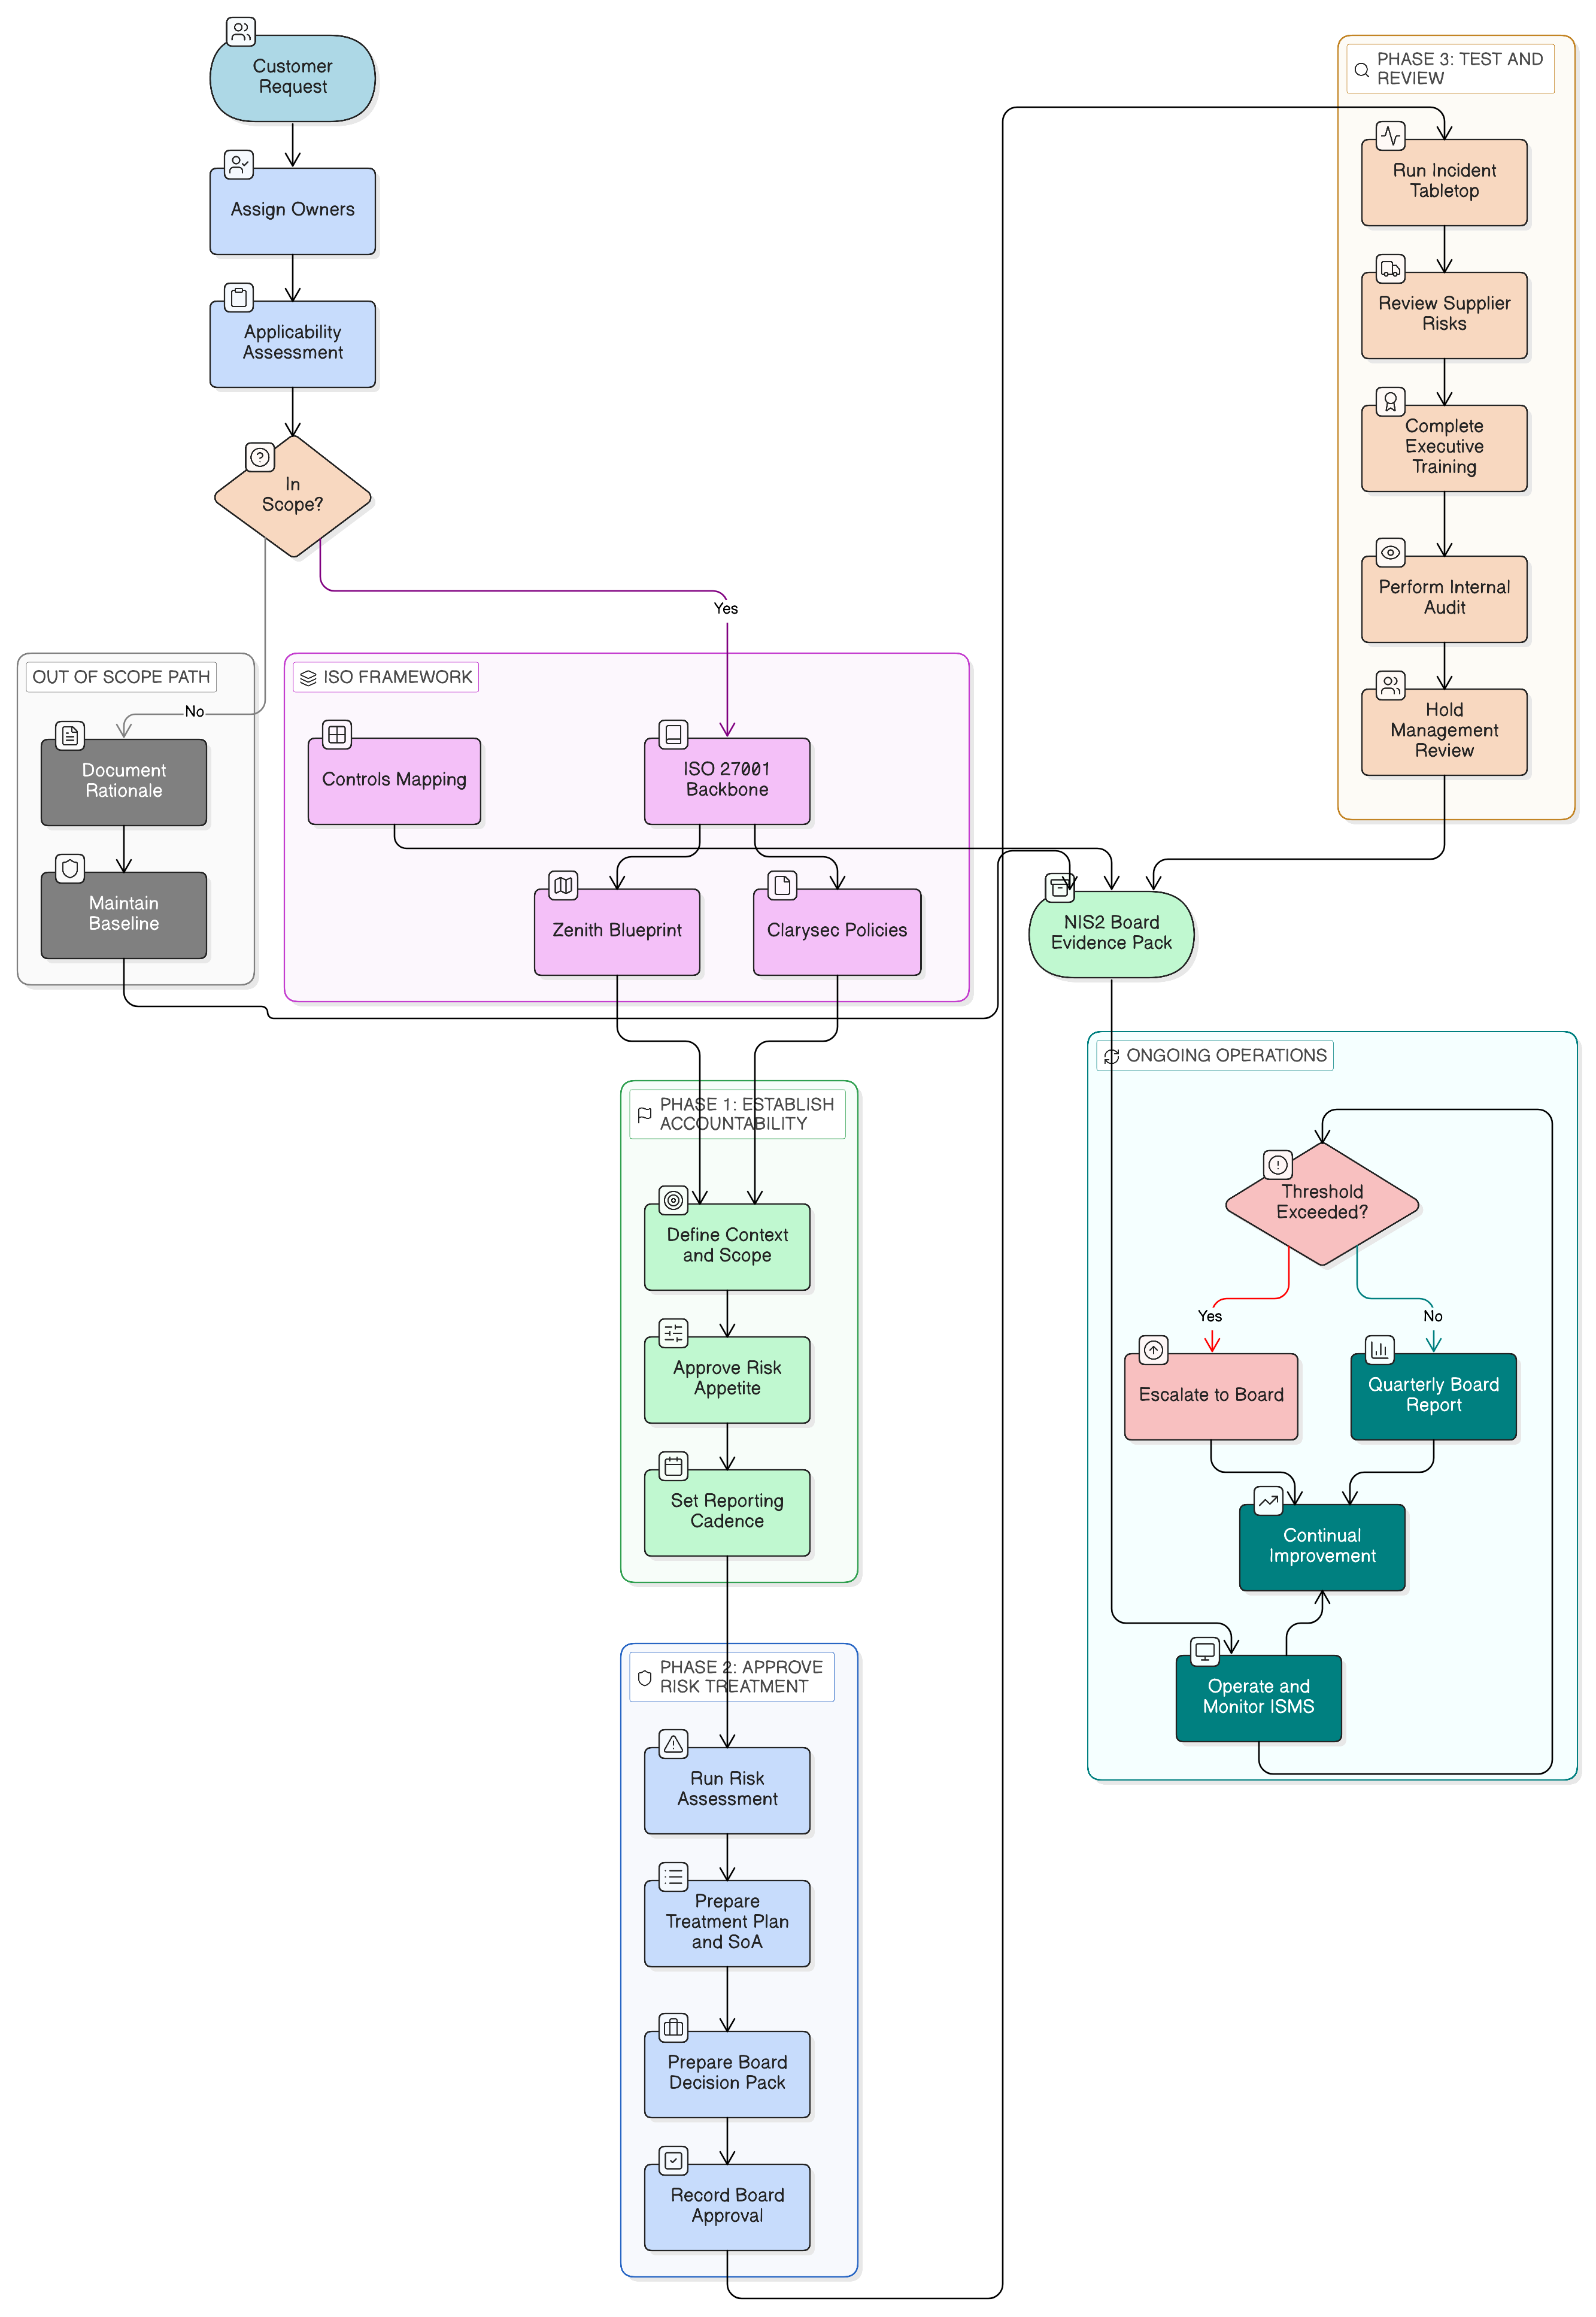
NIS2 makes cybersecurity a management-body accountability issue. This guide shows how boards, CISOs, and compliance leaders can use ISO/IEC 27001:2022, Clarysec policies, Zenith Blueprint, and Zenith Controls to prove oversight, due care, and cross-framework cyber governance.
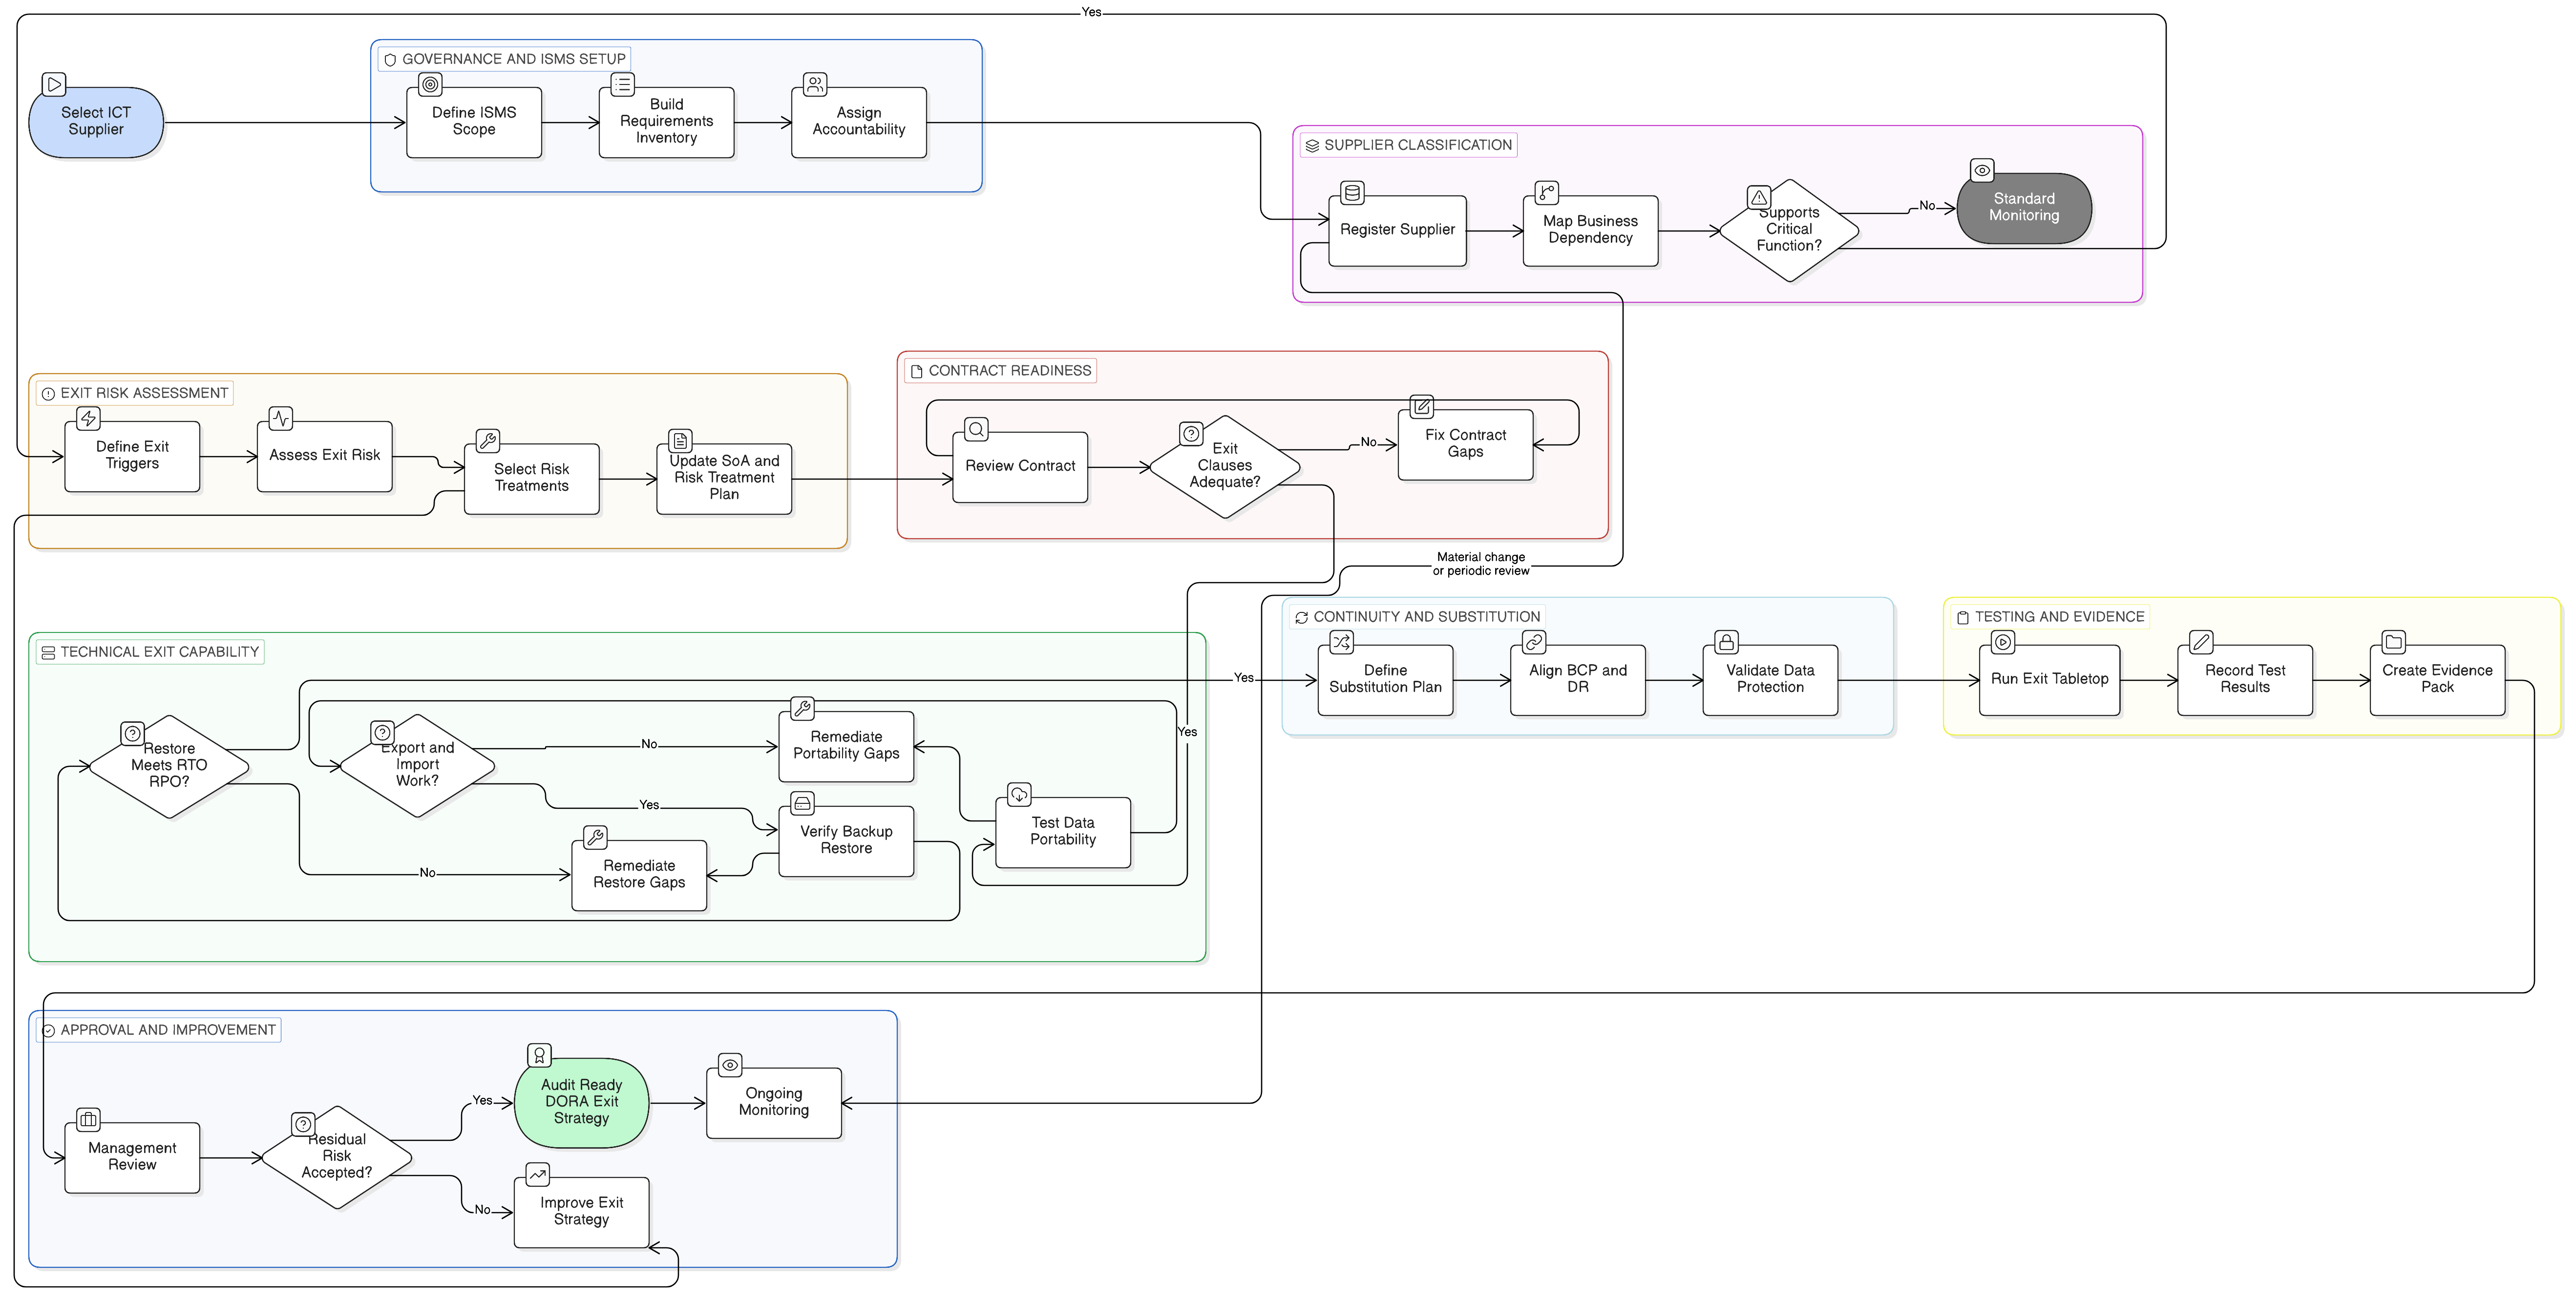
A practical guide for building DORA ICT third-party exit strategies that are contract-backed, technically feasible, tested, and audit-ready.
A practical guide for building audit-ready GDPR Article 32 technical and organisational measures using ISO 27001:2022, ISO 27005, NIS2, DORA and Clarysec toolkits.