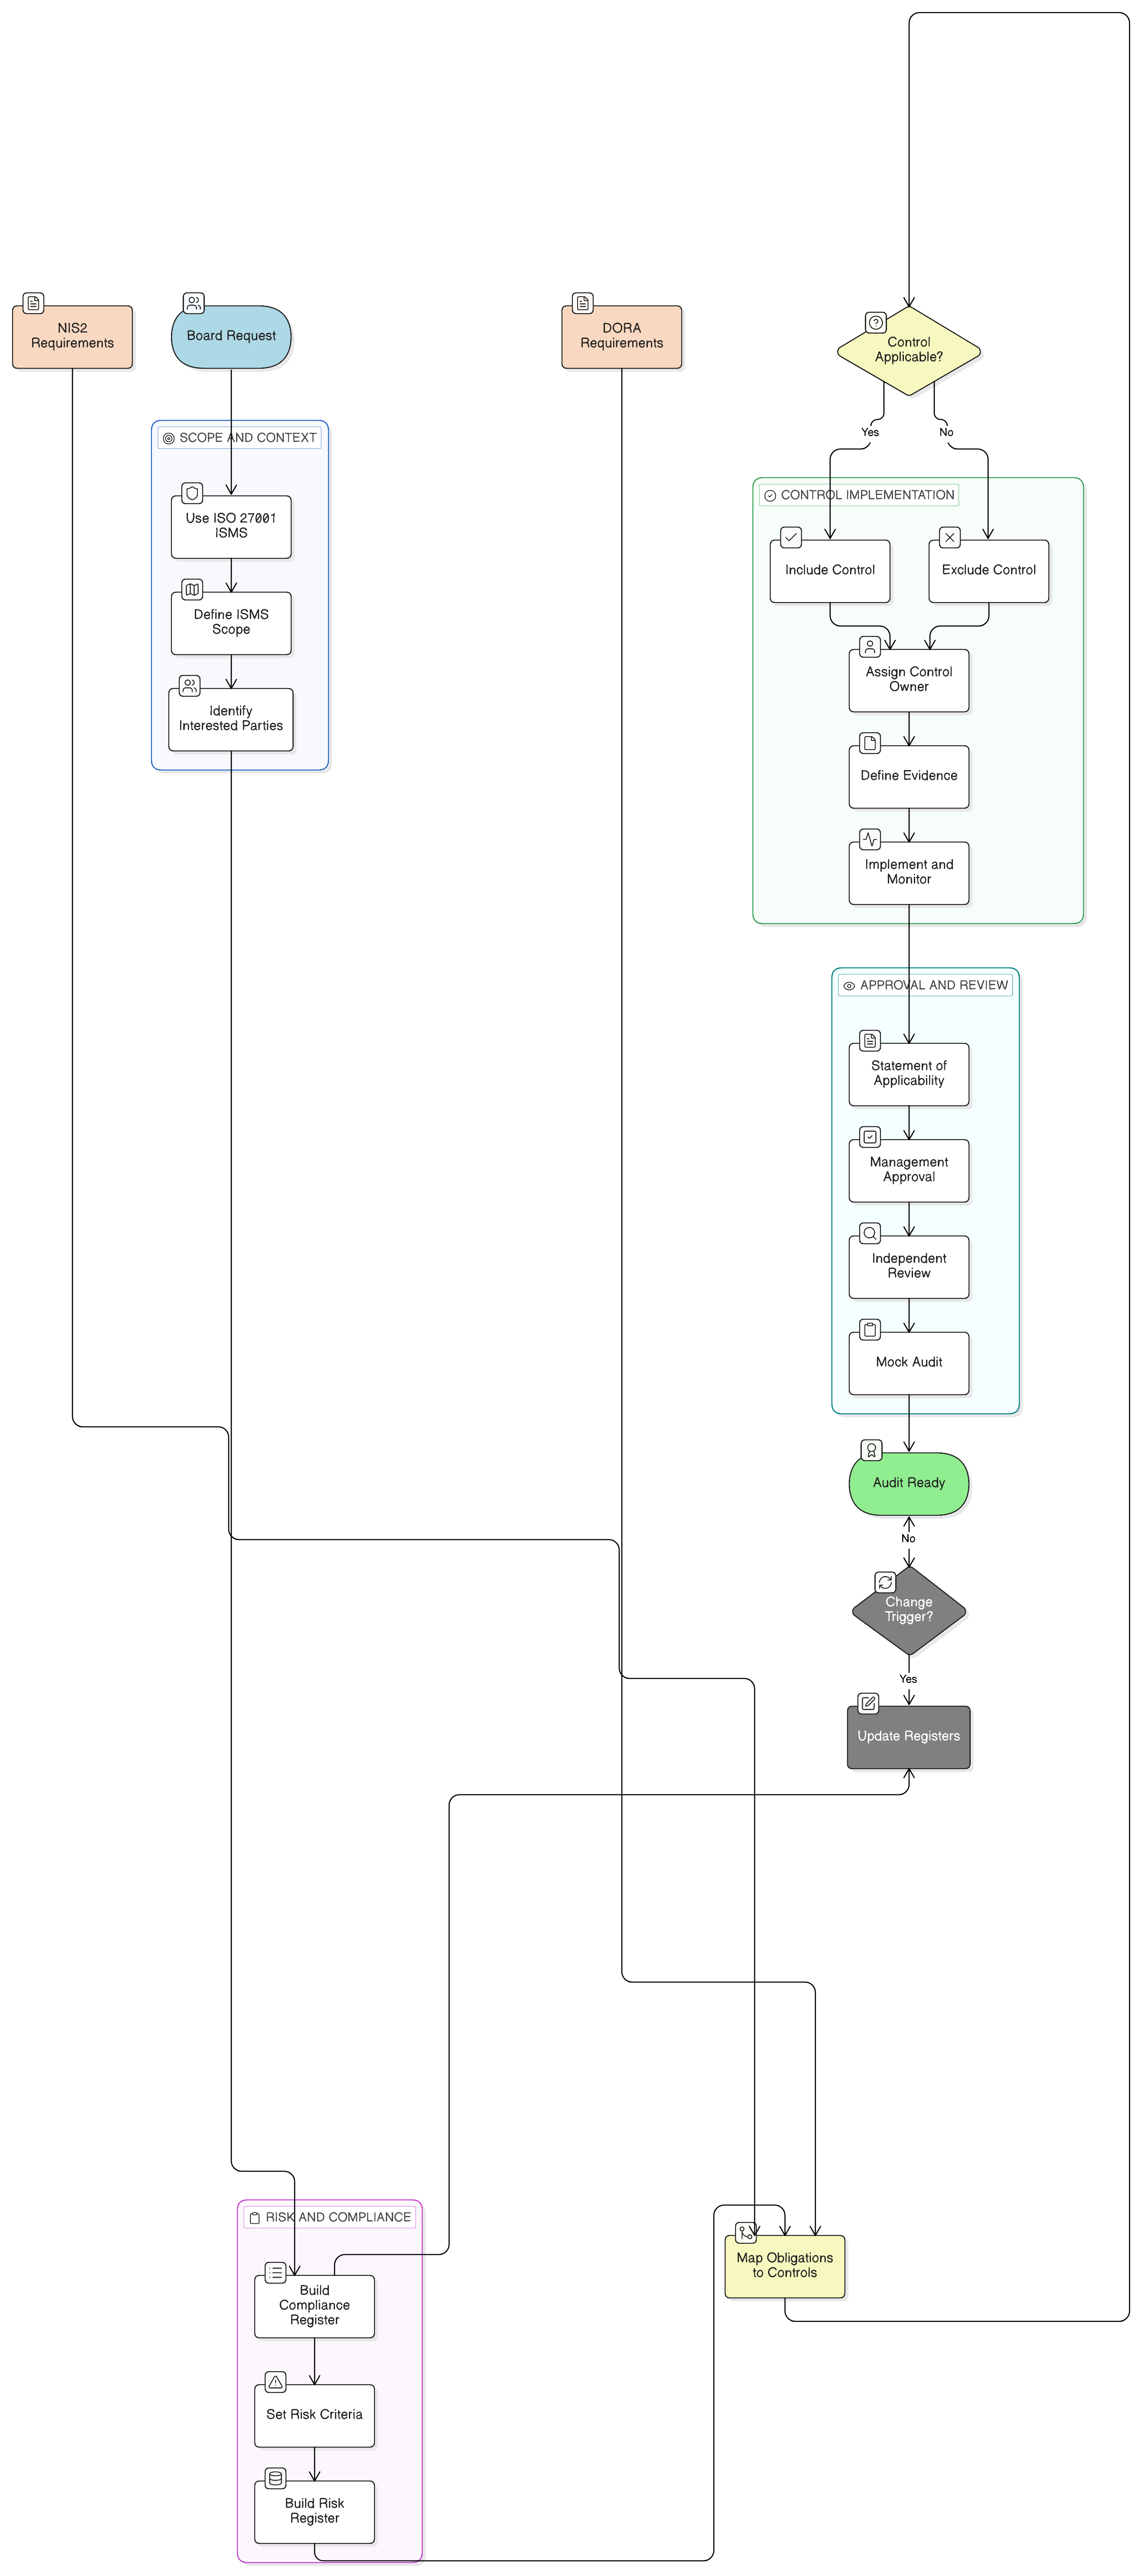
ISO 27001 SoA for NIS2 and DORA Readiness
Learn how to use the ISO 27001 Statement of Applicability as an audit-ready bridge between NIS2, DORA, GDPR, risk treatment, suppliers, incident response, and evidence.
Articles tagged with "Business Continuity"
Learn how to use the ISO 27001 Statement of Applicability as an audit-ready bridge between NIS2, DORA, GDPR, risk treatment, suppliers, incident response, and evidence.
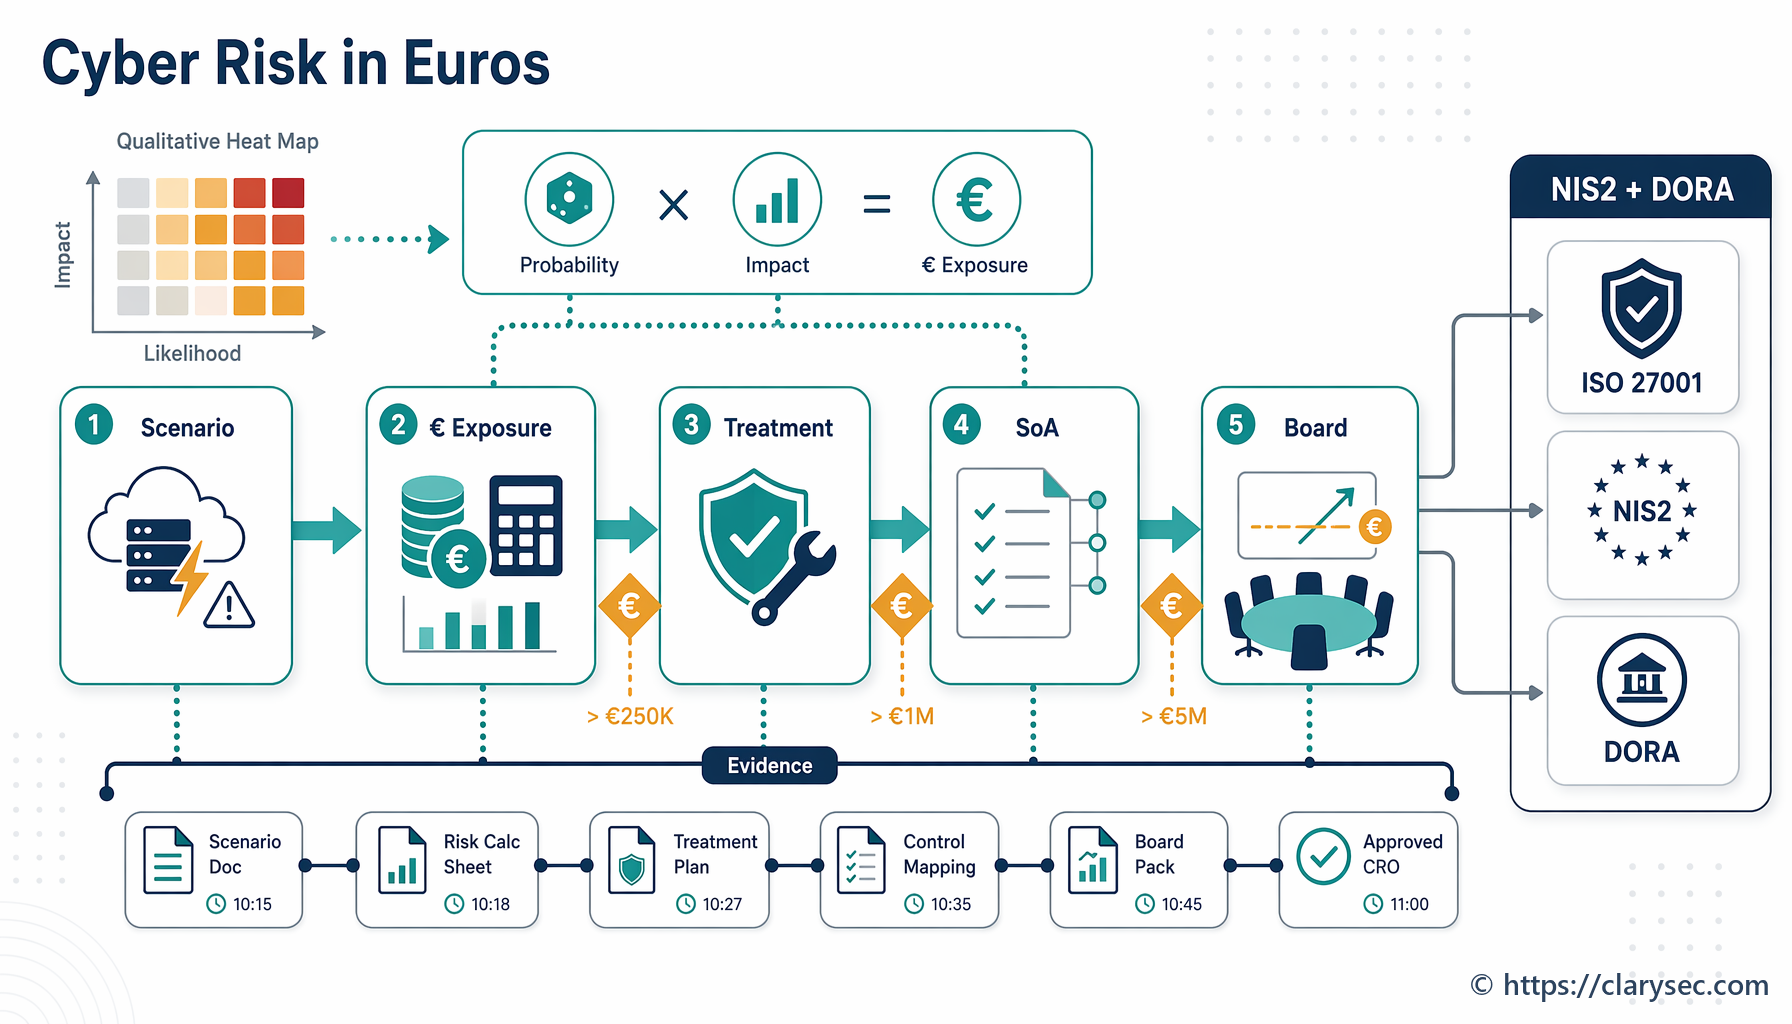
A practical guide for CISOs, compliance managers and boards on translating qualitative cyber risks into financial exposure, ISO 27001 evidence, NIS2 oversight and DORA ICT resilience decisions.
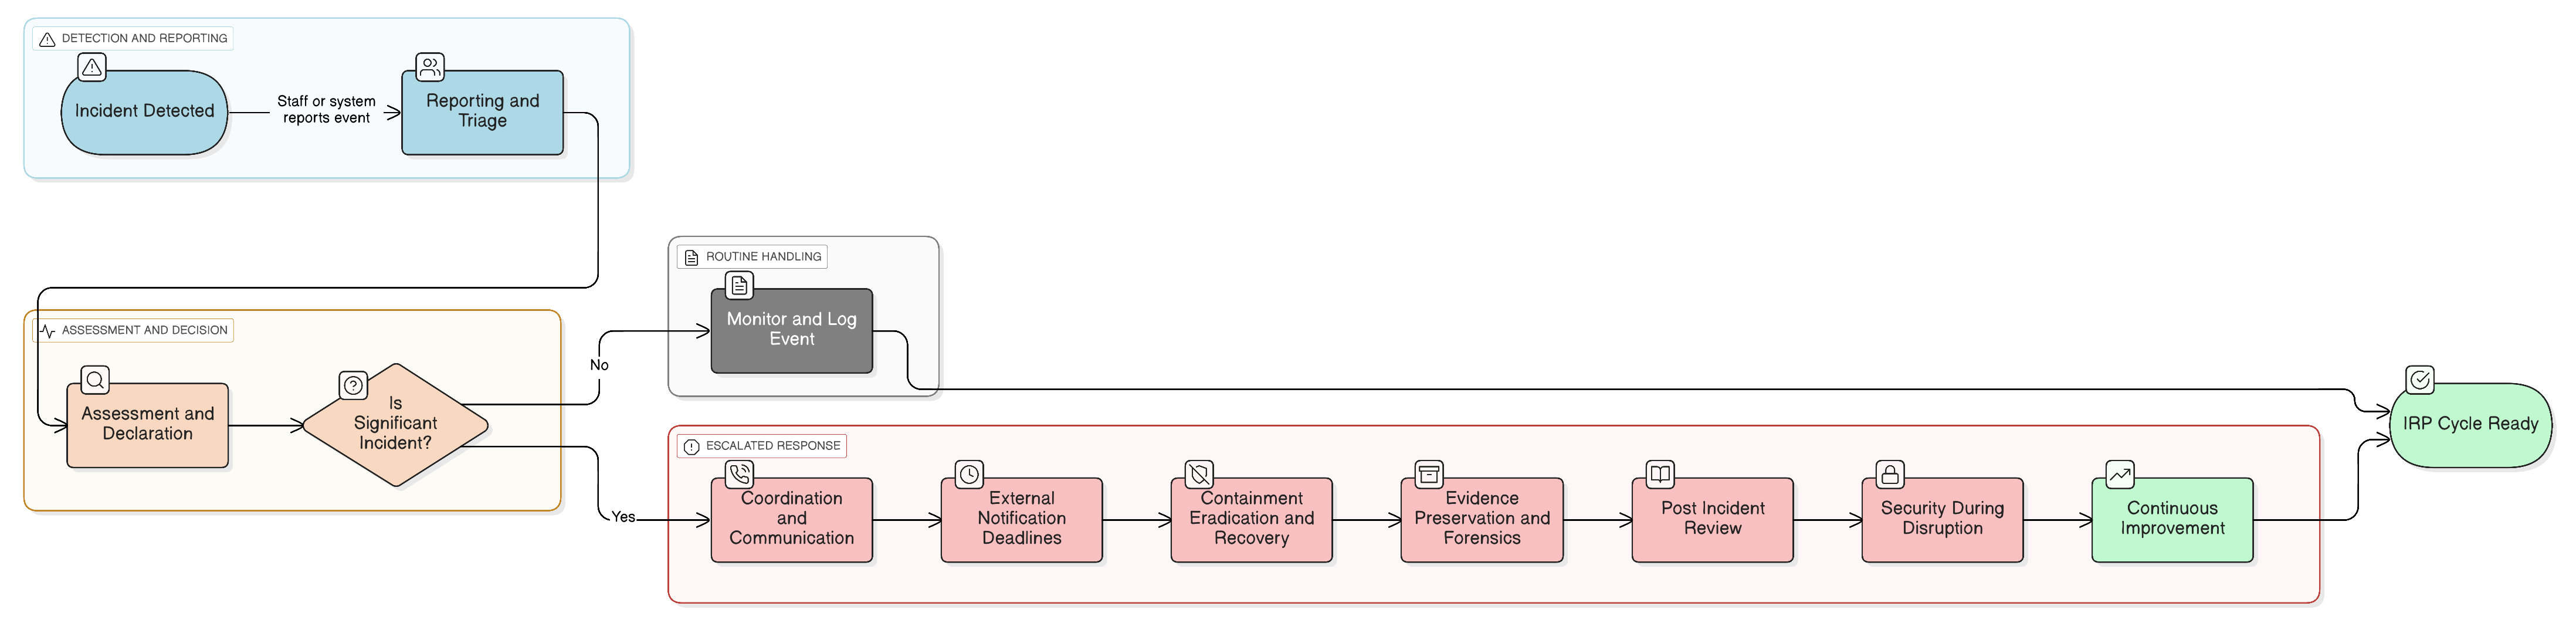
The NIS2 Directive’s 24-hour notification rule is a game-changer. This definitive guide shows CISOs and auditors how to engineer a resilient, compliant incident response plan that stands up to regulatory scrutiny and real-world attacks, using Clarysec’s policies and cross-compliance toolkits.
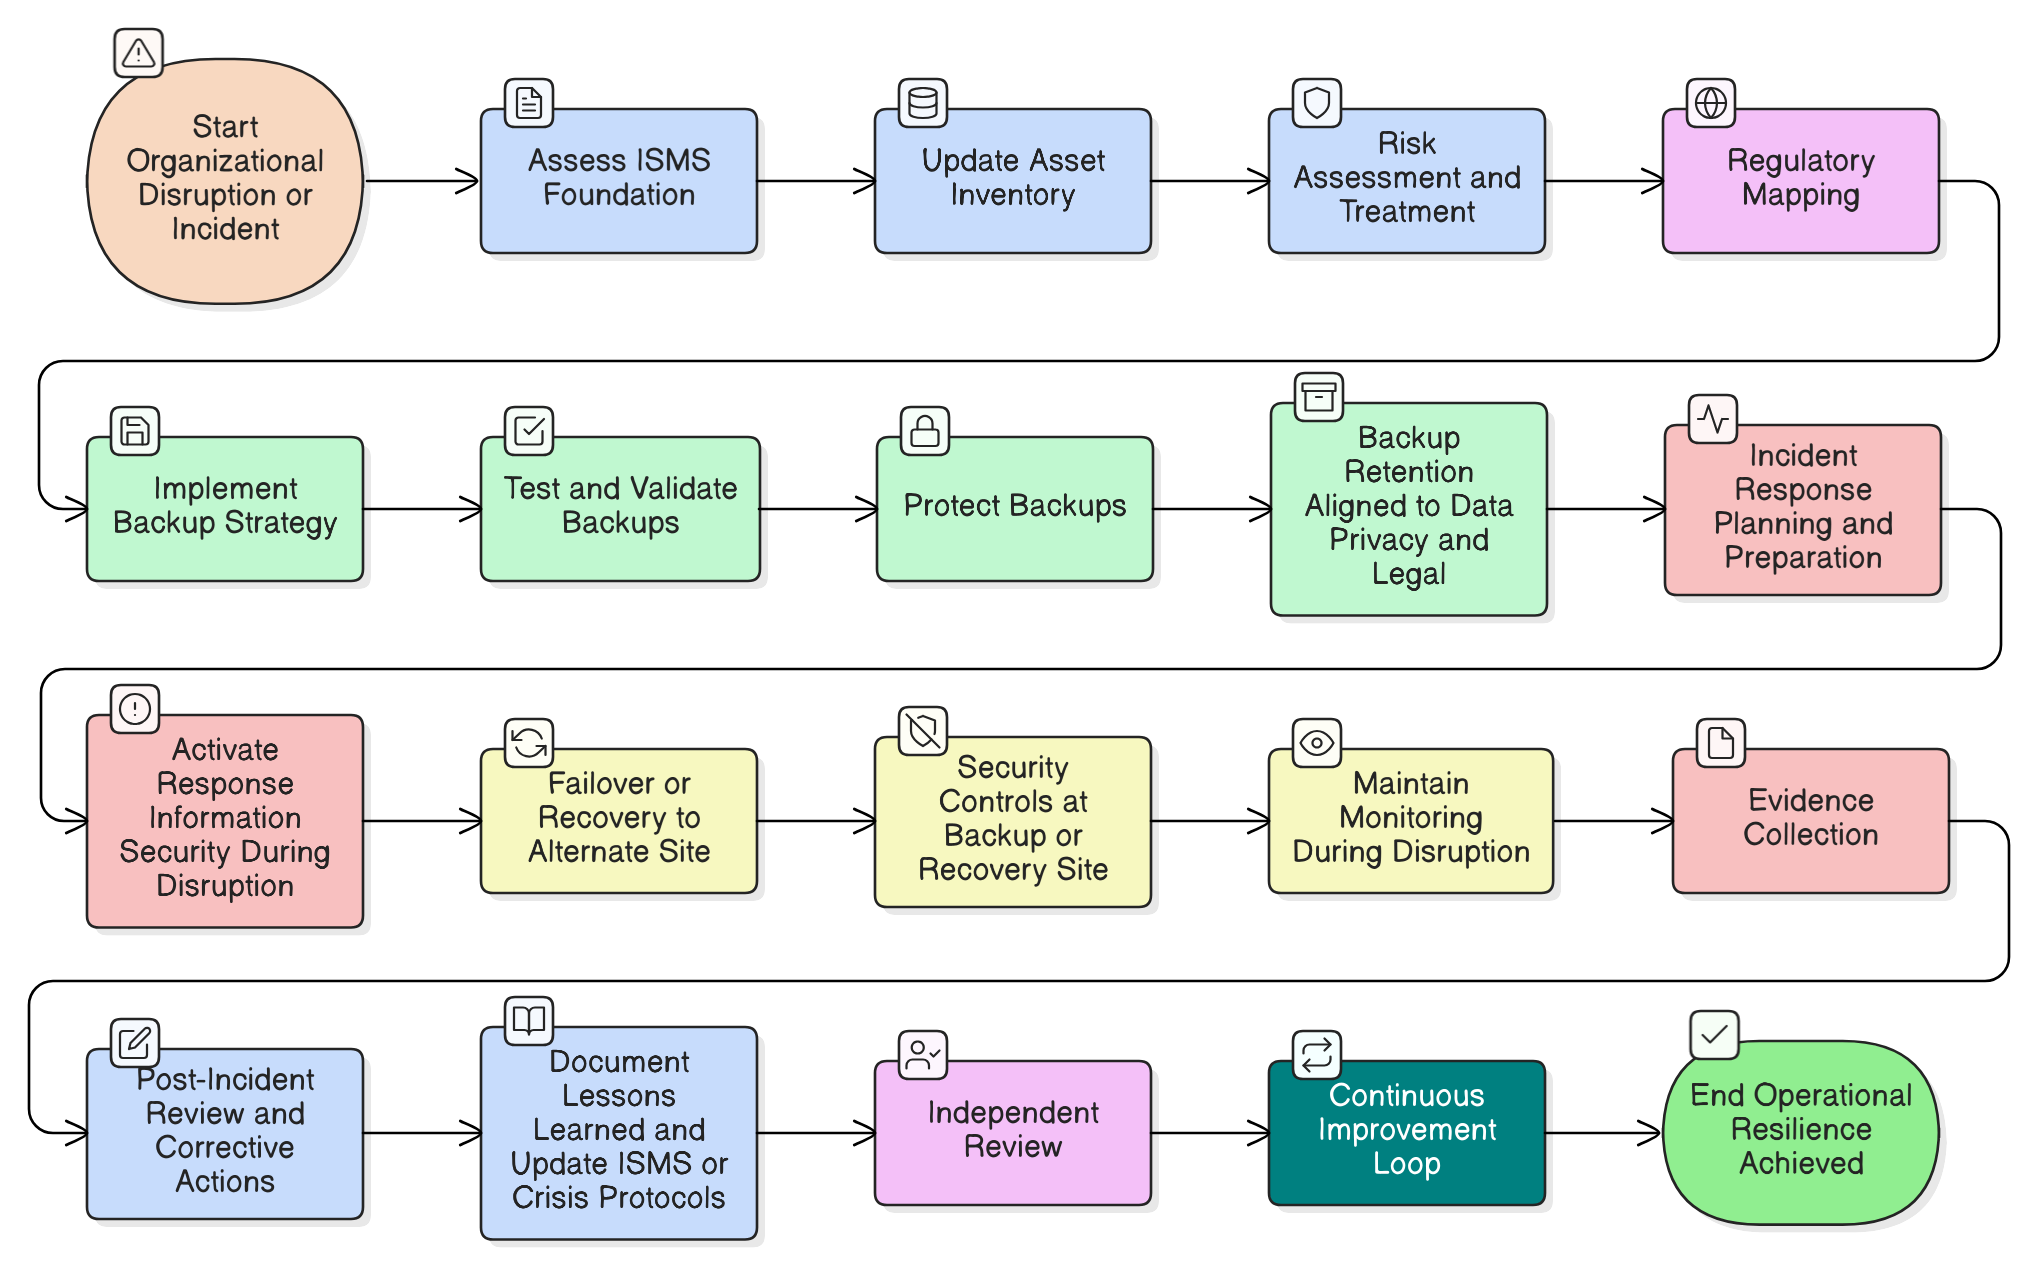
A ransomware attack hits during a board meeting. Your backups are working, but is your security? Discover how to implement ISO/IEC 27001:2022’s resilience controls to maintain security under pressure, satisfy auditors, and meet stringent DORA and NIS2 requirements with Clarysec’s expert roadmap.
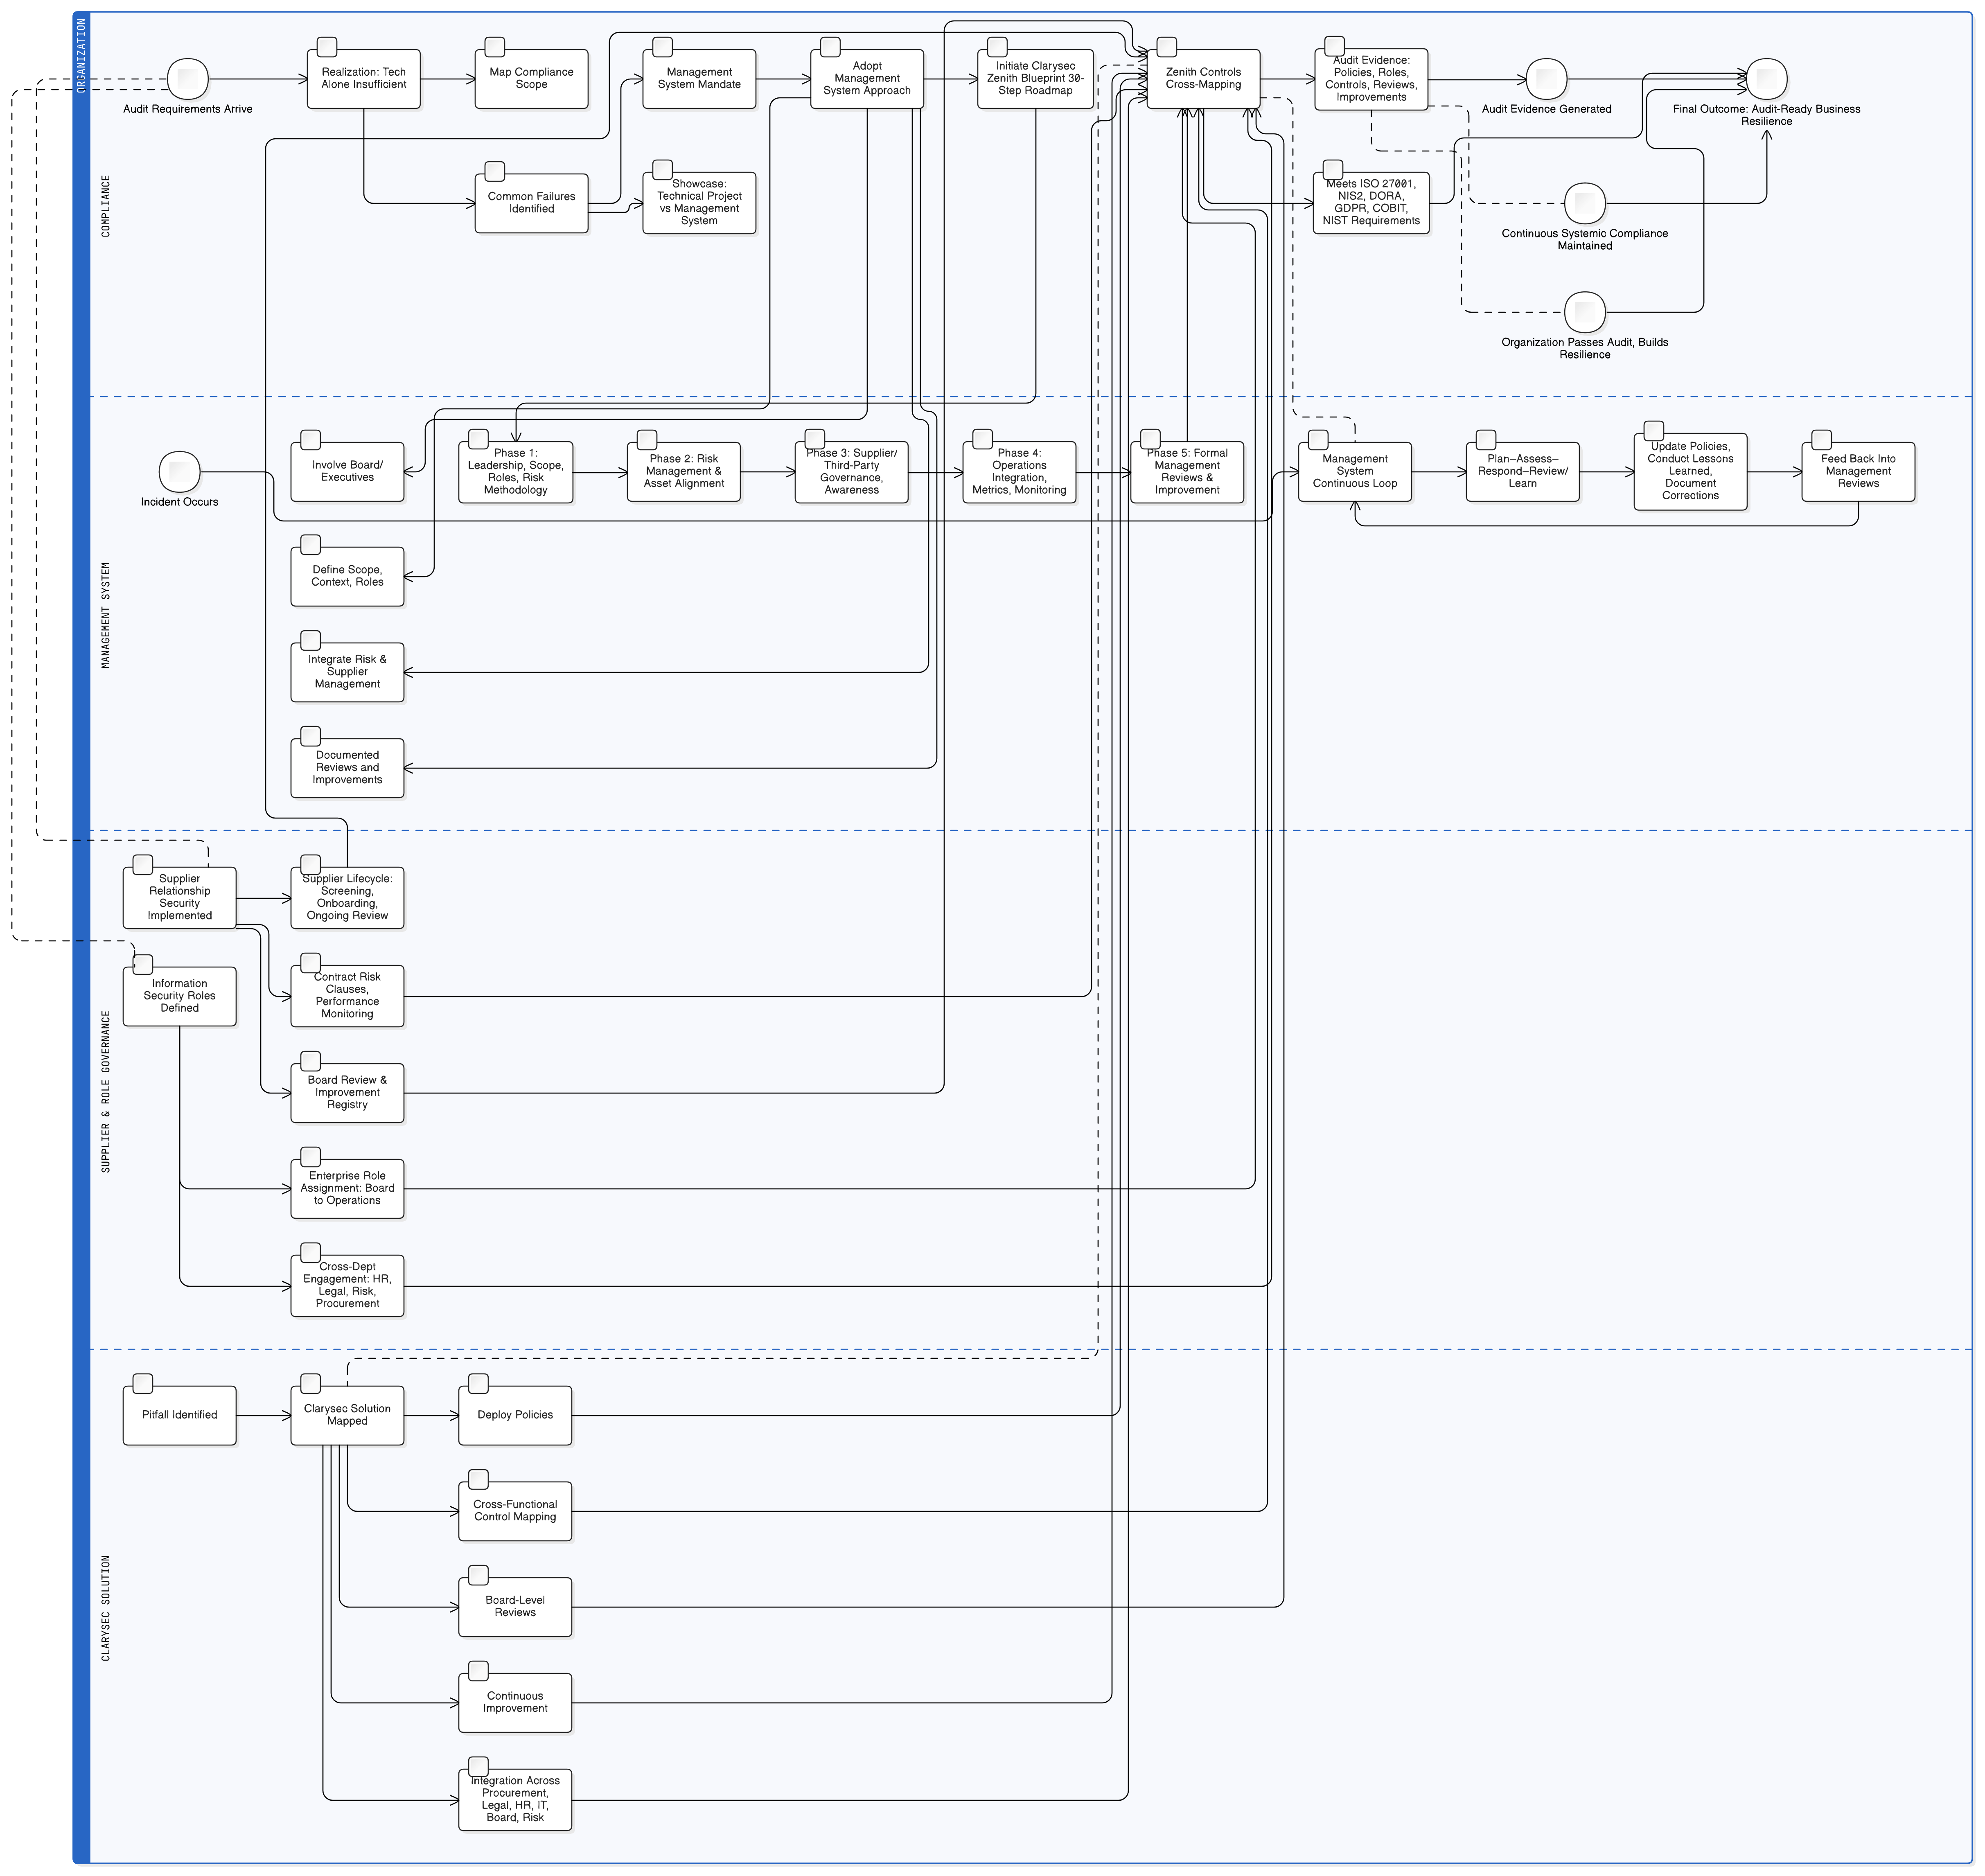
Audit disasters aren’t caused by weak firewalls, they’re the result of treating compliance as a tech checklist. Discover Clarysec’s management system strategies, mapped controls, and practical policies for seamless ISO 27001, NIS2, and DORA compliance.
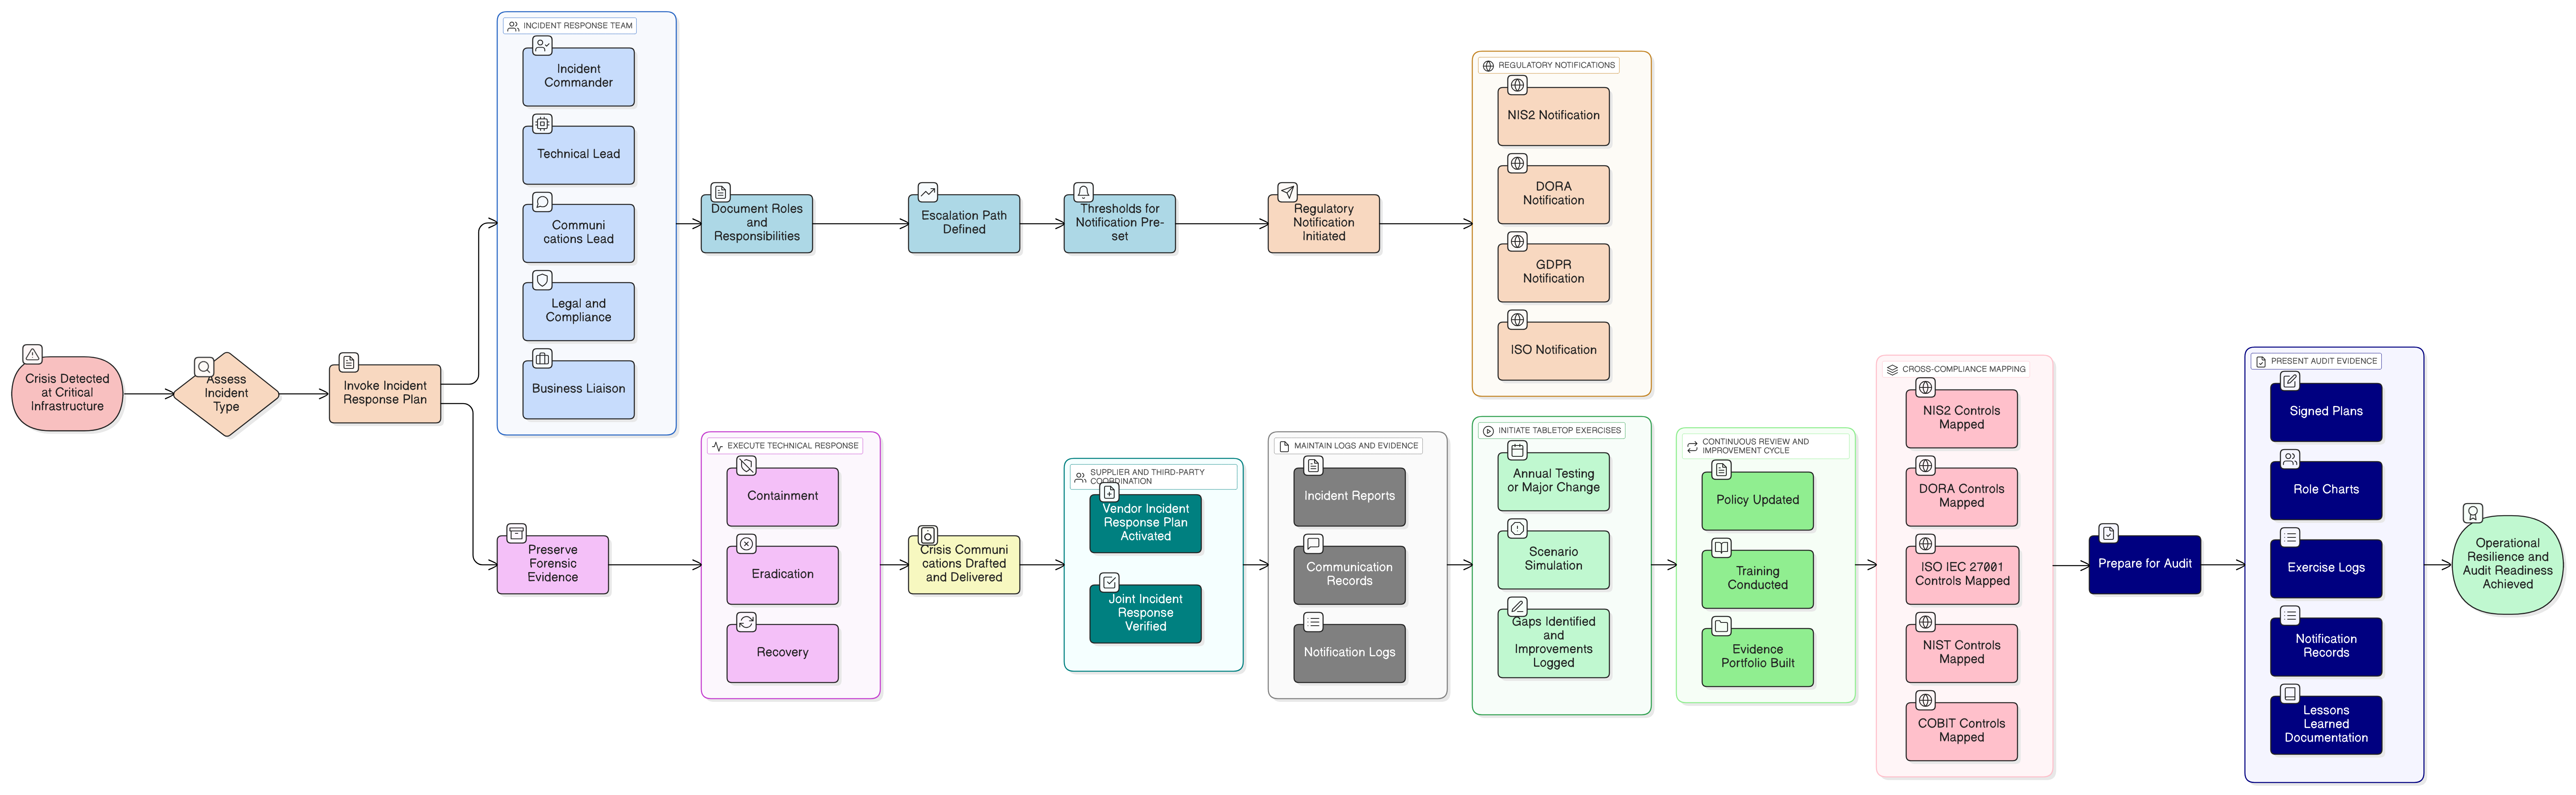
Unify your incident response strategy for NIS2, DORA, and ISO/IEC 27001:2022 compliance with Clarysec’s tested practices, actionable mappings, and robust policies. Includes real-world scenarios, practical checklists, and evidence-generation steps for audit readiness.
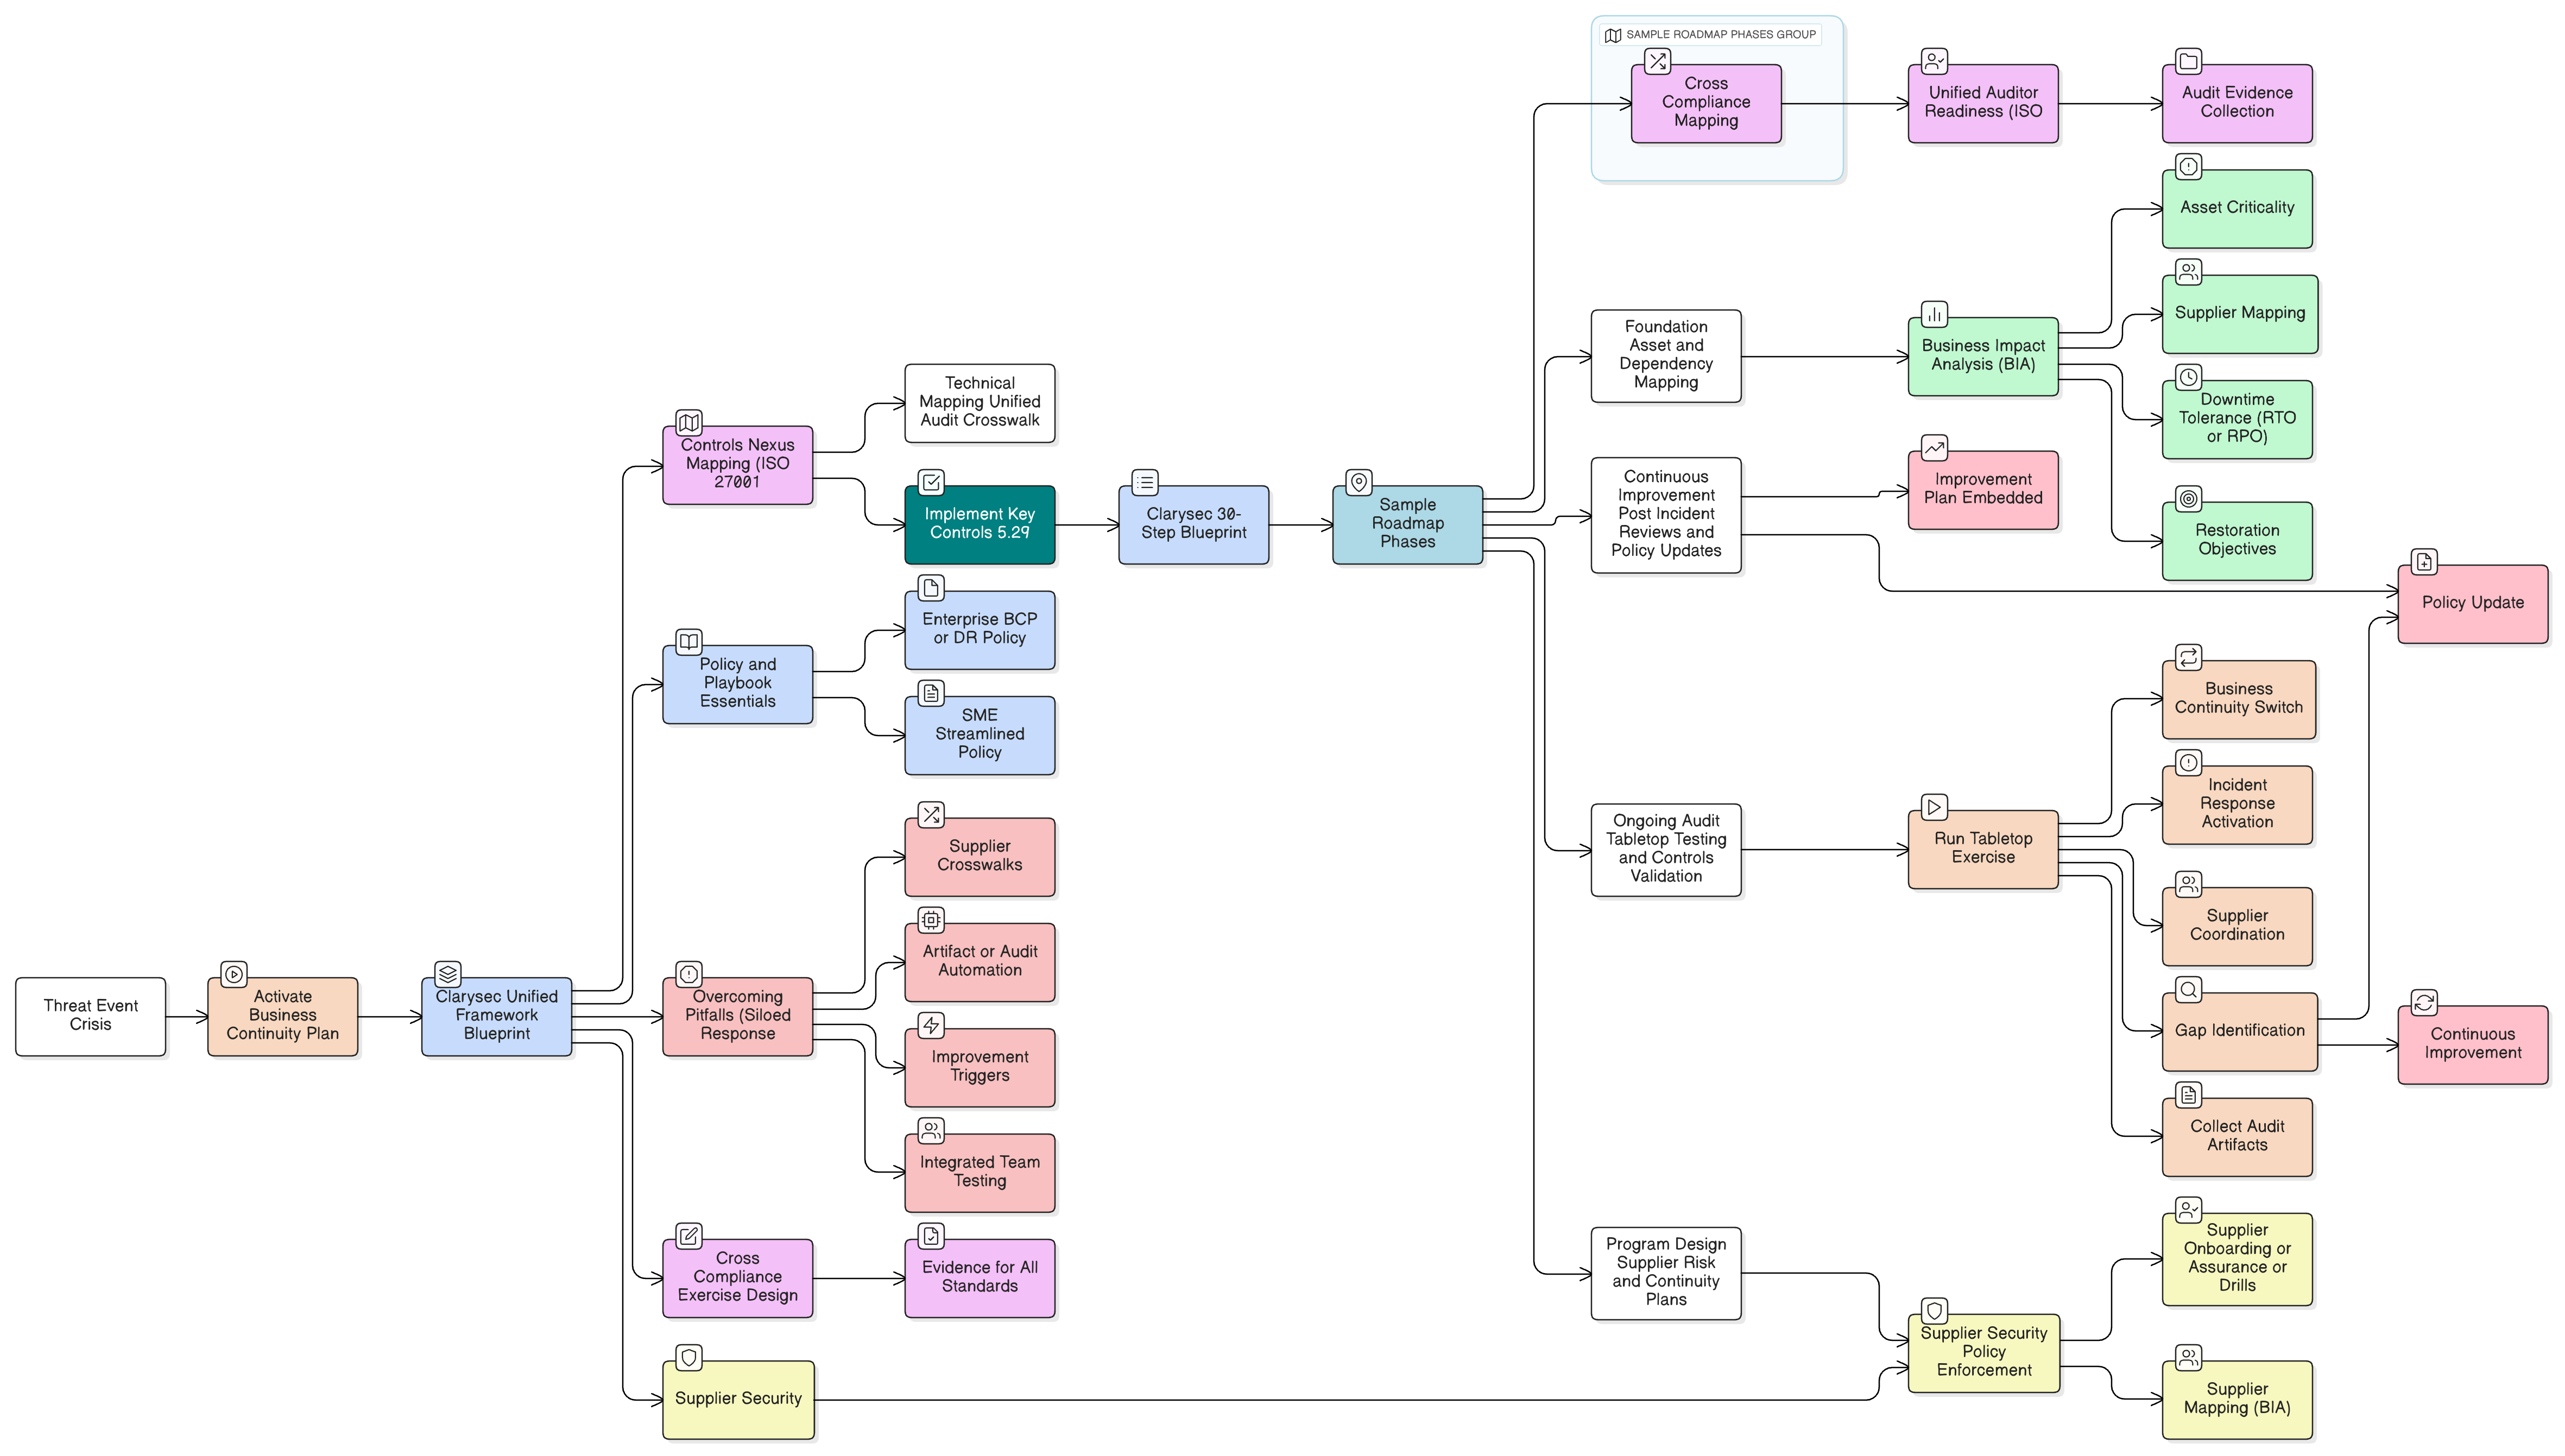
CISOs and compliance leaders face new urgency from DORA and NIS2. This flagship Clarysec guide demonstrates how to build robust operational resilience, across plans, controls, supplier management, and audits, by unifying global standards with tested action steps.
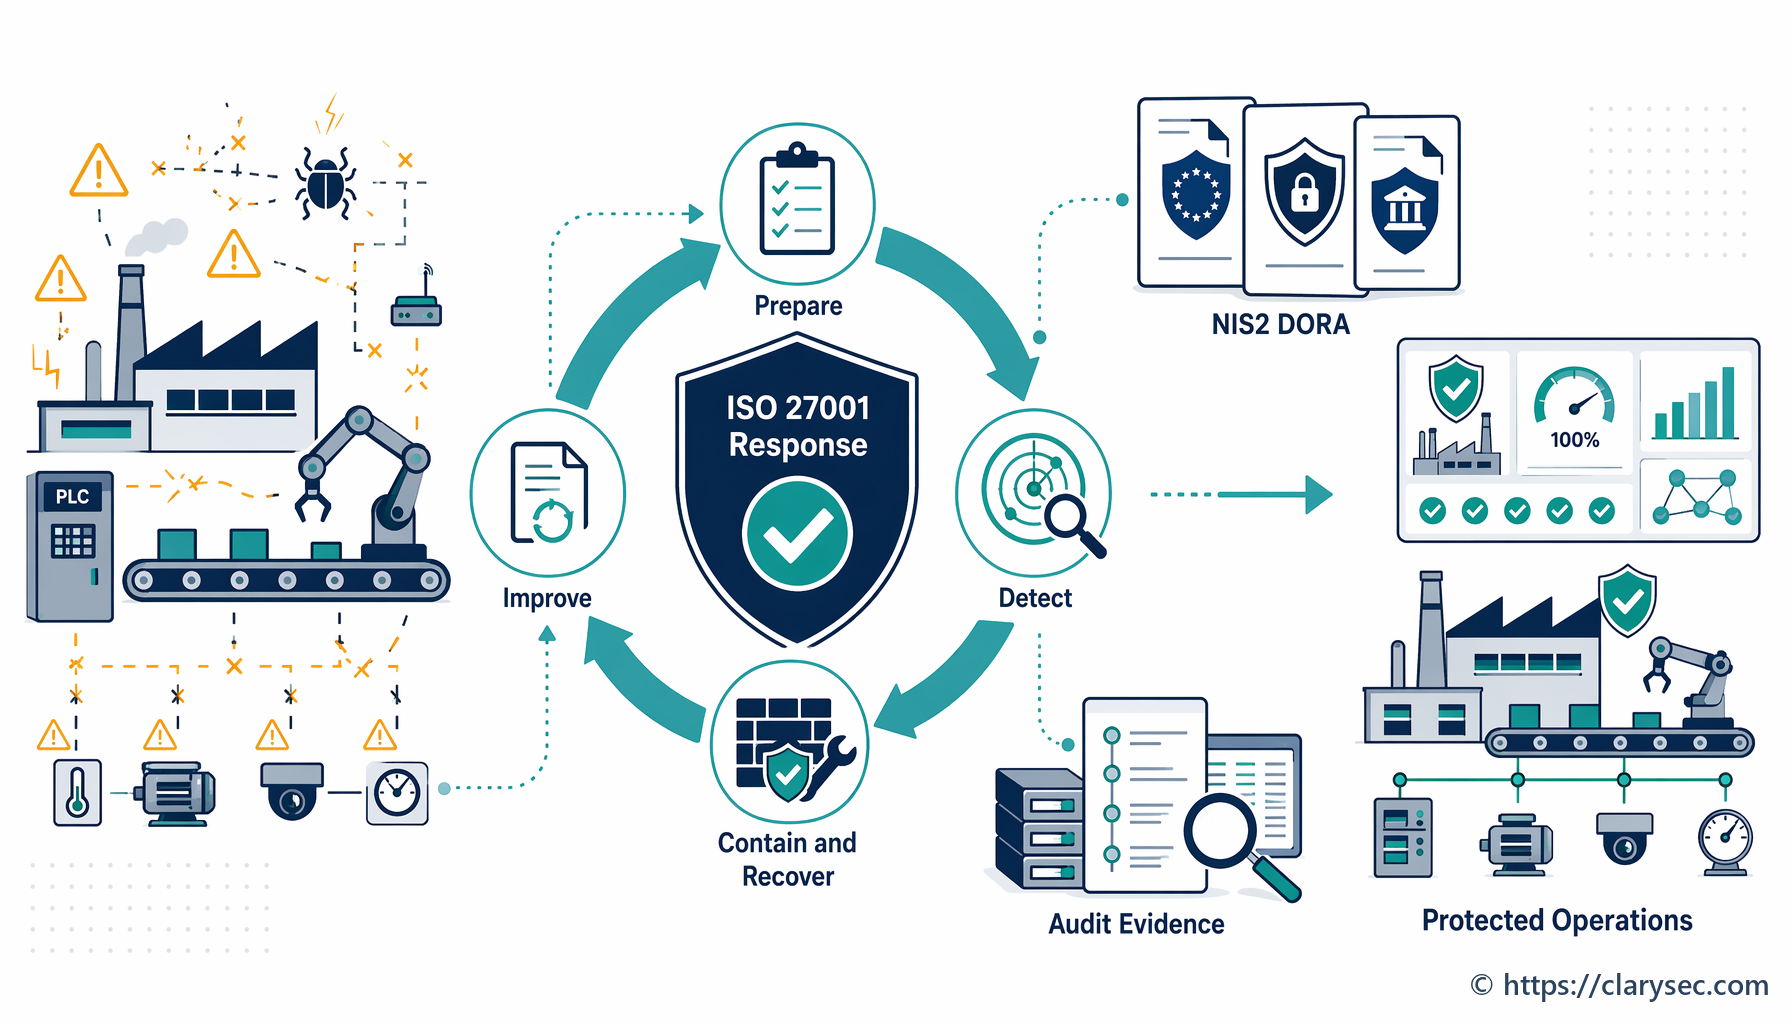
A guide for manufacturers on building a robust, ISO 27001-aligned incident response plan to protect operations and ensure compliance.
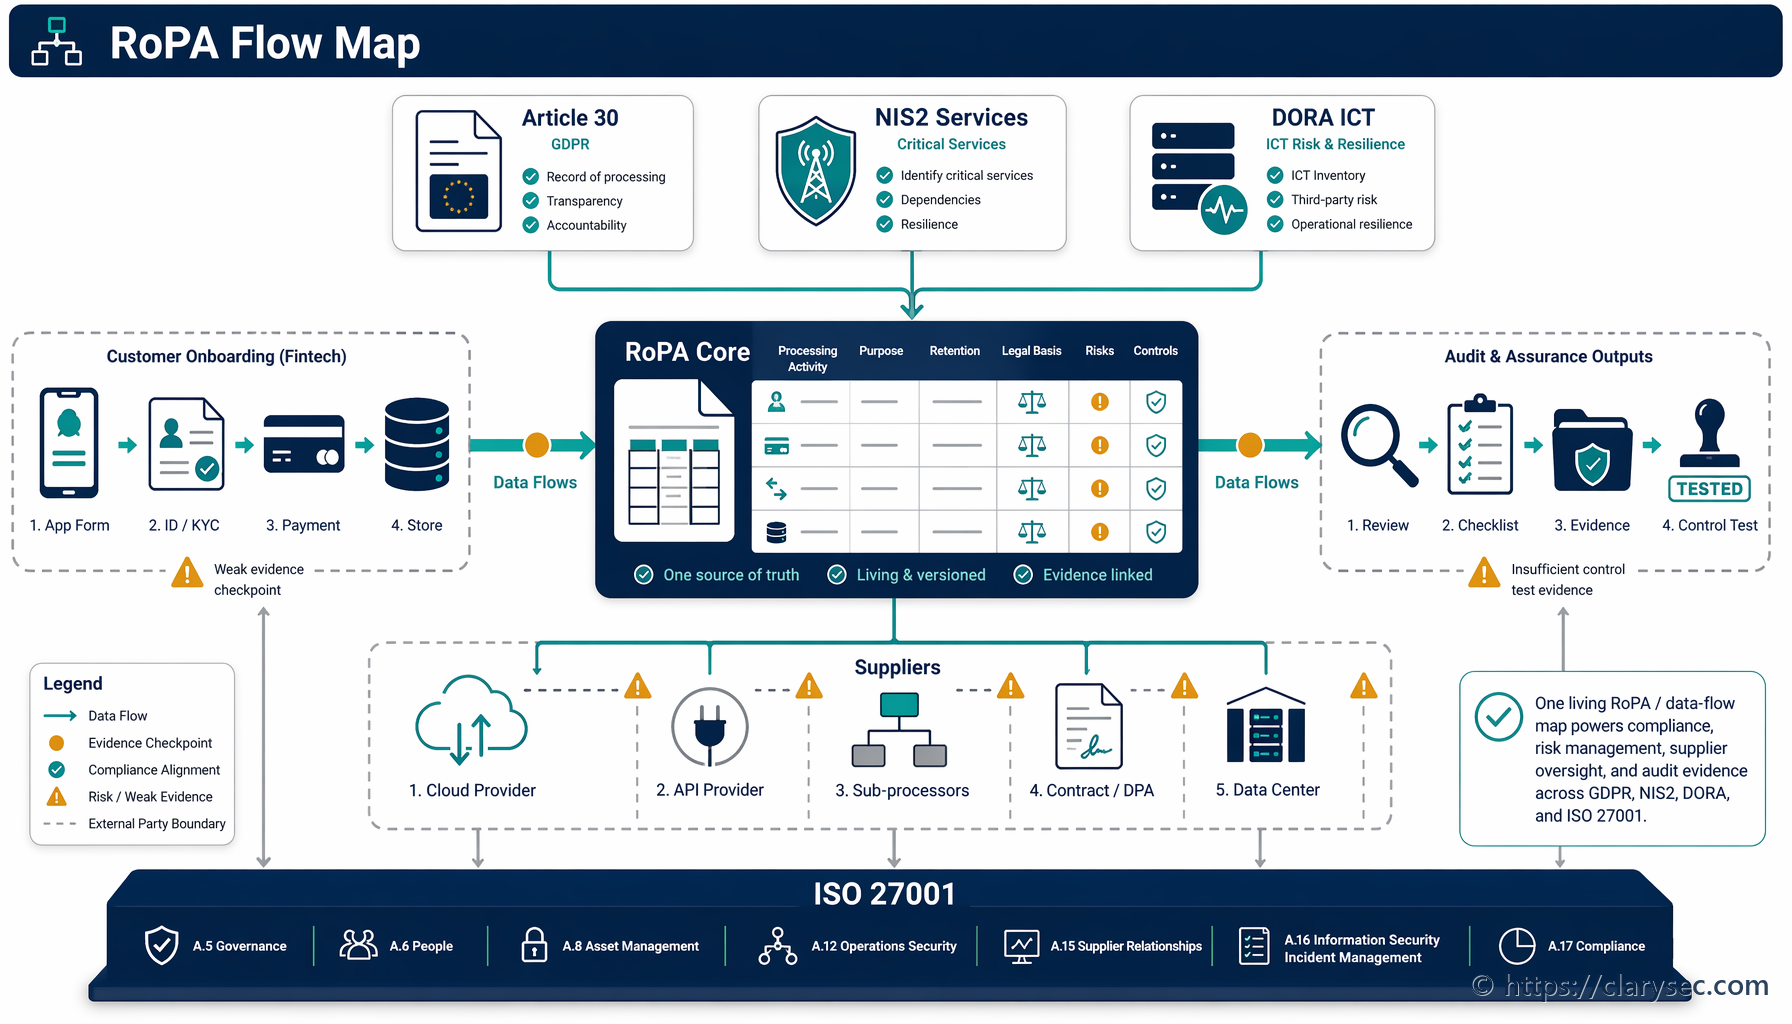
A practical 2026 guide for turning RoPA and data flow mapping into a unified evidence layer for GDPR Article 30, NIS2 critical services, DORA ICT dependencies and ISO/IEC 27001:2022 audits.