#Cloud Security
Articles tagged with "Cloud Security"
23 articles
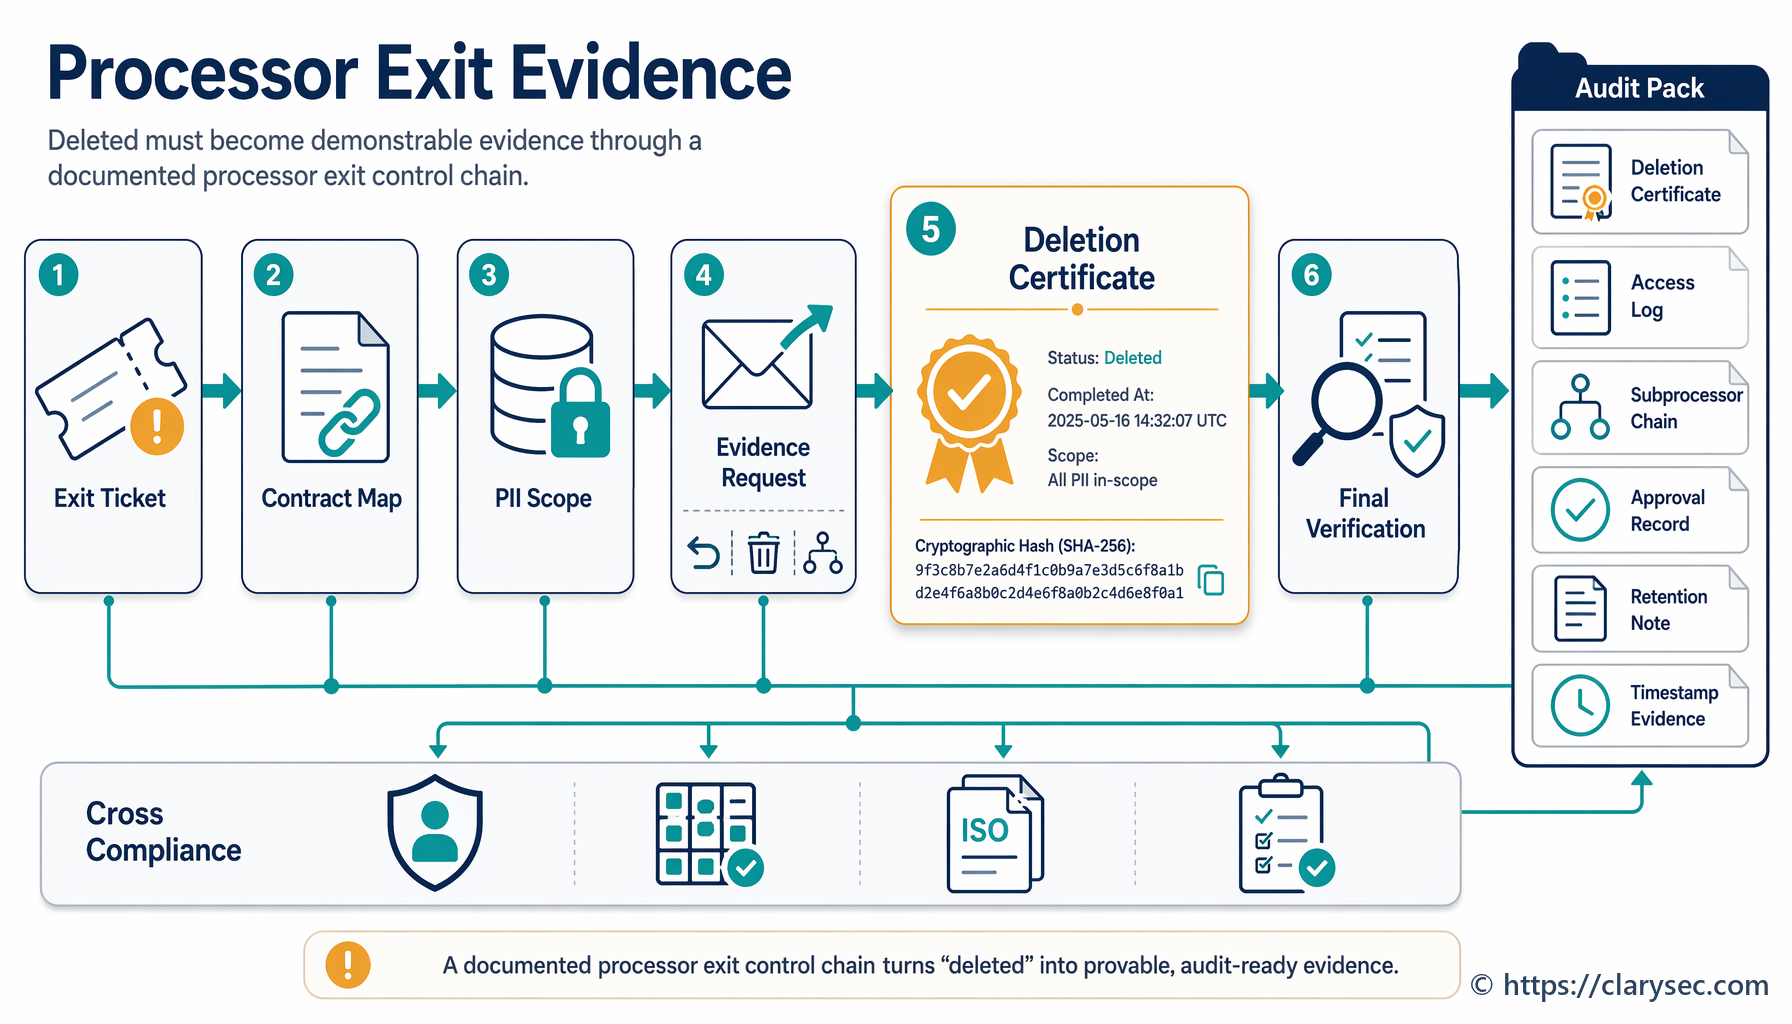
Processor exit is where supplier management, privacy governance, cloud offboarding and audit evidence collide. Learn how to build a deletion certificate workflow that supports GDPR, DORA, ISO/IEC 27701:2025 and ISO/IEC 27001:2022 compliance.
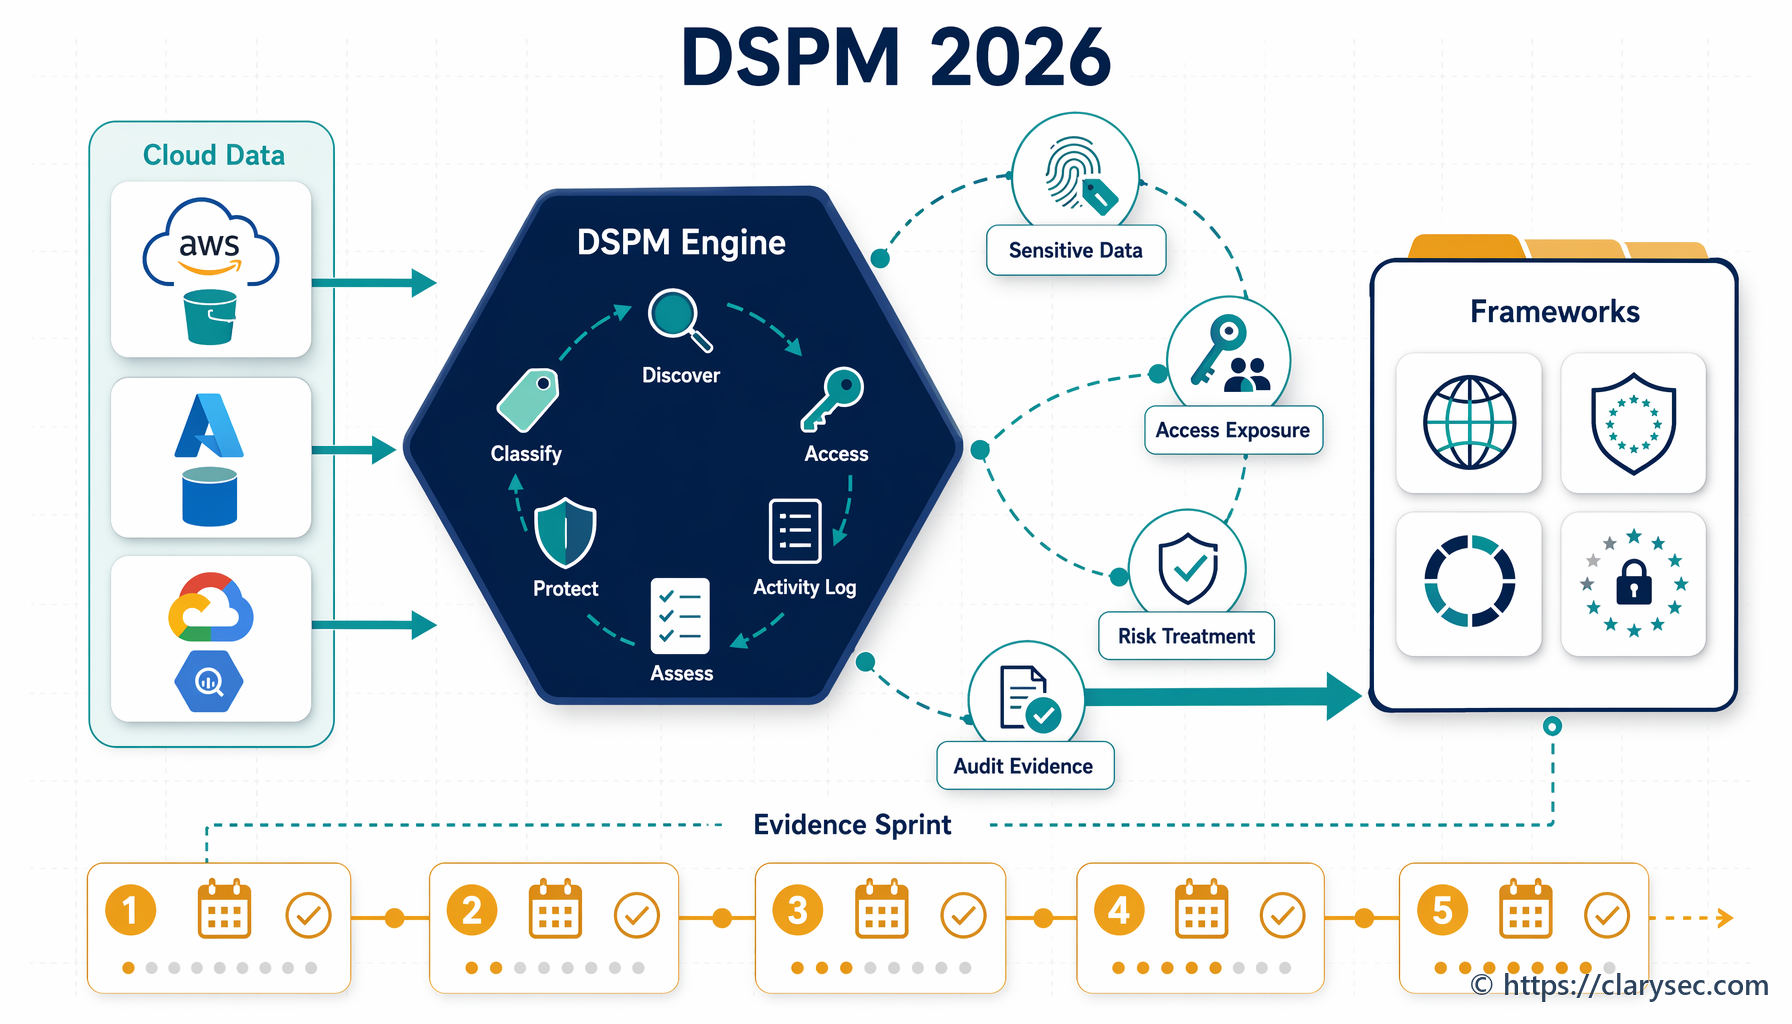
A unified CISO guide to Data Security Posture Management in 2026, showing how sensitive data discovery, access exposure and cloud data risk become reusable evidence for ISO/IEC 27001:2022, NIS2, DORA and GDPR.
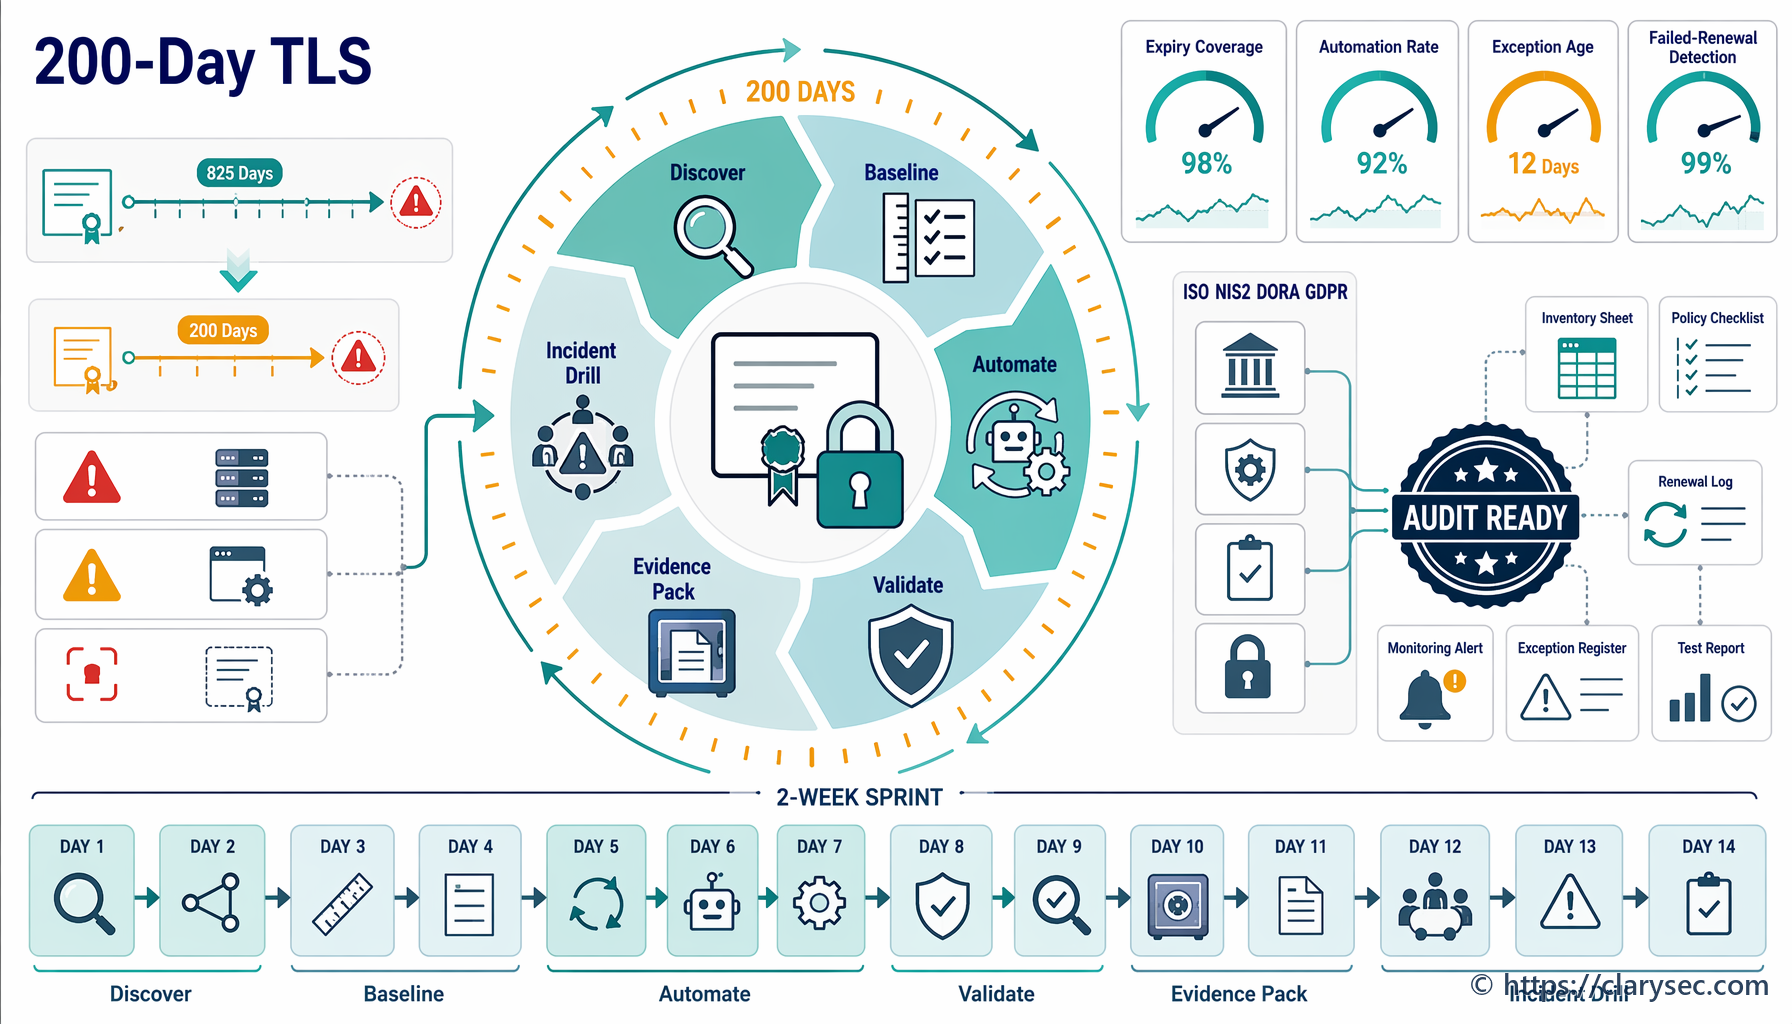
Shorter public TLS certificate validity turns renewal into a recurring governance, resilience and audit evidence challenge. This guide shows how to manage certificates as governed security assets under ISO/IEC 27001:2022, NIS2, DORA and GDPR Article 32.
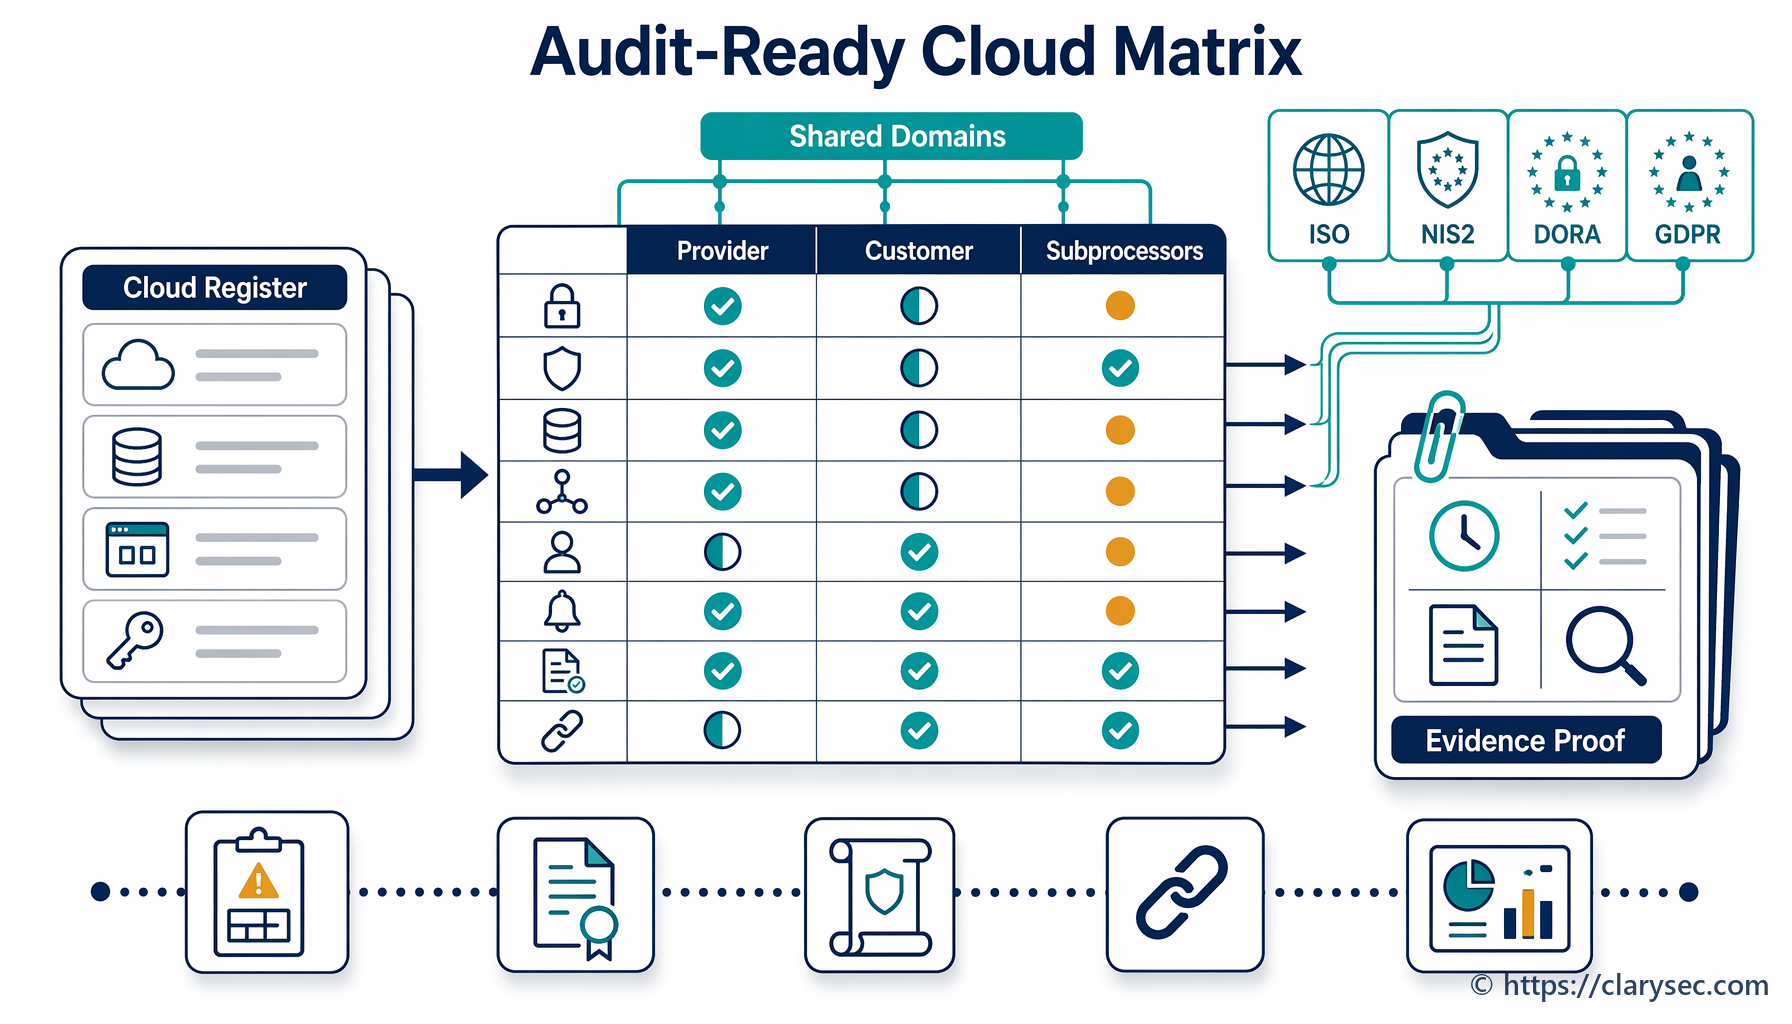
A practical CISO guide to building a cloud shared responsibility matrix that proves who owns each control, what evidence is required, and how cloud providers and subprocessors are governed across ISO/IEC 27001:2022, NIS2, DORA and GDPR.
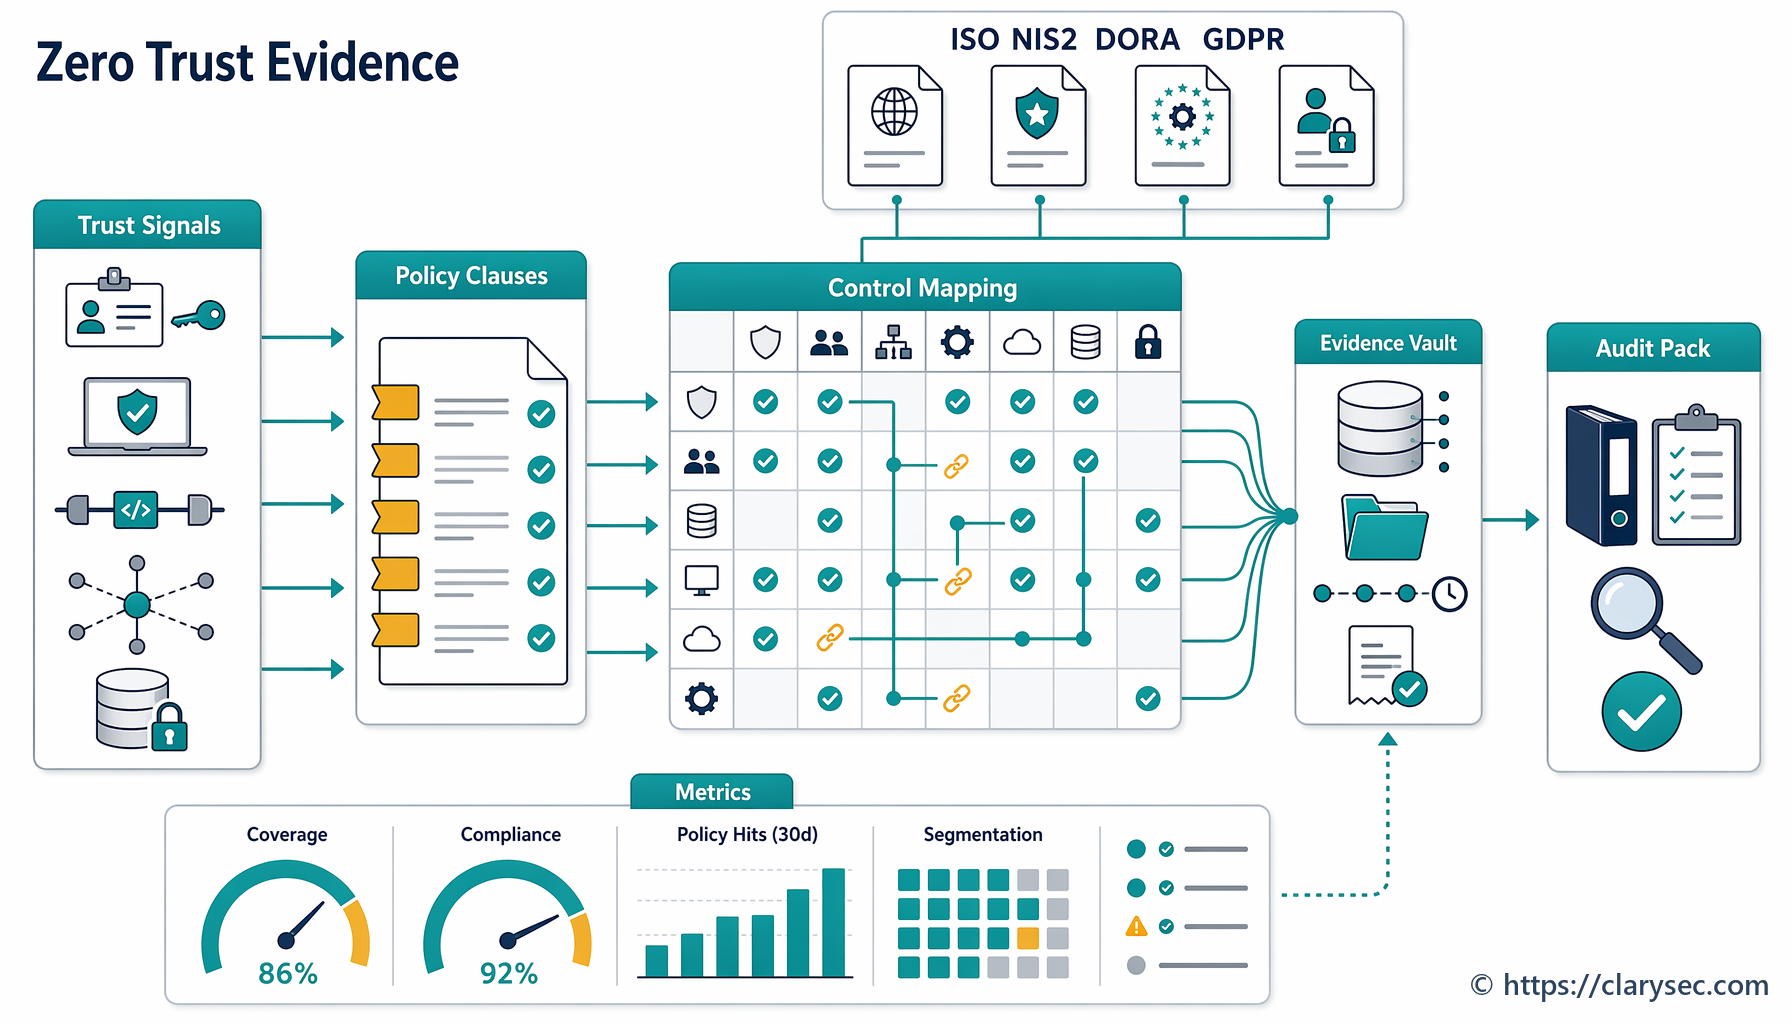
A practical guide to turning NIST SP 800-207 Zero Trust Architecture into audit-ready evidence for ISO/IEC 27001:2022, NIS2, DORA, GDPR and customer security reviews.
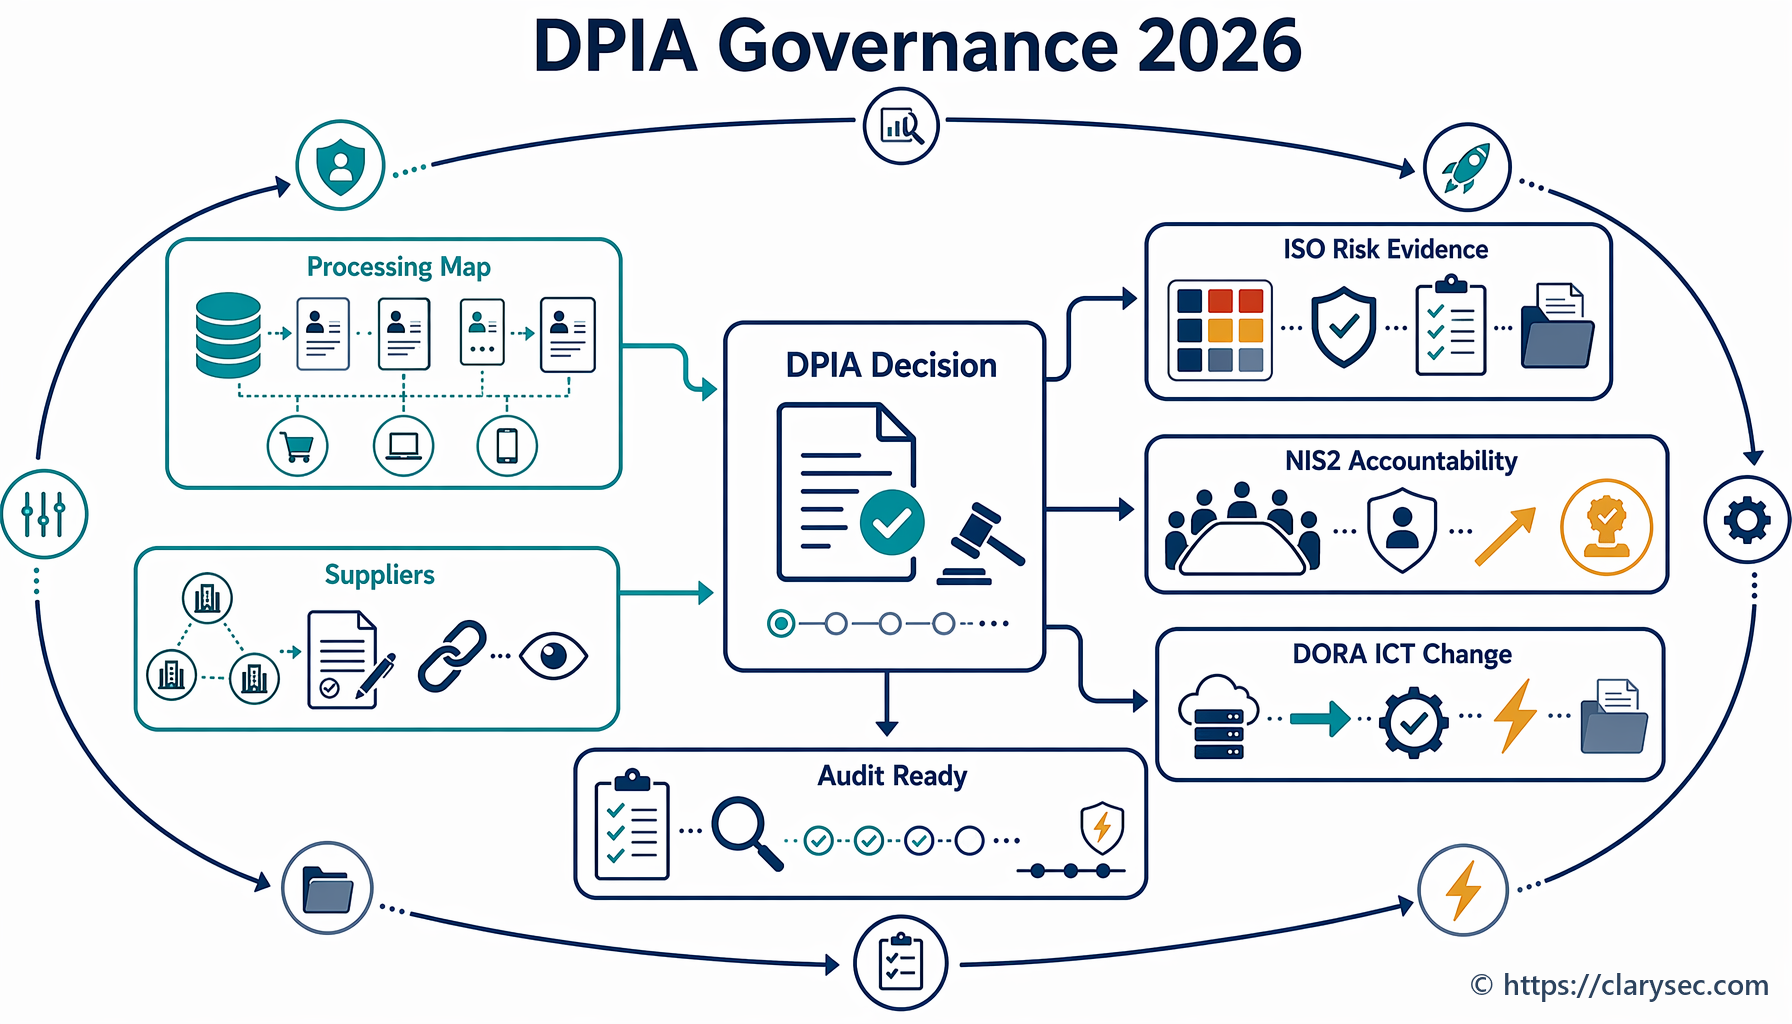
A unified 2026 guide for turning DPIAs into audit-ready governance evidence across GDPR accountability, ISO/IEC 27001:2022, NIS2 cybersecurity measures, DORA ICT change and supplier risk.
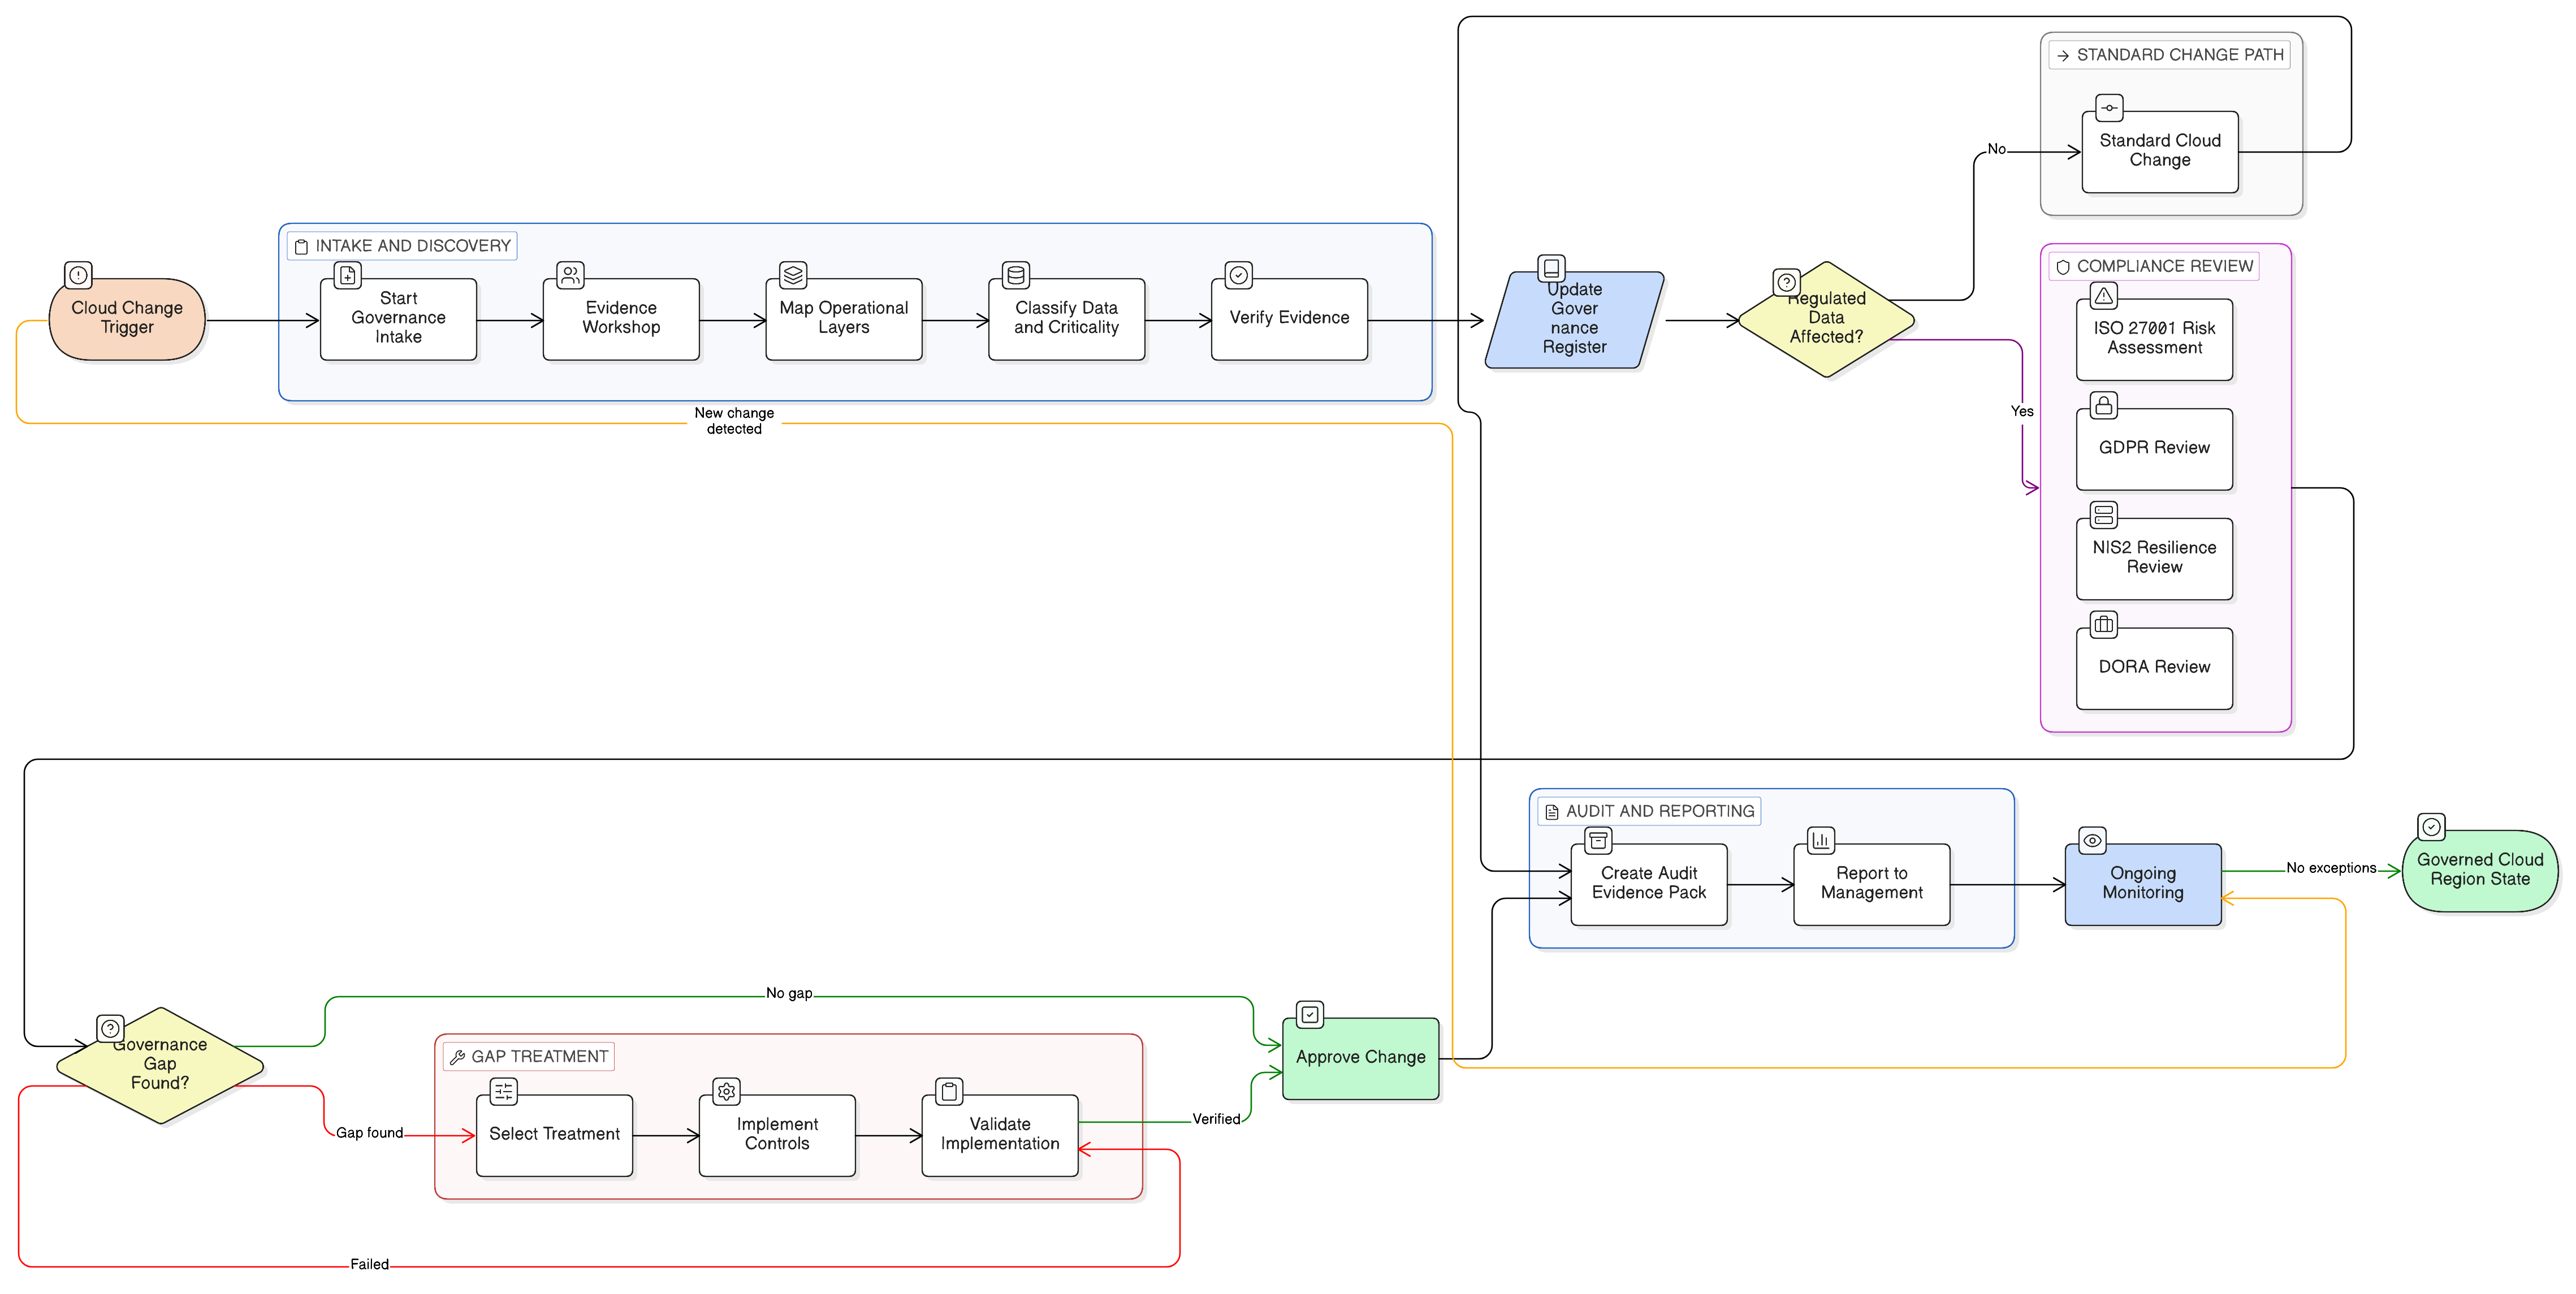
A practical CISO guide to governing cloud regions, backups, logs, support access and subcontractors through ISO/IEC 27001:2022, GDPR, NIS2 and DORA.
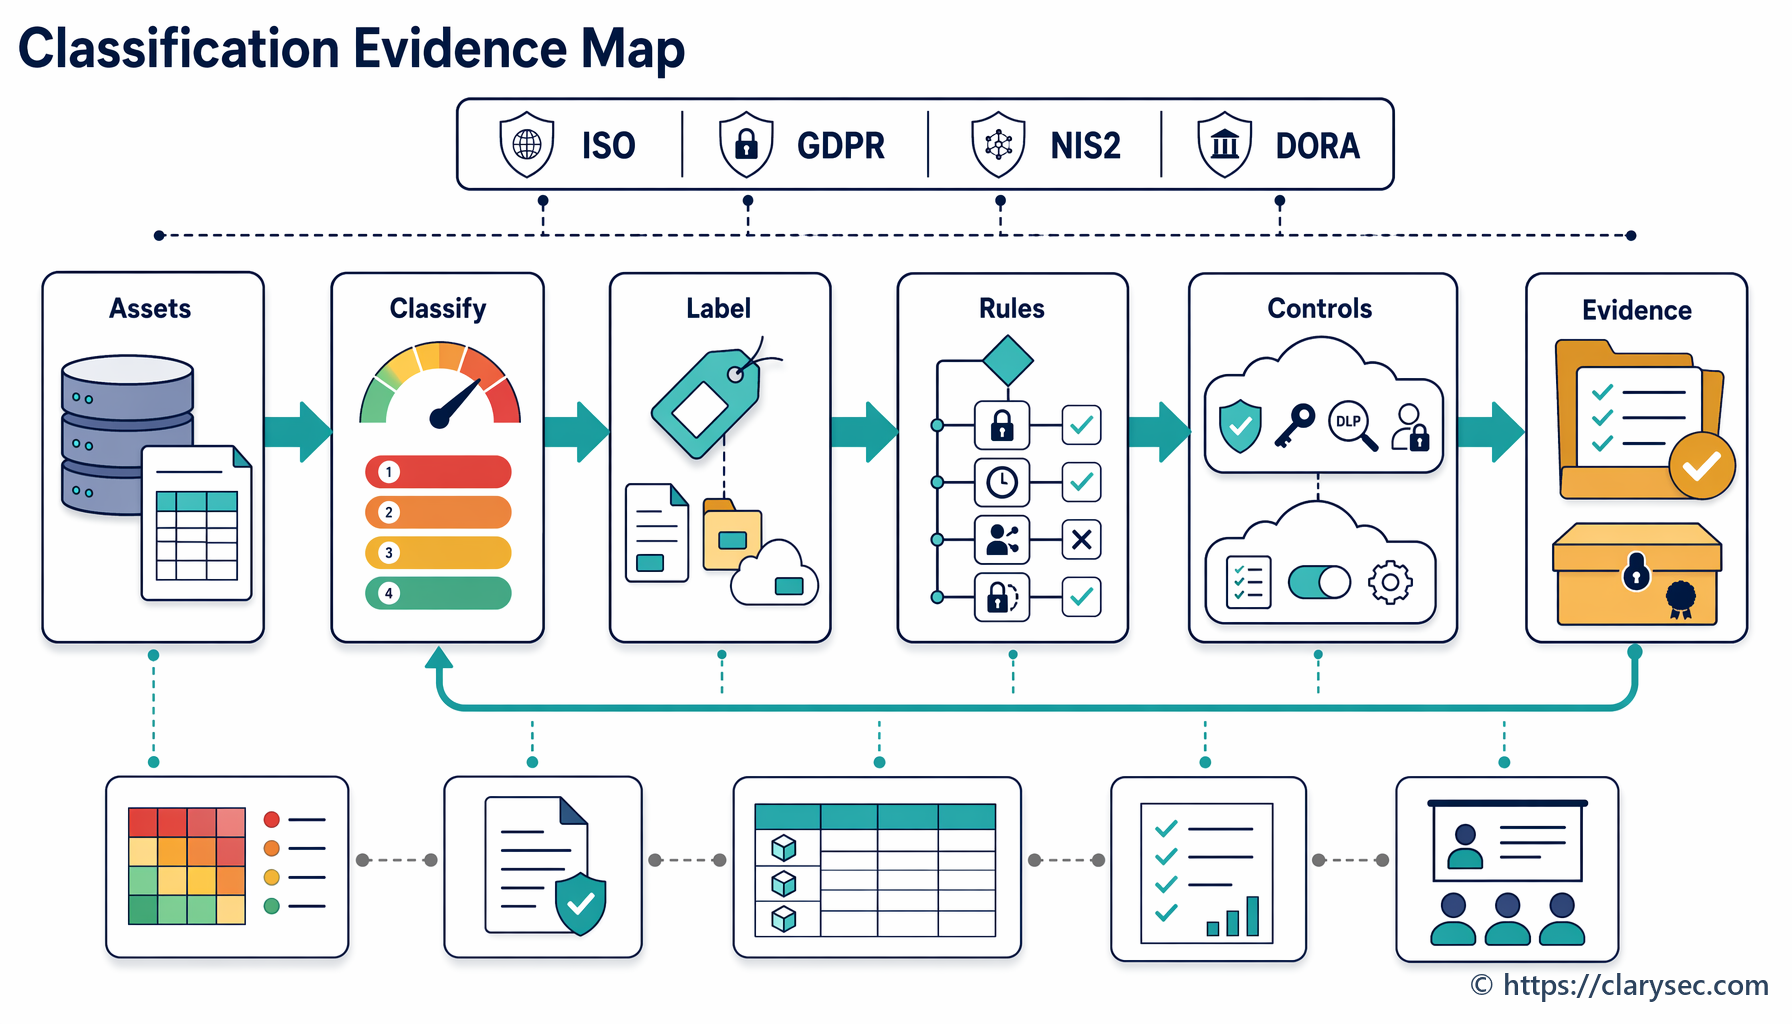
A practical CISO guide to using data classification and information labelling as the evidence layer for ISO/IEC 27001:2022, GDPR Article 32, NIS2 Article 21 and DORA ICT risk management.
A practical, scenario-driven guide to secure change management using ISO/IEC 27001:2022, Clarysec policies, Zenith Blueprint, and Zenith Controls to support NIS2, DORA, GDPR, NIST CSF 2.0, and audit evidence in 2026.