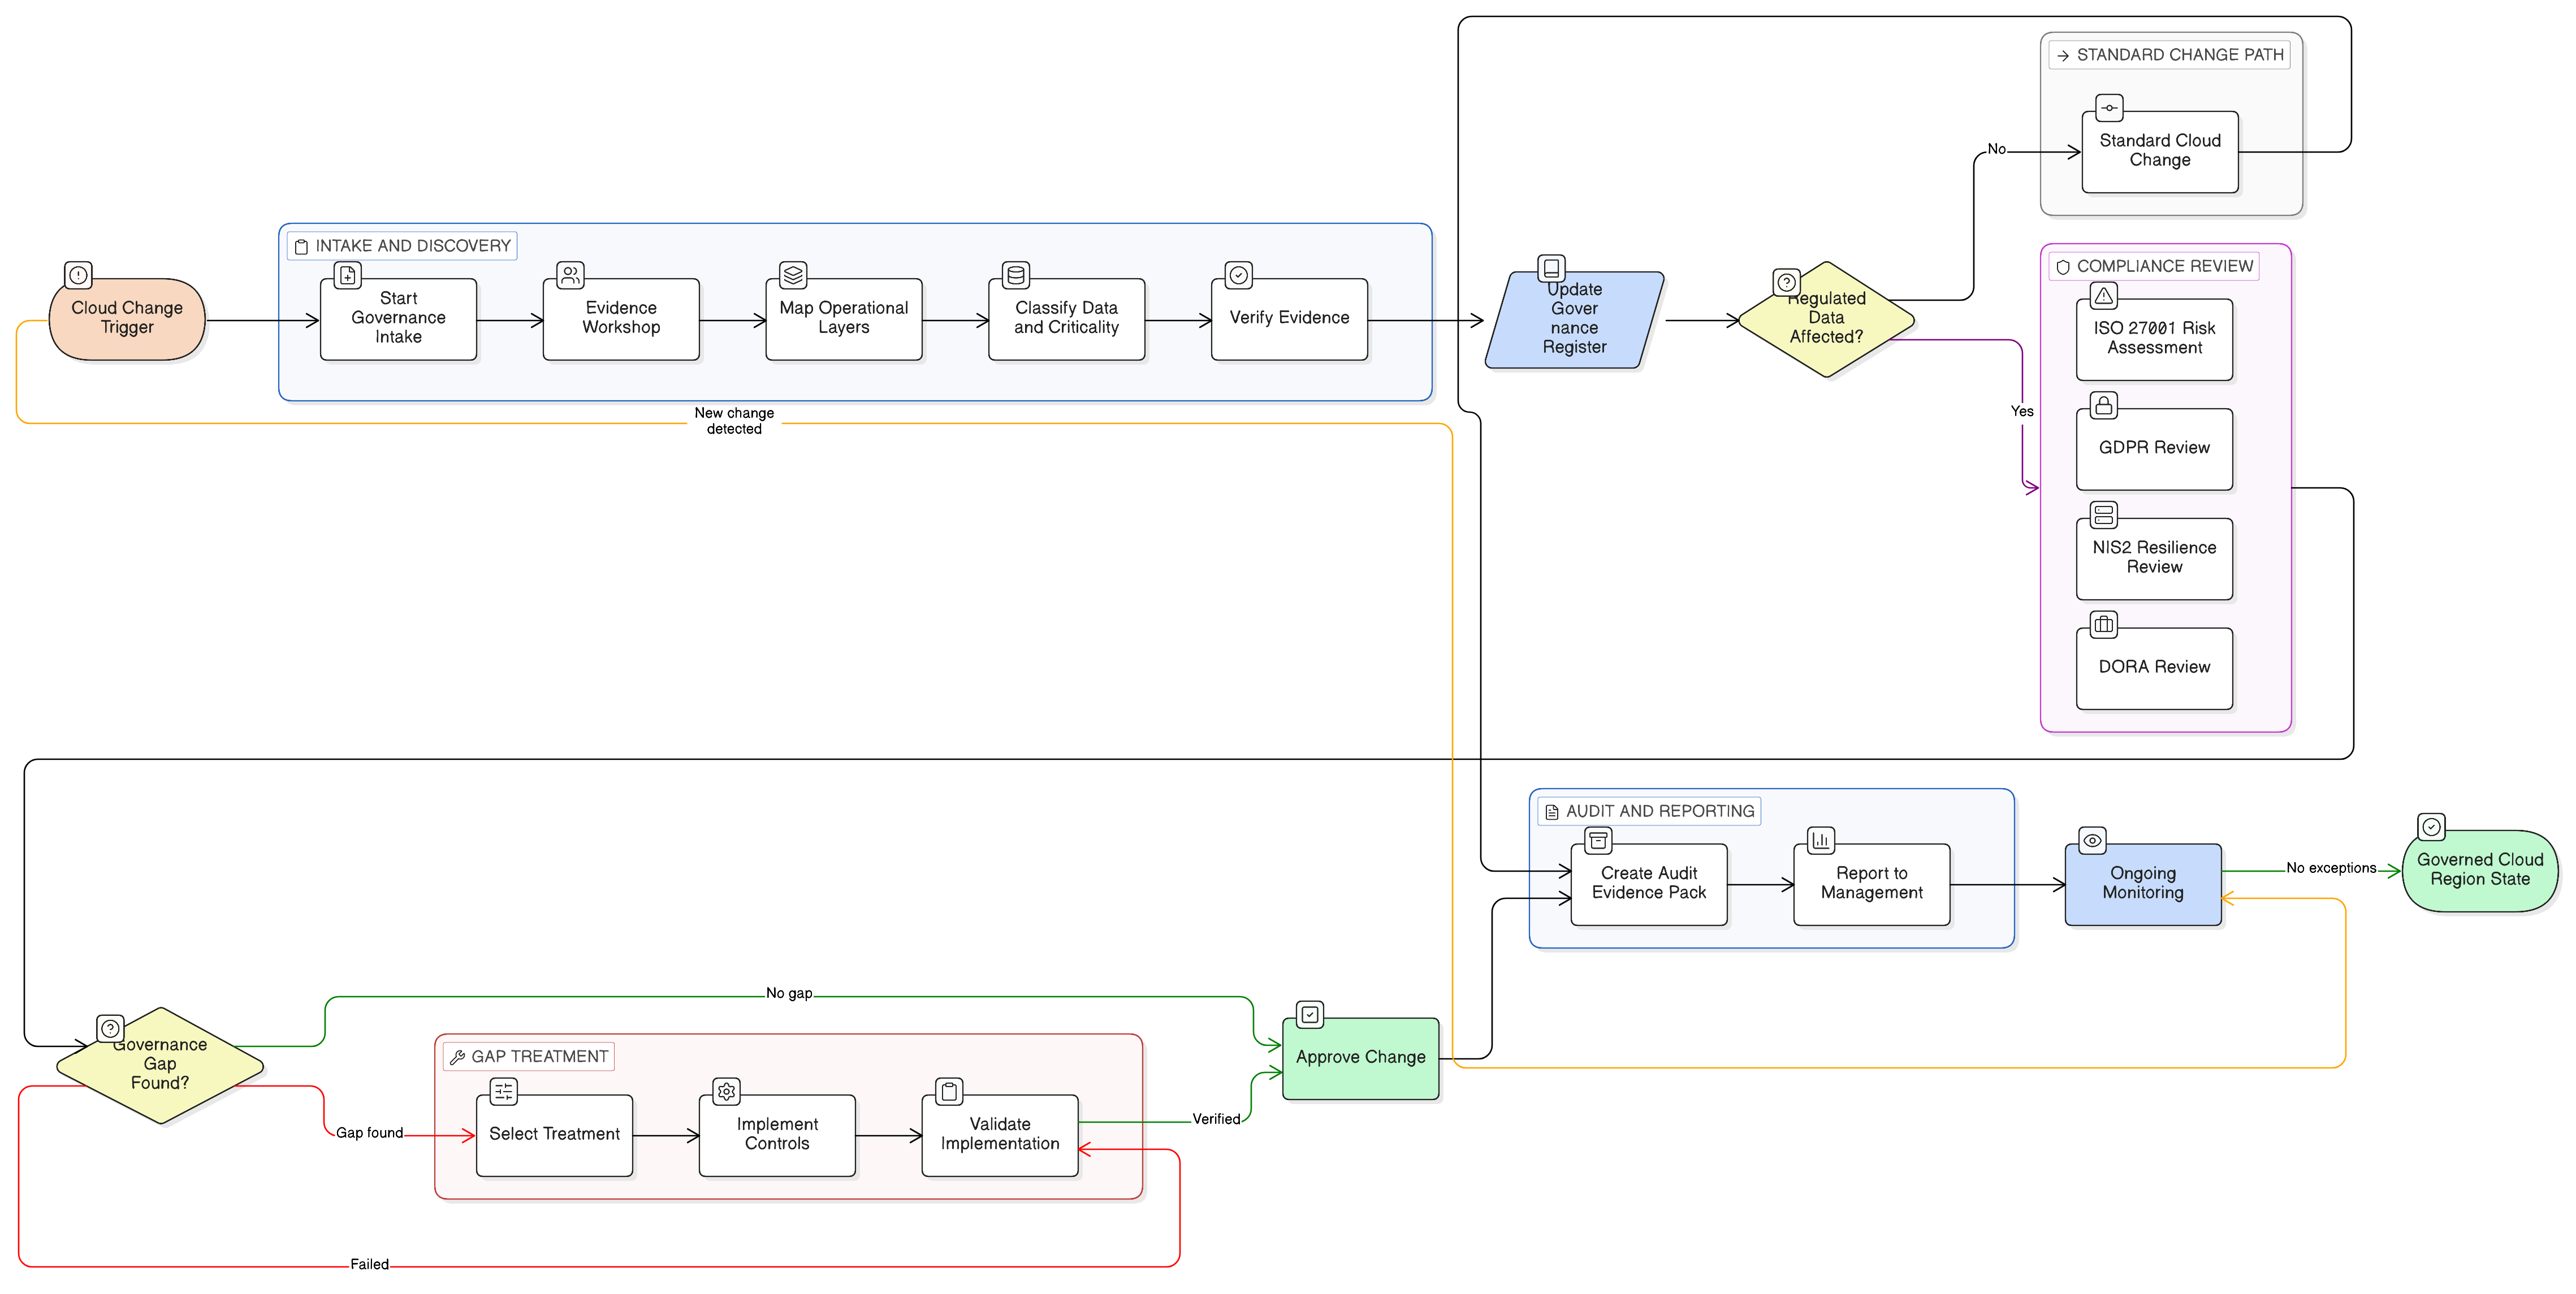
Cloud Region Governance for GDPR, NIS2 and DORA
A practical CISO guide to governing cloud regions, backups, logs, support access and subcontractors through ISO/IEC 27001:2022, GDPR, NIS2 and DORA.
Articles tagged with "Cloud Security"
A practical CISO guide to governing cloud regions, backups, logs, support access and subcontractors through ISO/IEC 27001:2022, GDPR, NIS2 and DORA.
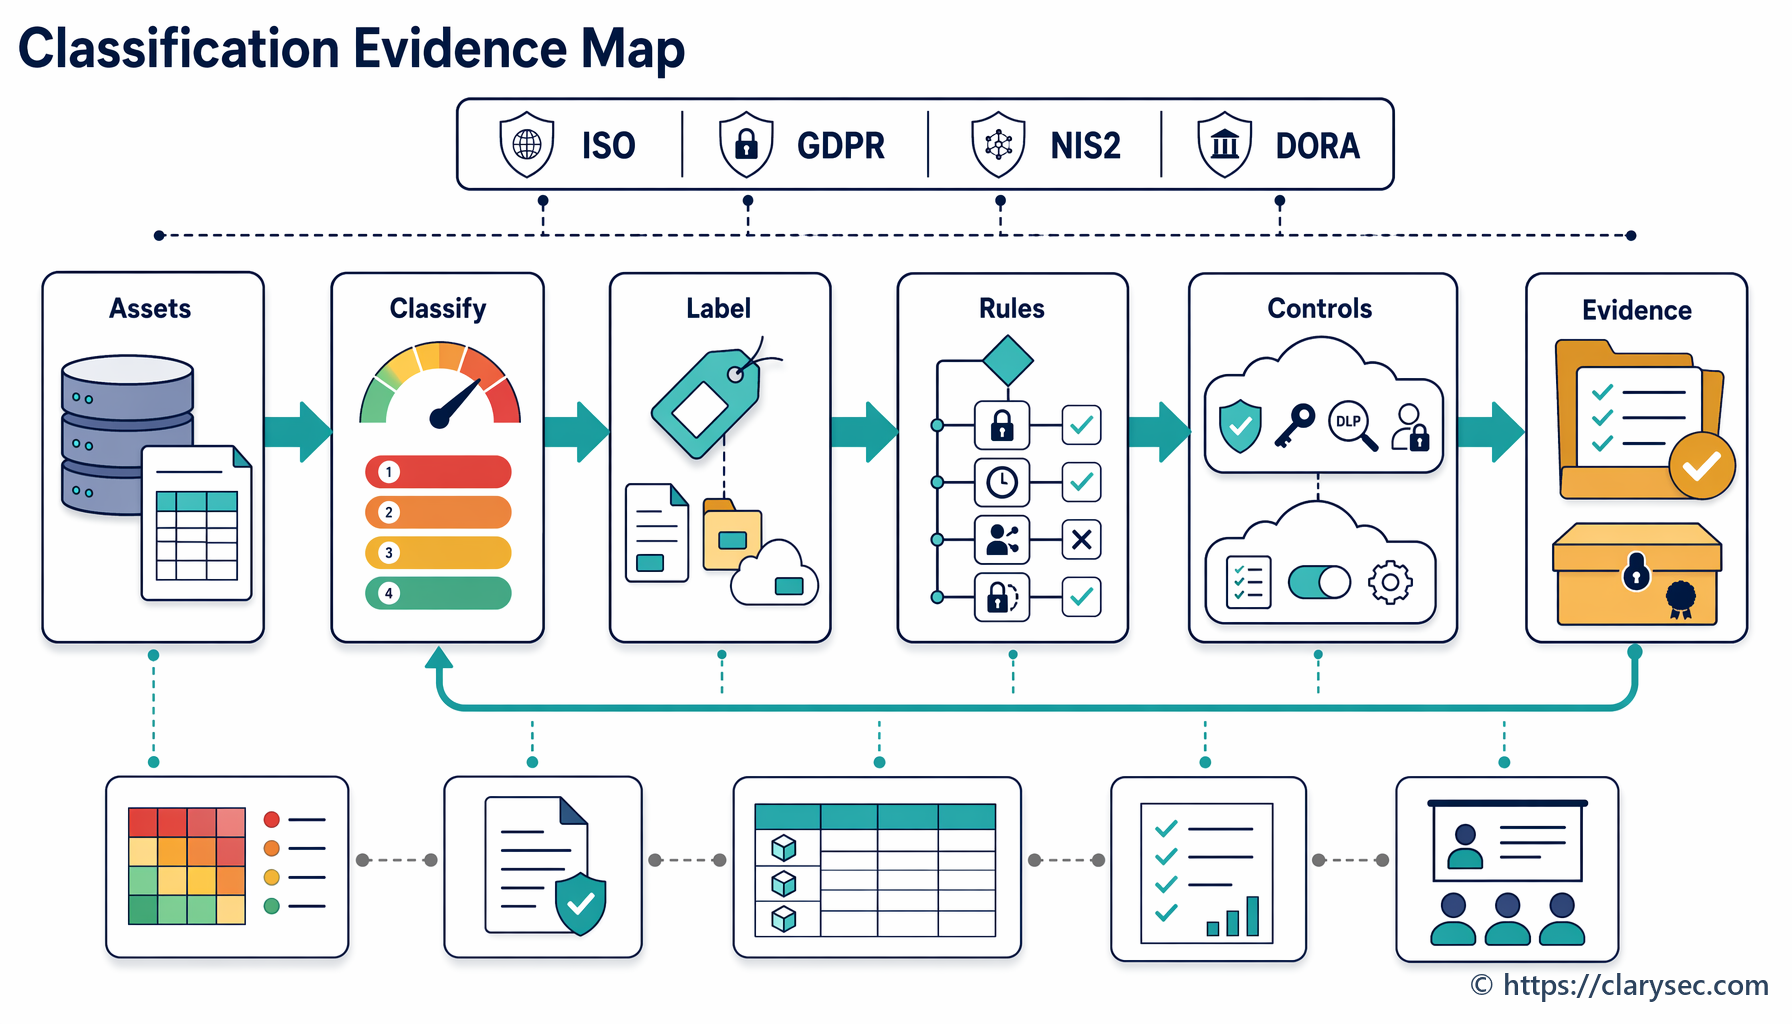
A practical CISO guide to using data classification and information labelling as the evidence layer for ISO/IEC 27001:2022, GDPR Article 32, NIS2 Article 21 and DORA ICT risk management.
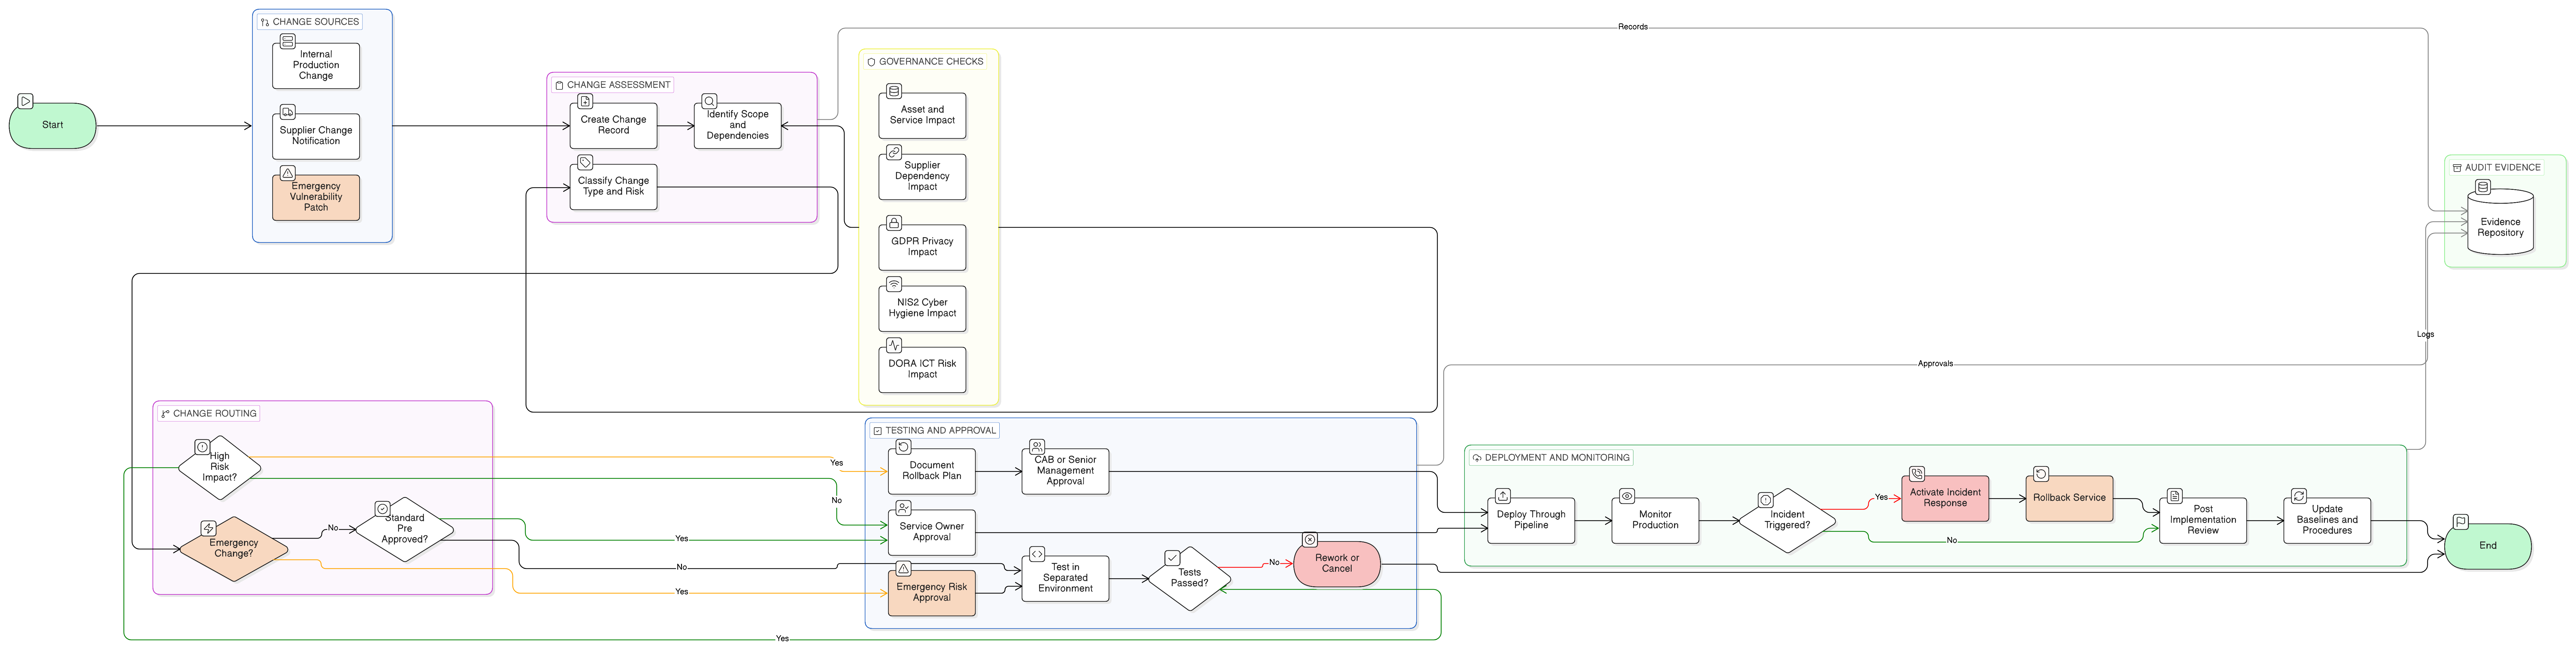
A practical, scenario-driven guide to secure change management using ISO/IEC 27001:2022, Clarysec policies, Zenith Blueprint, and Zenith Controls to support NIS2, DORA, GDPR, NIST CSF 2.0, and audit evidence in 2026.
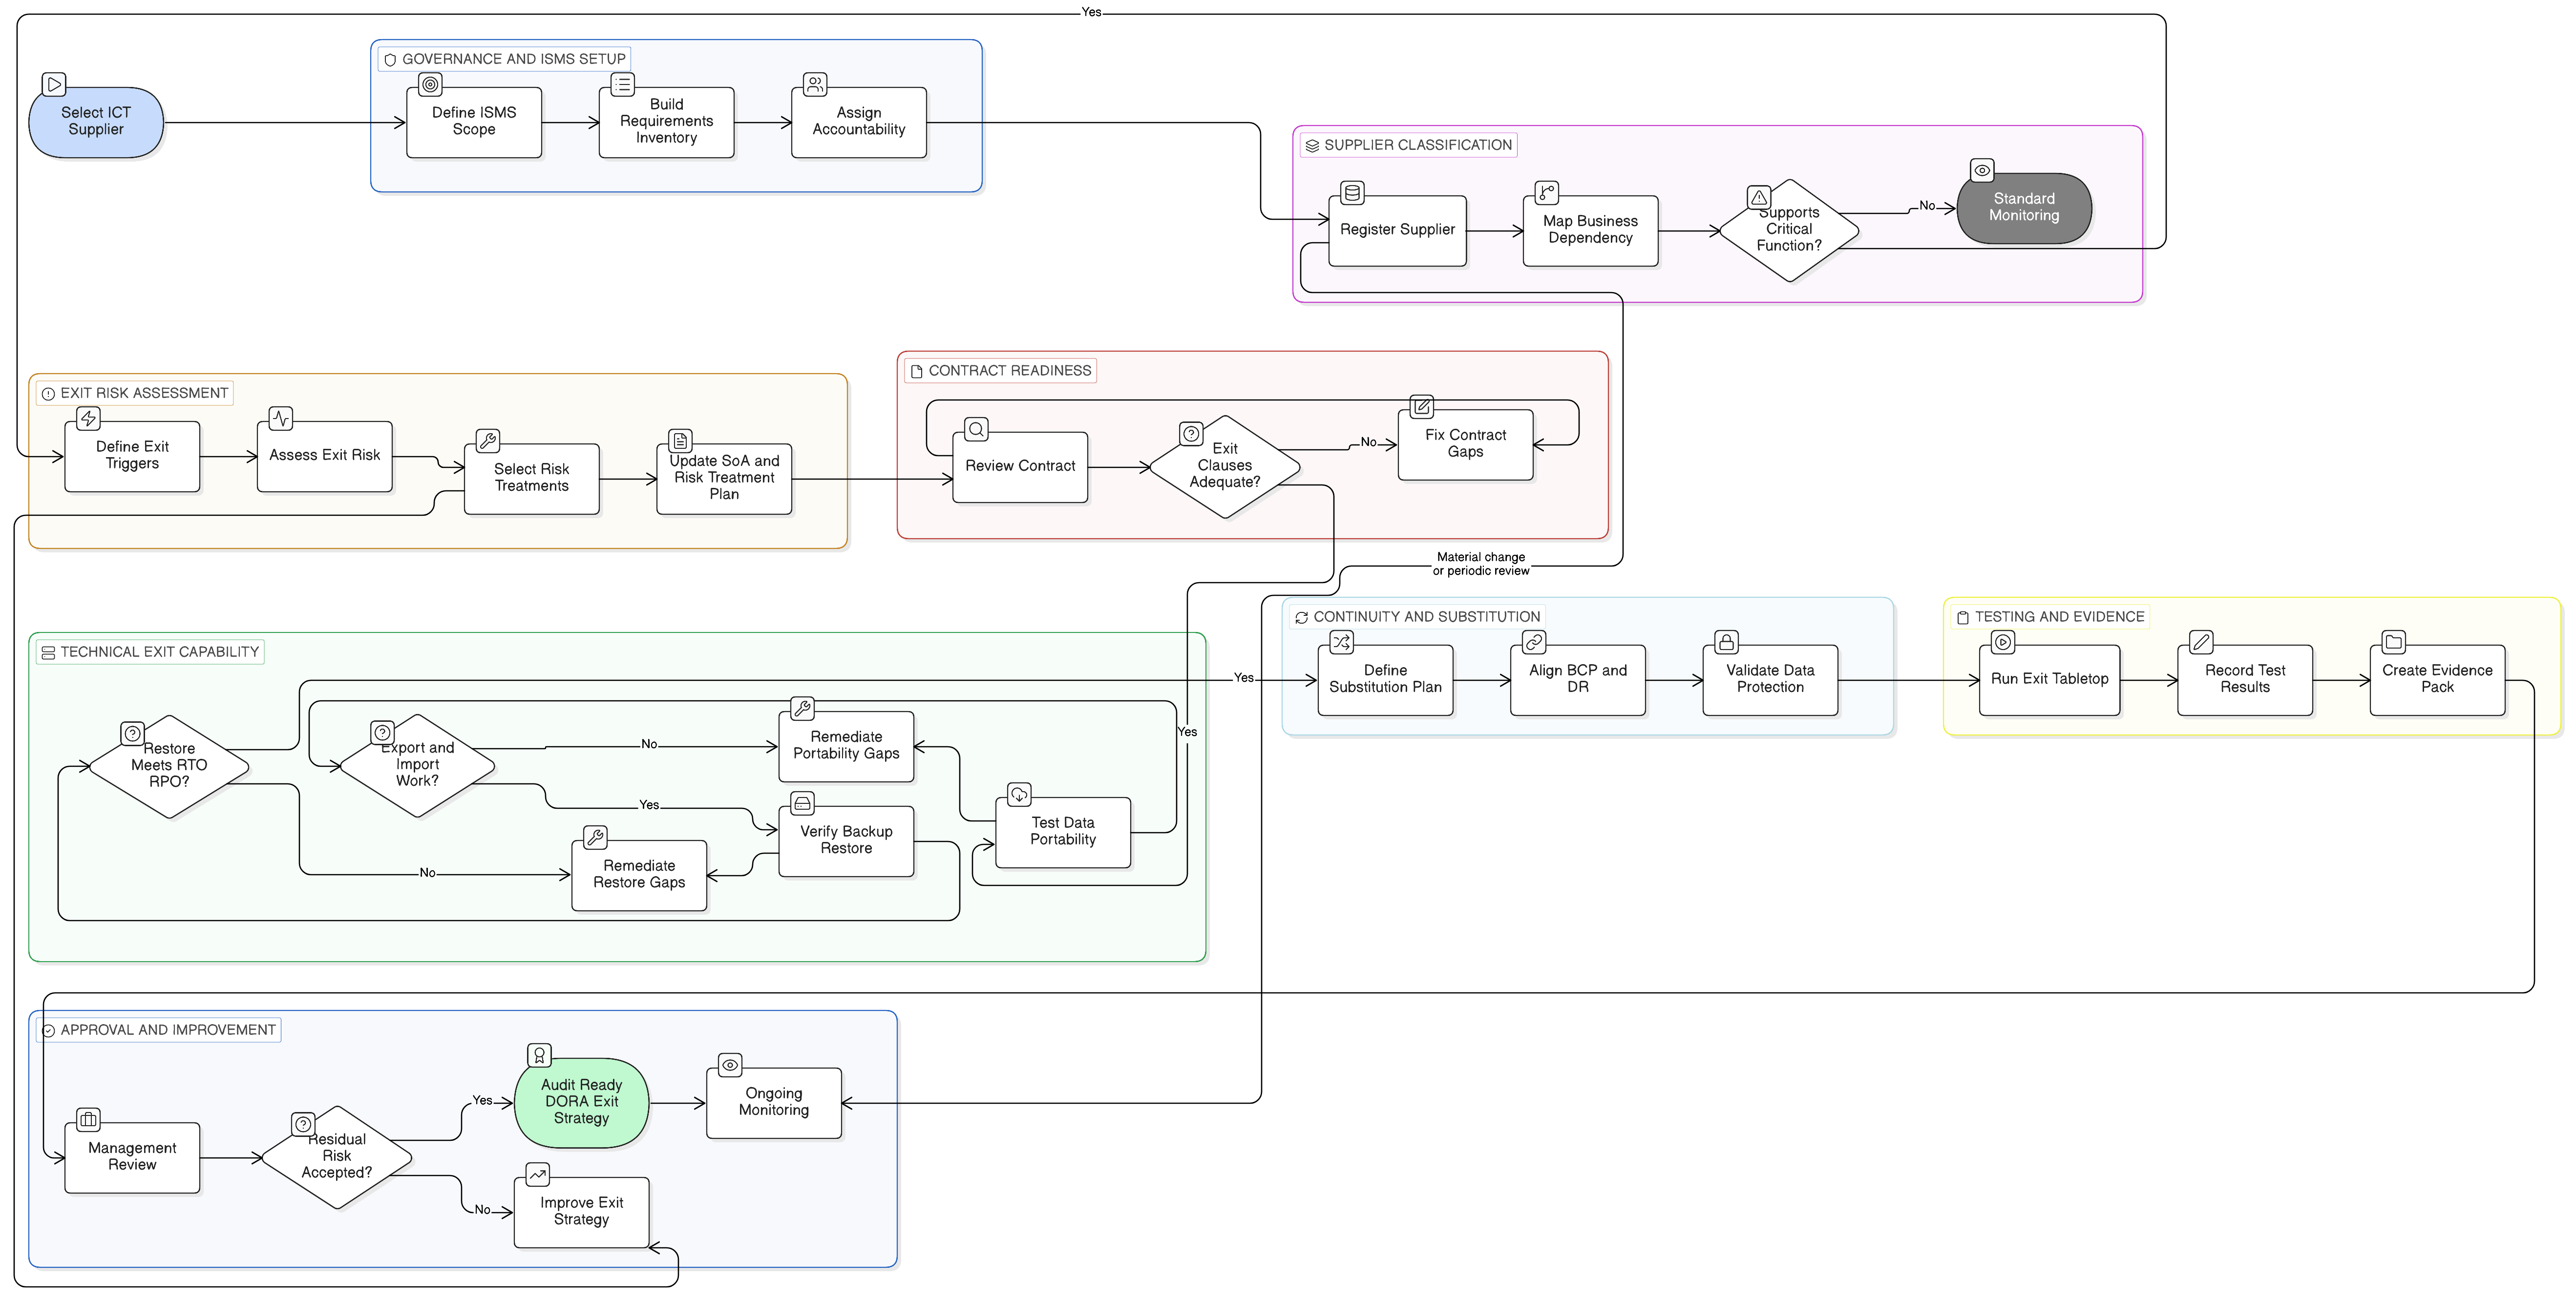
A practical guide for building DORA ICT third-party exit strategies that are contract-backed, technically feasible, tested, and audit-ready.
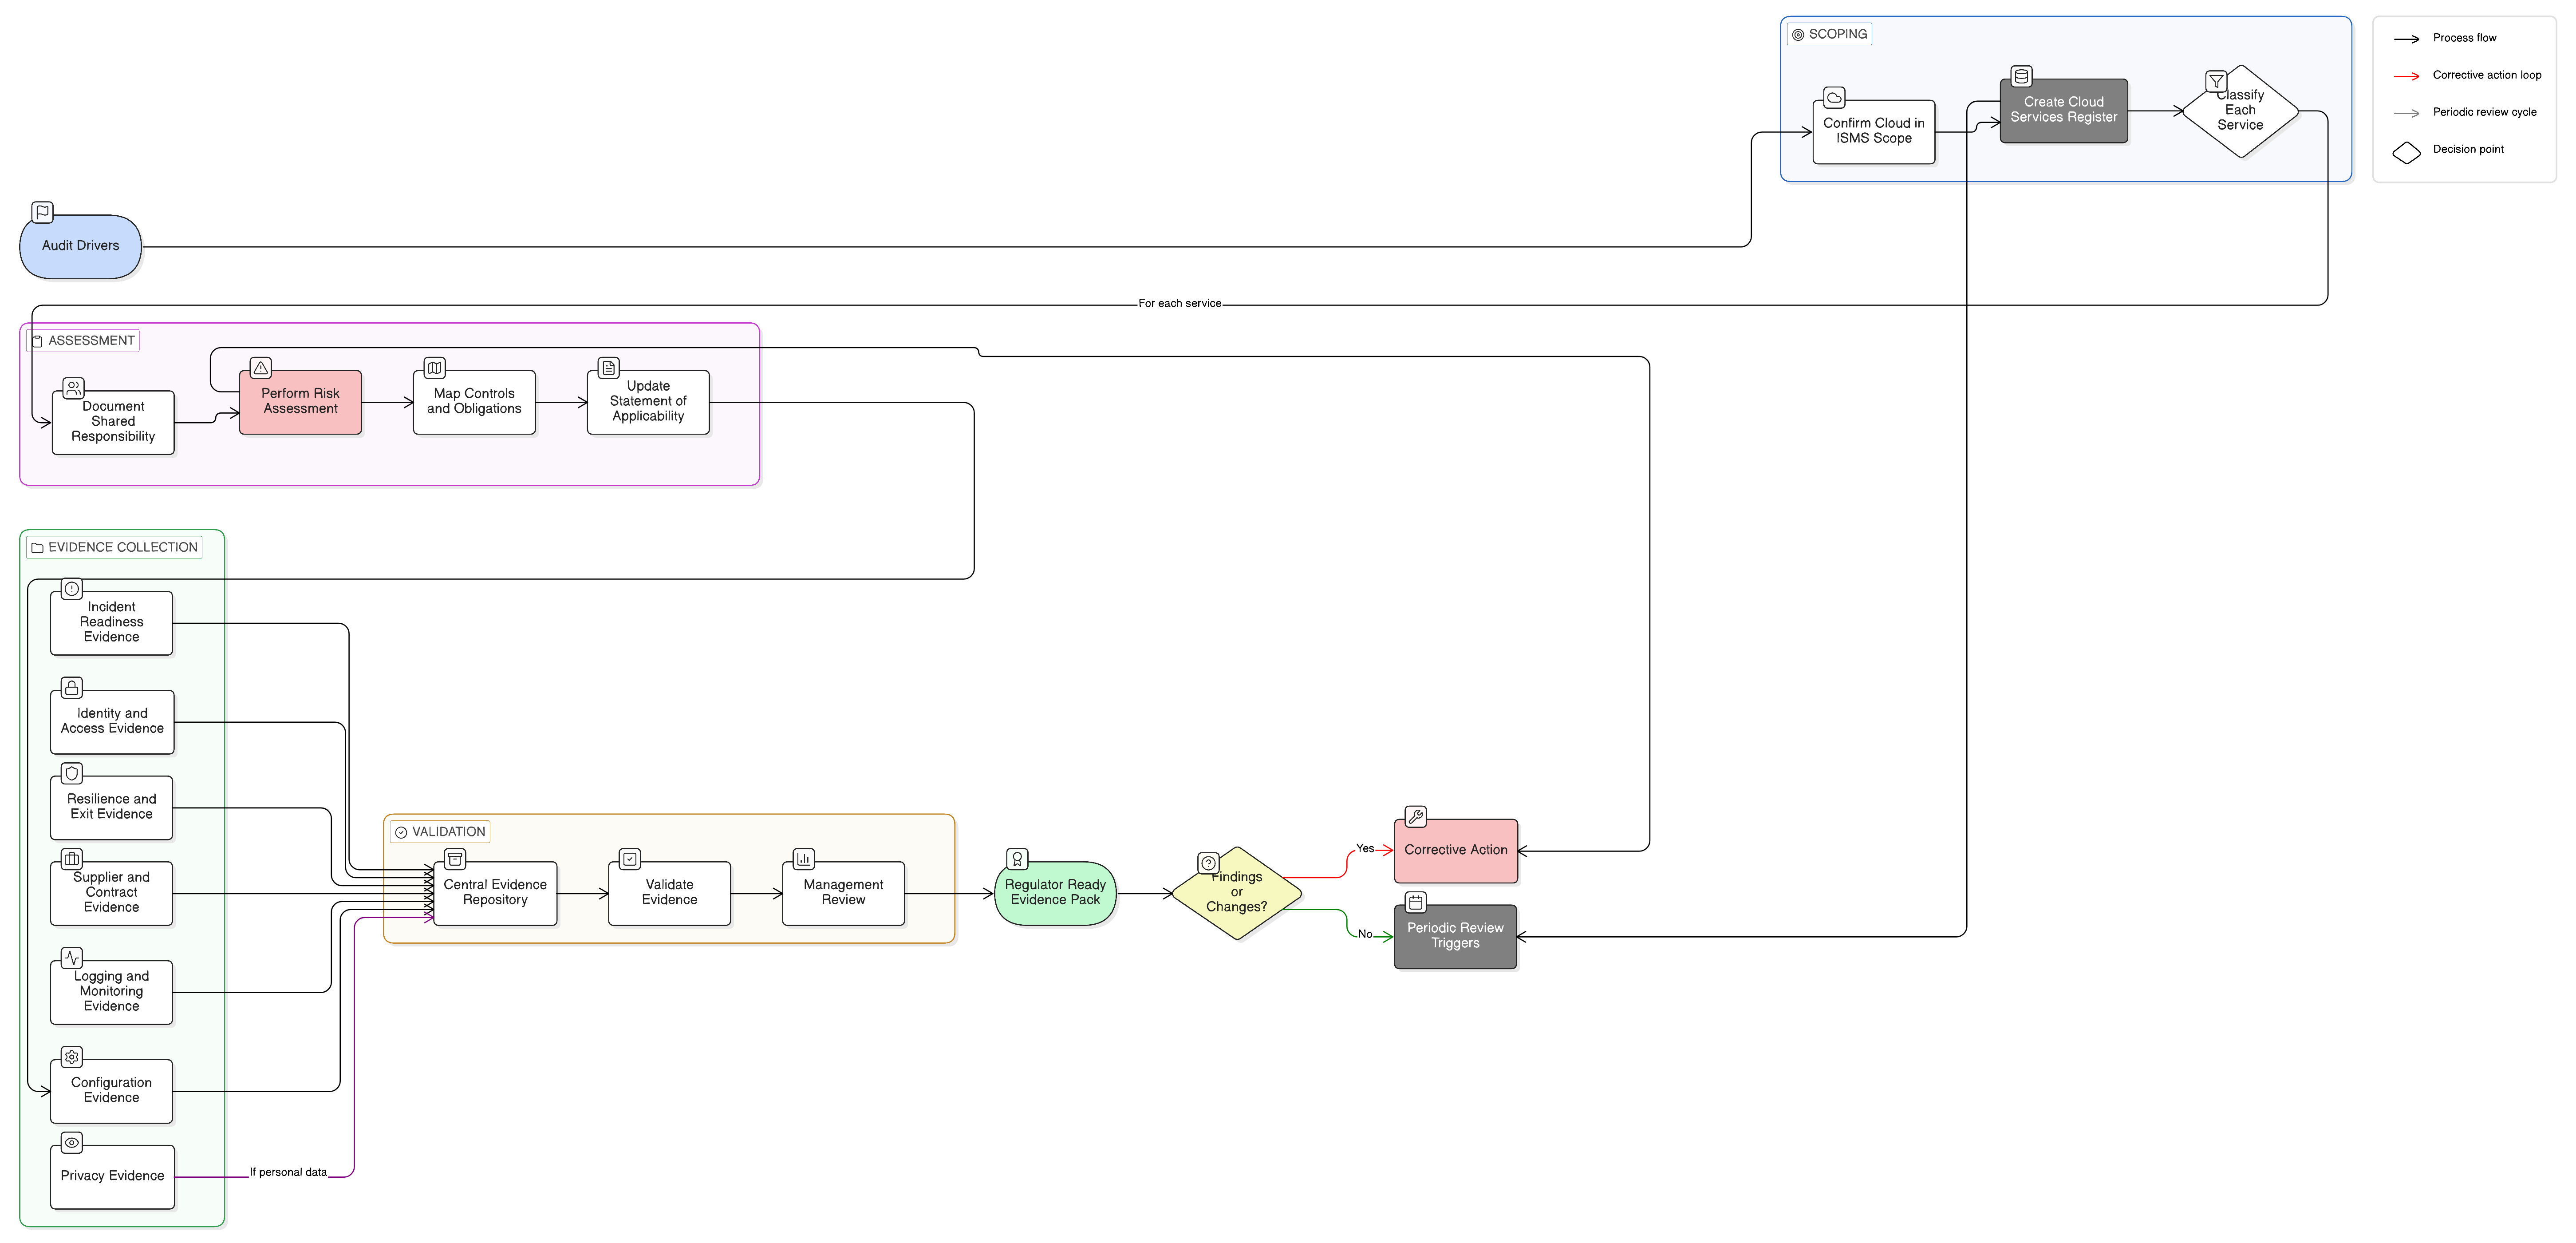
Cloud audit evidence fails when organizations cannot prove shared responsibility, SaaS configuration, IaaS controls, supplier oversight, logging, resilience and incident readiness. This guide shows how Clarysec structures regulator-ready proof across ISO 27001:2022, NIS2, DORA and GDPR.
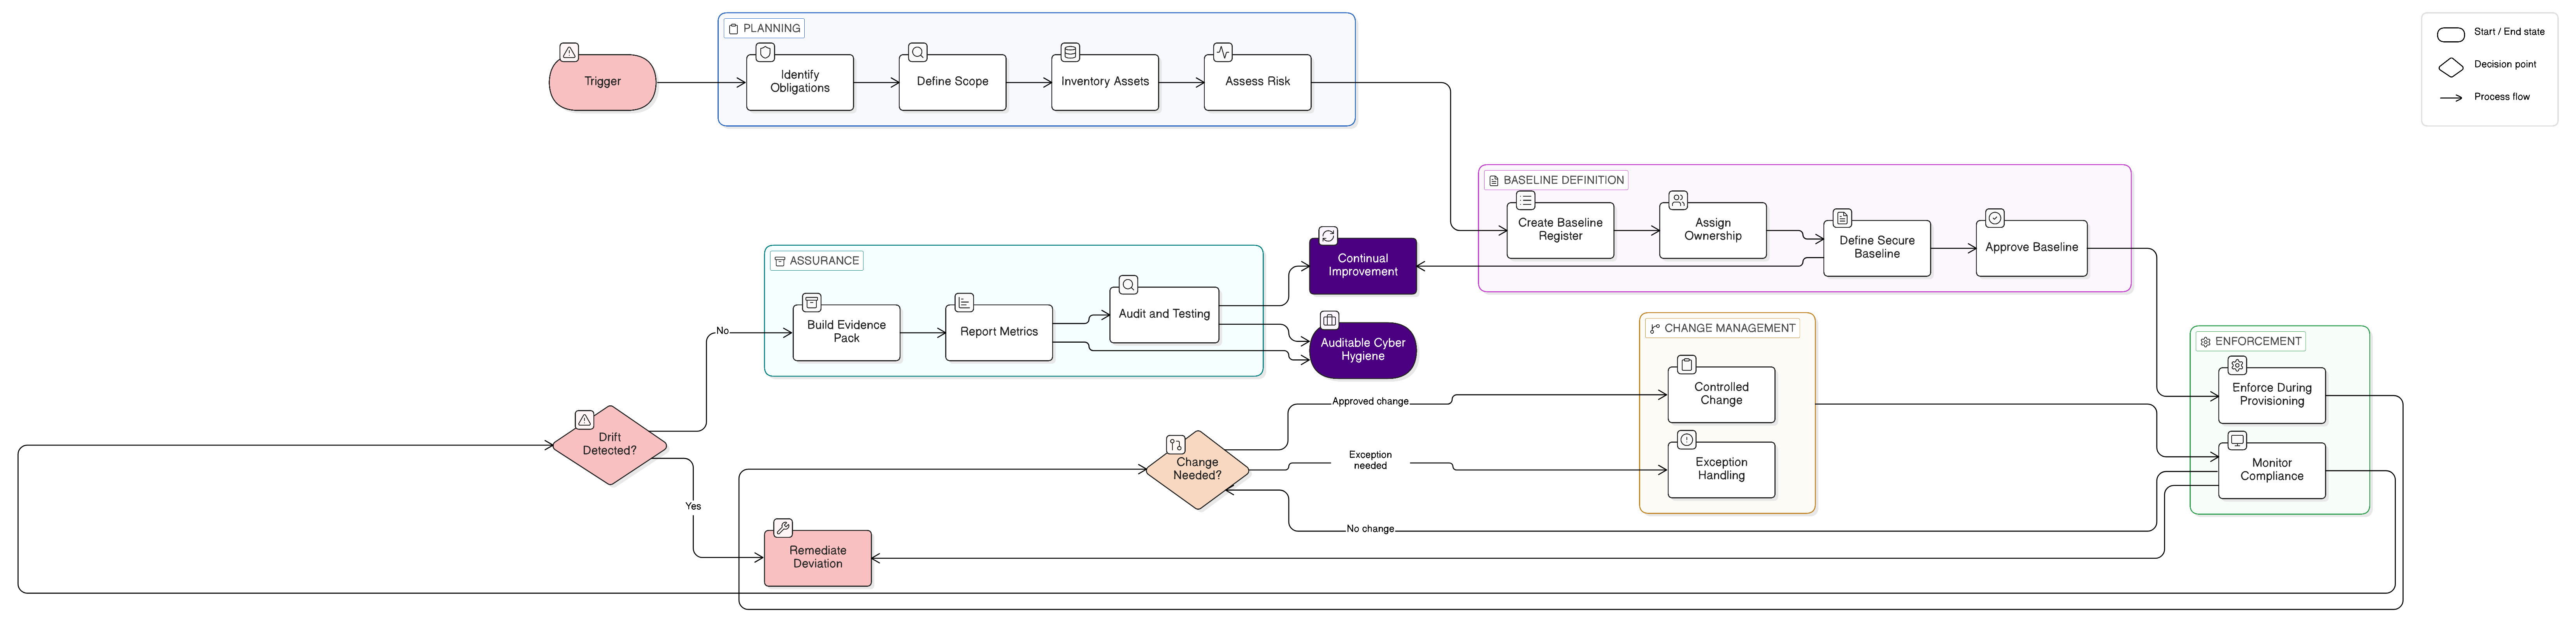
Secure configuration baselines are now a core proof point for ISO/IEC 27001:2022, NIS2, DORA, GDPR and customer security reviews. This flagship guide shows how to define, enforce, monitor and evidence secure baselines using Clarysec policies, Zenith Blueprint and Zenith Controls.
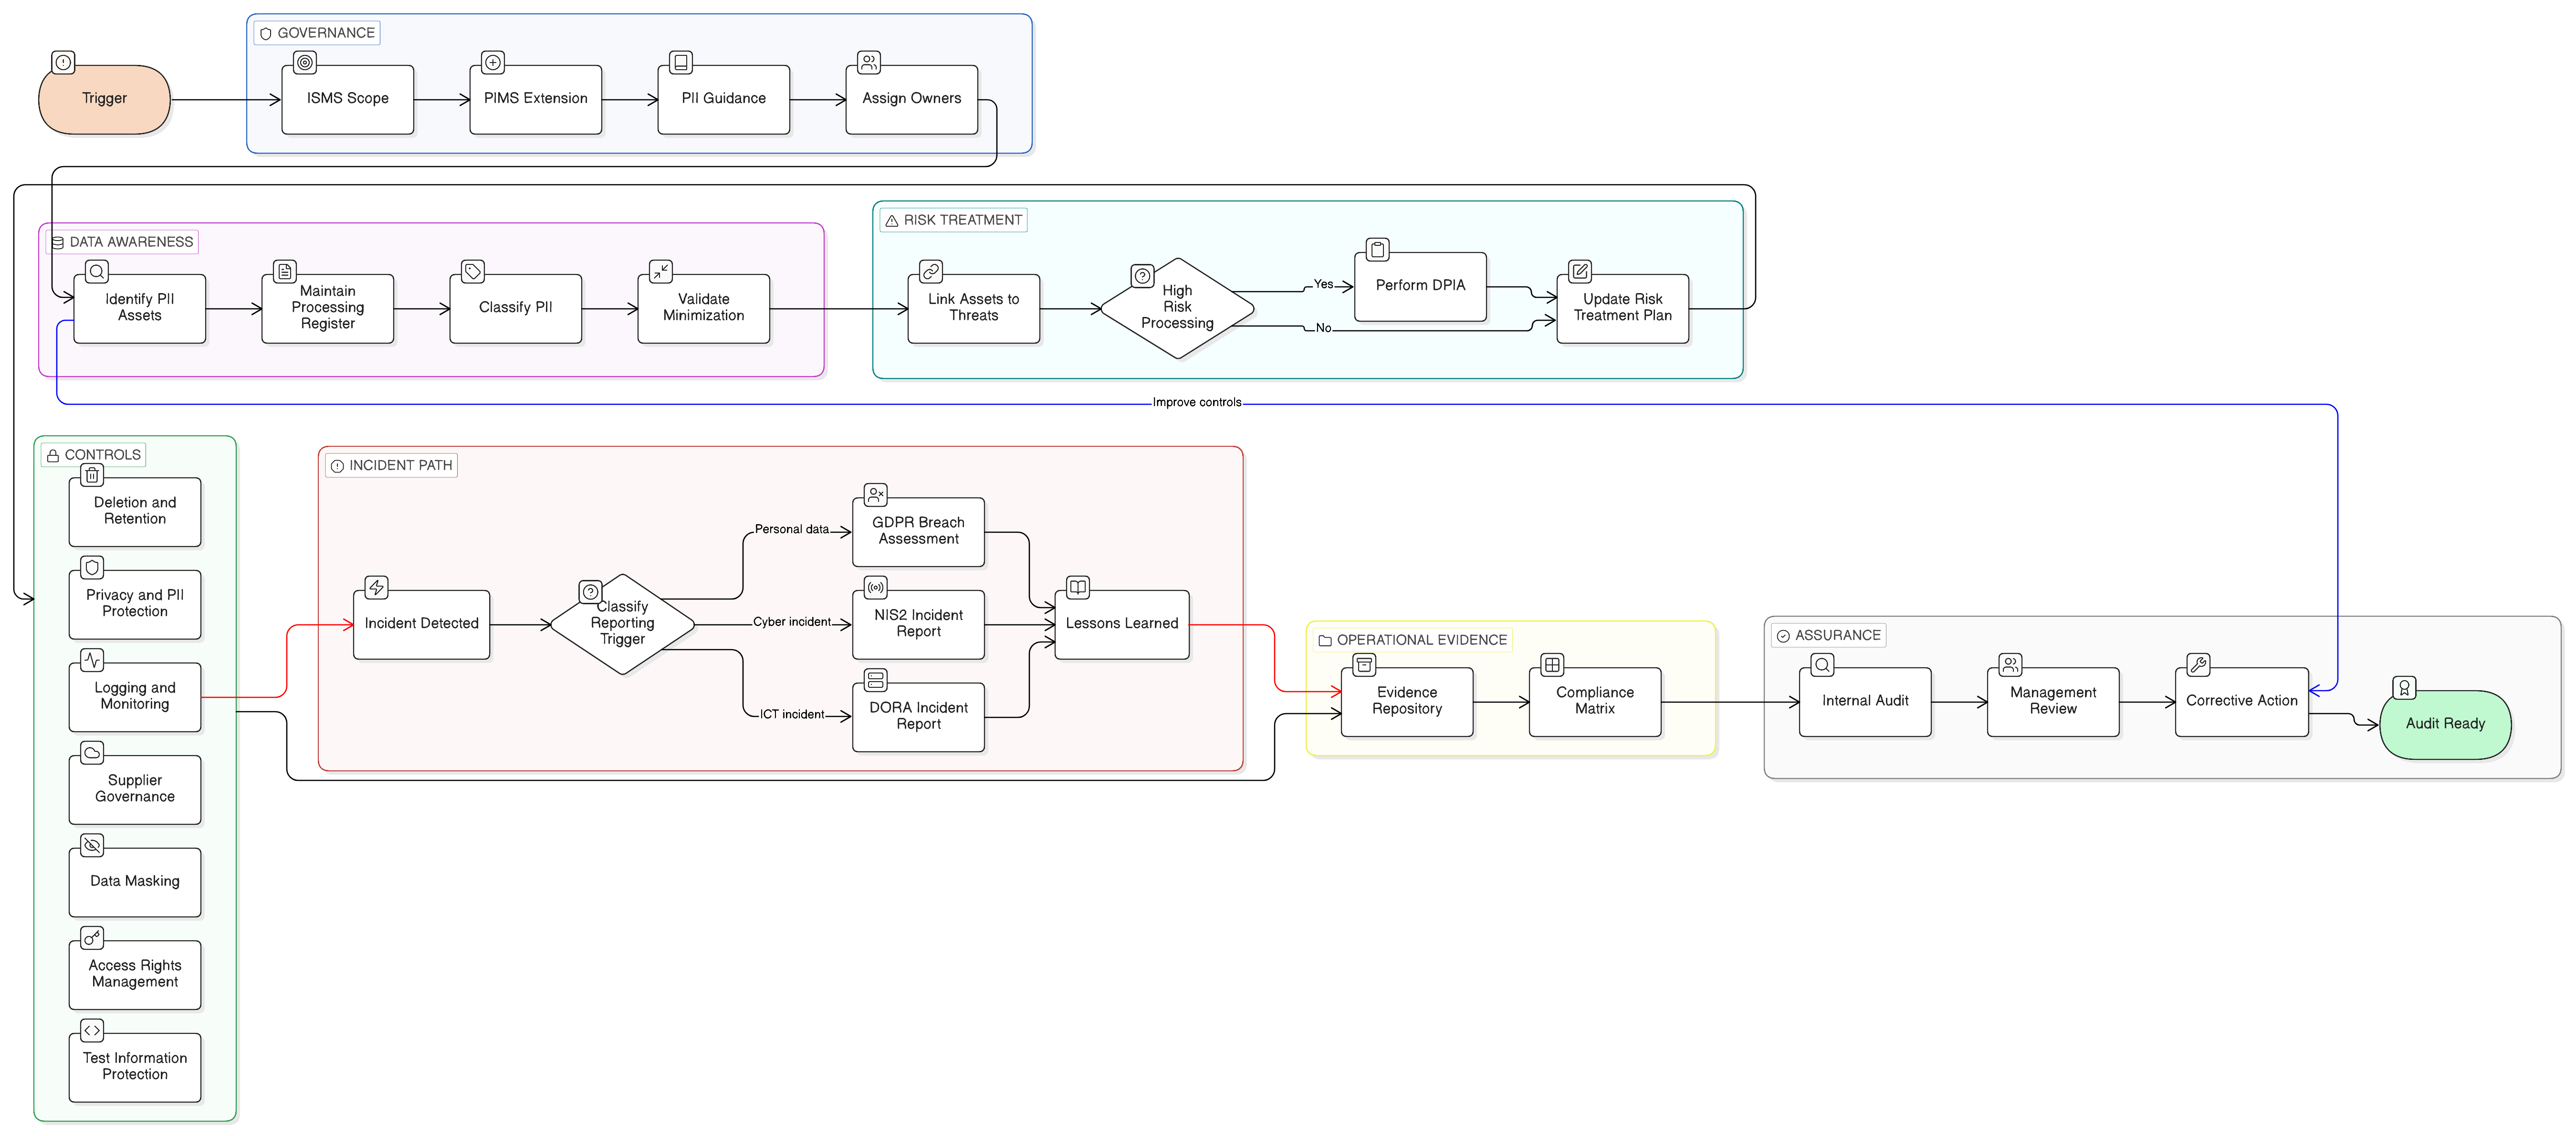
Learn how to build audit-ready PII protection controls by extending ISO/IEC 27001:2022 with ISO/IEC 27701:2025 and ISO/IEC 29151:2022, mapped to GDPR, NIS2, DORA, NIST-style assurance, and COBIT 2019 governance expectations.
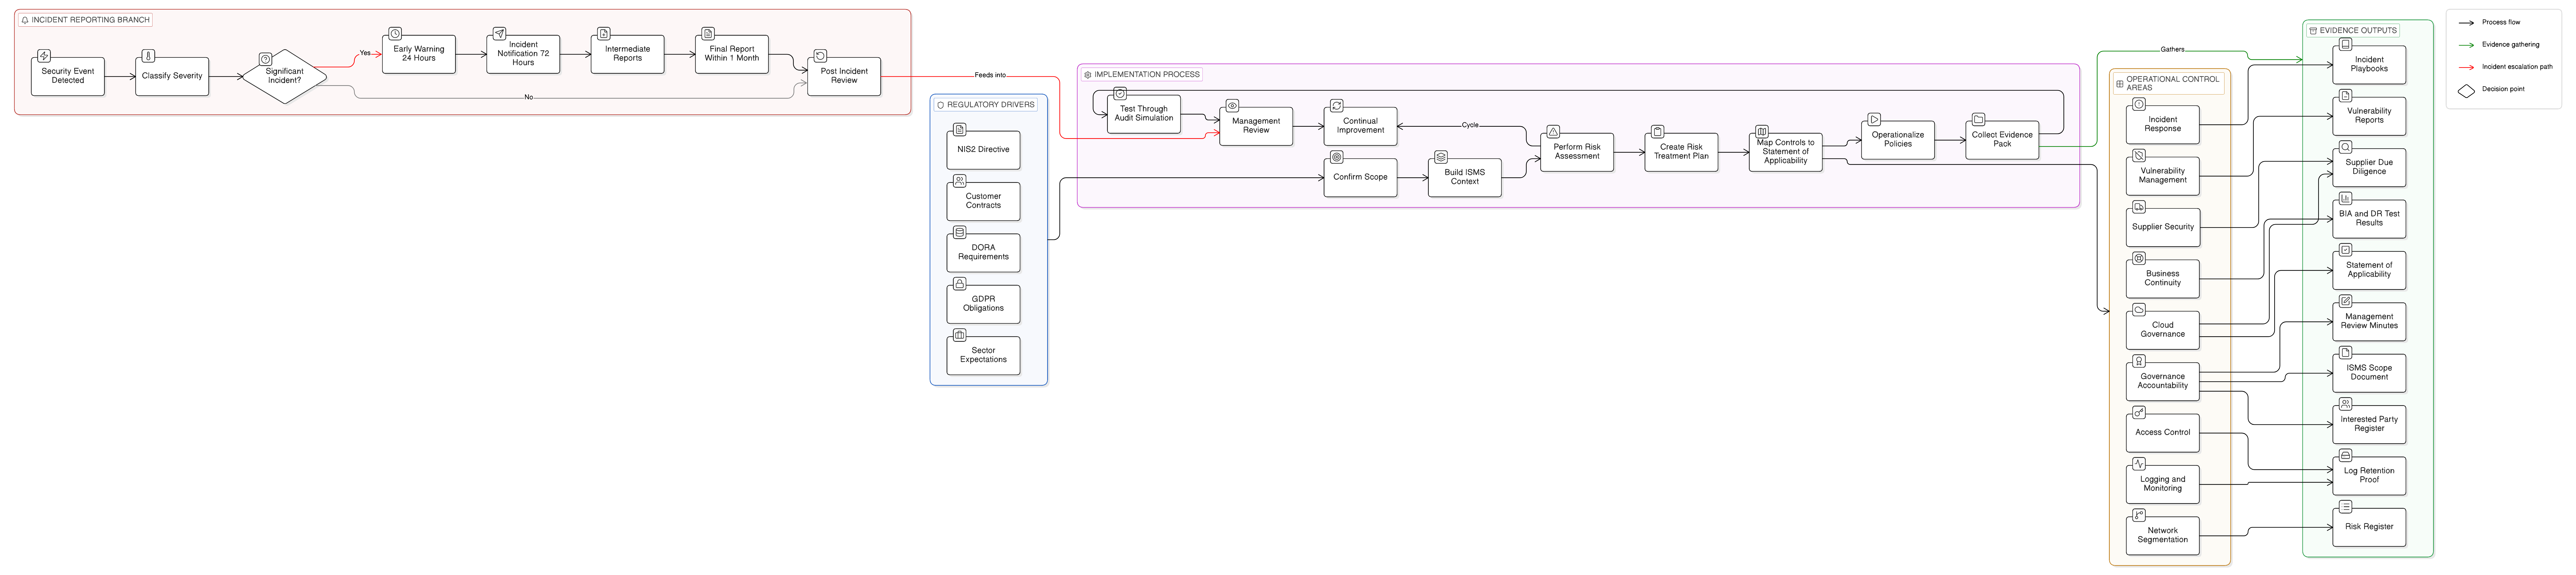
A unified NIS2 Implementing Regulation 2024/2690 to ISO/IEC 27001:2022 control mapping for cloud, MSP, MSSP and data centre providers. Includes Clarysec policy clauses, audit evidence, DORA and GDPR alignment, and a practical implementation roadmap.
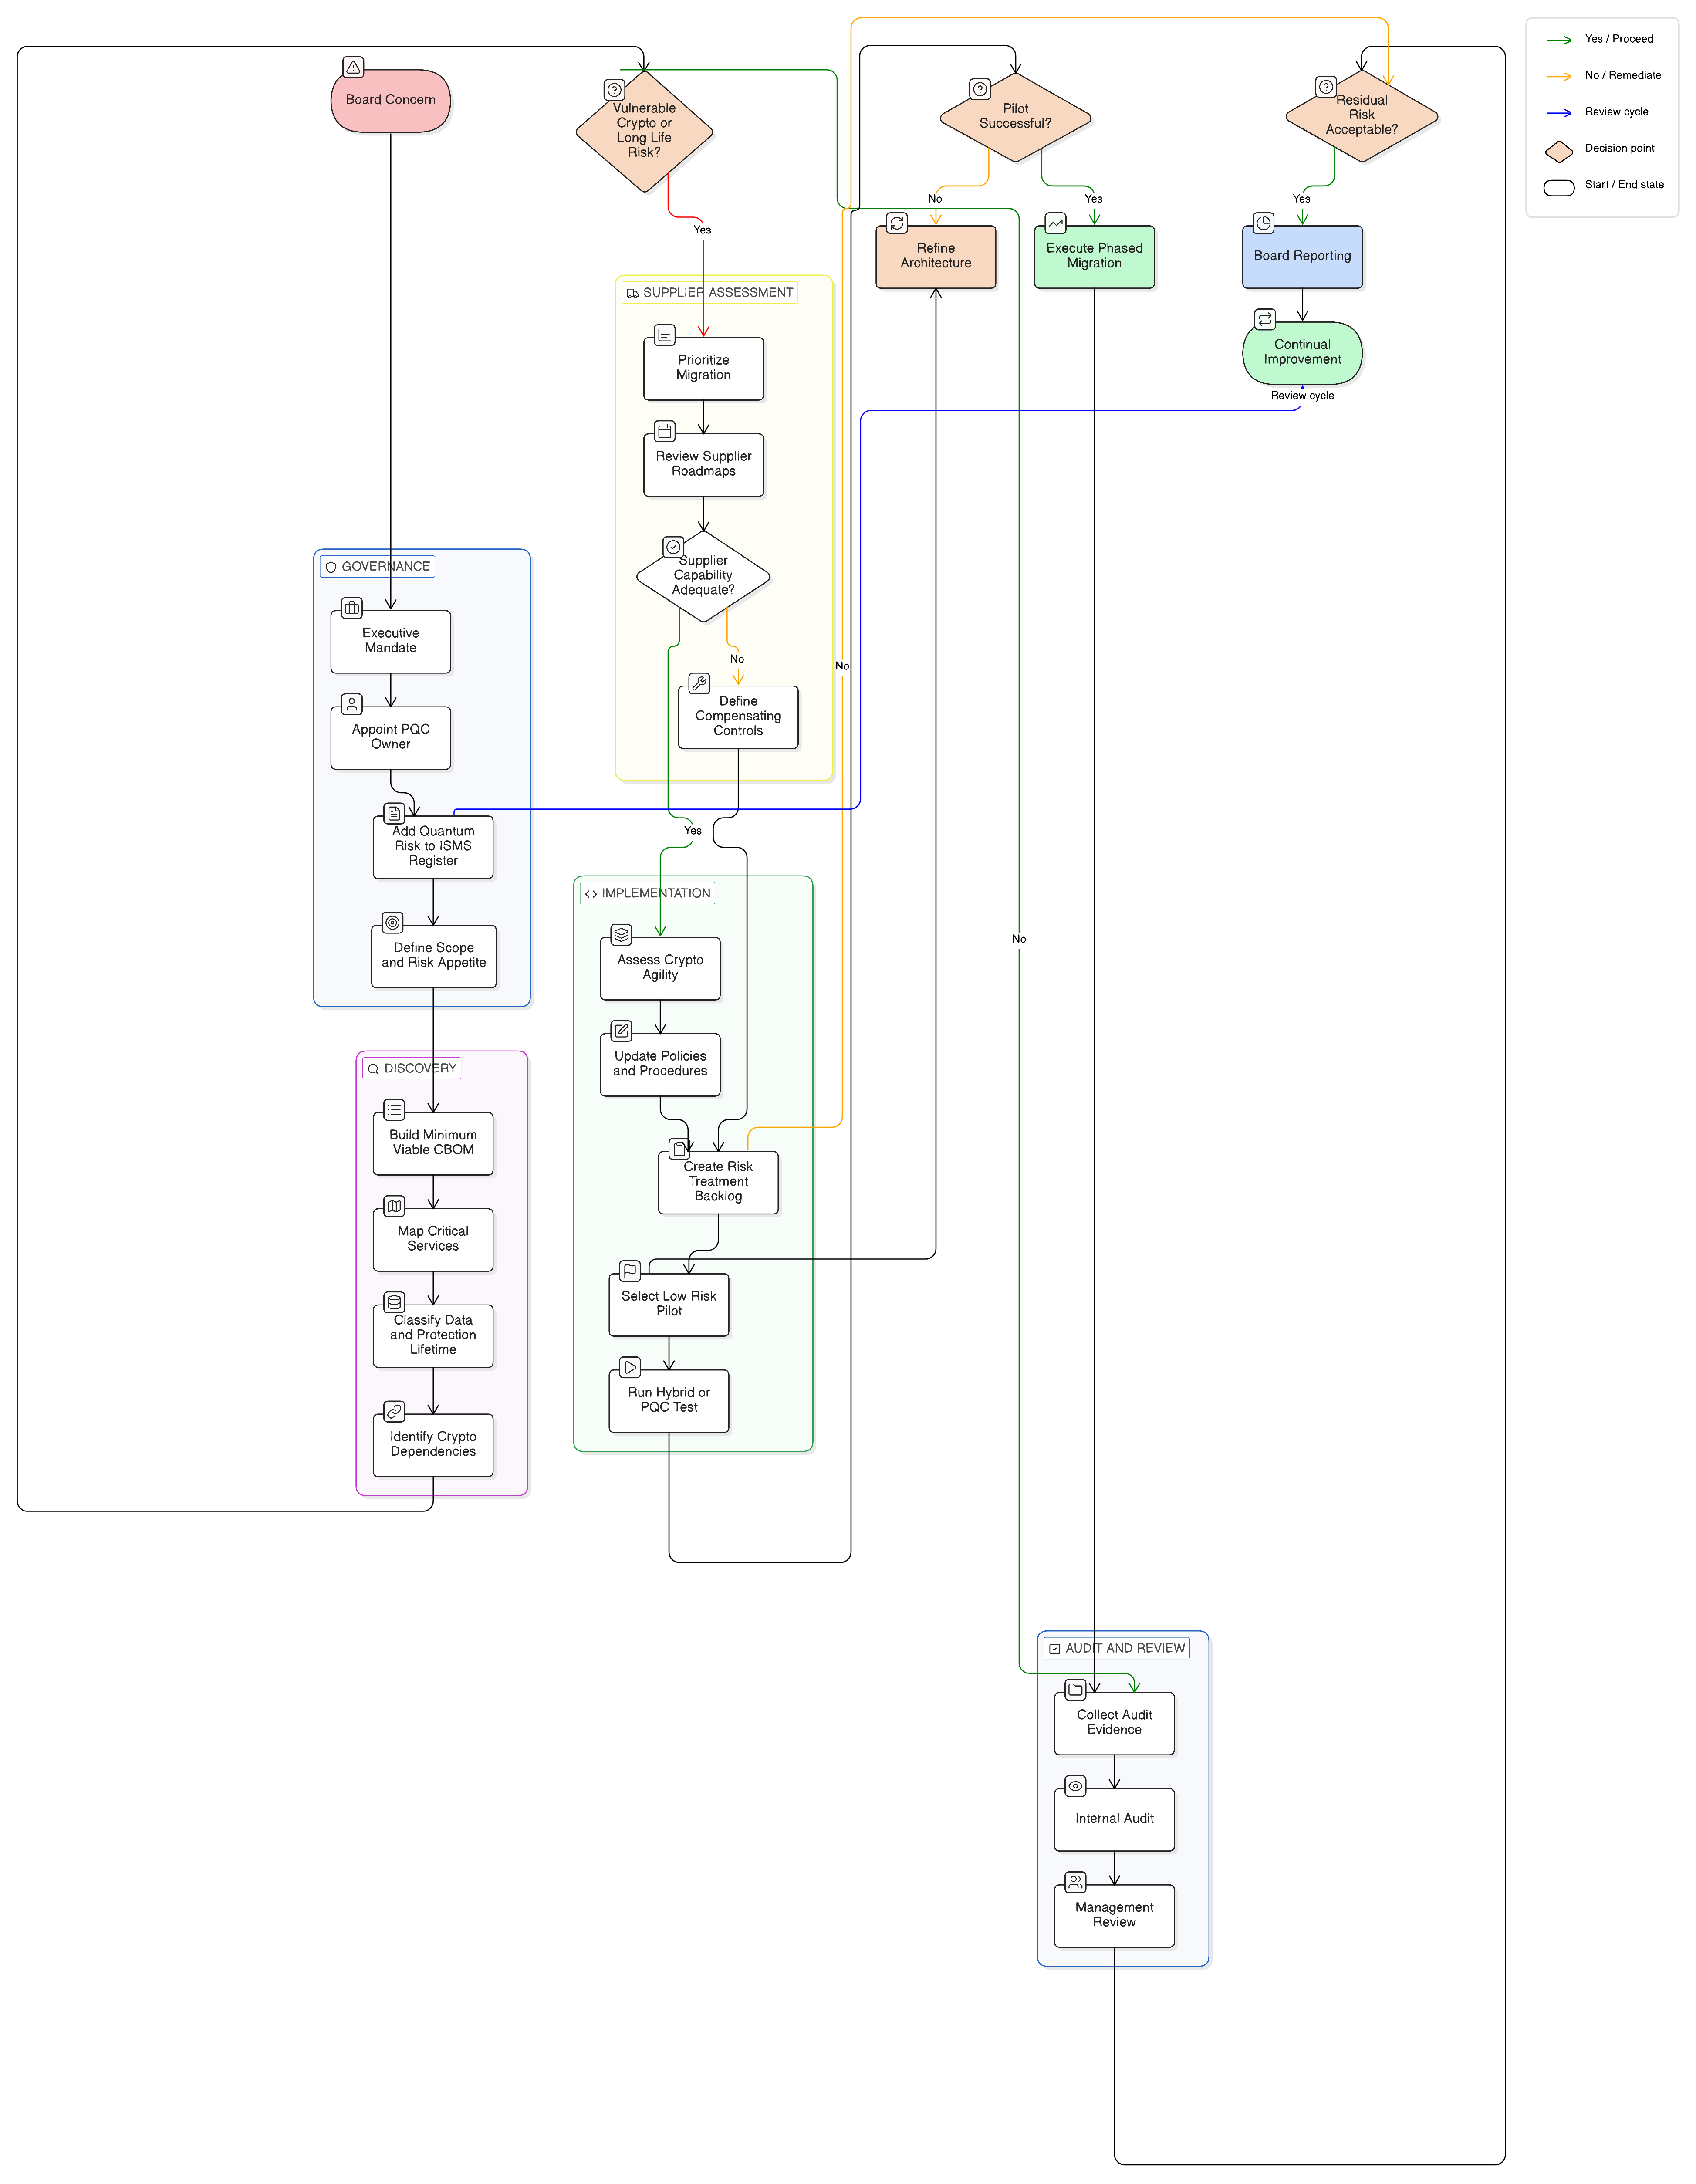
A practical CISO guide for building a quantum-ready cryptography migration plan using ISO/IEC 27001:2022, ISO/IEC 27002:2022, NIST PQC standards, and Clarysec’s audit-ready toolkits.