#Cloud Security
Articles tagged with "Cloud Security"
26 articles
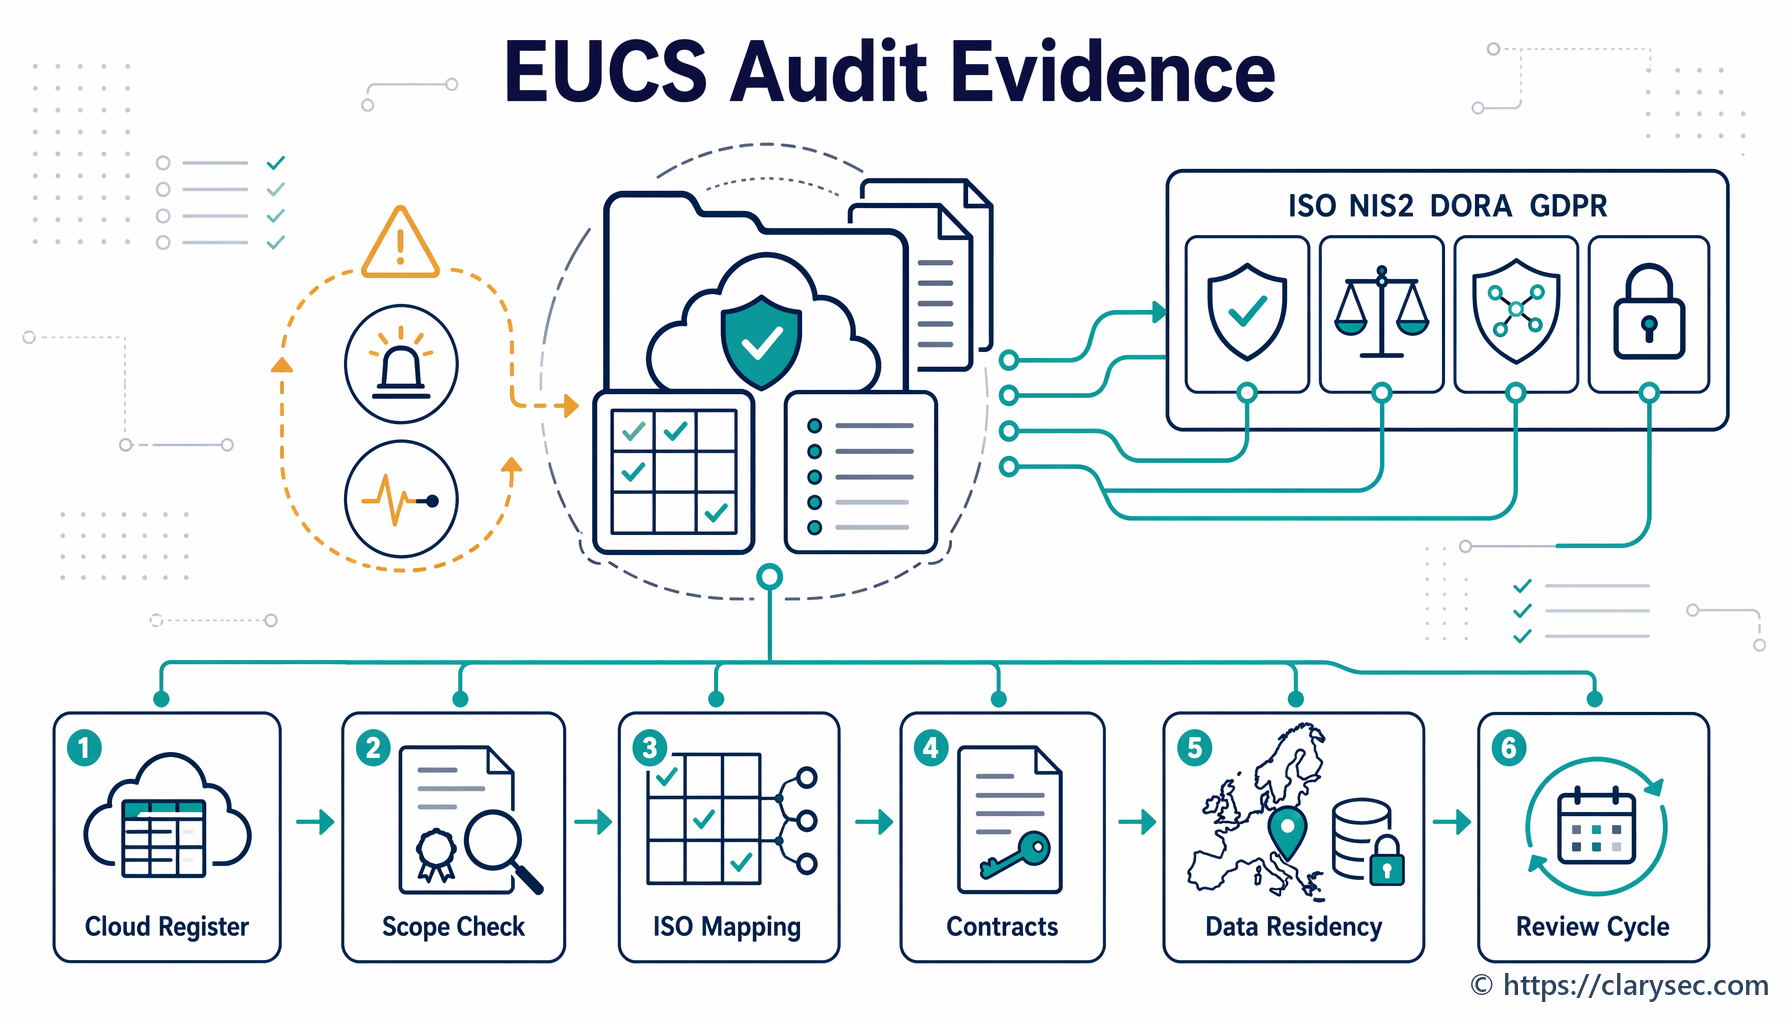
EUCS cloud certification can strengthen cloud provider assurance in 2026, but it must be mapped into your ISO 27001 ISMS, supplier risk process, contracts, incident playbooks and GDPR accountability evidence.
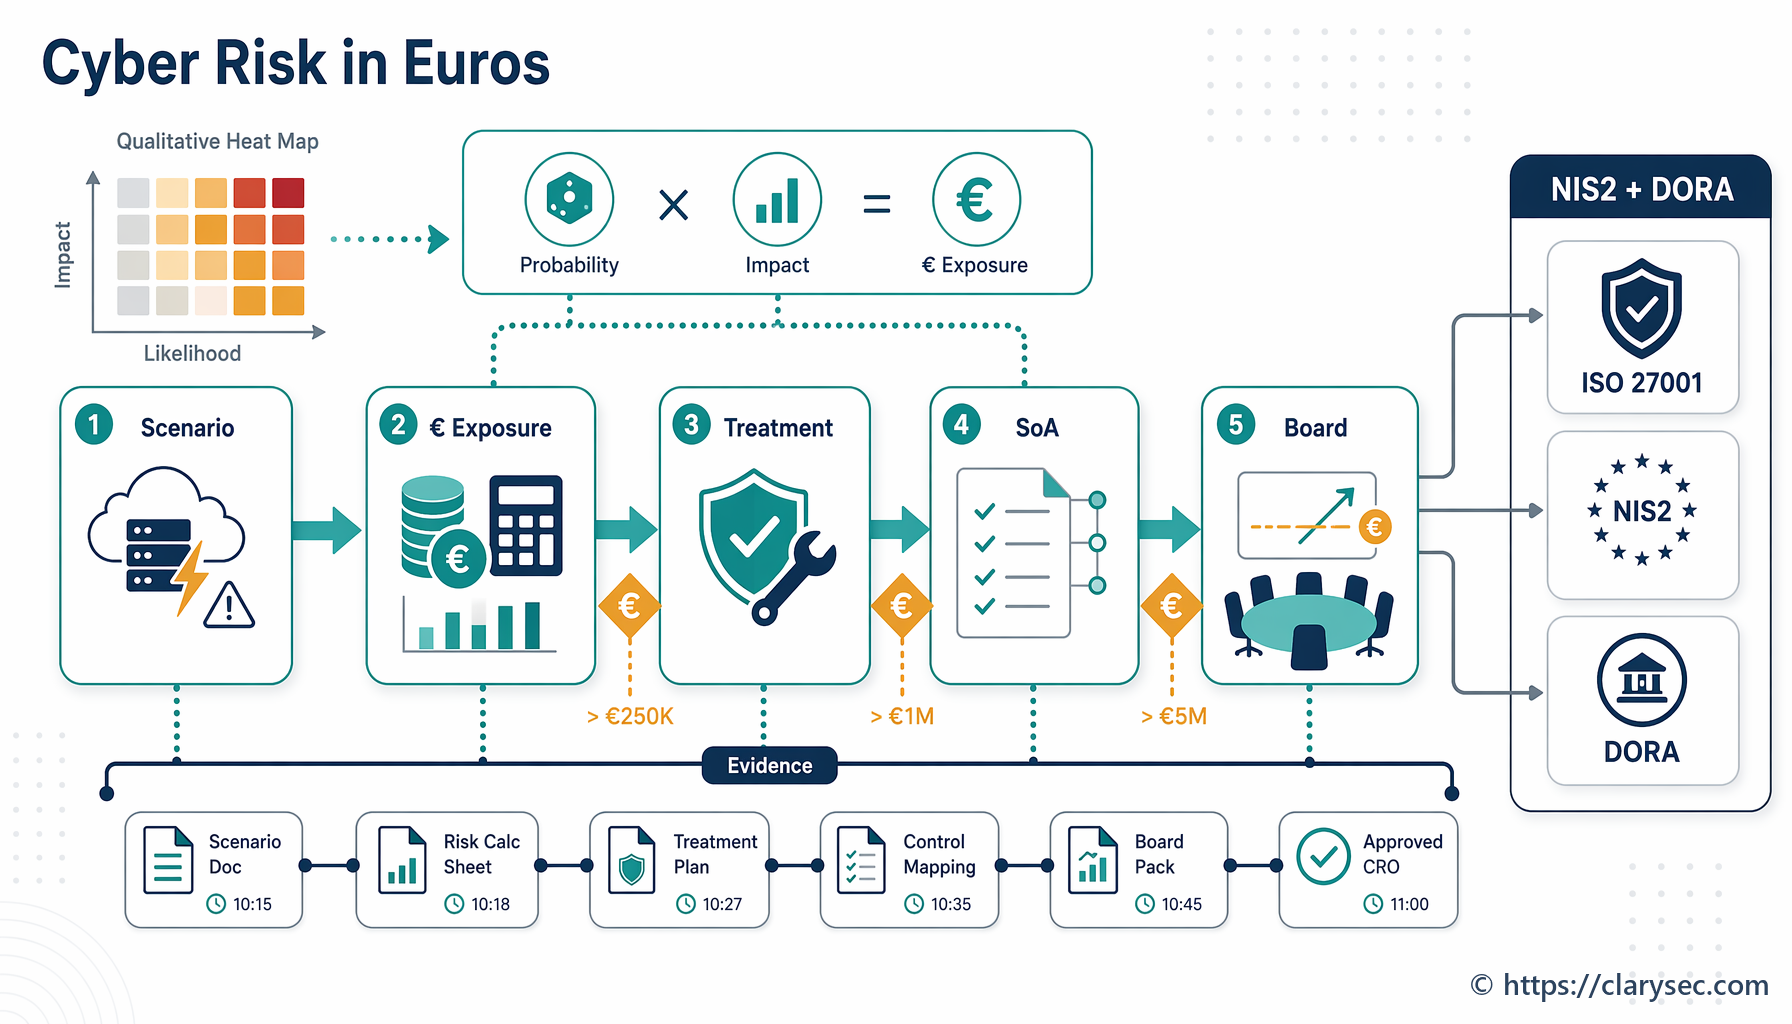
A practical guide for CISOs, compliance managers and boards on translating qualitative cyber risks into financial exposure, ISO 27001 evidence, NIS2 oversight and DORA ICT resilience decisions.
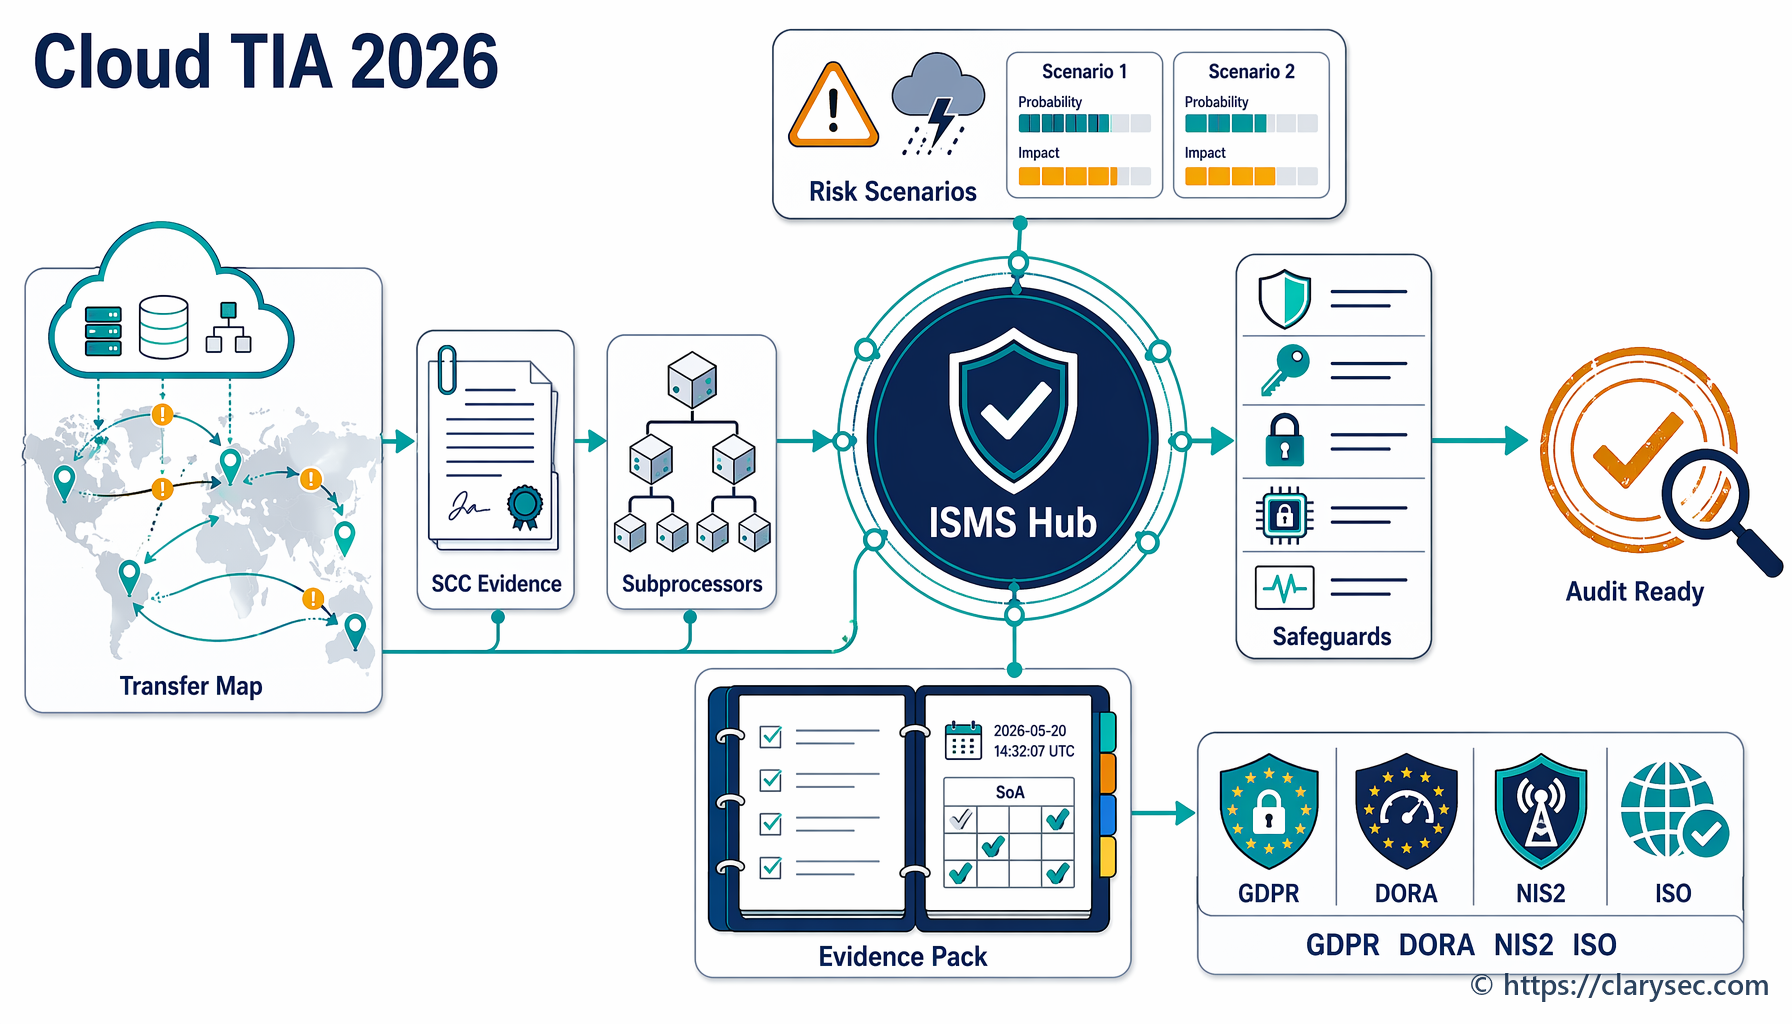
A practical guide to building audit-ready Transfer Impact Assessments for cloud services, SCCs, subprocessors, supplementary measures, ISO/IEC 27001:2022, NIS2 and DORA evidence.
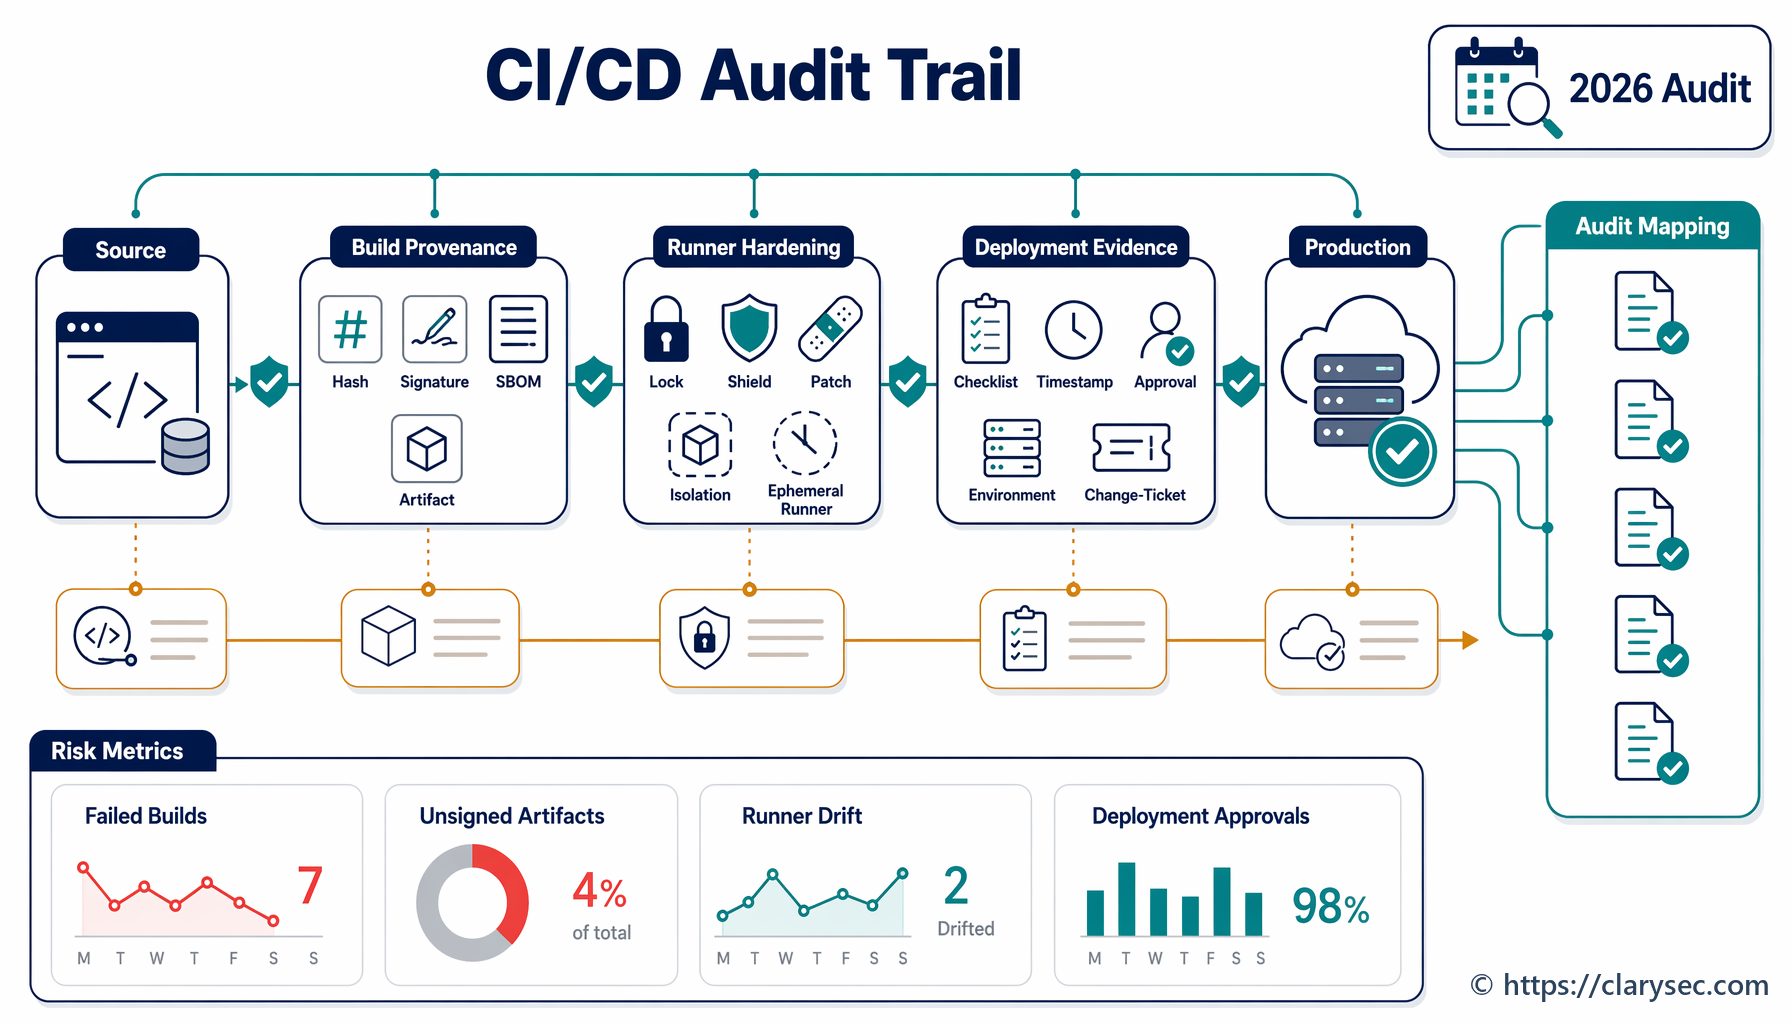
A practical CISO guide to governing CI/CD pipelines as auditable software supply chain systems, with build provenance, hardened runners, signed artifacts, deployment evidence and Clarysec policy mappings.
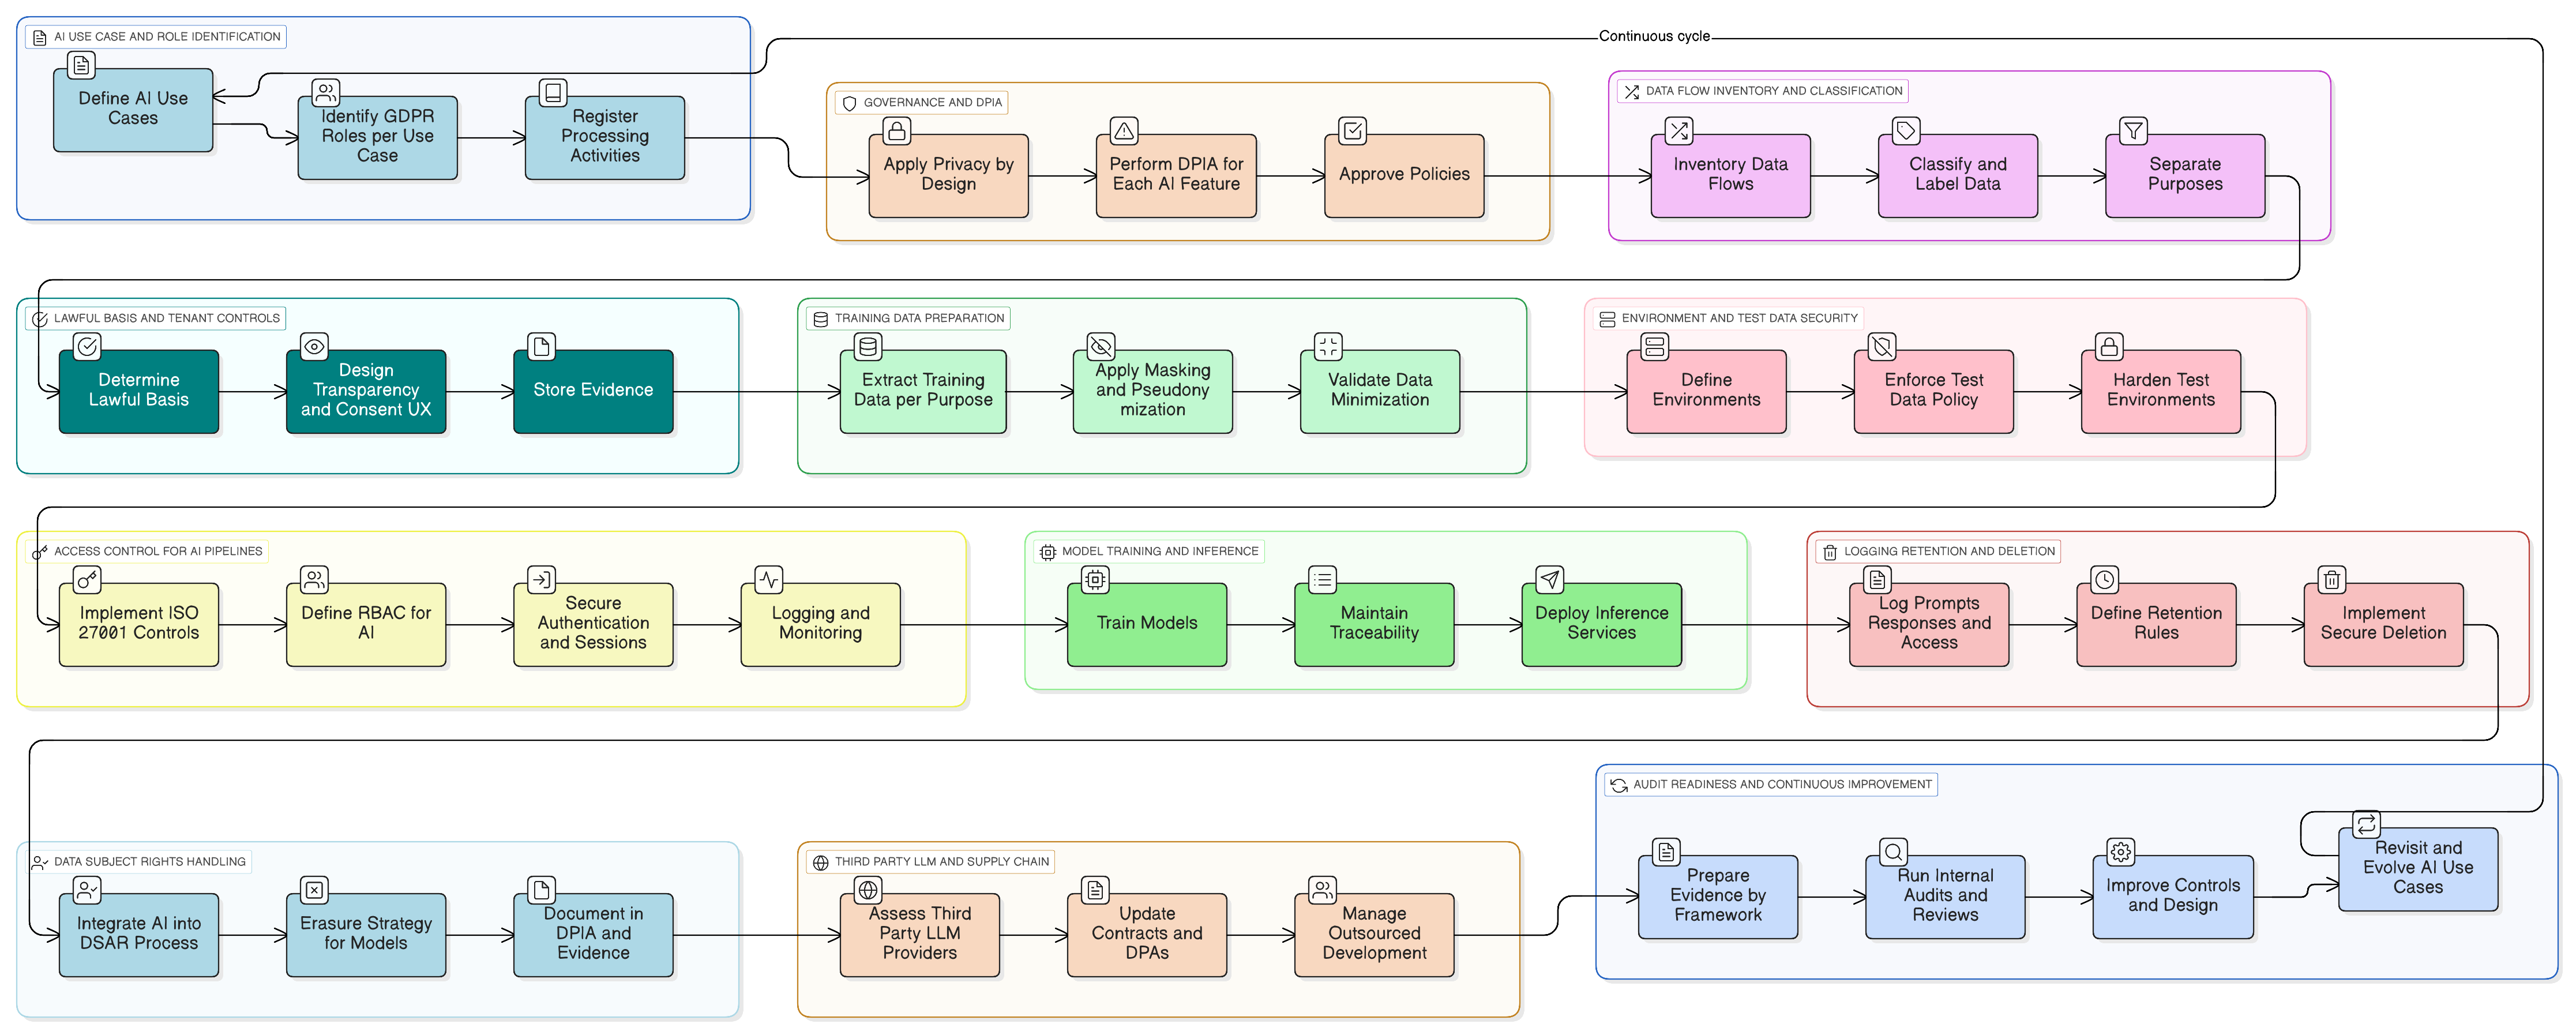
This article provides a practical playbook for CISOs to navigate the complex intersection of GDPR and AI. We offer a scenario-driven walkthrough for making SaaS products with LLMs compliant, focusing on training data, access controls, data subject rights, and multi-framework audit readiness.
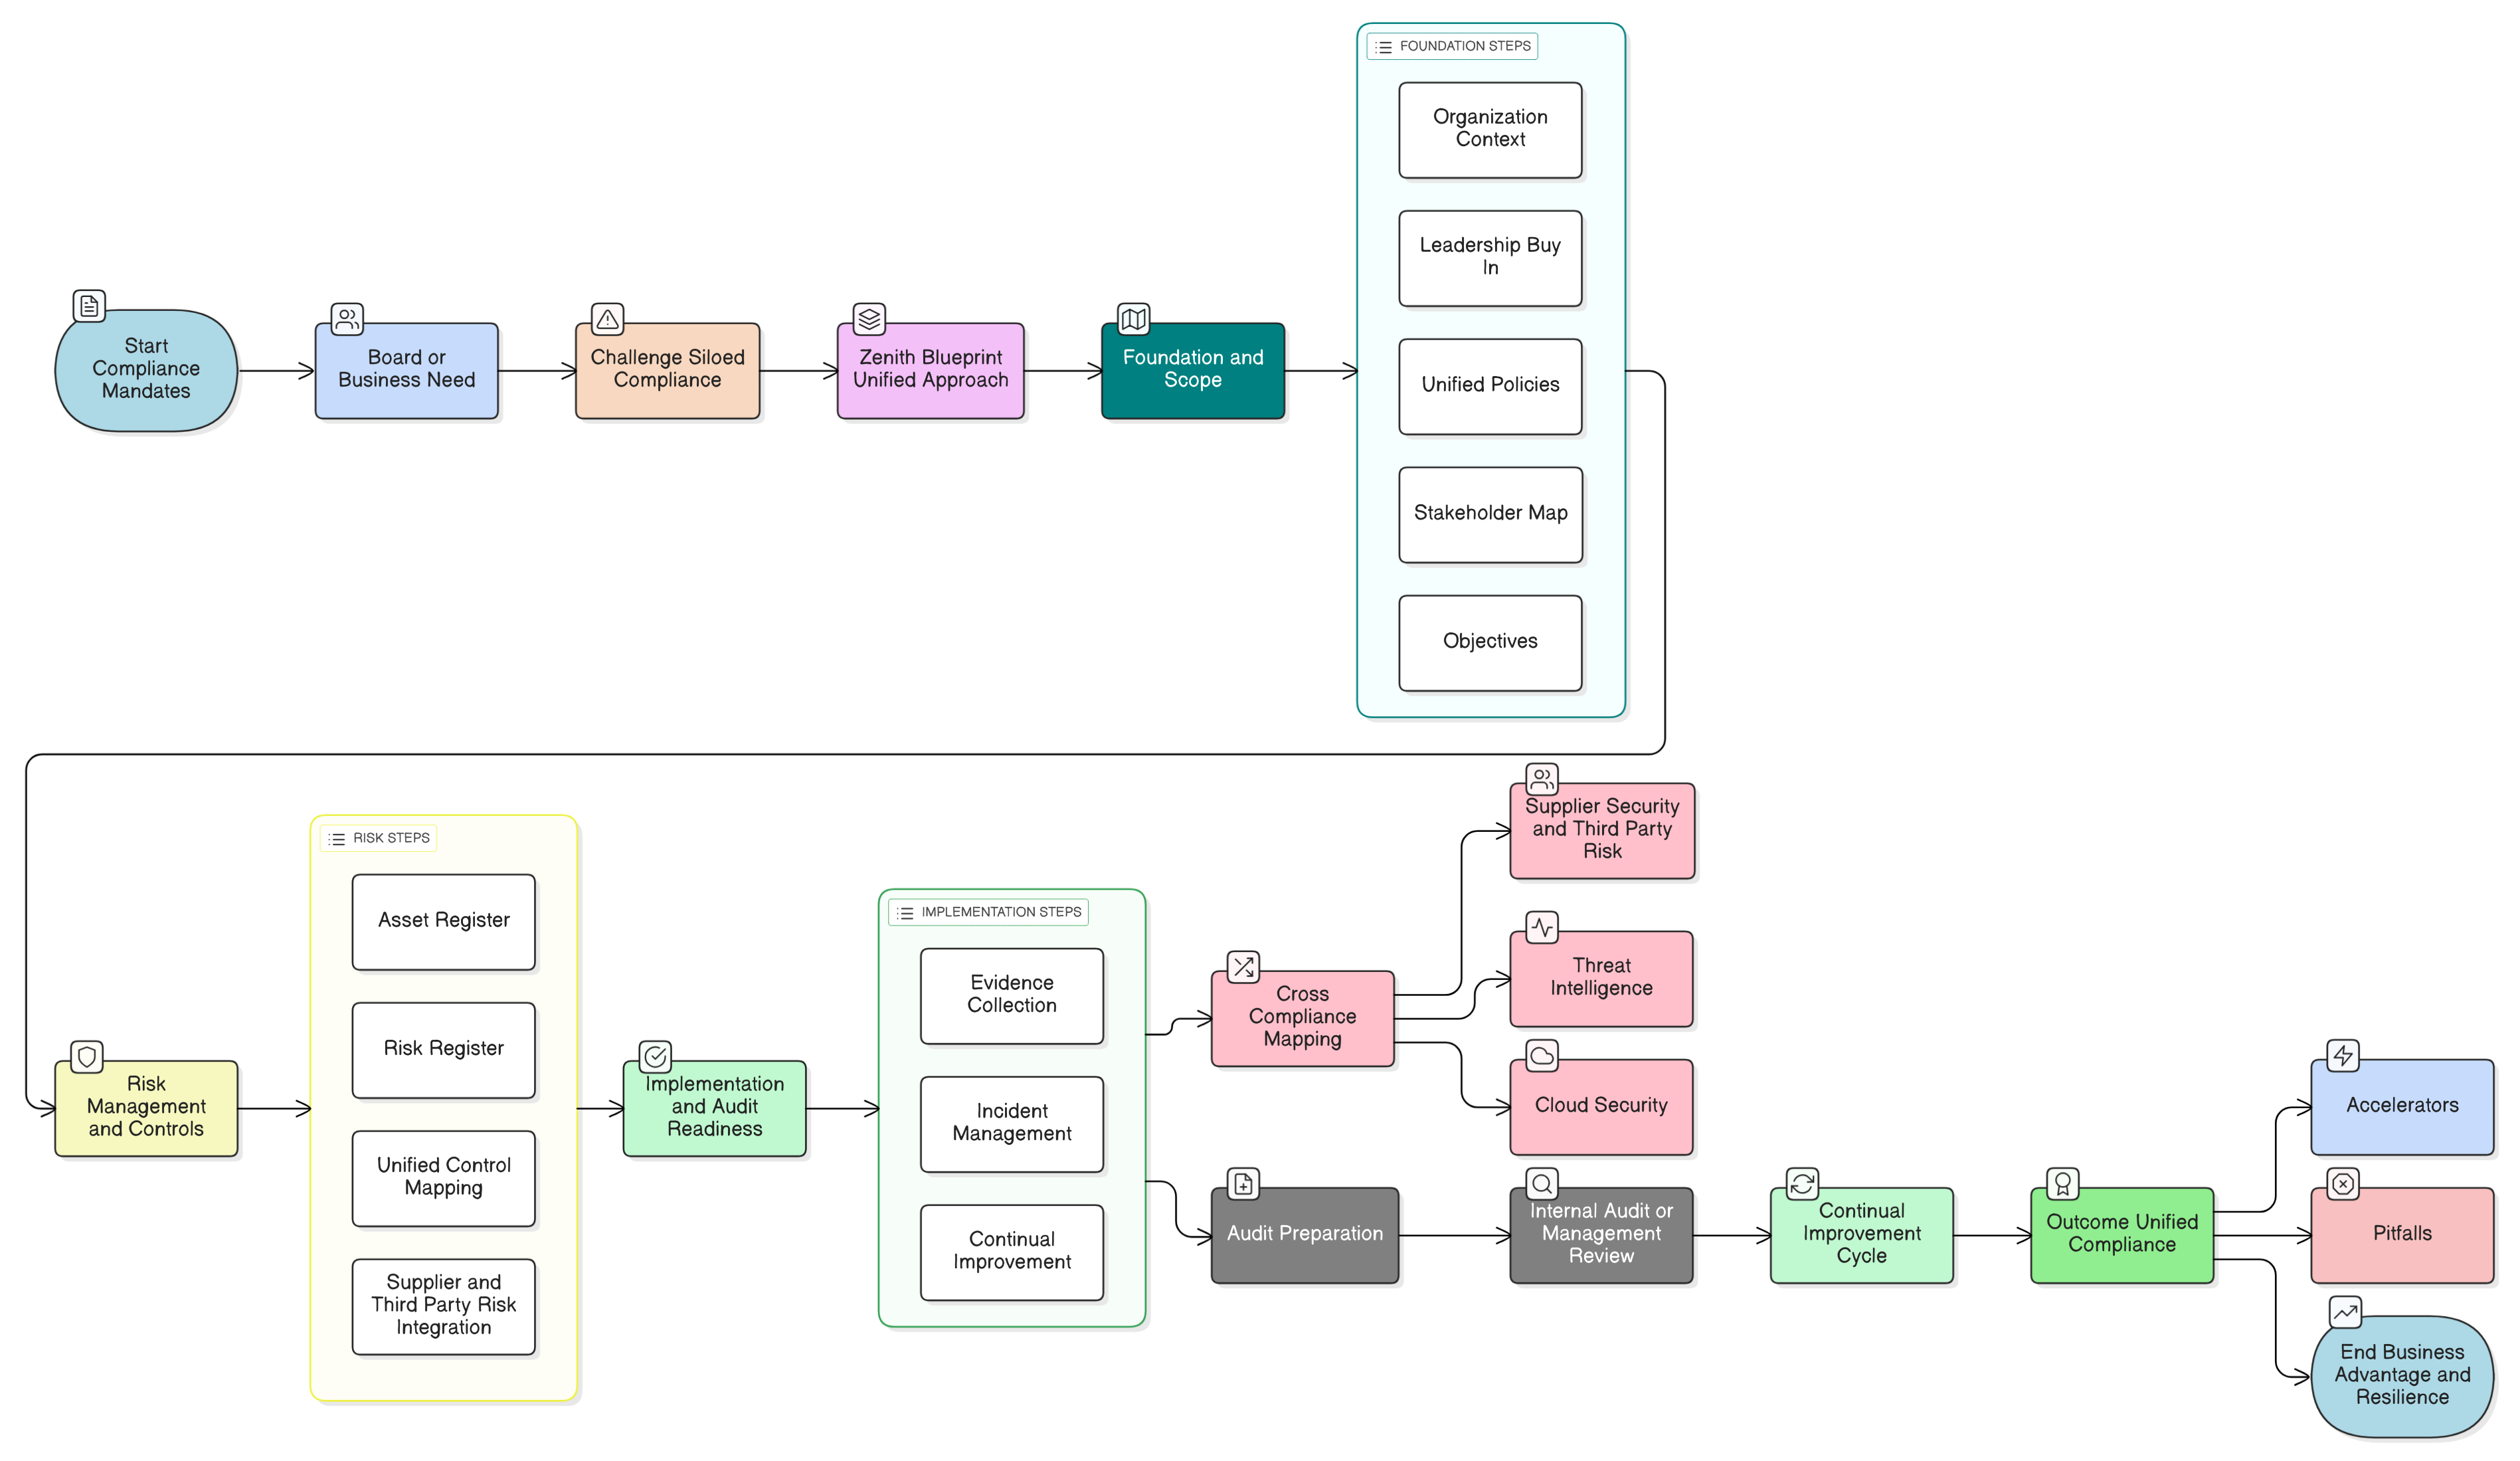
Clarysec’s Zenith Blueprint delivers the fastest and most reliable unified compliance for ISO 27001:2022, NIS2, and DORA. Discover actionable steps, control mappings, and real-world scenarios for CISOs and business leaders to achieve true audit and operational readiness.
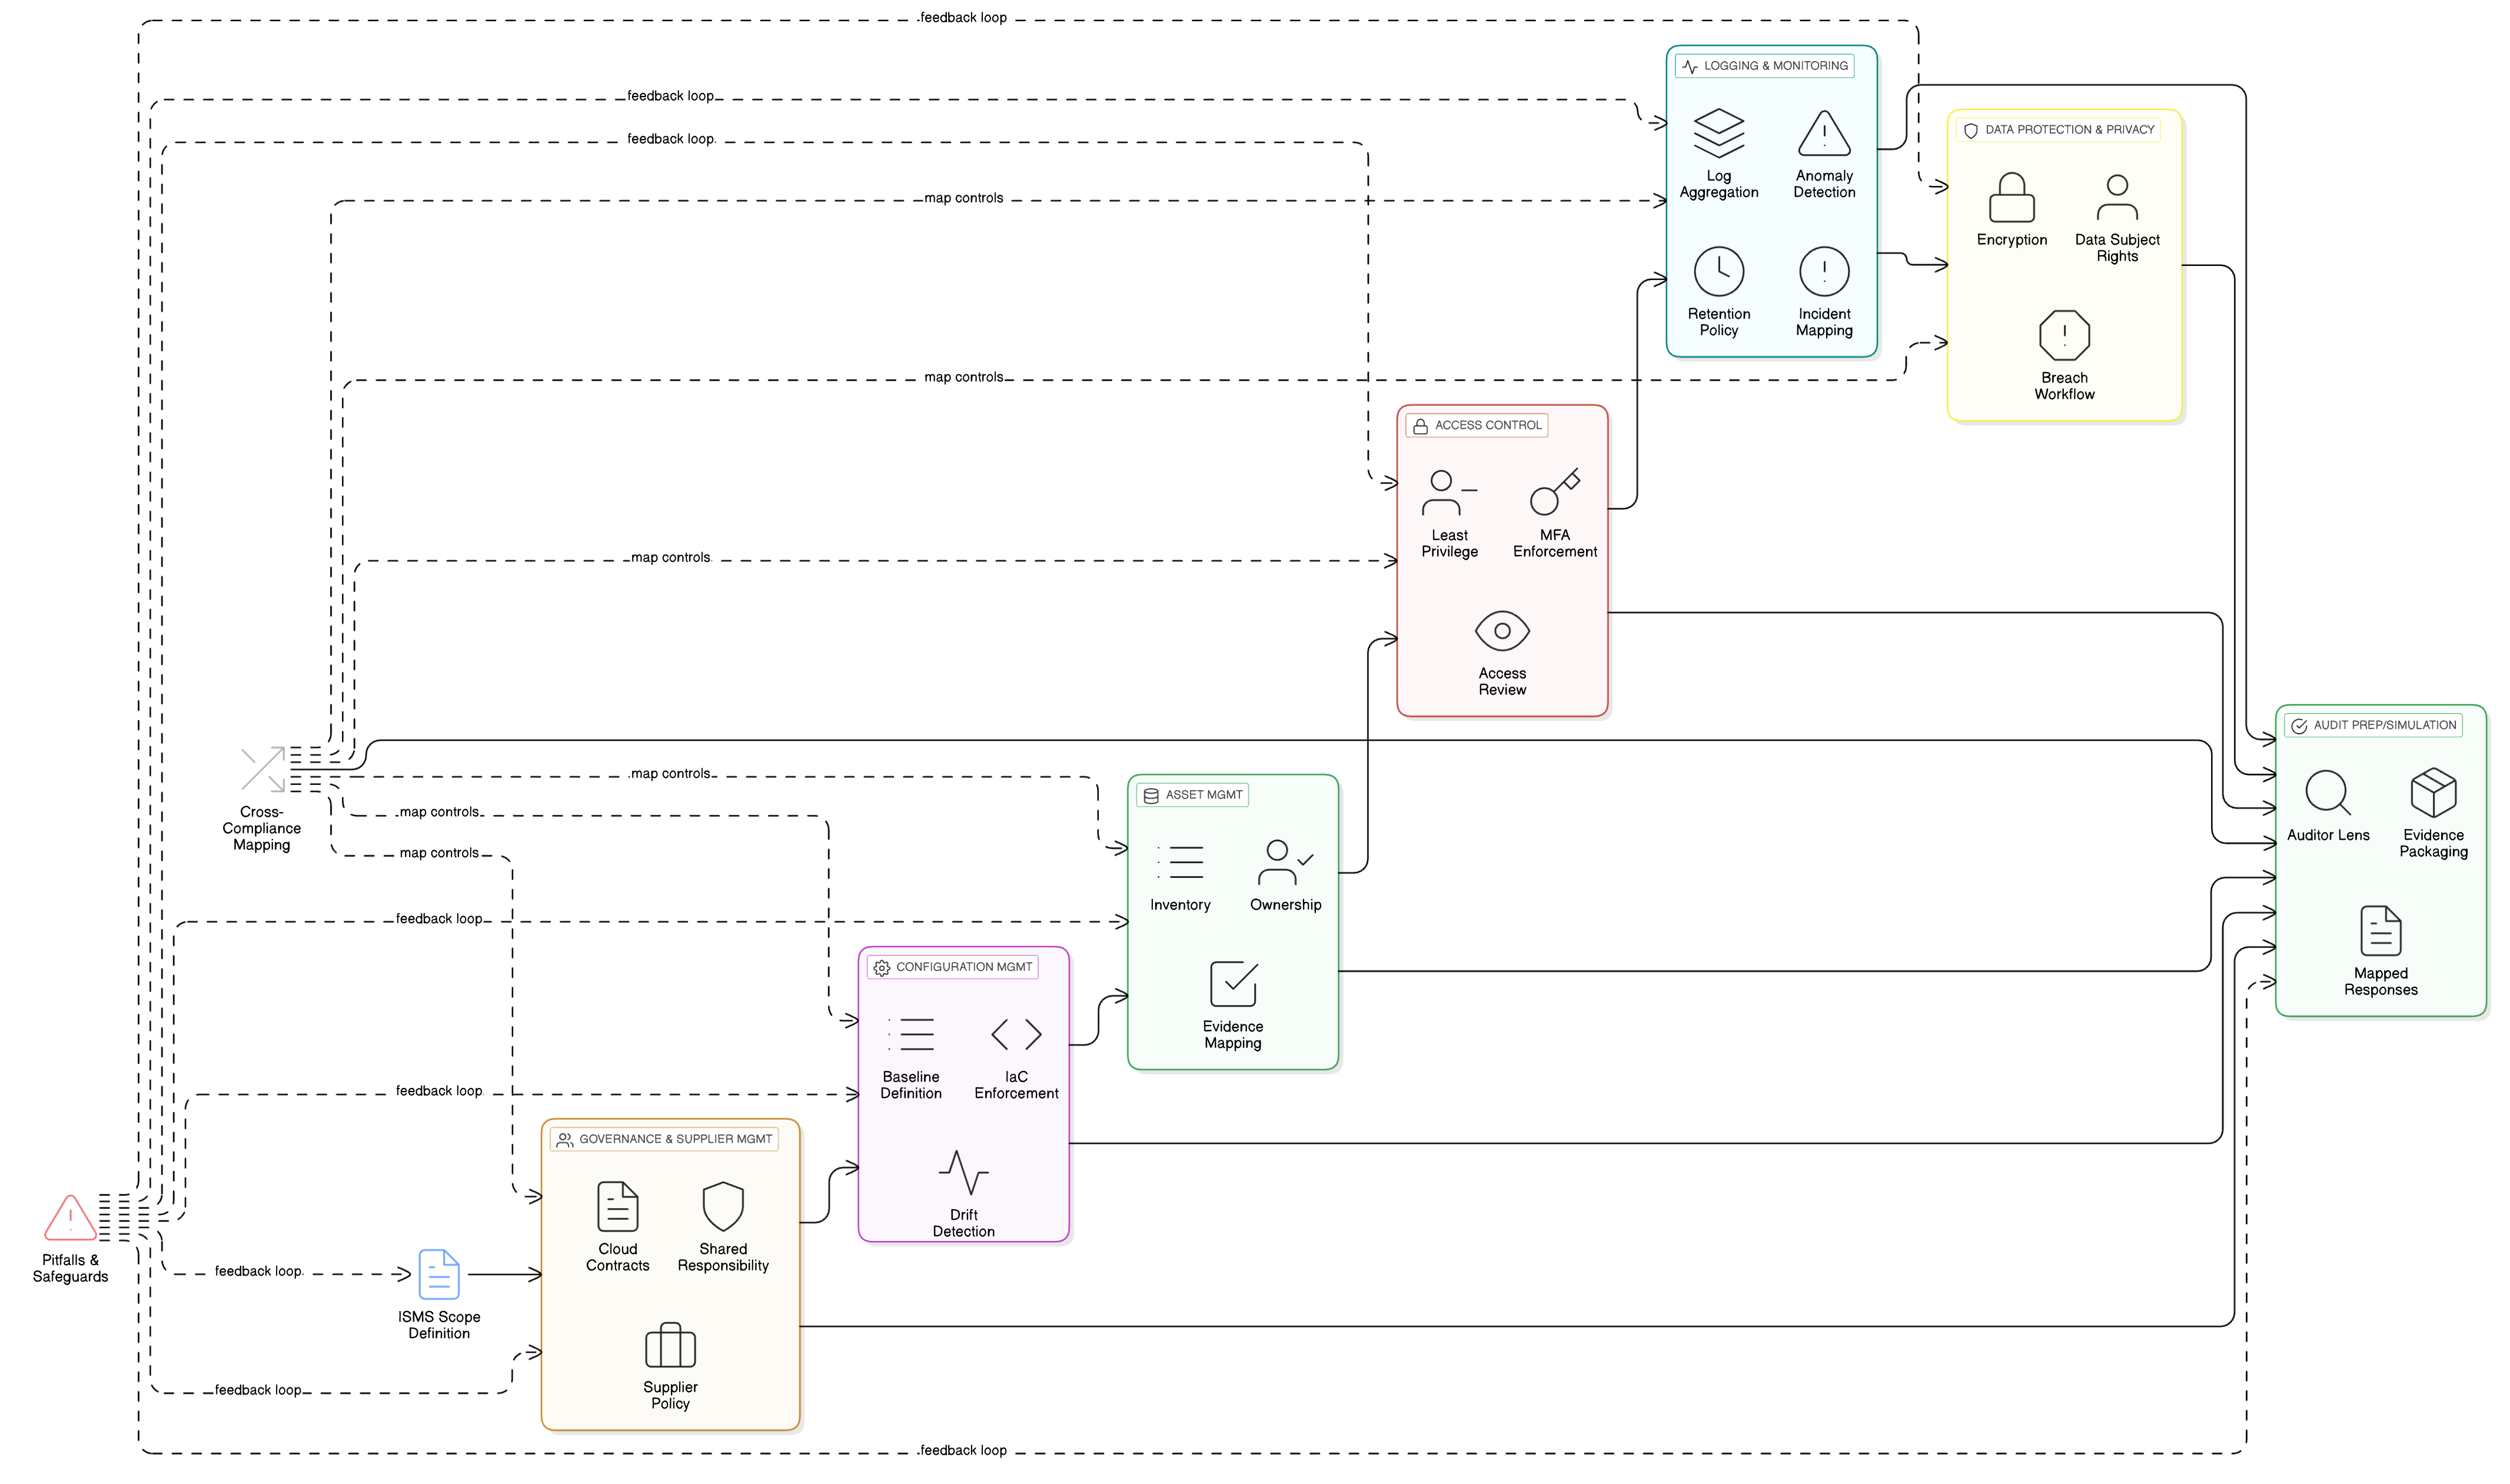
CISOs, compliance managers, and cloud architects: discover how to operationalize ISO 27001:2022 cloud controls for perpetual compliance. Real-world stories, technical mapping tables, and actionable blueprints from Clarysec unite security, governance, and audit-readiness across frameworks.
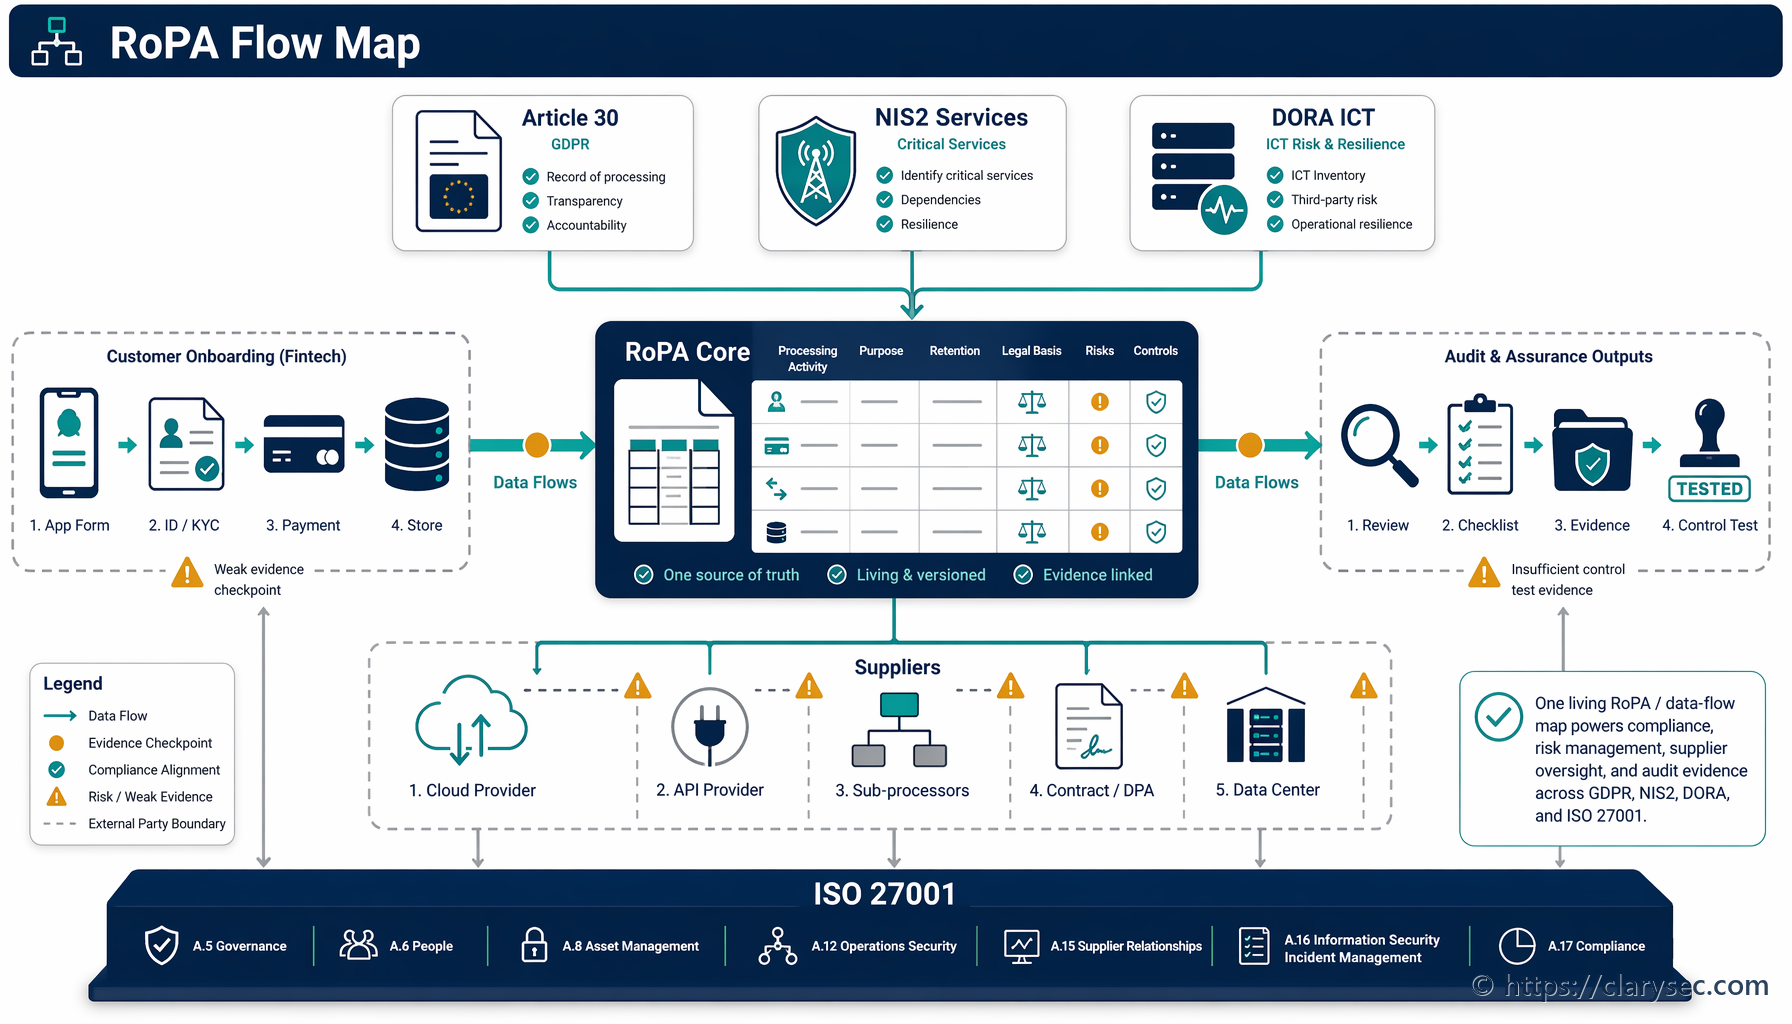
A practical 2026 guide for turning RoPA and data flow mapping into a unified evidence layer for GDPR Article 30, NIS2 critical services, DORA ICT dependencies and ISO/IEC 27001:2022 audits.