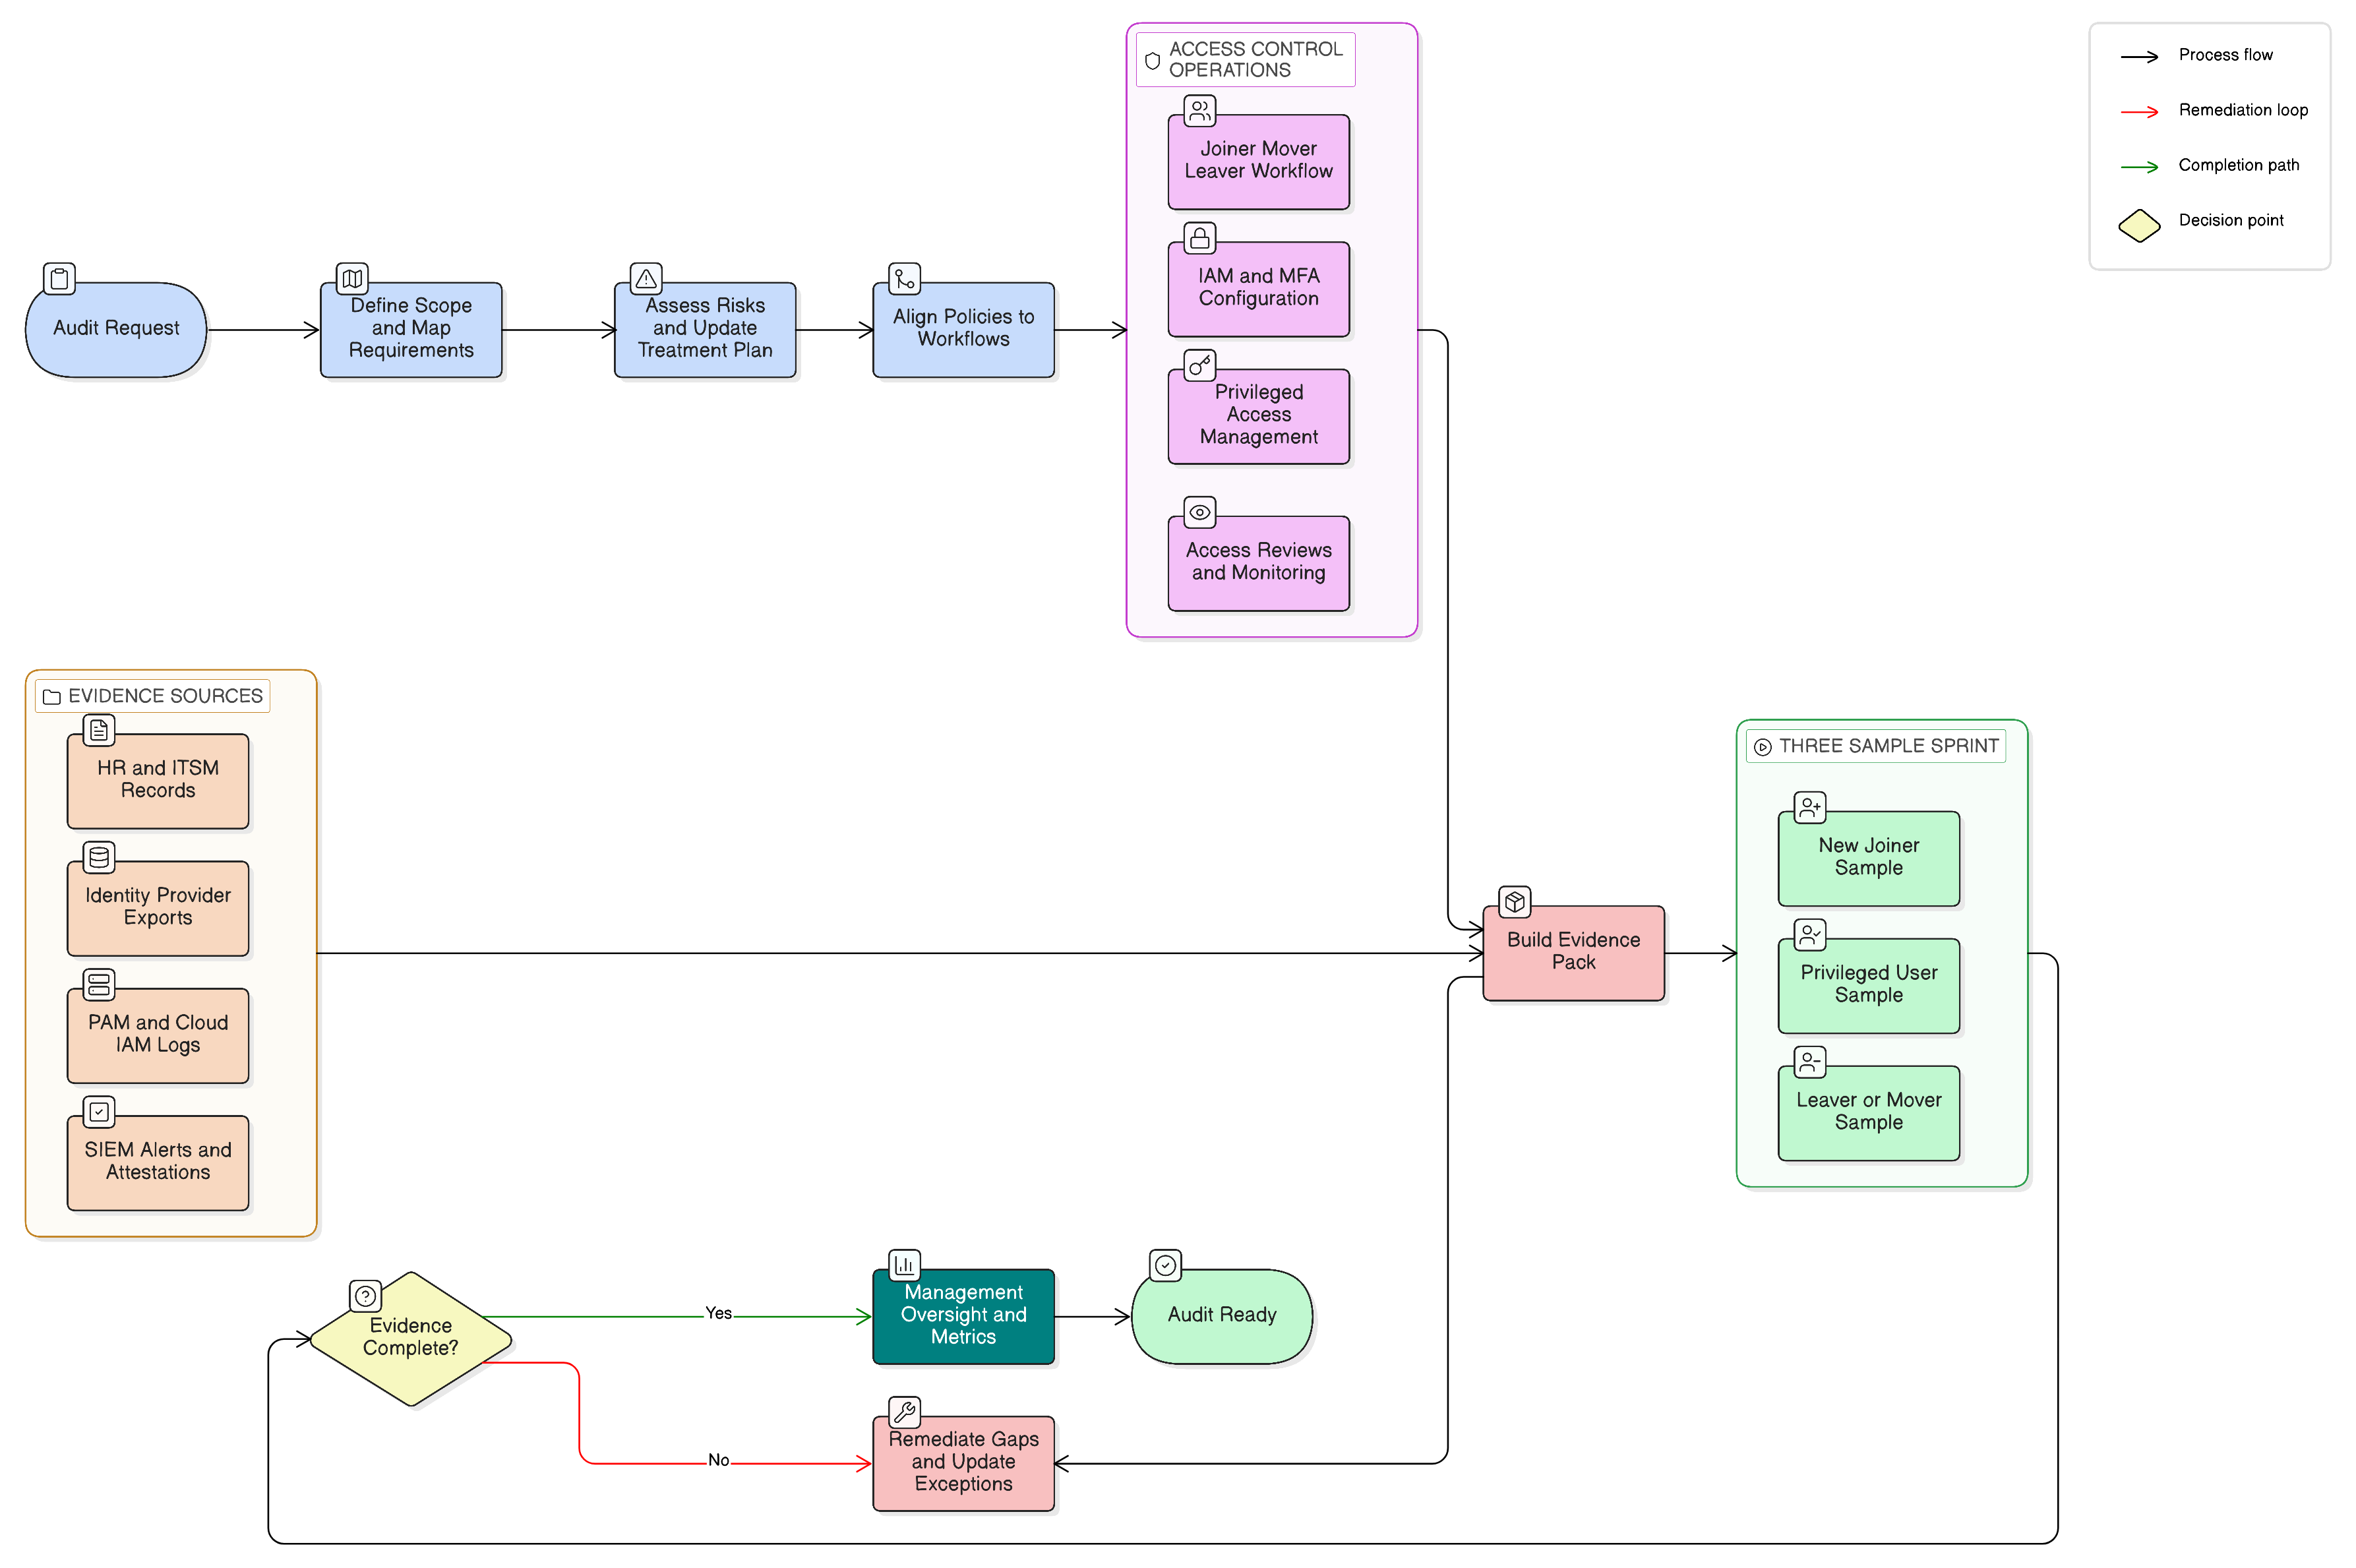
ISO 27001 Access Control Audit Evidence Guide
A practical CISO guide to building one access control evidence model for ISO/IEC 27001:2022, NIS2, DORA, GDPR, NIST and COBIT.
Articles tagged with "Data Protection"
A practical CISO guide to building one access control evidence model for ISO/IEC 27001:2022, NIS2, DORA, GDPR, NIST and COBIT.
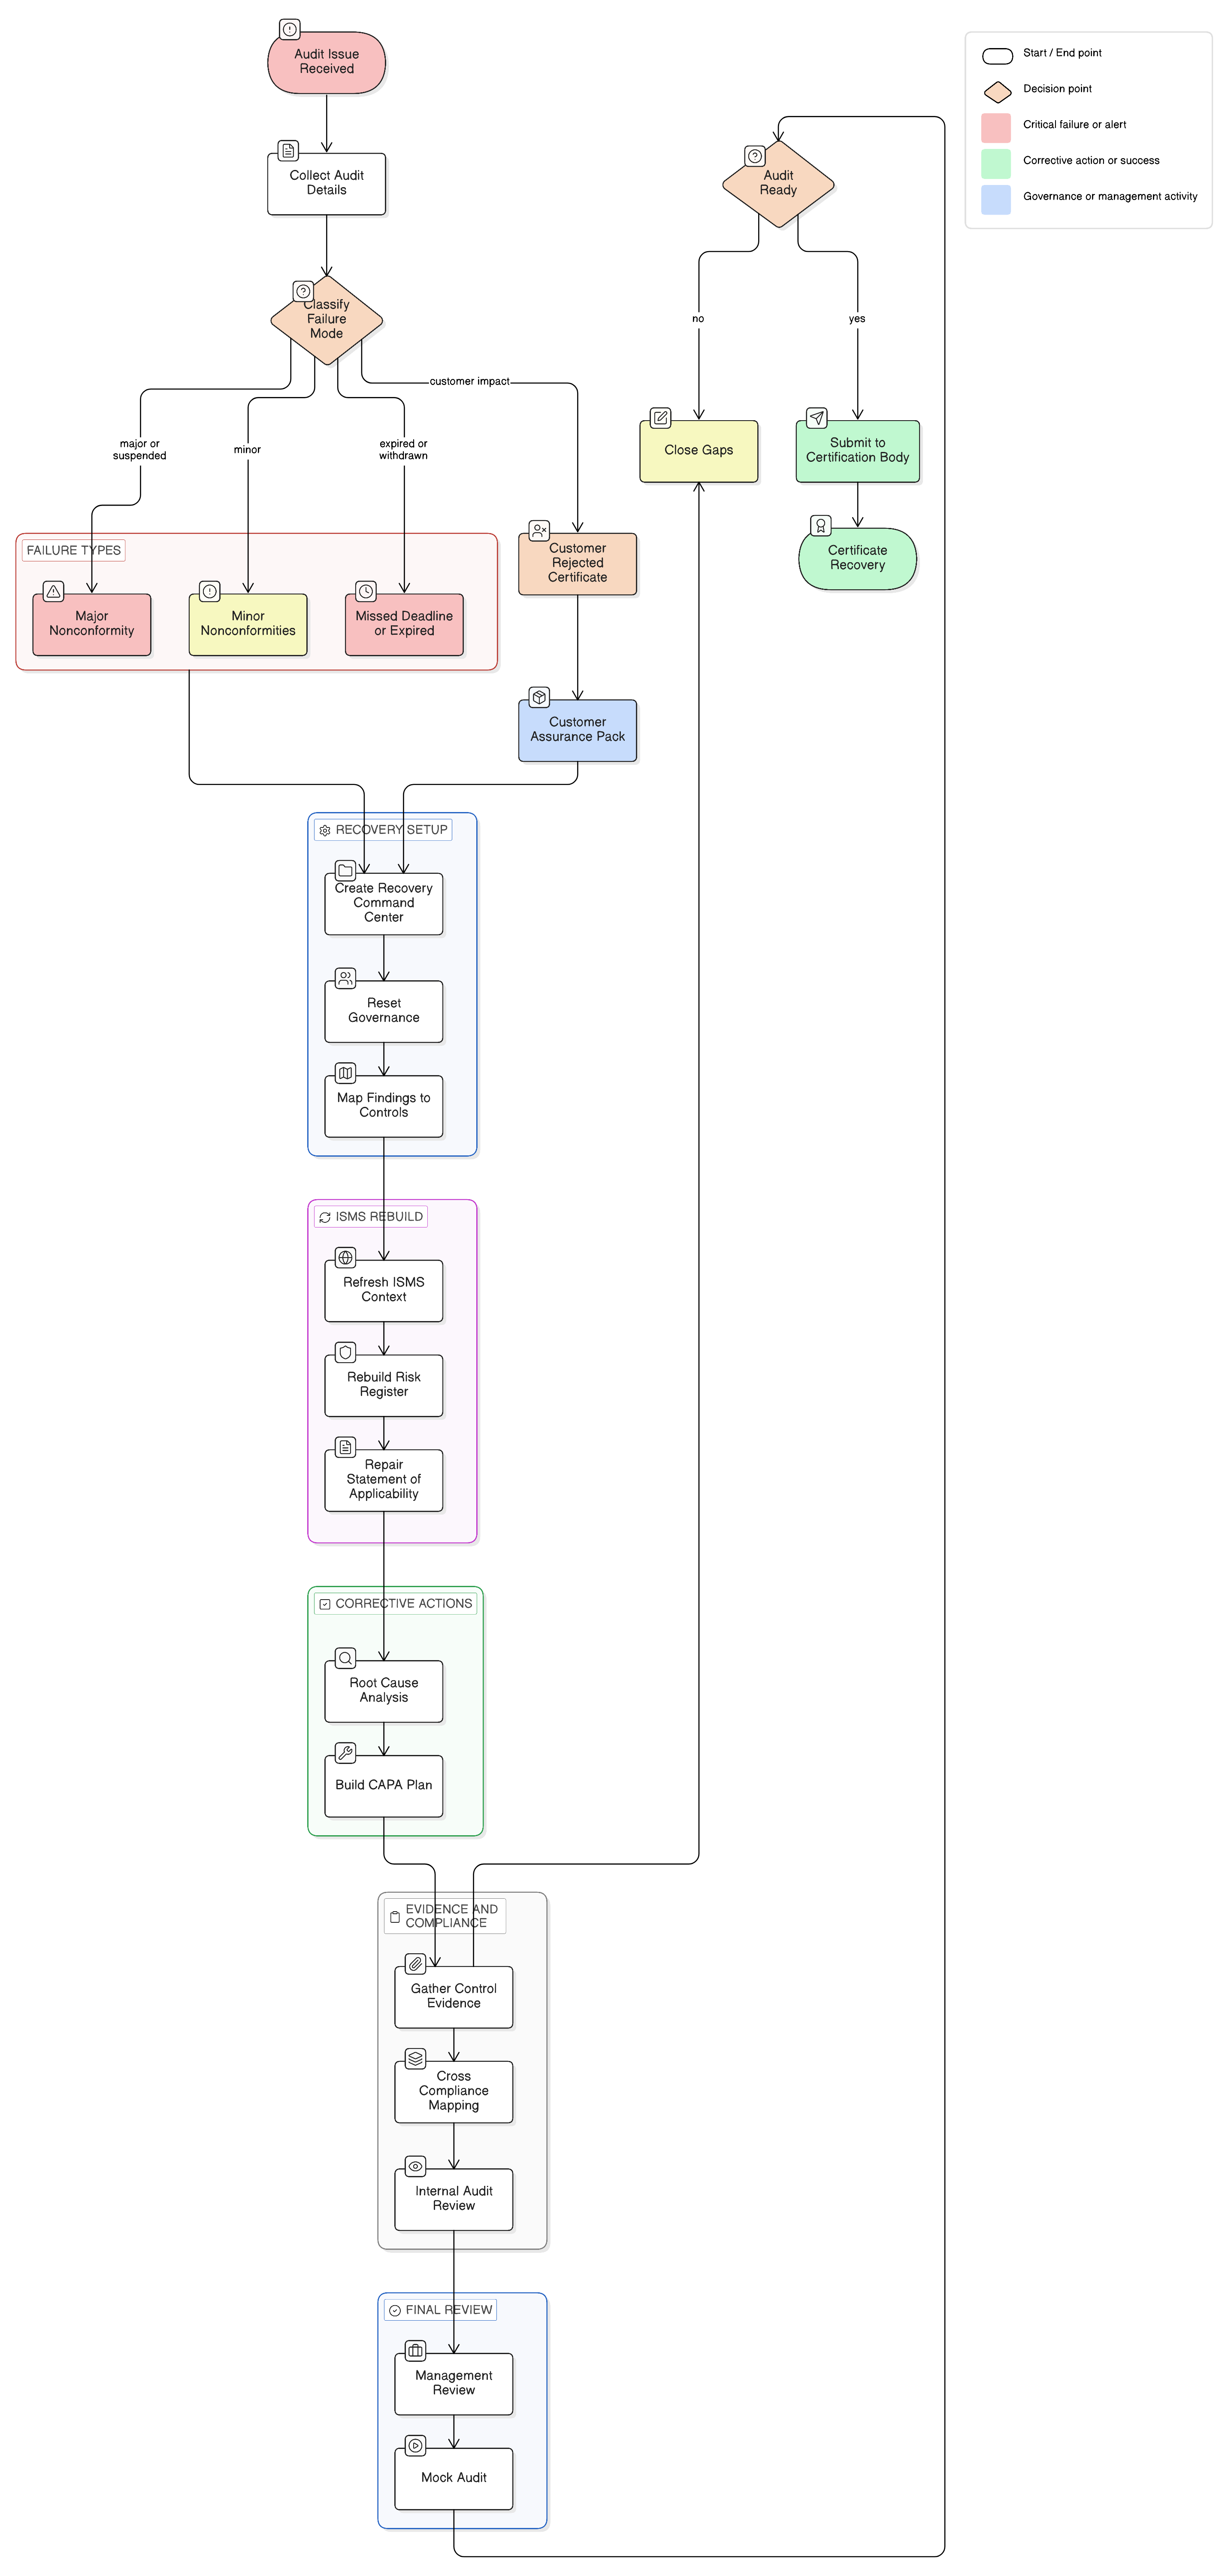
If your ISO 27001:2022 transition was missed or failed, the recovery path is disciplined triage, evidence repair, root cause analysis, SoA rebuild, and corrective action. This guide explains how Clarysec uses Zenith Blueprint, policies, and Zenith Controls to restore audit confidence.
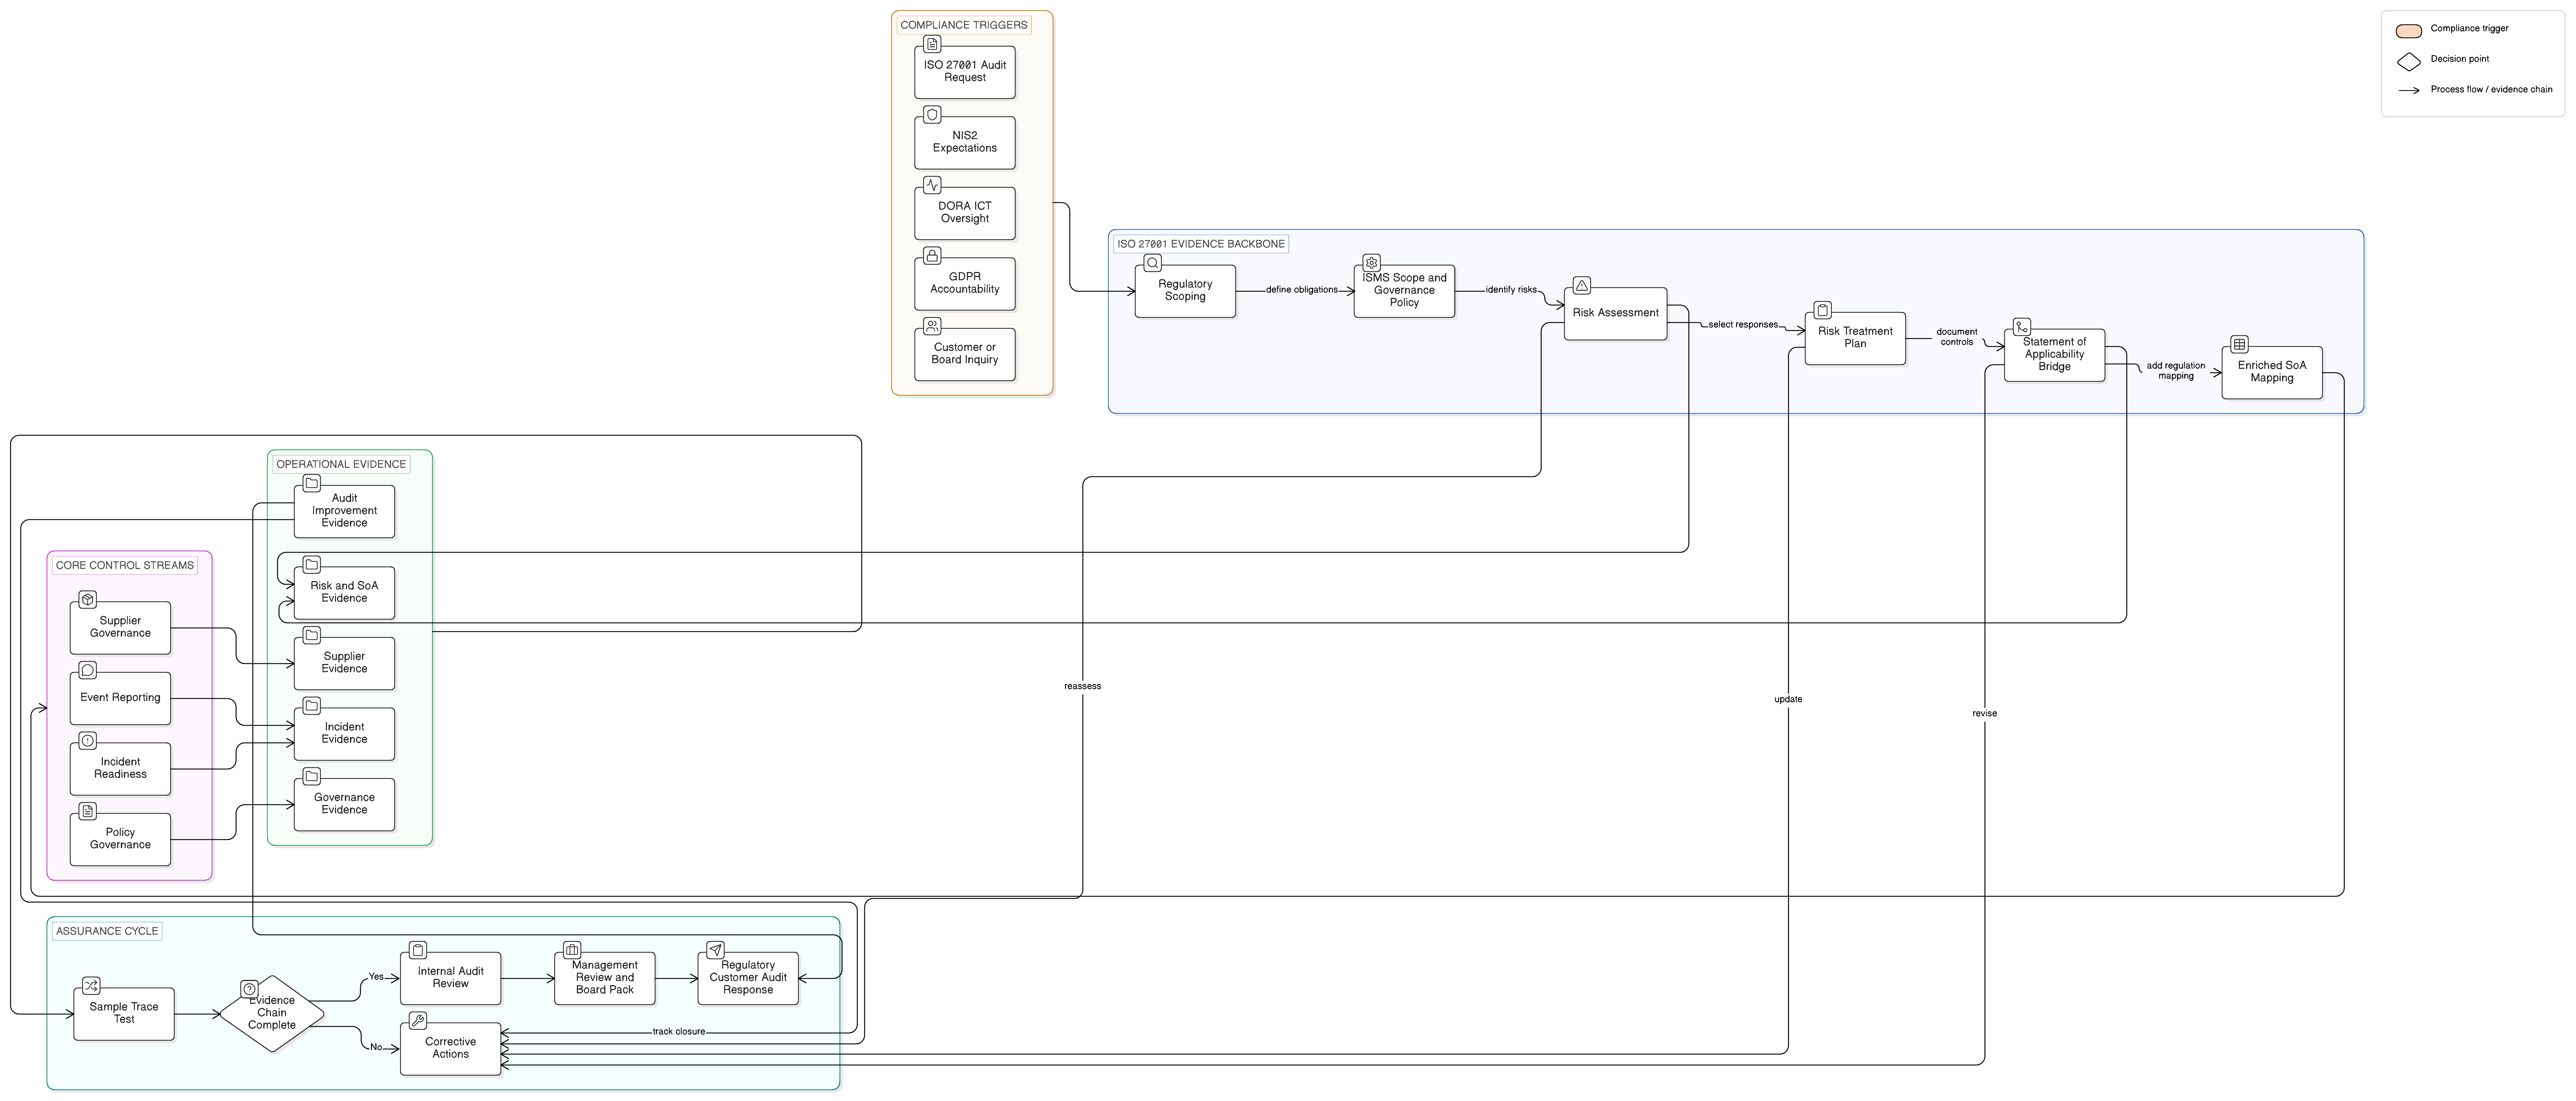
Use ISO 27001:2022, the Statement of Applicability, and Clarysec policy mapping to build an audit-ready evidence backbone for NIS2, DORA, GDPR, suppliers, incidents, and board oversight.

A practical CISO guide to mapping DORA major ICT-related incident reporting to ISO/IEC 27001:2022 Annex A controls, audit evidence, policy clauses, and Clarysec implementation tools.
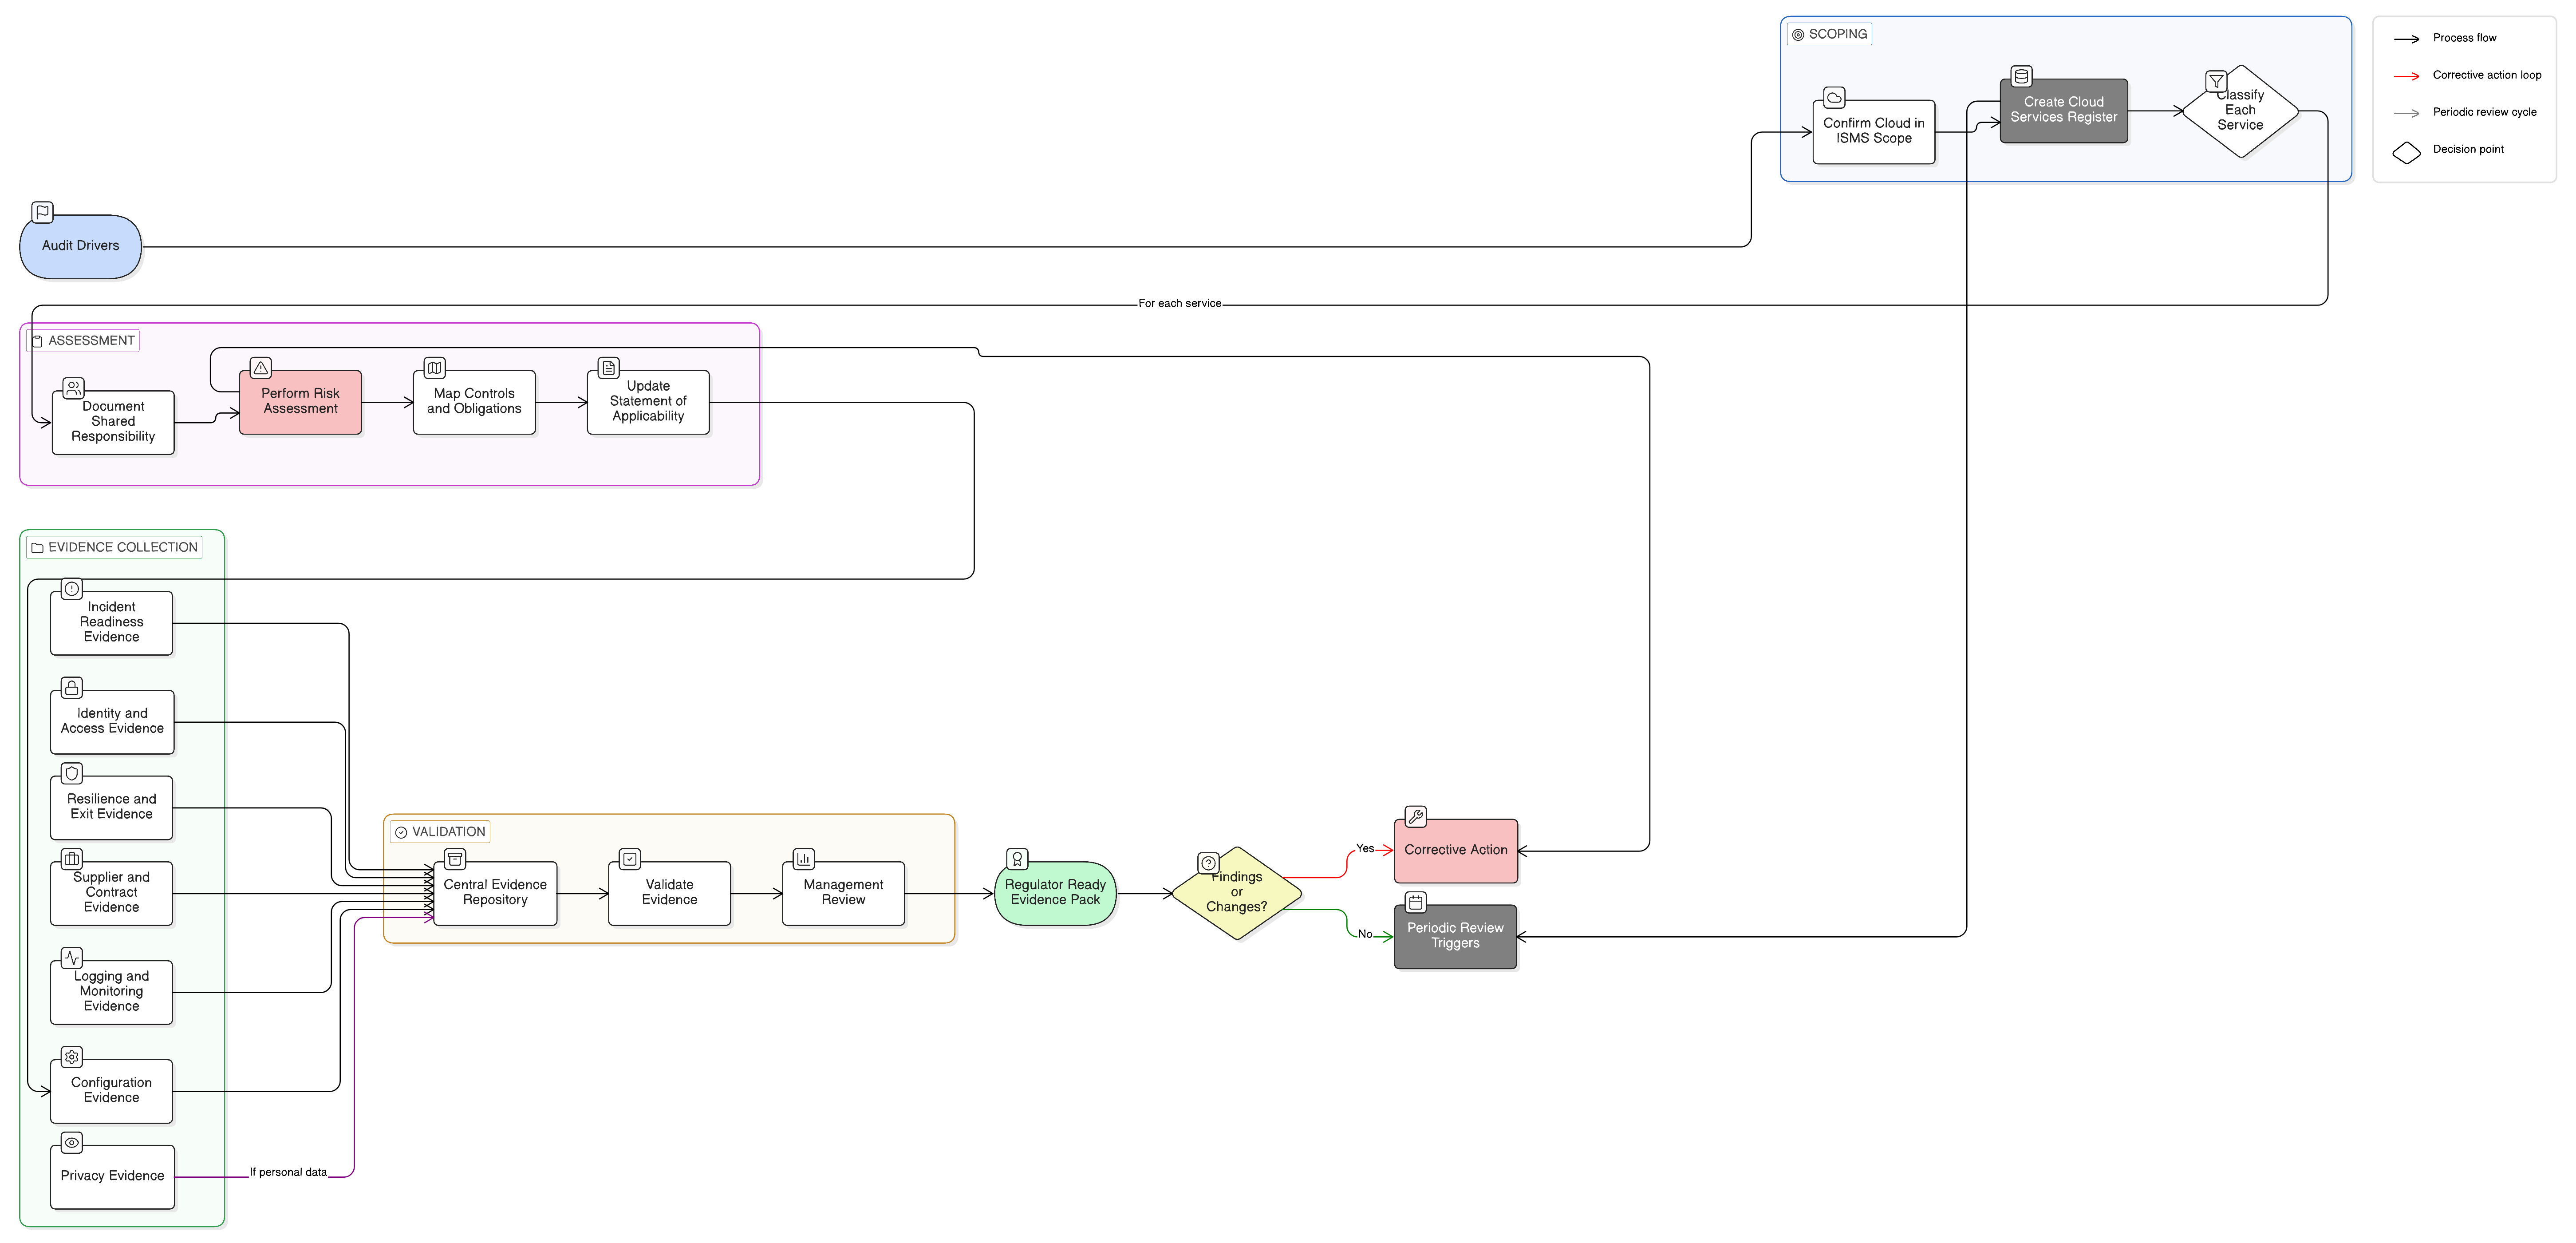
Cloud audit evidence fails when organizations cannot prove shared responsibility, SaaS configuration, IaaS controls, supplier oversight, logging, resilience and incident readiness. This guide shows how Clarysec structures regulator-ready proof across ISO 27001:2022, NIS2, DORA and GDPR.
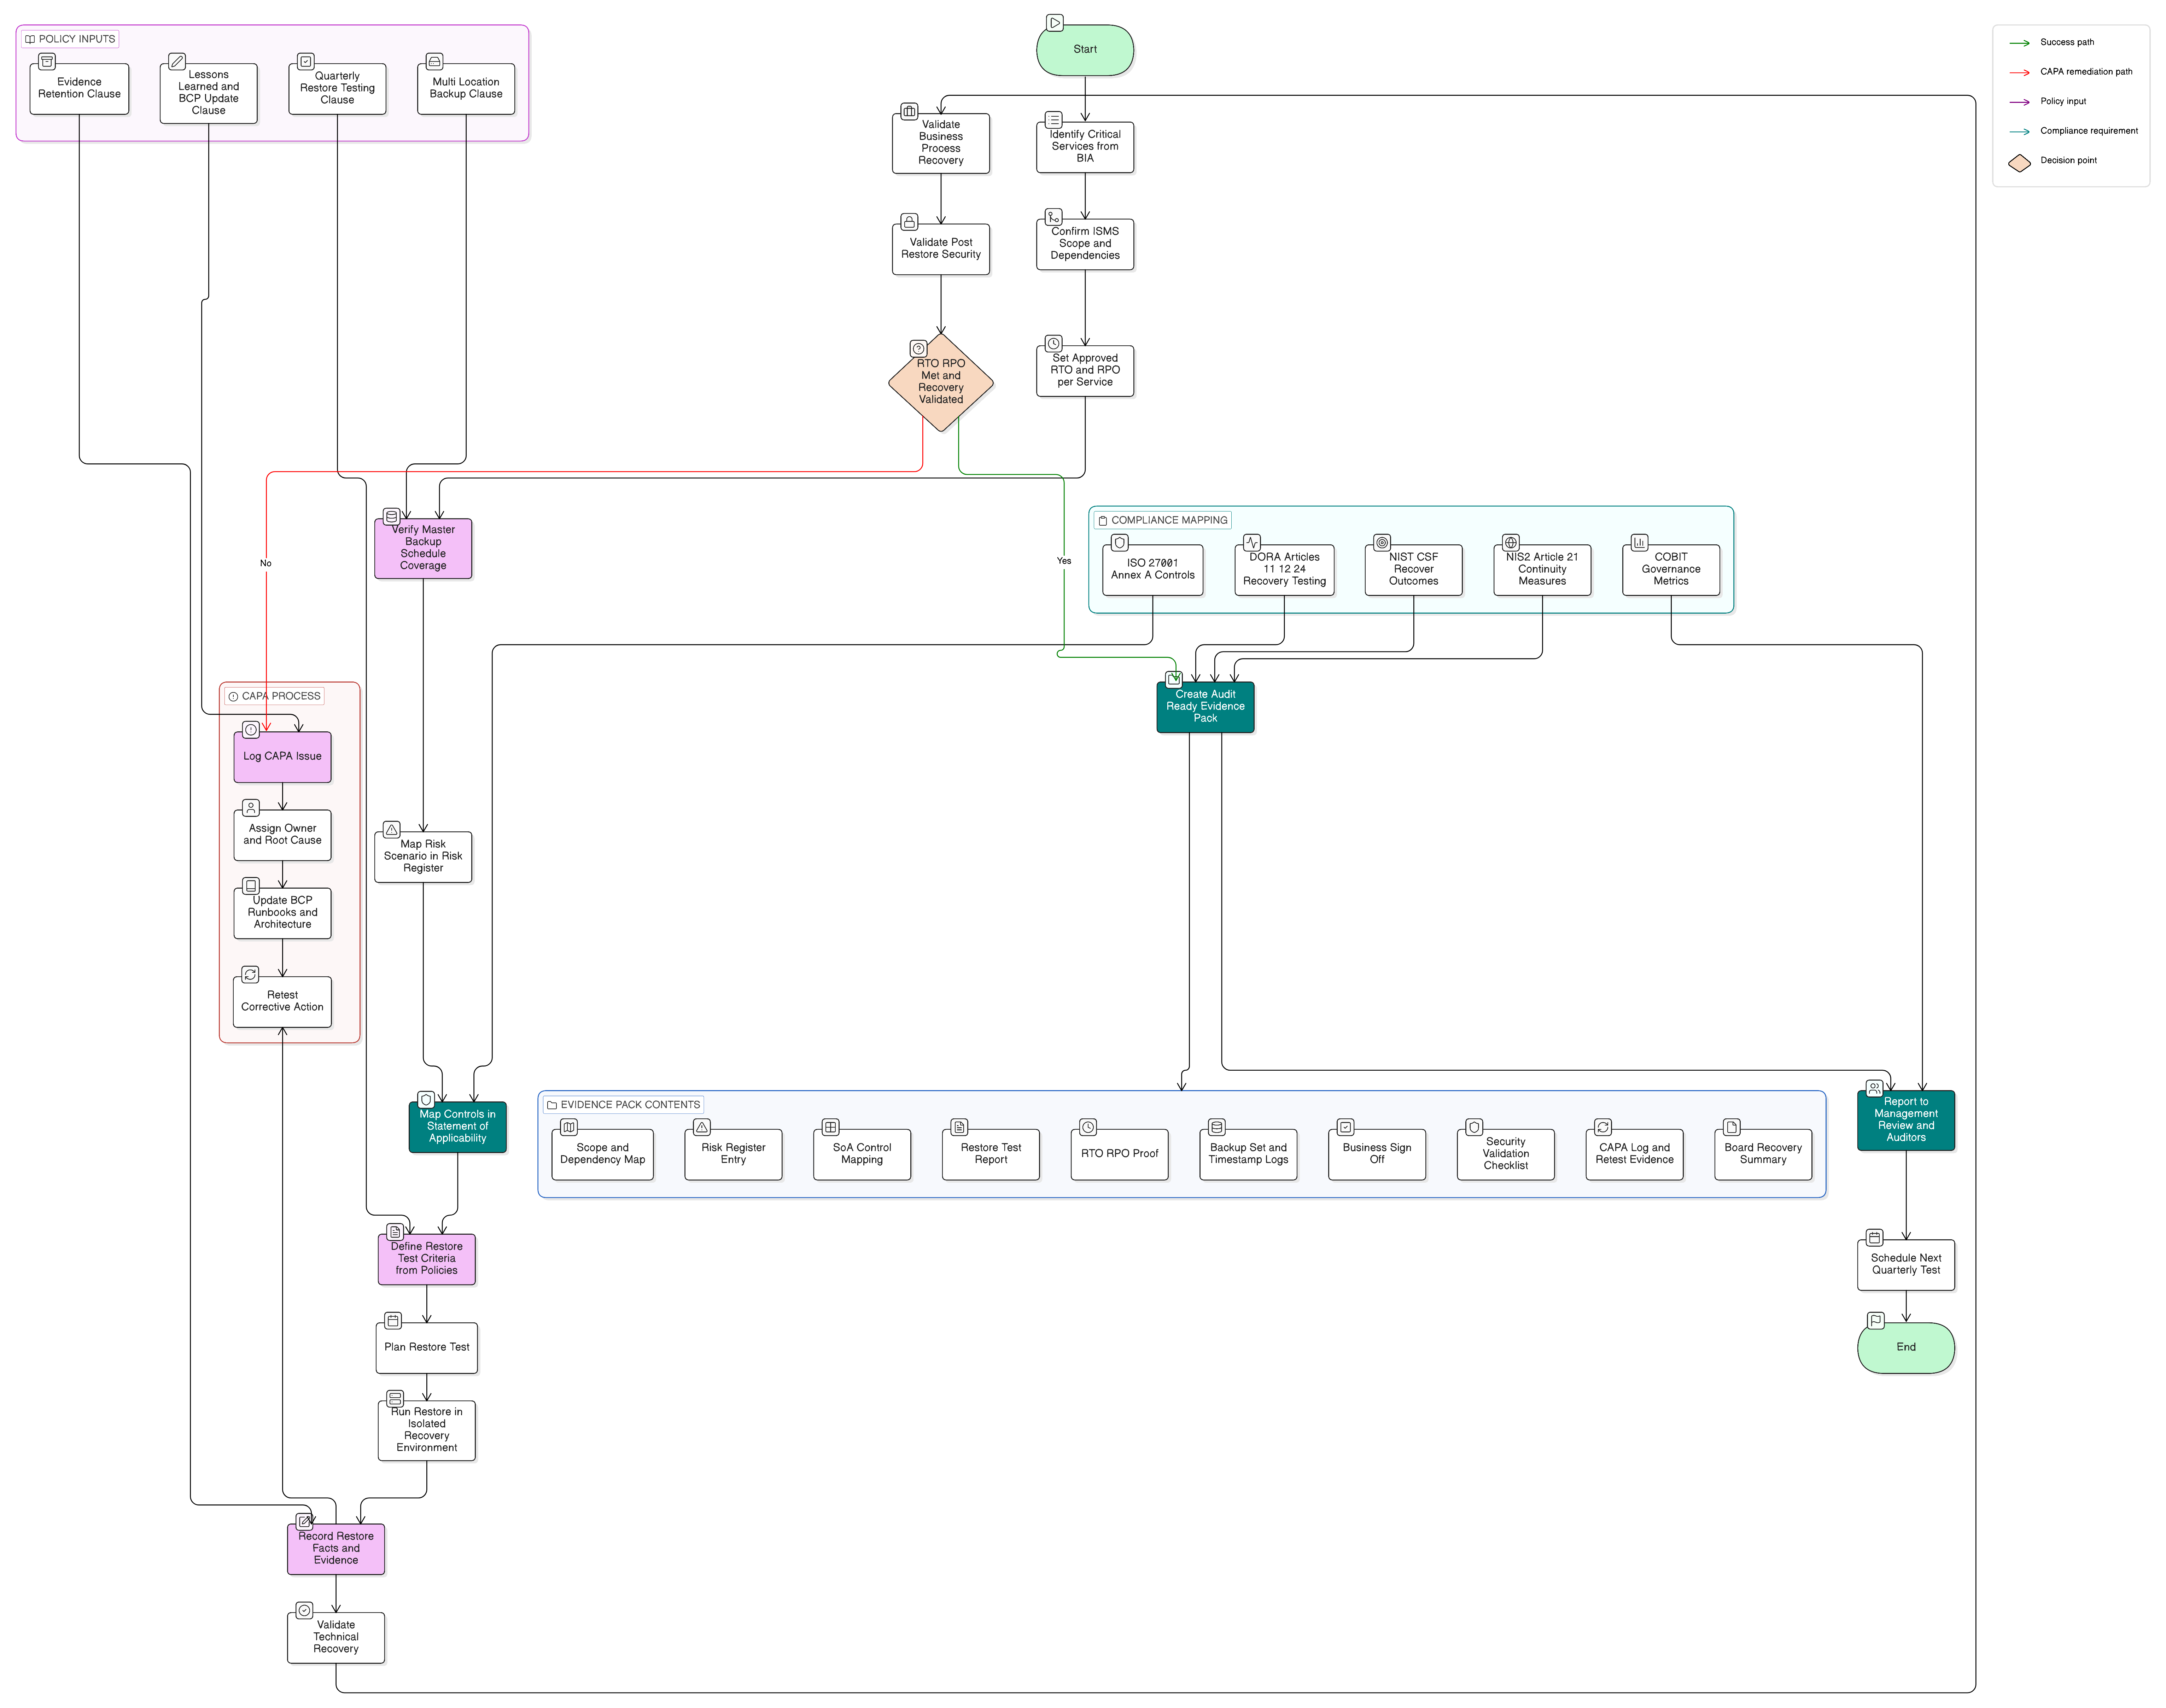
Backup testing is no longer technical hygiene. CISOs must prove recoverability, RTO/RPO performance, control traceability, and continual improvement.
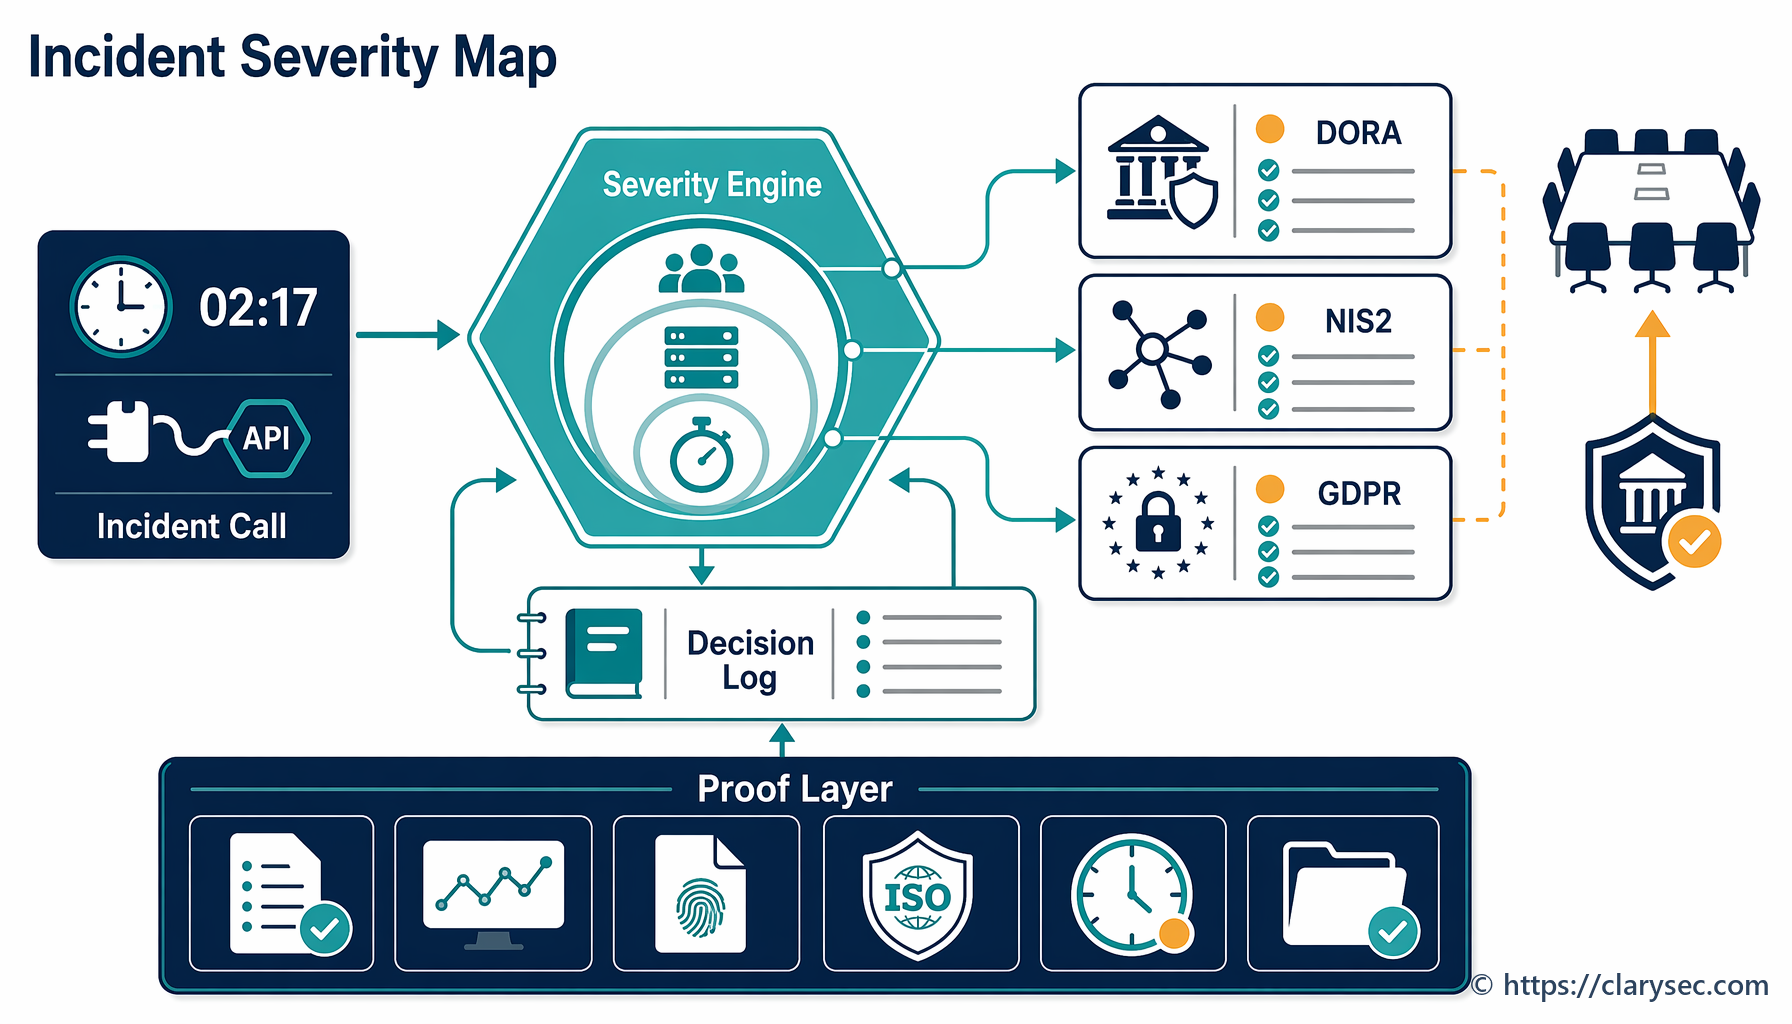
A practical guide to building a unified incident severity classification model that maps DORA major ICT incidents, NIS2 significant incidents and GDPR breach risk to ISO/IEC 27001:2022 evidence.
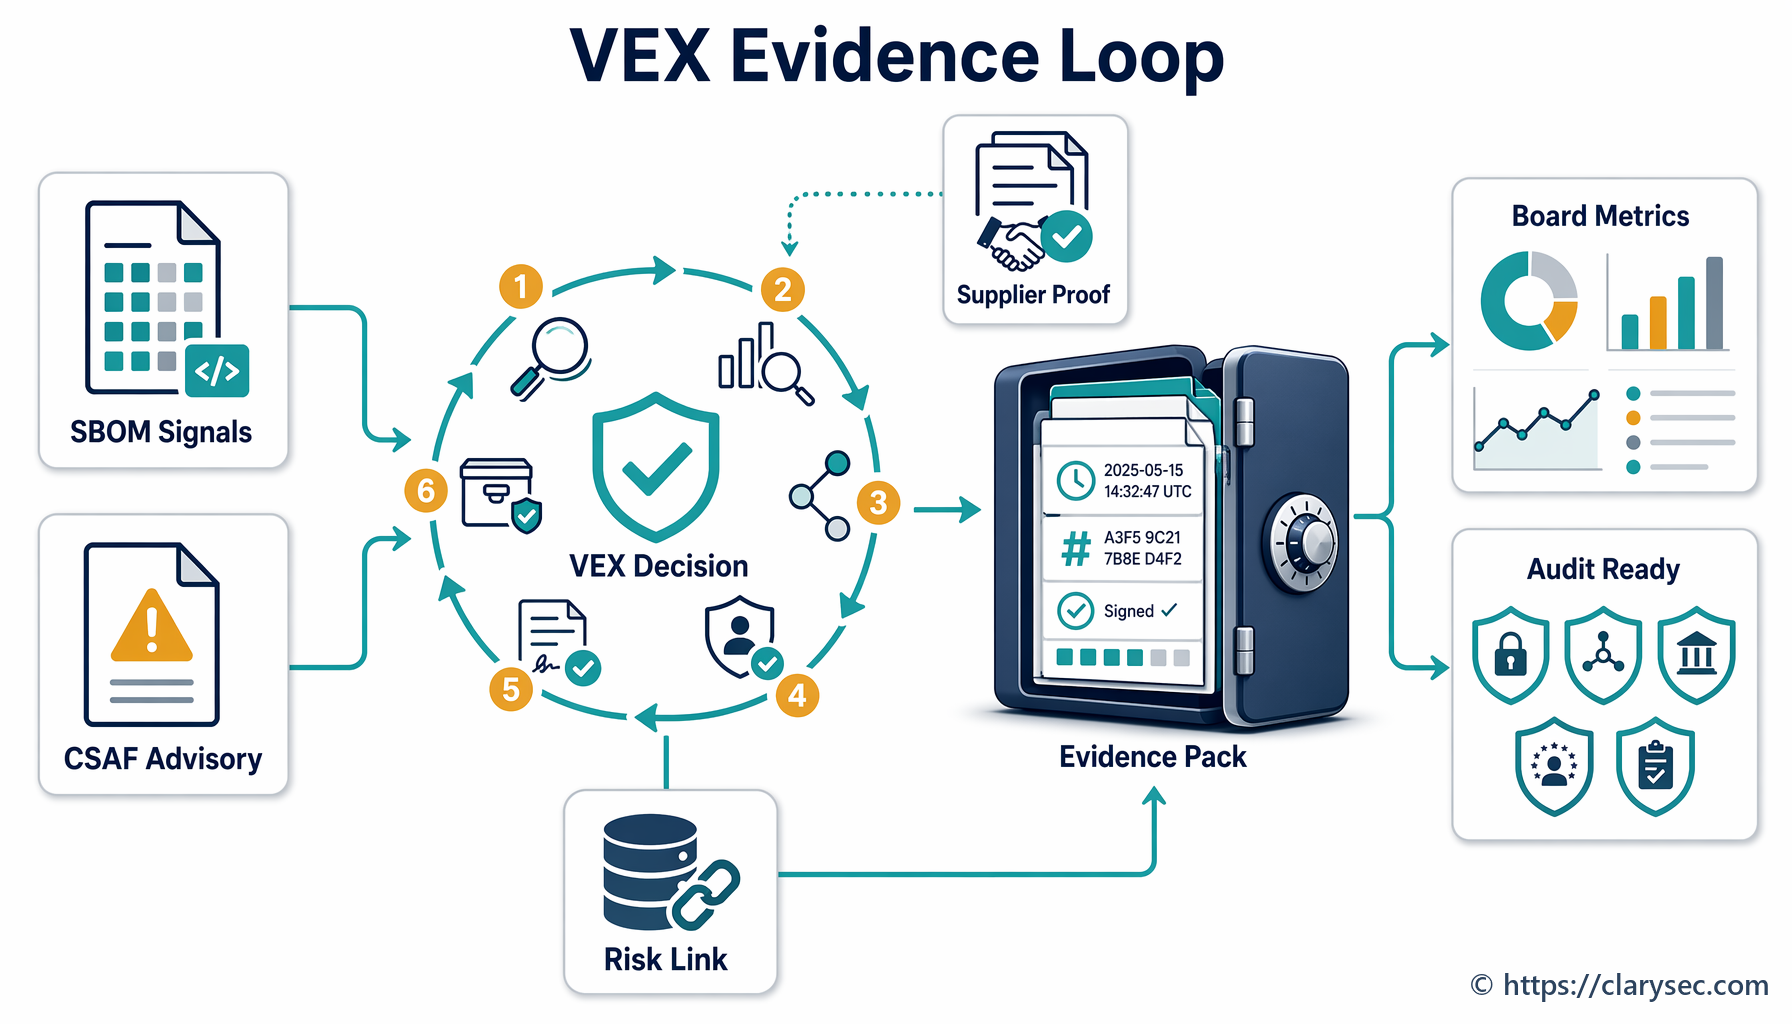
VEX and CSAF are becoming the evidence layer between SBOMs, supplier advisories, vulnerability triage and regulatory proof. This guide shows how to govern vulnerability status decisions across ISO 27001, NIS2, DORA, GDPR and CRA.
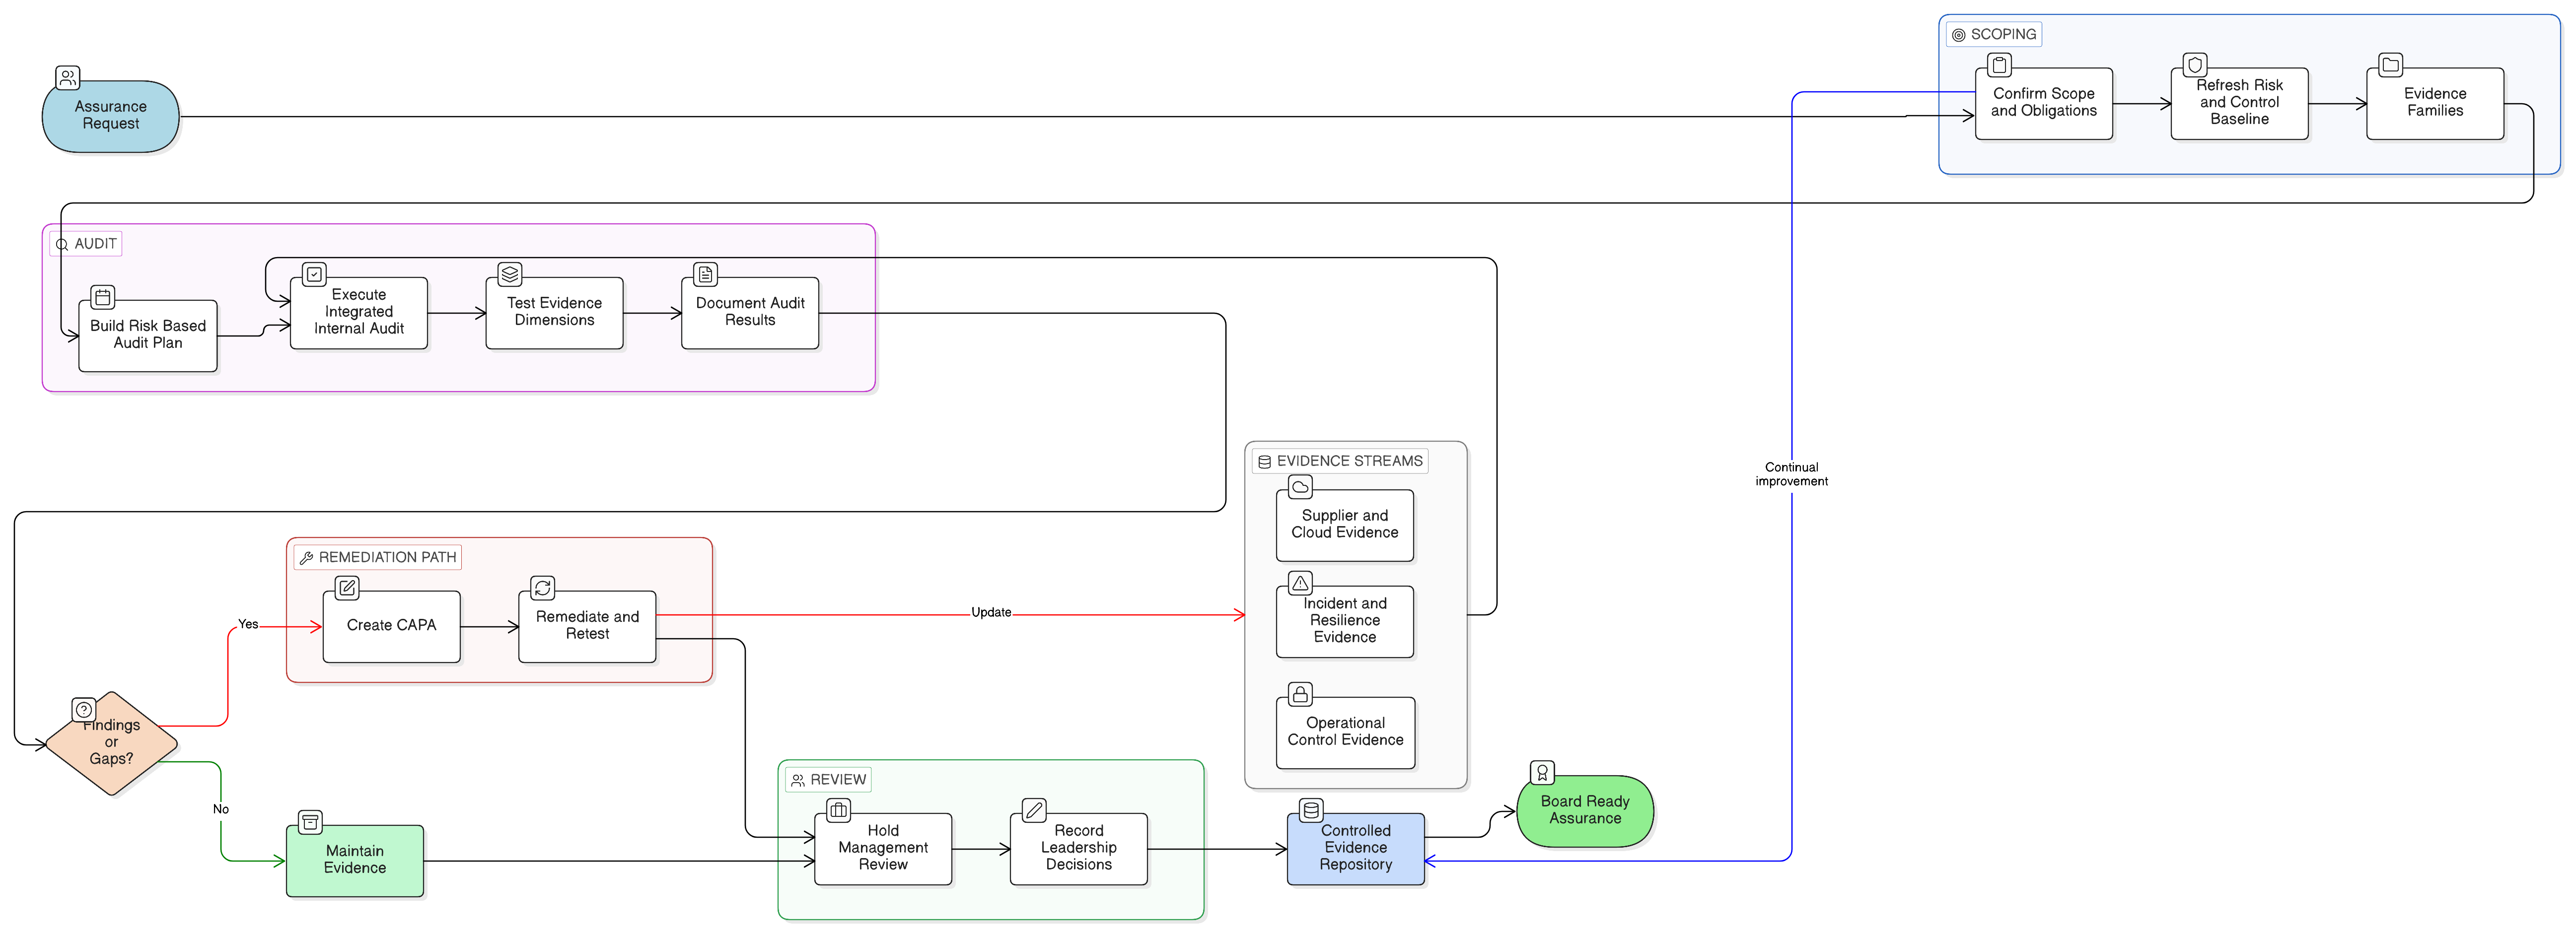
Learn how to use ISO/IEC 27001:2022 internal audit and management review as a unified evidence engine for NIS2, DORA, GDPR, supplier risk, customer assurance and board accountability.