#Data Protection
Articles tagged with "Data Protection"
62 articles
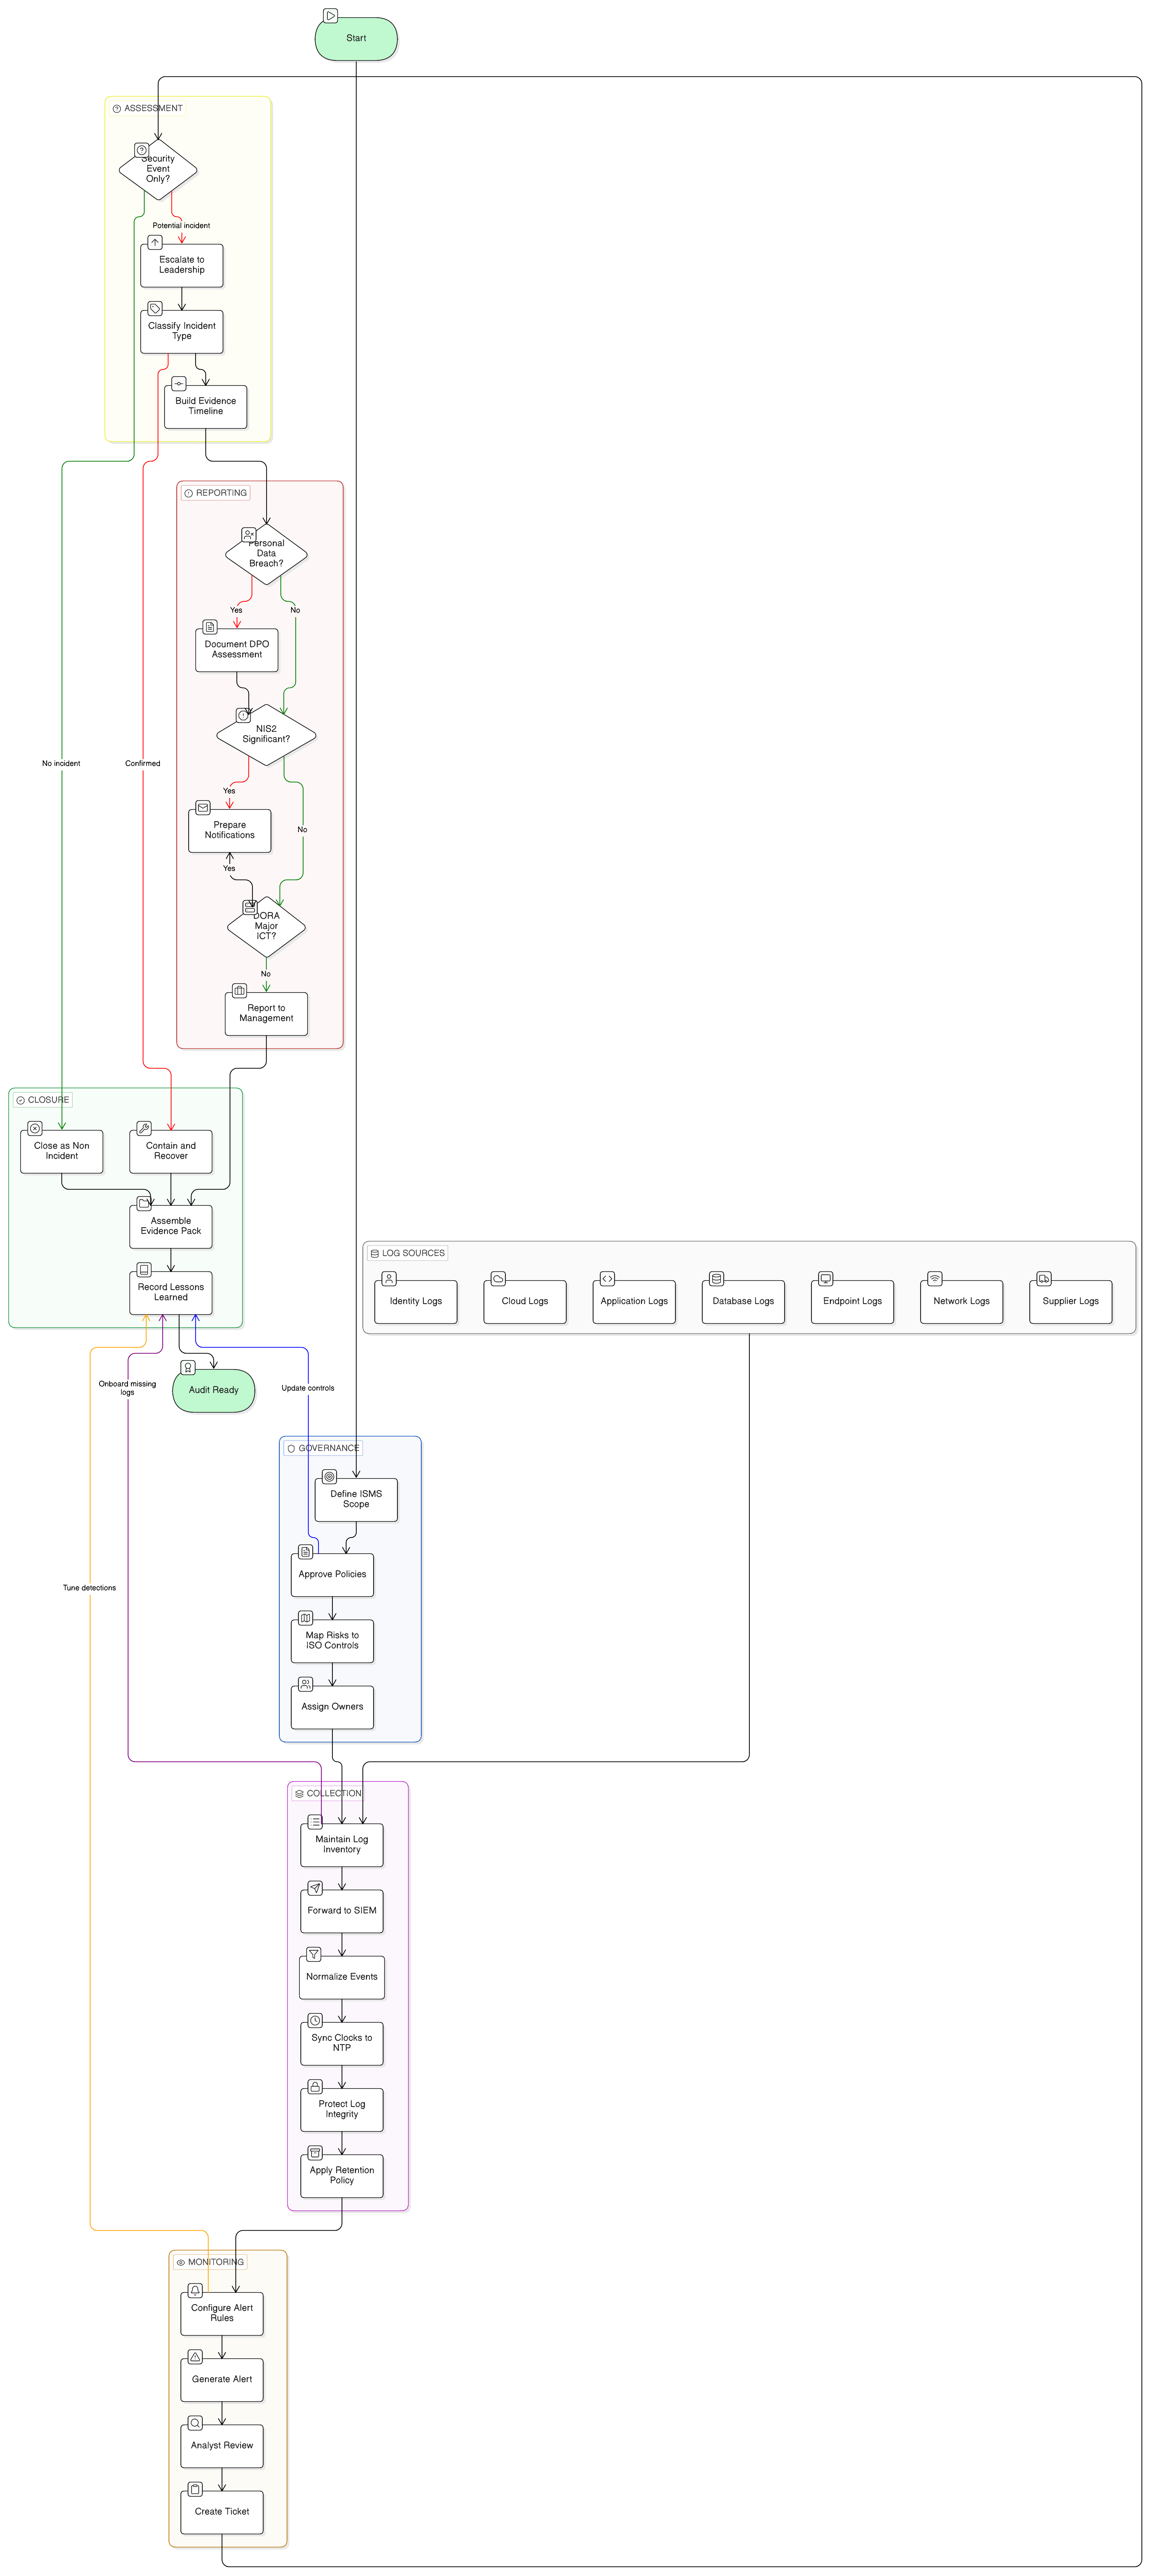
A practical guide to building audit-ready ISO/IEC 27001:2022 logging and monitoring evidence for NIS2, DORA and GDPR, with control mapping, policy clauses, incident workflows, supplier logging requirements and evidence pack guidance.
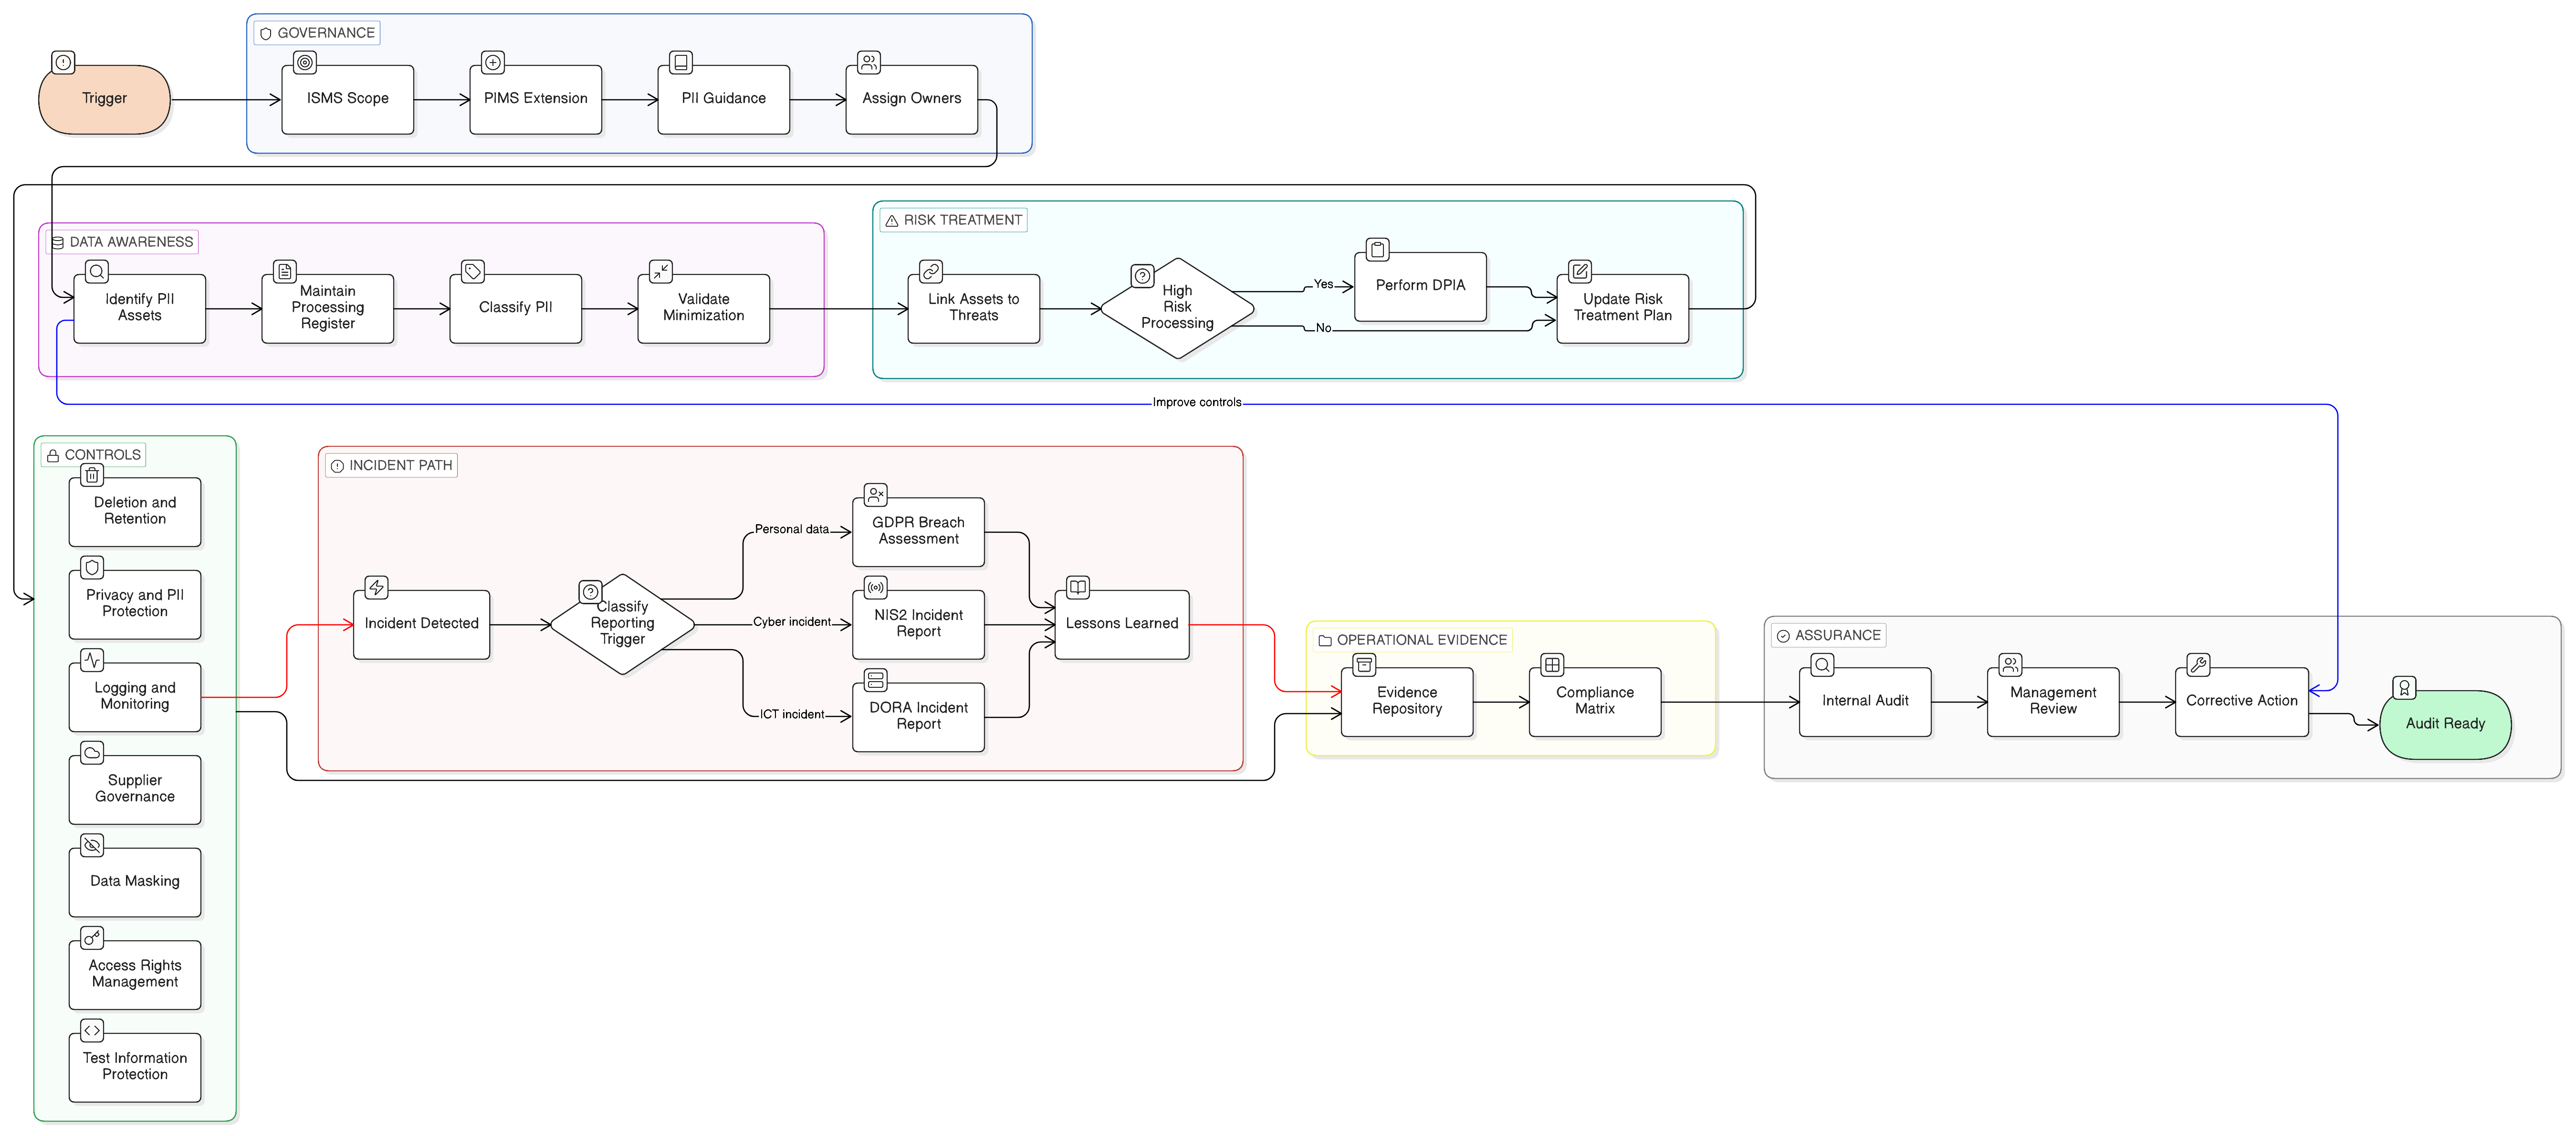
Learn how to build audit-ready PII protection controls by extending ISO/IEC 27001:2022 with ISO/IEC 27701:2025 and ISO/IEC 29151:2022, mapped to GDPR, NIS2, DORA, NIST-style assurance, and COBIT 2019 governance expectations.
A regulatory contact register is no longer administrative housekeeping. For NIS2, DORA, GDPR and ISO/IEC 27001:2022, it is operational evidence that your organization can notify the right authority, supervisor, supplier or executive before the clock runs out.
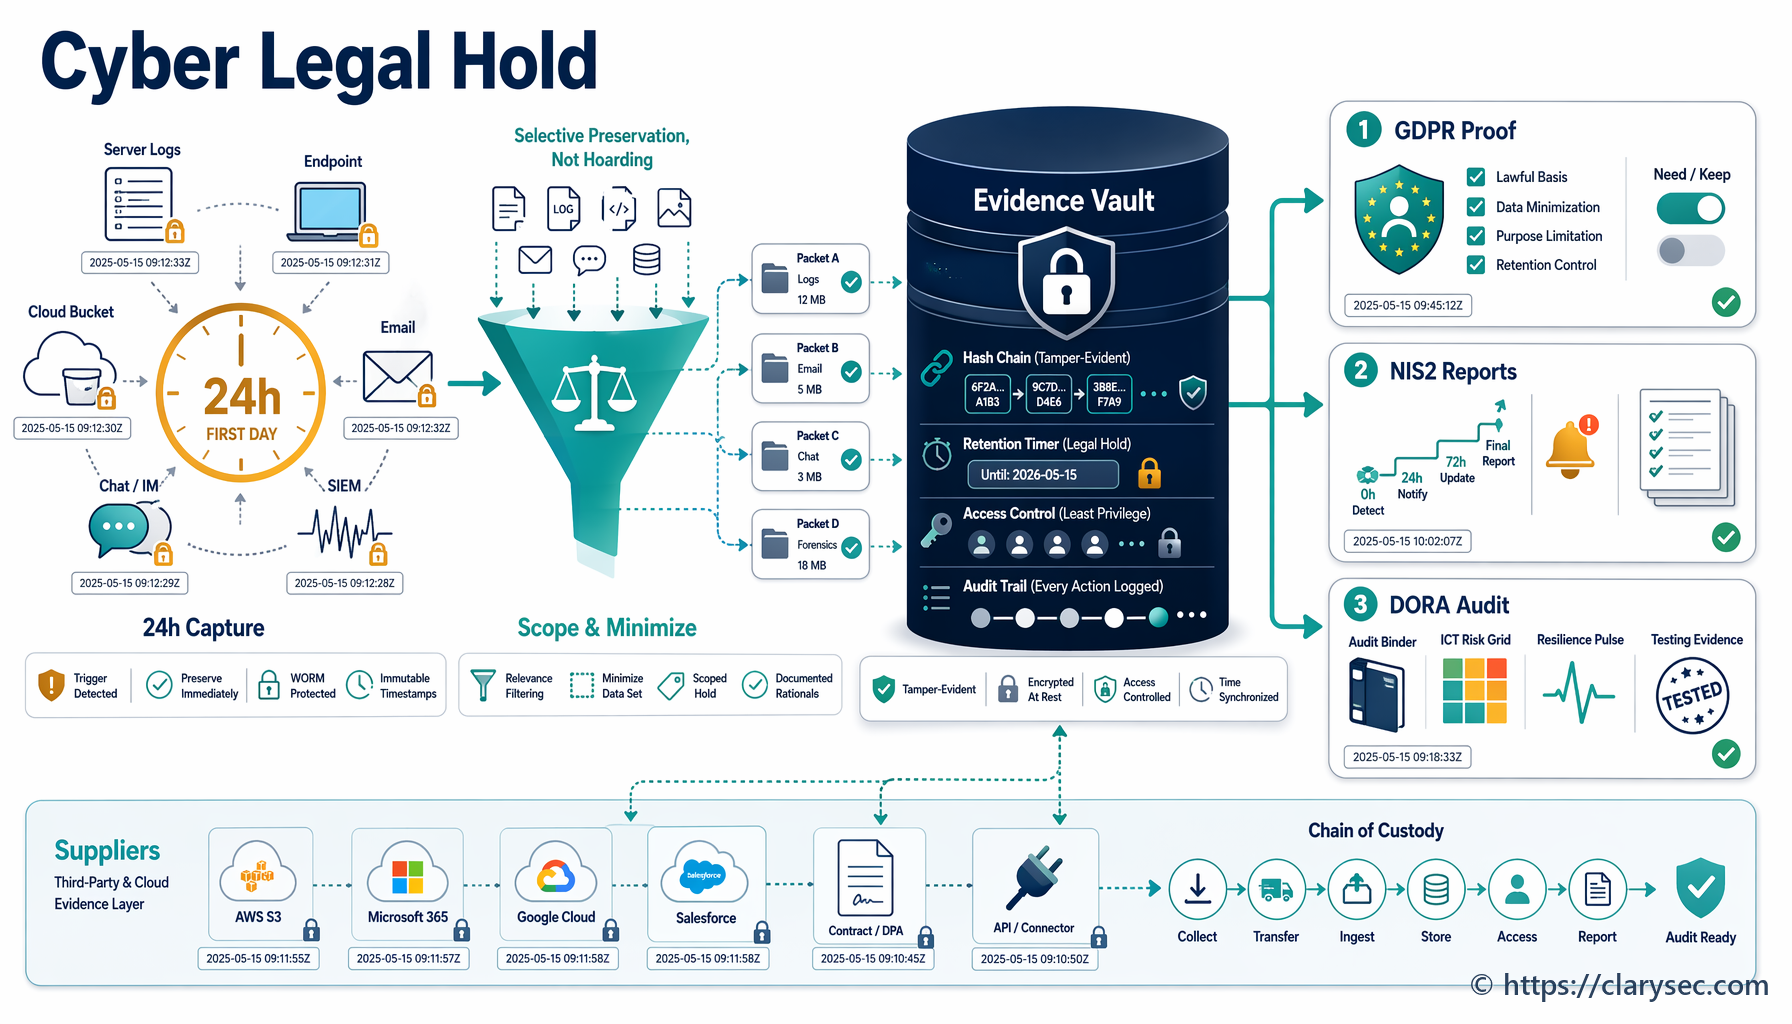
A practical CISO guide to cyber incident legal hold and evidence retention, mapped to ISO/IEC 27001:2022, GDPR, NIS2, DORA, NIST CSF 2.0 and COBIT 2019.
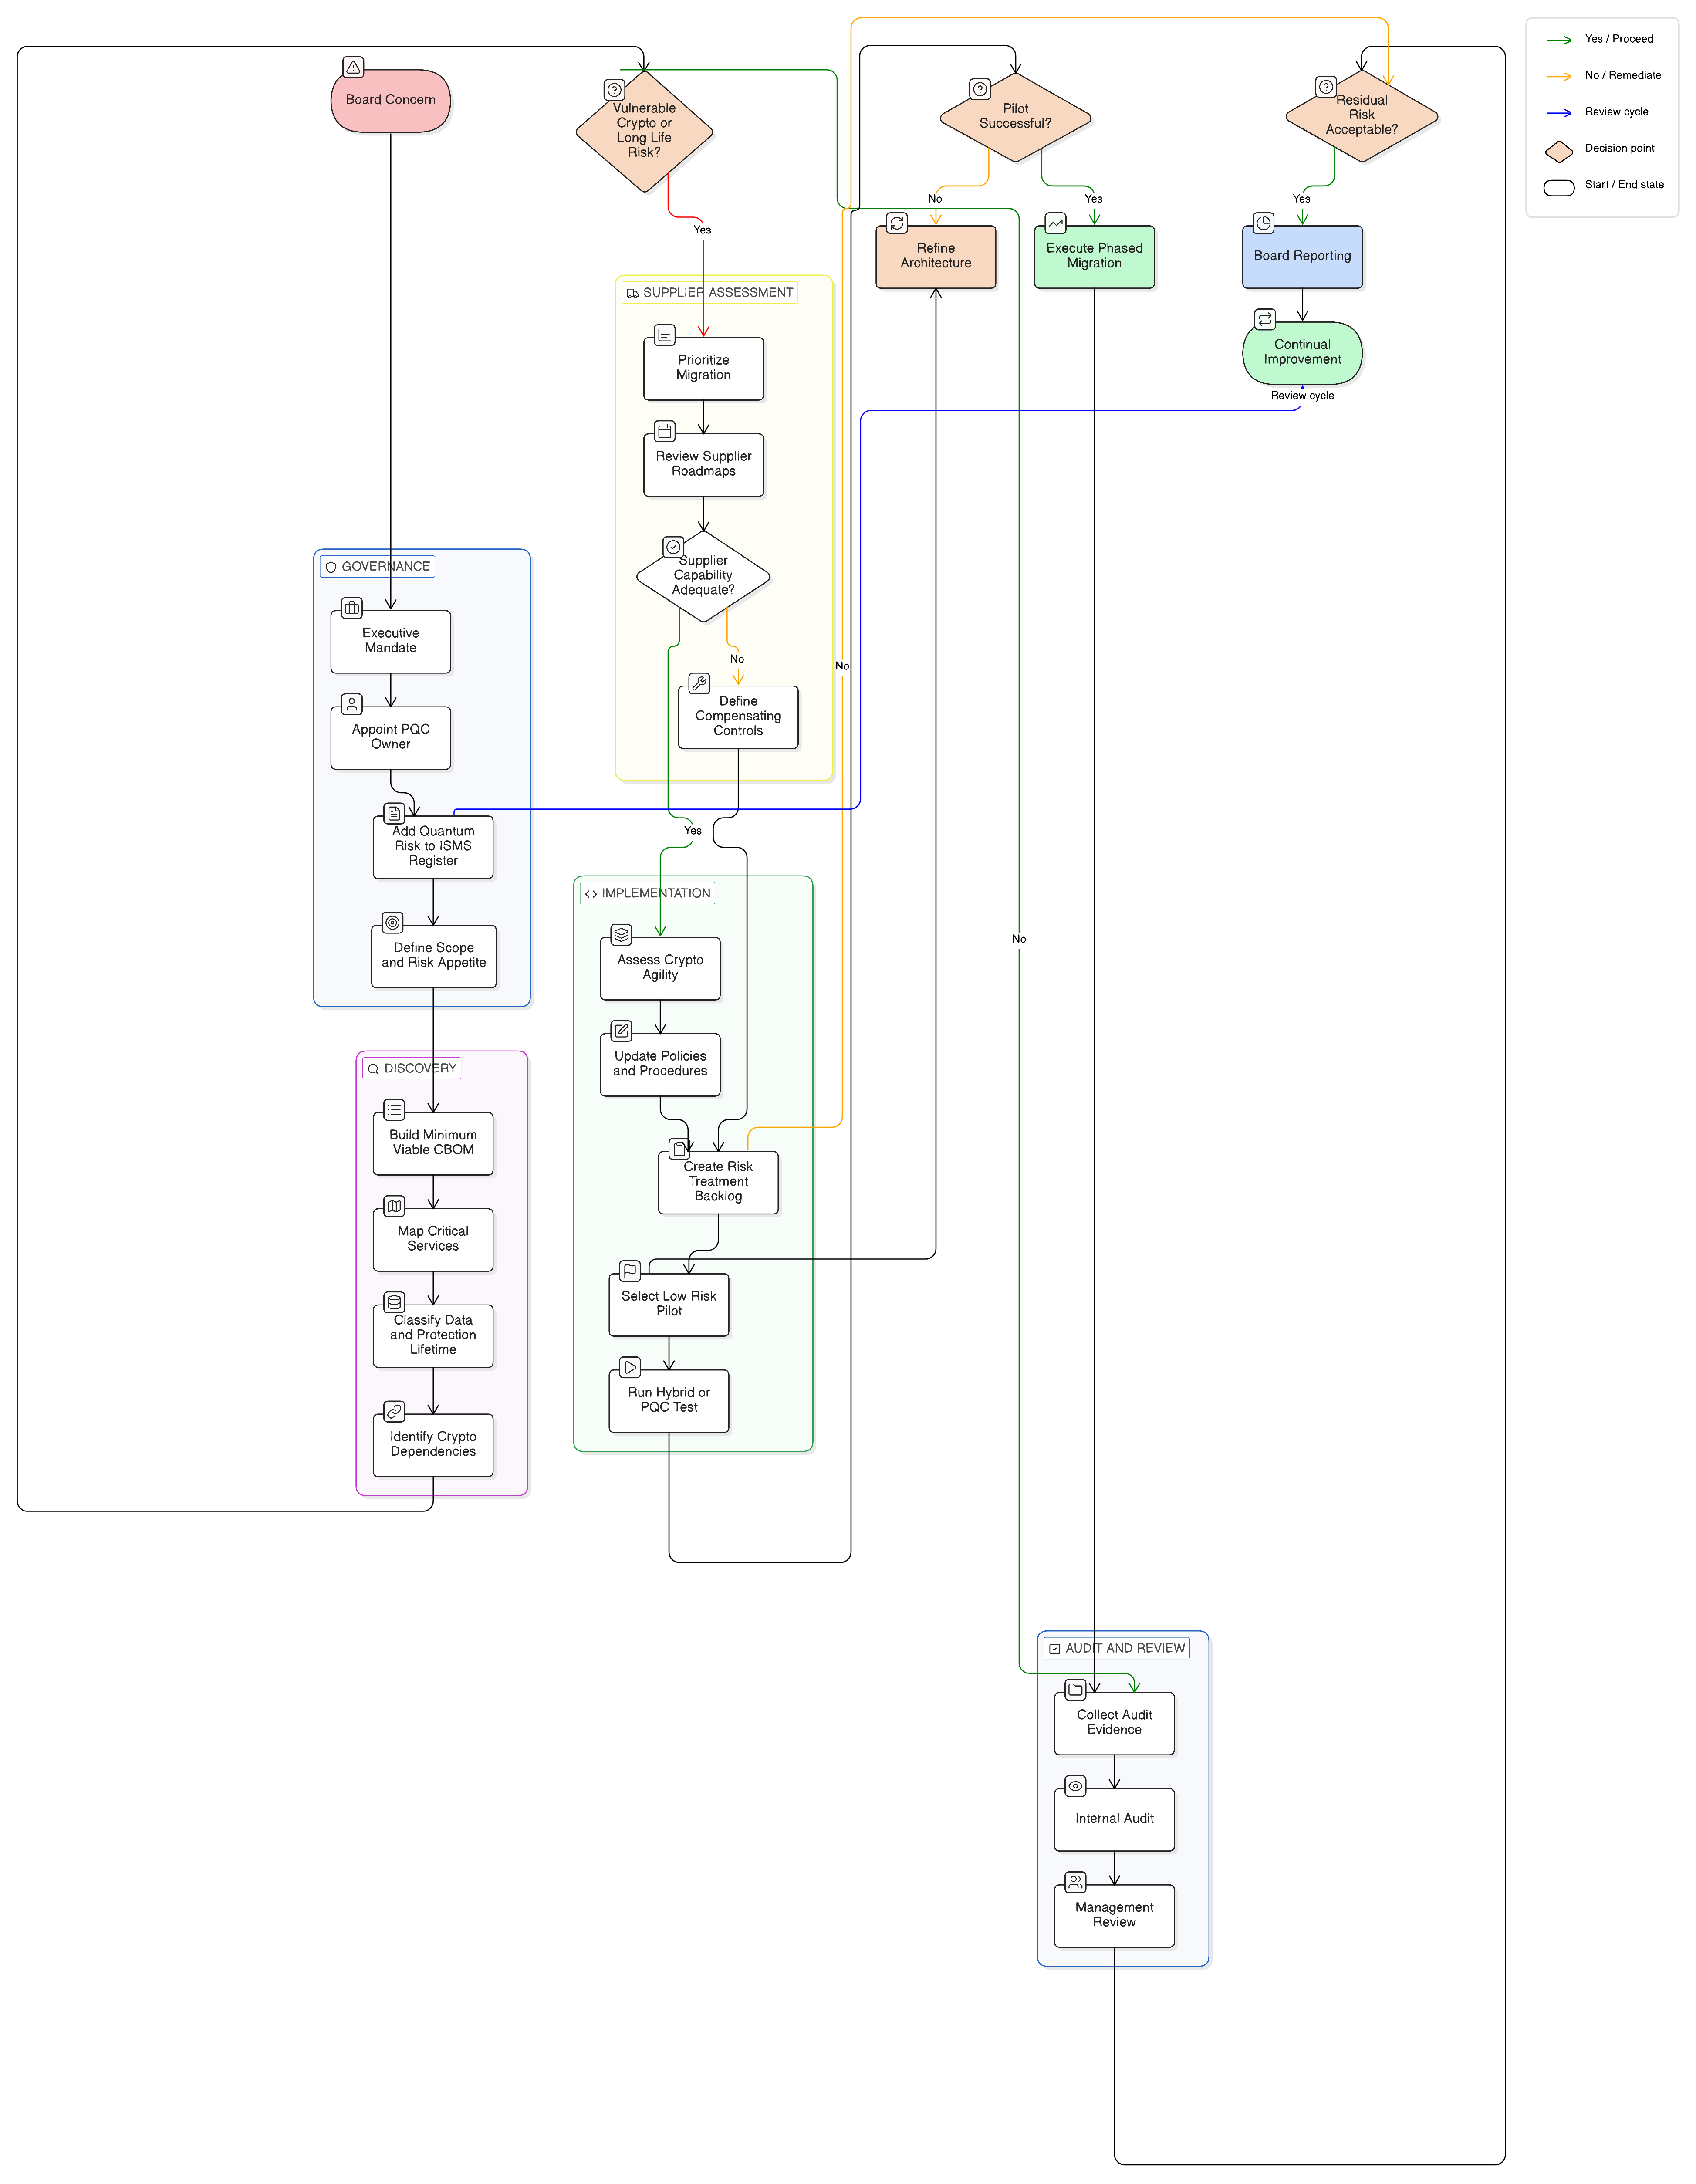
A practical CISO guide for building a quantum-ready cryptography migration plan using ISO/IEC 27001:2022, ISO/IEC 27002:2022, NIST PQC standards, and Clarysec’s audit-ready toolkits.
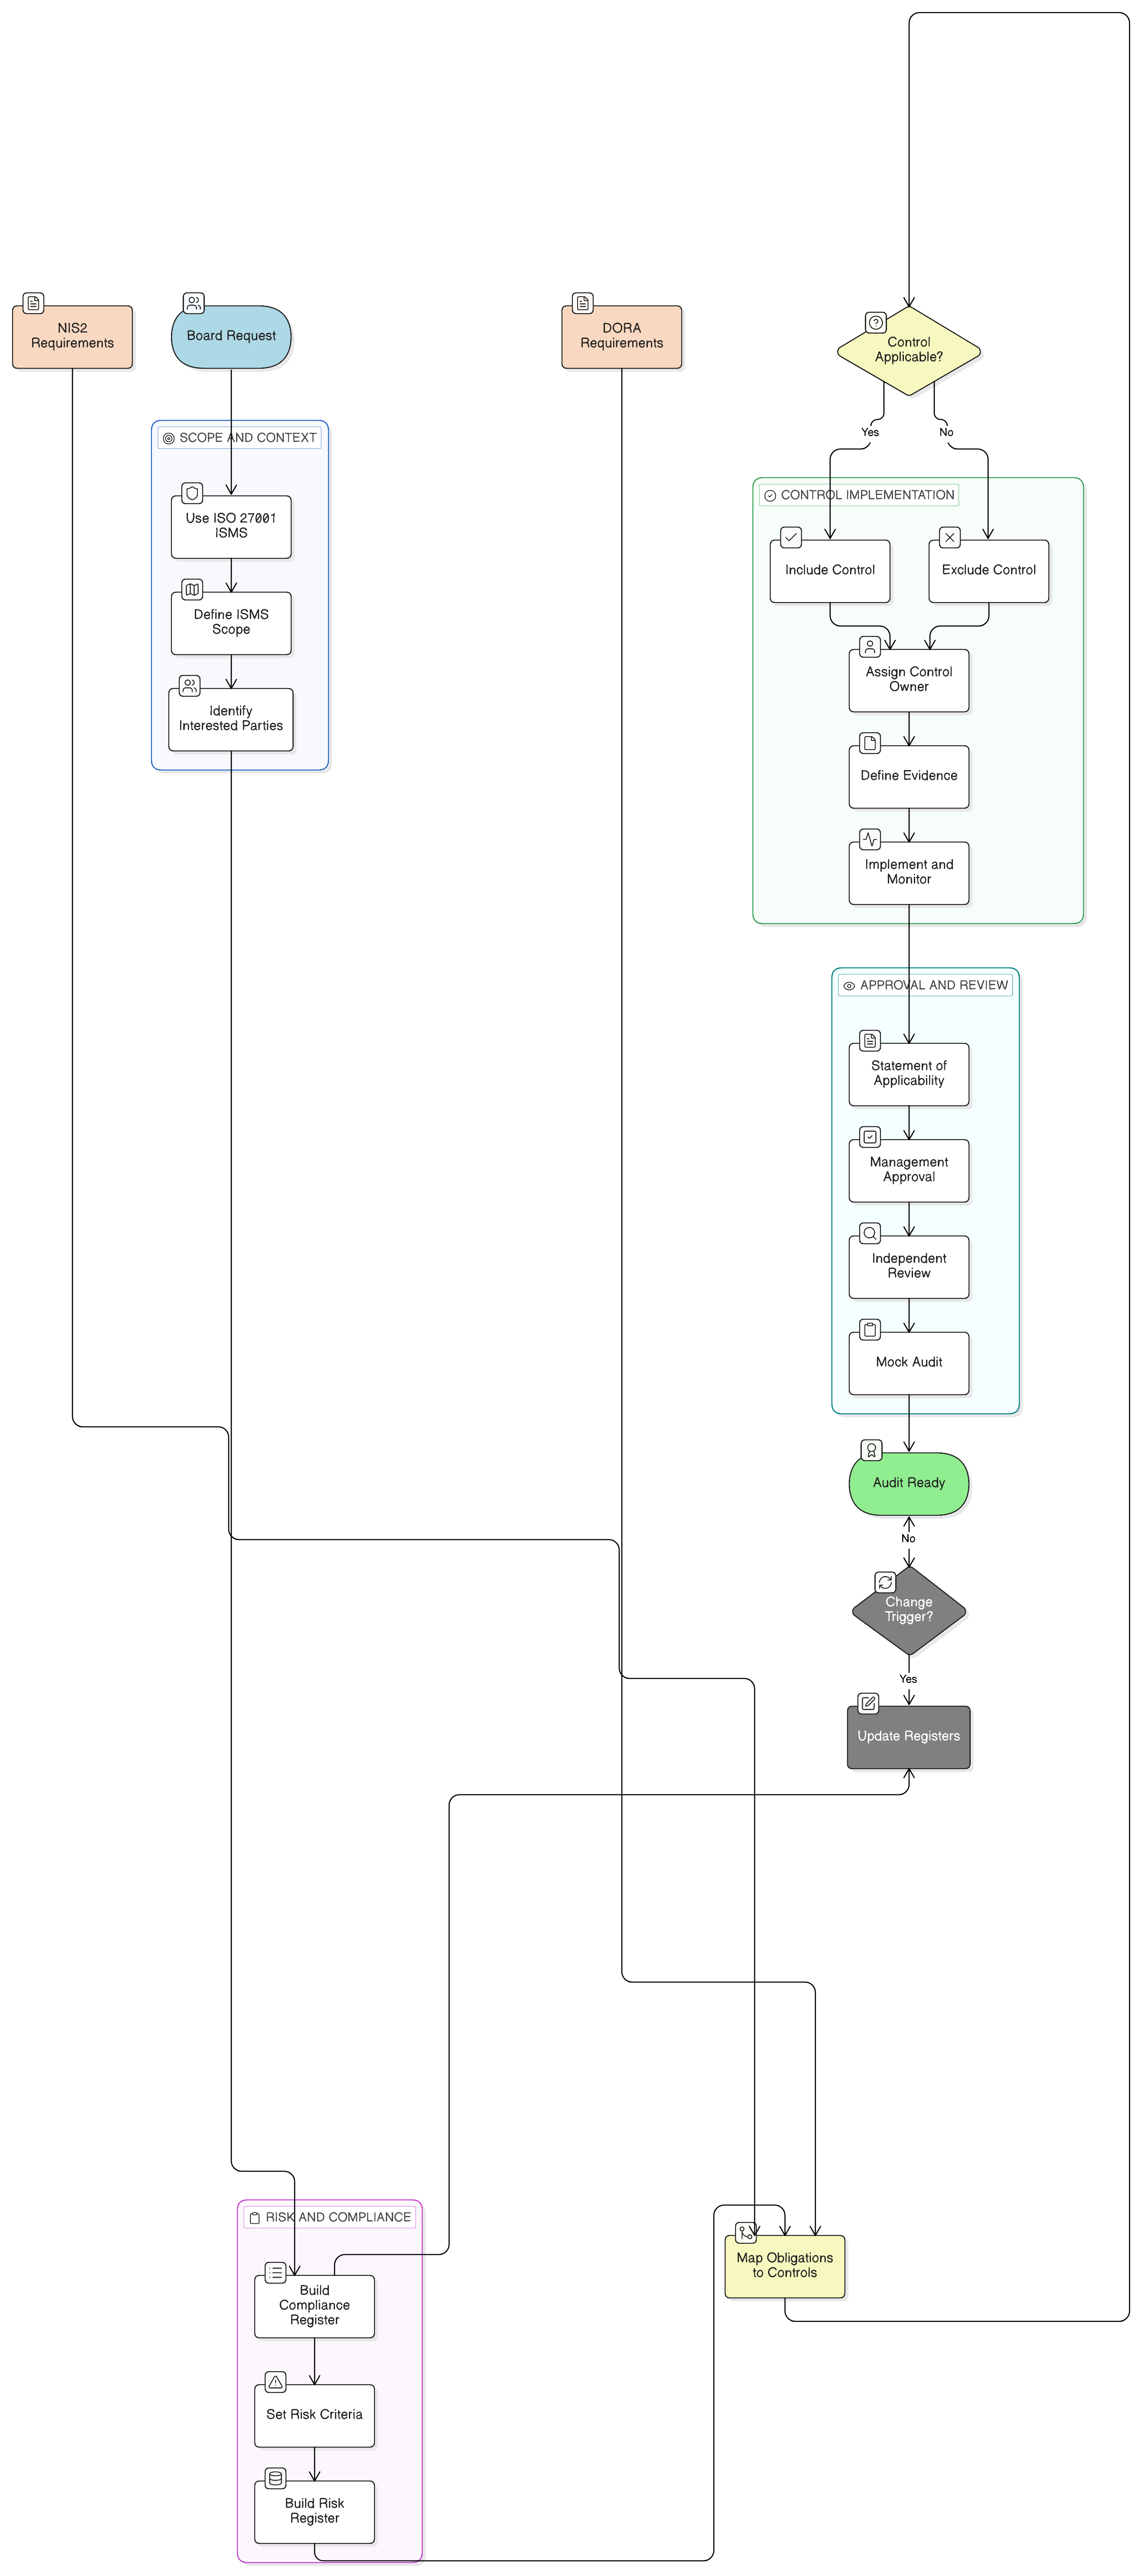
Learn how to use the ISO 27001 Statement of Applicability as an audit-ready bridge between NIS2, DORA, GDPR, risk treatment, suppliers, incident response, and evidence.
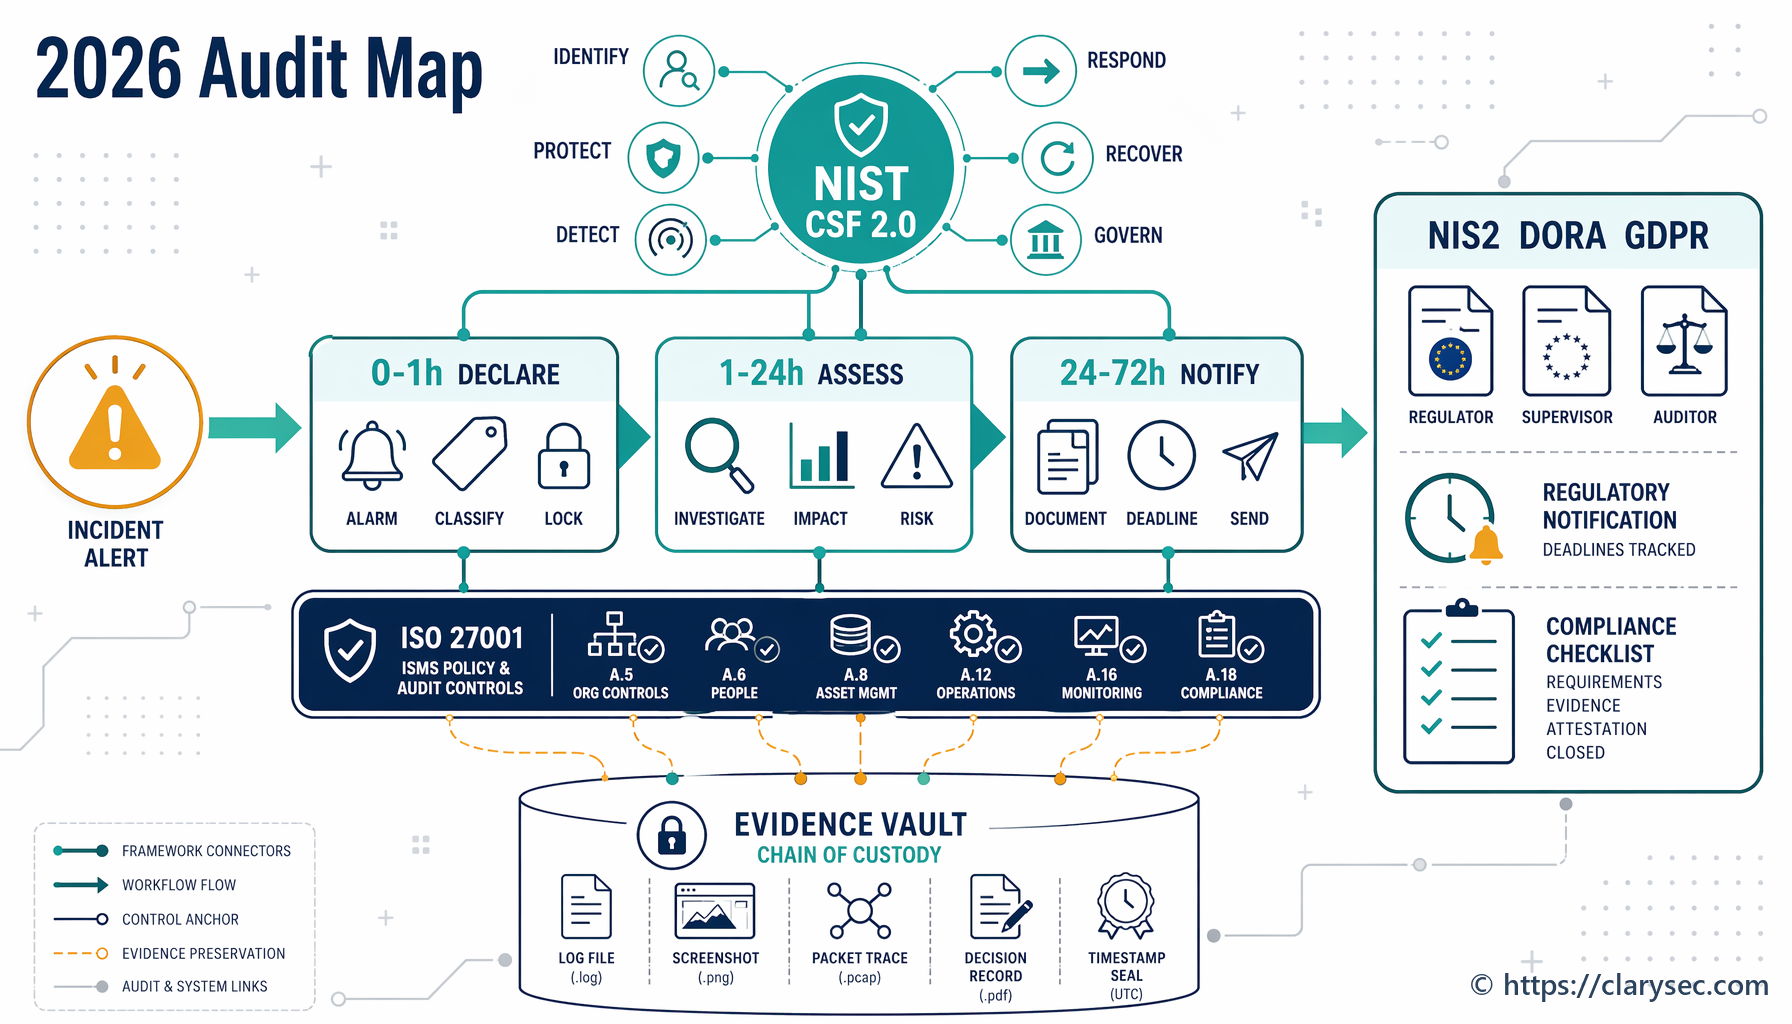
A practical CISO guide to mapping NIST SP 800-61 and NIST CSF 2.0 incident response to ISO/IEC 27001:2022, NIS2, DORA and GDPR evidence. Includes policy clauses, audit mappings, reporting timelines, evidence packs and Clarysec toolkit guidance.
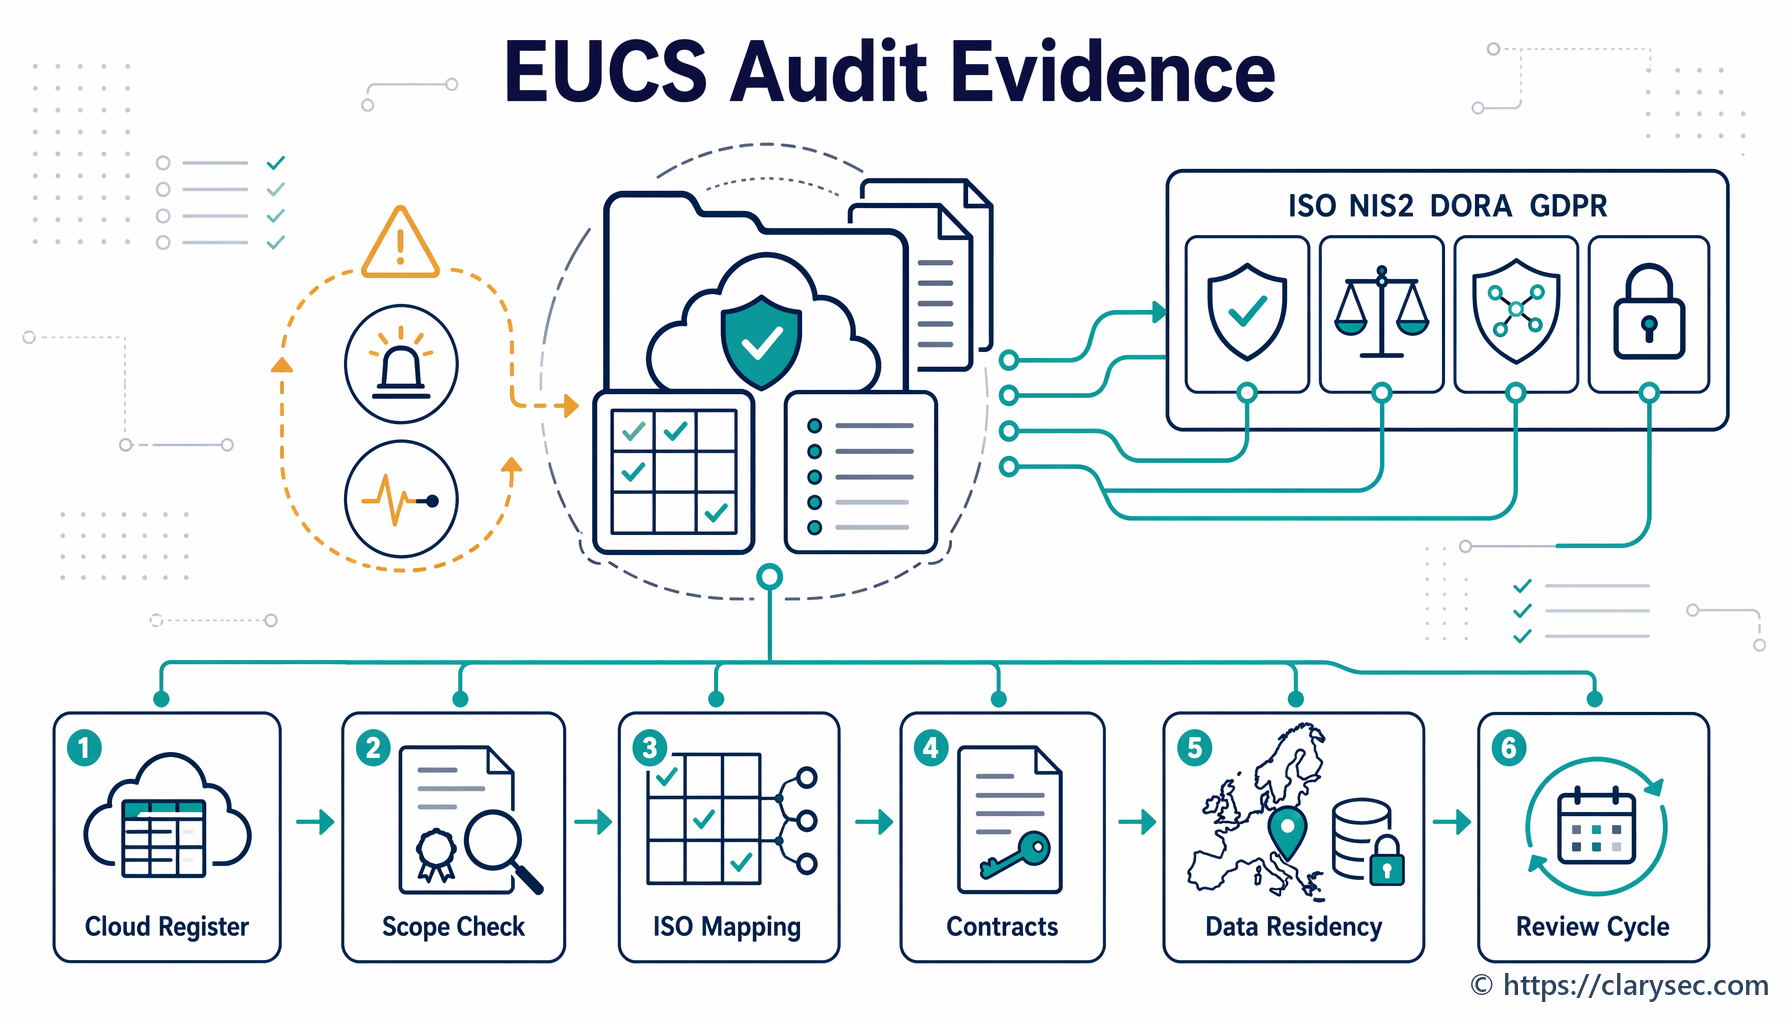
EUCS cloud certification can strengthen cloud provider assurance in 2026, but it must be mapped into your ISO 27001 ISMS, supplier risk process, contracts, incident playbooks and GDPR accountability evidence.
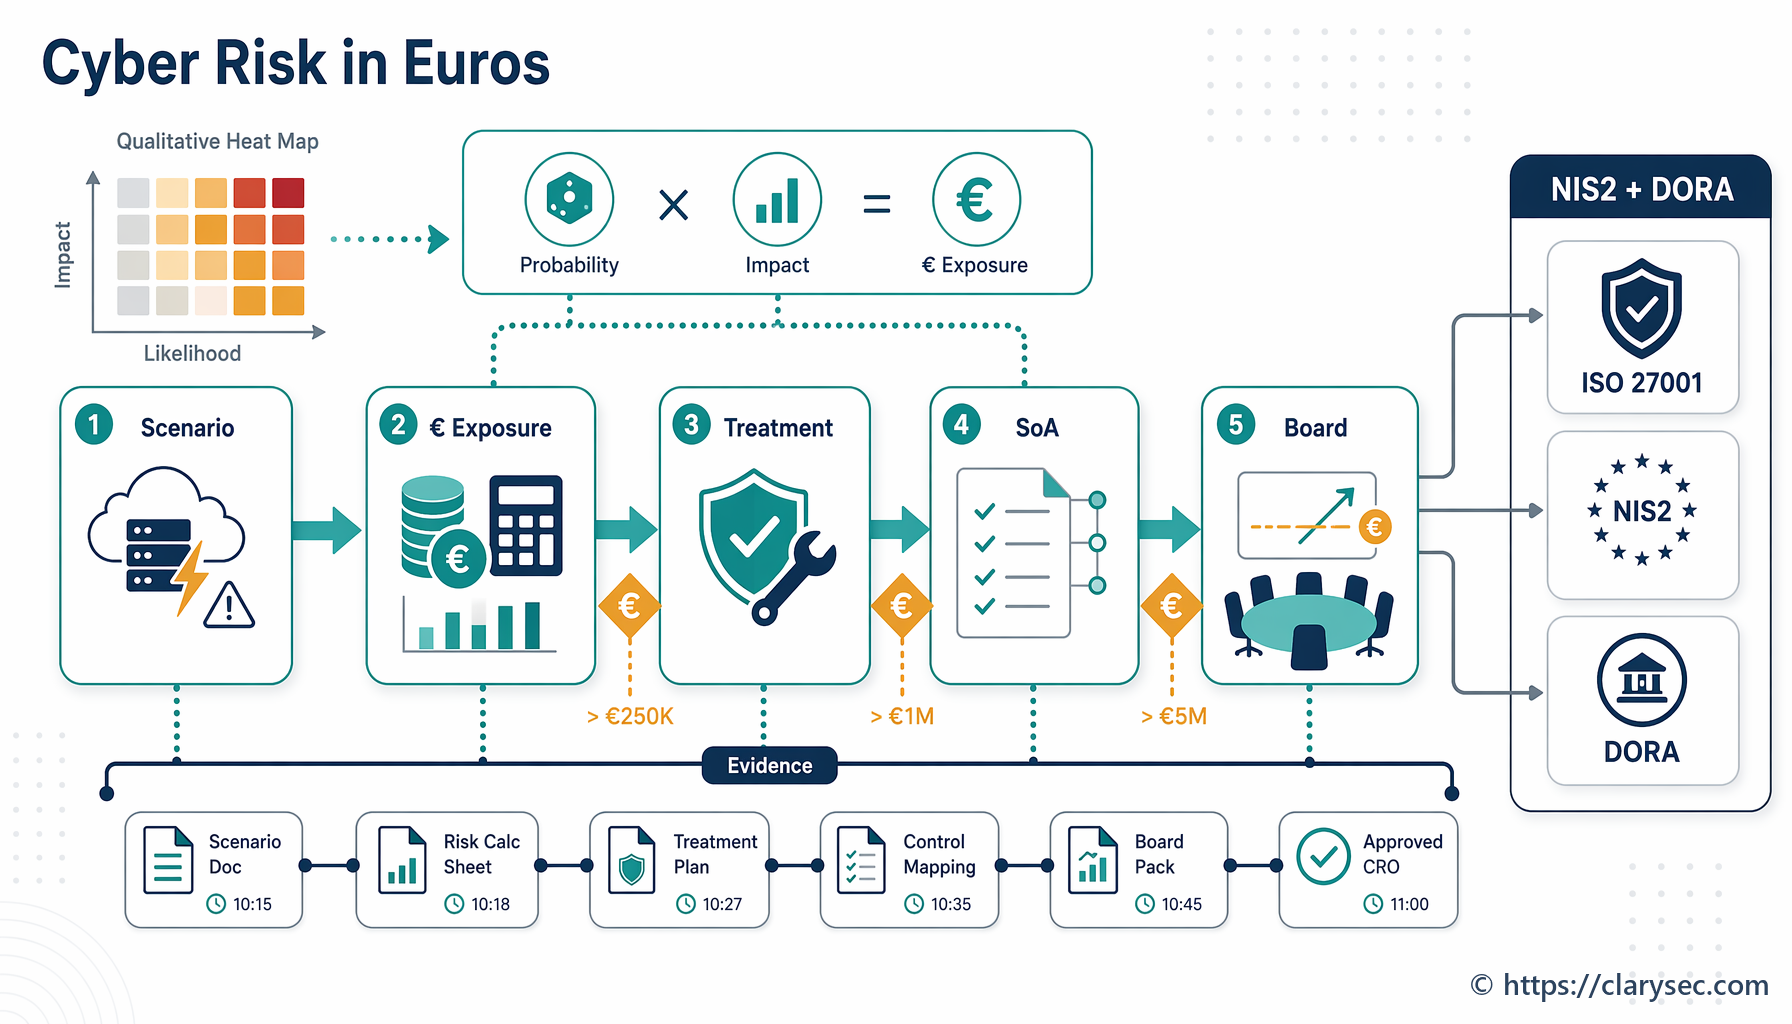
A practical guide for CISOs, compliance managers and boards on translating qualitative cyber risks into financial exposure, ISO 27001 evidence, NIS2 oversight and DORA ICT resilience decisions.