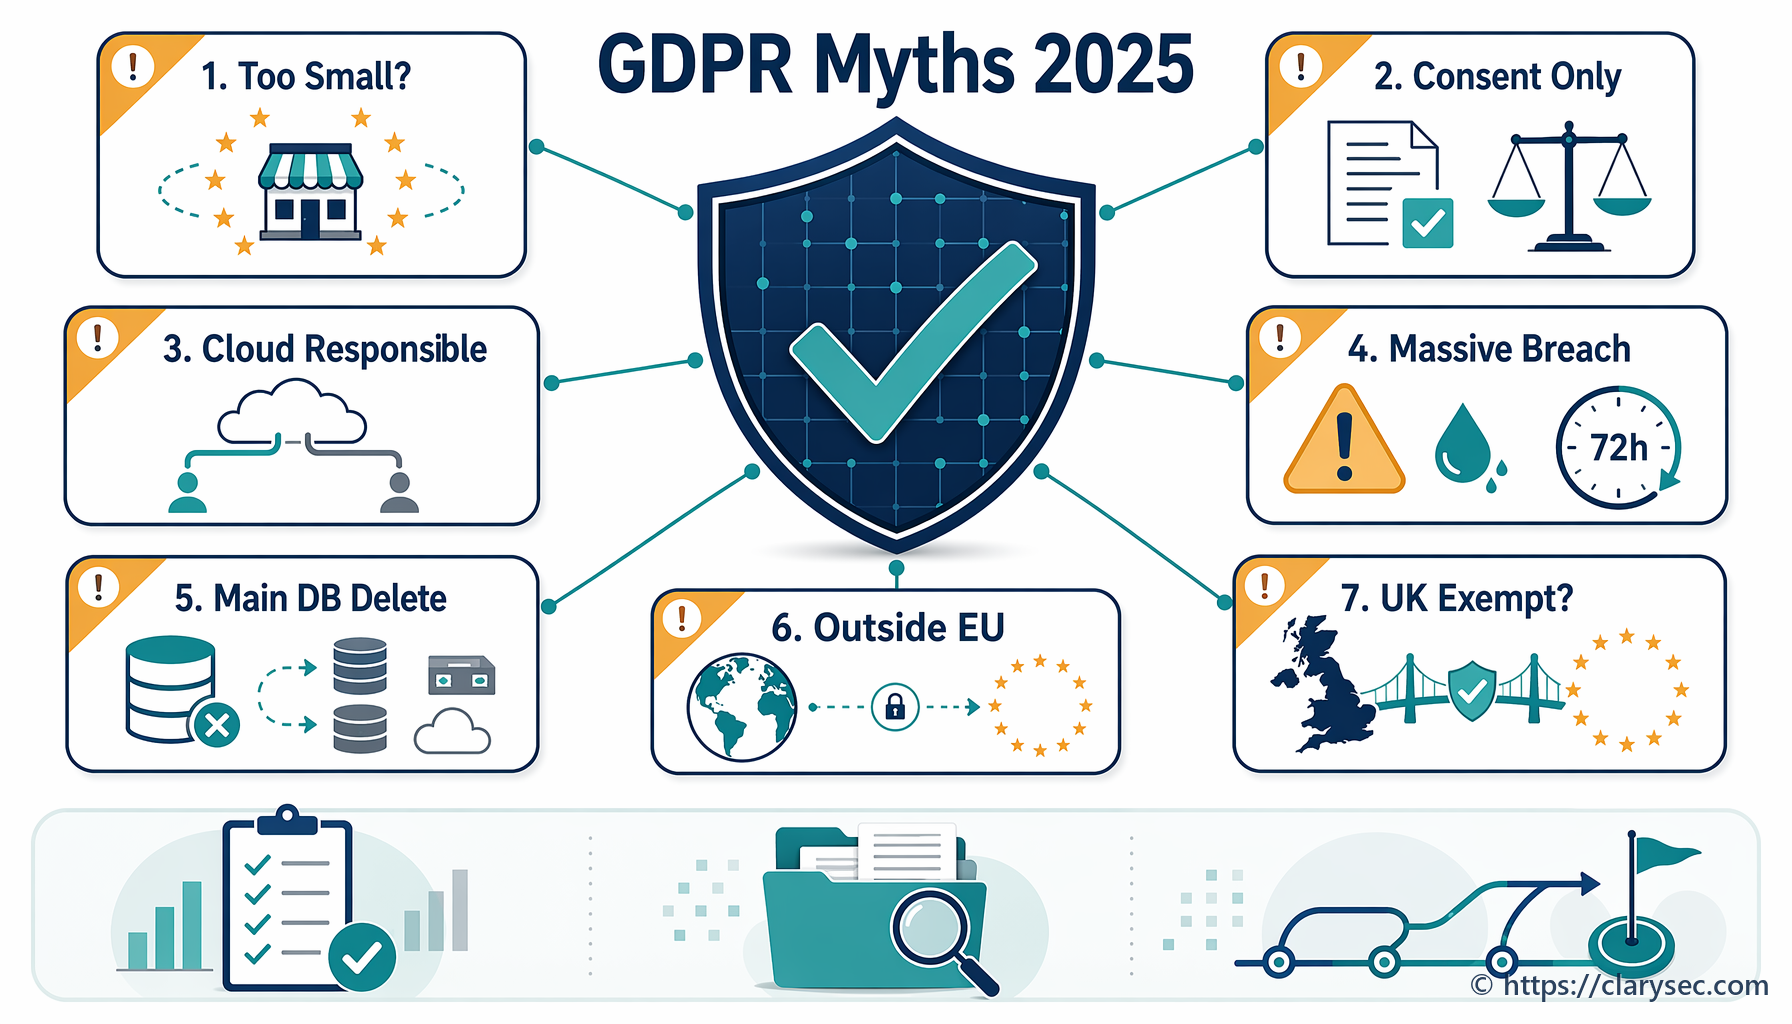
Debunking the Top 7 GDPR Myths in 2025: A CISO's Guide
Uncover the truth behind the top 7 GDPR myths of 2025. Our expert guide debunks common misconceptions about consent, data breaches, and compliance.
Articles tagged with "Data Protection"
Uncover the truth behind the top 7 GDPR myths of 2025. Our expert guide debunks common misconceptions about consent, data breaches, and compliance.
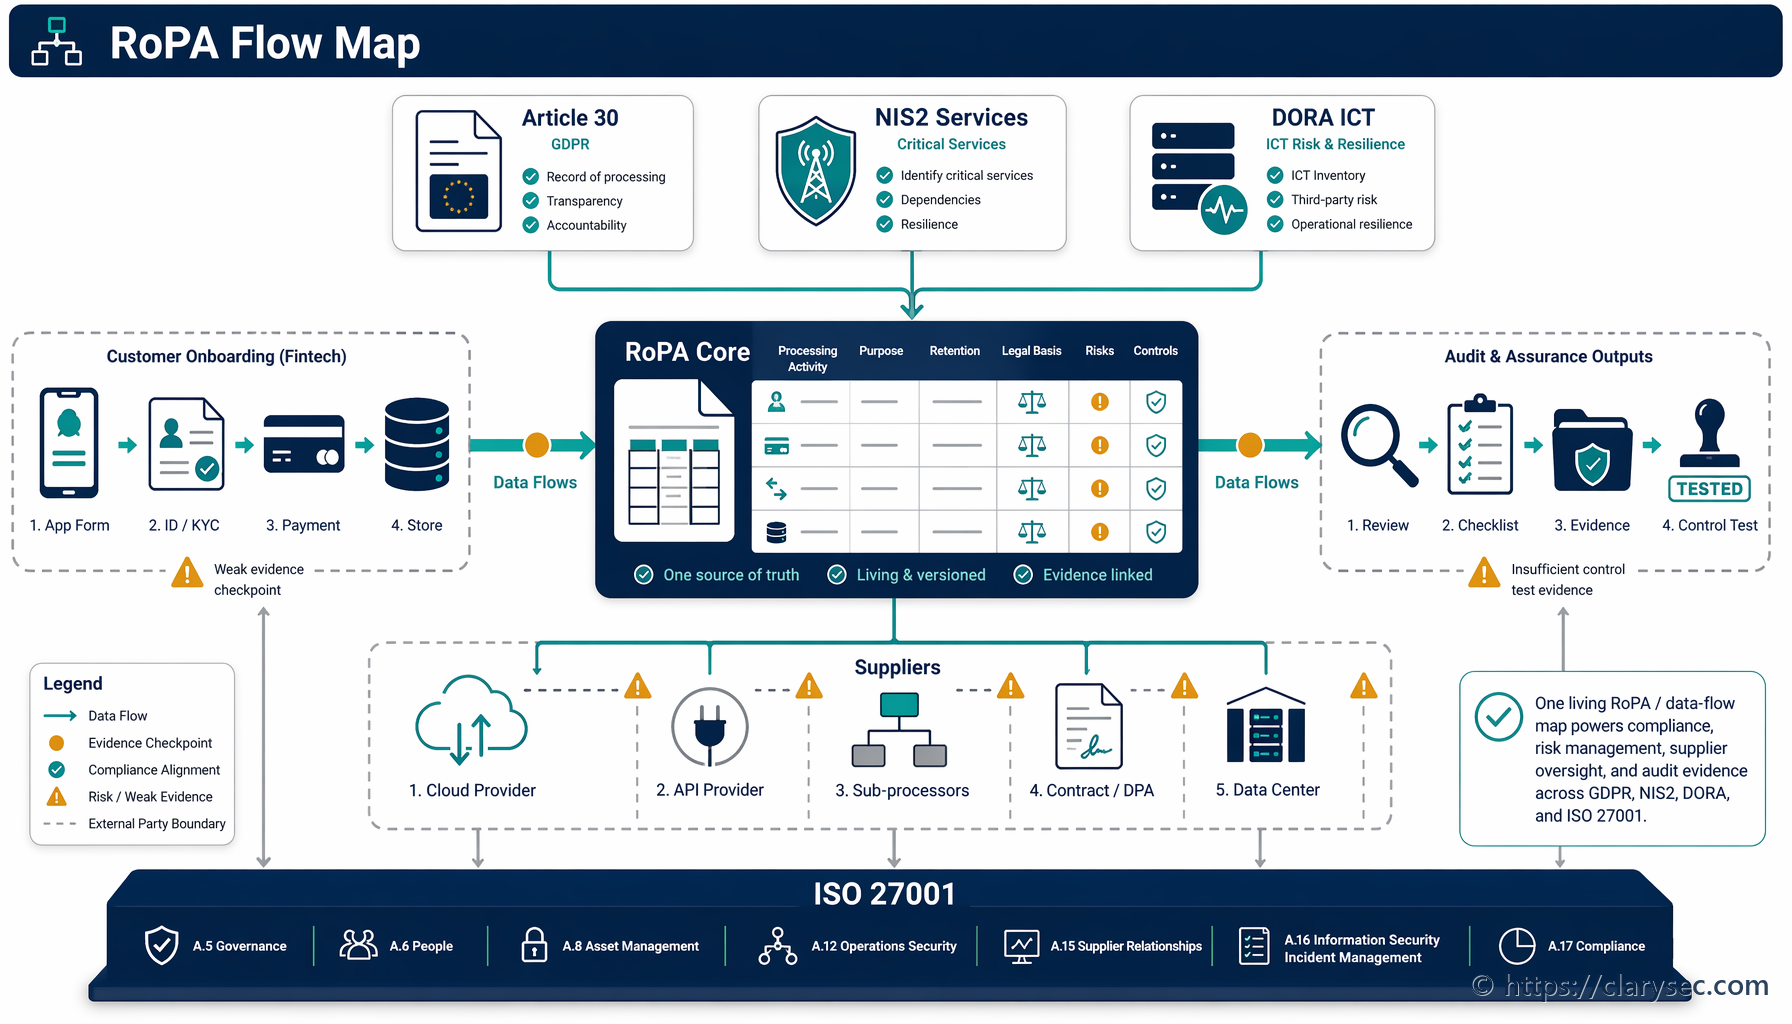
A practical 2026 guide for turning RoPA and data flow mapping into a unified evidence layer for GDPR Article 30, NIS2 critical services, DORA ICT dependencies and ISO/IEC 27001:2022 audits.
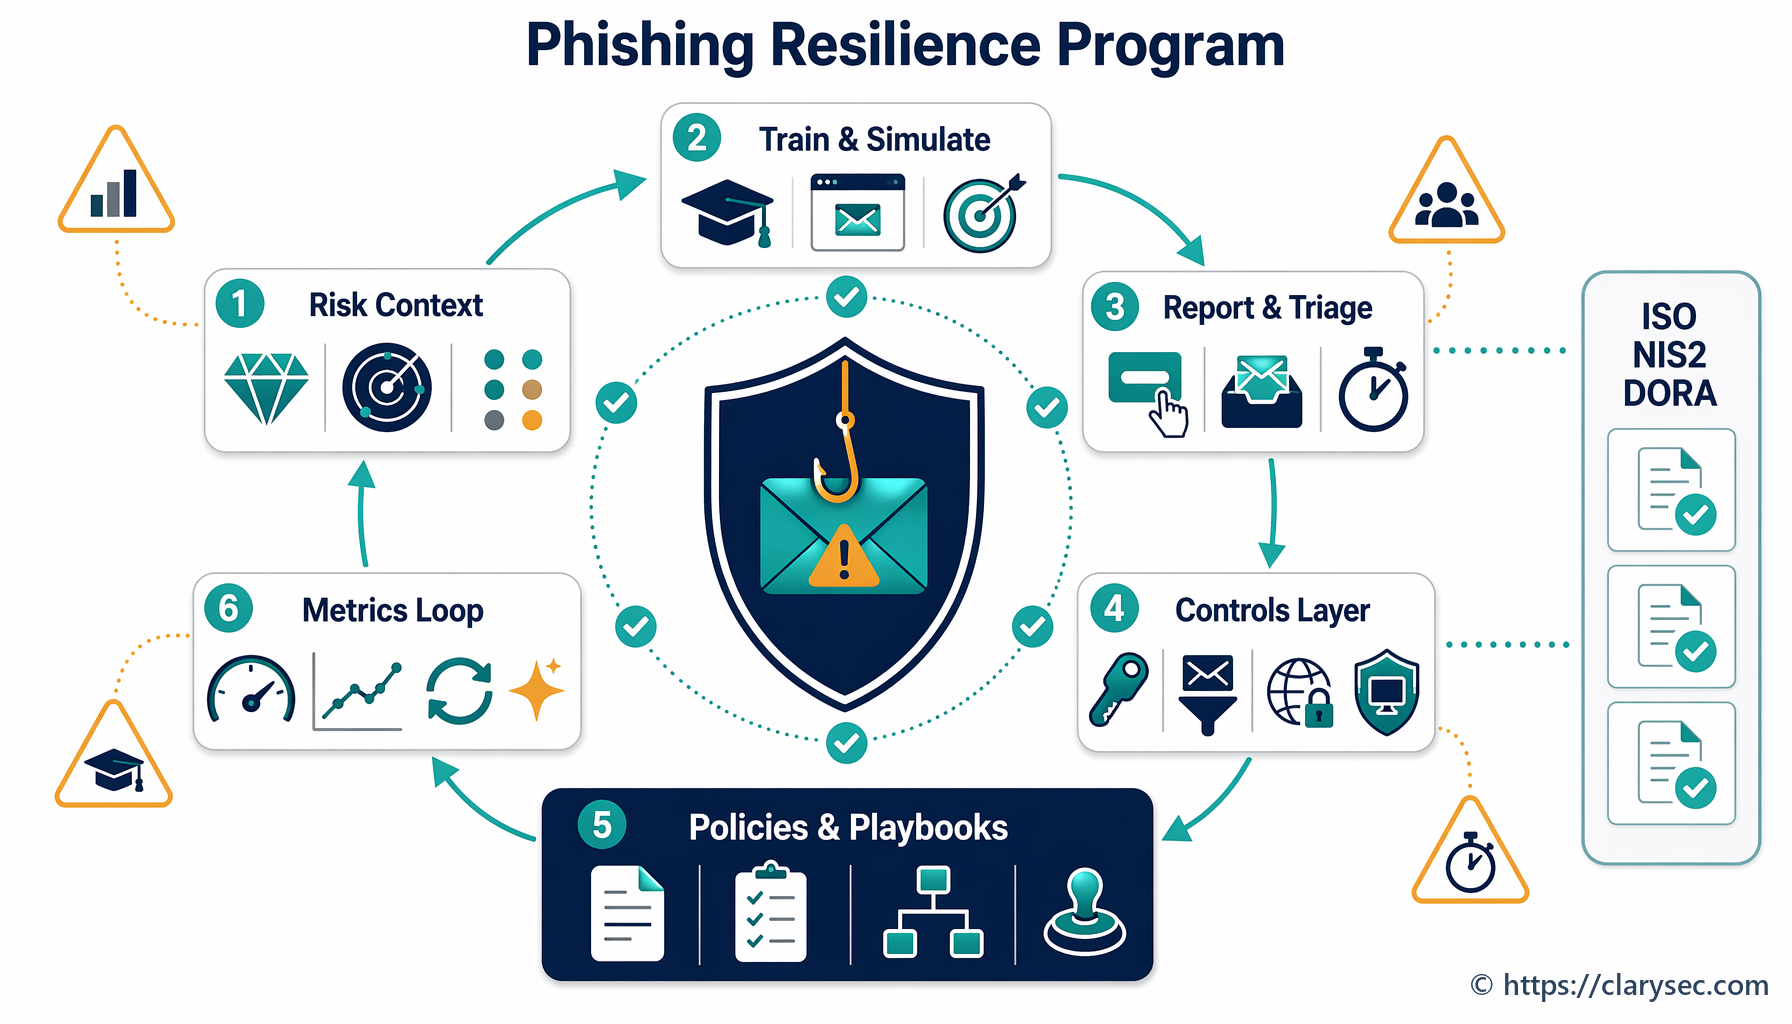
A practical guide for CISOs and SME owners on building a robust phishing resilience program aligned with ISO 27001:2022, NIS2, and DORA requirements.
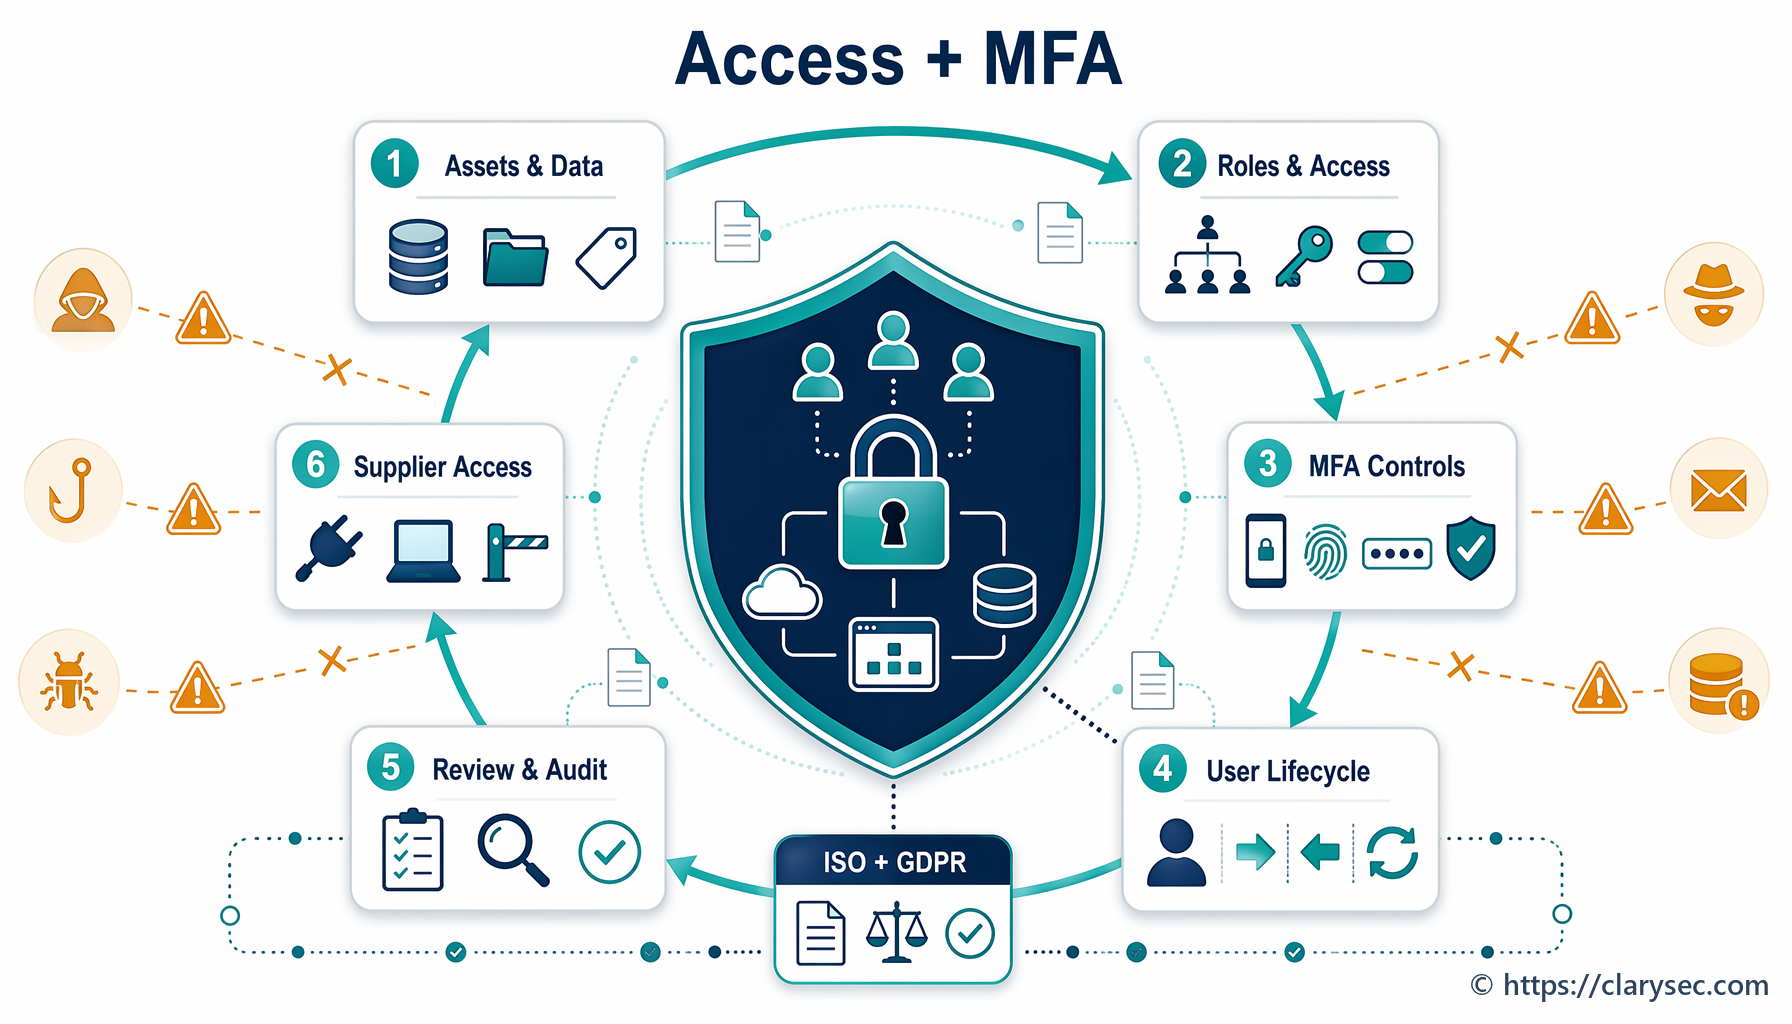
How SMEs can implement access control and MFA in line with ISO 27001:2022 A.8.2, A.8.3 and GDPR Article 32, reducing risk and ensuring regulatory compliance.
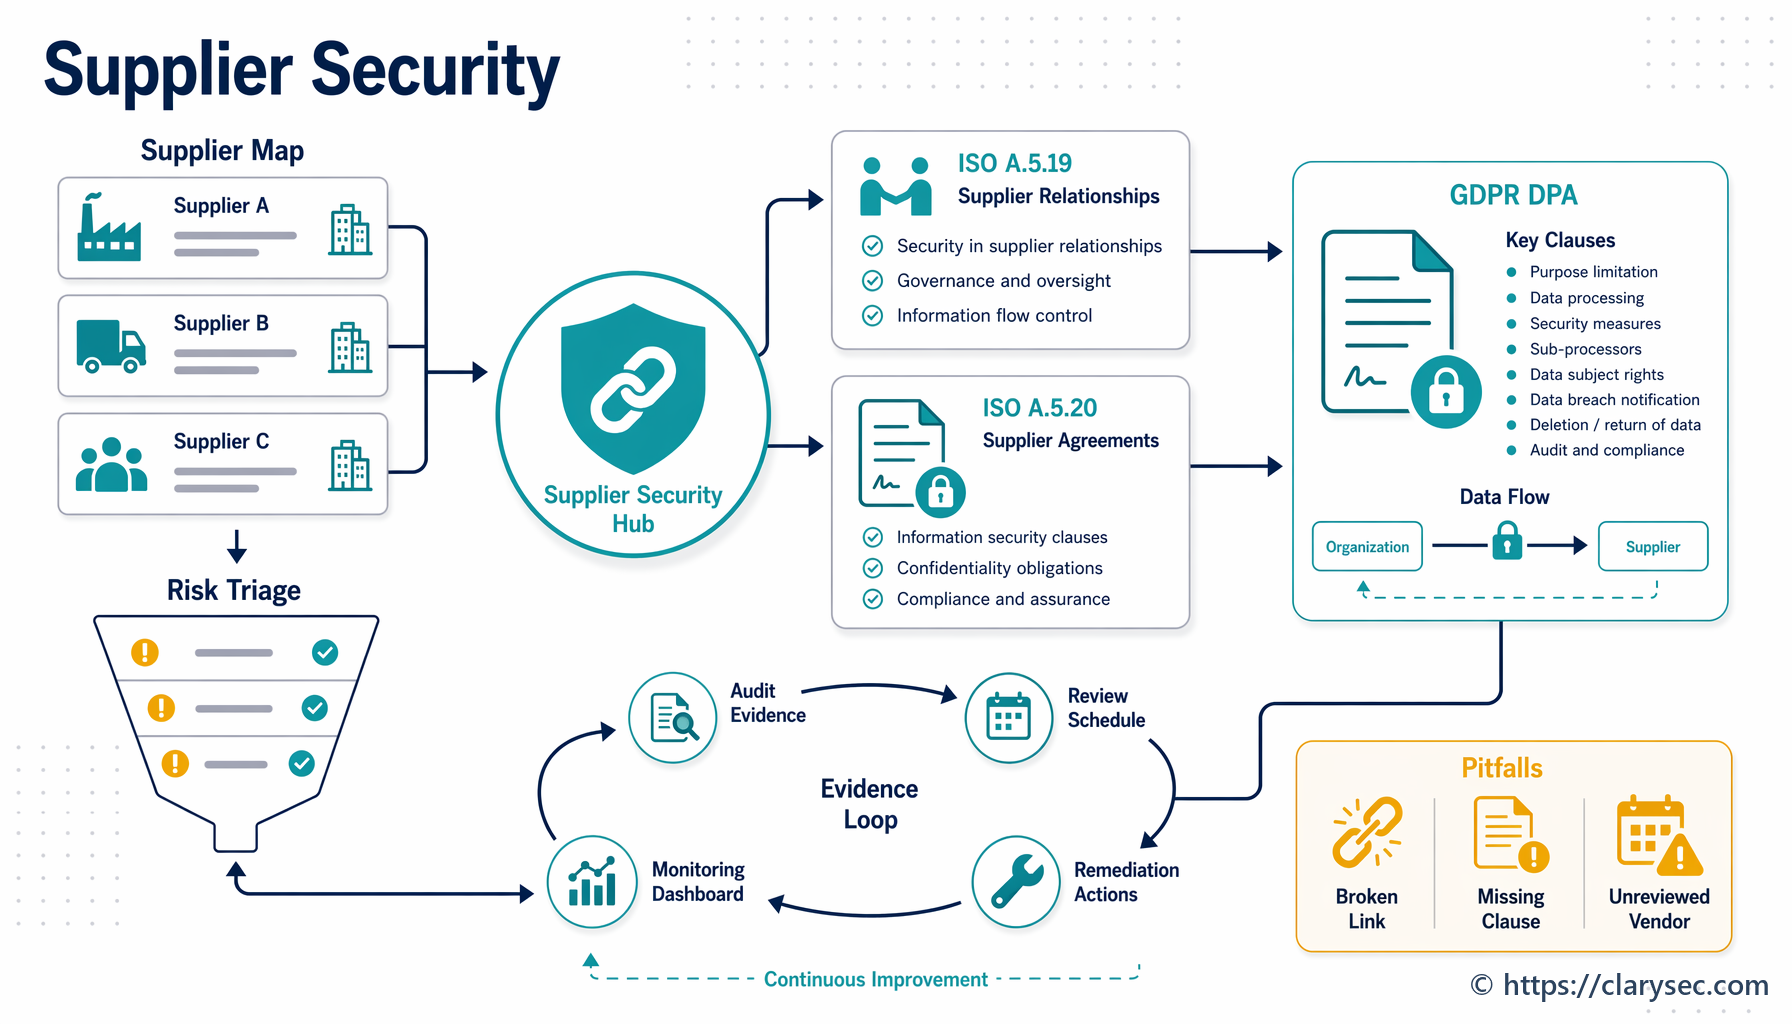
Learn to manage supplier security risks using ISO 27001:2022 controls A.5.19 and A.5.20, ensuring your DPAs and contracts meet stringent GDPR requirements.
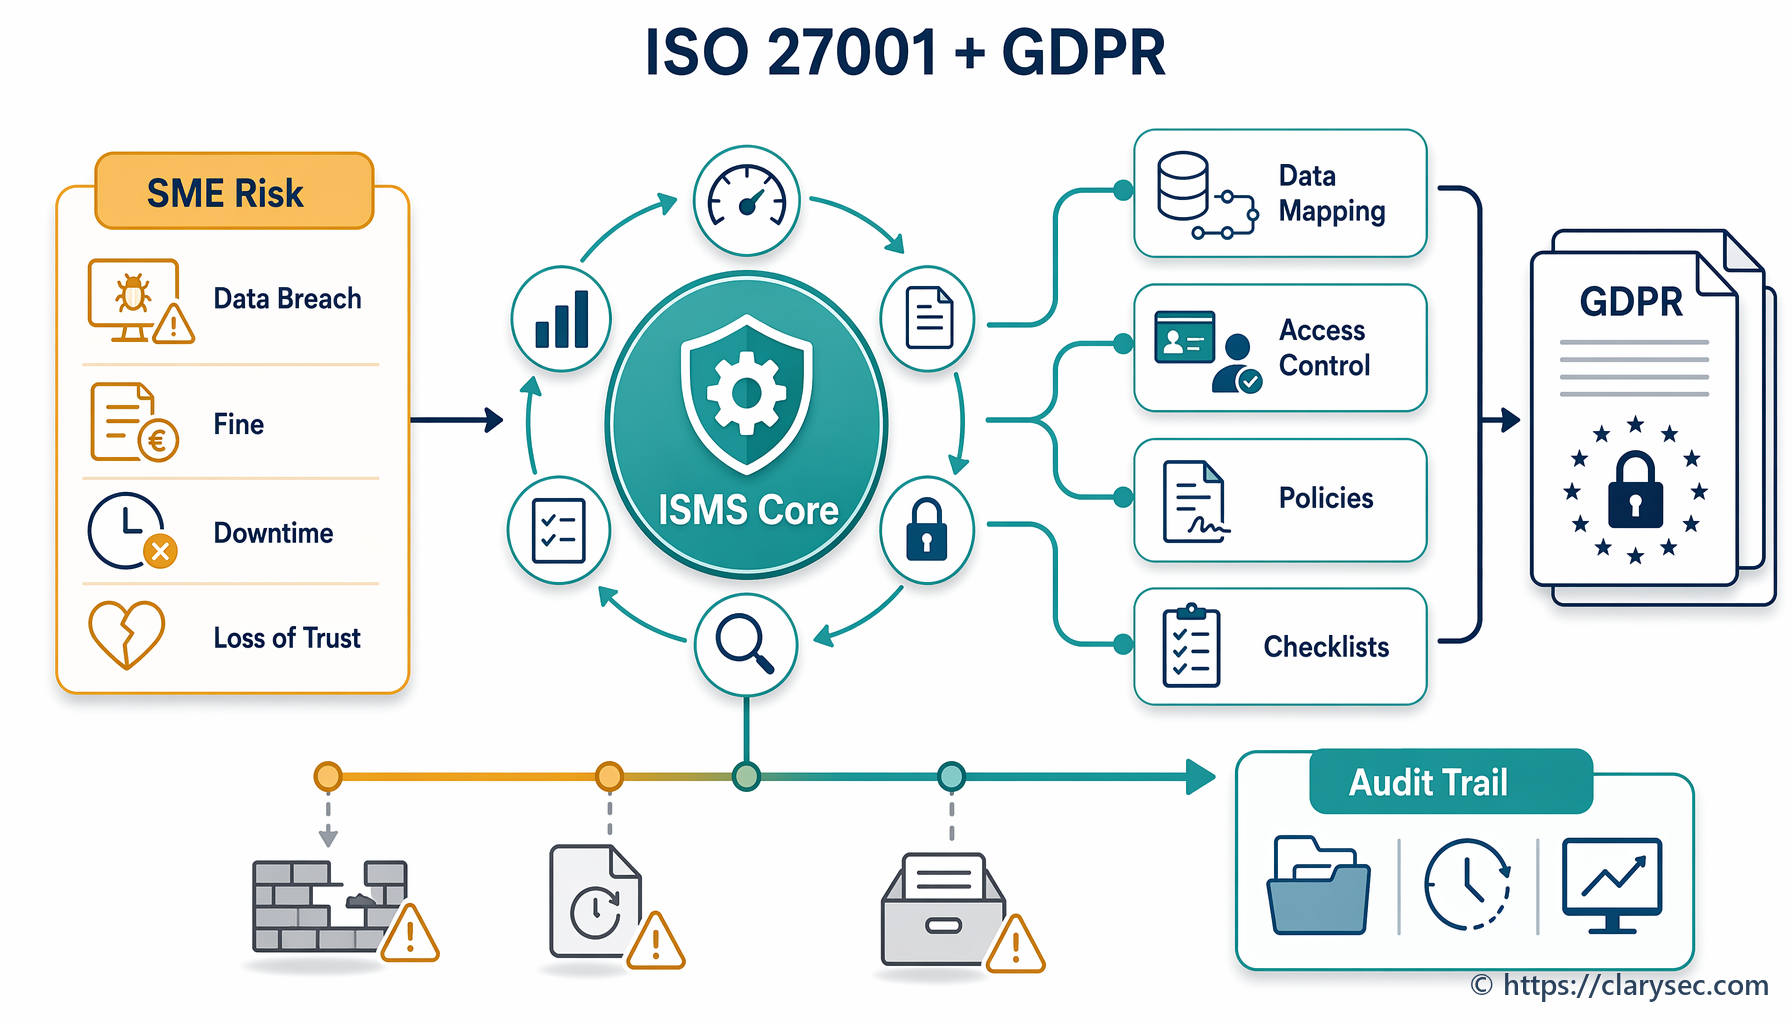
Learn how SMEs can leverage the ISO/IEC 27001:2022 framework to build a robust ISMS that systematically addresses GDPR requirements for data protection.
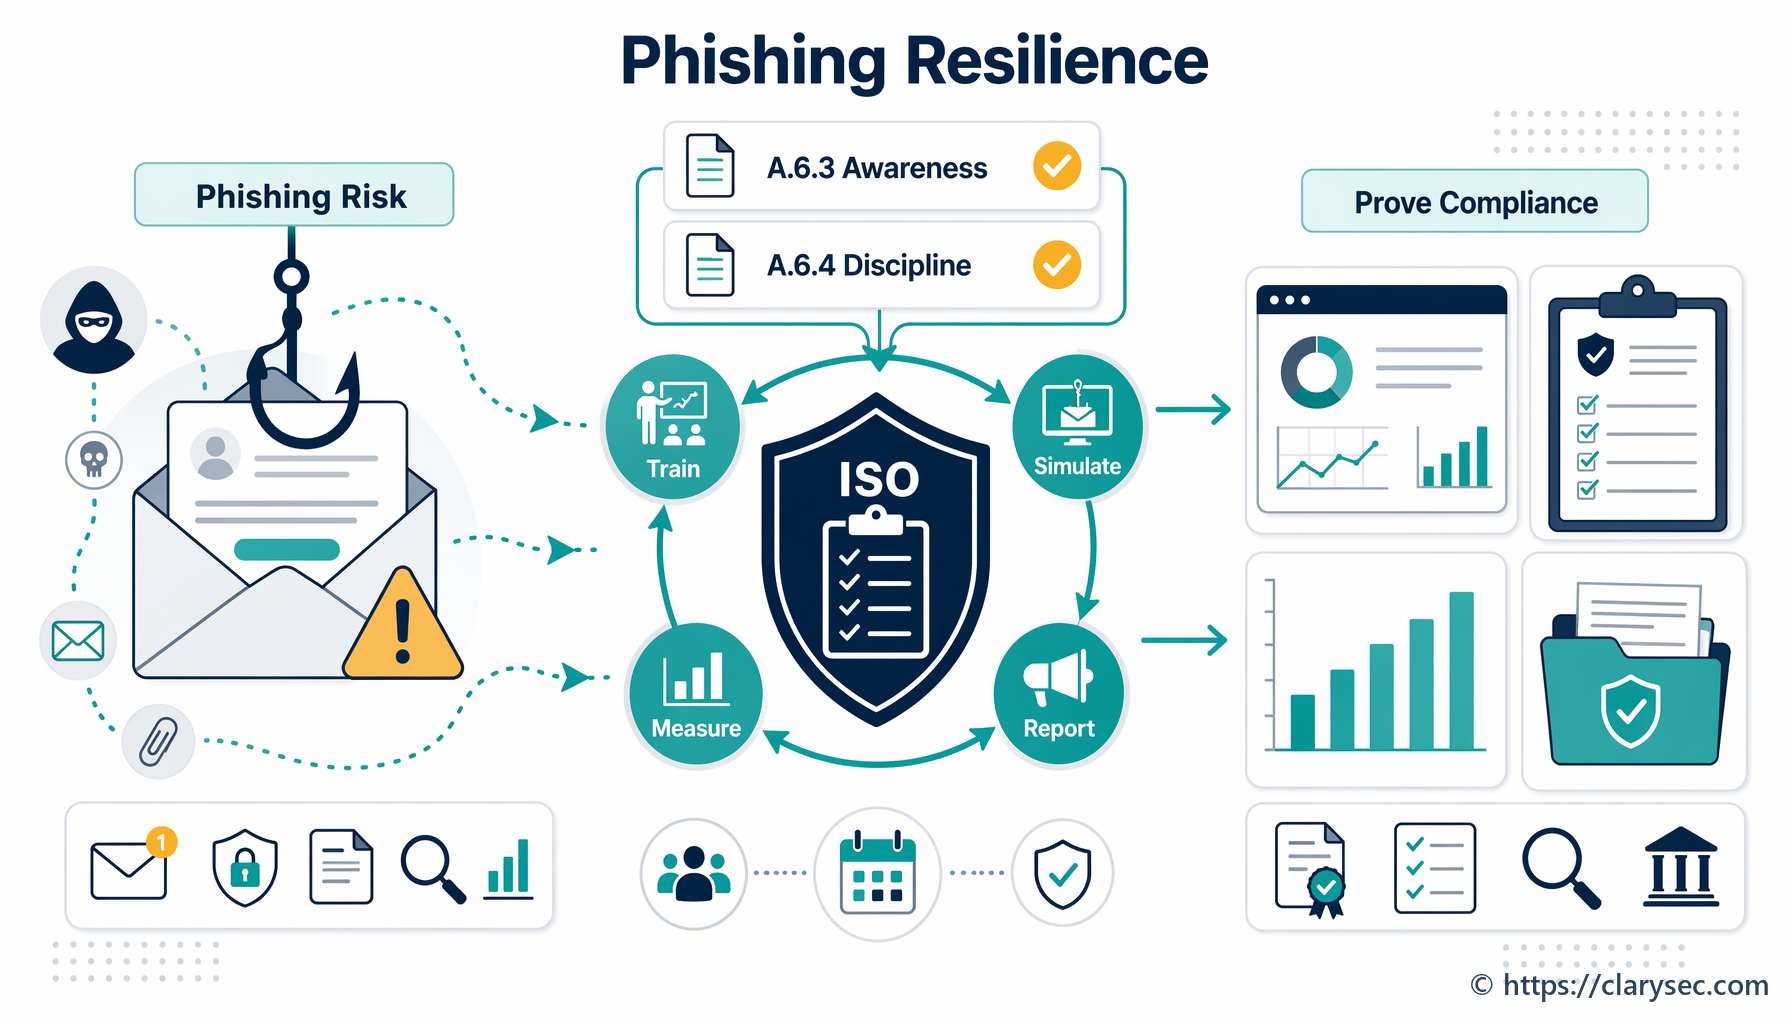
Learn how to build a measurable phishing resilience program using ISO 27001:2022 controls A.6.3 and A.6.4 to reduce human risk and prove compliance.
ISO 27001 is the international standard for information security management systems (ISMS). This comprehensive guide will walk you through the essential steps to implement ISO 27001 in your organization, from initial planning to certification.
ISO 27001 provides a systematic approach to managing sensitive company information and ensuring it remains secure. It includes people, processes, and IT systems by applying a risk management process.
Start by conducting a thorough gap analysis to understand your current security posture: