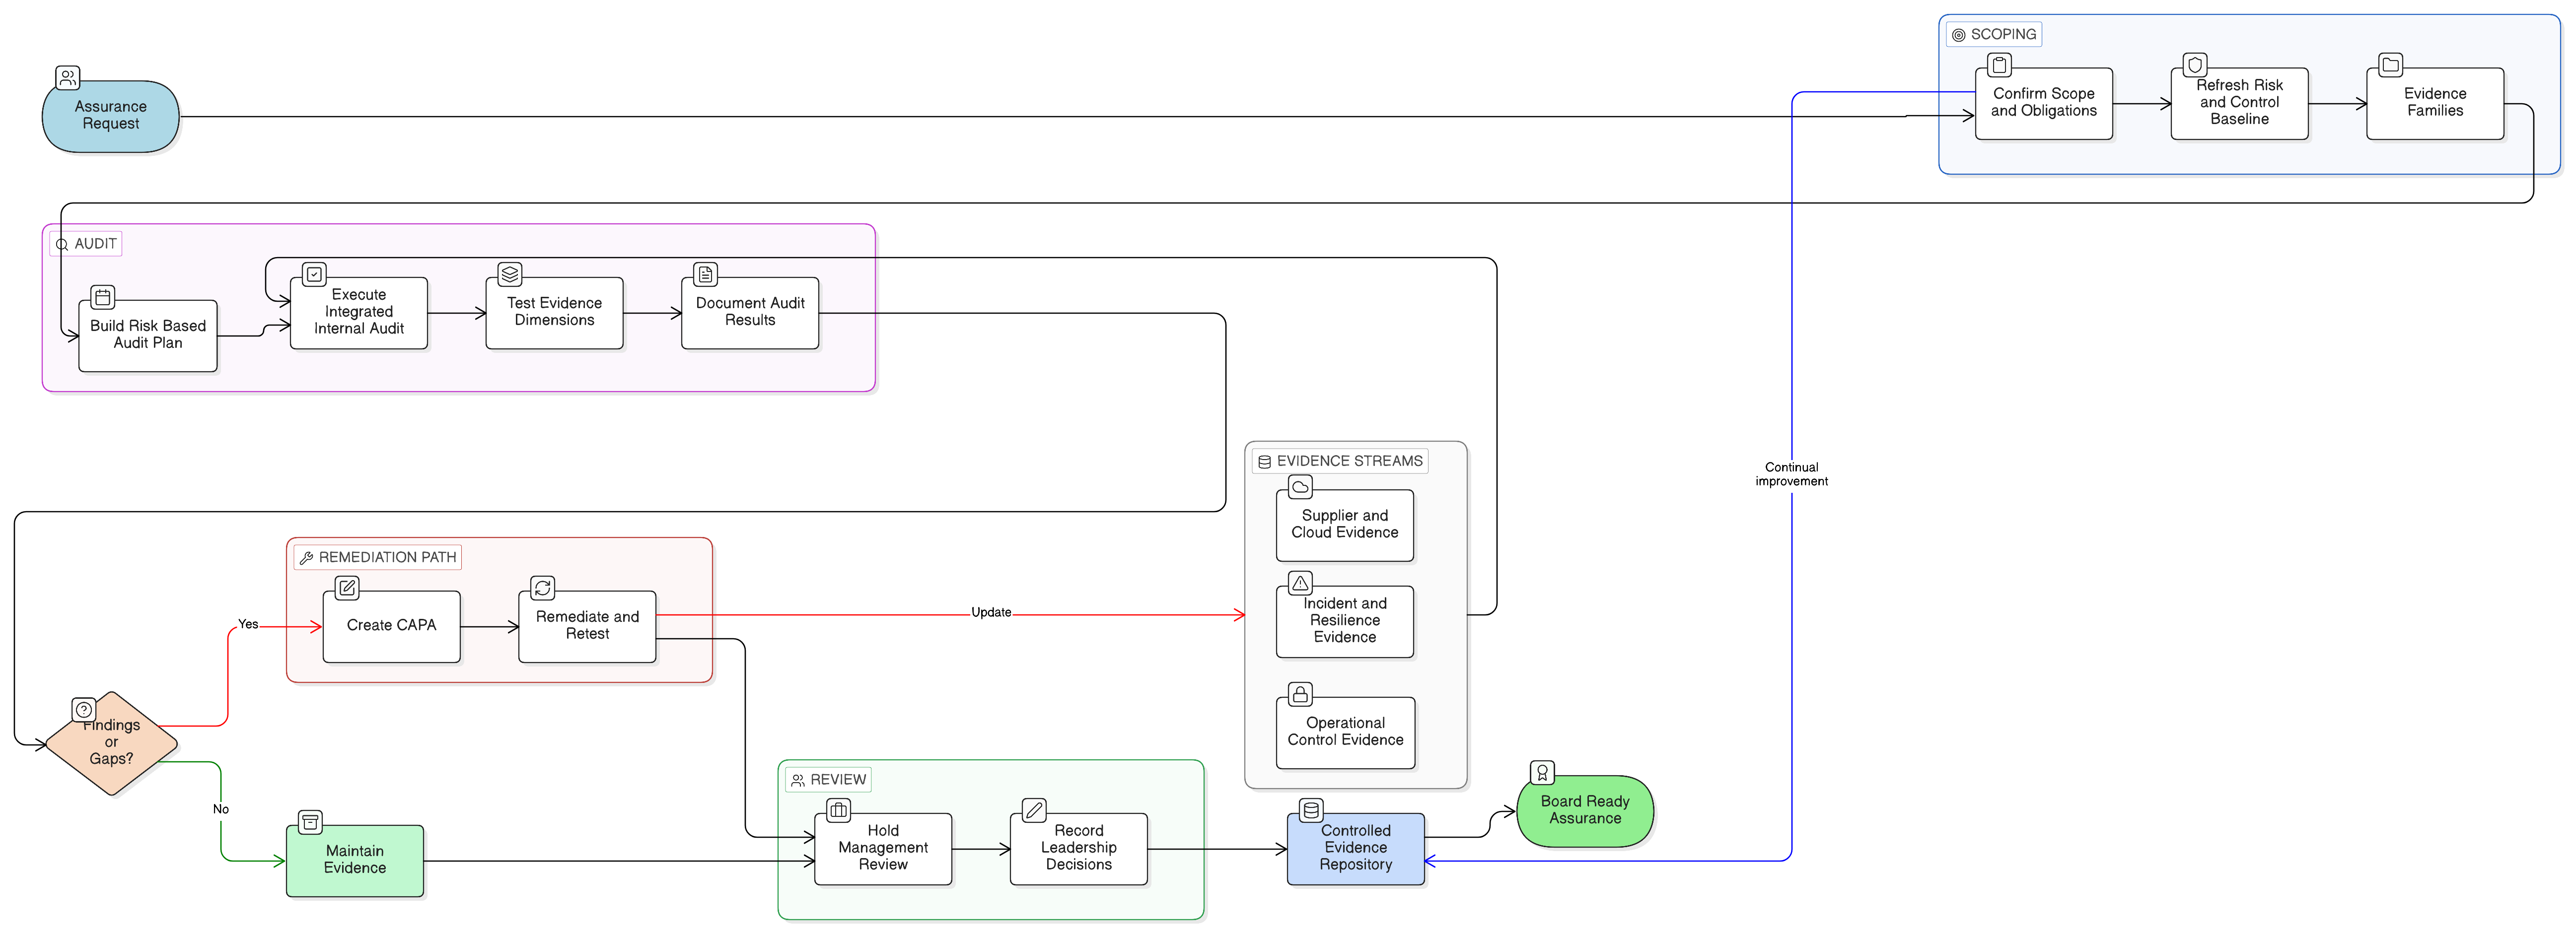
ISO 27001 Audit Evidence for NIS2 and DORA
Learn how to use ISO/IEC 27001:2022 internal audit and management review as a unified evidence engine for NIS2, DORA, GDPR, supplier risk, customer assurance and board accountability.
Articles tagged with "Incident Response"
Learn how to use ISO/IEC 27001:2022 internal audit and management review as a unified evidence engine for NIS2, DORA, GDPR, supplier risk, customer assurance and board accountability.
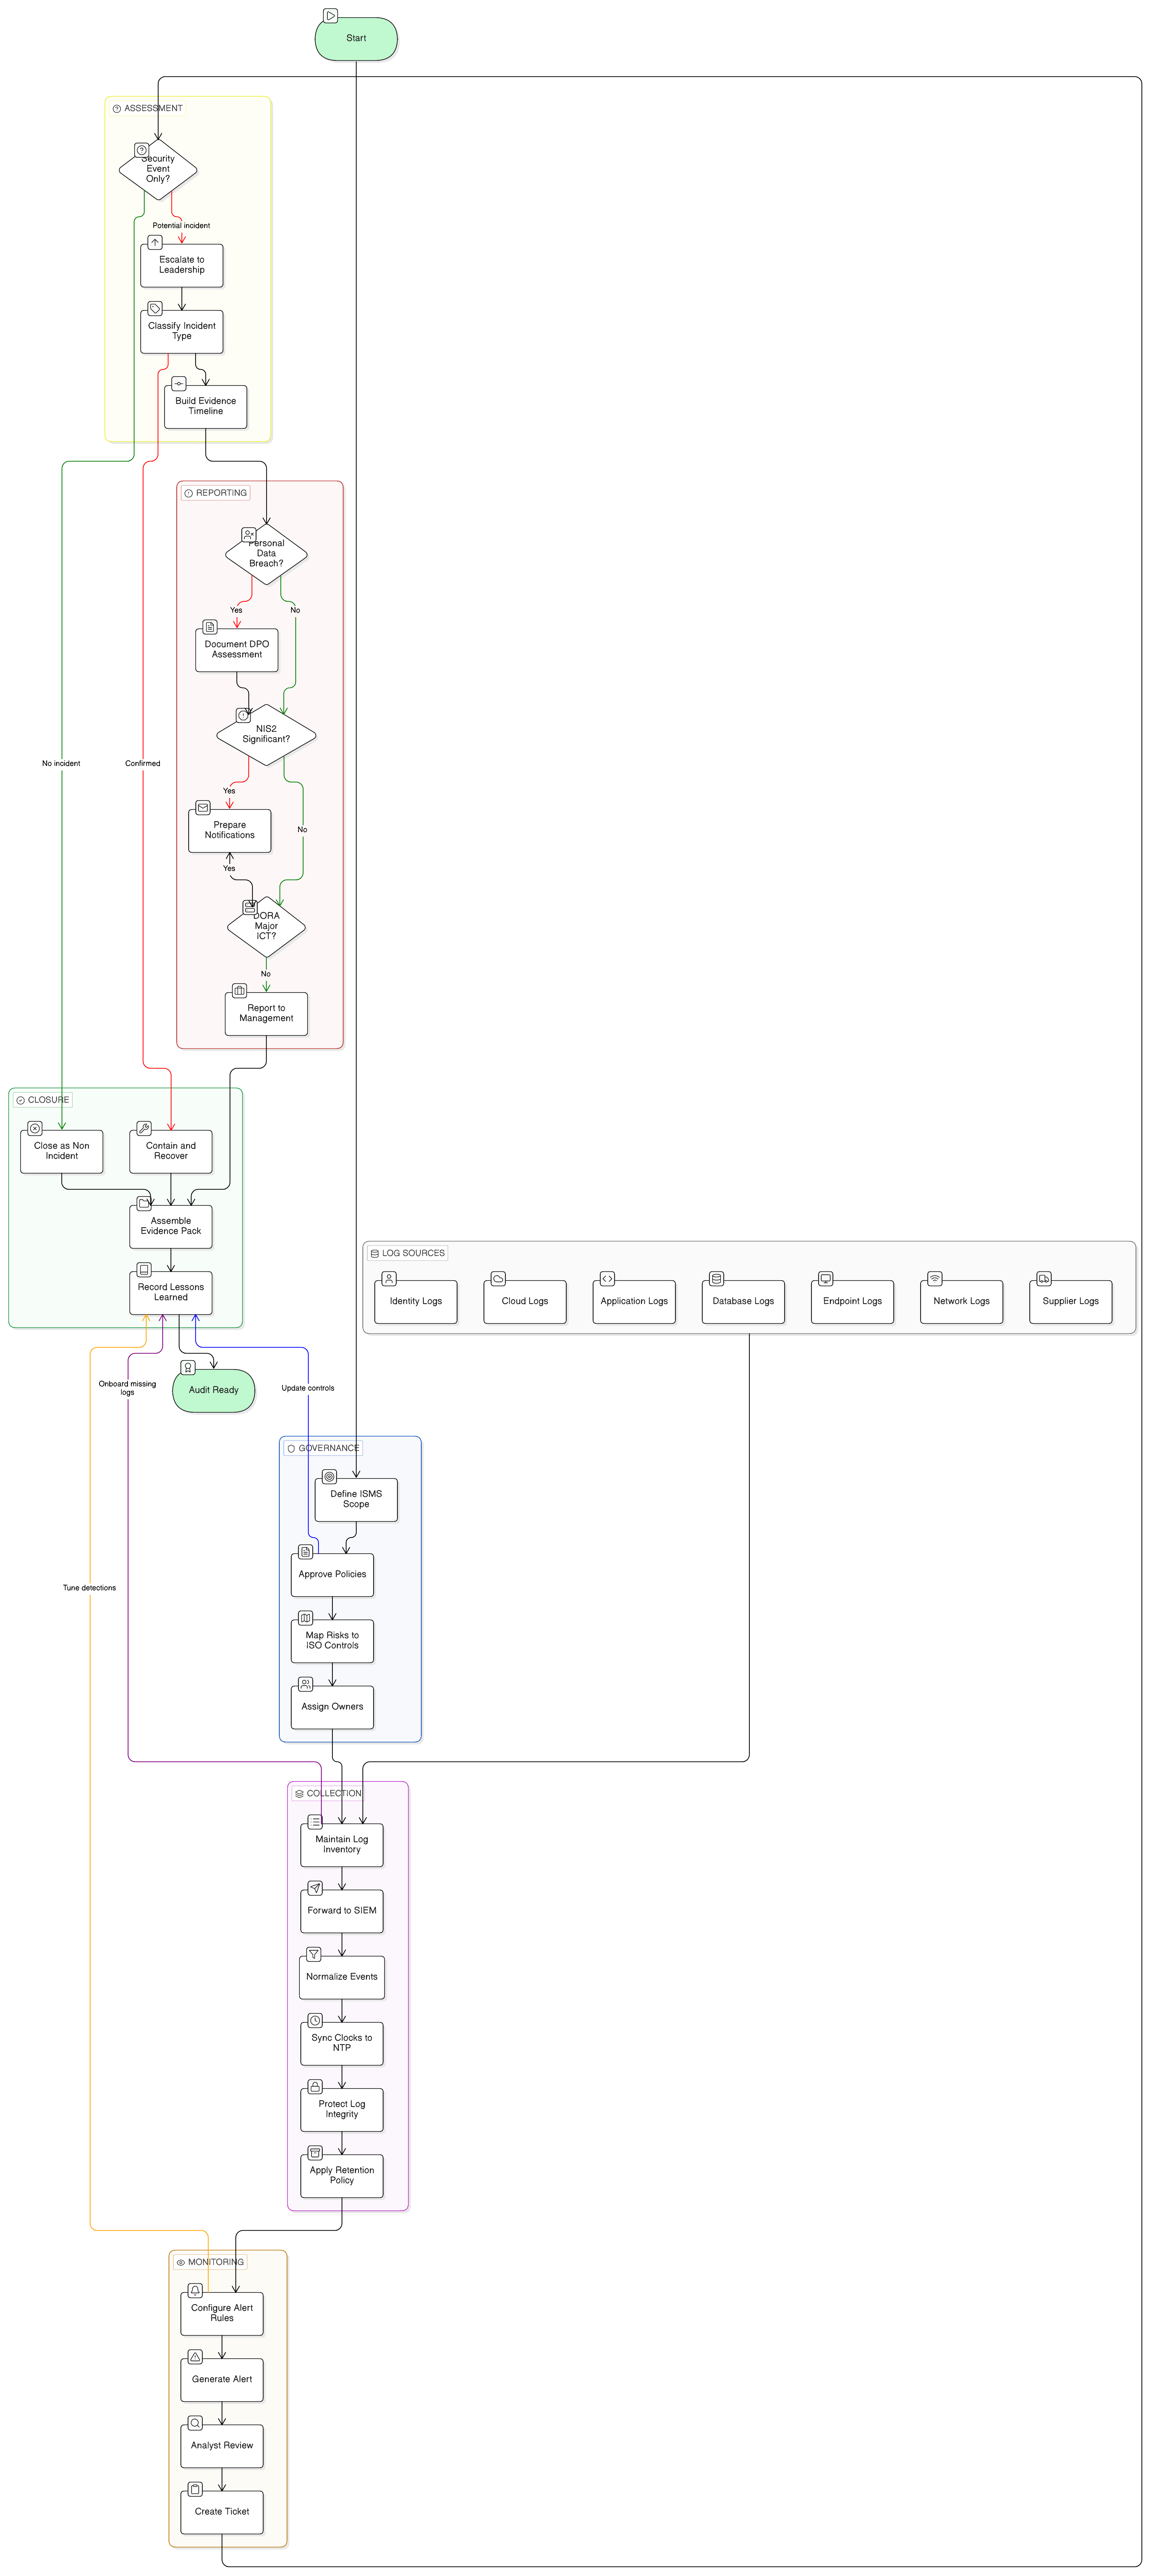
A practical guide to building audit-ready ISO/IEC 27001:2022 logging and monitoring evidence for NIS2, DORA and GDPR, with control mapping, policy clauses, incident workflows, supplier logging requirements and evidence pack guidance.
A regulatory contact register is no longer administrative housekeeping. For NIS2, DORA, GDPR and ISO/IEC 27001:2022, it is operational evidence that your organization can notify the right authority, supervisor, supplier or executive before the clock runs out.
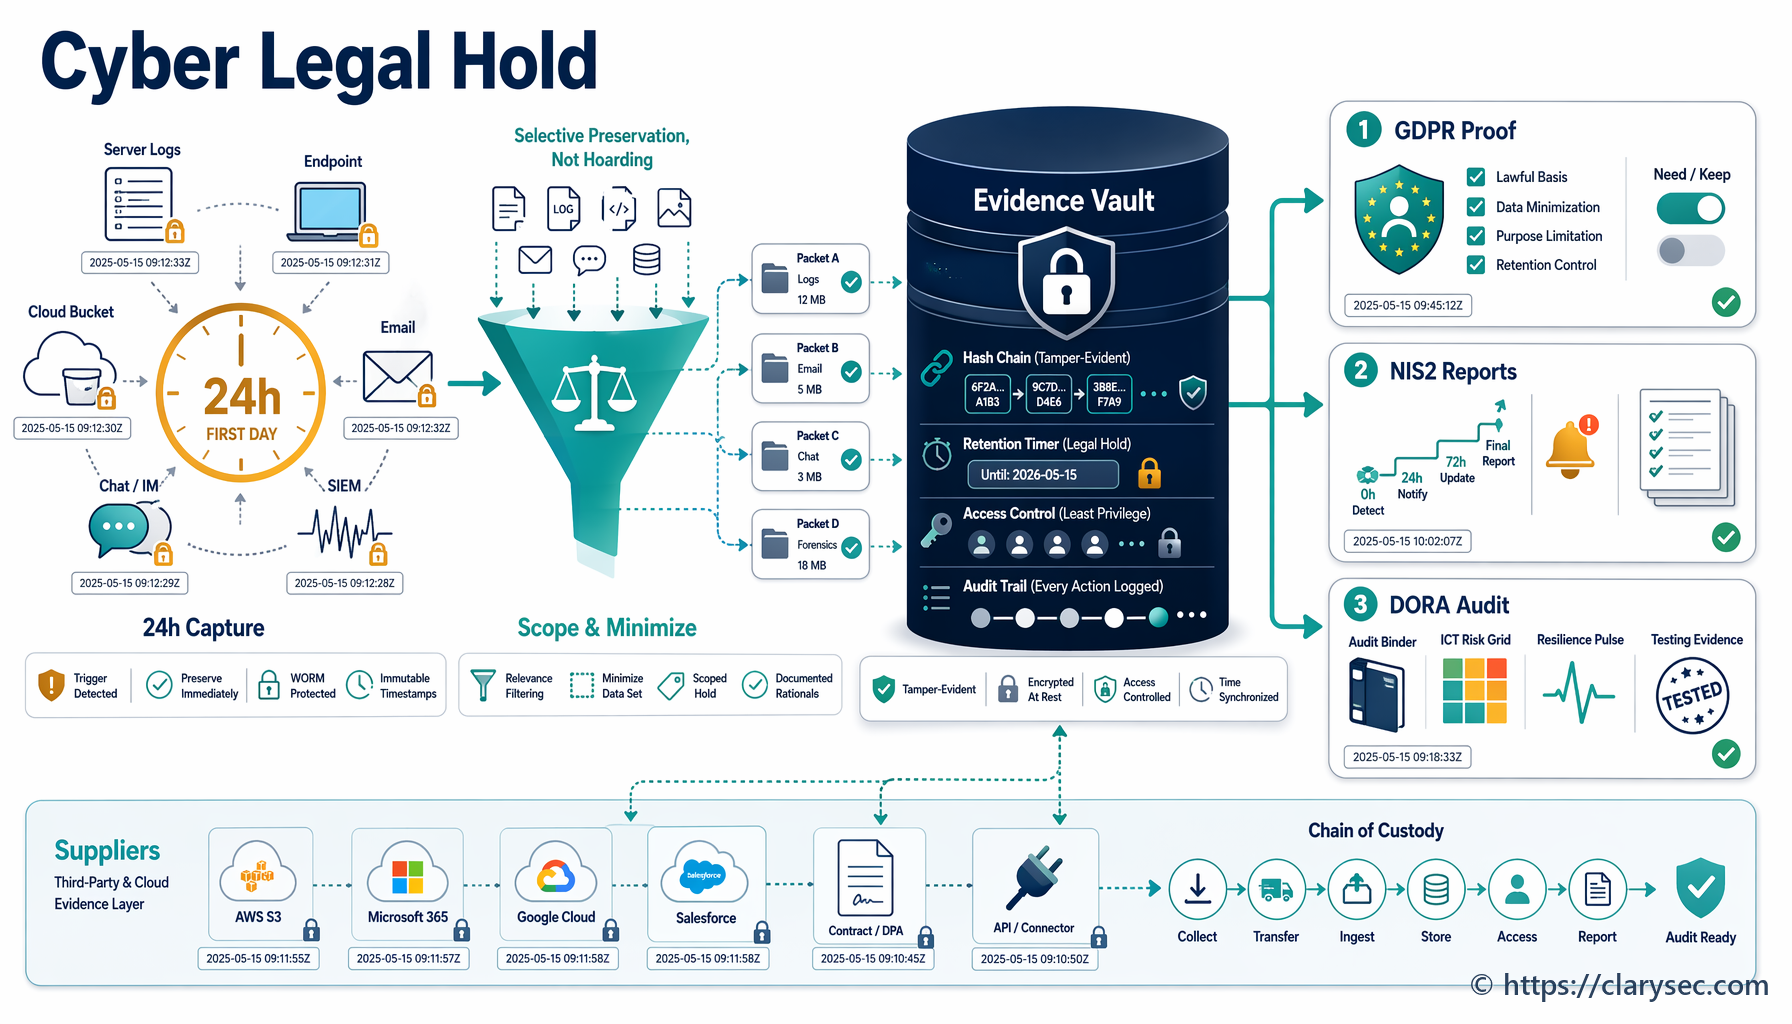
A practical CISO guide to cyber incident legal hold and evidence retention, mapped to ISO/IEC 27001:2022, GDPR, NIS2, DORA, NIST CSF 2.0 and COBIT 2019.
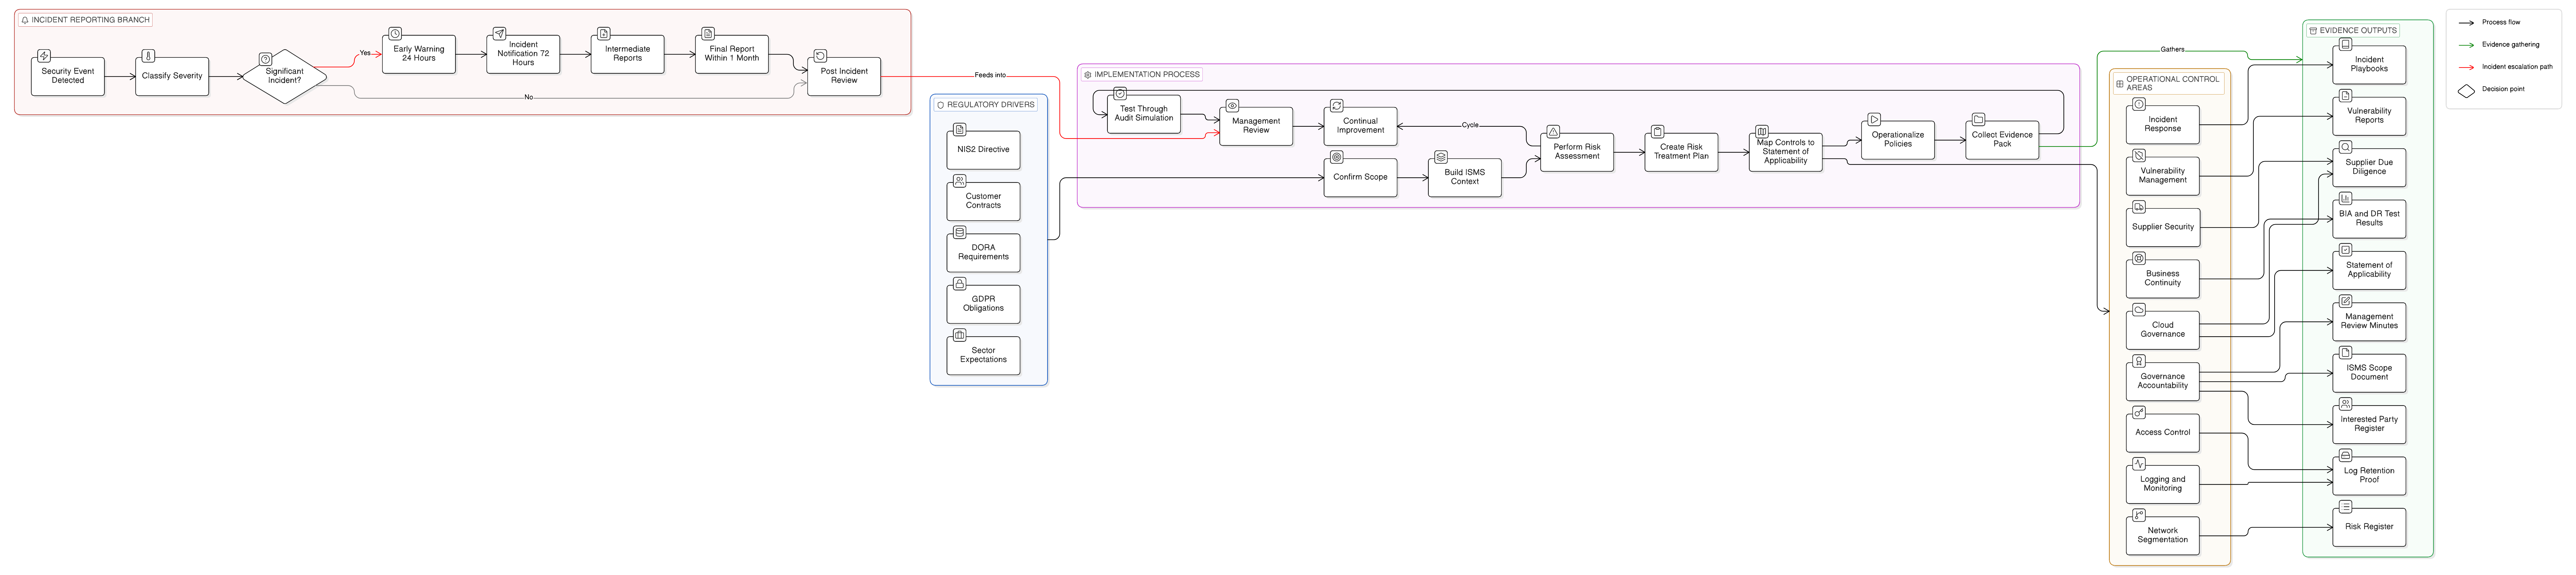
A unified NIS2 Implementing Regulation 2024/2690 to ISO/IEC 27001:2022 control mapping for cloud, MSP, MSSP and data centre providers. Includes Clarysec policy clauses, audit evidence, DORA and GDPR alignment, and a practical implementation roadmap.
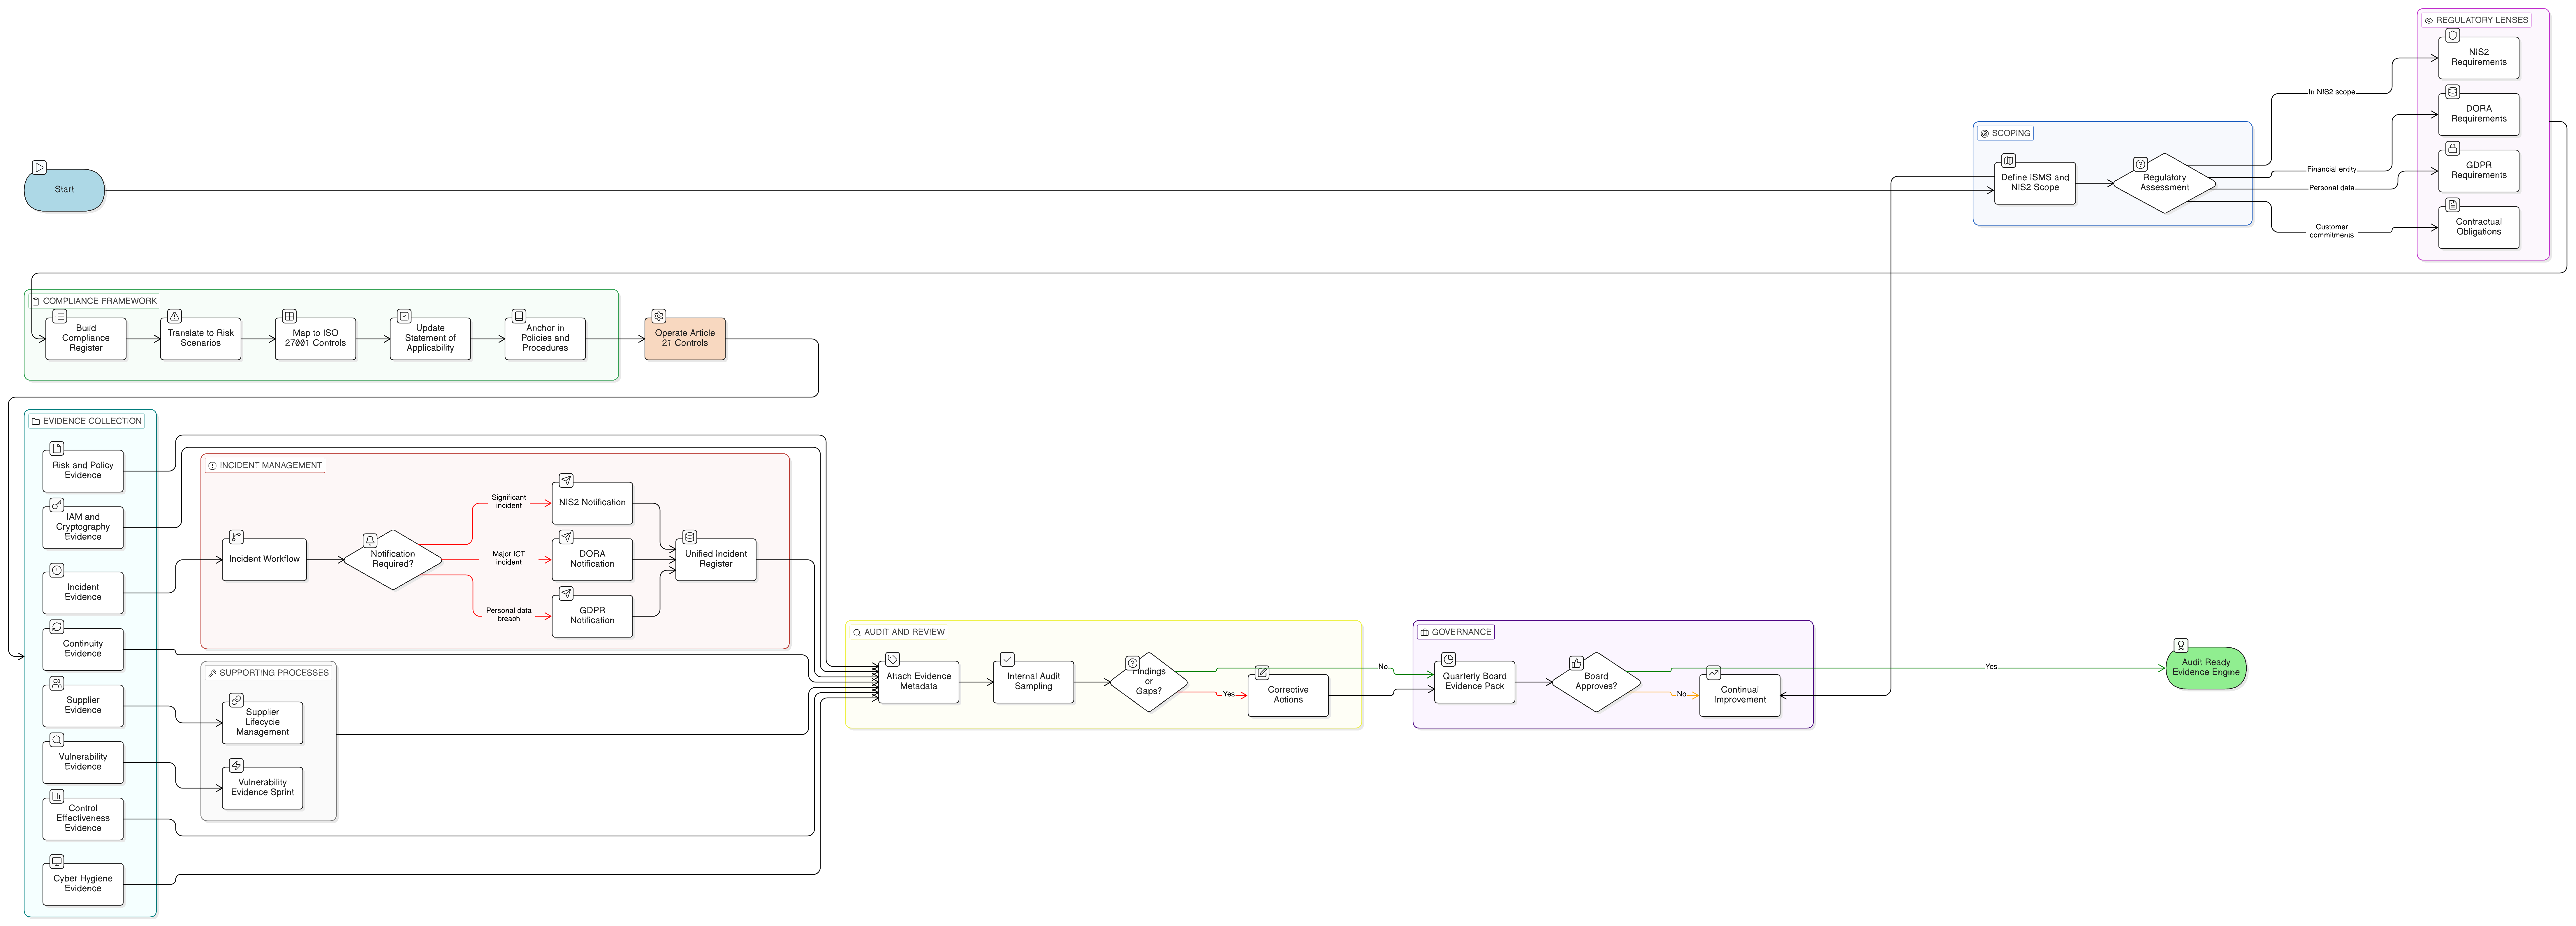
A flagship guide for CISOs, compliance managers and business leaders who need to turn NIS2 Article 21 technical measures into ISO 27001:2022 controls, policies, owners, records and defensible evidence.
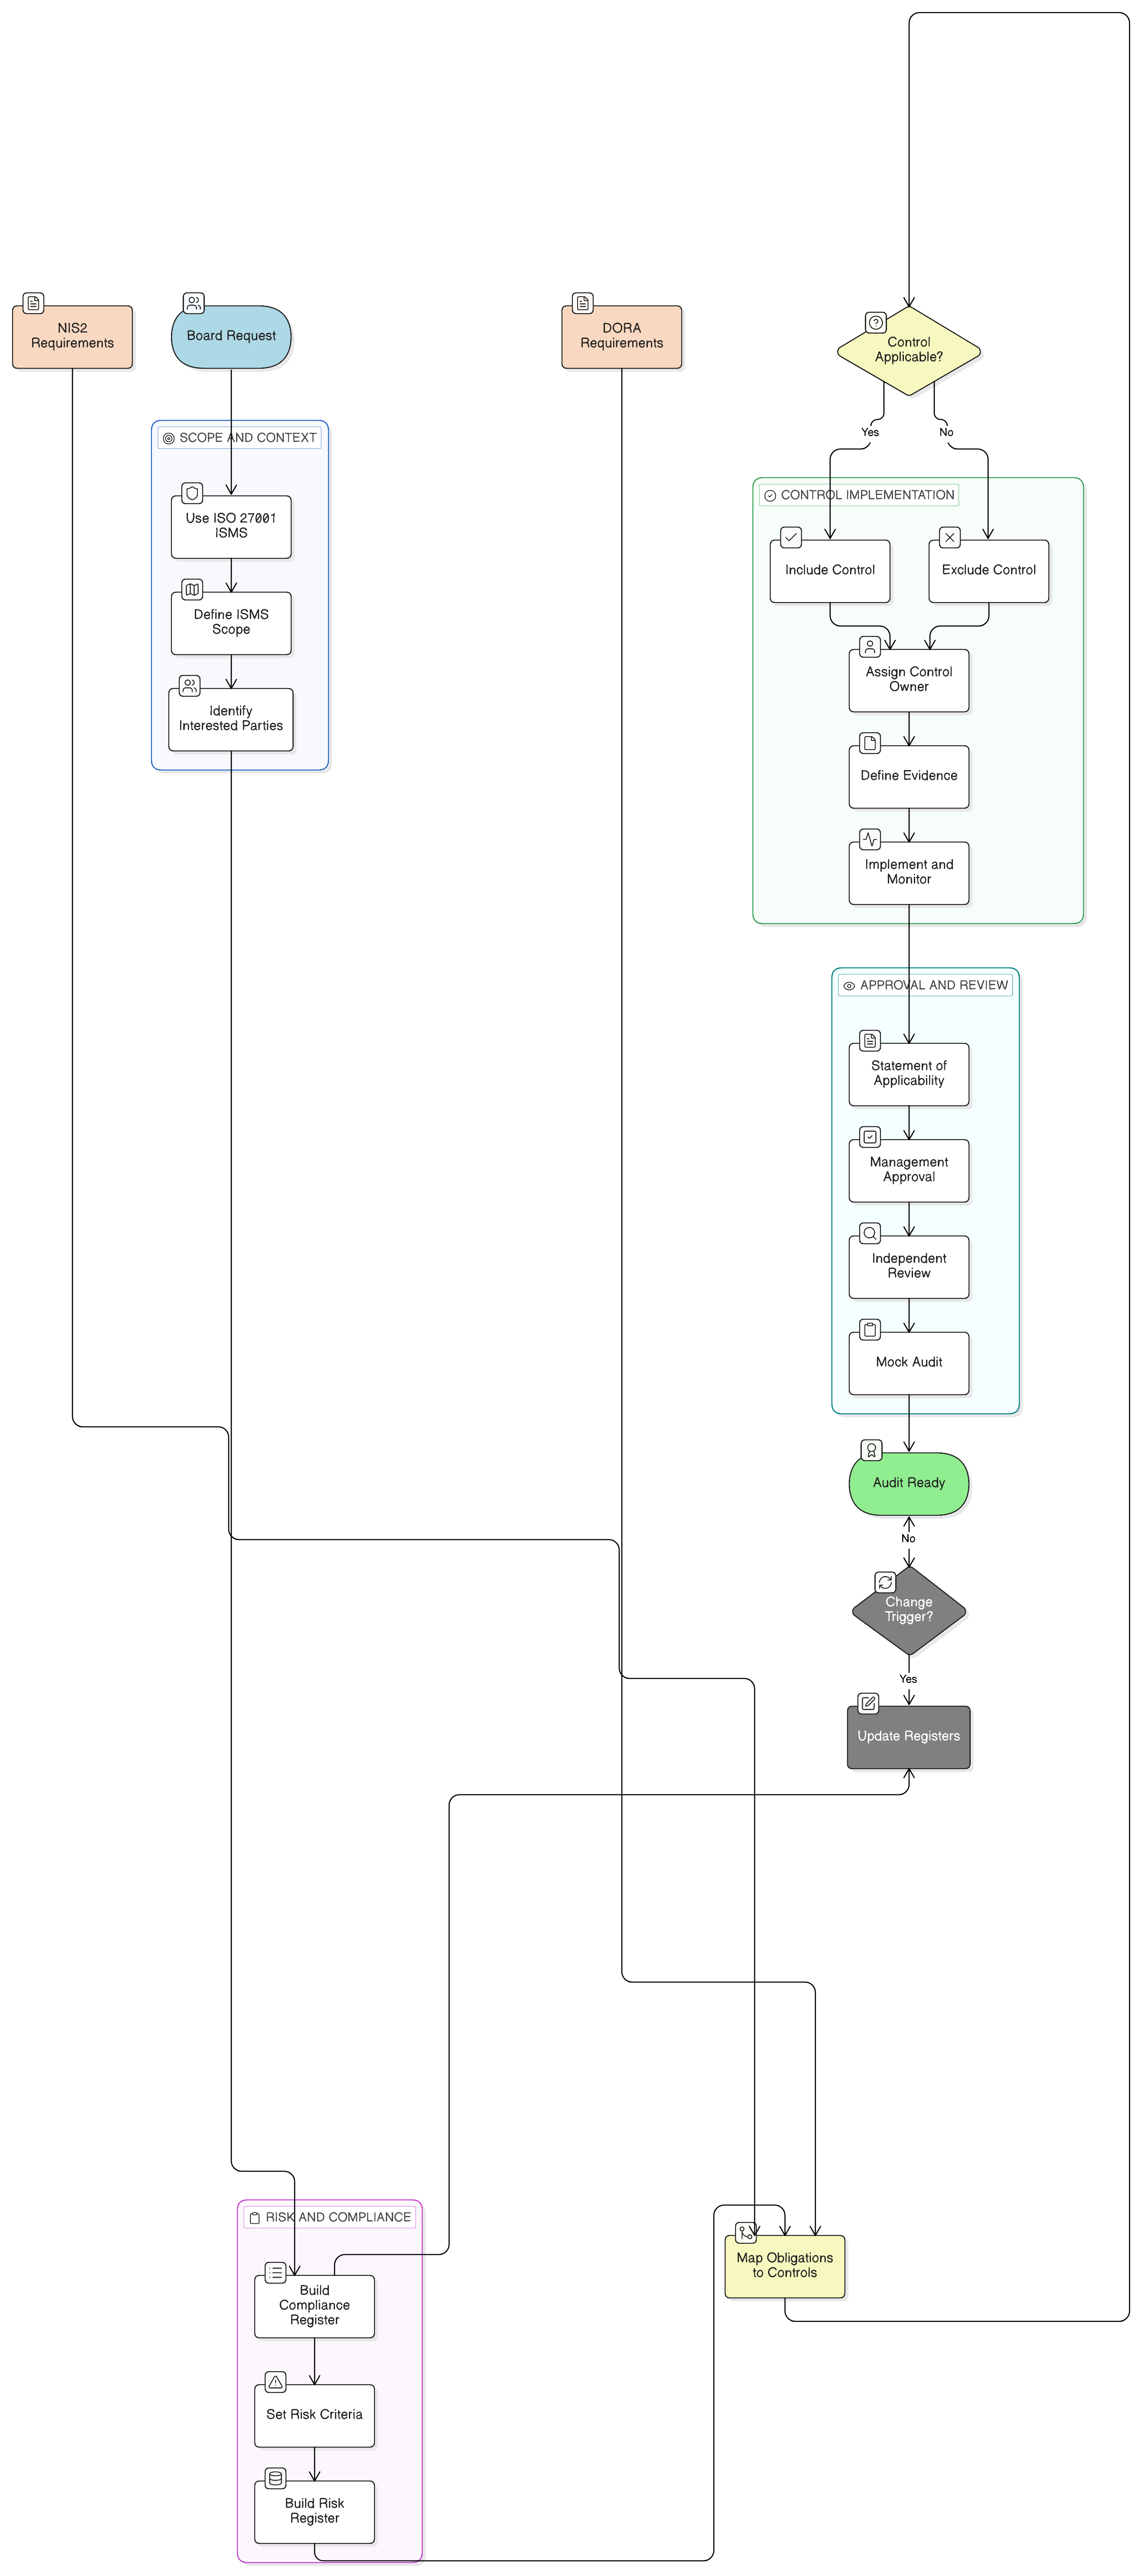
Learn how to use the ISO 27001 Statement of Applicability as an audit-ready bridge between NIS2, DORA, GDPR, risk treatment, suppliers, incident response, and evidence.
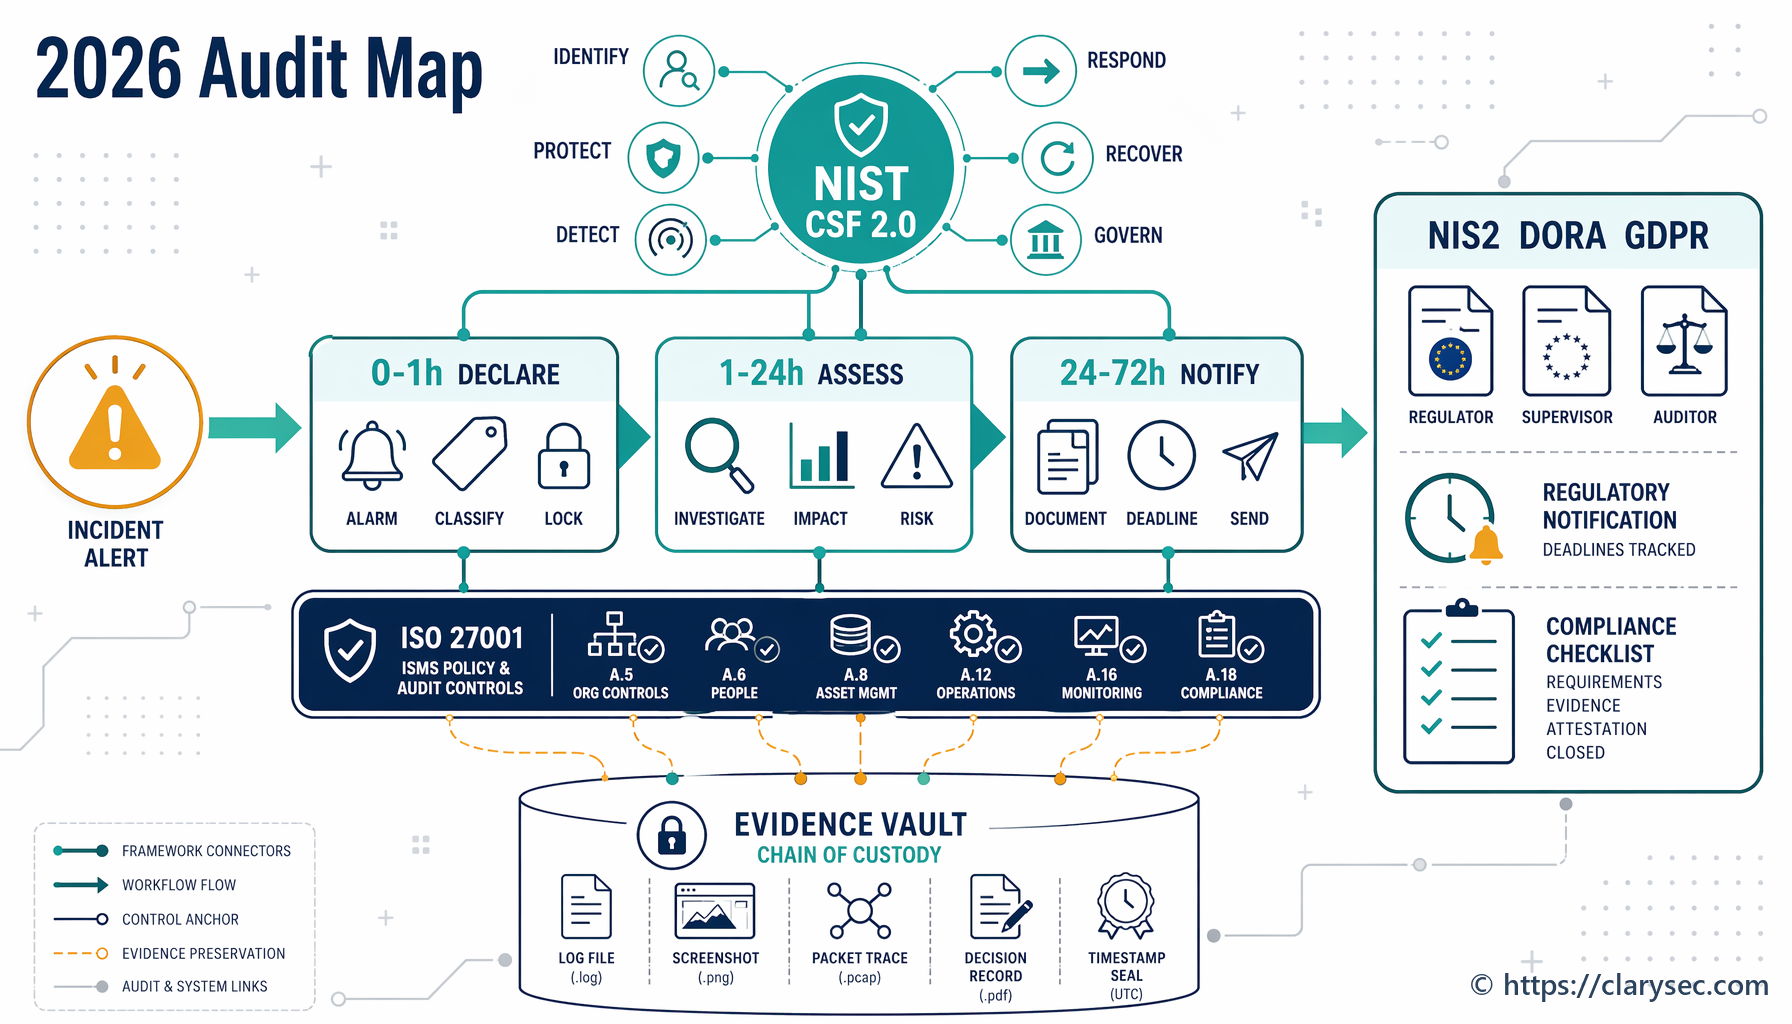
A practical CISO guide to mapping NIST SP 800-61 and NIST CSF 2.0 incident response to ISO/IEC 27001:2022, NIS2, DORA and GDPR evidence. Includes policy clauses, audit mappings, reporting timelines, evidence packs and Clarysec toolkit guidance.
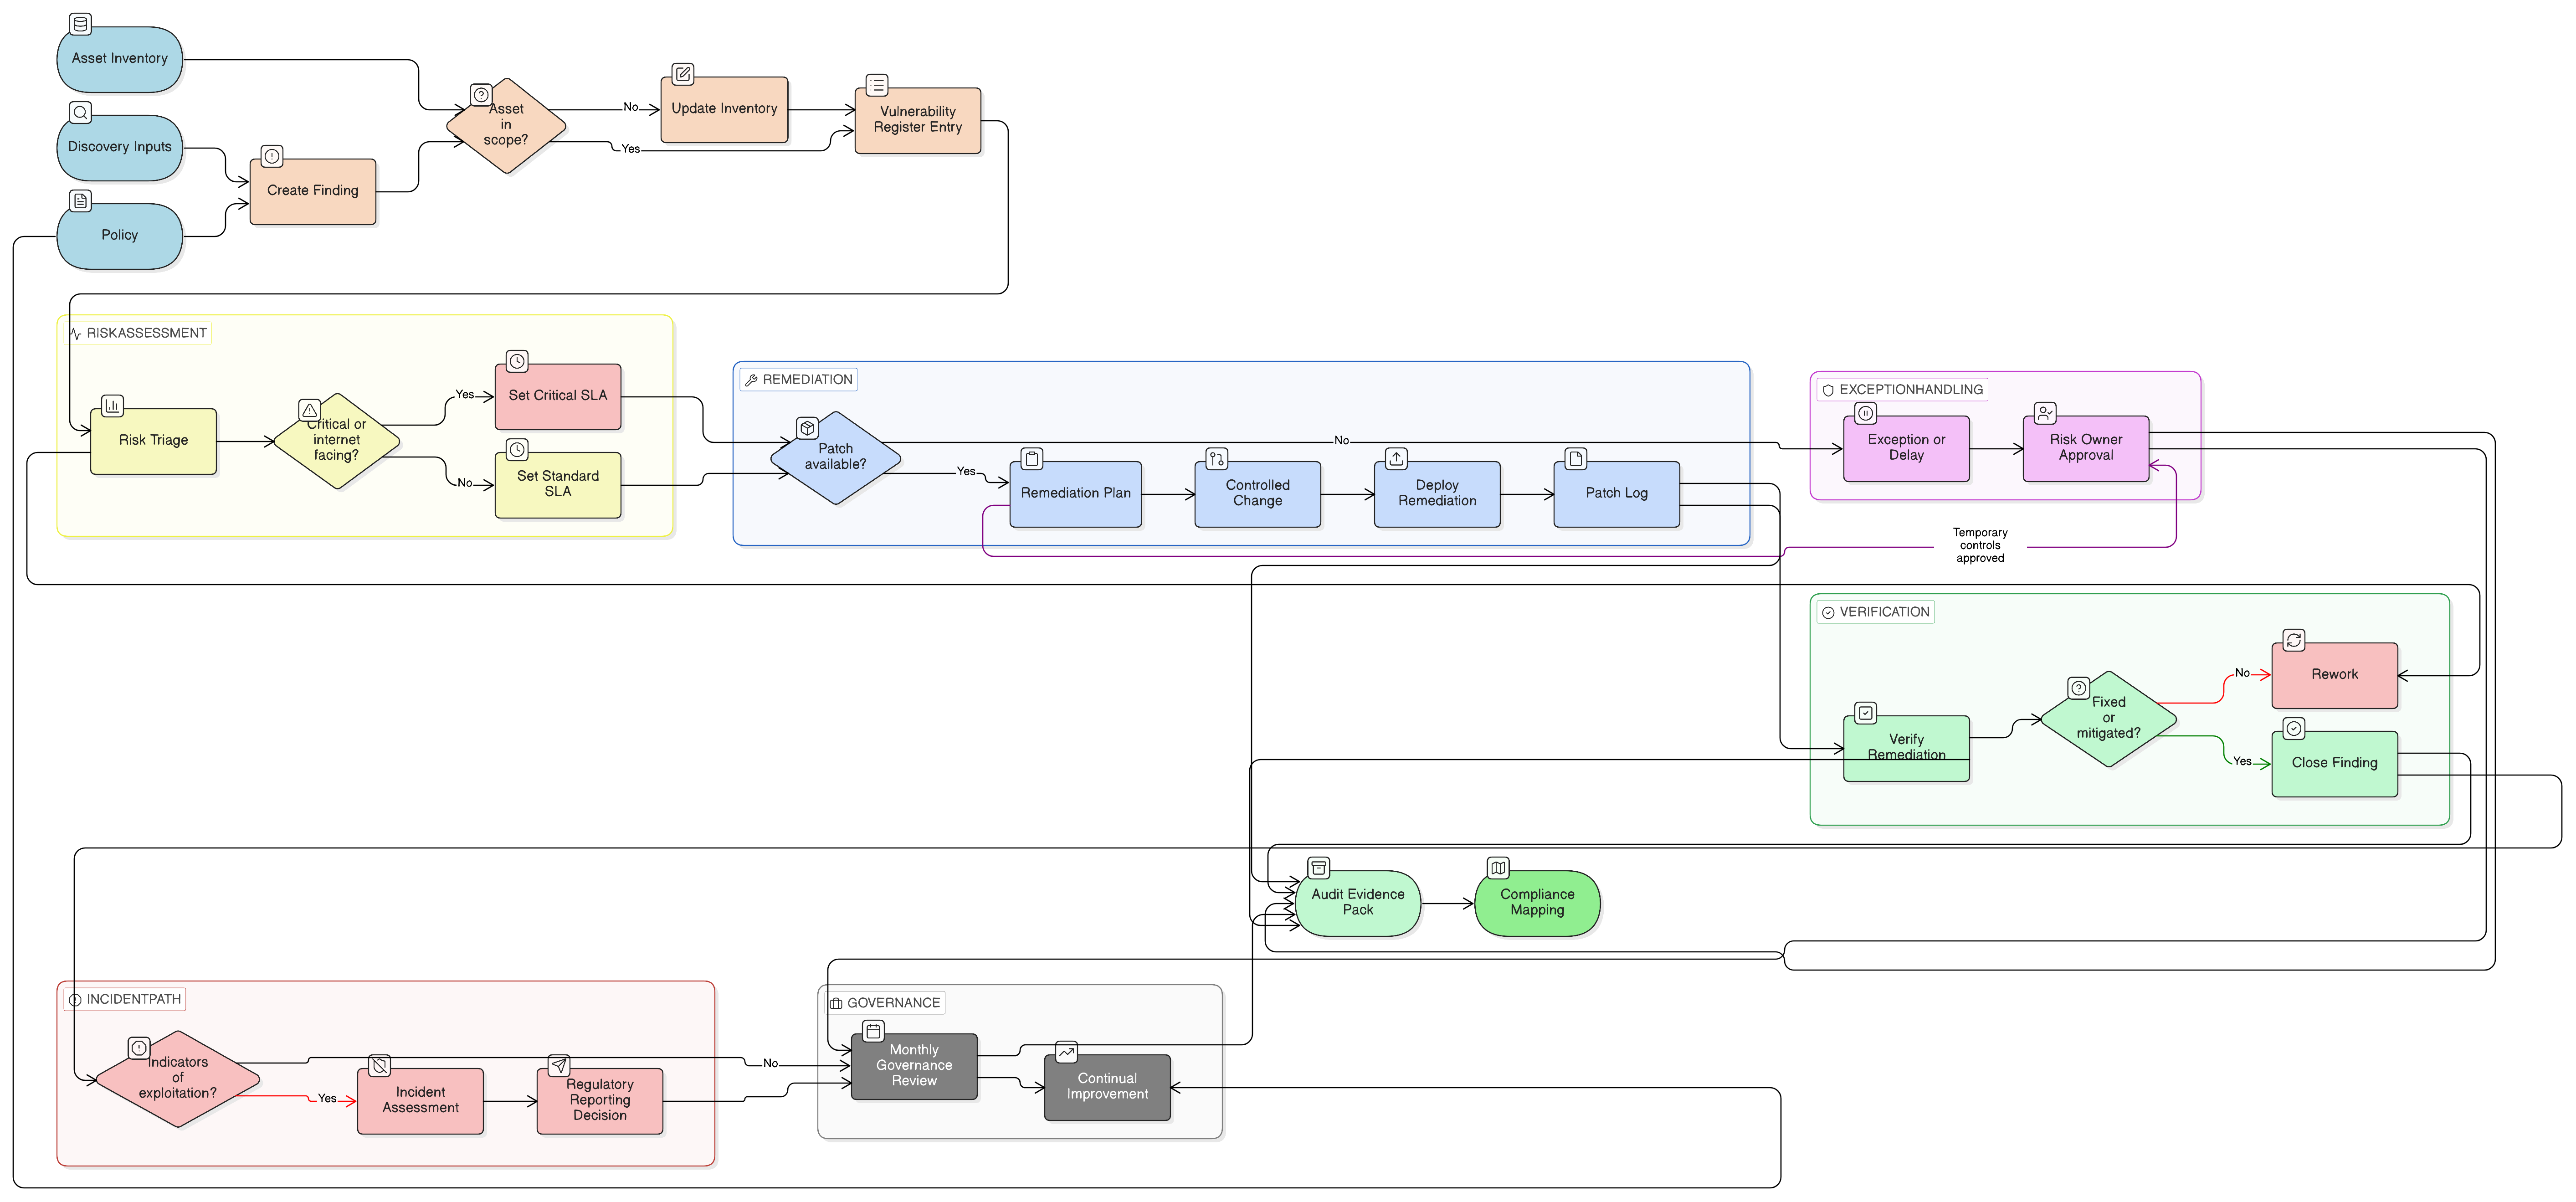
A practical CISO guide to converting vulnerability scans, patch logs, risk decisions and exceptions into audit-ready evidence for ISO 27001:2022, NIS2, DORA, GDPR and COBIT 2019.