#Logging and Monitoring
Articles tagged with "Logging and Monitoring"
49 articles
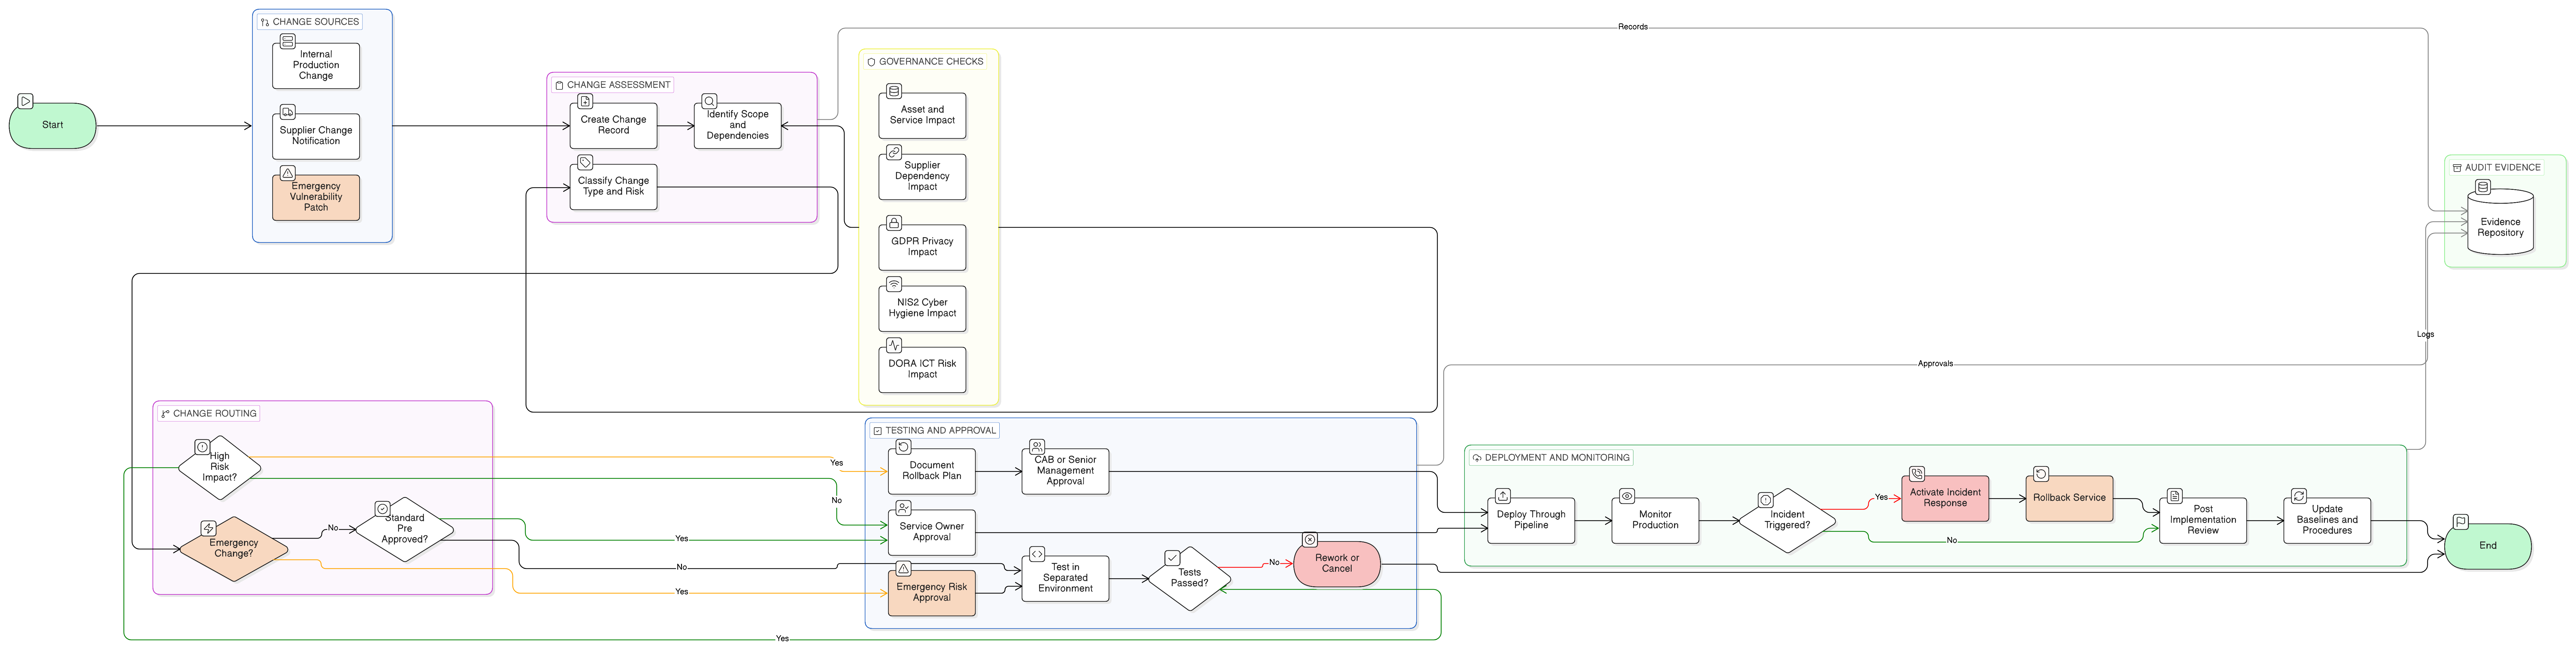
A practical, scenario-driven guide to secure change management using ISO/IEC 27001:2022, Clarysec policies, Zenith Blueprint, and Zenith Controls to support NIS2, DORA, GDPR, NIST CSF 2.0, and audit evidence in 2026.
A practical flagship guide for CISOs, compliance managers and auditors building a unified ISO 27001:2022 internal audit programme that supports NIS2, DORA, GDPR, NIST CSF and COBIT assurance. Includes scope design, sampling, findings, corrective action, cross-compliance mapping and a 2026 evidence calendar.
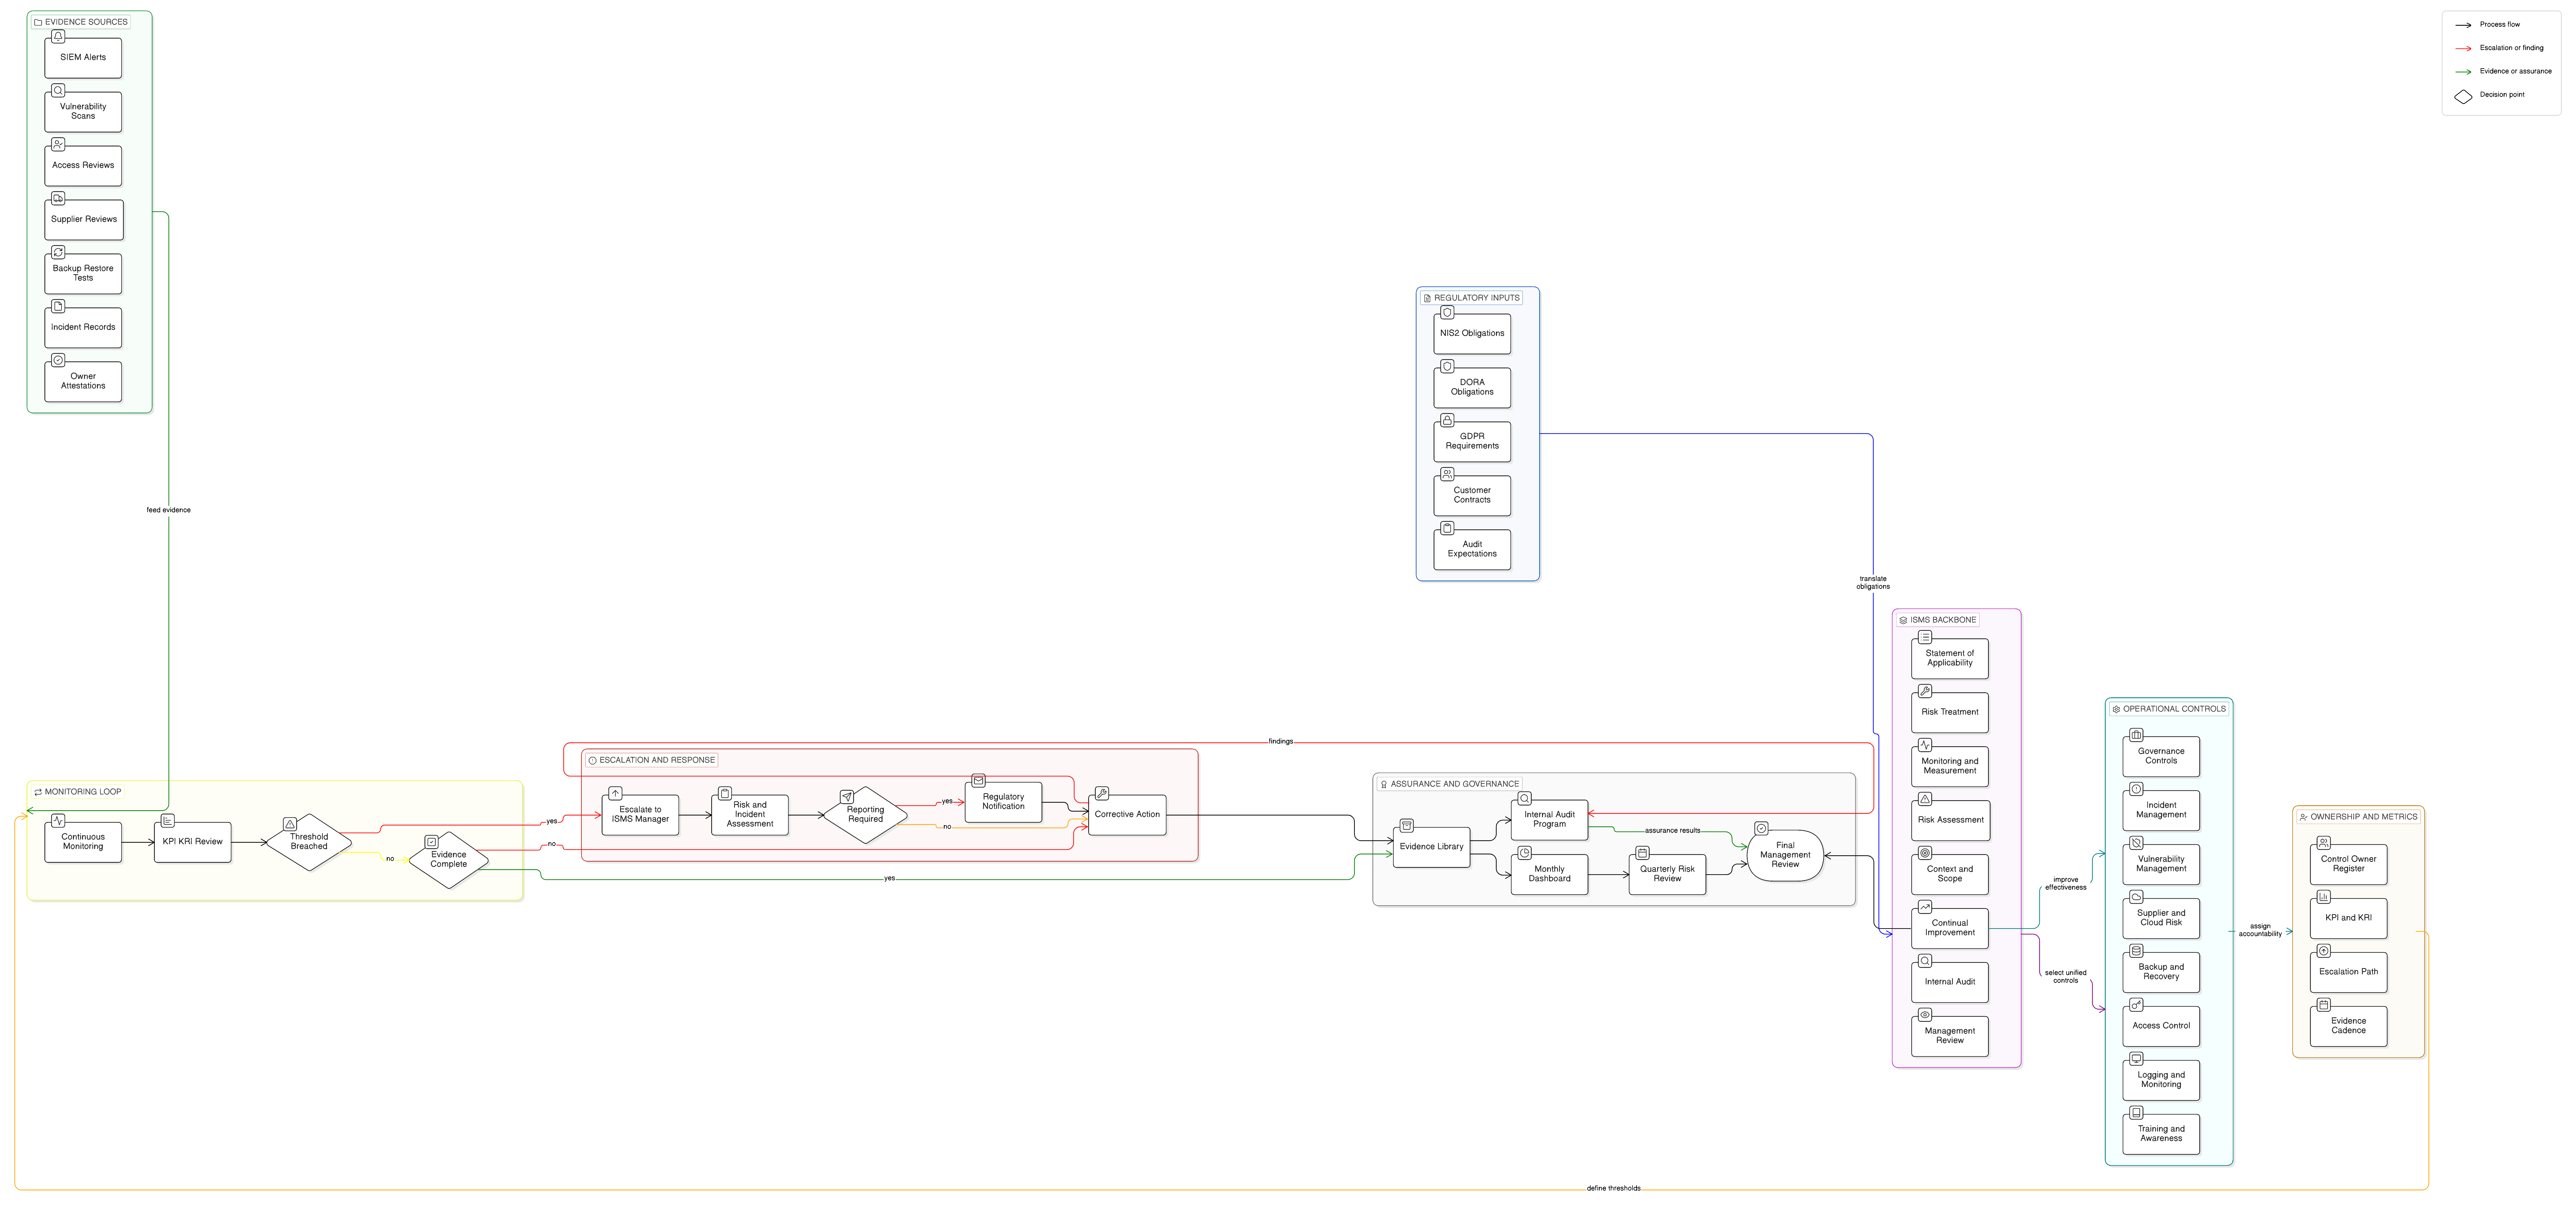
A practical CISO guide to continuous compliance monitoring for NIS2 and DORA using ISO/IEC 27001:2022, control ownership, KPIs, KRIs, evidence cadence, policy mapping, and audit-ready proof.
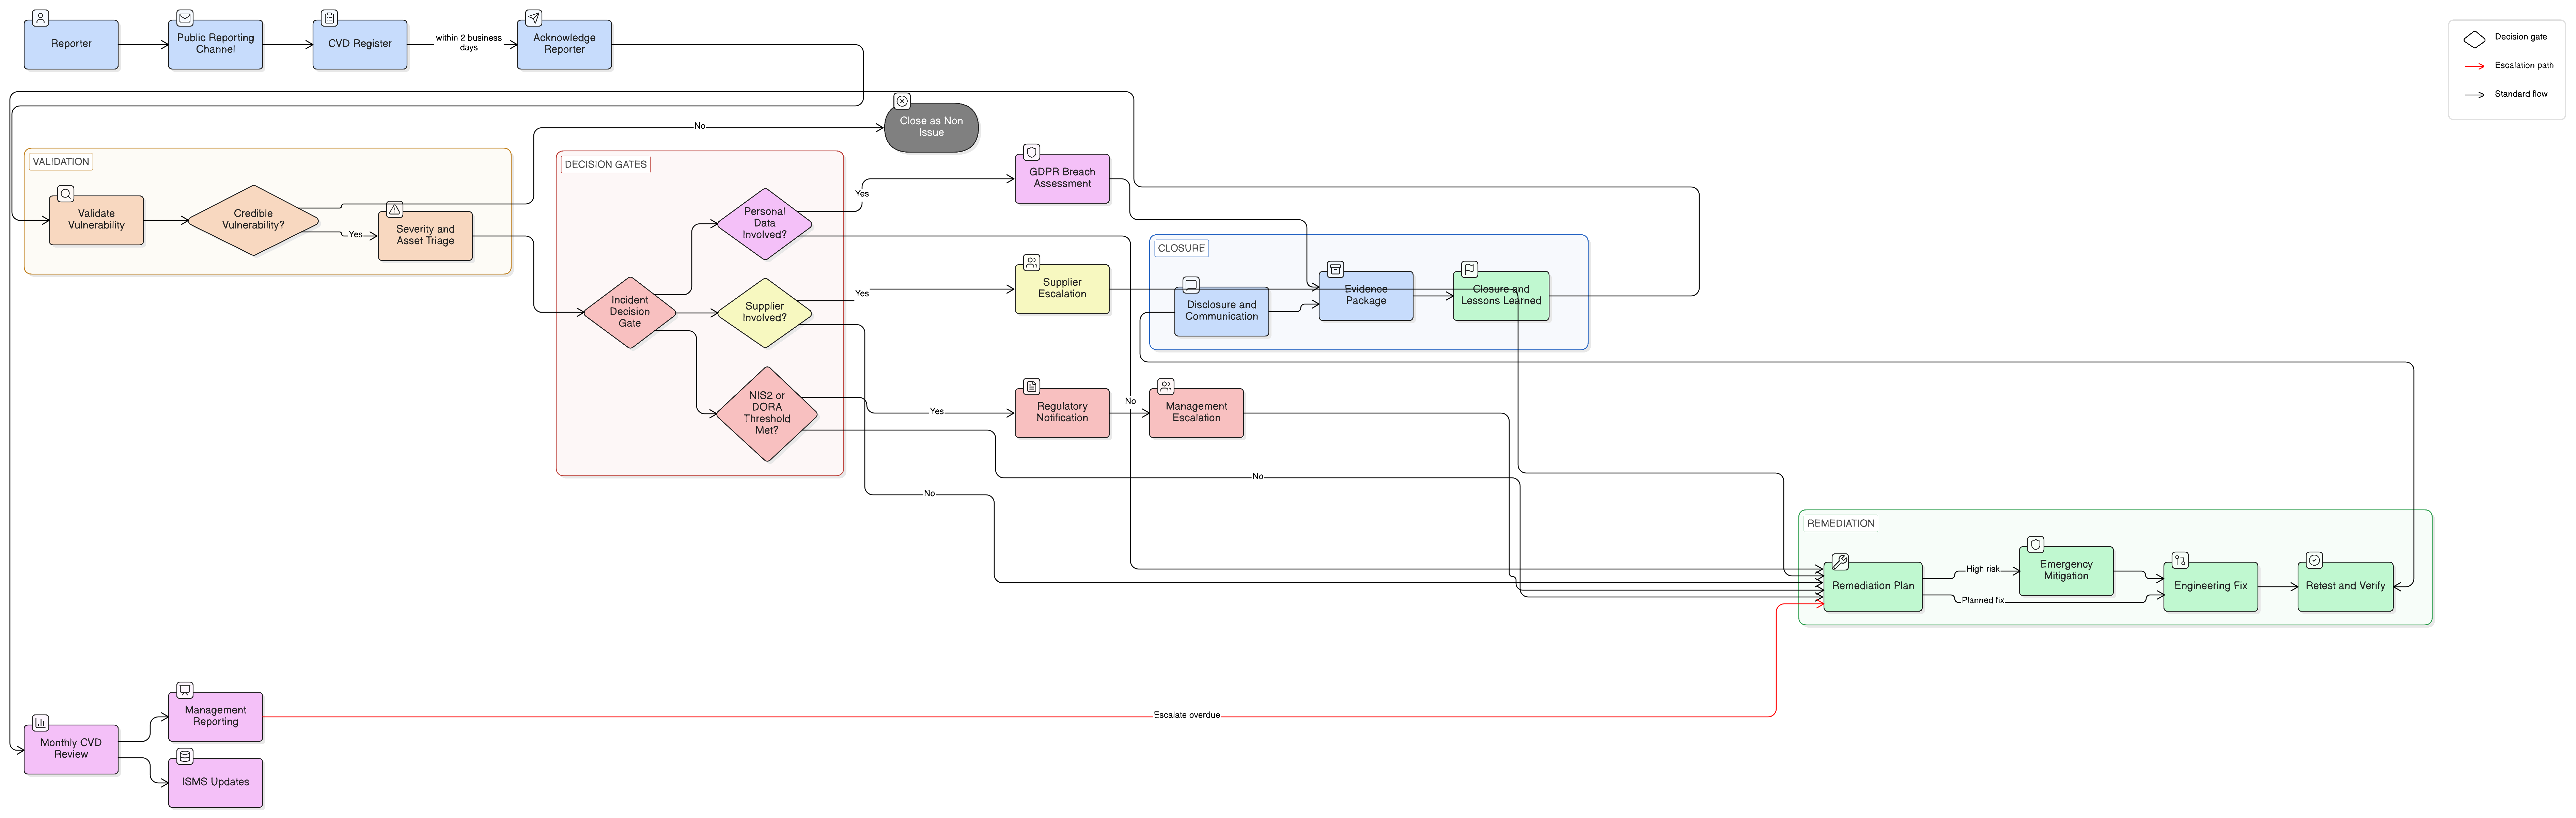
A practical CISO guide to coordinated vulnerability disclosure under NIS2, DORA, GDPR, and ISO/IEC 27001:2022, with policy wording, intake workflow, supplier escalation, audit evidence, and control mapping.
A practical guide for building audit-ready GDPR Article 32 technical and organisational measures using ISO 27001:2022, ISO 27005, NIS2, DORA and Clarysec toolkits.
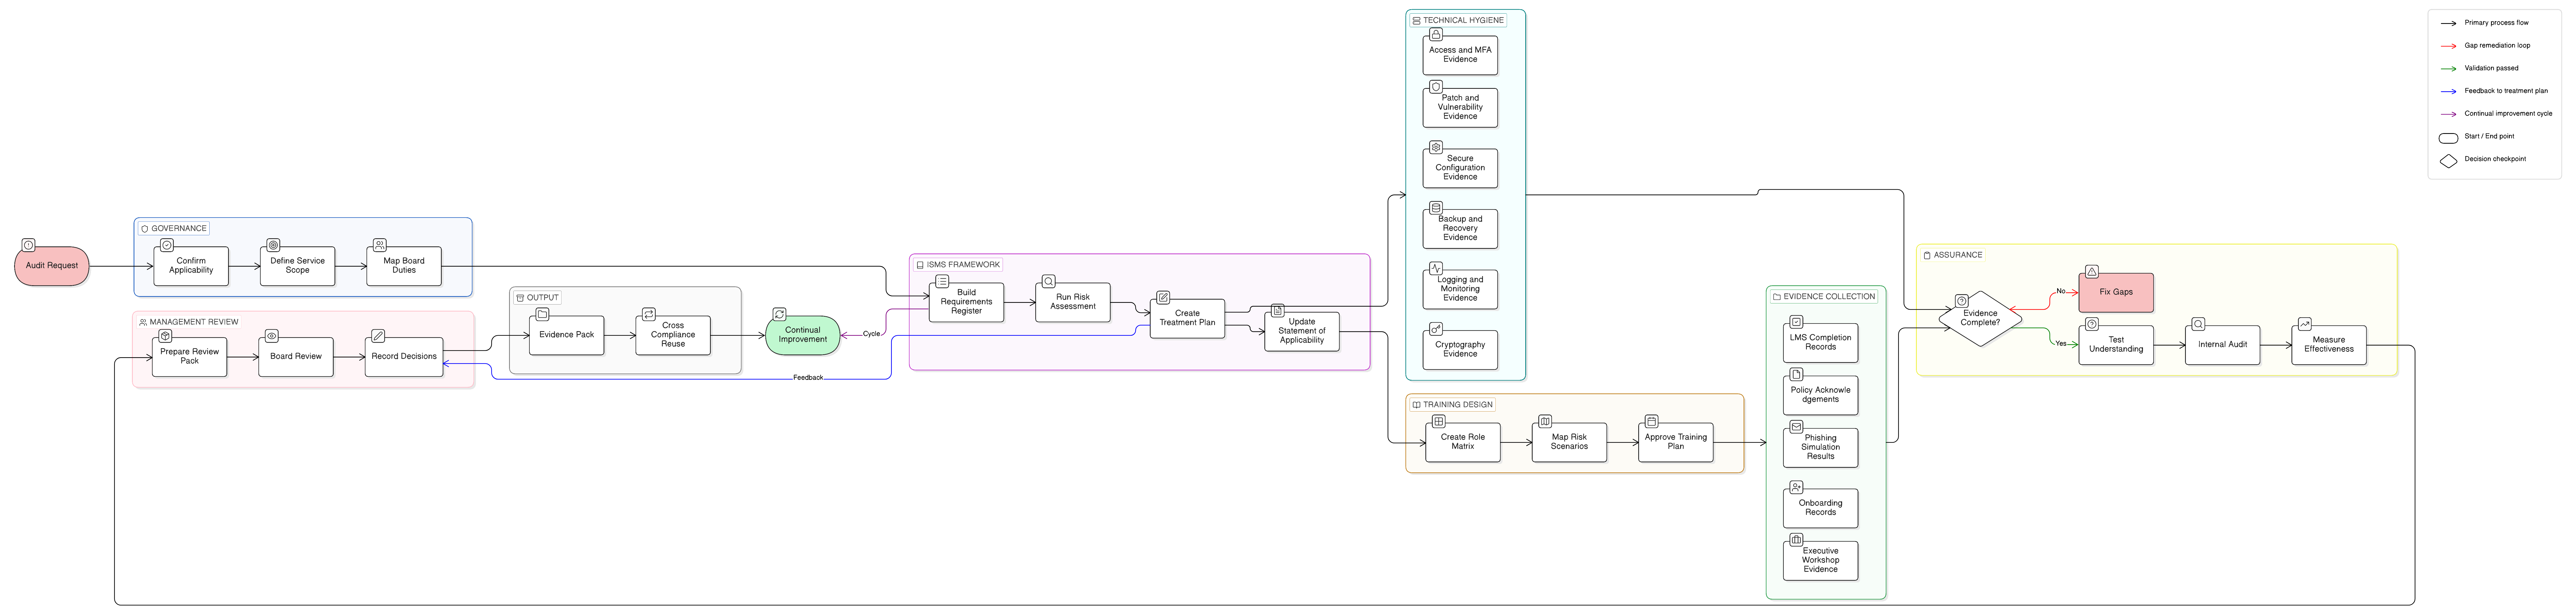
A practical CISO guide to turning NIS2 Article 21 cyber hygiene and cybersecurity training into audit-ready ISO/IEC 27001:2022 evidence, with policy clauses, control mapping, DORA and GDPR alignment, and a 10-day remediation sprint.
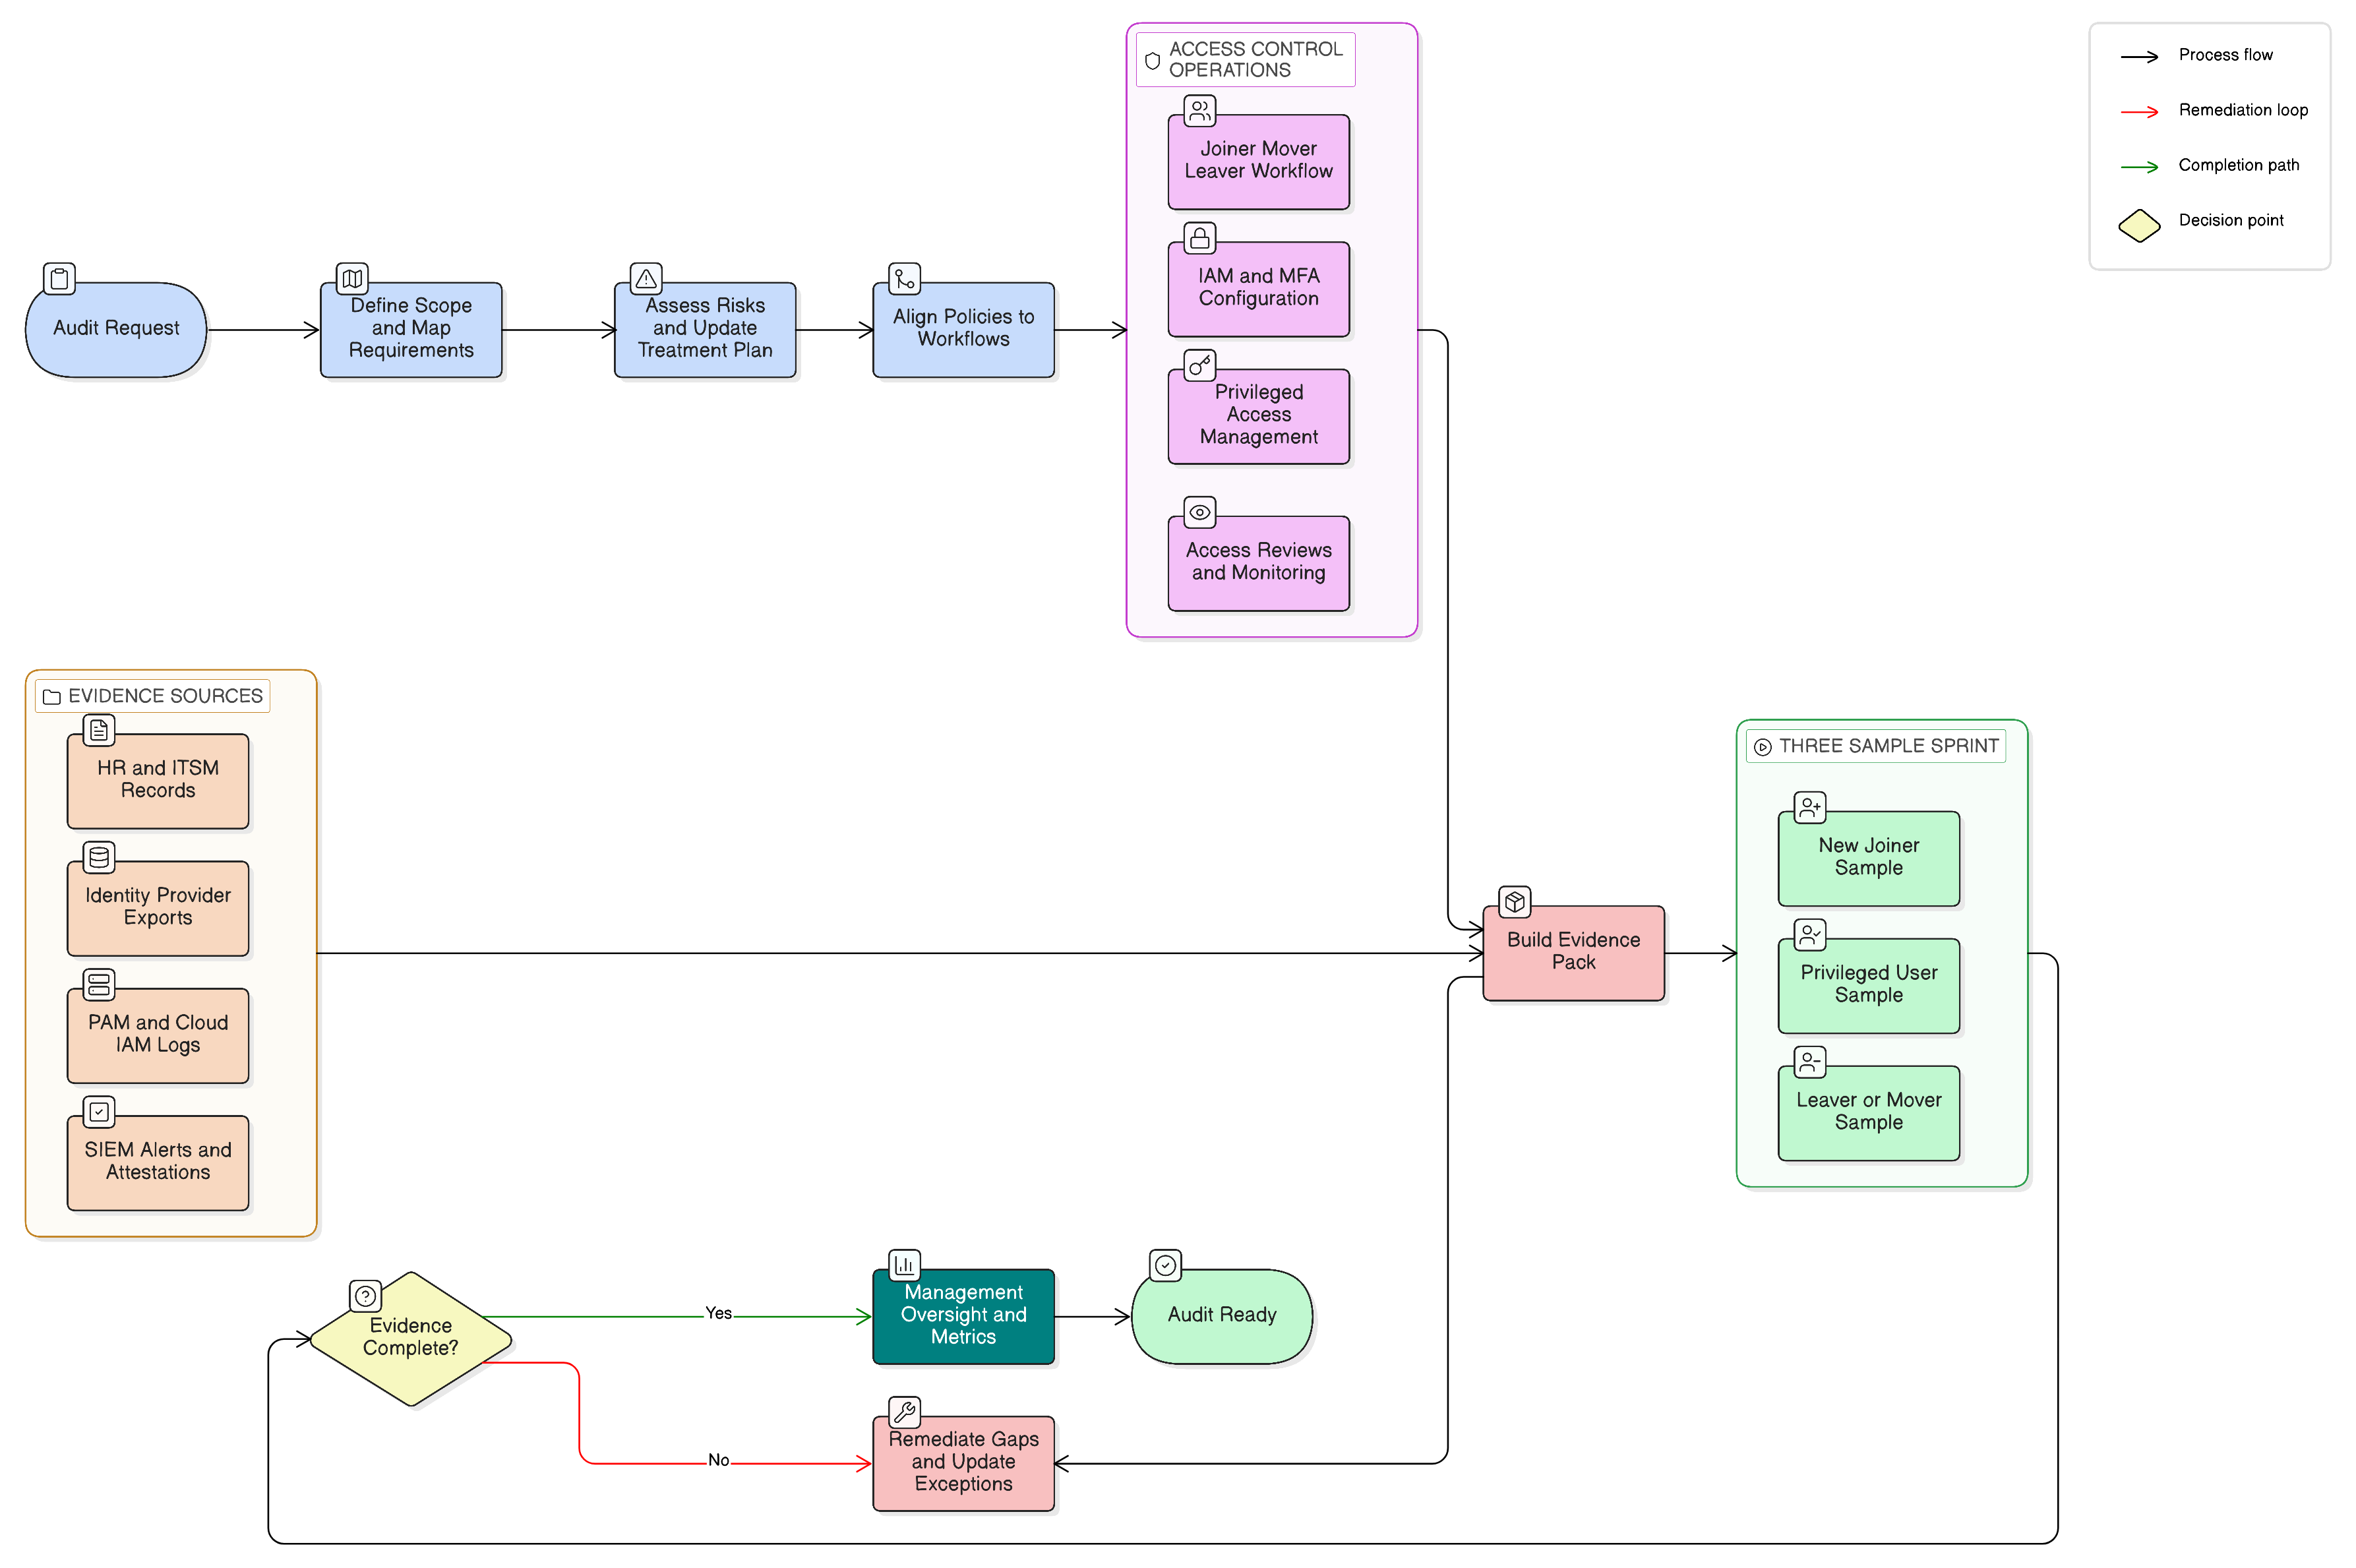
A practical CISO guide to building one access control evidence model for ISO/IEC 27001:2022, NIS2, DORA, GDPR, NIST and COBIT.
A practical CISO guide to mapping DORA major ICT-related incident reporting to ISO/IEC 27001:2022 Annex A controls, audit evidence, policy clauses, and Clarysec implementation tools.
A practical, audit-ready DORA 2026 roadmap for financial entities implementing ICT risk management, third-party oversight, incident reporting, operational resilience testing and TLPT using Clarysec policies, the Zenith Blueprint and Zenith Controls.