
EU Digital Identity Wallet Compliance Evidence Map 2026
A practical CISO guide for mapping EU Digital Identity Wallet relying-party evidence into ISO/IEC 27001:2022, GDPR, NIS2, DORA, NIST CSF 2.0 and COBIT 2019 using Clarysec policies and toolkits.
Articles tagged with "Supplier Management"
A practical CISO guide for mapping EU Digital Identity Wallet relying-party evidence into ISO/IEC 27001:2022, GDPR, NIS2, DORA, NIST CSF 2.0 and COBIT 2019 using Clarysec policies and toolkits.
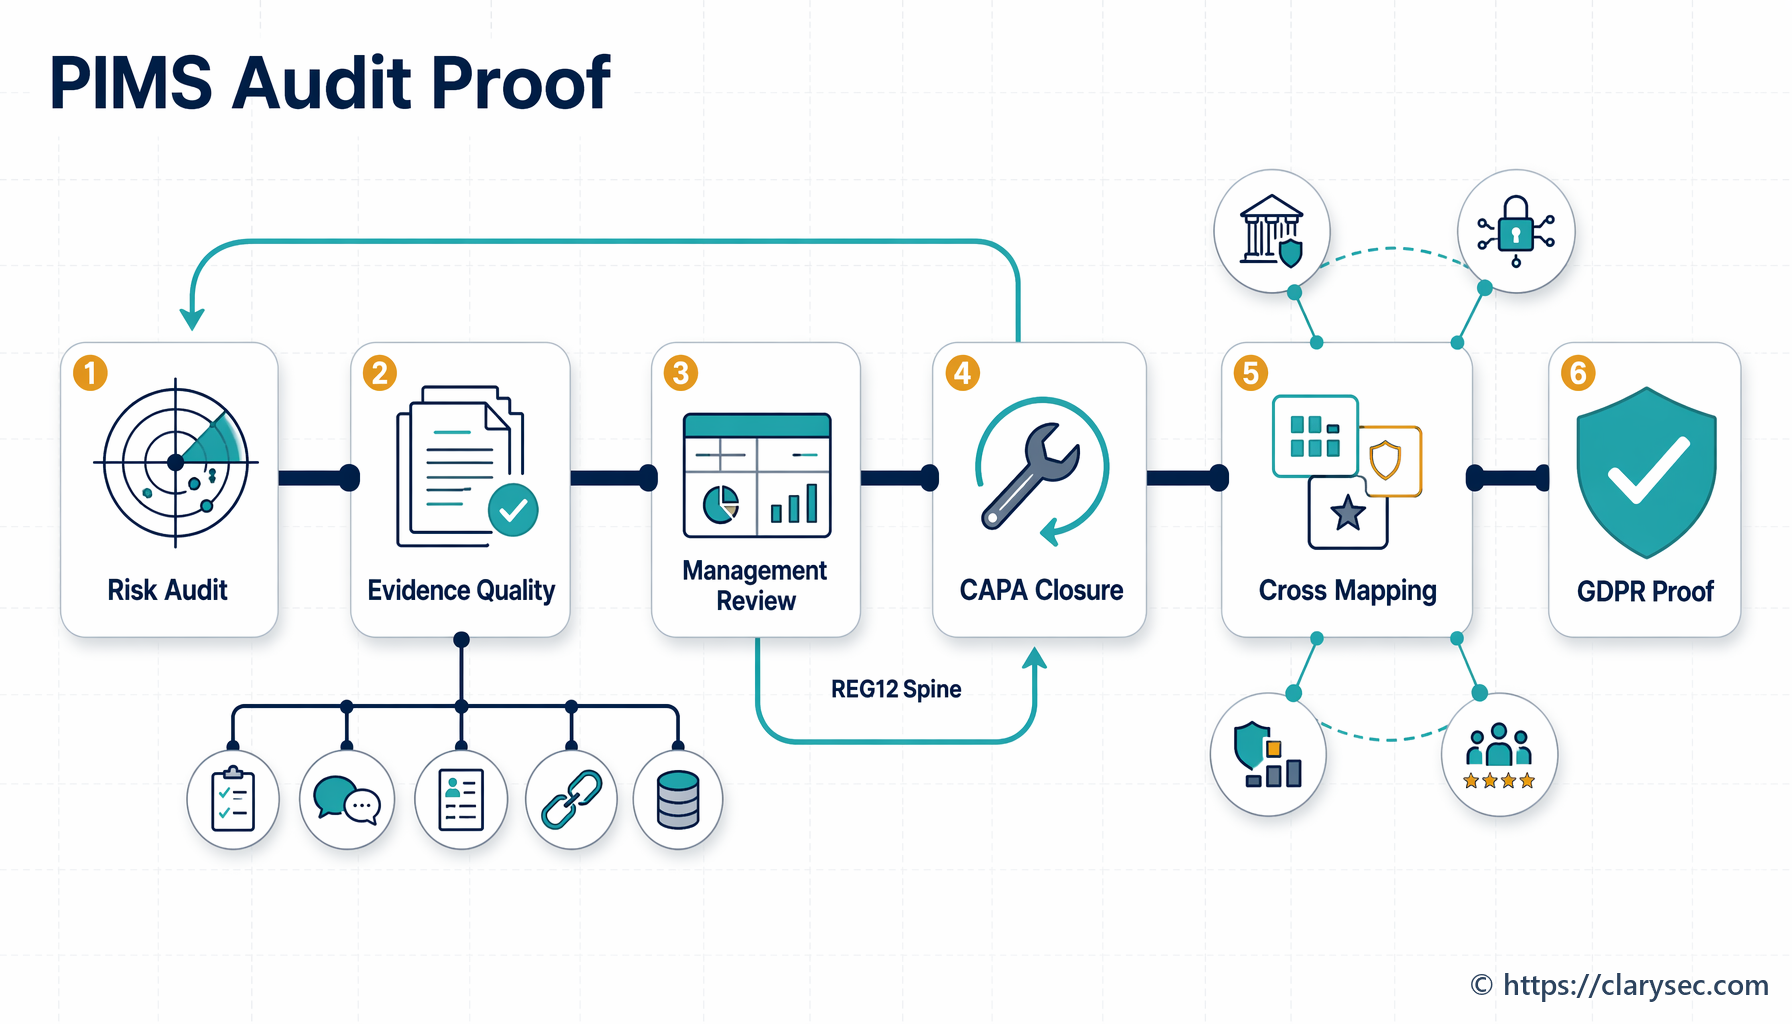
Learn how to build an ISO 27701:2025 PIMS audit and management review cycle that proves GDPR accountability with evidence, CAPA, leadership decisions and cross-compliance mapping.
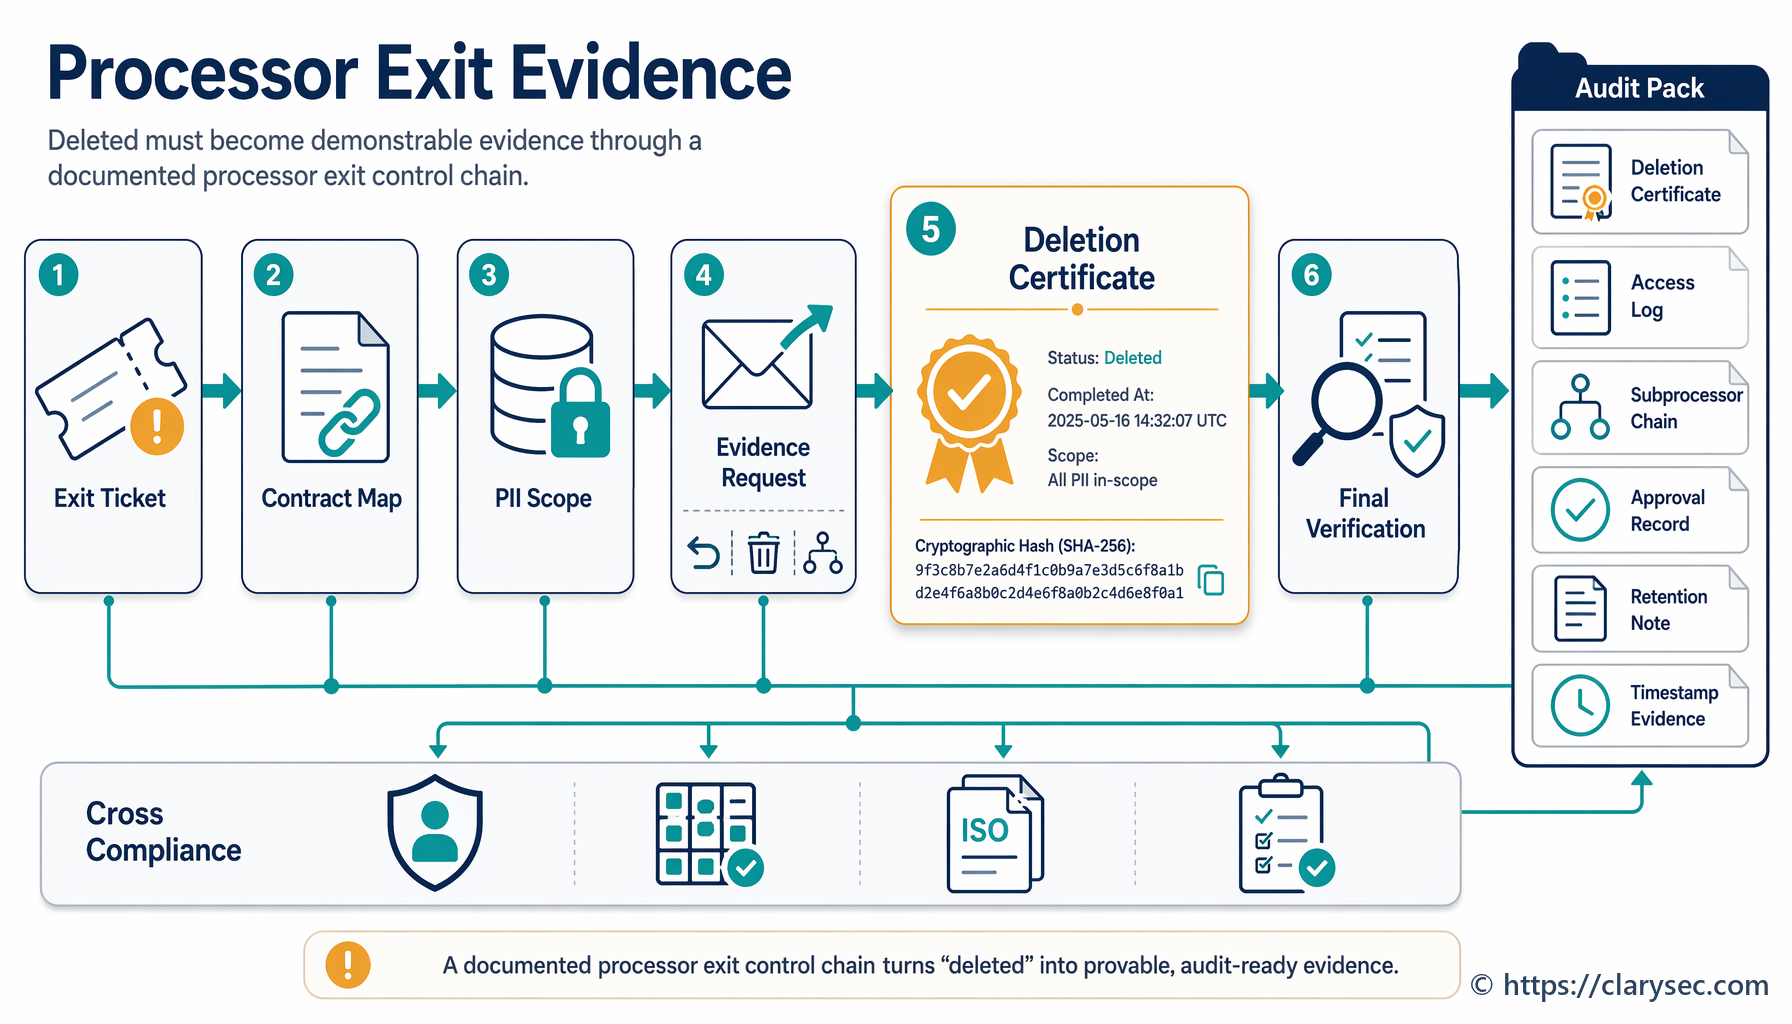
Processor exit is where supplier management, privacy governance, cloud offboarding and audit evidence collide. Learn how to build a deletion certificate workflow that supports GDPR, DORA, ISO/IEC 27701:2025 and ISO/IEC 27001:2022 compliance.
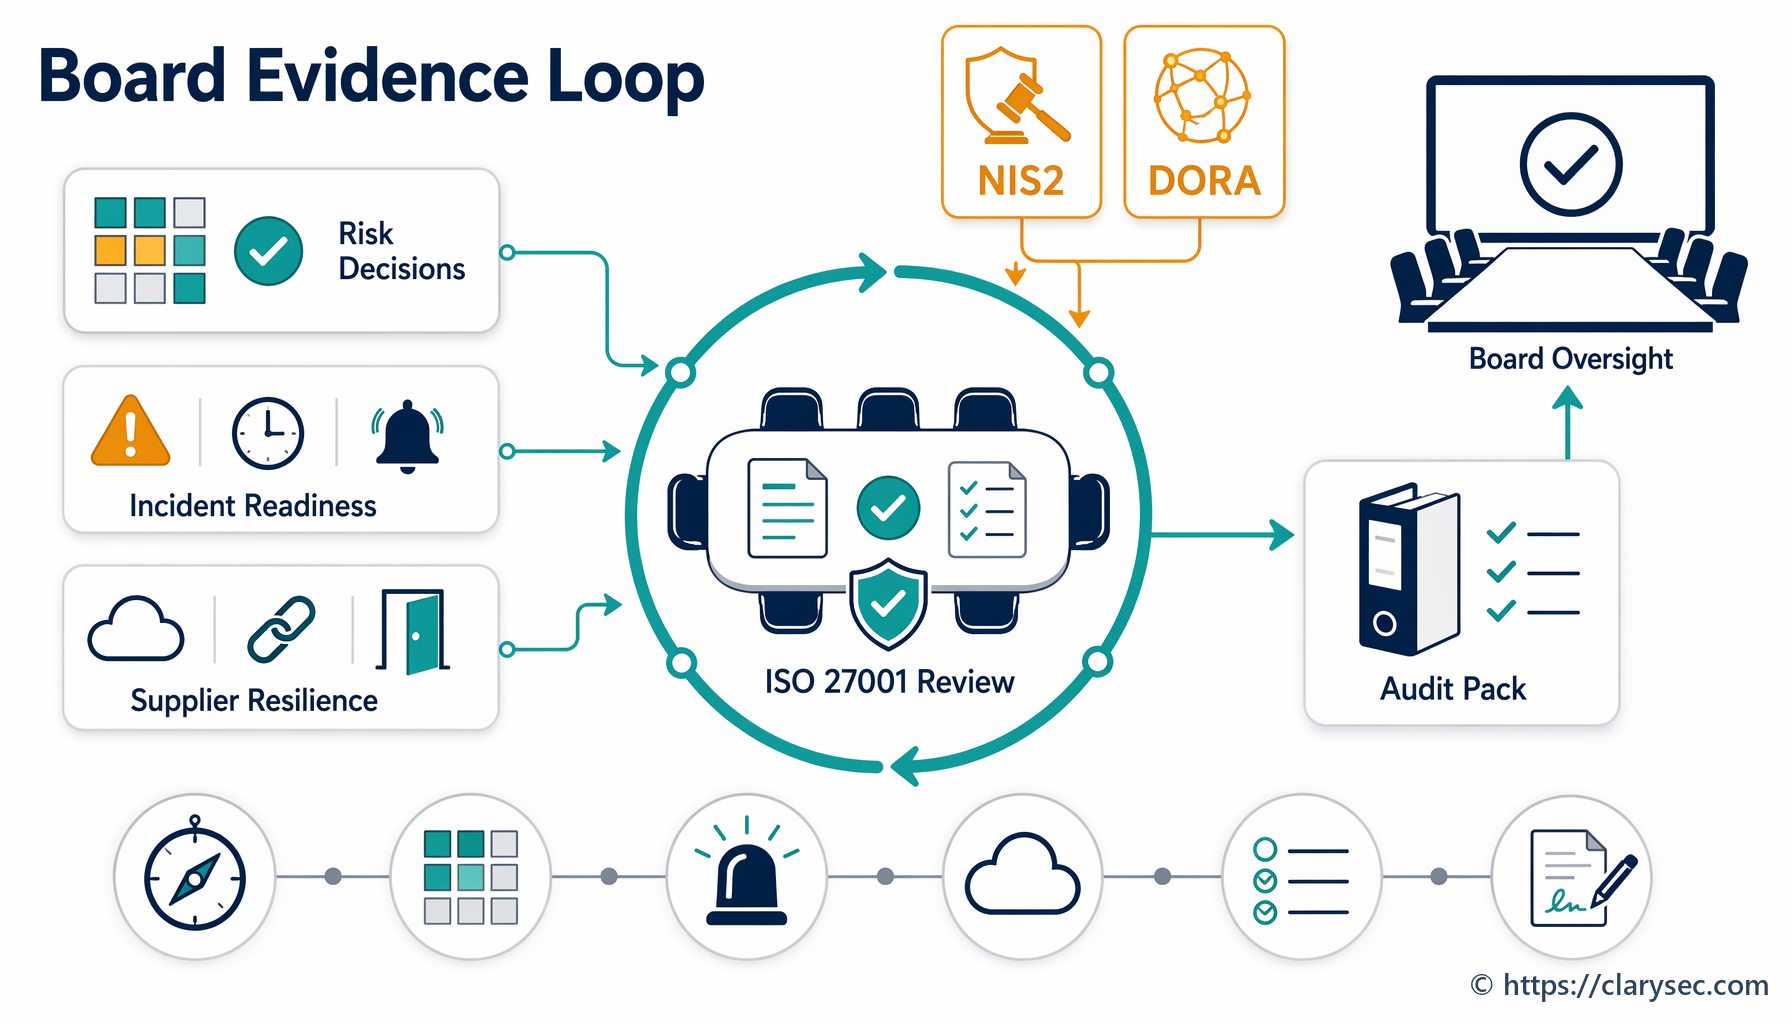
ISO/IEC 27001:2022 Clause 9.3 management review is becoming the practical board evidence mechanism for proving cybersecurity oversight under NIS2 and DORA. This guide shows how CISOs, compliance managers, auditors, and owners can turn review minutes, KPIs, incidents, risks, and corrective actions into defensible governance evidence.
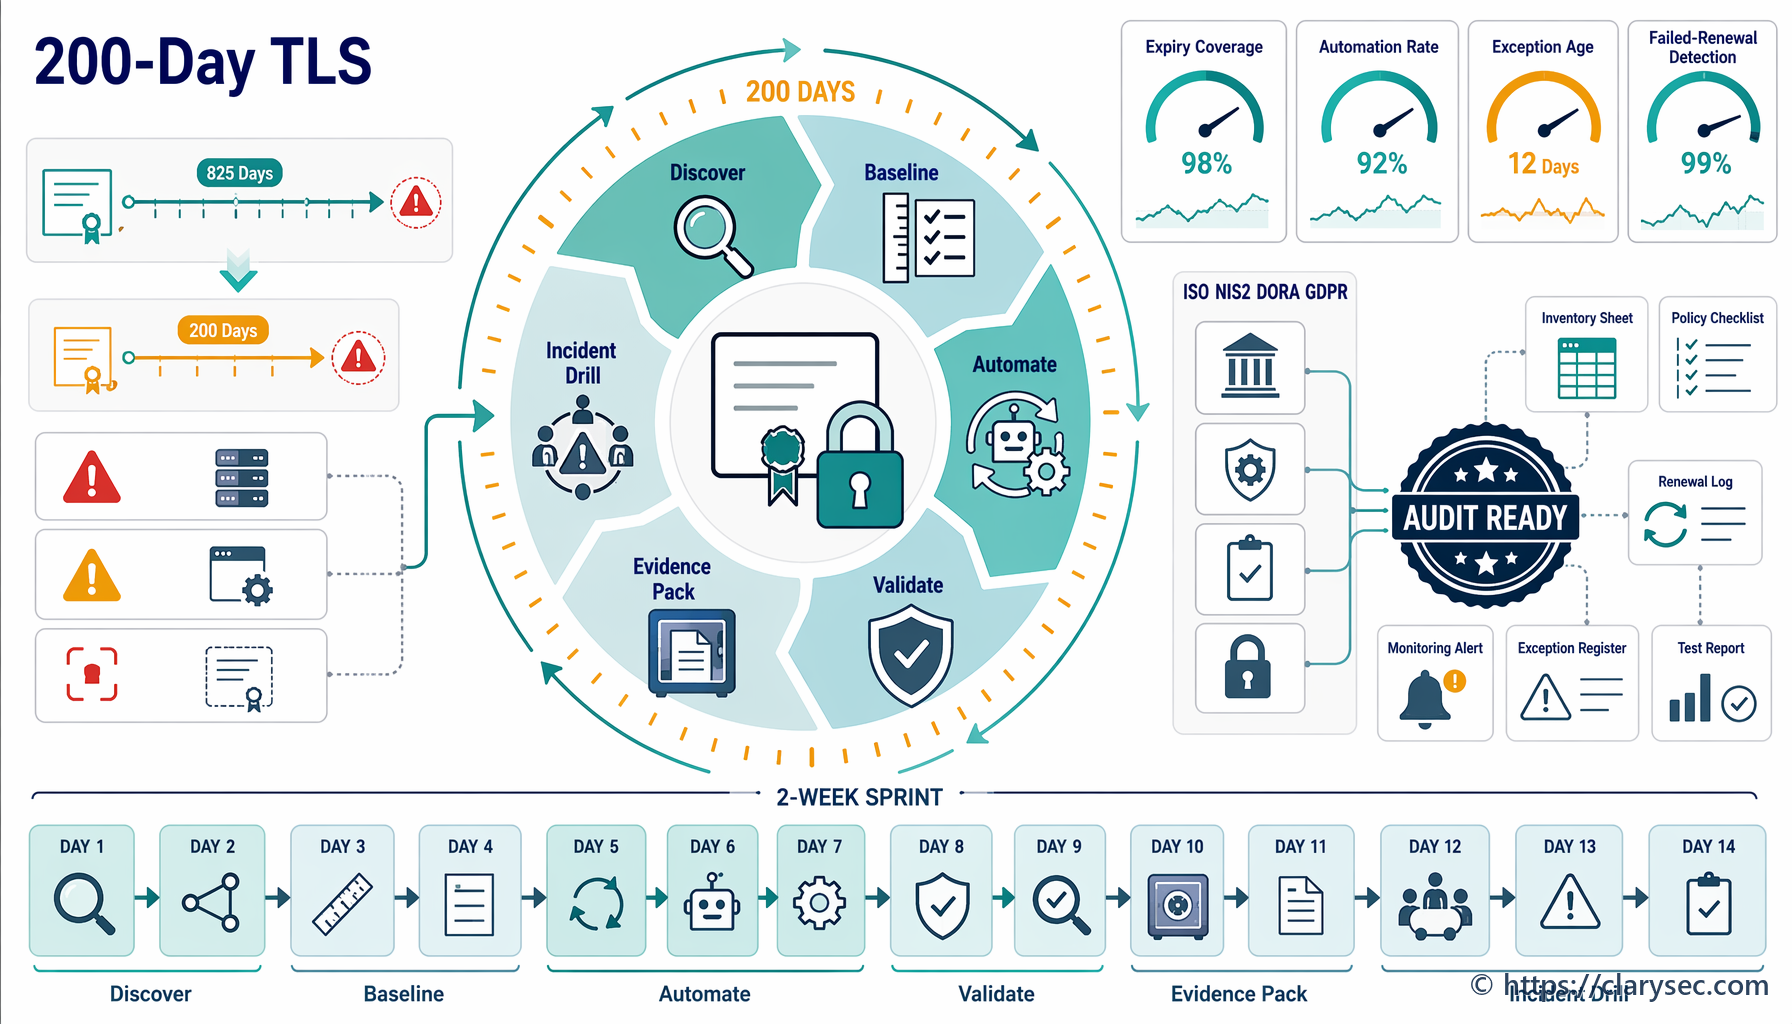
Shorter public TLS certificate validity turns renewal into a recurring governance, resilience and audit evidence challenge. This guide shows how to manage certificates as governed security assets under ISO/IEC 27001:2022, NIS2, DORA and GDPR Article 32.
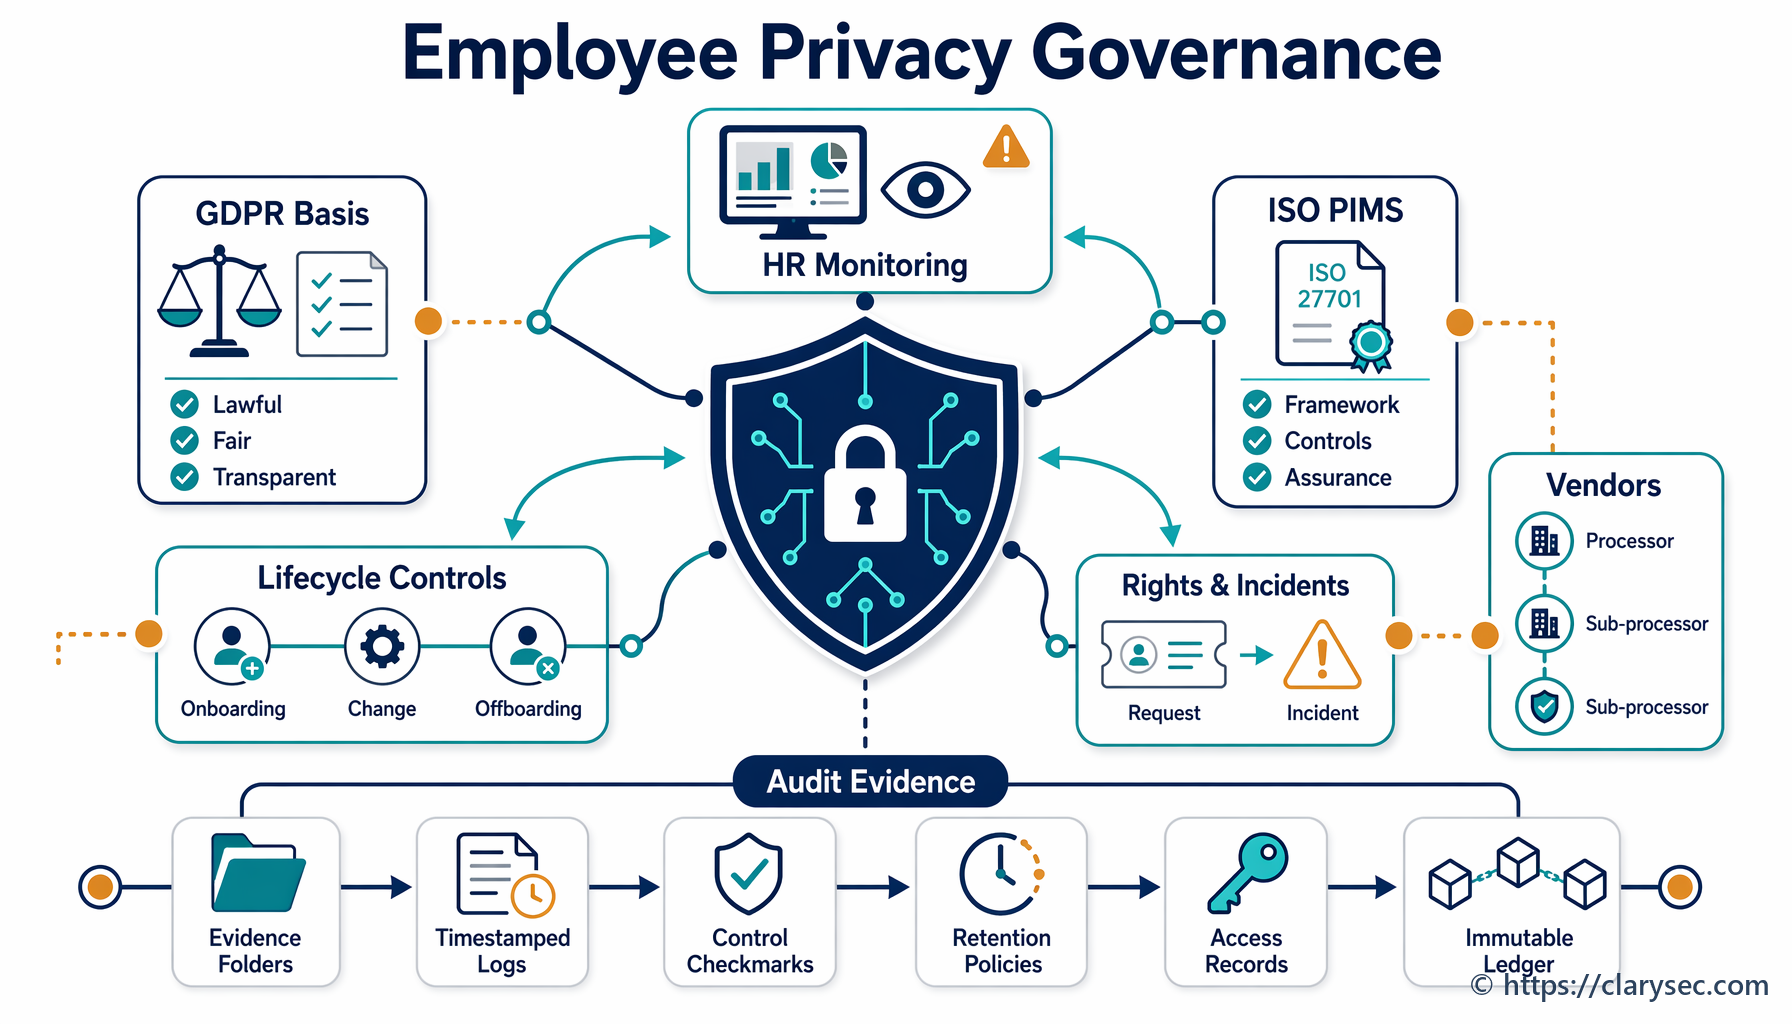
A practical CISO and HR compliance playbook for governing employee PII under GDPR, ISO/IEC 27701:2025, ISO/IEC 27001:2022, NIS2, DORA, NIST CSF 2.0, and COBIT 2019.
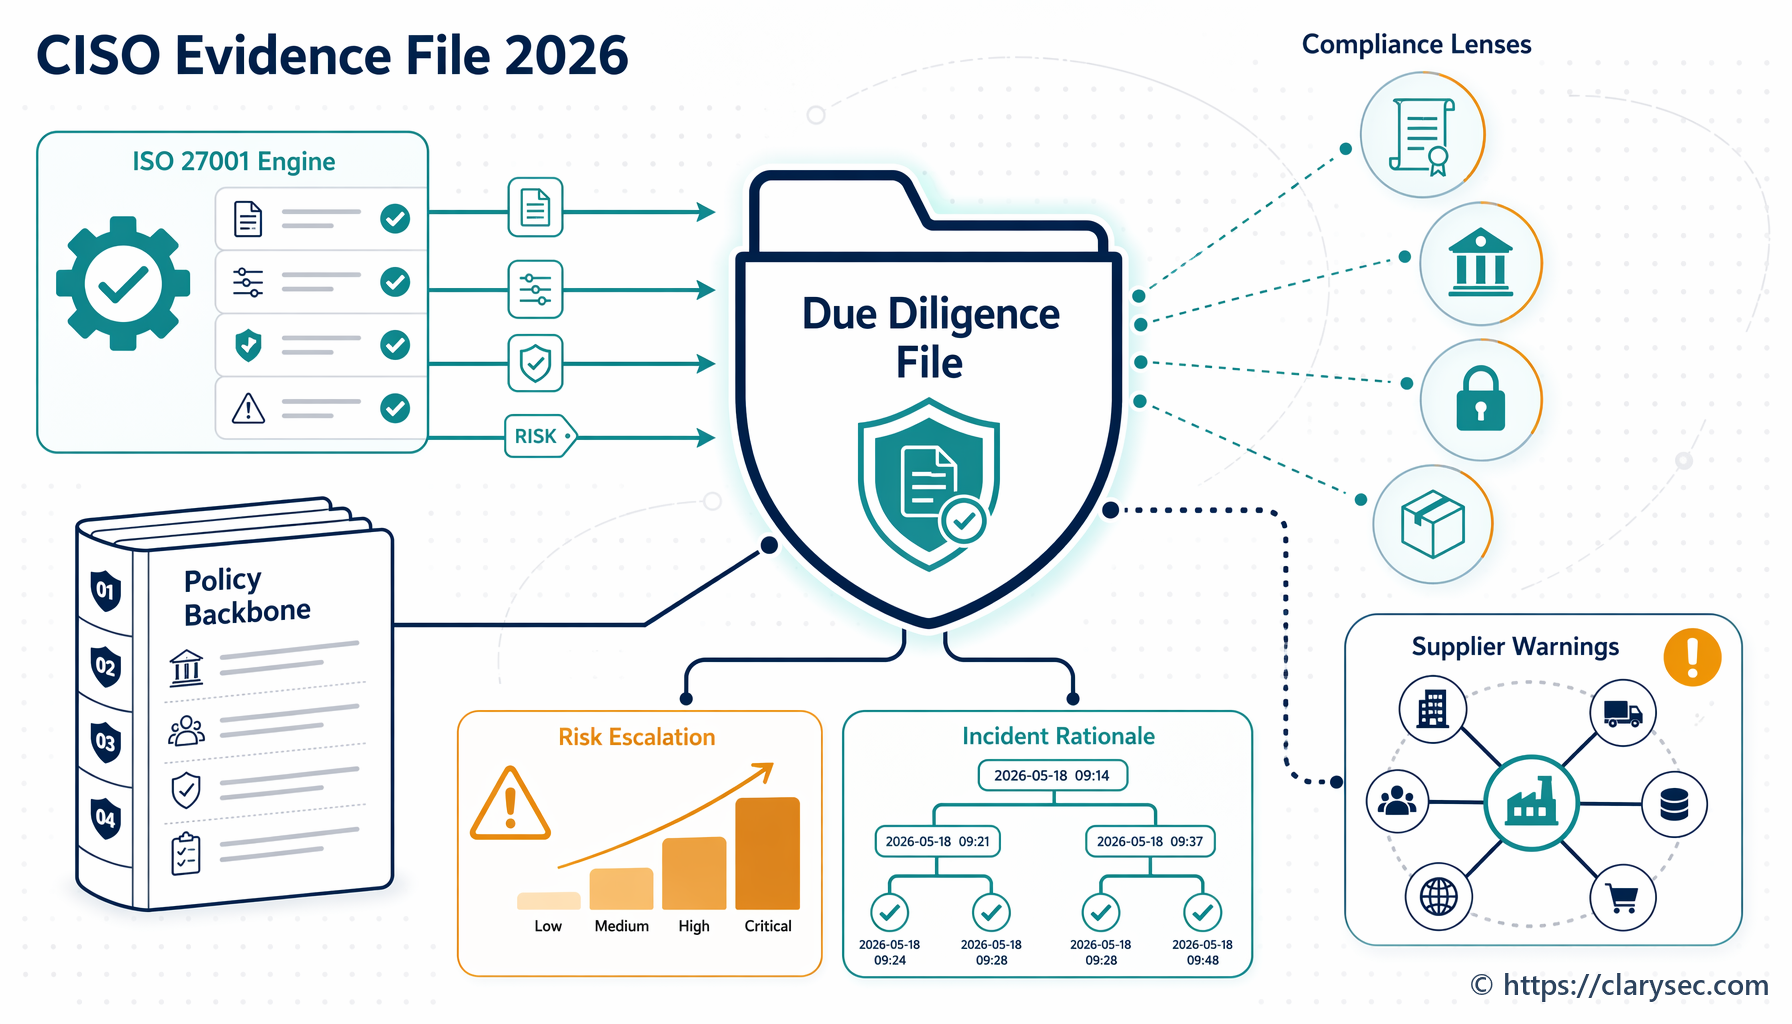
A practical guide for CISOs, compliance leaders and business owners who need defensible ISO 27001 evidence for NIS2 management accountability, DORA governance, supplier oversight and GDPR Article 32 security of processing.

A practical guide for CISOs and compliance teams to govern secure file transfer, map ISO/IEC 27001:2022 controls to GDPR, NIS2 and DORA, and produce audit-ready evidence.
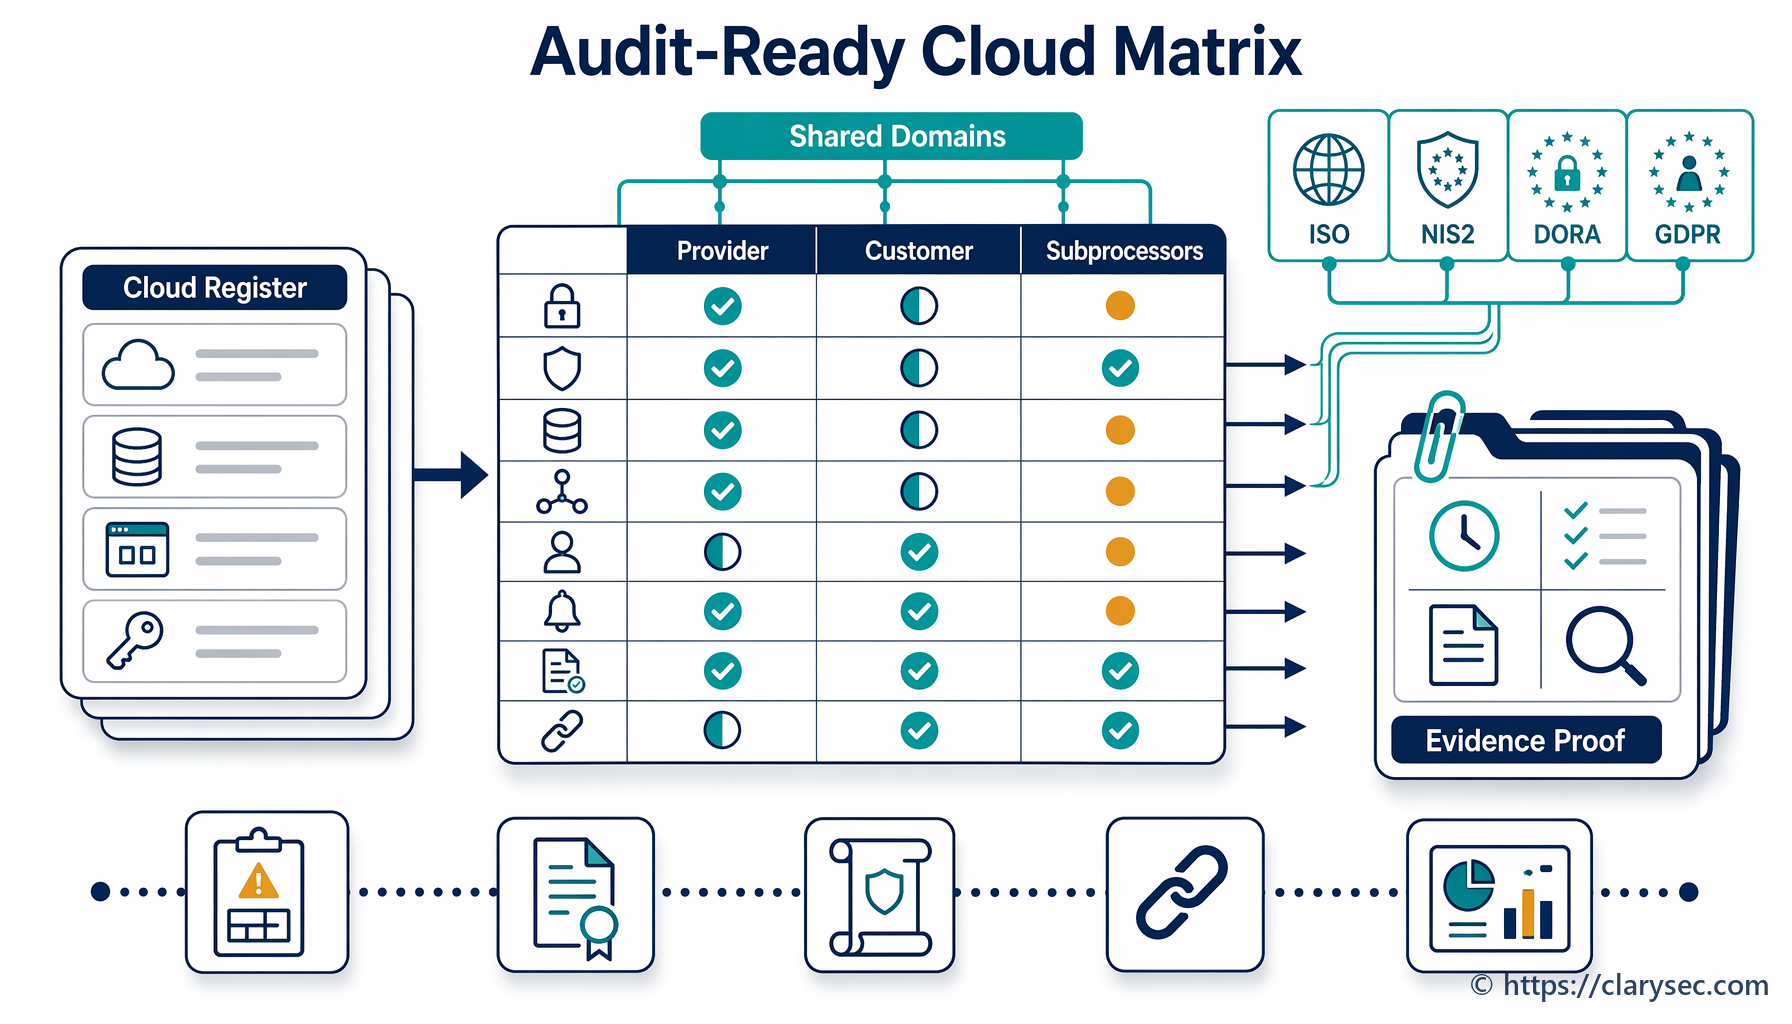
A practical CISO guide to building a cloud shared responsibility matrix that proves who owns each control, what evidence is required, and how cloud providers and subprocessors are governed across ISO/IEC 27001:2022, NIS2, DORA and GDPR.