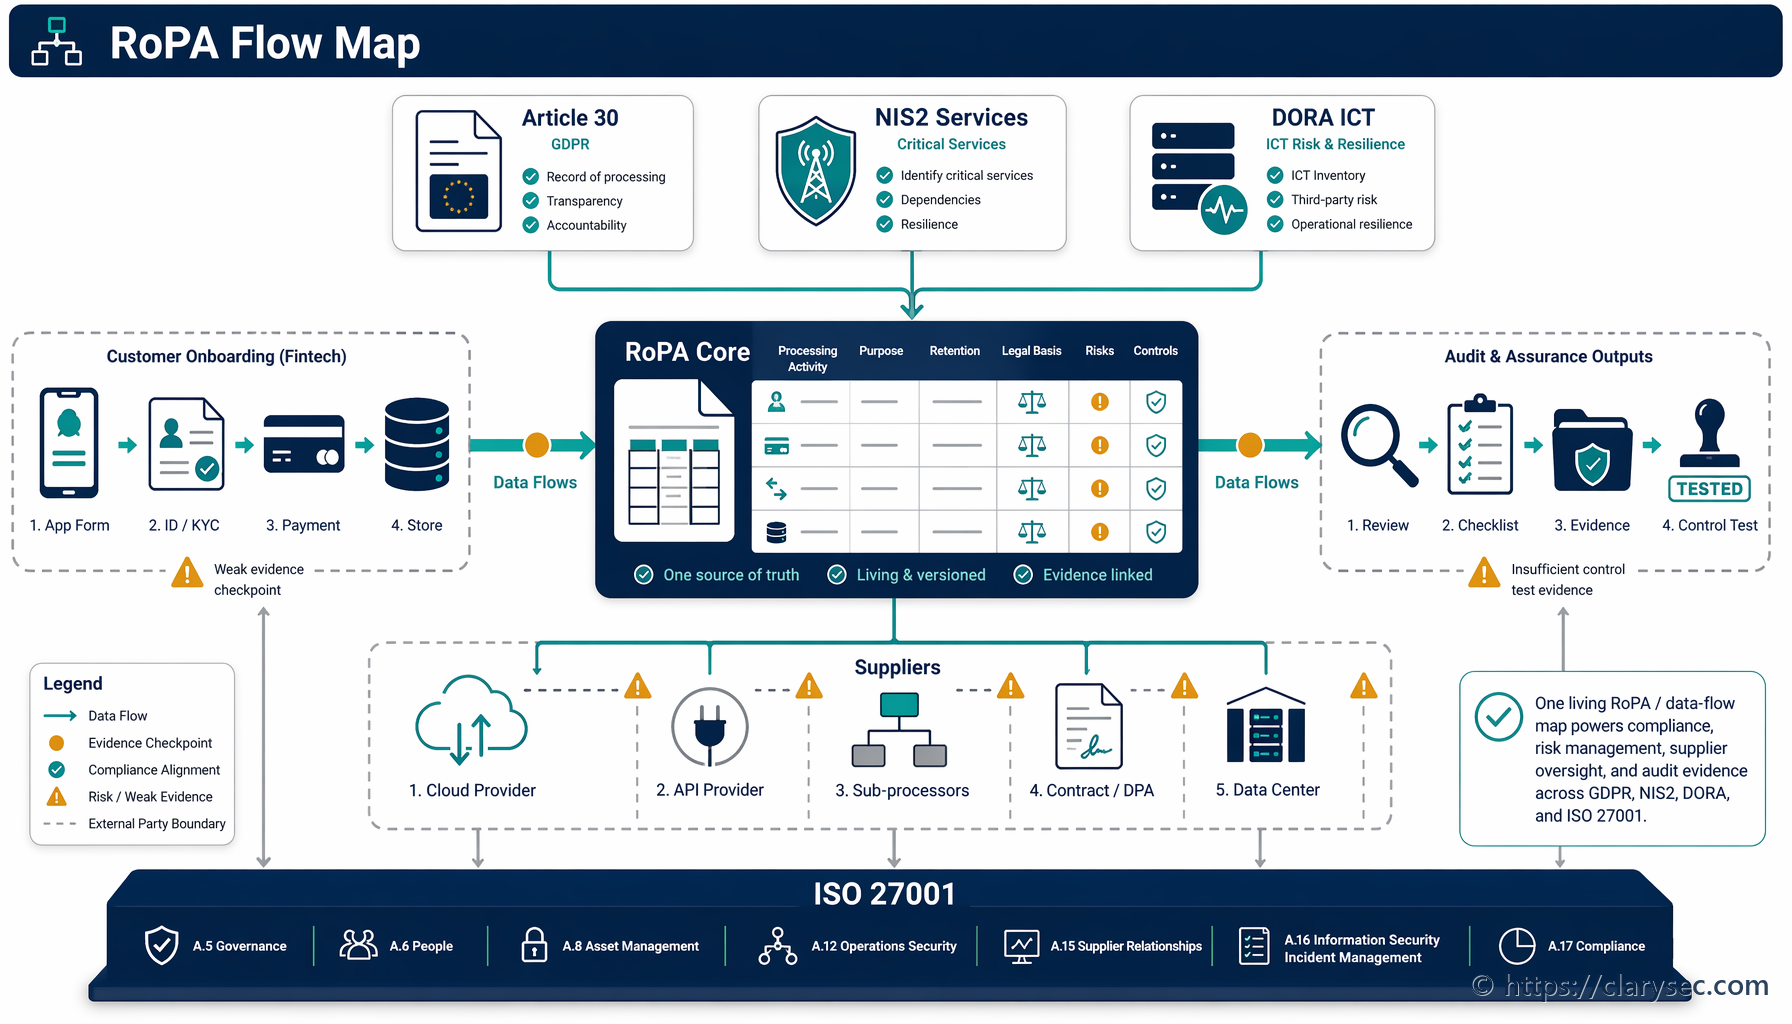
RoPA Data Flow Mapping for GDPR, NIS2 and DORA
A practical 2026 guide for turning RoPA and data flow mapping into a unified evidence layer for GDPR Article 30, NIS2 critical services, DORA ICT dependencies and ISO/IEC 27001:2022 audits.
Articles tagged with "Supplier Management"
A practical 2026 guide for turning RoPA and data flow mapping into a unified evidence layer for GDPR Article 30, NIS2 critical services, DORA ICT dependencies and ISO/IEC 27001:2022 audits.
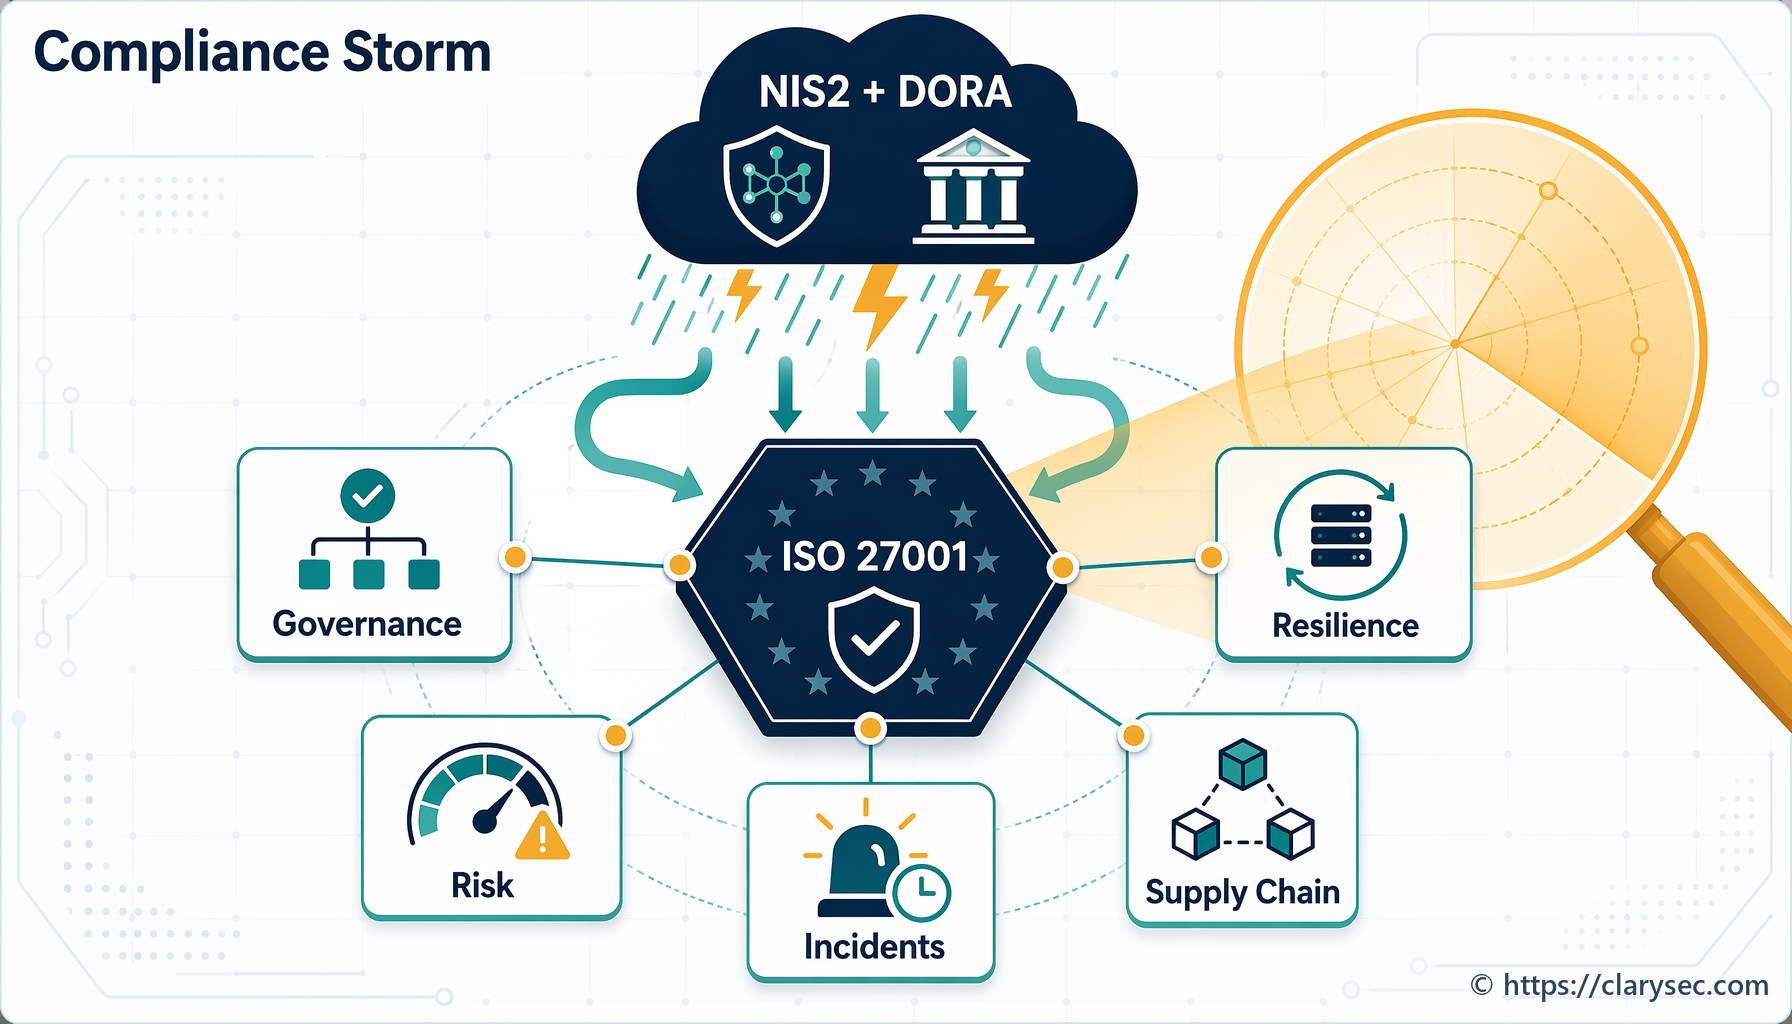
The EU’s NIS2 Directive and DORA Regulation are transforming cybersecurity compliance. This guide breaks down their impact and provides a practical path to readiness.
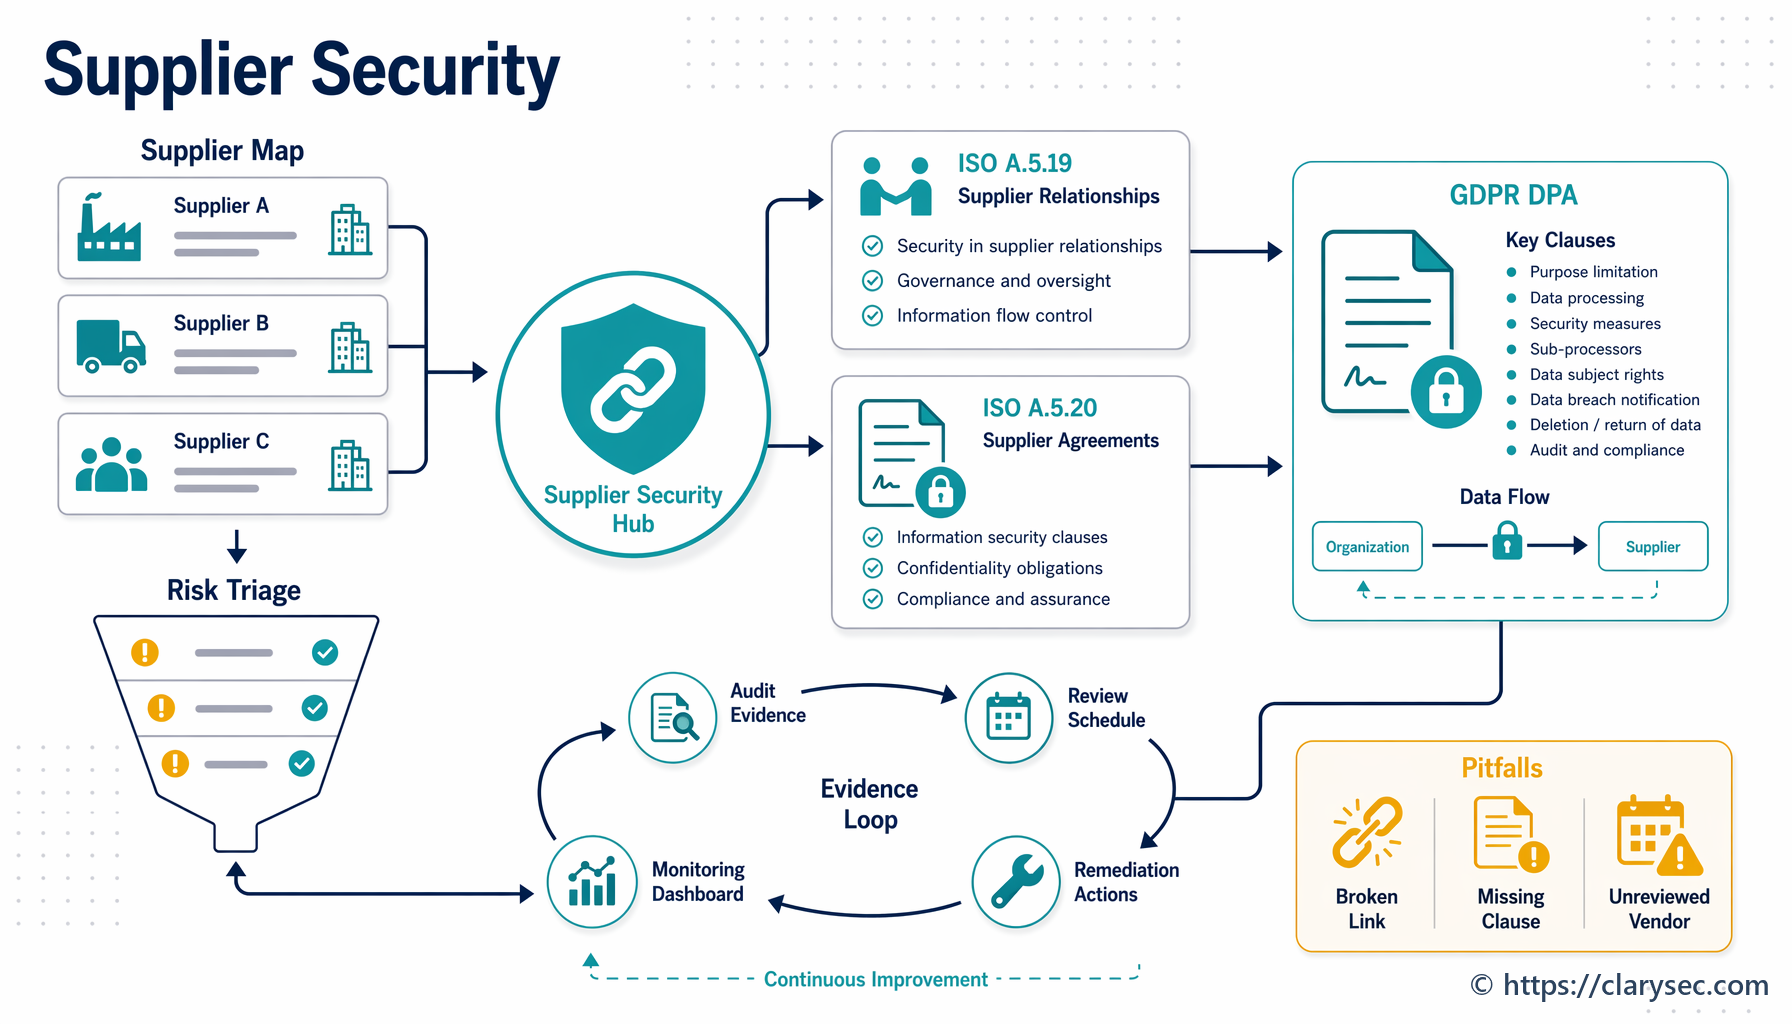
Learn to manage supplier security risks using ISO 27001:2022 controls A.5.19 and A.5.20, ensuring your DPAs and contracts meet stringent GDPR requirements.
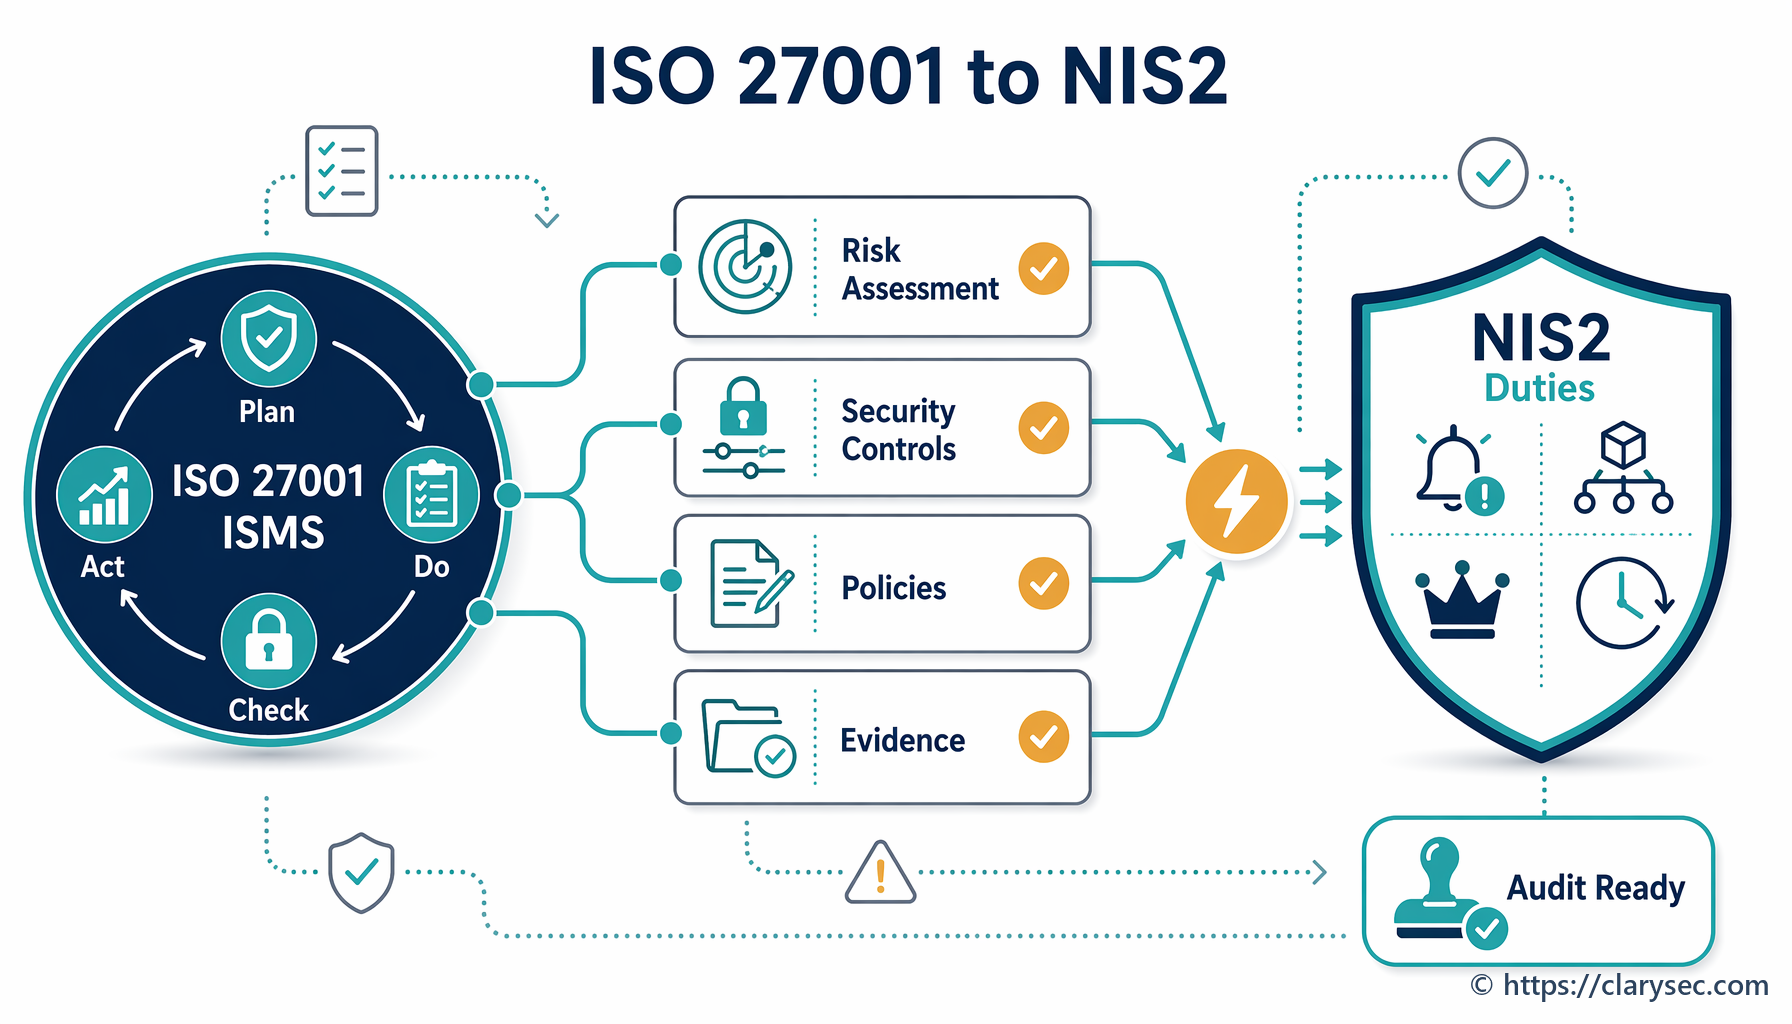
Learn how implementing an ISO/IEC 27001:2022 ISMS provides a robust framework that directly addresses the core cybersecurity requirements of the NIS2 Directive.